Article
Prying Eyes: Inside the NSA's War on Internet Security
Documents published with this article 44
-
BULLRUN CoI - Briefing Sheet [pdf]
A GCHQ briefing sheet introducing the BULLRUN Community of Interest — the access control framework protecting Five Eyes capabilities to defeat encryption across TLS/SSL, HTTPS, SSH, VPNs, IPSec, encrypted chat and encrypted VoIP — covering the classification structure, handling procedures and protective marking guidance for intelligence derived from cryptanalytic exploitation.
“N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Perlroth, Nicole · Larson, Jeff · Shane, Scott · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CLASSIFICATION GUIDE FOR CRYPTANALYSIS, 2-12 [pdf]
An NSA/CSS classification guide for cryptanalysis establishing the precise classification level for each type of information about NSA's capabilities to exploit commercial and indigenous encryption systems — from the unclassified acknowledgement that NSA exploits cryptographic devices, through to the Top Secret protection of cryptographic modifications made to commercial products to render them exploitable and industry relationships used to obtain cryptographic details.
“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Ball, James · Borger, Julian · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
TLS Trends: A roundtable discussion on current usage and future directions [pdf]
A presentation by Canada's Communications Security Establishment describing their TLS trend analysis programme, which systematically tracked SSL/TLS encryption parameters across warranted collection and Special Source access to identify cryptanalytic opportunities, monitor target behaviour and collaborate with GCHQ on exploiting weaknesses in widely-used encryption implementations.
-
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
TLS trends at GCHQ [pdf]
A GCHQ presentation describing their TLS trends analysis programme, which processed approximately 10 billion SSL/TLS Server Hello events per week from Special Source cable tapping and COMSAT collection to produce weekly trend reports, alongside two operational tools — TargeTLS for matching TLS events against BROAD OAK target profiles, and FLYING PIG, a TLS knowledge base enabling analysts to query certificate, IP and client data across the full intercept base.
-
TURMOIL/APEX/APEX High Level Description Document [pdf]
NSA WikiInfo page providing the high-level design description of APEX — the Active-Passive Integration capability integrating HAMMERMILL router implants with TURMOIL passive collection — enabling real-time exfiltration of targeted VPN (HAMMERSTEIN) and VoIP (HAMMERCHANT) traffic from compromised routers directly into NSA's passive collection and cryptanalytic attack infrastructure, with TURBINE providing automated command and control of the combined active-passive system.
Programs: TURMOIL · APEX · HAMMERMILL · HAMMERCHANT · HAMMERSTEIN · FASHIONCLEFT · TURBINE · TOYGRIPPE · METROTUBE · CHIMNEYPOOL · PIQBLADE · KEYCARD · FASCIA · ISLANDTRANSPORT · PRESSUREWAVE · ASDF · CONVEYANCE · TURBULENCE -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT -
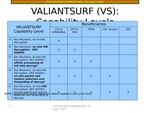
VALIANTSURF (VS): Capability Levels [pdf]
A capability status document for VALIANTSURF — NSA's programme for large-scale IPSec VPN decryption integrated with TURMOIL passive collection and LONGHAUL key recovery — defining five capability levels from basic key recovery through full hardware-accelerated on-site decryption with XKEYSCORE integration, and showing deployment status across named collection sites.
-
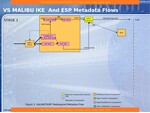
VS MALIBU IKE And ESP Metadata Flows [pdf]
A TOP SECRET four-slide architecture document describing MALIBU — NSA's system for intercepting and decrypting IPSec VPN traffic at the point where it crosses monitored internet cables — showing how intercepted VPN connections are processed, cryptographic keys recovered, traffic decrypted and results delivered to analysts, with separate diagrams for metadata collection, software decryption, full exploitation and survey modes.
-
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
VPN SigDev Basics [pdf]
A TOP SECRET VPN signals development training presentation from NSA's OTTERCREEK team introducing analysts to the six-stage workflow for discovering, assessing and exploiting VPN traffic — covering TOYGRIPPE, XKEYSCORE, DISCOROUTE and other repositories with live interface screenshots showing Iranian-German IPSec traffic and UNAMI (UN Assistance Mission for Iraq) router configurations containing pre-shared keys, including a Cuban VPN pre-shared key recovered in plaintext from a compromised router.
Programs: BLEAKINQUIRY · DISCOROUTE · TOYGRIPPE · MARINA · MASTERSHAKE · NKB · PINWALE · RENOIR · TREASUREMAP · TUNINGFORK · XKEYSCORE · GOLDPOINT · PILBEAM · RADIUS · CREAKSTILE · MAILORDER · ROADBED · DROPBOX · PPF -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
SPIN 15 VPN Story [pdf]
A TOP SECRET planning document describing two parallel workstreams in SPIN 15: the deployment of VPN decryption capabilities to SMOKYSINK (US-3237), a unilateral NSA RAMPART-T cable tap site operating without a third-party partner, and a risk reduction benchmarking activity measuring TURMOIL's VPN and SSL exploitation performance against the Net-Centric Capabilities (NCC) programme's Key Performance Parameters — which targeted 100,000 VPN decrypt requests per hour by the end of fiscal year 2011, and 10 million SSL sessions per day by the end of fiscal year 2012.
Programs: TURMOIL · SMOKYSINK · ISLANDHIDEAWAY · PICARESQUE · KEYCARD · XKEYSCORE · PRESSUREWAVE · ISLANDTRANSPORT · PIQBLADE -
Virtual Private Network Transform Engine Emulator [pdf]
An NSA WikiInfo page describing the Transform Engine Emulator (TEe) — a software tool that replicates at NSA headquarters the same VPN decryption pipeline that runs on deployed field collection systems, allowing encrypted VPN traffic forwarded back to headquarters to be broken using the same key recovery infrastructure, specifically by combining the VULCANDEATHGRIP and POISONNUT components.
-
Template:POISONNUT Product [pdf]
An NSA WikiInfo page describing the POISONNUT ESP attack scheduling component — the internal software element responsible for determining whether a VPN key recovery attack can proceed, submitting it to the cryptanalytic processing infrastructure, correlating responses, and marking each attack attempt as successful or failed.
Programs: POISONNUT -
TURMOIL GALLANTWAVE [pdf]
An NSA WikiInfo page describing TURMOIL GALLANTWAVE — a CES mission application hosted on TURMOIL that decrypts communications using Data Network Session Cipher (DNSC) technologies, such as SSL/TLS, by integrating with the LONGHAUL SCARLETFEVER key recovery service and forwarding decrypted sessions to XKEYSCORE for analyst access.
Programs: VALIANTSURF · XKEYSCORE · TURMOIL · GALLANTWAVE · LONGHAUL · TURBULENCE · BULLRUN · SCARLETFEVER · TUMULT · TUBE · UTT · BTUBE · FISHWAY · EXOPUMP · PURGE · SURGE · SCISSORS · PINWALE · TUSCARORA · NUCLEON · WDM · TURTLEPOWER · CONVEYANCE · ONEROOF · KEYCARD · SLIDETACKLE · POLARSTARKEY · TUMMS · CEMETERY · TEPIDTSUNAMI · PPF · ISLANDTRANSPORT -
TURMOIL VPN PROCESSING [pdf]
A TURMOIL VPN Processing technical briefing from October 2009 describing the full architecture for intercepting and decrypting IPSec VPN traffic within the TURMOIL passive collection platform — covering IKE/ESP protocol handling, five distinct data flow types, the Dell LPT hardware implementation, and live operational metrics showing over 8 million packets decrypted at Menwith Hill and 1.4 million at SMOKYSINK during a single week in October 2009.
-
VALIANTSURF [pdf]
An NSA WikiInfo page for VALIANTSURF — the coverterm for NSA's IPSec VPN decryption capability within the TURMOIL collection platform — describing the four data flow types for intercepting and breaking encrypted VPN traffic, the full deployment roster across collection sites including Menwith Hill, SMOKYSINK, MUSCULAR, CROSSCUT and others, and the architectural taxonomy of the VALIANTSURF programme including its MALIBU and WAIMEA processing architectures and their relationship to LONGHAUL, POISONNUT and GALLANTWAVE.
Programs: VALIANTSURF · TURMOIL · TURBULENCE · HOOKED · HOOKEDHAND · CINDER · CINDERASH · CINDERTRACK · SCARLETFEVER · LONGHAUL · FALLOUT · TOYGRIPPE · PICARESQUE · XKEYSCORE · PRESSUREWAVE · ASDF · MAILORDER · TUBE · KEYCARD · POISONNUT · ISLANDHIDEAWAY · ISLANDTRANSPORT · EXOPUMP · CORALREEF · PINWALE · TUSCARORA · ONEROOF · CONVEYANCE · TURTLEPOWER · WDM · CADENCE · UTT · SCISSORS · FISHWAY · BTUBE · DNCA · ROMULANALE · GALLANTWAVE · ROMULANGAWK · ROMULANGOWL · MALIBU · WAIMEA · WAIMEAVISAGE · ROMULANVISAGE · WAIMEAVISE · ROMULANVISE · APEX · METROTUBE · MADFORGE · JSORCERER · CROSSCUT · CIET · LATTICE · STARQUAKE · SARATOGA · MUSCULAR · SMOKYSINK · SLACKKEY · TUMMS · PURGE · SURGE · NUCLEON · SPAGIC · PPF · SOAP · TUMULT · FIP · PIQBLADE · DEEPDIVE · IBRIDGE -
TURMOIL IPSEC VPN SESSIONIZATION [pdf]
An NSA technical specification document describing how TURMOIL detects and sessionizes IPSec VPN protocol traffic — covering the six IPSec protocol stacks targeted for collection, the specific keyword and bitmask patterns used by the Atomic Event Generator to identify each packet type at wire speed, and the sessionization parameters used to group related packets into coherent sessions for downstream processing.
-
TURBULENCE - Fielded Capability: End-to-End VPN, SPIN 9 Design Review [pdf]
An NSA SPIN 9 design review presentation describing the transition of TURMOIL's VPN decryption capability from the legacy Red Architecture to the new Blue Architecture — covering the full end-to-end dataflow, component interfaces, test scenarios and detailed processing specifications for each system in the VPN decryption pipeline.
Programs: TURBULENCE · TURMOIL · KEYCARD · WEALTHYCLUSTER · TUBE · XKEYSCORE · PRESSUREWAVE · EXOPUMP · PWV · TOYGRIPPE · PICARESQUE · AGILITY · MAILORDER · ISLANDTRANSPORT · PIQBLADE · PINWALE · TRAFFICTHIEF · IBRIDGE · PPF · METROTUBE · FIP · SSO -
User's Guide For PRISM Skype Collection - August 2012 [pdf]
An NSA analyst user guide for PRISM Skype collection, explaining how to task Skype selectors, locate collected content across PINWALE, NUCLEON and MARINA, interpret common collection artefacts, and troubleshoot issues with video synchronisation, timestamp discrepancies and incomplete file transfers — covering peer-to-peer, in/out and conference call collection modes from PRISM coverage that began in February 2011.
-
BULLRUN [pdf]
A GCHQ TOP SECRET STRAP1 briefing presentation on BULLRUN — summarising the programme's purpose, the network security technologies it targets, the sensitivities surrounding cryptanalytic capabilities, and the access control framework protecting both technical details and the "fact of" capability — notable for explicitly naming three ECIs protecting the technical underpinnings: PICARESQUE, PAWLEYS and AMBULANT.
-
LONGHAUL [pdf]
An NSA WikiInfo page for LONGHAUL — the centralised end-to-end attack orchestration and key recovery service that sits at the heart of NSA's capability to break encrypted internet traffic, receiving cryptanalytic data from field collection systems, coordinating attacks against VPN and SSL/TLS encryption through child projects POISONNUT and SCARLETFEVER, and returning recovered keys to deployed CA Servers at collection sites worldwide.
Programs: LONGHAUL · MAILORDER · CASPORT · GECC · VIVIDDREAM · TURMOIL · WEALTHYCLUSTER · TUTELAGE · EINSTEIN · ISLANDTRANSPORT · HADOOP · NINJACOVE · JST · CST · VMM · VDG · ORDC · SCB · ISLANDHIDEAWAY · TURBULENCE · POISONNUT · SCARLETFEVER · HEROICSAND · PLATINUMRING · GALLANTWAVE · JEDIMINDTRICK · CHAOTICSTORMTROOPER · CORALREEF · SCUBADIVER2 · TERRACOTTA · HBASE · SCALA · MAPREDUCE · COALCAR · STOCKCAR · BEACHHEAD · MIDRIFT · WOLVERINESTAKE · NSP · PURGE · SURGE · C2DP · DOORS · HUDSON -
Net Defense from Encrypted Communications [pdf]
A NSA Technology Directorate briefing from February 2012 describing BLUESNORT — a capability that repurposes GALLANTWAVE's SSL/TLS decryption pipeline for network defence, re-injecting decrypted traffic into TURMOIL Stage 1 Prime where BLUESNORT detects malware and other malicious activity — representing description of NSA using its own bulk decryption infrastructure for cyber defence as well as intelligence collection.
-
SIGDEV Conference 2012 - Making Things Measureable: Technology Trending Challenges and Approaches [pdf]
An NSA presentation from the 2012 SIGDEV Conference describing NSA's technology trending methodology — a framework for identifying which encryption and communications technologies targets are adopting, measuring the SIGINT risk they pose, and prioritising capabilities development responses — notable for containing the risk matrix that was later cited in Der Spiegel's December 2014 encryption investigation showing NSA's difficulty levels against specific technologies including Tor, TrueCrypt, OTR and ZRTP.
Programs: XKEYSCORE · SEEKER · BIONICTURTLE · JEMA · JOLLYROGER · MARINA · TUNINGFORK · STARPROC · MICROEXPANSE · ECHOBASE · PRISM · GMHALO · UTT · TKB · LAE · FAMT · WPMO · AMOD · FORTREND · GAMBIT · DATAEXPLORER · MYNOC -
SCARLETFEVER [pdf]
NSA WikiInfo page describing SCARLETFEVER — the second LONGHAUL cryptanalytic capability, a message-driven cryptologic exploitation service for DNSC (Data Network Session Cipher) traffic serving clients including TURMOIL, WEALTHYCLUSTER and the TEe, communicating via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: SCARLETFEVER · LONGHAUL · TURMOIL · WEALTHYCLUSTER · TEE · ISLANDTRANSPORT · ISLANDHIDEAWAY · POISONNUT · PICARESQUE -
VoIP NSA alias [pdf]
A GCHQ GCWiki record of SAMESHEET — the joint NSA/GCHQ working group on media over packet and VoIP interception — containing meeting notes and IETF trip reports documenting NSA's monitoring of internet standards development, including the passage cited in Der Spiegel's December 2014 encryption article showing an NSA attendee at the IETF San Diego meeting reporting that "new session policy extensions may improve our ability to passively target two sided communications."
Marking: UK TOP SECRET -
A potential technique to deanonymise users of the TOR network [pdf]
A TOP SECRET GCHQ research presentation describing a traffic correlation attack against Tor — using cumulative packet counts observed simultaneously at a controlled exit node and at SIGINT collection points near a target's guard node to deanonymise Tor users without breaking the encryption — with GTE and JTRIG having adapted owned exit nodes to collect the required data for live deployment.
-
Tor Hidden Services - How Hidden is 'Hidden'? [pdf]
A TOP SECRET GCHQ presentation analysing the security of Tor hidden services — covering the hidden service protocol architecture, possible exploitation vectors including the Coil Attack against introduction points, a beaconing pattern discovered in idle hidden services, and the HOMING TROLL bridge discovery capability — concluding that hidden services are "near impossible" to deanonymise but noting several research avenues including PRESTON integration.
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
TOR deanonymisation research (MIP) [pdf]
A TOP SECRET GCHQ wiki page documenting the research task on Tor deanonymisation — the project page linking the entry-exit correlation attack described in the OPC-MCR presentation to its formal research output, confirming the attack was successfully documented in OPC-M/TECH.B/61, presented at SANAR11, and planned for prototyping in the REMATION II workshop.
-
Tor: Overview of Existing Techniques [pdf]
A TOP SECRET GCHQ presentation summarising existing Tor exploitation techniques and 2012/13 plans documenting GCHQ's Tor-related programmes, naming QUICK ANT, HOMING TROLL, NEWTONS CRADLE, TRIBAL CARNEM, EPIC FAIL, THEMP, NATURAL SELECTION and HAKIM alongside the MCR deanonymisation research, traffic shaping, hidden service investigation and bridge discovery work.
Programs: HOMINGTROLL · NEWTONSCRADLE · JTRIG · TRIBALCARNEM · EPICFAIL · QUICKANT · NATURALSELECTION · REMATION · HAKIM · THEMP -
A potential technique to deanonymise users of the TOR network [pdf]
The GCHQ technical report documenting the entry-exit traffic correlation attack against Tor — providing the complete mathematical specification, test methodology, experimental results and software reference implementation, with distribution to NSA R1, NSA R4, NSA CES, CSE, DSD, SEQUOIA, ICTR, JTRIG, TEA, GTE and multiple OPC divisions.
-
SIGINT Strategy Threads 4 and 7 SIDtoday [pdf]
A TOP SECRET SIDToday article from September 2011 describing SIGINT Strategy Threads 4 and 7 — NSA's two classified programmes addressing the challenge of ubiquitous internet encryption — directing cleared analysts to BULLRUN-protected content covering capabilities against commercial webmail encryption used by CT targets and VPN traffic exploitation, with access requiring BULLRUN Community of Interest indoctrination.
-
PGP encrypted email can't be decrypted by the NSA [pdf]
Two intercepted Yahoo email messages collected under FAA counterterrorism authority through PRISM (SIGAD US-984XN), both containing PGP-encrypted content that NSA was unable to decrypt — published by Der Spiegel as direct evidence that PGP encryption defeated NSA collection at the time of interception in January 2012.
Programs: PRISM -
Crypt Ops Data Store User Guide [pdf]
A SECRET GCHQ user guide for the Crypt Ops Data Store — the internal task management system used by GCHQ's cryptanalytic operations division to receive, triage, assign and track decryption and cryptanalytic requests — notable for its category list which maps task types to operational programmes including BULLRUN, BEARDED PIGGY and VPN exploitation.
Marking: SECRET -
Crypt Discovery Joint Collaboration Activity 20 January 2011 [pdf]
A TOP SECRET NSA/GCHQ joint collaboration activity plan from January 2011 describing a research programme to understand and mitigate the threat that rising encryption adoption poses to target discovery and development — measuring encryption prevalence across SIGINT collection, assessing the impact on metadata-based targeting tradecraft, and developing new techniques for identifying targets behind encrypted traffic using a joint cloud environment fed by MUTANT BROTH, BEARDED PIGGY, KARMA POLICE, MEMORY HOLE, MARBLED GECKO, SOCIAL ANIMAL and ASDF metadata.
Marking: TOP SECRETPrograms: TICKETWINDOW · MUTANTBROTH · BEARDEDPIGGY · KARMAPOLICE · MEMORYHOLE · MARBLEDGECKO · SOCIALANIMAL · XKEYSCORE · ASDF“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Profiled: From Radio to Porn, British Spies Track Web Users' Online Identities” - The Intercept ↗ (2015-09-25) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Gallagher, Ryan -
Cryptographic Modernization (CryptoMod) Classification Guide 3-9 [pdf]
A partial NSA/CSS classification guide for the Cryptographic Modernisation (CryptoMod) programme — establishing classification levels for information about NSA's transition of US cryptographic products to modern algorithms, Positive Access Control parameters, software signing, and the association of specific algorithms with critical year and life-of-use assessments.
-
"The EDGE" - National Information Assurance Research Laboratory (NIARL) Science, Technology, and Personnel Highlights, 2008 [pdf]
The September 2008 edition of "The EDGE" — the internal newsletter of NSA's National Information Assurance Research Laboratory (NIARL/R2) — covering research highlights including the TUNDRA project investigating a new AES cryptanalysis technique, the TUNDRA Tau statistic for codebook analysis, photonic logic research at Sandia, anti-tamper work, the CLARIFYMIND wireless pilot, FLOWBEE network metadata collection, POPQUIZ/DISTILLERY analytics and FMAC mandatory access controls for OpenSolaris, notable for containing the first published description of the TUNDRA cryptanalysis project against AES.
Programs: DISTILLERY · HAIRBALL · GRAPHVIZ · POPEYESEAR · RANDOMIZERS · TUNDRA · CLOUD · STARFIRE · CARPAT · MAPREDUCE · NUCLEARWINTER · CLARIFYMIND · FLOWBEE · POPQUIZ · BYZANTINEHADES · TREEVIZ · GROUPDIVE · BLUESASH -
What Your Mother Never Told You About SIGDEV Analysis [pdf]
An NSA presentation covering VPN signals development tradecraft and the prototype DARKSUNRISE VPN analytics tool — describing how analysts use DISCOROUTE, BLACKPEARL, TOYGRIPPE, NKB, RONIN and GNETWORK GNOME to map target VPN networks from router configuration data, with live screenshots of DARKSUNRISE's SHADOWNET interface showing IPSec VPN connections associated with Pakistani, Afghan and other targets collected through MUSCULAR (DS-200B).
Programs: TOYGRIPPE · DISCOROUTE · BLACKPEARL · GNETWORKGNOME · NKB · RONIN · XKEYSCORE · TREASUREMAP · RENOIR · ROYALNET · GNOME · ASDF · DARKSUNRISE · SHADOWNET · WEALTHYCLUSTER · MUSCULAR · CASPORT · CUE · BLACKSAND · DANCINGOASIS · BLACKBEACH · POTLUCK · SSO · DNIPRESENTER · TNS · BLACKPEAL · ROADBED · TROPICNET · SILVERZEPHYR · SITESTORE -
OTR encrypted messages can't be decrypted by the NSA [pdf]
Three intercepted chat sessions from 16 March 2012 collected under PRISM, showing a target switching mid-conversation from unencrypted to OTR-encrypted messaging — with NSA able to collect the session metadata and unencrypted portions but unable to decrypt the OTR messages, each annotated "No decrypt available for this OTR encrypted message."
Programs: PRISM