Program: OLYMPIA 6 documents
Search documents matching “OLYMPIA” →Codenames and programs recorded for each document.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
AND THEY SAID TO THE TITANS: « WATCH OUT OLYMPIANS IN THE HOUSE! » [pdf]
This Top Secret CSEC “Olympia” document details a Canadian intelligence program that analyzed and tracked the Brazilian Ministry of Mines and Energy’s telecommunications, mapping IPs, servers, proxies, and mobile devices while automating data collection and network analysis to develop actionable intelligence. It outlines tools, workflows, and contacts used for surveillance, though the presentation does not explain the specific purpose of the operation.
Programs: OLYMPIA · QUOVA · PROMETHEUS · PEITHO · SLINGSHOT · LEVITATE · STRATOS · EVILOLIVE · GCHQ Geofusion · ATLAS · HYPERION · ATHENA · DANAUS · TIDALSURGE · BLACKPEARL · MARINA · STARSEARCH · PEPPERBOX · TRITON · PACKAGEDGOODS · ARK · TOYGRIPPE · FRIARTUCK · MASTERSHAKE · COEUS · STALKER · MAINWAY · FASCIA · SEDB · OCTSKYWARD · FASTBAT · TWINSERPENT · EONBLUE · DISHFIRE · GNDB“Read a CSEC document that was first acquired by Edward Snowden” - The Globe and Mail ↗ (2013-11-30) · “Ministério de Minas e Energia está na mira de espiões americanos e canadenses” - O Globo ↗ (2013-10-06) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Freeze, Colin · Bridi, Sônia · Greenwald, Glenn -
Automated NOC detection [pdf]
This slide deck lays out how GCHQ and Canada’s CSEC systematically identified and penetrated Network Operations Centers—most notably Belgacom—by automating NOC discovery and weaponizing that mapping for QUANTUM INSERT attacks. It reads like a blueprint for turning router configs, metadata, and bulk scans into cookie-based targeting against telecom engineers inside core networks.
Programs: SURGE · NOCTURNALSURGE · RT · NACSHACK · CHAINGUARD · TIDALSURGE · GLOBALSURGE · PENTAHO · OLYMPIA · HYPERION · TERMINALSURGE · HACIENDA · QUANTUMINSERT · MUTANTBROTH · OPSOCIALIST · SAMUEL PEPYS · GEOFUSION · FIVEALIVE · NRTA · RADIUS“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
LEVITATION and the FFU Hypothesis [pdf]
This document describes LEVITATION, a top-secret Canadian Communications Security Establishment (CSE) project that monitors millions of daily file uploads and downloads from free file-sharing sites to identify potential extremist activity. It details the program’s data collection methods, analytical workflow, use of partner databases, and examples of successful discoveries related to terrorist materials and hostage videos.
-
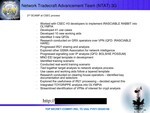
NSA/GCHQ/CSEC Network Tradecraft Advancement Team [pdf]
The "NSA/GCHQ/CSEC Network Tradecraft Advancement Team (NTAT) 2010" document describes a collaborative mission between the US, UK, and Canada to synchronize and advance SIGINT techniques. The NTAT focused on "Network Analysis Tradecraft," specifically integrating analysis tools such as IRASCIABLE RABBIT and TOYGRIPPE into CSEC's OLYMPIA and developing standardized "use cases" for tracking mobile networks and virtual private networks (VPNs).
-
TLS Trends: A roundtable discussion on current usage and future directions [pdf]
A presentation by Canada's Communications Security Establishment describing their TLS trend analysis programme, which systematically tracked SSL/TLS encryption parameters across warranted collection and Special Source access to identify cryptanalytic opportunities, monitor target behaviour and collaborate with GCHQ on exploiting weaknesses in widely-used encryption implementations.
-
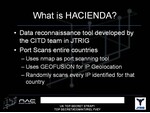
What is HACIENDA? [pdf]
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).