Internet Anonymity 2011
Open PDFDocument date: 2011
Pages: 51
Genre: slides
Banner: TOP SECRET//COMINT REL TO USA, FVEY
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, FVEY
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
My notes
(C//REL) Internet Anonymity 2011
- NSA (S31323)
- [REDACTED]
- [REDACTED]
- [REDACTED] NSTS
TOP SECRET//COMINT REL TO USA, FVEY
1
(C//REL) What is Internet Anonymity?
- (U) Many Possible Meanings/Interpretations
- (S//REL) Simply Not Using Real Name for Email
- (S//REL) Private Forum with Unadvertised Existence
- (S//REL) Unlocatable Endpoint on Internet
- (S//REL) This Talk Concerns Endpoint Location
- (S//REL) The Network Address (IP Address) is Crucial
- (S//REL) It is Not Always Sufficient, However
- (S//REL) Dynamic IP Address
- (S//REL) Mobile Device
TOP SECRET//COMINT REL TO USA,FVEY
2
(C//REL) What is Internet Anonymity?
- (S//REL) Anonymity Is Not Simply Encryption
- (S//REL) Encryption Can Simply Hide Content
- (S//REL) Anonymity Masks the MetaData and hence association with user
- (S//SI//REL) Importance of MetaData to SIGINT post-2001 can not be overstated
- (S//REL) There is also anonymity specifically for publishing information
- (S//REL) Beyond the Scope of this Talk!
- (U) Anonymity is the antithesis of most business transactions (but encryption may be crucial)
- (U) Authentication for monetary exchange
- (U) Marketing wants to know customer well
- (U) The same goes for Taxing Authorities :-)
TOP SECRET//COMINT REL TO USA,FVEY
3
(C//REL) Who Wants Internet Anonymity?
- (U) All Technology is Dual-Use
- (U) Nuclear Weapon to Plug Oil Well
- (U) Homicide by Hammer
- (U) Internet Anonymity for Good
- (U) Anonymous Surveys (Ex: Diseases)
- (U) Human Rights Bloggers
- (U) HUMINT Sources
TOP SECRET//COMINT REL TO USA,FVEY
4
(C//REL) Who Wants Internet Anonymity?
- (U) Internet Anonymity for Bad (Semi to Really)
- (U) Copyright Violators (File Sharing)
- (U) Internet Scam Artists
- (U) Pedophiles
- (C//REL) Foreign Intelligence Agents
- (S//REL) Terrorist Actors (Our Concern)
- (U) Both Cases Use Internet Anonymity Technology (IAT)
TOP SECRET//COMINT REL TO USA,FVEY
5
(S//REL) Internet Censorship: A "Dual"
- (U) Different Scenario
- (U//FOUO) User IP Address known
- (U//FOUO) User Blocked from accessing certain site IP Addresses
- (U//FOUO) Users get around it with Circumvention Technology - Mostly the same as Internet Anonymity Technology (IAT)
TOP SECRET//COMINT REL TO USA,FVEY
6
(C//REL) Types Of IAT
- (S//REL) Single Hop Proxies
- (S//REL) Web Site Proxies
- (S//REL) HTTP/SOCKS Proxies
- (S//REL) Browser Configured to Access
- (S//REL) Proxy Aggregator Sites for Both
- (S//REL) May support SSL/TLS
- (S//REL) HTTP Sites: Only User → Proxy
- (S//REL) SSL Sites (HTTPS)
- (S//REL) Transparent (Just Pass the Bits)
- (S//REL) Man-in-the-Middle (MITM)
TOP SECRET//COMINT REL TO USA, FVEY
7
(C//REL) Types Of IAT: HTTP Proxies/Aggregators
- (S//REL) Web-Site Proxy Aggregator sites
- (S//REL) May list thousands of proxies
- (S//REL) Taxonomy may be country where hosted
- (S//REL) Taxonomy may be ego/business related
- (S//REL) Taxonomy may be proxy software related
- (S//REL) Taxonomy may be provider related
- (S//REL) Proxy Information IS Temporal
- (S//REL) Requires active confirmation
- (S//REL) Requires revisits
- (S//REL) May list thousands of proxies
TOP SECRET//COMINT REL TO USA,FVEY
8
(C//REL) Types Of IAT: HTTP Proxies/Aggregators
- (S//REL) Web Proxy Sites (and Aggregator sites) – Info We Want
- (S//REL) Domain Name (obvious :-) )
- (S//REL) Associated IP address(es)
- (S//REL) Can get live (nslookup, host, dig, etc)
- (S//REL) Can maybe get internally (Foxtrail, NKB, etc.)
- (S//REL) "Exit" IP address (where does user appear?)
- (S//REL) Obtaining manually easy (http://checkip.dyndns.org)
- (S//REL) How to Automate?
- (S//REL) Proxy Discoverer (Originally S31323)
- (S//REL) Other miscellaneous (cookie modification, SSL support, etc.)
TOP SECRET//COMINT REL TO USA,FVEY
9
(C//REL) Types Of IAT: HTTP Proxies/Aggregators
- (S//REL) Web Proxy Aggregator sites Analysis
- (S//REL) Proxy Discoverer
- (S//REL) Scrapes Aggregator (ie www.proxy.org)
- (S//REL) For each proxy, GET www.checkin.dyndns.org
- (S//REL) Iterate over software, variations
- (S//REL) Glype, PHProxy, CGIProxy, ASP.NET, cURLProxy, Surrogafier, Zelune
- (S//REL) Try multiple times
- (S//REL) Aggregator may give software hints
- (S//REL) Failure may indicate site down, or proxy SW modification
- (S//REL) Results from Proxy Discoverer must bridge low->high
- (S//REL) Operationalized by NAC/RONIN with NTOC support (project PONTENTPOTABLES)
- (S//REL) See SDC2011: [REDACTED]
- (S//REL) Proxy Discoverer
TOP SECRET//COMINT REL TO USA, FVEY
10
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Provider may offer multiple servers
- (S//REL) Different Sovereign Nations
- (S//REL) Different Bandwidths
- (S//REL) Most fee based: Can vary on time/number of servers
- (S//REL) May offer multiple VPN protocols
- (S//REL) PPTP (No client software)
- (S//REL) SSH
- (S//REL) OpenVPN
- (S//REL) L2TP/IPSEC
- (S//REL) SSTP
- (S//REL) Communications User ↔ Server Encrypted
- (S//REL) Provider may offer multiple servers
TOP SECRET//COMINT REL TO USA,FVEY
11
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Plethora of providers (I found about 200)
- (S//REL) 12VPN, Ace VPN, Air VPN, AlwaysVPN, Ananoos, AnoCentral, Anonine, Anonyproz, AnonymityNetwork, Anonymizer, Anti-Hadopi, Arethusa, ArtofPing, Astrill, BananaVPN, BeeVPN, BlackLogic, BlackVPN, BolchVPN, BuyProxyService, Change-Mon-IP, Cienen, ClearVPN, ConnectInPrivate, ConnectionVPN, CrackIP, Cryptline, Cryptocloud, CyberGhostVPN, DarknetVPN, DrakkerVPN, DoubleVPN, ExpressVPN, Eztun, FBVPN, FlashVPN, FQVPN, Freedur, FreeVPN, GateVPN, GoldenFrogVyprVPN, GoTrusted, HappyVPN, HideIPVPN, HideMyAss, Hideway, High-Speed-VPN, HostSpotVPN, HotspotShield, IAPSSecurityStore, ibVPN, IdealVPN, InvisibleBrowsing, iOpusiPig, IPJET, Ipredator, ItsHidden, Ivacy, IVPN, Ksecure, KeyVPN, Kryptnet, LamniaVPN, LeVPN, LibertyVPN, LifeVPN, Linkideo, Loki, MadVPN, MetroPipe, MicroVPN, MonkeyVPN, Mullvad, MyOpenGateway, MyVPN, Overplay, oVPN, PacketIX, PC-Streaming, PerfectPrivacy, Privacy.io, Privacy.li, PrivacyTunnel, PrivateInternetAccess, PrivateVPN, PRQtunnel, PublicVPN, PureVPN, Relakks, RemoteVPN, RoadWarriorVPN, RootPanama, RoxNetworks, SaferSurf, SecretsLine, SecureNetics, SecureSwiss, SecureTunnel, SecureVPN, SlickyProxy, SmallVPN, SofanetSofaLINK, SteganosInternetAnonymVPN, StrongVPN, SuperVPN, SurfBouncer, SurfoNym, SurfRescue, SwissPVN, SwitchVPN, TheSafety, Tiggerswelt, tonVPN, Trackbuster, trilightzone, TorrentFreedeom, Tunnelr, TUVPN, UkiVPN, UltraVPN, UnblockVPN, USAIP, VIPAccounts, VIPVPN, VPN4ALL, VPNDeutschland, VPNDog, VPNGates, VPNMaster, VPNonline.ru, VPNPrivacy, VPNProNet, VPNSeek, VPNSteel, VPNSwiss, VPNtraffic, VPNTunnel, vpntunnel.se, VPNSecure, VPNod, VPNout, VPNWorld, VyprVPN, Witopia, WorldVPN, WOWVPN, XeroBank, xtra-vpn, YourFreedom, YourPrivateVPN
- (S//REL) Plethora of providers (I found about 200)
TOP SECRET//COMINT REL TO USA, FVEY
12
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Range of Sovereign Nations/Localities in this set huge!
- (S//REL) Multiple Cities in more popular countries
- (S//REL) Most fee based: Can vary on time/number of servers
- (S//REL) Most notable exception: Hotspot Shield (Provider AnchorFree)
- » (S//REL) Advertising supported
- » (S//REL) Multiple OSINT reports of "most popular"
- (S//REL) About a half dozen others claim they are free
- (S//REL) Most notable exception: Hotspot Shield (Provider AnchorFree)
- (S//REL) Package deals (Europe, any 3 servers, etc.) sometimes available
- (S//REL) Poster child for location selection: IAPS (www.intl-alliance.com)
- (S//REL) AE, AG, AI, AM, AN, AQ, AT, AU, AW, BB, BD, BG, BM, BR, BS, BZ, CA, CH, CL, CN, CO, CR, CU, CY, DK, DO, EE, EG, FJ, GB, GD, GI, GL, GR, GT, HK, HU, ID, IE, IL, IN, IR, IS, JM, JO, JP, KN, KP, KR, KW, KY, LC, LI, LU, MA, MC, MH, MK, MN, MT, MX, MY, NI, NO, NP, NZ, OM, PA, PE, PF, PG, PH, PK, PR, PS, PY, QA, RO, RU, SA, SB, SC, SE, SG, SI, SK, SN, TC, TH, TR, TV, TW, UA, US, UZ, VA, VE, VG, VI, VU, ZA,
- (S//REL) Range of Sovereign Nations/Localities in this set huge!
TOP SECRET//COMINT REL TO USA, FVEY
13
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Search of SIGINT Forensics Lab Holdings for OpenVPN
- (S//REL) Using SNAPE Portal
- (S//REL) OpenVPN specifically because a client is required
- (S//REL) Listing is just name of IAT provider
- (S//REL) HotSpot Shield
- (S//REL) Steganos Anonymous VPN
- (S//REL) Securenetics
- (S//REL) General references to using OpenVPN products
- (S//REL) Several references to IP address only: Need more products in RONIN!
- (S//REL) Search of SIGINT Forensics Lab Holdings for OpenVPN
TOP SECRET//COMINT REL TO USA,FVEY
14
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) What “we” want
- (S//REL) Server enumeration
- (S//SI//REL) SIGINT: Obvious – target using such a service
- » (S//SI//REL) One hop, so enough coverage means success!
- (S//SI//REL) Compliance: FAA – Is target in US is important!
- (S//SI//REL) SIGINT: Obvious – target using such a service
- (S//REL) Exploiting User ↔ VPN traffic
- (S//SI//REL) Very case by case
- » (S//SI//REL) Coverage (may need 2 sided collection)
- » (S//SI//REL) Protocol (may or may not have vulnerabilities)
- » (S//SI//REL) Settings (implementation important)
- » (TS//SI//REL) “Collateral” - NCSC, TAO, FISA, etc.
- » (S//SI//REL) Request sent to CES if important
- (S//SI//REL) Very case by case
- (S//REL) Server enumeration
- (S//REL) What “we” want
TOP SECRET//COMINT REL TO USA, FVEY
15
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Server enumeration
- (S//SI//REL) Manual work with Covered Internet (Linux/Windows)
- » (S//SI//REL) Sometimes info derived from documentation
- » (S//SI//REL) Sometimes need to access service
- » (S//SI//REL) May be a trial version to get "seed"
- » (S//SI//REL) Even if paid may only get some servers
- » (S//SI//REL) Some providers give you the works, YMMV
- » (S//SI//REL) Try to minimize work!
- » (S//SI//REL) Try to extend seed(S//REL)
- » (S//SI//REL) DNS “Pattern”, ex. vpn01.hidegood.net
- » (S//SI//REL) Use scripting/free Linux tools to exhaust space (try nslookup on vpn01.hidegood.net, vpn02.hidegood.net, etc.)
- » (S//SI//REL) Open source DNS enumeration scripts (brief look)
- » (S//REL) Where do results go? (Again, See NAC/RONIN talk)
- (S//SI//REL) Manual work with Covered Internet (Linux/Windows)
- (S//REL) Server enumeration
TOP SECRET//COMINT REL TO USA,FVEY
16
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Server enumeration
- (S//SI//REL) Use the XKEYSCORE, Luke – AKA Fun with X.509
- (S//SI//REL) Prompted by Hotspot Shield (HSS), the free service for which server lists are NOT readily available (Software Reverse Engineering required)
- (S//SI//REL) OpenVPN, as well as SSL/SSTP, send a server x.509 certificate to client as part of setup
- (S//SI//REL) XKEYSCORE sees a LOT of traffic worldwide
- (S//SI//REL) XKEYSCORE fingerprints aren't too hard
- » (S//SI//REL) Need unique string, usually CN and/or DN
- » (S//SI//REL) Check for valid X.509 certificate
- (S//SI//REL) Query safe: Traffic encrypted (still do 1-side defeat)
- (S//SI//REL) Use the XKEYSCORE, Luke – AKA Fun with X.509
- (S//REL) Server enumeration
TOP SECRET//COMINT REL TO USA, FVEY
17
(C//REL) Types Of IAT
- (S//REL) VPN Anonymity Providers
- (S//REL) Server enumeration
- (S//SI//REL) Use the XKEYSCORE, Luke – AKA Fun with X.509
- (S//SI//REL) Prompted by Hotspot Shield (HSS), the free service for which server lists are NOT readily available (Software Reverse Engineering required)
- (S//SI//REL) fingerprint('encryption/hotspot_shield/x509') = $pkcs and $udp and 'metrofreefivpn';
- (S//SI//REL) fingerprint('encryption/easy_hide_ip/x509') = $tcp and from_port(8881) and ('\x06\x09\x2a\x86\x48\x86\xf7\x0d\x01\x01\x01'c) /RSA/ and'www.easy-hide-ip.com';
- (S//SI//REL) fingerprint('encryption/comodo_trustconnect/x509') = $tcp and from_port(443) and ('\x06\x09\x2a\x86\x48\x86\xf7\x0d\x01\x01\x01'c) /RSA/ and 'ComodoVPNS-';
- (S//SI//REL) Use the XKEYSCORE, Luke – AKA Fun with X.509
- (S//REL) Server enumeration
TOP SECRET//COMINT REL TO USA,FVEY
18
(C//REL) Types Of IAT
- (S//REL) Proprietary Multi-Hop Networks (Usually Circumventor Motivated)
- (S//REL) Freegate
- (S//REL) Ultrasurf
- (S//REL) Gpass
- (S//REL) Garden
- (S//REL) Haystack (by Austin Heap – ruled bogus by community)
- (S//REL) Movement to Secure US Government Support to Providers (Congress)
- (S//REL) US Dept of State
- (S//REL) Broadcasting Board of Governors (Independent USG Agency)
- (S//REL) Has instructions for "Getting around Internet Blockage" on Radio Free Asia (RFA) and VOA Persian news sites
TOP SECRET//COMINT REL TO USA, FVEY
20
(C//REL) Types Of IAT
- (S//REL) Anonymous Remailers (Multi-Hop)
- (S//REL) Most Secure
- (S//REL) Main examples: Mixmaster and Mixminion
- (S//REL) Extremely High Latency (Random Delays)
- (S//REL) Only useful for email, other store and forward communications
- (S//REL) Not much use
- (S//REL) NOTE 1: Usability and Anonymity are Foes!
TOP SECRET//COMINT REL TO USA,FVEY
21
(C//REL) Types Of IAT
(S//REL) Miscellaneous IAT Technologies (Single Hop)
- (S//REL) PSIPHON
- (S//REL) Discussed in Censorship Circumvention Circles
- (S//REL) Technology for known associate to setup in appropriate place
- (S//REL) Access via knowing obscure URL and Username/Password w/HTTPS
- (S//REL) Miscellaneous Multi-Selectors
- (S//REL) Some are just "HTTP and/or Socks Proxy Aggregators"
- (S//REL) EasyHideIP.com
- (S//REL) Real-Hide-IP.com
- (S//REL) Found researching this presentation!
- (S//REL) Both of these yield list with HTTP GET!
- (S//REL) Postprocessing: Shell/PERL/etc. script to extract another to check w/Covered Internet (simple proxy option to wget)
- (S//REL) NAC/RONIN will track these
- (S//REL) Some are just "HTTP and/or Socks Proxy Aggregators"
TOP SECRET//COMINT REL TO USA,FVEY
22
(C//REL) Types Of IAT
(S//REL) Miscellaneous IAT Technologies (Single Hop)
- (S//REL) Miscellaneous Multi-Selectors
- (S//REL) Proprietary Proxy Provider/Chooser
- (S//REL) Paid product, Client Software
- (S//REL) Usually involves obfuscation and/or encryption
- (S//REL) GHOSTSURF
- » (S//REL) First analyzed 2006 – uses obfuscaton
- » (S//REL) Server list has changed but all else same
- (S//REL) Easy-Hide-IP
- » (S//REL) Analyzed in 2011 – uses TLS on port 8881
- » (S//REL) Over 400 servers in 7 countries
- (S//REL) Hide-IP
- » (S//REL) Analyzed in 2006 – New product now
- » (S//REL) Need to re-analyze
- (S//REL) Proprietary Proxy Provider/Chooser
TOP SECRET//COMINT REL TO USA,FVEY
23
(C//REL) Types Of IAT
(S//REL) Miscellaneous IAT Technologies (Single Hop)
- (S//REL) Bot-Based Proxy Networks
- (U//FOUO) Kudos to [REDACTED], NGA, for pointing this out in her Intelink-TS blog, Sphinx1121 (Pointer to krebsonsecurity.com)
- (S//REL) Bot owners drop socks proxies on compromised computers
- (S//REL) Said proxies are then rented out to "customers" for anonymity
- (S//REL) OSINT indicates a "product" called XSOX available on underground forums as a C&C for such a network
- (S//REL) General Note for IAT analysts: Details IMPORTANT
- (S//REL) Proof by example: EasyHideIp.com NOT the same as Easy-Hide-IP.com (Of course domains are not case sensitive)
TOP SECRET//COMINT REL TO USA,FVEY
24
(C//REL) Types of IAT
- (S//REL) Open Source Multi-Hop Networks
- (S//REL) Jondo Anonymous Proxy (JAP)
- (S//REL) Championed by German University (Dresden)
- (S//REL) (Mostly?) Open source software – some Docs in German
- (S//REL) Uses a technology known as Cascades
- (S//REL) Each cascade is set of 2 or 3 Mixes
- (S//REL) All internal traffic encrypted
- (S//REL) Free service AN.ON: 5 Cascades
- (S//REL) Premium service JonDoNym: 10 Cascades
- (S//REL) Countries: BG, CA, CH, CZ, DE, DK, FR, GB, IT, LU, US,
- (S//REL) Less than 50 mixes total
TOP SECRET//COMINT REL TO USA,FVEY
25
(C//REL) Types of IAT
- (S//REL) Open Source Multi-Hop Networks
- (S//REL) Jondo Anonymous Proxy (JAP)
- (S//REL) Comparison with Tor
- (S//REL) Not nearly as well studied
- (S//REL) Much smaller contained development community
- (S//REL) More centralized structure (all mixes centrally approved)
- (S//REL) Not as diverse geographically or scalable
- (S//REL) Not as well used or publicized
- (S//REL) Not analyzed in great detail here at NSA (or FVEY?)
- (TS//SI//REL) Much better chance for Global Adversary (SIGINT :-) )
- (TS//SI//REL) Sessionization of DNI still would be a problem
TOP SECRET//COMINT REL TO USA,FVEY
26
(C//REL) Types of IAT
- (S//REL) Open Source Multi-Hop Networks
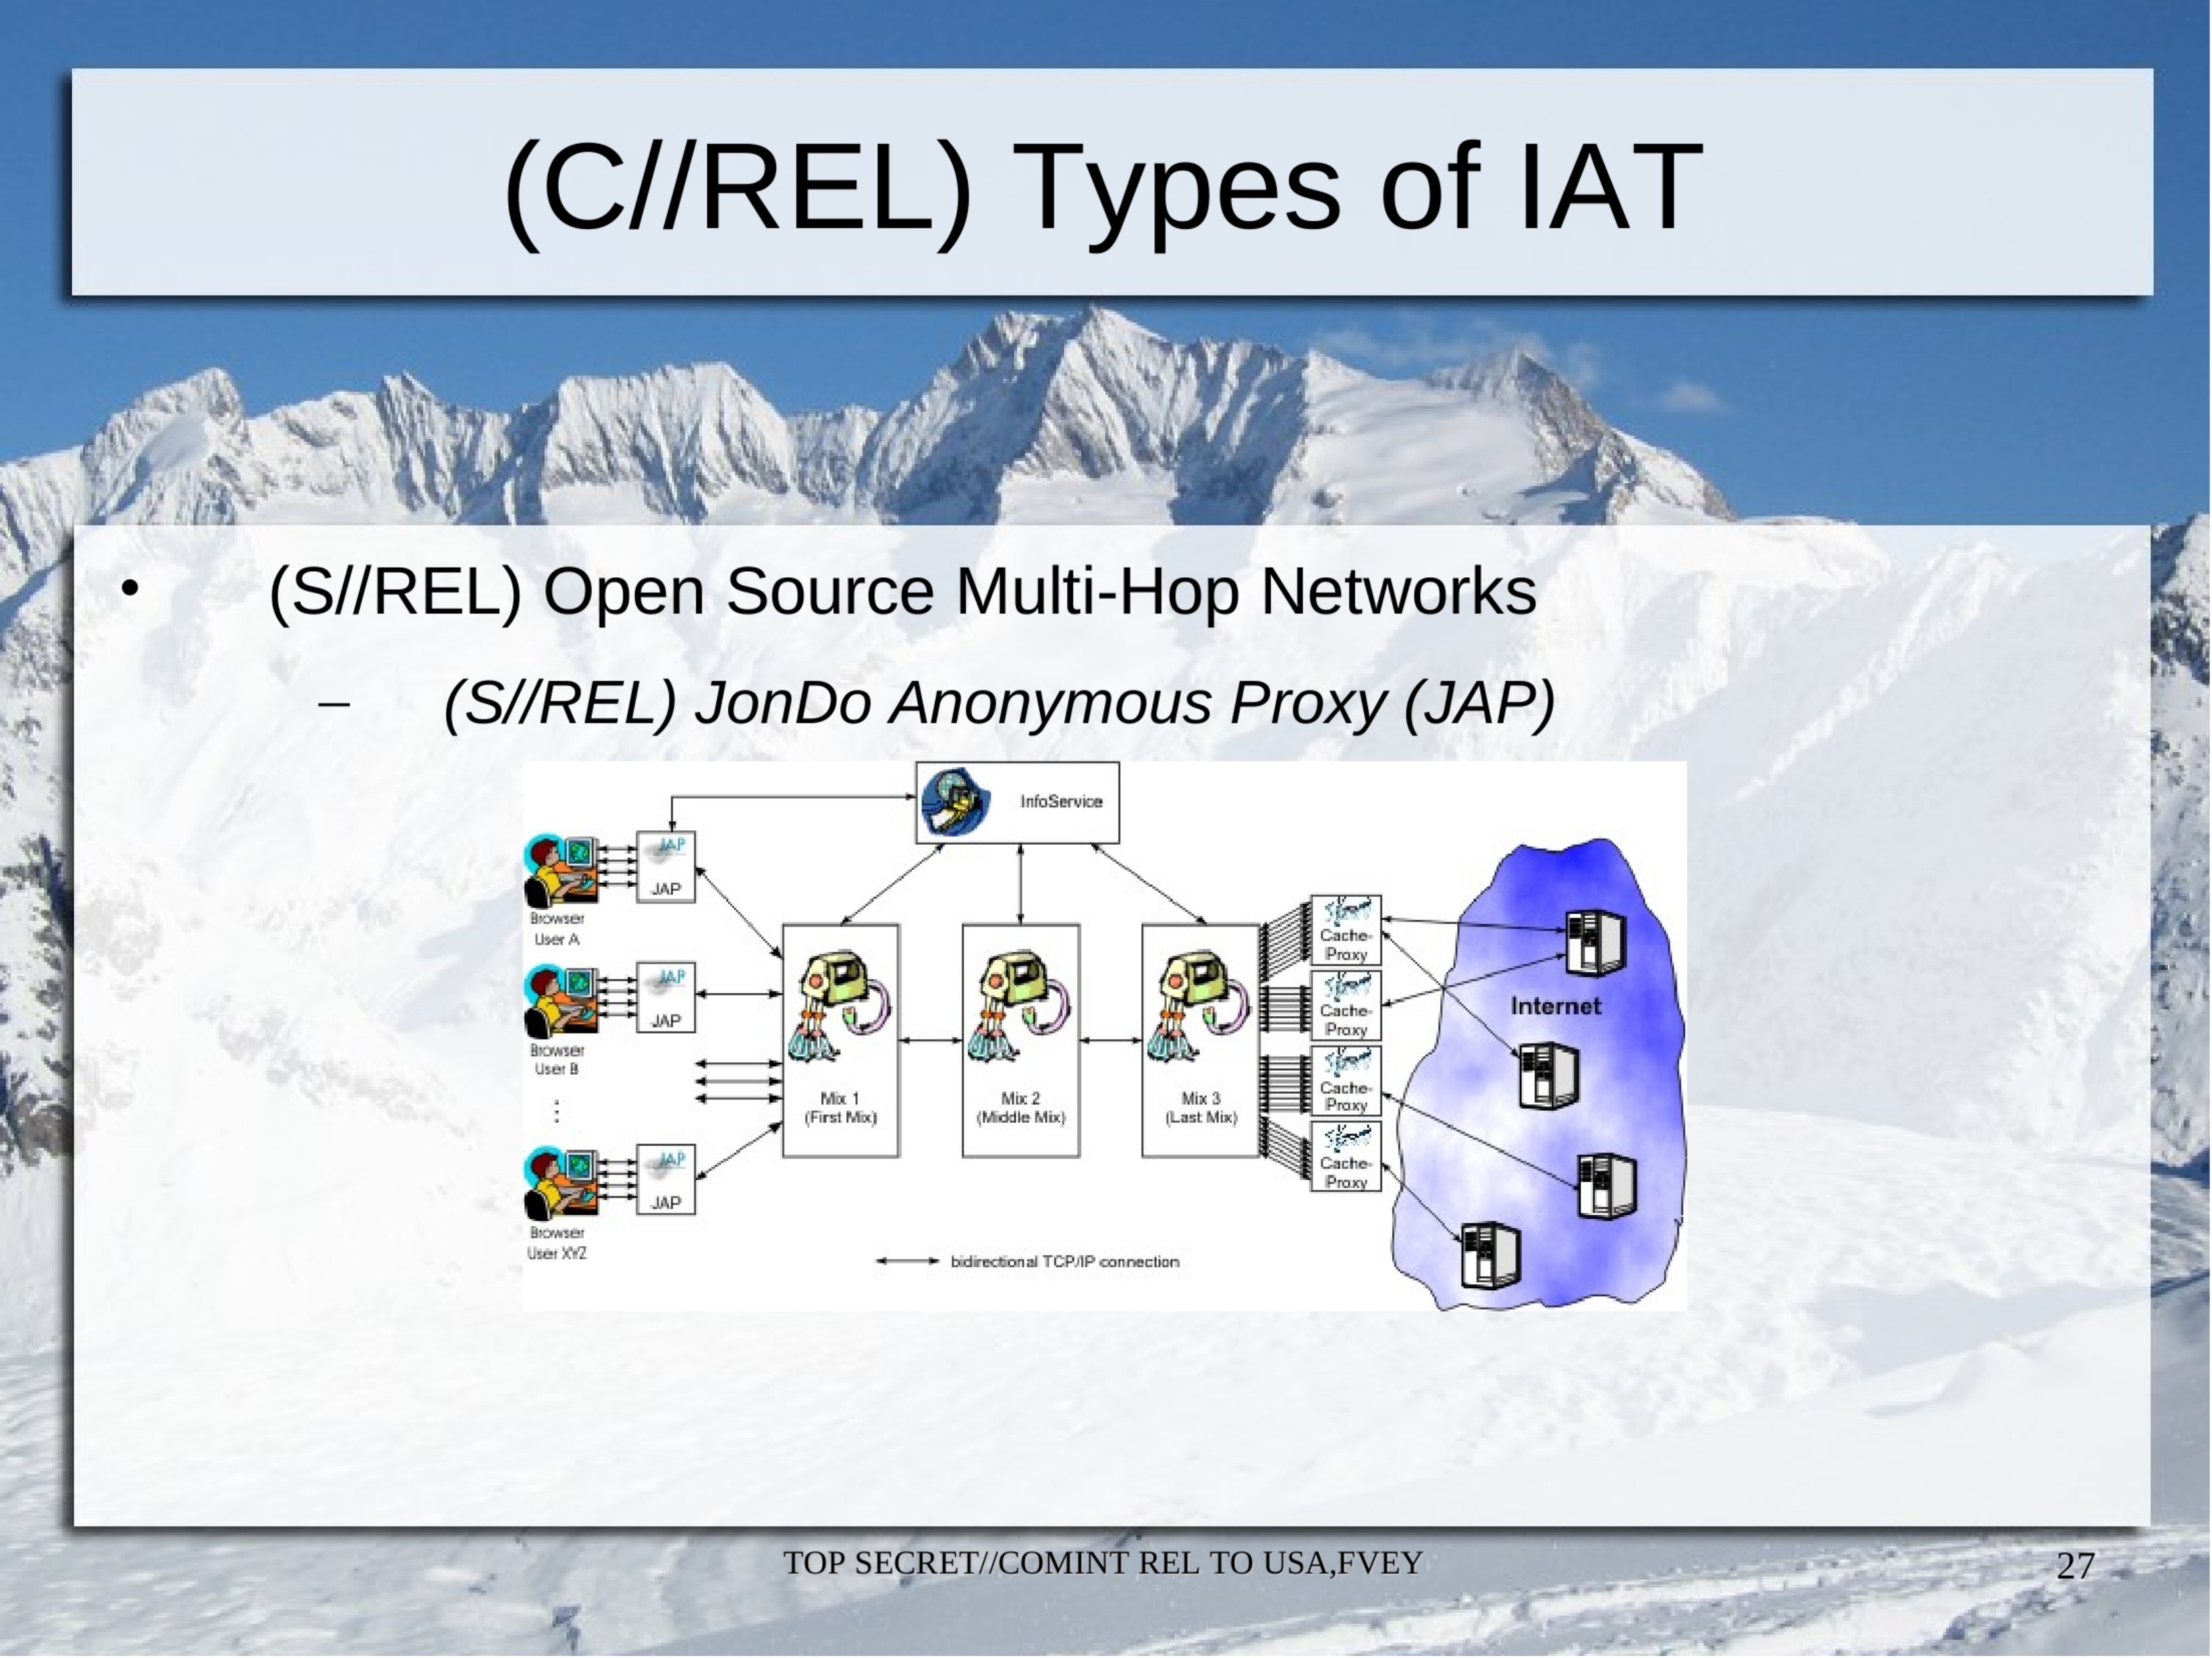
- (S//REL) JonDo Anonymous Proxy (JAP)
Browser User A
JAP

Browser User B
JAP

Browser User XYZ
JAP

InfoService

Mix 1 (First Mix)
Mix 2 (Middle Mix)
Mix 3 (Last Mix)

Cache-Proxy
Cache-Proxy
Cache-Proxy
Cache-Proxy

Internet

bidirectional TCP/IP connection
TOP SECRET//COMINT REL TO USA,FVEY
27
(C//REL) Types of IAT
- (S//REL) Open Source Multi-Hop Networks
- (S//REL) Tor
- (S//REL) Very widely used worldwide
- (S//REL) Open Source
- (S//REL) Active Development
- (S//REL) Mitigates Threats
- (S//REL) Very Secure
- (S//REL) Low enough latency for most TCP uses
- (S//REL) Still the King of high secure, low latency Internet Anonymity
- (S//REL) There are no contenders for the throne in waiting
TOP SECRET//COMINT REL TO USA,FVEY
28
(S//REL) Tor Operation (1)
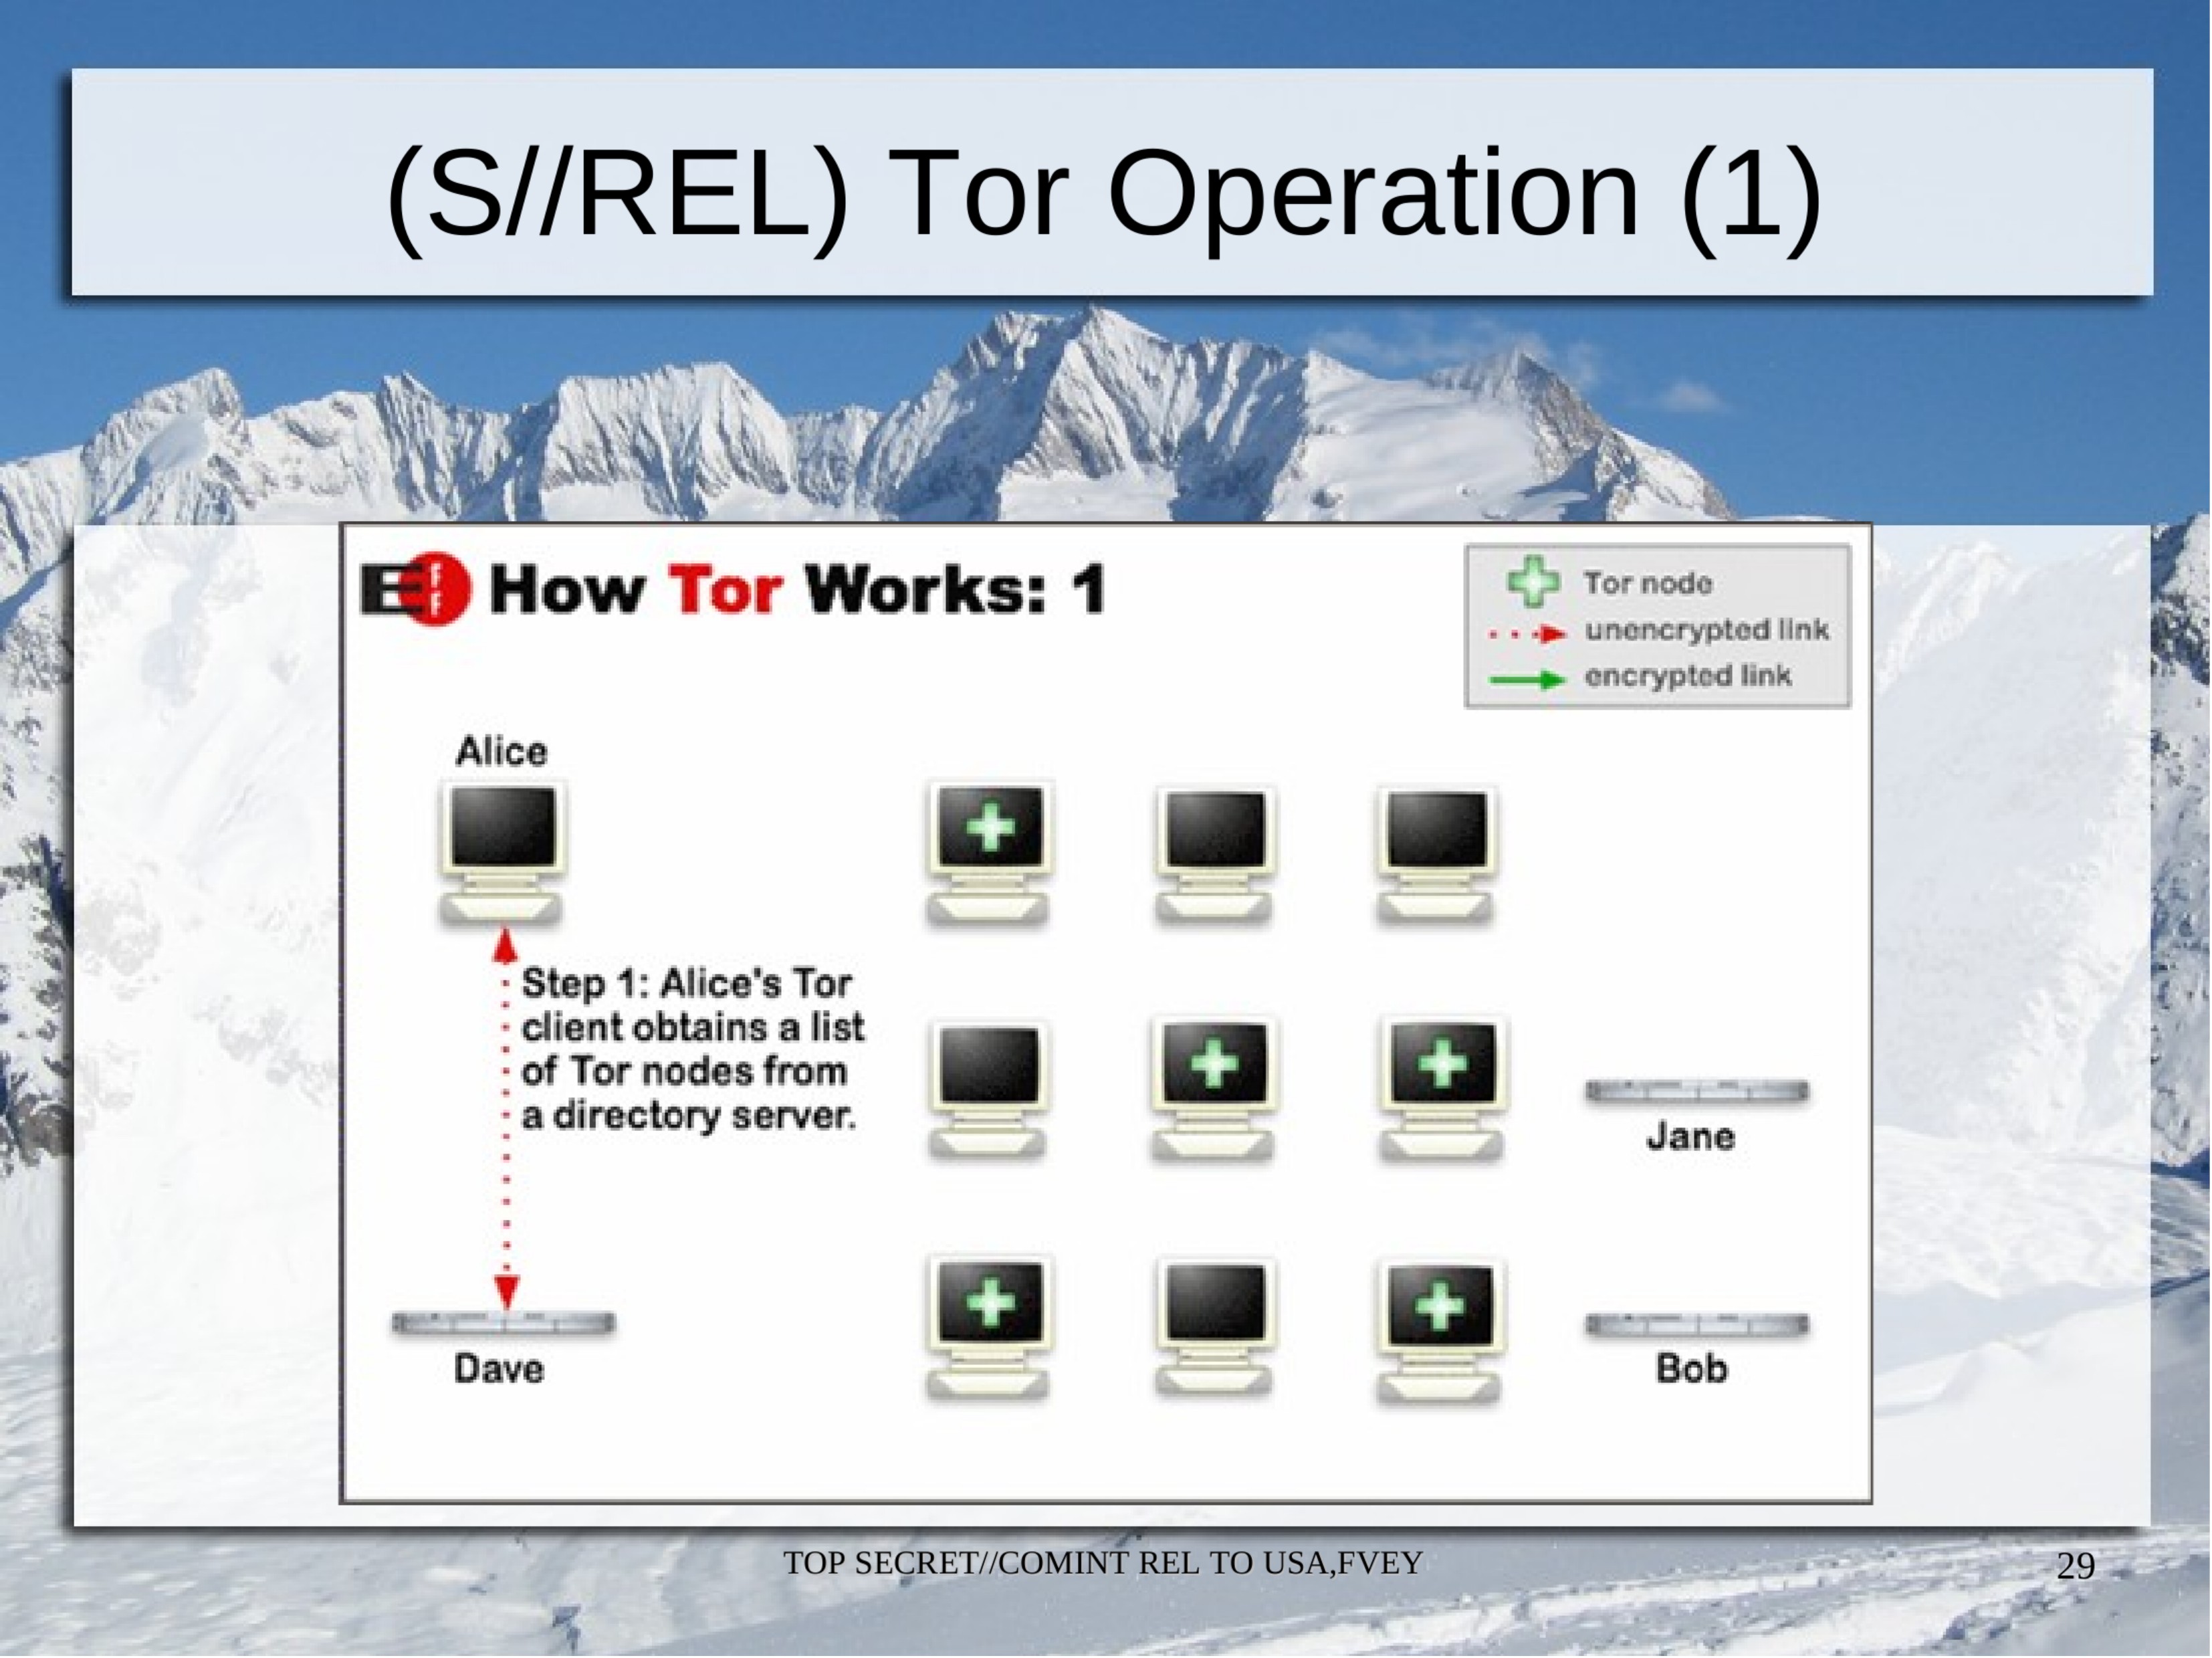
EFF How Tor Works: 1

Alice
Step 1: Alice's Tor client obtains a list of Tor nodes from a directory server.

Dave
Jane
Bob

Tor node
unencrypted link
encrypted link
TOP SECRET//COMINT REL TO USA,FVEY
29
(S//REL) Tor Operation (2)
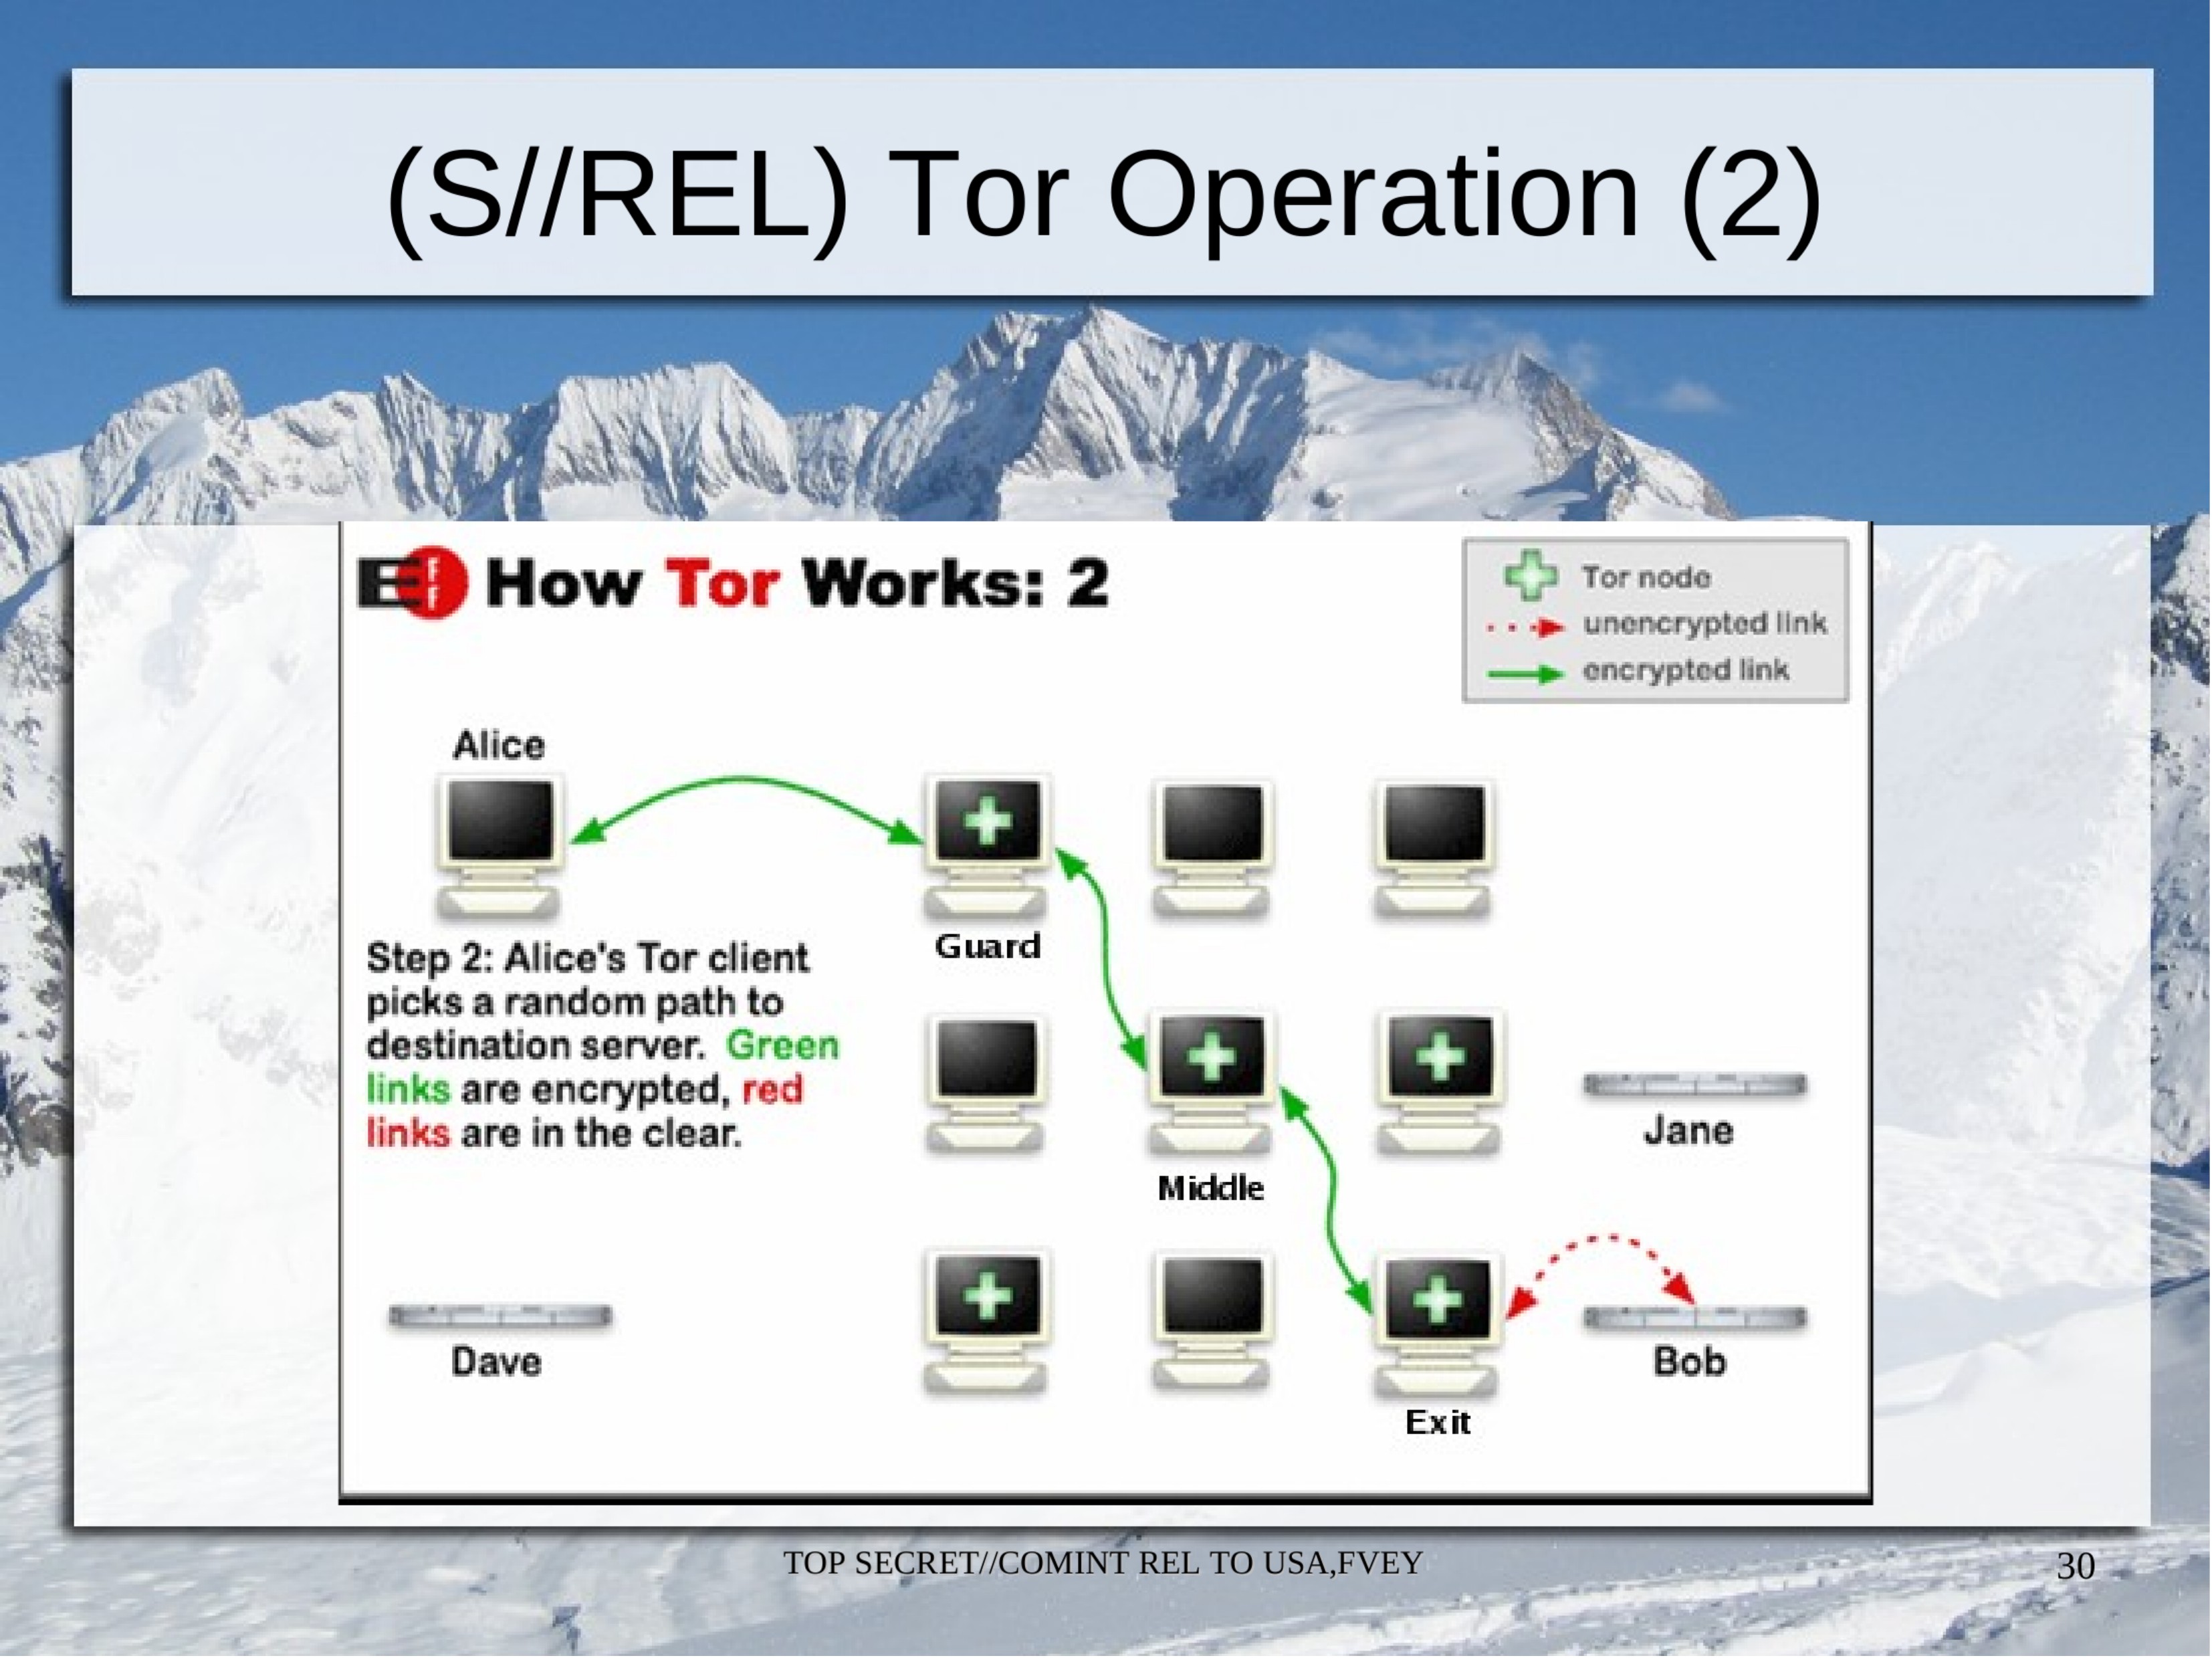
EFF How Tor Works: 2

Alice
Step 2: Alice's Tor client picks a random path to destination server. Green links are encrypted, red links are in the clear.

Dave

Guard
Middle
Exit

Jane
Bob

Tor node
unencrypted link
encrypted link
TOP SECRET//COMINT REL TO USA,FVEY
30
(S//REL) Mom: Where Do Tor Relays Come From?
- (S//REL) Recall there is (well actually more than 1) Tor Directory server?
- (S//REL) This is the pool
- (S//REL) Choices made in terms of advertised capabilities:
- (S//REL) Bandwidth
- (S//REL) Uptime
- (S//REL) Supported Protocols
- (S//REL) Tor client has total final say
TOP SECRET//COMINT REL TO USA,FVEY
31
(S//REL) Mom: Where Do Tor Relays Come From?
- (S//REL) Pool is still currently about 1500
- (S//REL) Many countries represented
- (S//REL) Most in DE
- (S//REL) Second most in US
- (S//REL) Anyone can set one up and register it
- (S//REL) Exit nodes are scary (Kiddie Porn)
- (S//REL) Many countries represented
- (S//REL) How about a private pool? (heh-heh)
- (S//REL) Note 2: Private Resources and Anonymity are foes!
TOP SECRET//COMINT REL TO USA,FVEY
32
(S//REL) Bridges: Special Tor Relays
- (S//REL) Having the set of relays public makes it easy for government censors
- (S//REL) Just block access to all relays from that country
- (S//REL) Tor Project staffed with smart people!
- (S//REL) Introduce new concept: Bridge Nodes
- (S//REL) Unadvertised Entry Nodes distributed "out-of-band"
- (S//REL) Project will hand out three at a time (weekly)
- (S//REL) Email or surf bridges.torproject.org
- (S//SI//REL) SIGINT: Use Tor Against Itself! (Bridge requests from exit nodes)
- (S//REL) Circa April 2011: Tor Project claims around 600 Bridges
- (S//REL) Introduce new concept: Bridge Nodes
TOP SECRET//COMINT REL TO USA,FVEY
33
(S//SI//REL) Tor and NSA Targets
- (TS//SI//REL) Sophisticated CT Targets use TOR to access Terrorist Web Forums
- (TS//SI//REL) Web Forums: al-Faloja, CEMF, al-Hisbah, shumukh, TRSC
- (TS//SI//REL) Persona: DLW, Song of Terror, Time of Terror
- (TS//SI//REL) Visible exit traffic allows for "All except the Client IP" SIGDEV
- (TS//SI//REL) Solving (attempting to solve :-( ) this IP address problem was the work of NSA PARTNERSNIPPET team
- (S//SI//REL) Also 80+ CT email selectors who have used Tor
TOP SECRET//COMINT REL TO USA,FVEY
34
(S//SI//REL) Passive Traffic Analysis
- (S//SI//REL) For Normal SIGINT flow, need to identify Tor traffic!
- (S//SI//REL) Only outer TLS layer visible → How to Distinguish?
- (S//SI//REL) Tor developers attempt to remain anonymous by blending in with myriad other TLS traffic
- (S//SI//REL) Tor TLS has changed over the years
- (S//SI//REL) There ARE some server → client features which are recognizable NOW
TOP SECRET//COMINT REL TO USA,FVEY
35
(S//SI//REL) Passive Traffic Analysis (2)
- (S//SI//REL) Tor TLS (server → client) startup features
- (S//SI//REL) Certificate: Specific Diffie-Hellman (DH) Modulus (just string match)
- (S//SI//REL) Certificate: Issuer and Subject random names of same form – ex: CN=www.ofzgkdjxvjrss.net (regex match)
- (S//SI//REL) Certificate: Always 2-hour lifetime (ASN.1 format → more intensive computation)
- (S//SI//REL) Several XKS fingerprints and a plugin implemented
TOP SECRET//COMINT REL TO USA,FVEY
36
(S//REL) Tor Project Recent Activity
- (S//REL) Driven by Censorship Circumvention, Hide Signature
- (S//REL) New bridge nodes blocked in China
- (S//REL) Researching better bridge distribution strategies
- (S//REL) Claim by Tor Project is 8000 requests/day for <1000 total
- (S//REL) Around Feb 2011, changed the TLS handshake
- (S//REL) Signature more like Apache web-server
- (S//REL) Different DH Modulus
- (S//SI//REL) New XKS Signatures address this
- (S//REL) Signature more like Apache web-server
- (TS//SI//REL) Proposed eventual change will kill identification!
- (S//REL) Each Tor node will generate randomish signatures in a volatile way specifically designed to look like normal website TLS traffic!
TOP SECRET//COMINT REL TO USA,FVEY
37
(S//REL) Tor Project Recent Activity
- (S//REL) Tor on non-traditional platforms
- (S//REL) ORBOT, Tor for Android smartphones
- (S//REL) Tor Router Project
- (S//REL) Modified Linksys Router – everything over Tor
- (S//REL) Hide-My-IP-Address
- (S//REL) Proprietary replacement for Tor Browser Bundle
- (S//REL) From "WCCL Network" not part of Tor Project
- (S//SI//REL) Looked at based on reference by CT target
- (S//REL) Tor Project working on better strategies to distribute bridges
- (S//REL) Tails: Complete Bootable OS on CD for anonymity
- (S//REL) Tor is a crucial component
TOP SECRET//COMINT REL TO USA,FVEY
38
(S//REL) Tor Hidden Service URLs
- (S//REL) Tor Hidden Services (HS) for anonymous publishing
- (S//REL) Not real reliable, but Tor Project research continues
- (U//FOUO) I said outside scope, sorry
- (S//REL) Tor HS accessed via Tor only by http://xxxxxx.onion
- (S//REL) There is the tor2web.com site which is a HTTP to Tor proxy
- (S//REL) Loses some anonymity but easy to use
- (S//REL) Good tool for Covered Internet research
- (S//REL) Site on WikiInfo to document Tor HS URLs
- (S//REL) "The Onion Realm" - [REDACTED]
- (U//FOUO) Kudos to CES/CTSO (S314) for populating this
TOP SECRET//COMINT REL TO USA,FVEY
39
(S//REL) Public IAT Resources Inside
- (U//FOUO) General IAT
- (S//REL) [REDACTED]
- (S//REL) Tor
- (S//REL) [REDACTED]
- (S//REL) [REDACTED]
TOP SECRET//COMINT REL TO USA,FVEY
40
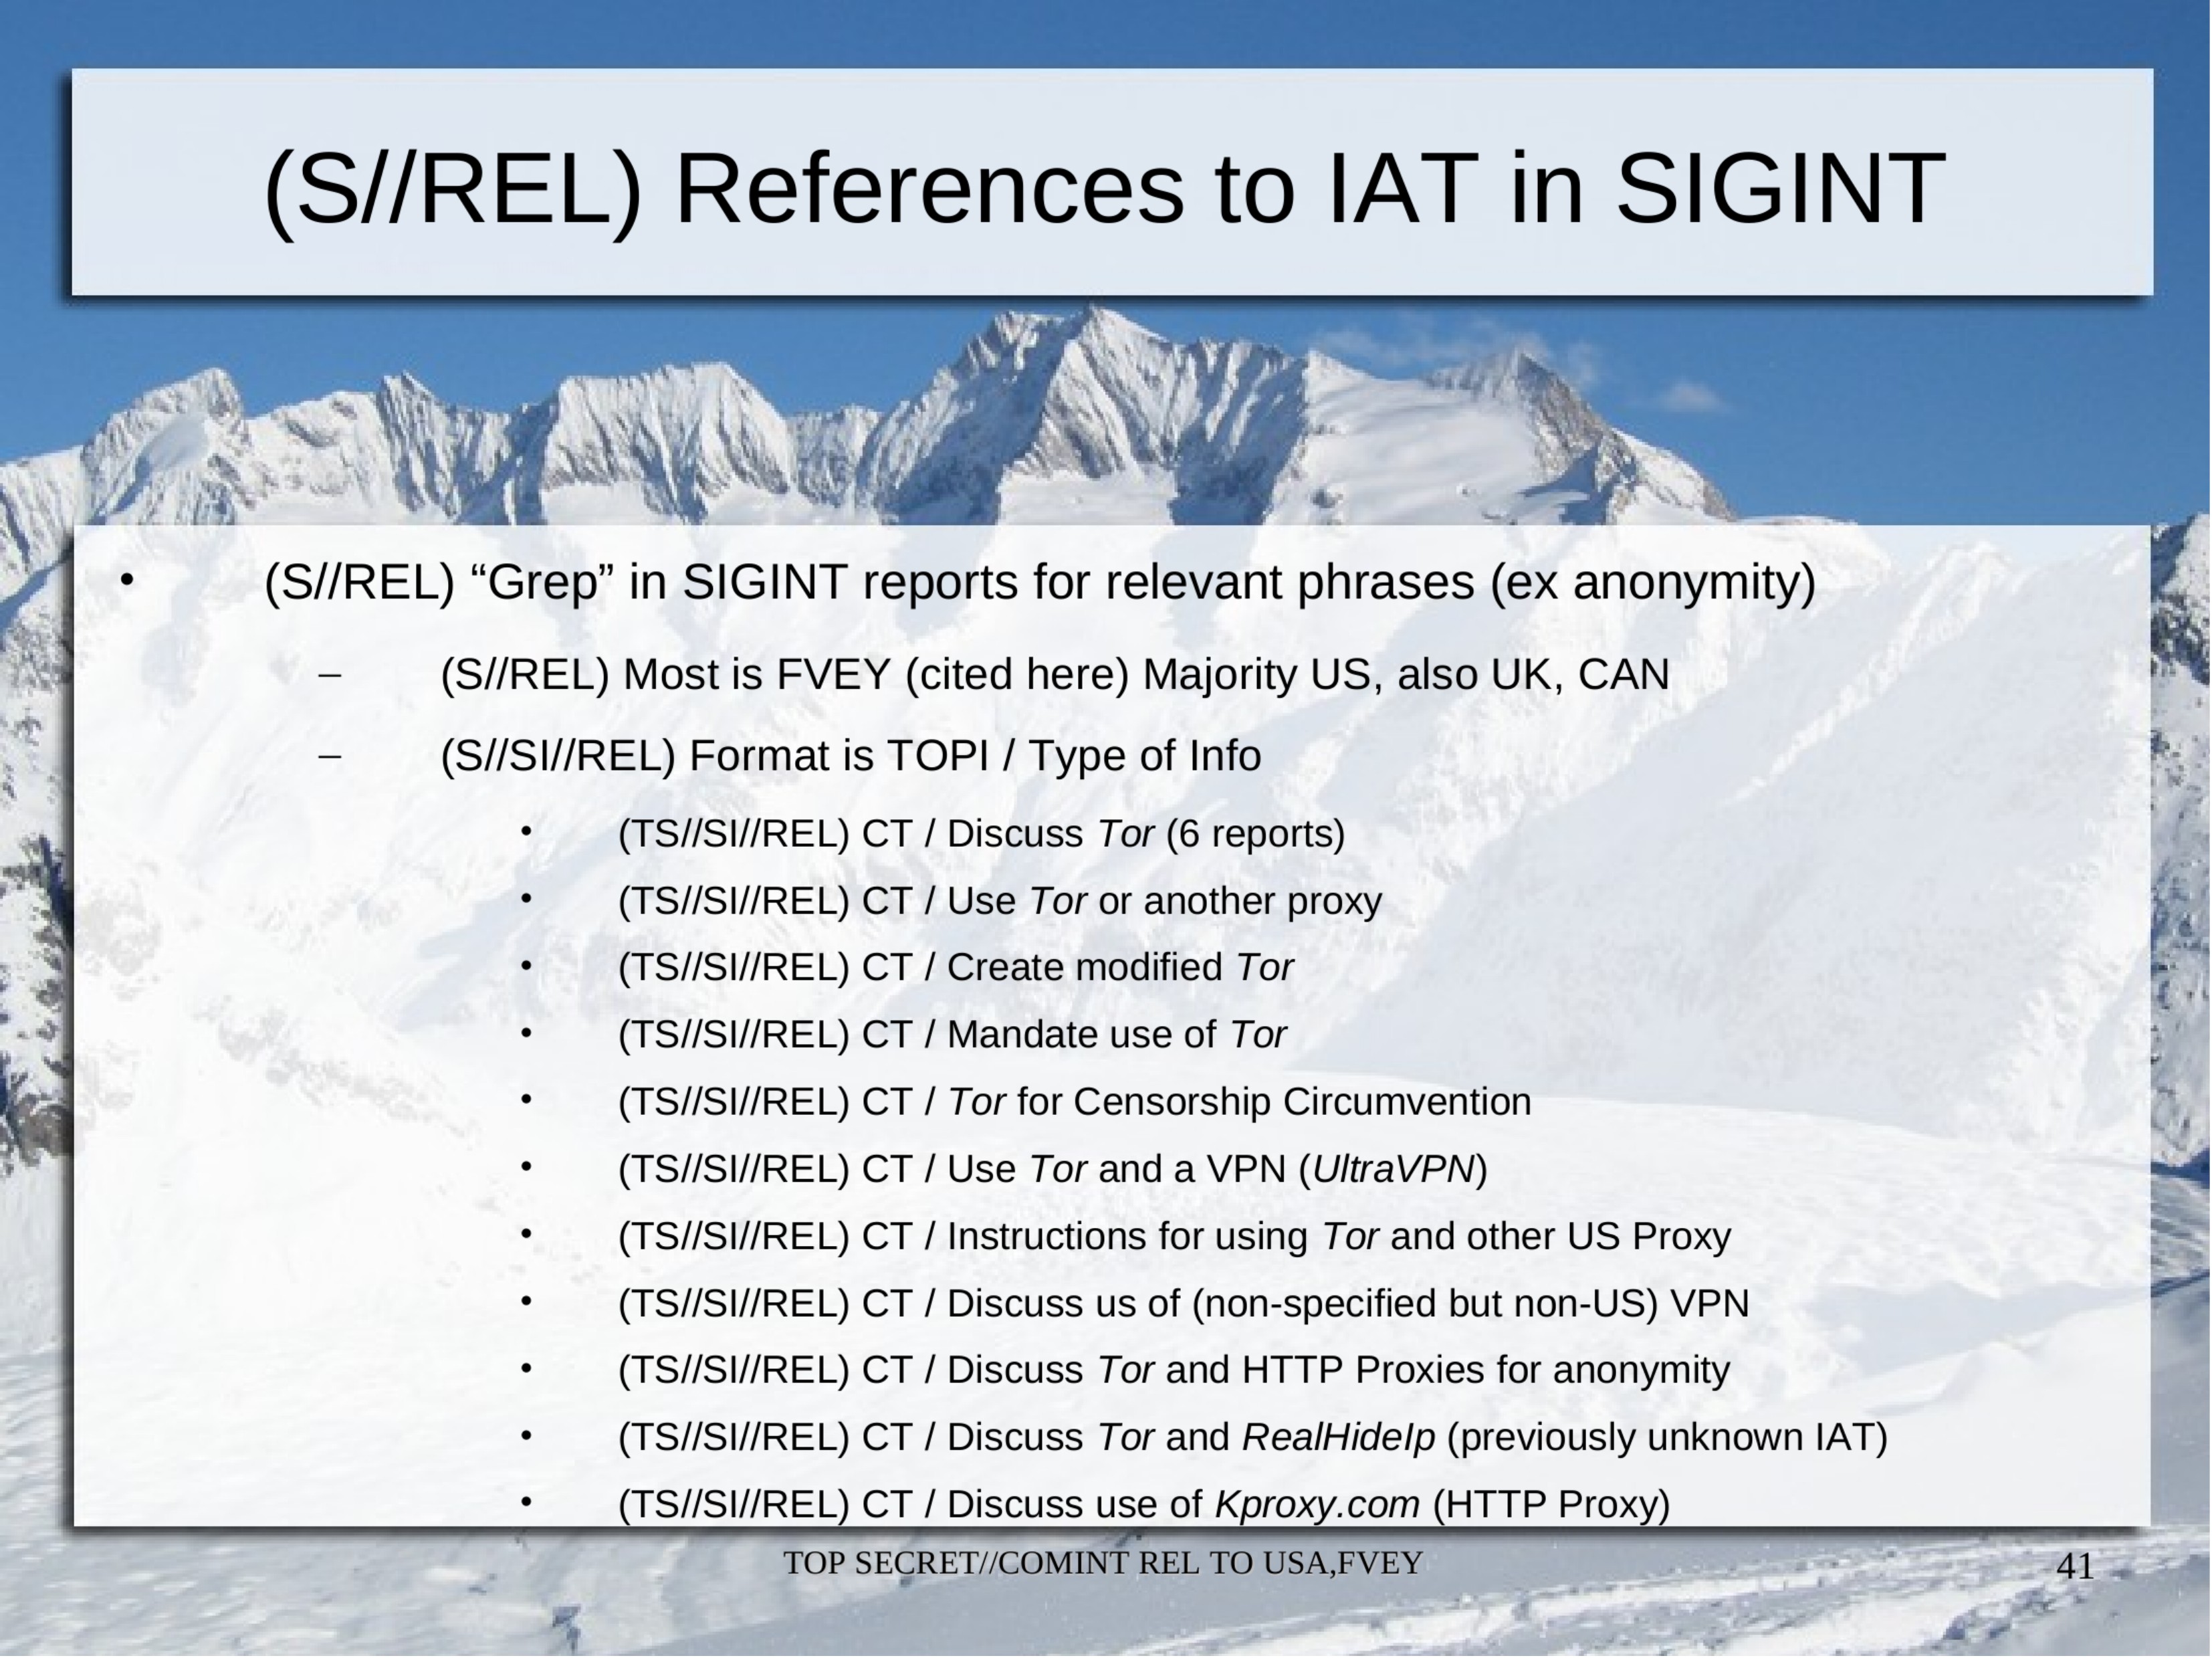
(S//REL) References to IAT in SIGINT
- (S//REL) “Grep” in SIGINT reports for relevant phrases (ex anonymity)
- (S//REL) Most is FVEY (cited here) Majority US, also UK, CAN
- (S//SI//REL) Format is TOPI / Type of Info
- (TS//SI//REL) CT / Discuss Tor (6 reports)
- (TS//SI//REL) CT / Use Tor or another proxy
- (TS//SI//REL) CT / Create modified Tor
- (TS//SI//REL) CT / Mandate use of Tor
- (TS//SI//REL) CT / Tor for Censorship Circumvention
- (TS//SI//REL) CT / Use Tor and a VPN (UltraVPN)
- (TS//SI//REL) CT / Instructions for using Tor and other US Proxy
- (TS//SI//REL) CT / Discuss us of (non-specified but non-US) VPN
- (TS//SI//REL) CT / Discuss Tor and HTTP Proxies for anonymity
- (TS//SI//REL) CT / Discuss Tor and RealHideIp (previously unknown IAT)
- (TS//SI//REL) CT / Discuss use of Kproxy.com (HTTP Proxy)
TOP SECRET//COMINT REL TO USA,FVEY
41
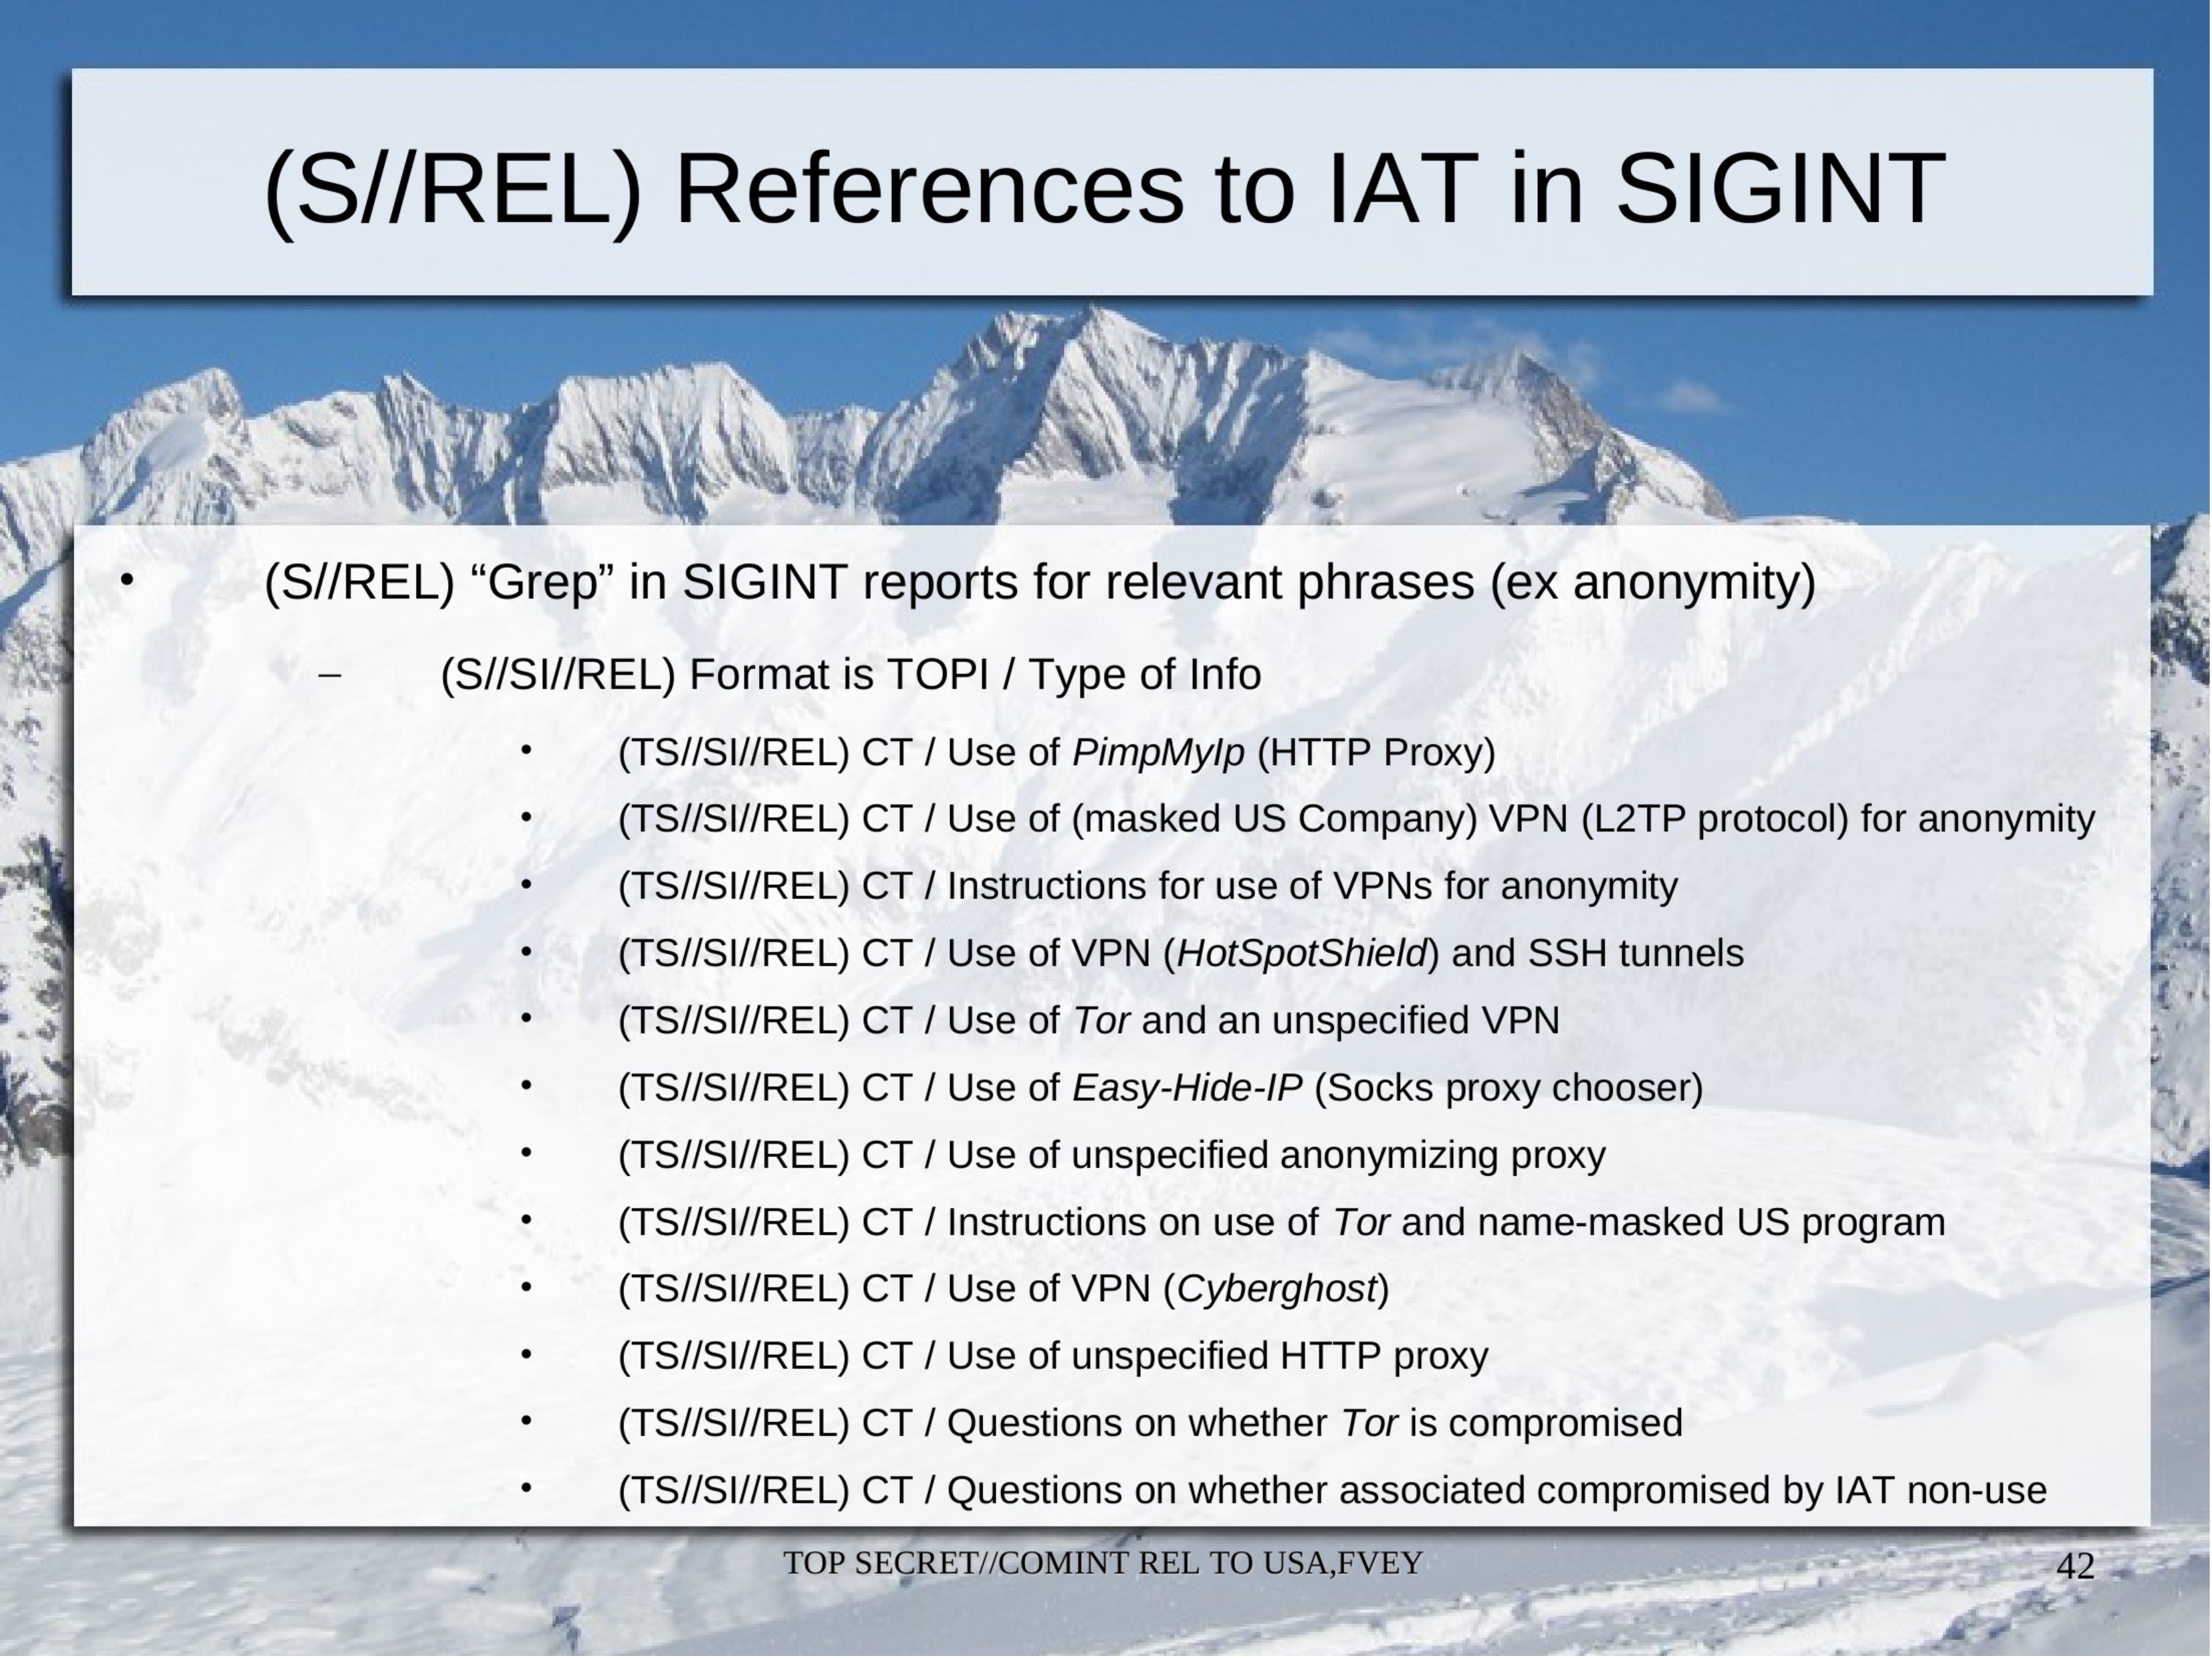
(S//REL) References to IAT in SIGINT
- (S//REL) “Grep” in SIGINT reports for relevant phrases (ex anonymity)
- (S//SI//REL) Format is TOPI / Type of Info
- (TS//SI//REL) CT / Use of PimpMyIp (HTTP Proxy)
- (TS//SI//REL) CT / Use of (masked US Company) VPN (L2TP protocol) for anonymity
- (TS//SI//REL) CT / Instructions for use of VPNs for anonymity
- (TS//SI//REL) CT / Use of VPN (HotSpotShield) and SSH tunnels
- (TS//SI//REL) CT / Use of Tor and an unspecified VPN
- (TS//SI//REL) CT / Use of Easy-Hide-IP (Socks proxy chooser)
- (TS//SI//REL) CT / Use of unspecified anonymizing proxy
- (TS//SI//REL) CT / Instructions on use of Tor and name-masked US program
- (TS//SI//REL) CT / Use of VPN (Cyberghost)
- (TS//SI//REL) CT / Use of unspecified HTTP proxy
- (TS//SI//REL) CT / Questions on whether Tor is compromised
- (TS//SI//REL) CT / Questions on whether associated compromised by IAT non-use
- (S//SI//REL) Format is TOPI / Type of Info
TOP SECRET//COMINT REL TO USA,FVEY
42
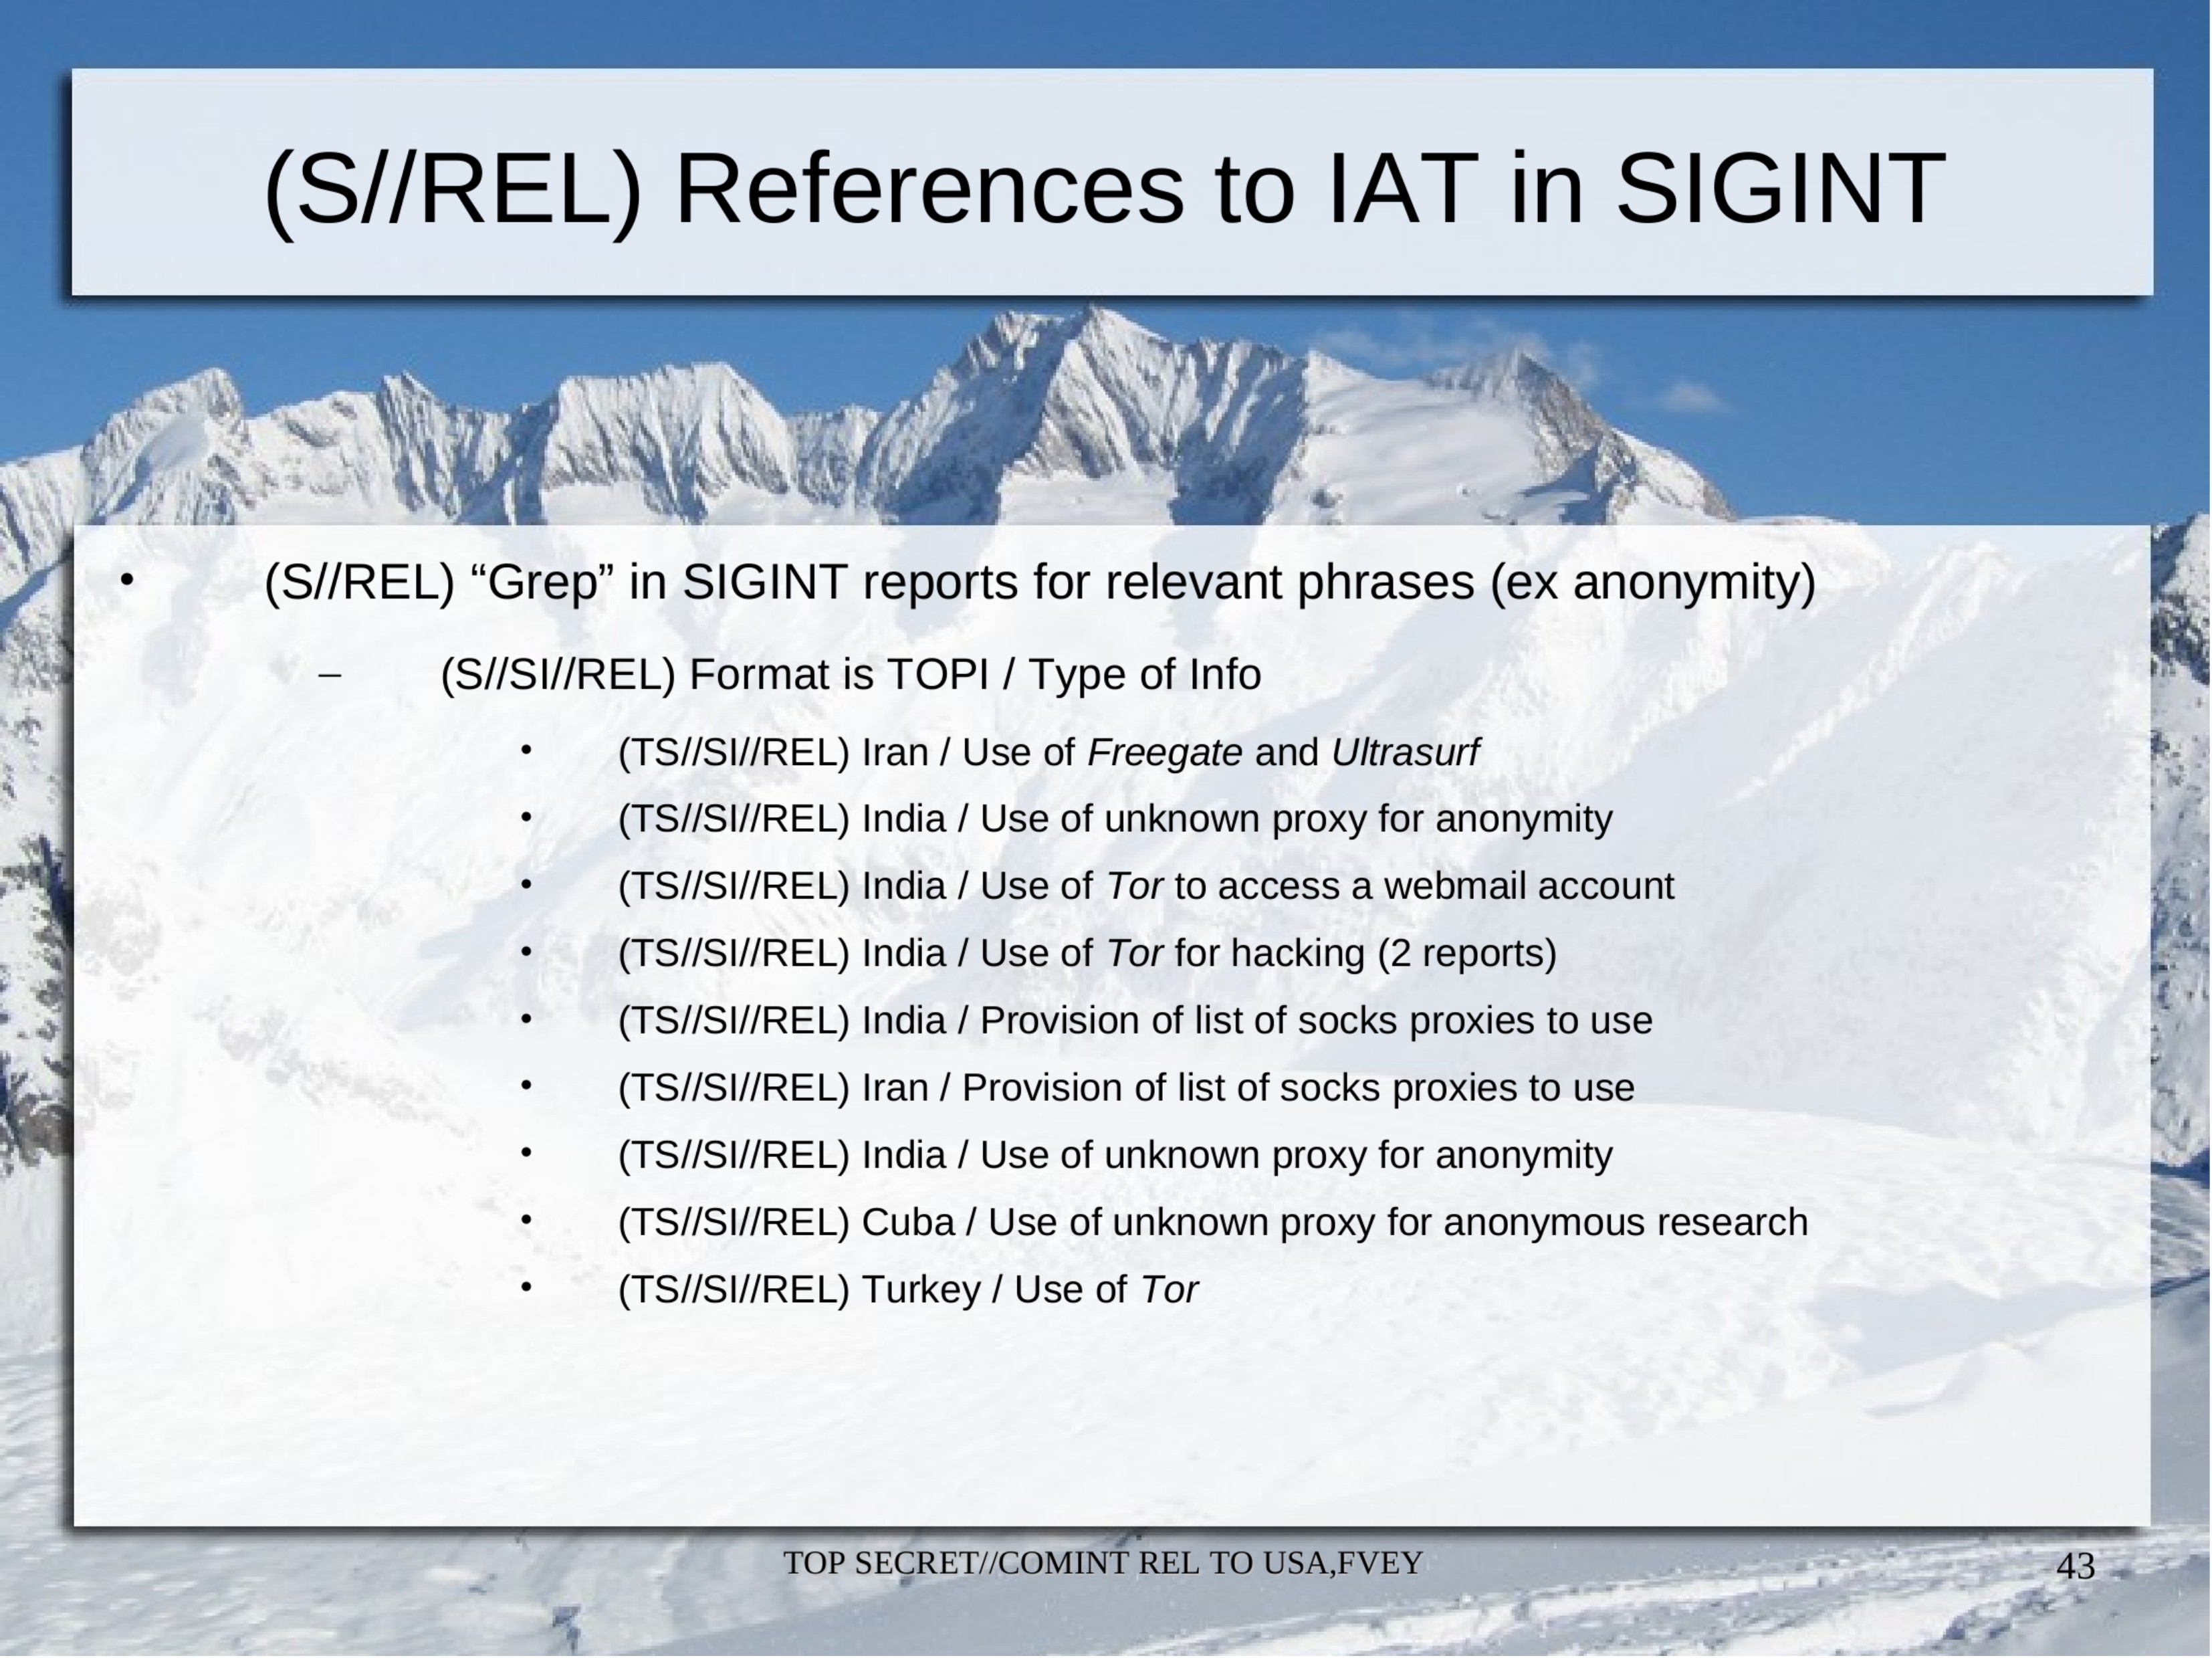
(S//REL) References to IAT in SIGINT
- (S//REL) “Grep” in SIGINT reports for relevant phrases (ex anonymity)
- (S//SI//REL) Format is TOPI / Type of Info
- (TS//SI//REL) Iran / Use of Freegate and Ultrasurf
- (TS//SI//REL) India / Use of unknown proxy for anonymity
- (TS//SI//REL) India / Use of Tor to access a webmail account
- (TS//SI//REL) India / Use of Tor for hacking (2 reports)
- (TS//SI//REL) India / Provision of list of socks proxies to use
- (TS//SI//REL) Iran / Provision of list of socks proxies to use
- (TS//SI//REL) India / Use of unknown proxy for anonymity
- (TS//SI//REL) Cuba / Use of unknown proxy for anonymous research
- (TS//SI//REL) Turkey / Use of Tor
- (S//SI//REL) Format is TOPI / Type of Info
TOP SECRET//COMINT REL TO USA,FVEY
43
(U) Backup Slides
- (S//REL) From Last years SDC Tor Talk
TOP SECRET//COMINT REL TO USA,FVEY
44
(S//REL) Tor (The onion router)
- (S//REL) Development originally NRL funded
- (S//REL) Original developers from Anonymous Remailer Research Community
- (S//REL) Project now a US non-profit (www.torproject.org)
- (S//REL) User to Internet site interaction uses 3 hops through Tor "Relays"
- (S//REL) Entry
- (S//REL) Middle
- (S//REL) Exit
TOP SECRET//COMINT REL TO USA,FVEY
45
(S//REL) Tor Security
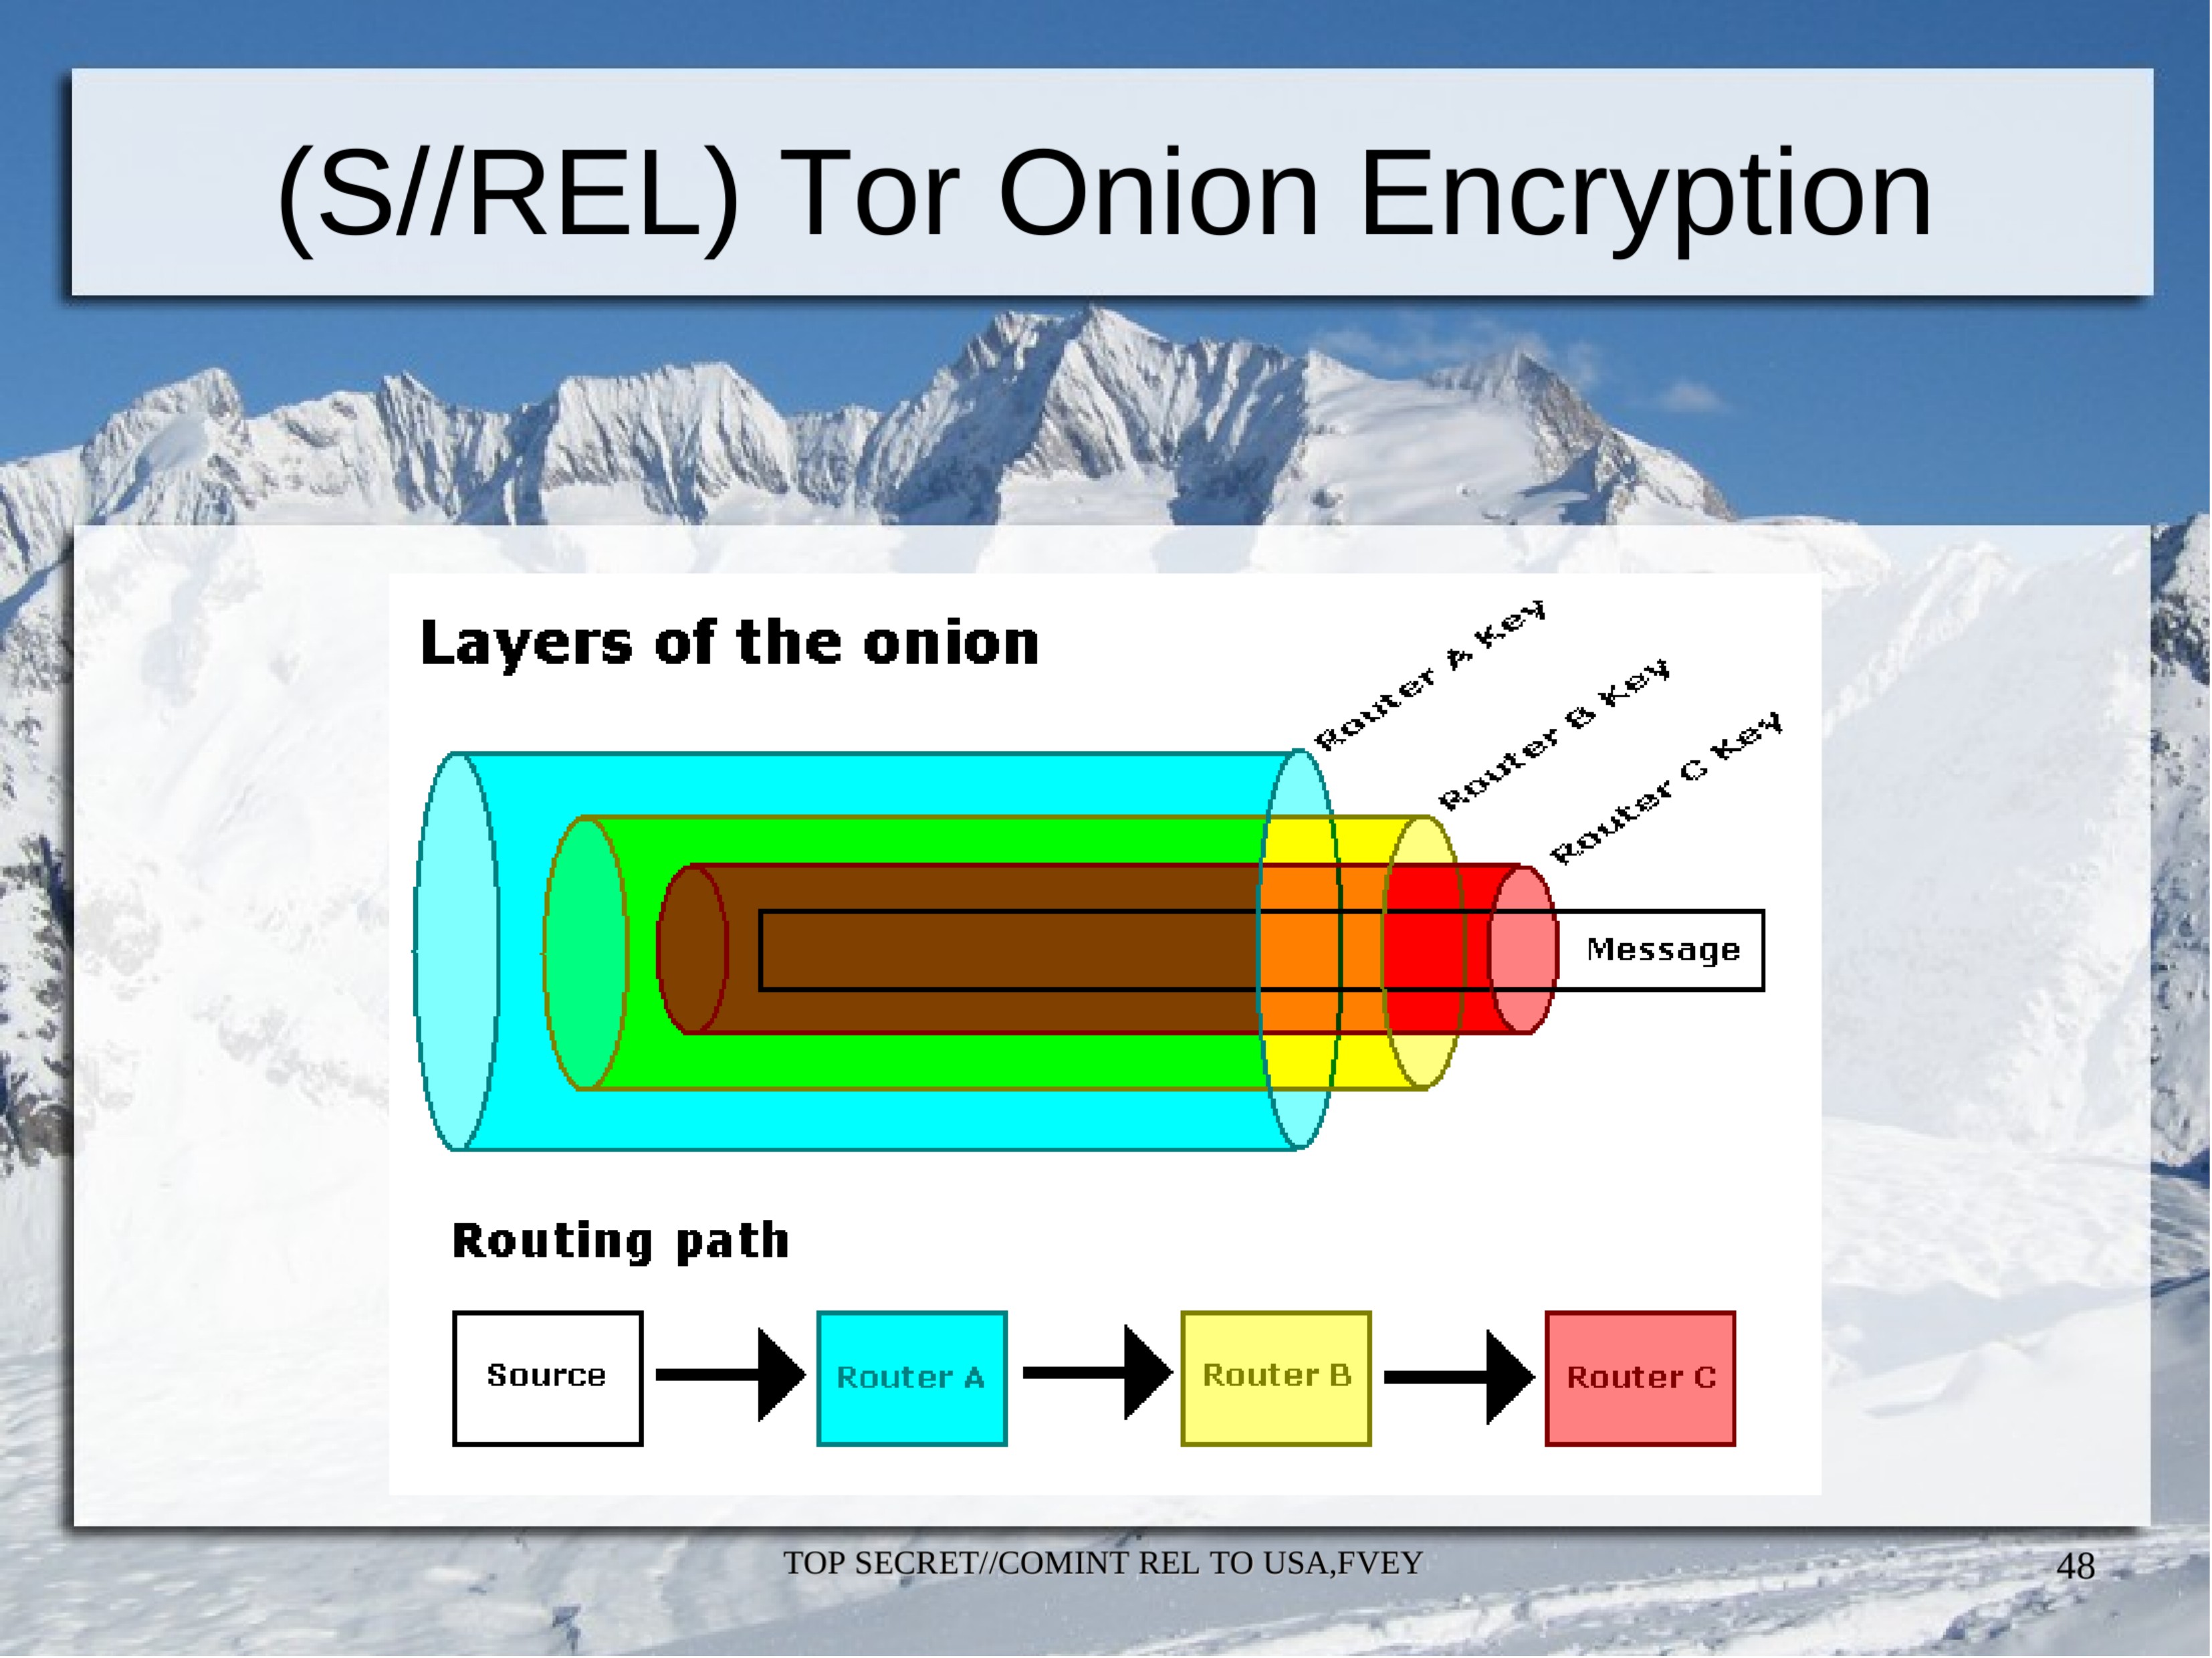
- (S//SI//REL) As you can see from the diagram, everything except for final hop is encrypted.
- (S//SI//REL) The final hop may be also in the case of Bob being an SSL site.
- (S//SI//REL) Two-layer TOR encryption: Pipe between any 2 nodes TLS encrypted (Only thing seen externally).
- (S//SI//REL) Inside the TLS is the Onion Routing (see following diagram):
TOP SECRET//COMINT REL TO USA,FVEY
46
(S//REL) Tor Security (2)
- (S//SI//REL) So each node can only decrypt data between its predecessor and itself and only knows about its predecessor and successor.
- (S//SI//REL) The exit node can read the final traffic if it is not SSL.
- (S//SI//REL) The user Tor client is in control of everything
- (S//SI//REL) Setting up keys for cryptography
- (S//SI//REL) Choosing the Entry, Middle, and Exit
- (TS//SI//REL) Tor is very good – No passive exploitation :-(
TOP SECRET//COMINT REL TO USA,FVEY
47
(S//REL) Tor Onion Encryption
Layers of the onion

Router A Key
Router B Key
Router C Key
Message

Routing path
Source -> Router A -> Router B -> Router C
TOP SECRET//COMINT REL TO USA,FVEY
48
(S//SI//REL) Passive Traffic Analysis (3)
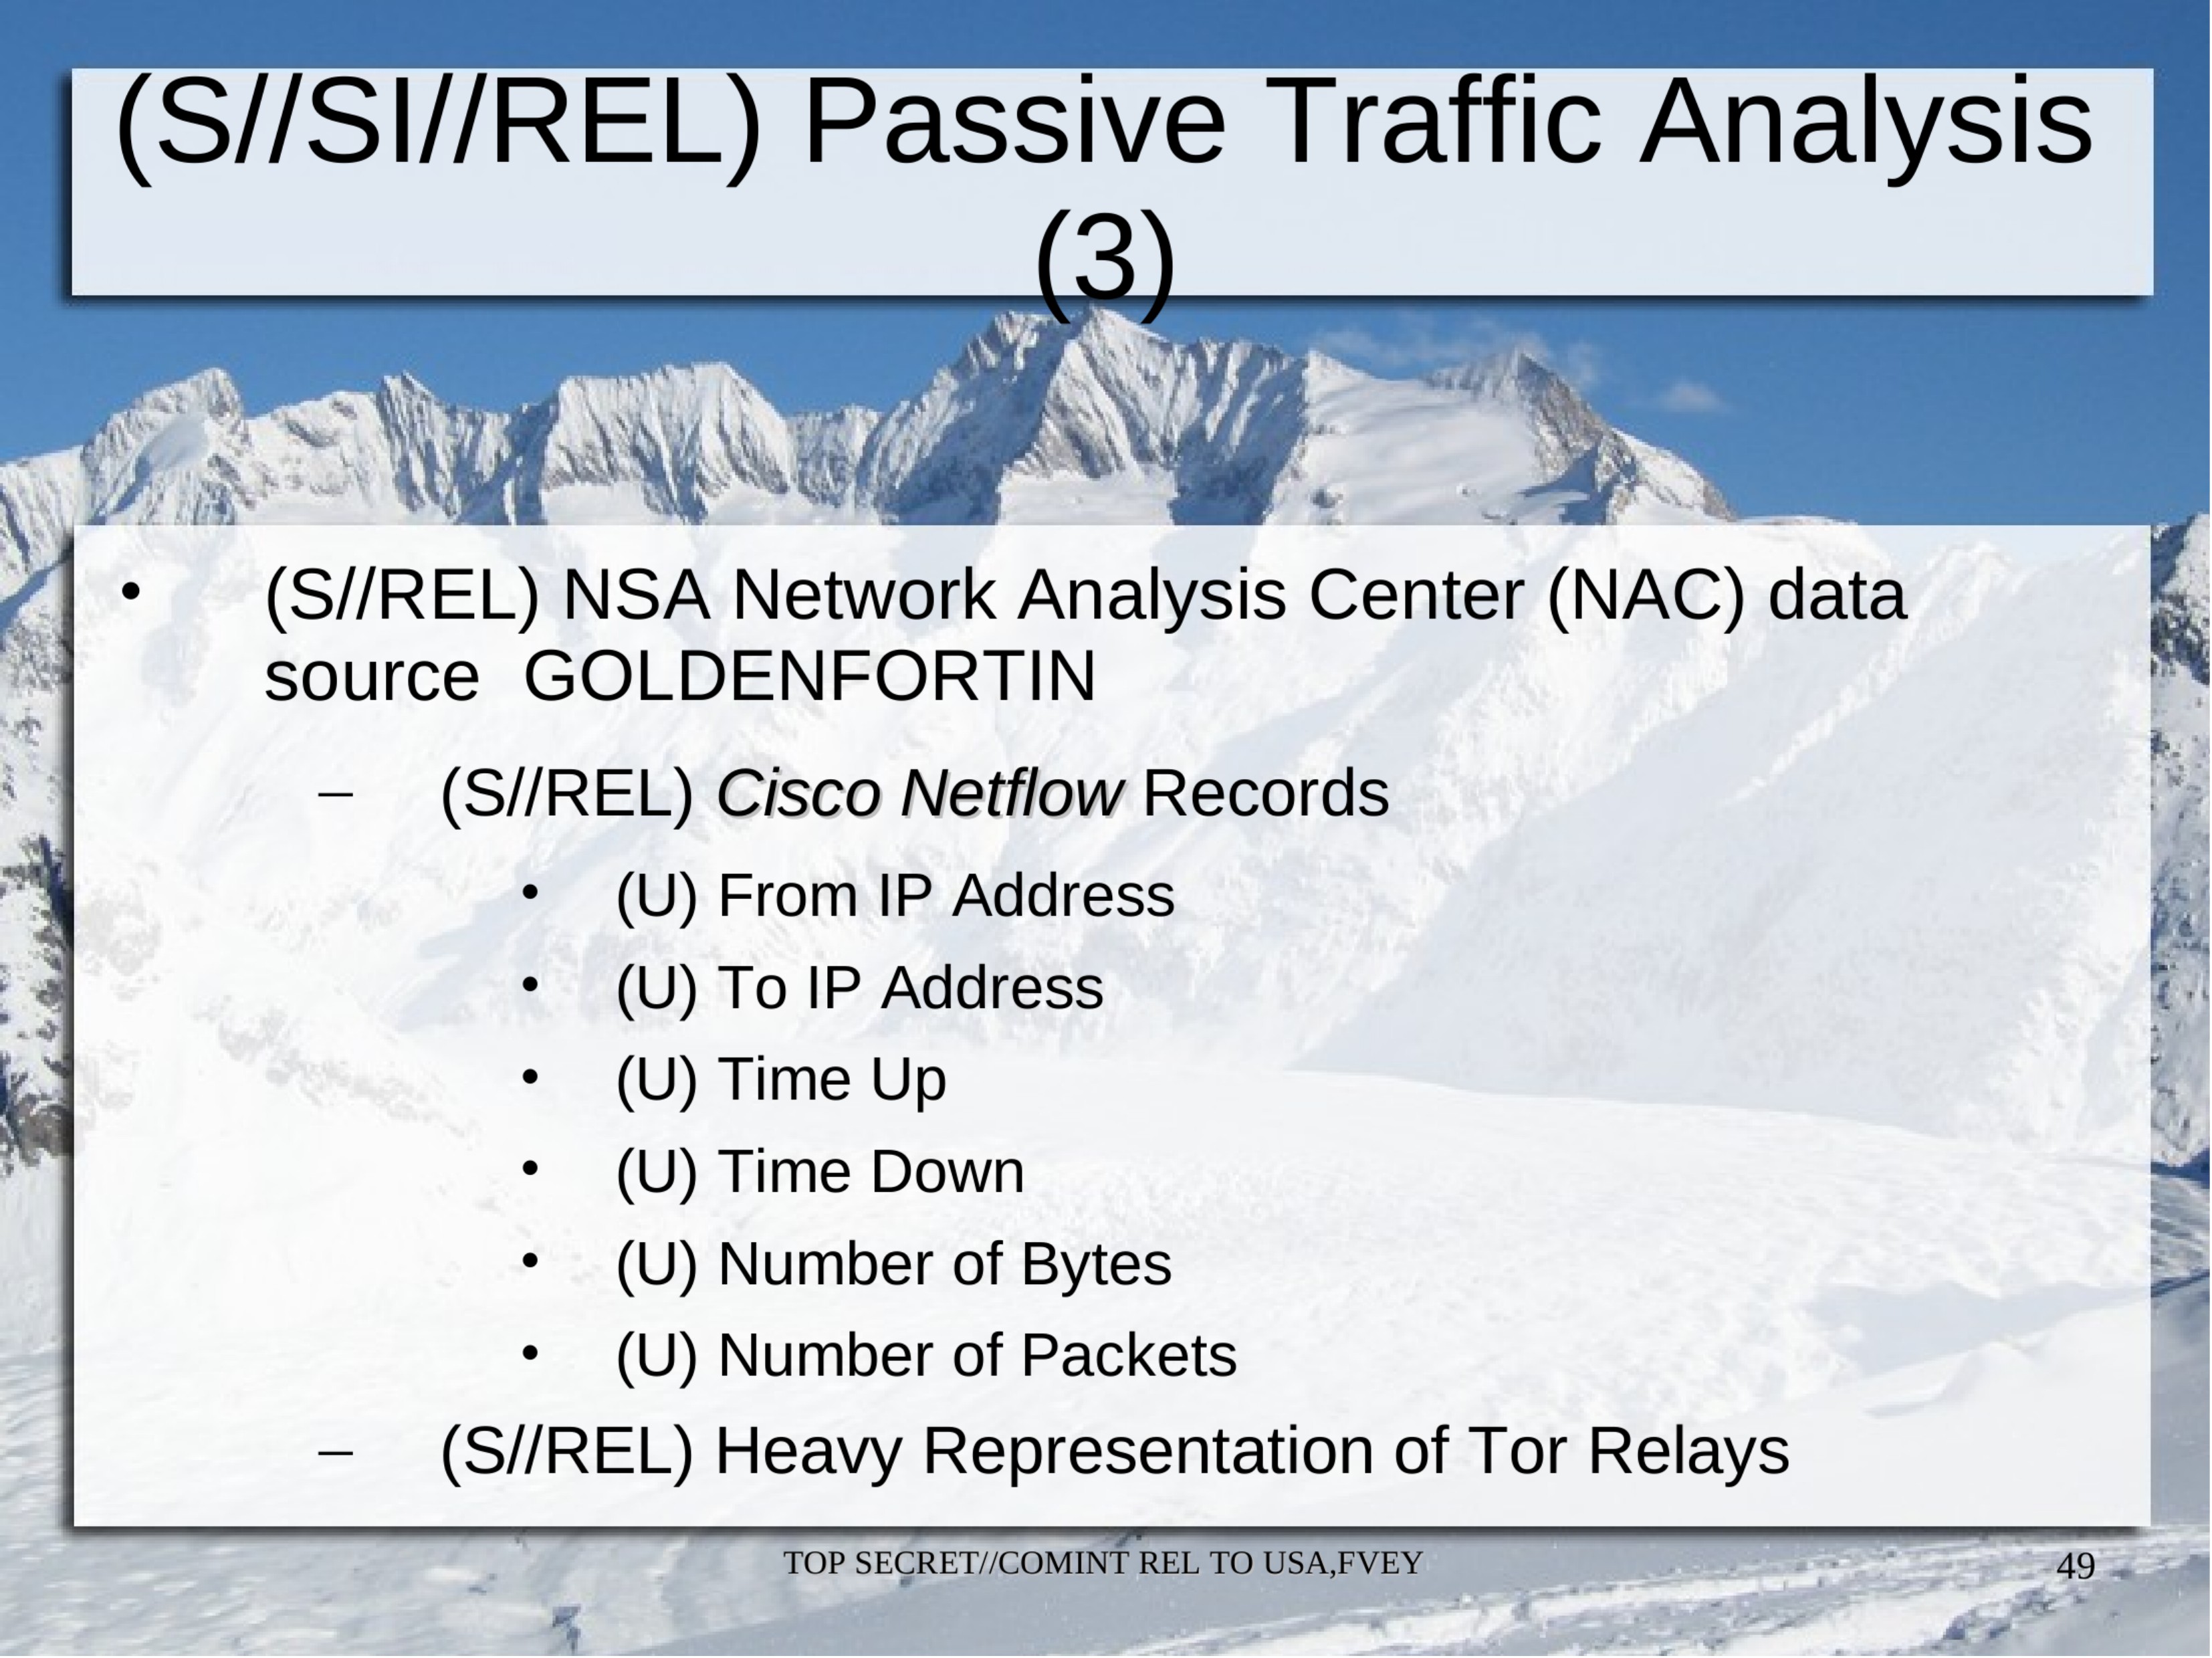
- (S//REL) NSA Network Analysis Center (NAC) data source GOLDENFORTIN
- (S//REL) Cisco Netflow Records
- (U) From IP Address
- (U) To IP Address
- (U) Time Up
- (U) Time Down
- (U) Number of Bytes
- (U) Number of Packets
- (S//REL) Heavy Representation of Tor Relays
- (S//REL) Cisco Netflow Records
TOP SECRET//COMINT REL TO USA,FVEY
49
(S//SI//REL) Passive Traffic Analysis (4)
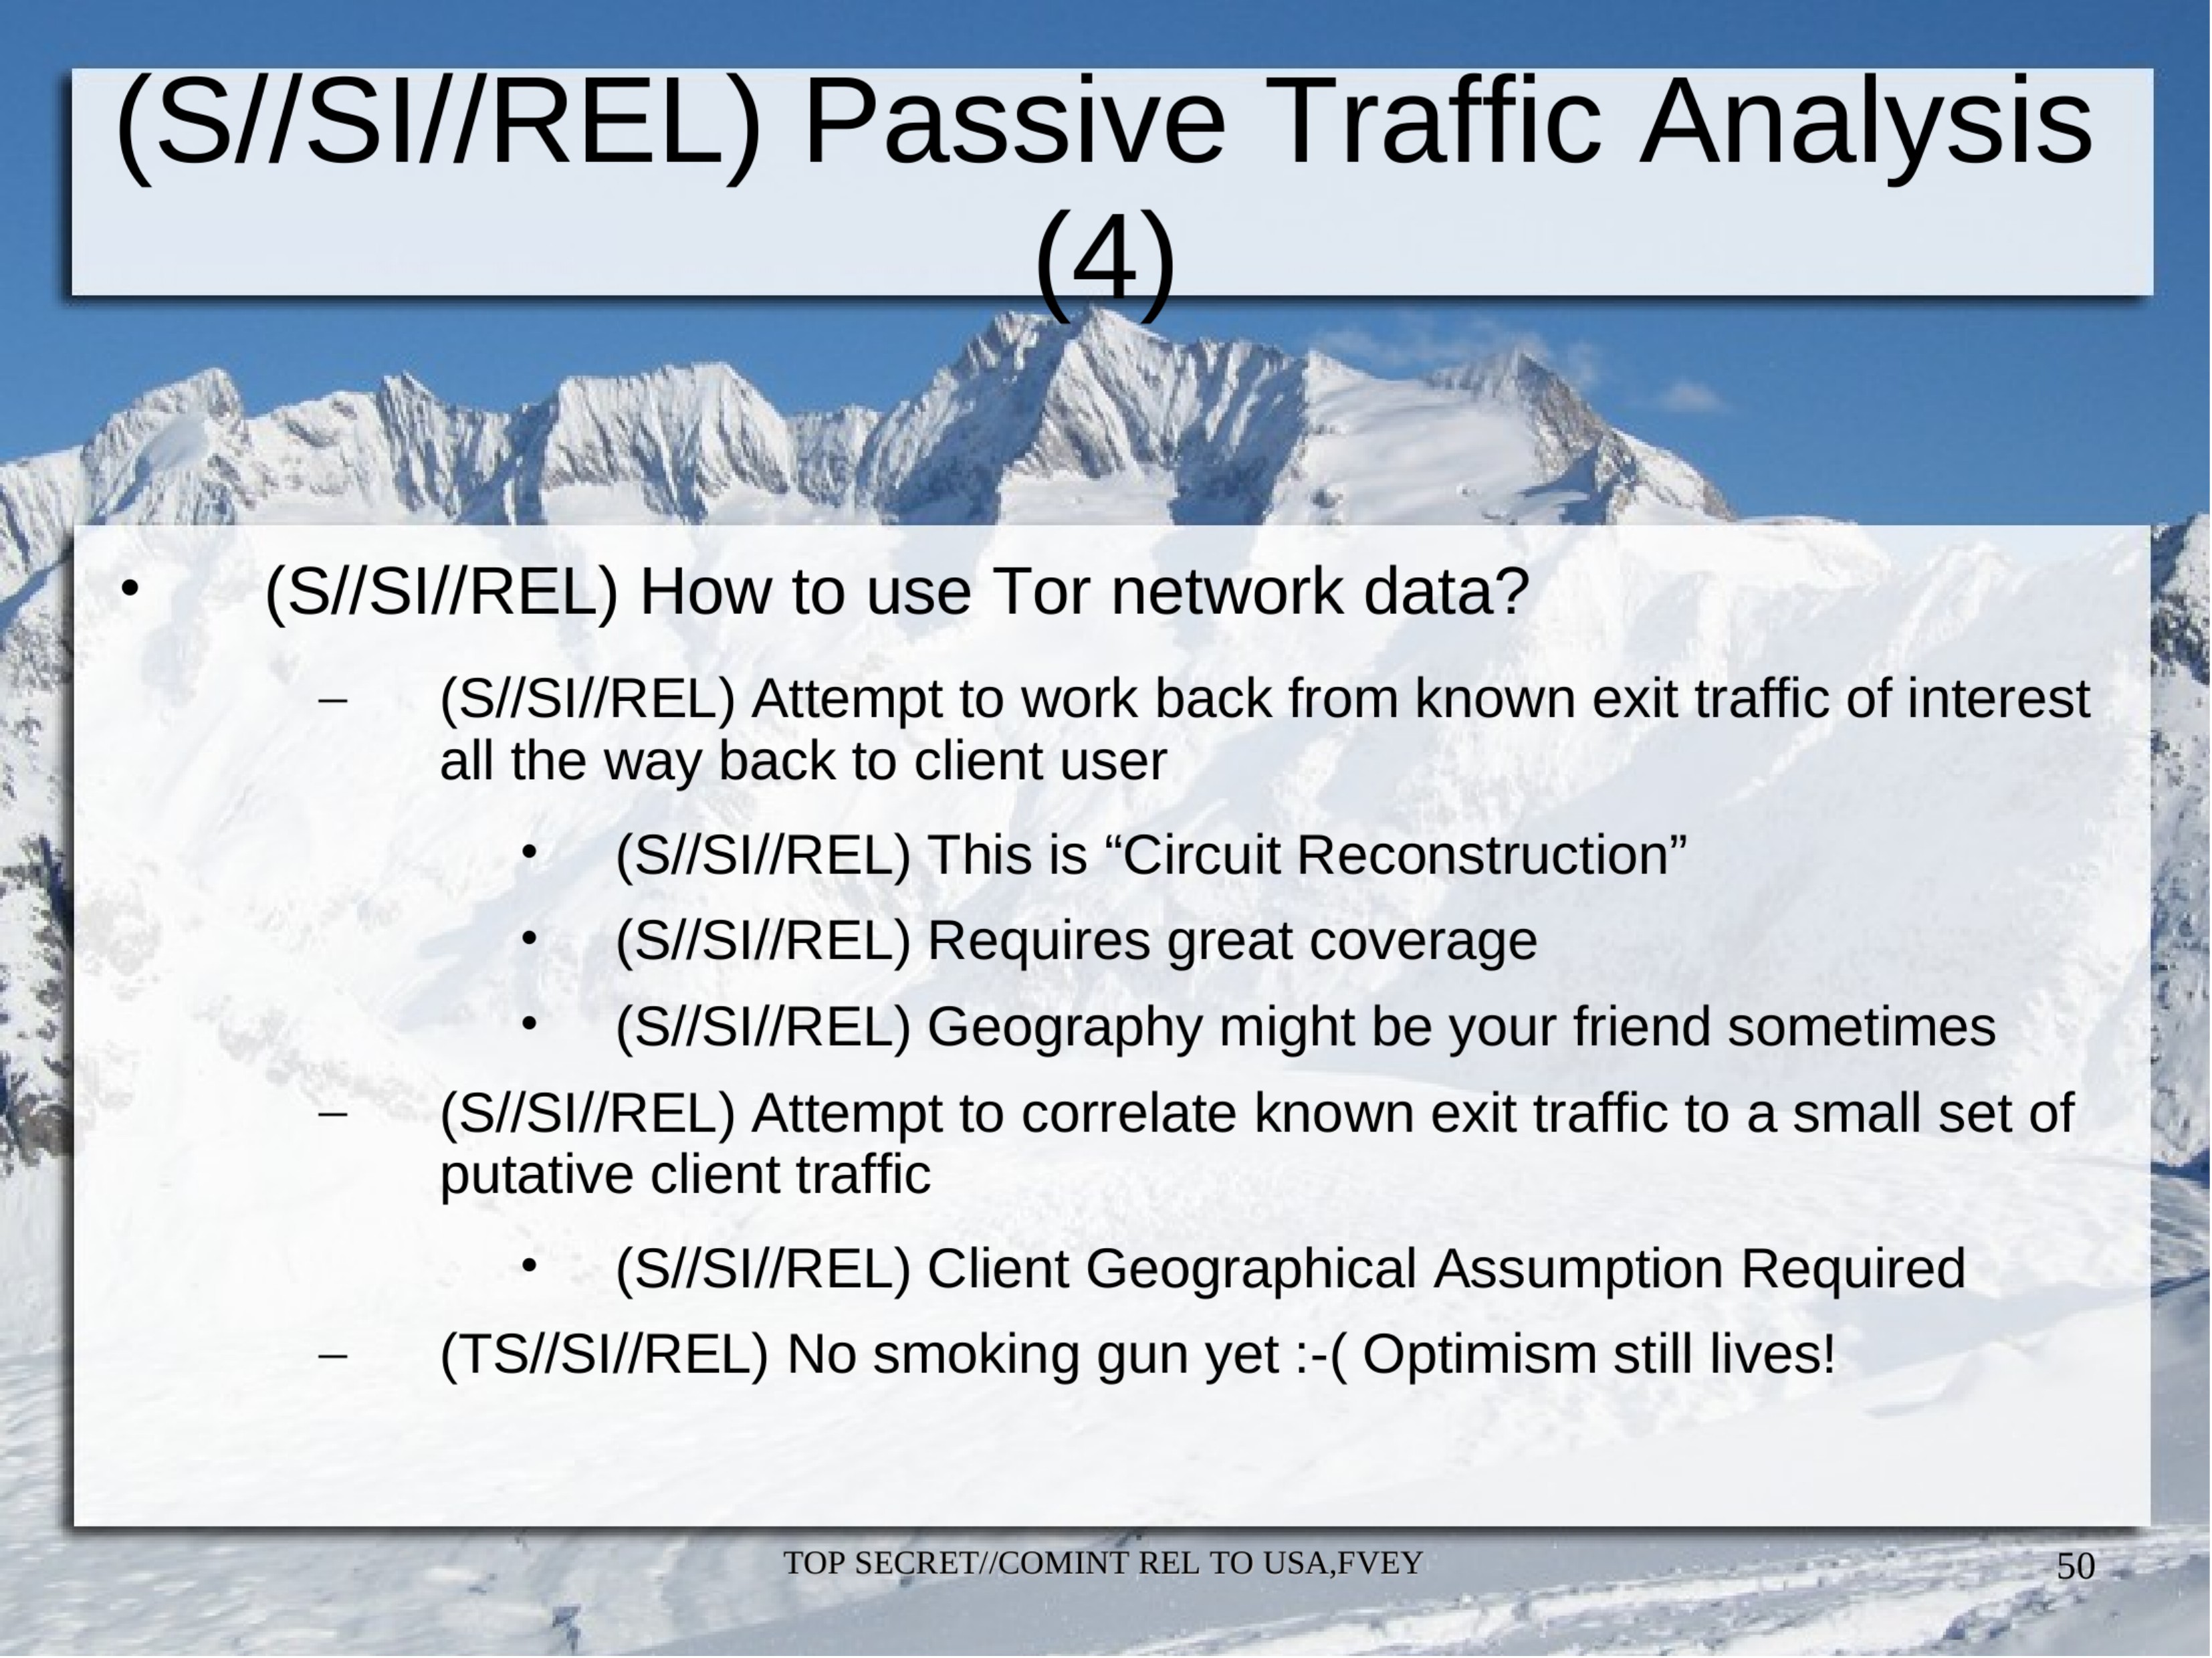
- (S//SI//REL) How to use Tor network data?
- (S//SI//REL) Attempt to work back from known exit traffic of interest all the way back to client user
- (S//SI//REL) This is “Circuit Reconstruction”
- (S//SI//REL) Requires great coverage
- (S//SI//REL) Geography might be your friend sometimes
- (S//SI//REL) Attempt to correlate known exit traffic to a small set of putative client traffic
- (S//SI//REL) Client Geographical Assumption Required
- (TS//SI//REL) No smoking gun yet :-( Optimism still lives!
- (S//SI//REL) Attempt to work back from known exit traffic of interest all the way back to client user
TOP SECRET//COMINT REL TO USA,FVEY
50
(TS//SI//REL) Active: Traffic Shaping
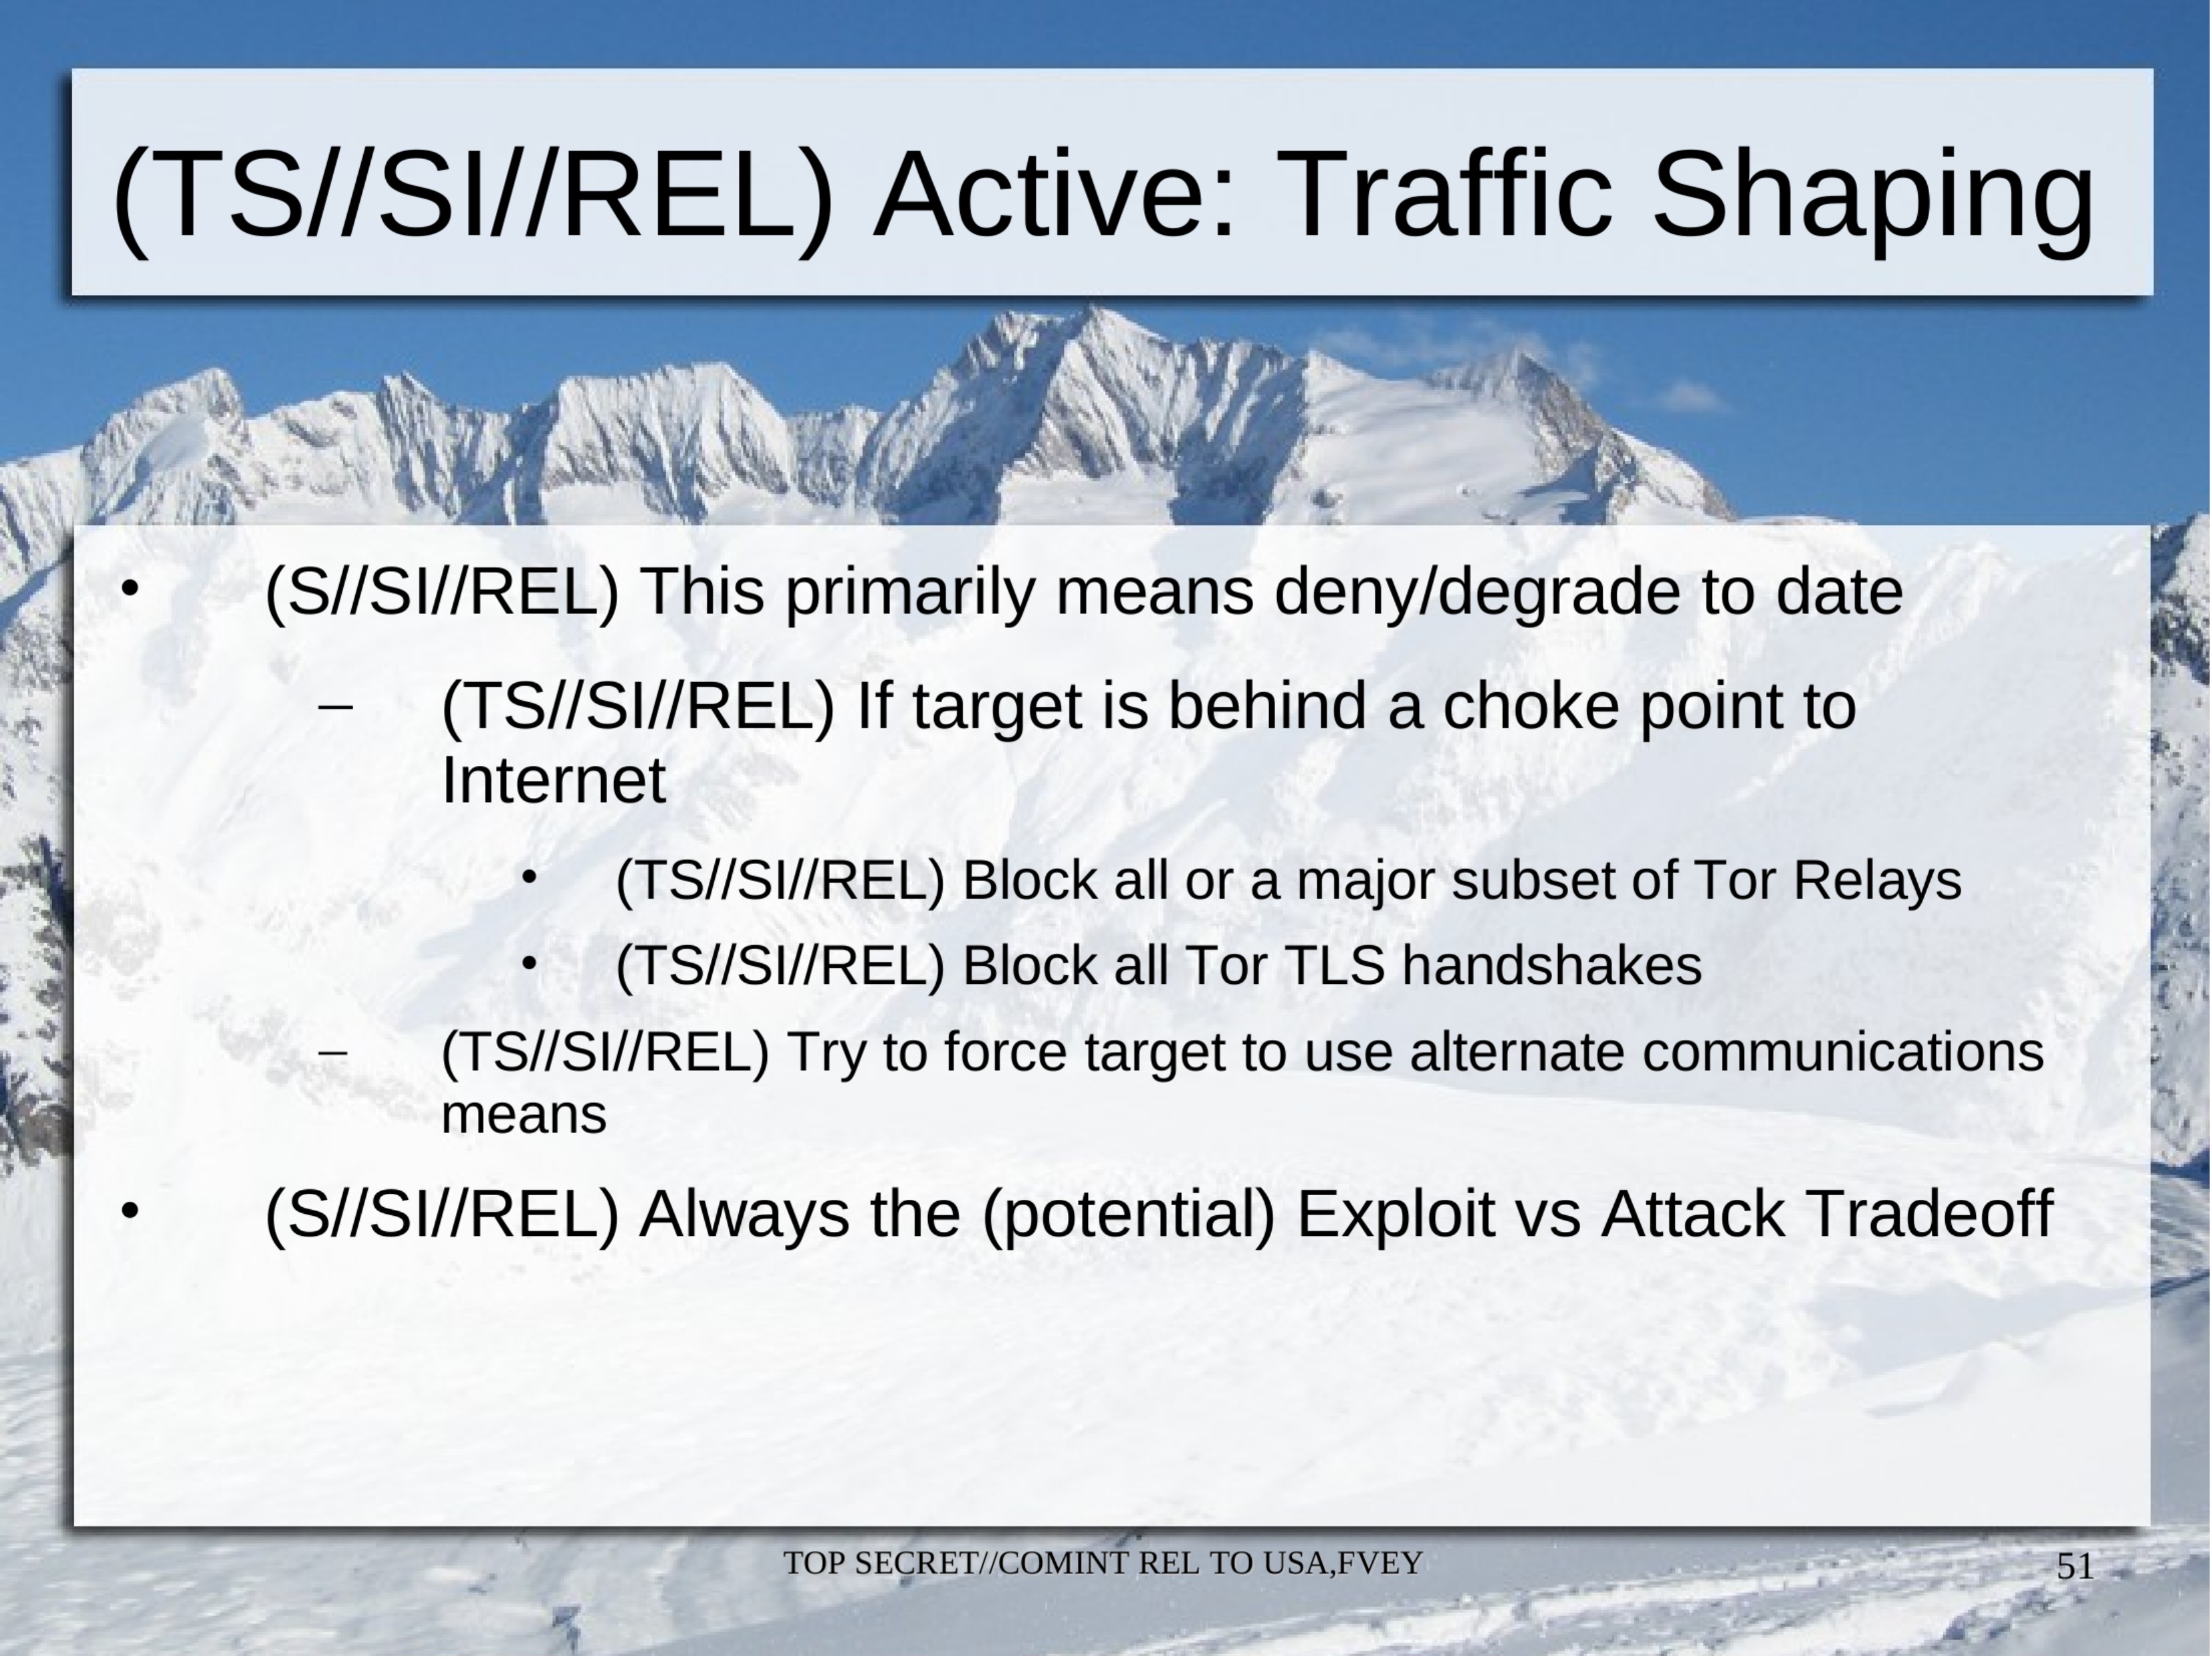
- (S//SI//REL) This primarily means deny/degrade to date
- (TS//SI//REL) If target is behind a choke point to Internet
- (TS//SI//REL) Block all or a major subset of Tor Relays
- (TS//SI//REL) Block all Tor TLS handshakes
- (TS//SI//REL) Try to force target to use alternate communications means
- (TS//SI//REL) If target is behind a choke point to Internet
- (S//SI//REL) Always the (potential) Exploit vs Attack Tradeoff
TOP SECRET//COMINT REL TO USA,FVEY
51
(TS//SI//REL) Active: Implants
- (S//SI//REL) TorButton: A Thorn in the side of SIGINT
- (S//REL) One of the components of The Tor Browser Bundle – AKA "Tor for Dummies"
- (S//REL) Firefox browser plugin – on/off switch for Tor
- (S//REL) Locks down browser REAL good (disables all active content things, sandboxes state, etc.)
- (TS//SI//REL) No current bypass methods for CNE Exploits
- (TS//SI//REL) Only hope is implanting web server with poisoned content document intended for target
TOP SECRET//COMINT REL TO USA,FVEY
52
Published in the Same Report
(10 of 43 documents)
-
BULLRUN CoI - Briefing Sheet [pdf]
A GCHQ briefing sheet introducing the BULLRUN Community of Interest — the access control framework protecting Five Eyes capabilities to defeat encryption across TLS/SSL, HTTPS, SSH, VPNs, IPSec, encrypted chat and encrypted VoIP — covering the classification structure, handling procedures and protective marking guidance for intelligence derived from cryptanalytic exploitation.
“N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Perlroth, Nicole · Larson, Jeff · Shane, Scott · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CLASSIFICATION GUIDE FOR CRYPTANALYSIS, 2-12 [pdf]
An NSA/CSS classification guide for cryptanalysis establishing the precise classification level for each type of information about NSA's capabilities to exploit commercial and indigenous encryption systems — from the unclassified acknowledgement that NSA exploits cryptographic devices, through to the Top Secret protection of cryptographic modifications made to commercial products to render them exploitable and industry relationships used to obtain cryptographic details.
“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Ball, James · Borger, Julian · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
TLS Trends: A roundtable discussion on current usage and future directions [pdf]
A presentation by Canada's Communications Security Establishment describing their TLS trend analysis programme, which systematically tracked SSL/TLS encryption parameters across warranted collection and Special Source access to identify cryptanalytic opportunities, monitor target behaviour and collaborate with GCHQ on exploiting weaknesses in widely-used encryption implementations.
-
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
TLS trends at GCHQ [pdf]
A GCHQ presentation describing their TLS trends analysis programme, which processed approximately 10 billion SSL/TLS Server Hello events per week from Special Source cable tapping and COMSAT collection to produce weekly trend reports, alongside two operational tools — TargeTLS for matching TLS events against BROAD OAK target profiles, and FLYING PIG, a TLS knowledge base enabling analysts to query certificate, IP and client data across the full intercept base.
-
TURMOIL/APEX/APEX High Level Description Document [pdf]
NSA WikiInfo page providing the high-level design description of APEX — the Active-Passive Integration capability integrating HAMMERMILL router implants with TURMOIL passive collection — enabling real-time exfiltration of targeted VPN (HAMMERSTEIN) and VoIP (HAMMERCHANT) traffic from compromised routers directly into NSA's passive collection and cryptanalytic attack infrastructure, with TURBINE providing automated command and control of the combined active-passive system.
Programs: TURMOIL · APEX · HAMMERMILL · HAMMERCHANT · HAMMERSTEIN · FASHIONCLEFT · TURBINE · TOYGRIPPE · METROTUBE · CHIMNEYPOOL · PIQBLADE · KEYCARD · FASCIA · ISLANDTRANSPORT · PRESSUREWAVE · ASDF · CONVEYANCE · TURBULENCE -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT







Related Documents
-
What Your Mother Never Told You About SIGDEV Analysis [pdf]
An NSA presentation covering VPN signals development tradecraft and the prototype DARKSUNRISE VPN analytics tool — describing how analysts use DISCOROUTE, BLACKPEARL, TOYGRIPPE, NKB, RONIN and GNETWORK GNOME to map target VPN networks from router configuration data, with live screenshots of DARKSUNRISE's SHADOWNET interface showing IPSec VPN connections associated with Pakistani, Afghan and other targets collected through MUSCULAR (DS-200B).
Programs: TOYGRIPPE · DISCOROUTE · BLACKPEARL · GNETWORKGNOME · NKB · RONIN · XKEYSCORE · TREASUREMAP · RENOIR · ROYALNET · GNOME · ASDF · DARKSUNRISE · SHADOWNET · WEALTHYCLUSTER · MUSCULAR · CASPORT · CUE · BLACKSAND · DANCINGOASIS · BLACKBEACH · POTLUCK · SSO · DNIPRESENTER · TNS · BLACKPEAL · ROADBED · TROPICNET · SILVERZEPHYR · SITESTORE -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
VPN SigDev Basics [pdf]
A TOP SECRET VPN signals development training presentation from NSA's OTTERCREEK team introducing analysts to the six-stage workflow for discovering, assessing and exploiting VPN traffic — covering TOYGRIPPE, XKEYSCORE, DISCOROUTE and other repositories with live interface screenshots showing Iranian-German IPSec traffic and UNAMI (UN Assistance Mission for Iraq) router configurations containing pre-shared keys, including a Cuban VPN pre-shared key recovered in plaintext from a compromised router.
Programs: BLEAKINQUIRY · DISCOROUTE · TOYGRIPPE · MARINA · MASTERSHAKE · NKB · PINWALE · RENOIR · TREASUREMAP · TUNINGFORK · XKEYSCORE · GOLDPOINT · PILBEAM · RADIUS · CREAKSTILE · MAILORDER · ROADBED · DROPBOX · PPF -
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
Types of IAT - Advanced Open Source Multi-hop [pdf]
This top-secret NSA/GCHQ document provides a detailed technical overview of the Tor network, including how it works, its strengths as the “king of high secure, low-latency Internet anonymity,” methods for identifying Tor traffic, censorship-driven protocol obfuscation, and ongoing intelligence efforts to analyze, fingerprint, and exploit Tor through passive SIGINT and active research, including collaboration between US and UK agencies.
People: Appelbaum, Jacob