Dissemination control: REL FVEY 10 documents
Search documents matching “REL FVEY” →Handling controls assessed for each document, as component values. If a document contains multiple disseminations, the most restrictive is used here.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Broadcast/Internet Radio Exploitation and Analysis, 6th November 2009, GCHQ [pdf]
This GCHQ report analyzes 6.68 million internet radio listening events collected over three months in 2009, detailing global broadcasting patterns, user behaviors, and specifically examining Islamic radio stations and Pakistan-UK connections for potential radicalization intelligence, while recommending integration with bulk surveillance databases like KARMA POLICE for enhanced user profiling.
-
CASCADE - Joint Cyber Sensor Architecture [pdf]
This presentation outlines the Communications Security Establishment’s (CSE) plans to unify and expand its cyber sensor networks (ITS and SIGINT) to create a comprehensive, multi-layered national cyber defense system, enabling threat detection, intelligence collection, and defensive operations across Canadian and foreign networks. It emphasizes standardizing sensor deployments, integrating analytic capabilities, and preparing for “Effects” operations to mitigate cyber threats by 2015. The presentation is duplicated from page 33 onwards - three slides of the duplicated slides have internal CSE comments.
Programs: CASCADE · PHOTONICPRISM · EONBLUE · INDUCTION · THIRDEYE · CRUCIBLE · CHOKEPOINT · SUNWHEEL · CASSIOPEIA · SCNET · JAZZFLUTE · GAZEBO · SEEDSPHERE · TEXPRO · SSO -
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
Exploiting Facebook traffic in the passive environment to obtain specific information [pdf]
A GCHQ Global Telecommunications Exploitation presentation on extracting information about Facebook users from passively collected traffic: why online social networks are a rich source, how Facebook's use of the Akamai content delivery network exposes a user's ID inside image URLs, and how profile and album images are then obtained through SPRING BISHOP, GODFATHER and JTRIG.
-
FAIRVIEW brief overview [pdf]
This document outlines the FAIRVIEW program, established in 1985, which leverages a corporate partner to exploit international communications through cables, switches, and routers. It is one of the NSA's top sources for metadata and serialized intelligence, supporting a wide range of targets including counter-terrorism, crime, and international security issues.
Programs: FAIRVIEW -
GRIMPLATE - First Steps Toward Identifying Adversarial Use of BitTorrent [pdf]
This document outlines the NSA's GRIMPLATE program, which was developed to monitor and analyze BitTorrent traffic on the Department of Defense's NIPRnet to identify potentially malicious activity. The program focuses on crawling the Distributed Hash Table (DHT) of BitTorrent networks to gather data on file-sharing nodes and peer connections, in order to detect and mitigate threats while building a case for halting unauthorized P2P usage on secure networks.
-
MORECOWBELL [pdf]
This document describes how NSA is covertly monitoring DNS resolutions and target websites in near real-time using covertly rented servers in Malaysia, Germany and Denmark.
-
SIGDEV Conference 2012 - Making Things Measureable: Technology Trending Challenges and Approaches [pdf]
An NSA presentation from the 2012 SIGDEV Conference describing NSA's technology trending methodology — a framework for identifying which encryption and communications technologies targets are adopting, measuring the SIGINT risk they pose, and prioritising capabilities development responses — notable for containing the risk matrix that was later cited in Der Spiegel's December 2014 encryption investigation showing NSA's difficulty levels against specific technologies including Tor, TrueCrypt, OTR and ZRTP.
Programs: XKEYSCORE · SEEKER · BIONICTURTLE · JEMA · JOLLYROGER · MARINA · TUNINGFORK · STARPROC · MICROEXPANSE · ECHOBASE · PRISM · GMHALO · UTT · TKB · LAE · FAMT · WPMO · AMOD · FORTREND · GAMBIT · DATAEXPLORER · MYNOC -
Tor Stinks [pdf]
A June 2012 joint NSA-GCHQ presentation titled "Tor Stinks" detailing the two agencies' attempts to de-anonymize Tor users through analytics, exploitation, and network disruption — candidly admitting they will never be able to identify all Tor users, but outlining a range of techniques including cookie leakage tracking, QUANTUM attacks, circuit reconstruction, timing analysis, and deliberate network degradation.
Programs: REMATION · EPICFAIL · QUANTUM · NEWTONSCRADLE · QUICKANT · GREATEXPECTATIONS · RONIN · ONIONBREATH · QUANTUMCOOKIE · SHORTSHEET · FOXACID -
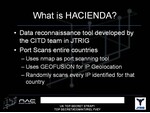
What is HACIENDA? [pdf]
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).