Crypt Discovery Joint Collaboration Activity 20 January 2011
Open PDFDocument date: 2011-01-20
Pages: 3
Genre: other
Banner: TOP SECRET
Classification: TOP SECRET
Dissemination: -
A TOP SECRET NSA/GCHQ joint collaboration activity plan from January 2011 describing a research programme to understand and mitigate the threat that rising encryption adoption poses to target discovery and development — measuring encryption prevalence across SIGINT collection, assessing the impact on metadata-based targeting tradecraft, and developing new techniques for identifying targets behind encrypted traffic using a joint cloud environment fed by MUTANT BROTH, BEARDED PIGGY, KARMA POLICE, MEMORY HOLE, MARBLED GECKO, SOCIAL ANIMAL and ASDF metadata.
My notes
TOP SECRET
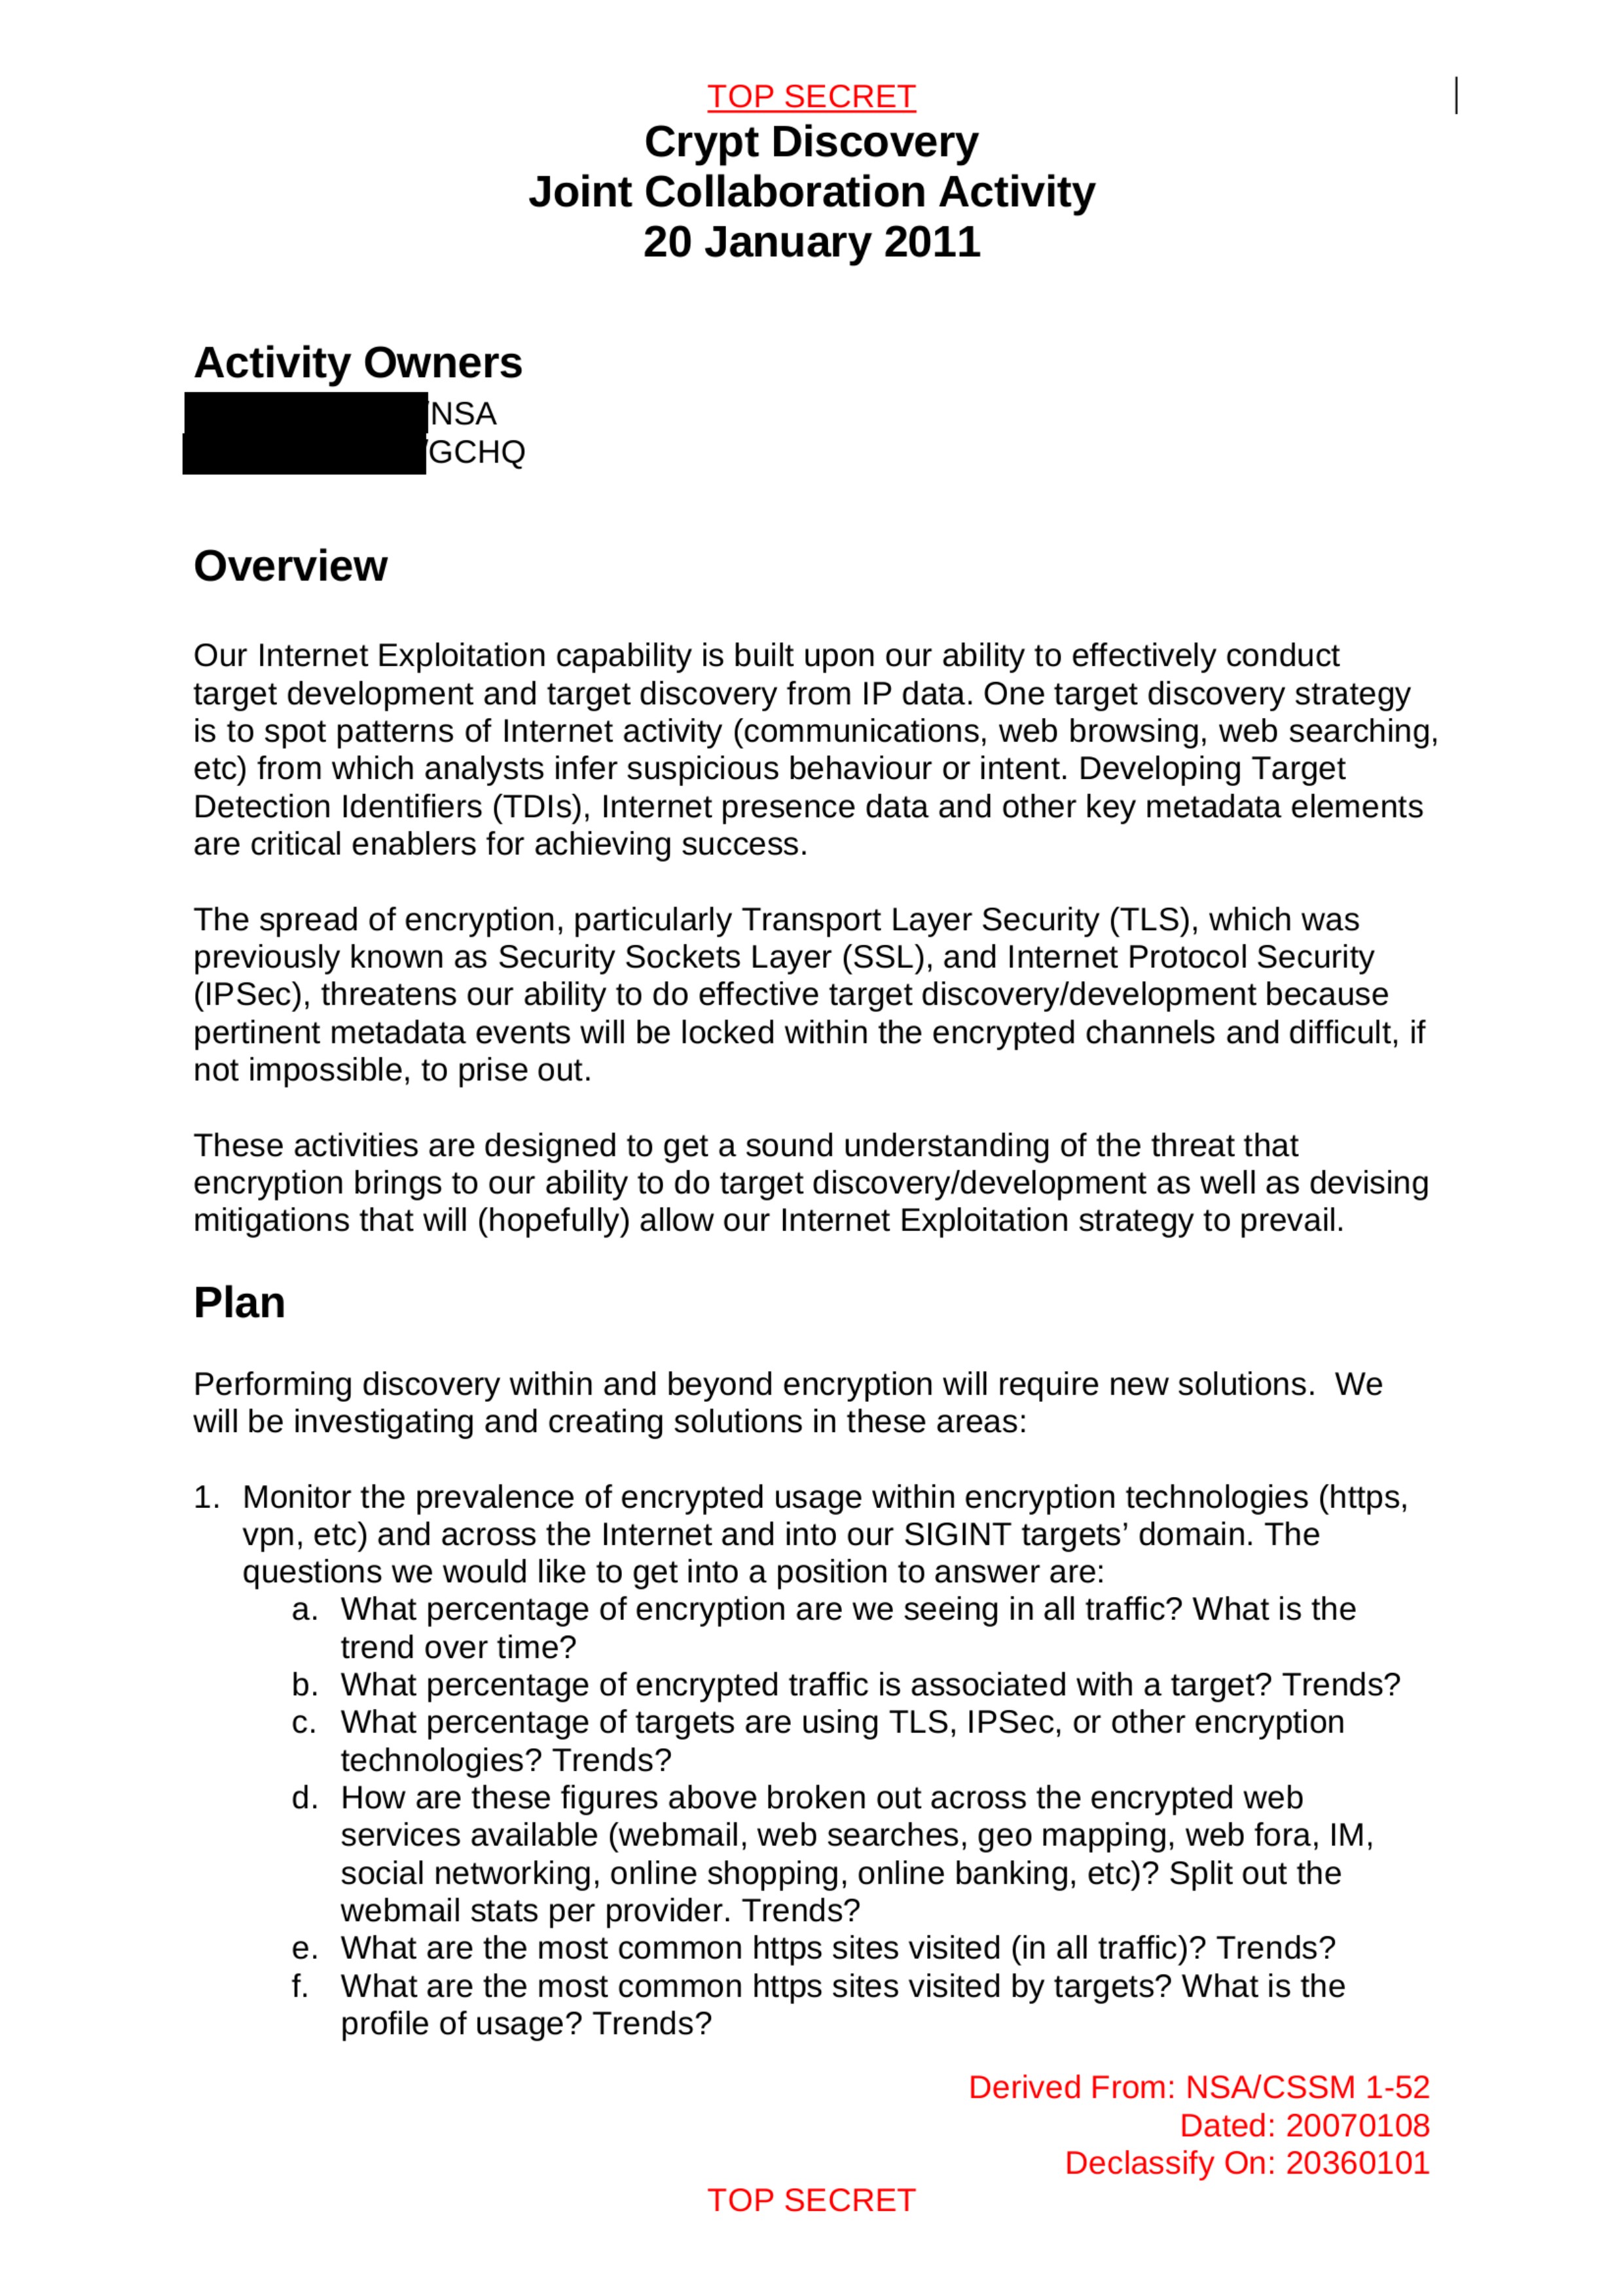
Crypt Discovery
Joint Collaboration Activity
20 January 2011
Activity Owners
[REDACTED] NSA
[REDACTED] GCHQ
Overview
Our Internet Exploitation capability is built upon our ability to effectively conduct target development and target discovery from IP data. One target discovery strategy is to spot patterns of Internet activity (communications, web browsing, web searching, etc) from which analysts infer suspicious behaviour or intent. Developing Target Detection Identifiers (TDIs), Internet presence data and other key metadata elements are critical enablers for achieving success.
The spread of encryption, particularly Transport Layer Security (TLS), which was previously known as Security Sockets Layer (SSL), and Internet Protocol Security (IPSec), threatens our ability to do effective target discovery/development because pertinent metadata events will be locked within the encrypted channels and difficult, if not impossible, to prise out.
These activities are designed to get a sound understanding of the threat that encryption brings to our ability to do target discovery/development as well as devising mitigations that will (hopefully) allow our Internet Exploitation strategy to prevail.
Plan
Performing discovery within and beyond encryption will require new solutions. We will be investigating and creating solutions in these areas:
- Monitor the prevalence of encrypted usage within encryption technologies (https, vpn, etc) and across the Internet and into our SIGINT targets' domain. The questions we would like to get into a position to answer are:
a. What percentage of encryption are we seeing in all traffic? What is the trend over time?
b. What percentage of encrypted traffic is associated with a target? Trends?
c. What percentage of targets are using TLS, IPSec, or other encryption technologies? Trends?
d. How are these figures above broken out across the encrypted web services available (webmail, web searches, geo mapping, web fora, IM, social networking, online shopping, online banking, etc)? Split out the webmail stats per provider. Trends?
e. What are the most common https sites visited (in all traffic)? Trends?
f. What are the most common https sites visited by targets? What is the profile of usage? Trends?
Derived From: NSA/CSSM 1-52
Dated: 20070108
Declassify On: 20360101
TOP SECRET
TOP SECRET
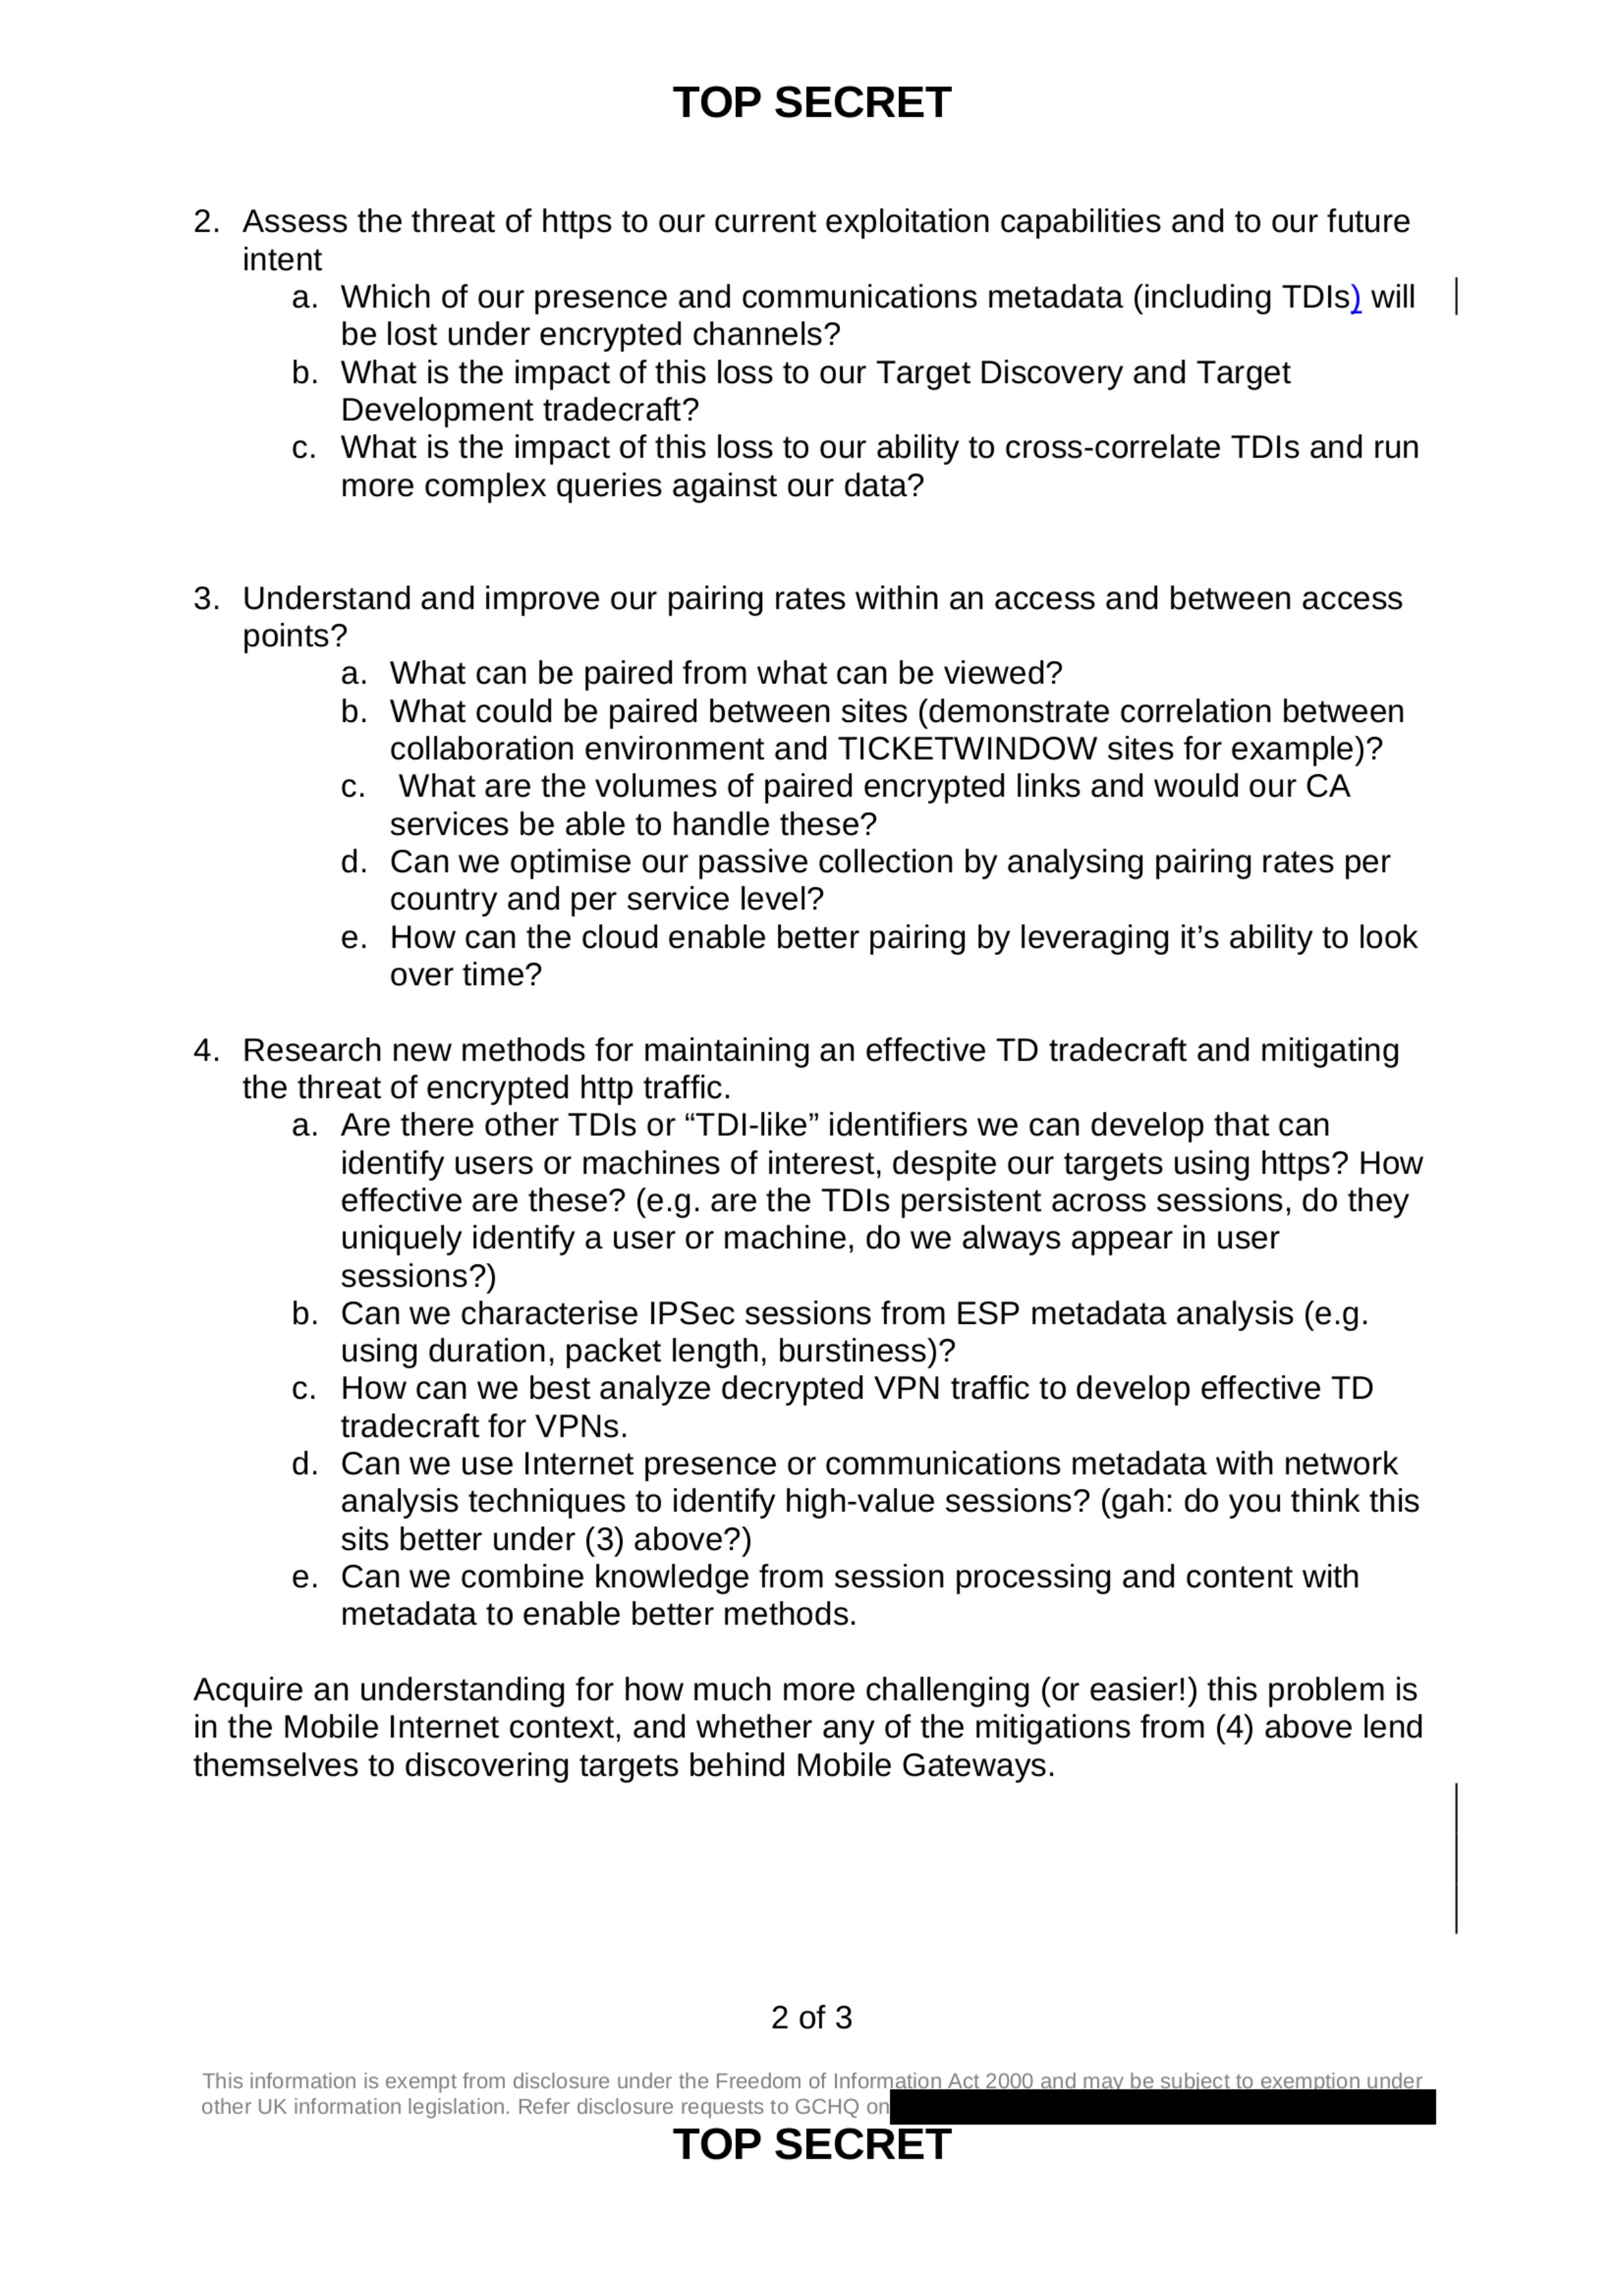
- Assess the threat of https to our current exploitation capabilities and to our future intent
a. Which of our presence and communications metadata (including TDIs) will be lost under encrypted channels?
b. What is the impact of this loss to our Target Discovery and Target Development tradecraft?
c. What is the impact of this loss to our ability to cross-correlate TDIs and run more complex queries against our data?
- Understand and improve our pairing rates within an access and between access
points?
a. What can be paired from what can be viewed?
b. What could be paired between sites (demonstrate correlation between collaboration environment and TICKETWINDOW sites for example)?
c. What are the volumes of paired encrypted links and would our CA services be able to handle these?
d. Can we optimise our passive collection by analysing pairing rates per country and per service level?
e. How can the cloud enable better pairing by leveraging it's ability to look over time?
- Research new methods for maintaining an effective TD tradecraft and mitigating the threat of encrypted http traffic.
a. Are there other TDIs or "TDI-like” identifiers we can develop that can identify users or machines of interest, despite our targets using https? How effective are these? (e.g. are the TDIs persistent across sessions, do they uniquely identify a user or machine, do we always appear in user sessions?)
b. Can we characterise IPSec sessions from ESP metadata analysis (e.g. using duration, packet length, burstiness)?
c. How can we best analyze decrypted VPN traffic to develop effective TD tradecraft for VPNs.
d. Can we use Internet presence or communications metadata with network analysis techniques to identify high-value sessions? (gah: do you think this sits better under (3) above?)
e. Can we combine knowledge from session processing and content with metadata to enable better methods.
Acquire an understanding for how much more challenging (or easier!) this problem is in the Mobile Internet context, and whether any of the mitigations from (4) above lend themselves to discovering targets behind Mobile Gateways.
2 of 3
This information is exempt from disclosure under the Freedom of Information Act 2000 and may be subject to exemption under other UK information legislation. Refer disclosure requests to GCHQ on [REDACTED]
TOP SECRET
TOP SECRET
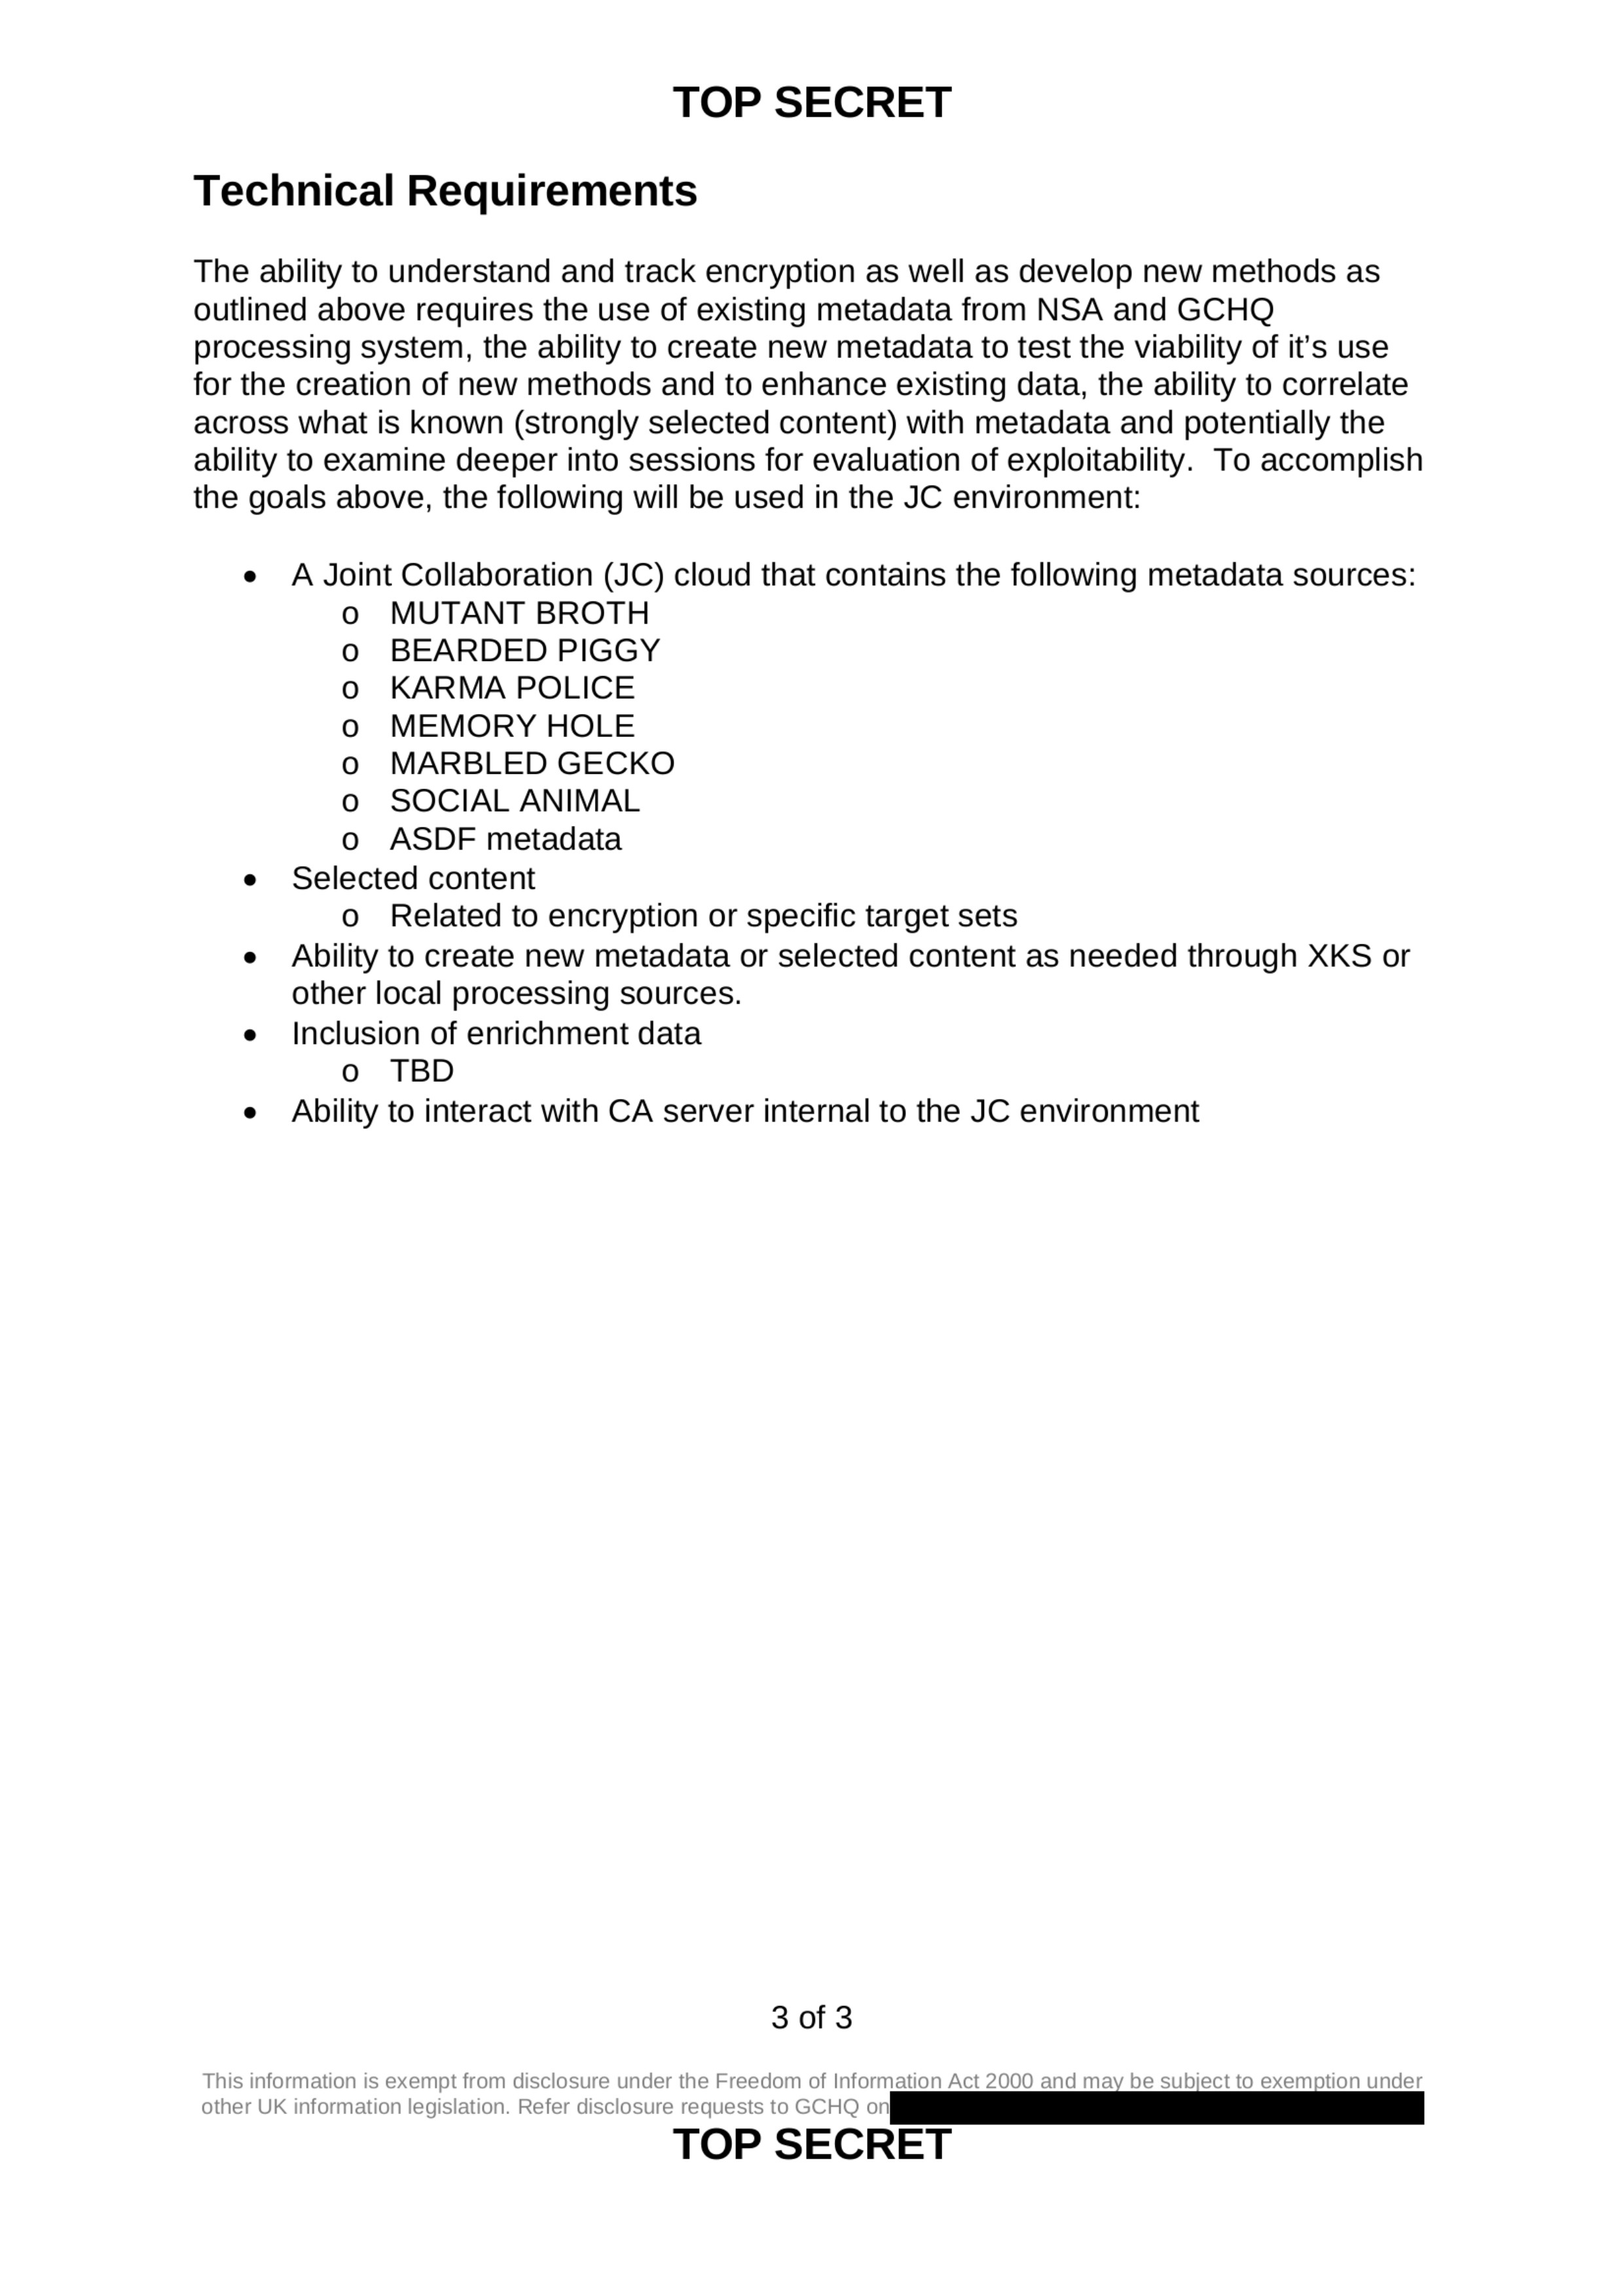
Technical Requirements
The ability to understand and track encryption as well as develop new methods as outlined above requires the use of existing metadata from NSA and GCHQ processing system, the ability to create new metadata to test the viability of it's use for the creation of new methods and to enhance existing data, the ability to correlate across what is known (strongly selected content) with metadata and potentially the ability to examine deeper into sessions for evaluation of exploitability. To accomplish the goals above, the following will be used in the JC environment:
- A Joint Collaboration (JC) cloud that contains the following metadata sources:
- MUTANT BROTH
- BEARDED PIGGY
- KARMA POLICE
- MEMORY HOLE
- MARBLED GECKO
- SOCIAL ANIMAL
- ASDF metadata
- Selected content
- Related to encryption or specific target sets
- Ability to create new metadata or selected content as needed through XKS or other local processing sources.
- Inclusion of enrichment data
- TBD
- Ability to interact with CA server internal to the JC environment
3 of 3
This information is exempt from disclosure under the Freedom of Information Act 2000 and may be subject to exemption under other UK information legislation. Refer disclosure requests to GCHQ on [REDACTED]
TOP SECRET
Published in the Same Report
(10 of 71 documents)
-
BULLRUN CoI - Briefing Sheet [pdf]
A GCHQ briefing sheet introducing the BULLRUN Community of Interest — the access control framework protecting Five Eyes capabilities to defeat encryption across TLS/SSL, HTTPS, SSH, VPNs, IPSec, encrypted chat and encrypted VoIP — covering the classification structure, handling procedures and protective marking guidance for intelligence derived from cryptanalytic exploitation.
“N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Perlroth, Nicole · Larson, Jeff · Shane, Scott · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CLASSIFICATION GUIDE FOR CRYPTANALYSIS, 2-12 [pdf]
An NSA/CSS classification guide for cryptanalysis establishing the precise classification level for each type of information about NSA's capabilities to exploit commercial and indigenous encryption systems — from the unclassified acknowledgement that NSA exploits cryptographic devices, through to the Top Secret protection of cryptographic modifications made to commercial products to render them exploitable and industry relationships used to obtain cryptographic details.
“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Ball, James · Borger, Julian · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
TLS Trends: A roundtable discussion on current usage and future directions [pdf]
A presentation by Canada's Communications Security Establishment describing their TLS trend analysis programme, which systematically tracked SSL/TLS encryption parameters across warranted collection and Special Source access to identify cryptanalytic opportunities, monitor target behaviour and collaborate with GCHQ on exploiting weaknesses in widely-used encryption implementations.
-
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
TLS trends at GCHQ [pdf]
A GCHQ presentation describing their TLS trends analysis programme, which processed approximately 10 billion SSL/TLS Server Hello events per week from Special Source cable tapping and COMSAT collection to produce weekly trend reports, alongside two operational tools — TargeTLS for matching TLS events against BROAD OAK target profiles, and FLYING PIG, a TLS knowledge base enabling analysts to query certificate, IP and client data across the full intercept base.
-
TURMOIL/APEX/APEX High Level Description Document [pdf]
NSA WikiInfo page providing the high-level design description of APEX — the Active-Passive Integration capability integrating HAMMERMILL router implants with TURMOIL passive collection — enabling real-time exfiltration of targeted VPN (HAMMERSTEIN) and VoIP (HAMMERCHANT) traffic from compromised routers directly into NSA's passive collection and cryptanalytic attack infrastructure, with TURBINE providing automated command and control of the combined active-passive system.
Programs: TURMOIL · APEX · HAMMERMILL · HAMMERCHANT · HAMMERSTEIN · FASHIONCLEFT · TURBINE · TOYGRIPPE · METROTUBE · CHIMNEYPOOL · PIQBLADE · KEYCARD · FASCIA · ISLANDTRANSPORT · PRESSUREWAVE · ASDF · CONVEYANCE · TURBULENCE -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT







See all 44 documents published with “Prying Eyes: Inside the NSA's War on Internet Security” →
Related Documents
-
VALIANTSURF [pdf]
An NSA WikiInfo page for VALIANTSURF — the coverterm for NSA's IPSec VPN decryption capability within the TURMOIL collection platform — describing the four data flow types for intercepting and breaking encrypted VPN traffic, the full deployment roster across collection sites including Menwith Hill, SMOKYSINK, MUSCULAR, CROSSCUT and others, and the architectural taxonomy of the VALIANTSURF programme including its MALIBU and WAIMEA processing architectures and their relationship to LONGHAUL, POISONNUT and GALLANTWAVE.
Programs: VALIANTSURF · TURMOIL · TURBULENCE · HOOKED · HOOKEDHAND · CINDER · CINDERASH · CINDERTRACK · SCARLETFEVER · LONGHAUL · FALLOUT · TOYGRIPPE · PICARESQUE · XKEYSCORE · PRESSUREWAVE · ASDF · MAILORDER · TUBE · KEYCARD · POISONNUT · ISLANDHIDEAWAY · ISLANDTRANSPORT · EXOPUMP · CORALREEF · PINWALE · TUSCARORA · ONEROOF · CONVEYANCE · TURTLEPOWER · WDM · CADENCE · UTT · SCISSORS · FISHWAY · BTUBE · DNCA · ROMULANALE · GALLANTWAVE · ROMULANGAWK · ROMULANGOWL · MALIBU · WAIMEA · WAIMEAVISAGE · ROMULANVISAGE · WAIMEAVISE · ROMULANVISE · APEX · METROTUBE · MADFORGE · JSORCERER · CROSSCUT · CIET · LATTICE · STARQUAKE · SARATOGA · MUSCULAR · SMOKYSINK · SLACKKEY · TUMMS · PURGE · SURGE · NUCLEON · SPAGIC · PPF · SOAP · TUMULT · FIP · PIQBLADE · DEEPDIVE · IBRIDGE -
What Your Mother Never Told You About SIGDEV Analysis [pdf]
An NSA presentation covering VPN signals development tradecraft and the prototype DARKSUNRISE VPN analytics tool — describing how analysts use DISCOROUTE, BLACKPEARL, TOYGRIPPE, NKB, RONIN and GNETWORK GNOME to map target VPN networks from router configuration data, with live screenshots of DARKSUNRISE's SHADOWNET interface showing IPSec VPN connections associated with Pakistani, Afghan and other targets collected through MUSCULAR (DS-200B).
Programs: TOYGRIPPE · DISCOROUTE · BLACKPEARL · GNETWORKGNOME · NKB · RONIN · XKEYSCORE · TREASUREMAP · RENOIR · ROYALNET · GNOME · ASDF · DARKSUNRISE · SHADOWNET · WEALTHYCLUSTER · MUSCULAR · CASPORT · CUE · BLACKSAND · DANCINGOASIS · BLACKBEACH · POTLUCK · SSO · DNIPRESENTER · TNS · BLACKPEAL · ROADBED · TROPICNET · SILVERZEPHYR · SITESTORE -
VS MALIBU IKE And ESP Metadata Flows [pdf]
A TOP SECRET four-slide architecture document describing MALIBU — NSA's system for intercepting and decrypting IPSec VPN traffic at the point where it crosses monitored internet cables — showing how intercepted VPN connections are processed, cryptographic keys recovered, traffic decrypted and results delivered to analysts, with separate diagrams for metadata collection, software decryption, full exploitation and survey modes.
-
Crypt Ops Data Store User Guide [pdf]
A SECRET GCHQ user guide for the Crypt Ops Data Store — the internal task management system used by GCHQ's cryptanalytic operations division to receive, triage, assign and track decryption and cryptanalytic requests — notable for its category list which maps task types to operational programmes including BULLRUN, BEARDED PIGGY and VPN exploitation.
Marking: SECRET -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY