TURMOIL IPSEC VPN SESSIONIZATION
Open PDFDocument date: 2008-08-15
Pages: 18
Genre: manual
Banner: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, AUS, CAN, GBR, NZL
An NSA technical specification document describing how TURMOIL detects and sessionizes IPSec VPN protocol traffic — covering the six IPSec protocol stacks targeted for collection, the specific keyword and bitmask patterns used by the Atomic Event Generator to identify each packet type at wire speed, and the sessionization parameters used to group related packets into coherent sessions for downstream processing.
My notes
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
NATIONAL SECURITY AGENCY
UNITED STATES OF AMERICA
TURMOIL
TURMOIL
IPSEC VPN
SESSIONIZATION
Issue No.1...............................................................................................
Issue Date 08/15/08......................................................................................
Responsible Authority
Author : [REDACTED]
Technical P.O.C..: [REDACTED]
Product Approver.........................................................................................
DERIVED FROM: NSA/CSSM 1-52
DATED: 20041123
DECLASSIFY ON: 20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
Table of Contents
Derived From: NSA/CSSM 1-52
Dated: 20041123
DECLASSIFY On: 20291123
Revision History..........................................................................................................4
Reference Documents..................................................................................................4
1.0 (U) SCOPE............................................................................................................5
2.0 (S) ESP SESSIONIZATION...............................................................................5
2.1 (S) IP/ESP...........................................................................................................5
2.1.1 (S) Detection...........................................................................................5
2.1.2 (S) Sessionizing......................................................................................6
2.1.3 (S) The Stack..........................................................................................6
2.2 (S) IP/AH/ESP....................................................................................................7
2.2.1 (S) Detection...........................................................................................7
2.2.2 (S) Sessionizing......................................................................................7
2.2.3 (S) The Stack..........................................................................................8
3.0 (S) IKE SESSIONIZATION...............................................................................9
3.1 (U) IP/UDP/ISAKMP..........................................................................................9
3.1.1 (S) Detection...........................................................................................9
3.1.2 (S) Sessionizing......................................................................................9
3.1.3 (S) The Stack........................................................................................10
3.2 (U) IP/UDP/NULLS/ISAKMP...........................................................................10
3.2.1 (S) Detection.........................................................................................10
3.2.2 (S) Sessionizing....................................................................................11
3.2.3 (U) The Stack.......................................................................................12
3.3 (U) IP/TCP/ISAKMP.........................................................................................12
3.3.1 (S) Detection.........................................................................................12
3.3.2 (S) Sessionizing....................................................................................13
3.3.3 (S) The Stack........................................................................................14
3.4 (U) IP/TCP/NULLS/ISAKMP...........................................................................14
3.4.1 (S) Detection.........................................................................................14
3.4.2 (S) Sessionizing....................................................................................15
3.4.3 (S) The Stack........................................................................................16
4.0 (U) SUMMARY..................................................................................................17
PAGE 2 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
PAGE 3 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
REVISION HISTORY
| Issue | Date | Author | Amendments |
|---|---|---|---|
| 0.1 | 8/15/08 | ET | First draft of document |
REFERENCE DOCUMENTS
PAGE 4 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
1.0 (U) SCOPE
This document describes the sessionization requirements for the various IPSec VPN protocols processed in Turmoil. The list of IPSec protocol stacks of interest is shown here:
- IP/ESP
- IP/AH/ESP
- IP/UDP/ISAKMP
- IP/UDP/nulls/ISAKMP
- IP/TCP/ISAKMP
- IP/TCP/nulls/ISAKMP
Currently, IP/ESP, IP/UDP, and IP/TCP are successfully sessionized by the FIP. Other IPSec stacks have been observed in the field, and we have requirements to process them in Turmoil. For completeness, all of the stacks are discussed in this document, even though some are currently being processed.
2.0 (S) ESP SESSIONIZATION
2.1 (S) IP/ESP
2.1.1 (S) DETECTION
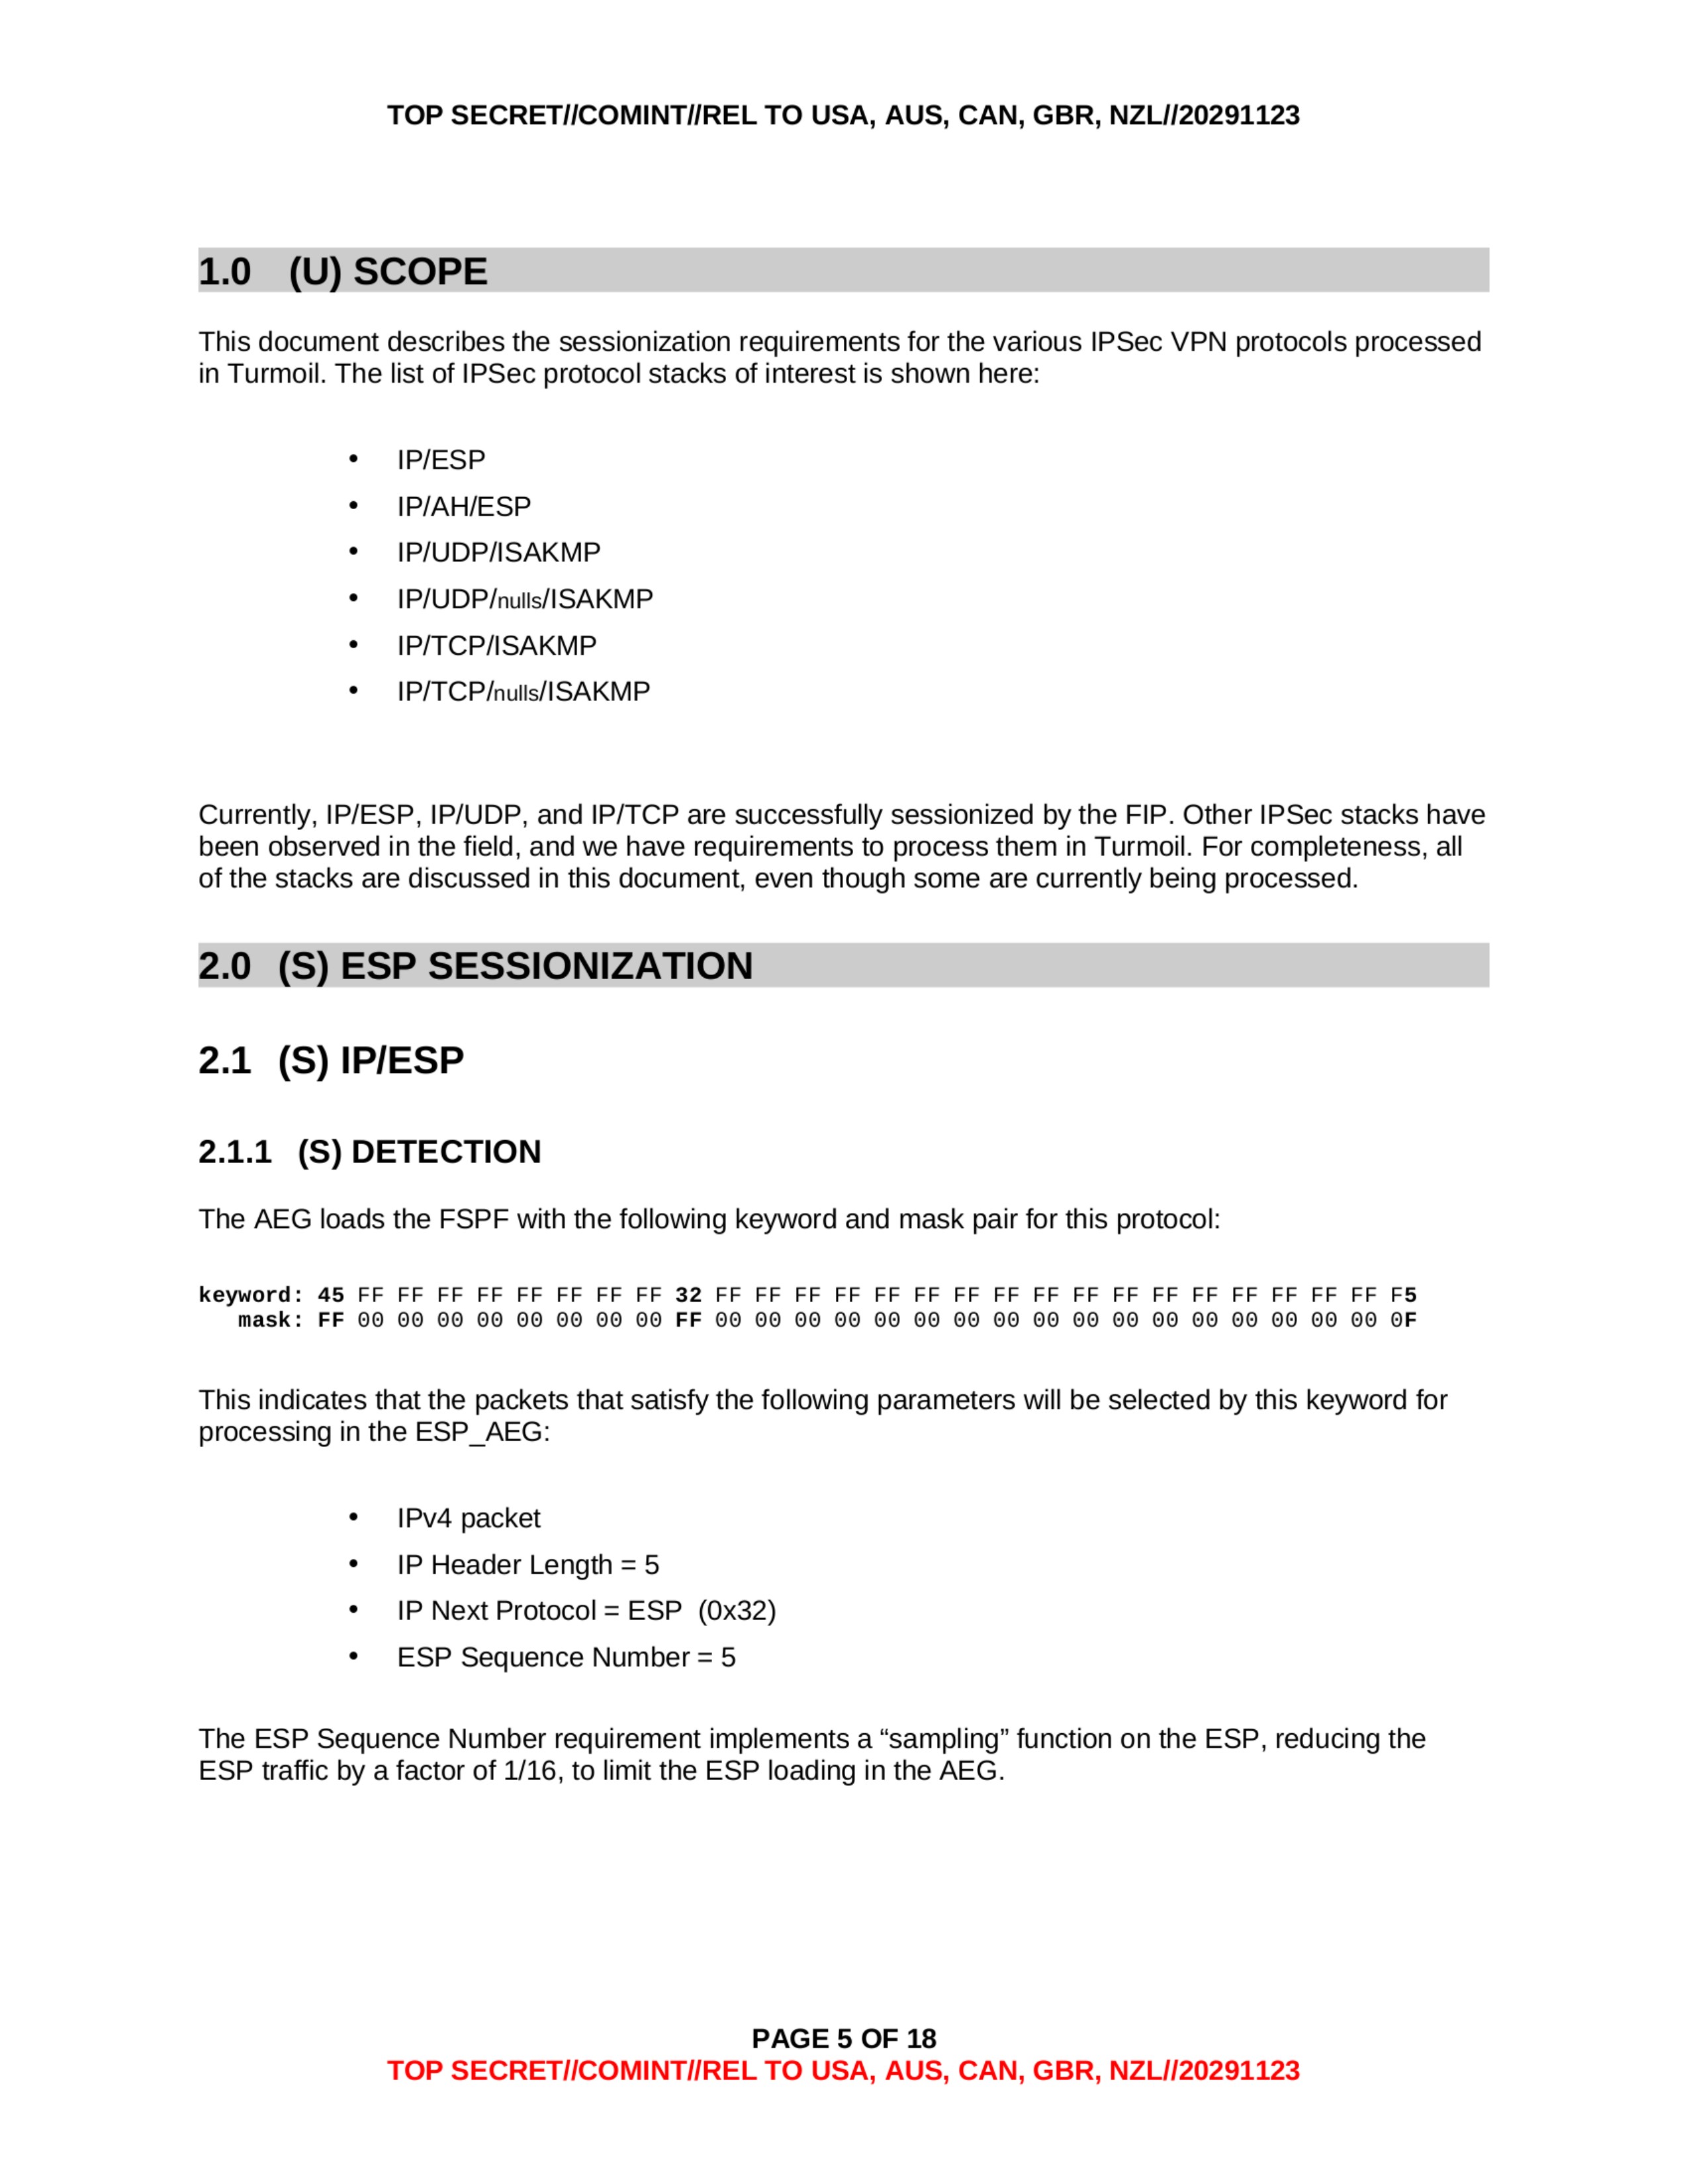
The AEG loads the FSPF with the following keyword and mask pair for this protocol:
keyword: 45 FF FF FF FF FF FF FF FF 32 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF F5
mask: FF 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 0F
This indicates that the packets that satisfy the following parameters will be selected by this keyword for processing in the ESP_AEG:
- IPv4 packet
- IP Header Length = 5
- IP Next Protocol = ESP (0x32)
- ESP Sequence Number = 5
The ESP Sequence Number requirement implements a "sampling" function on the ESP, reducing the ESP traffic by a factor of 1/16, to limit the ESP loading in the AEG.
PAGE 5 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
2.1.2 (S) SESSIONIZING
The ESP packets would be sessionized by the following set of parameters:
- IP Next Protocol = 50 (0x32)
- IP Source Address
- IP Destination Address
- ESP Spi
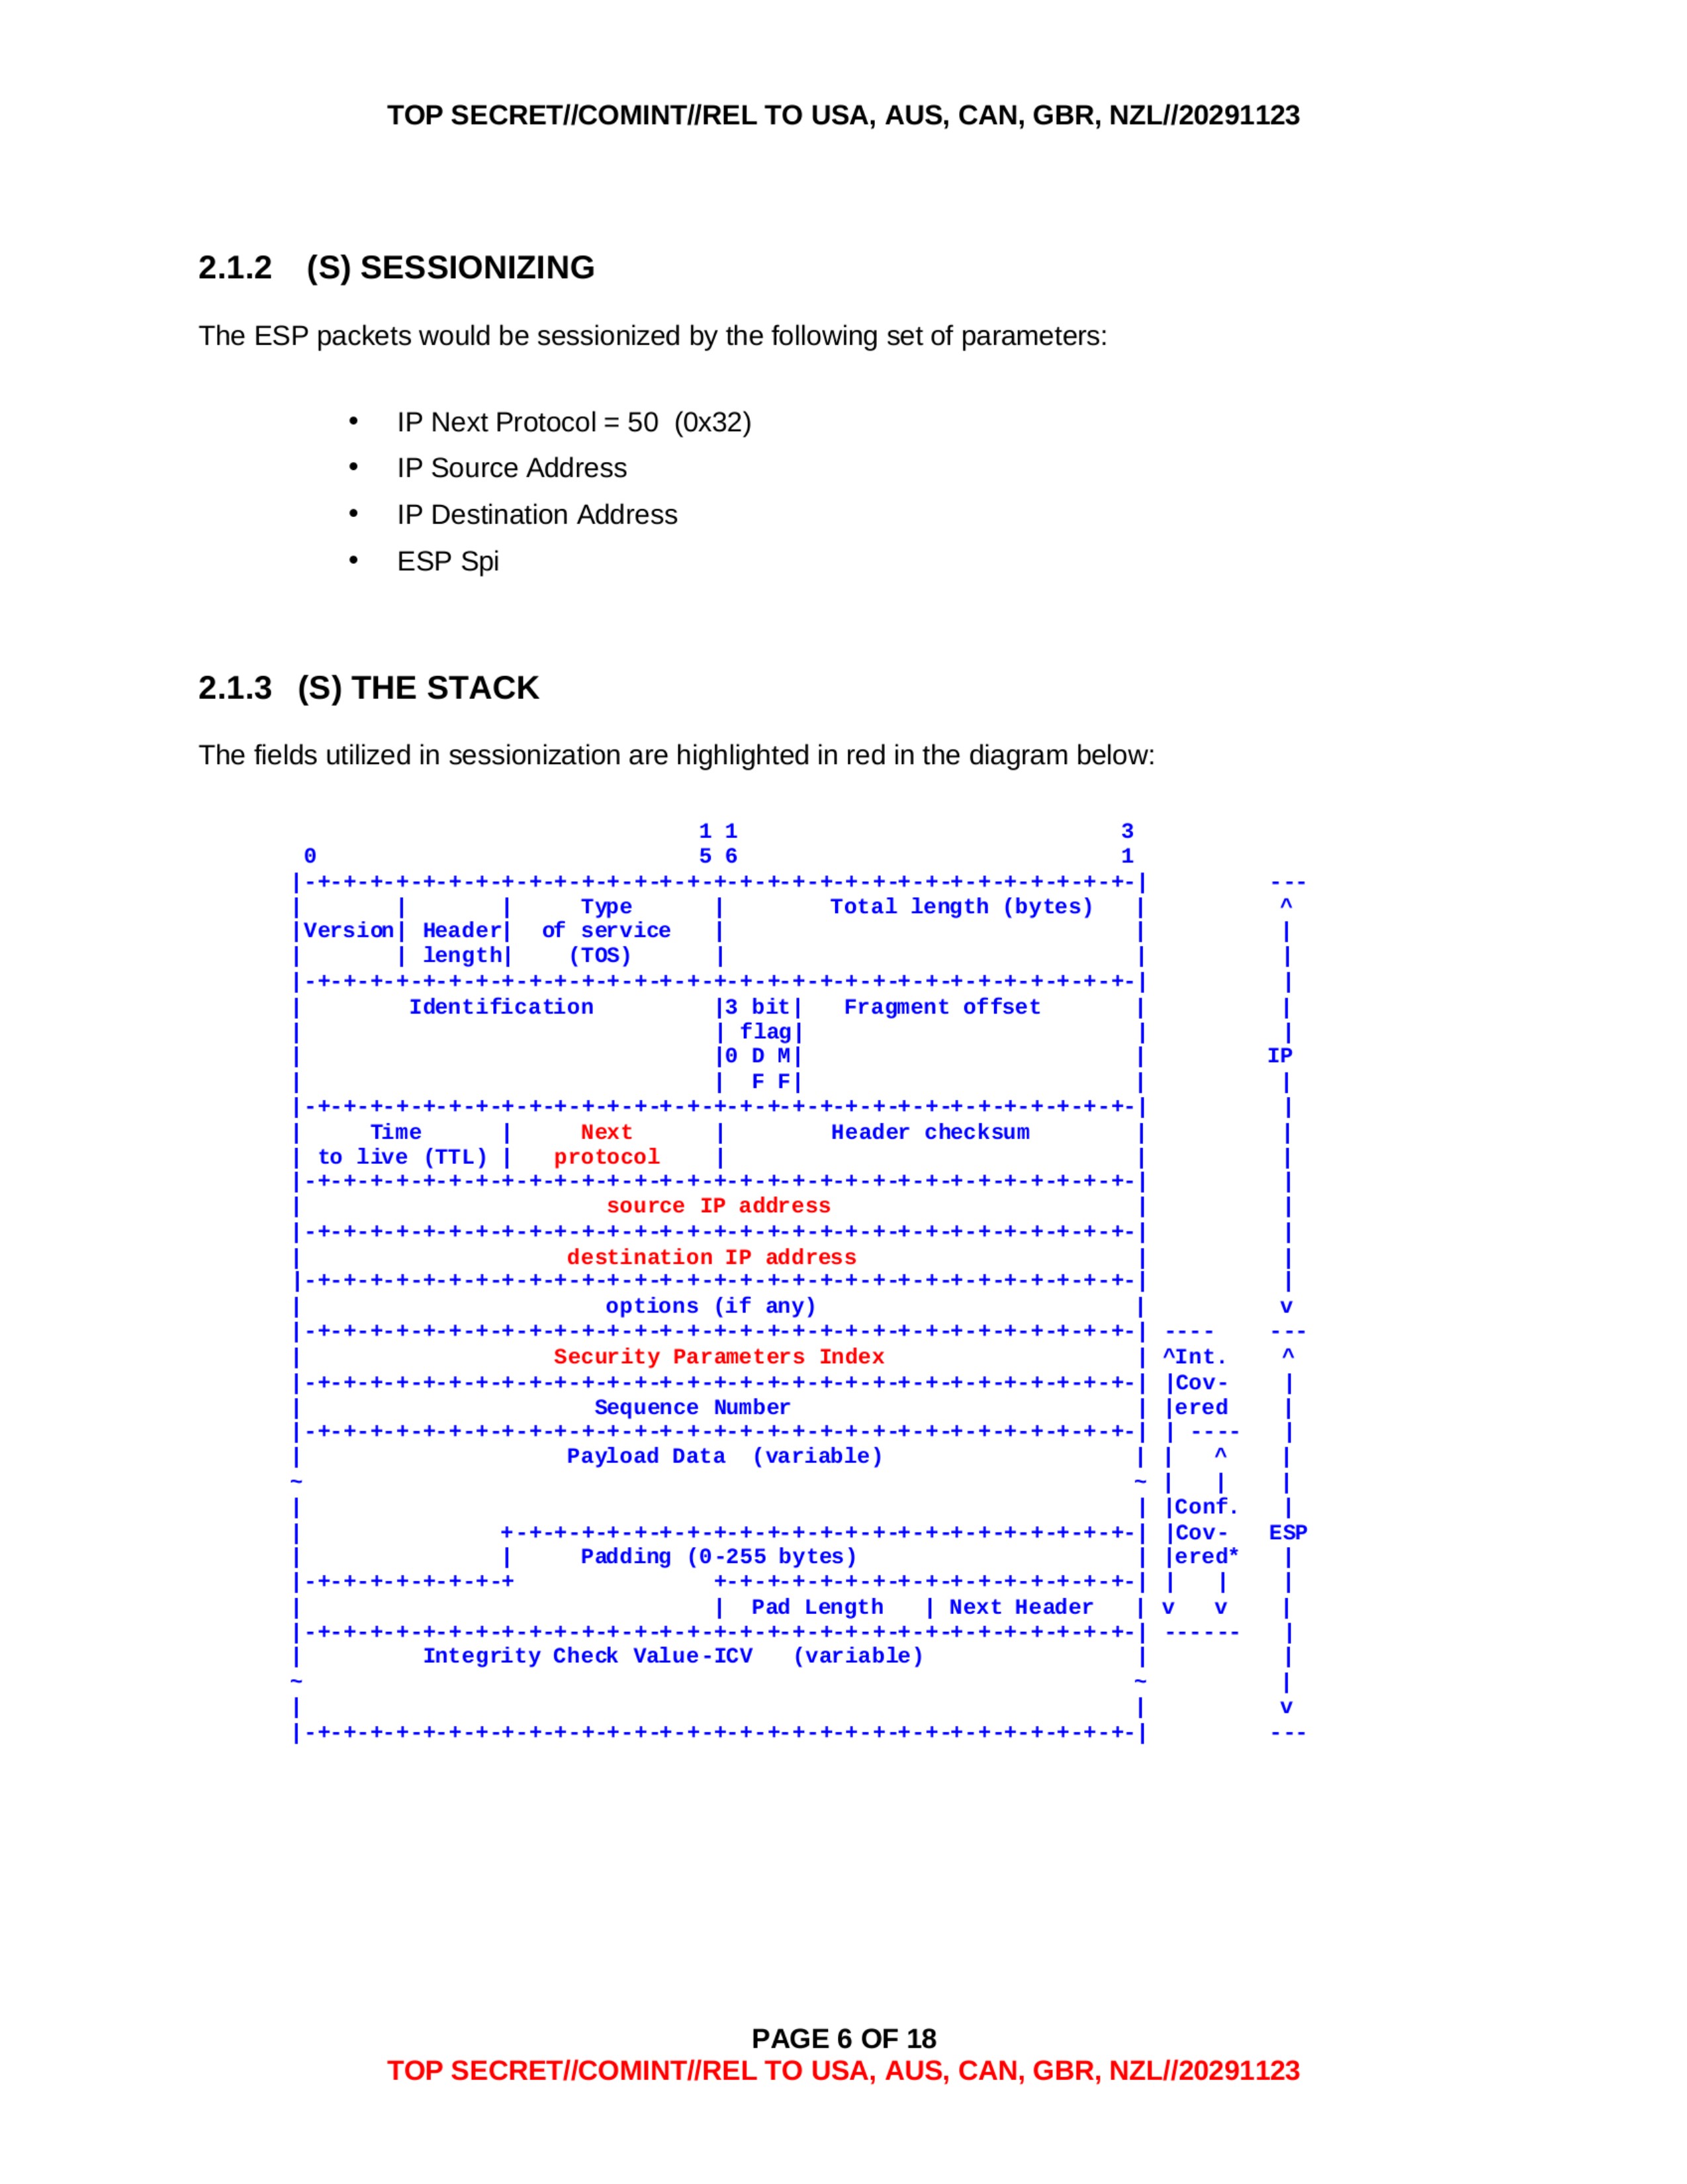
2.1.3 (S) THE STACK
The fields utilized in sessionization are highlighted in red in the diagram below.
0                               1 1                             3
                                5 6                             1

|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|          ---
|Version| Header|  Type         |                               |           ^
|       | length| of service    |      Total length (bytes)     |           |
|       |       | (TOS)         |                               |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                               |3 bit|                         |           |
|        Identification         | flag|    Fragment offset      |           |
|                               |0 D M|                         |          IP
|                               |  F F|                         |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|    Time       |     Next      |                               |           |
| to live (TTL) |   protocol    |       Header checksum         |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                       source IP address                       |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                    destination IP address                     |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                        options (if any)                       |           v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| ----     ---
|                  Security Parameters Index                    | ^Int.     ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| |Cov      |
|                       Sequence Number                         | |ered     |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| | ----    |
|                                                               | |    ^    |
~                  Payload Data  (variable)                     ~ |    |    |
|                                                               | |Conf.    |
|       +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| | Cov-   ESP
|       |                  Padding (0-255 bytes)                | |ered*    |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| |   |     |
|                               |  Pad Length   | Next Header   | v   v     |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| ------    |
|                                                               |           |
~               Integrity Check Value-ICV  (variable)           ~           |
|                                                               |           v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|          ---
PAGE 6 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
2.2 (S) IP/AH/ESP
2.2.1 (S) DETECTION
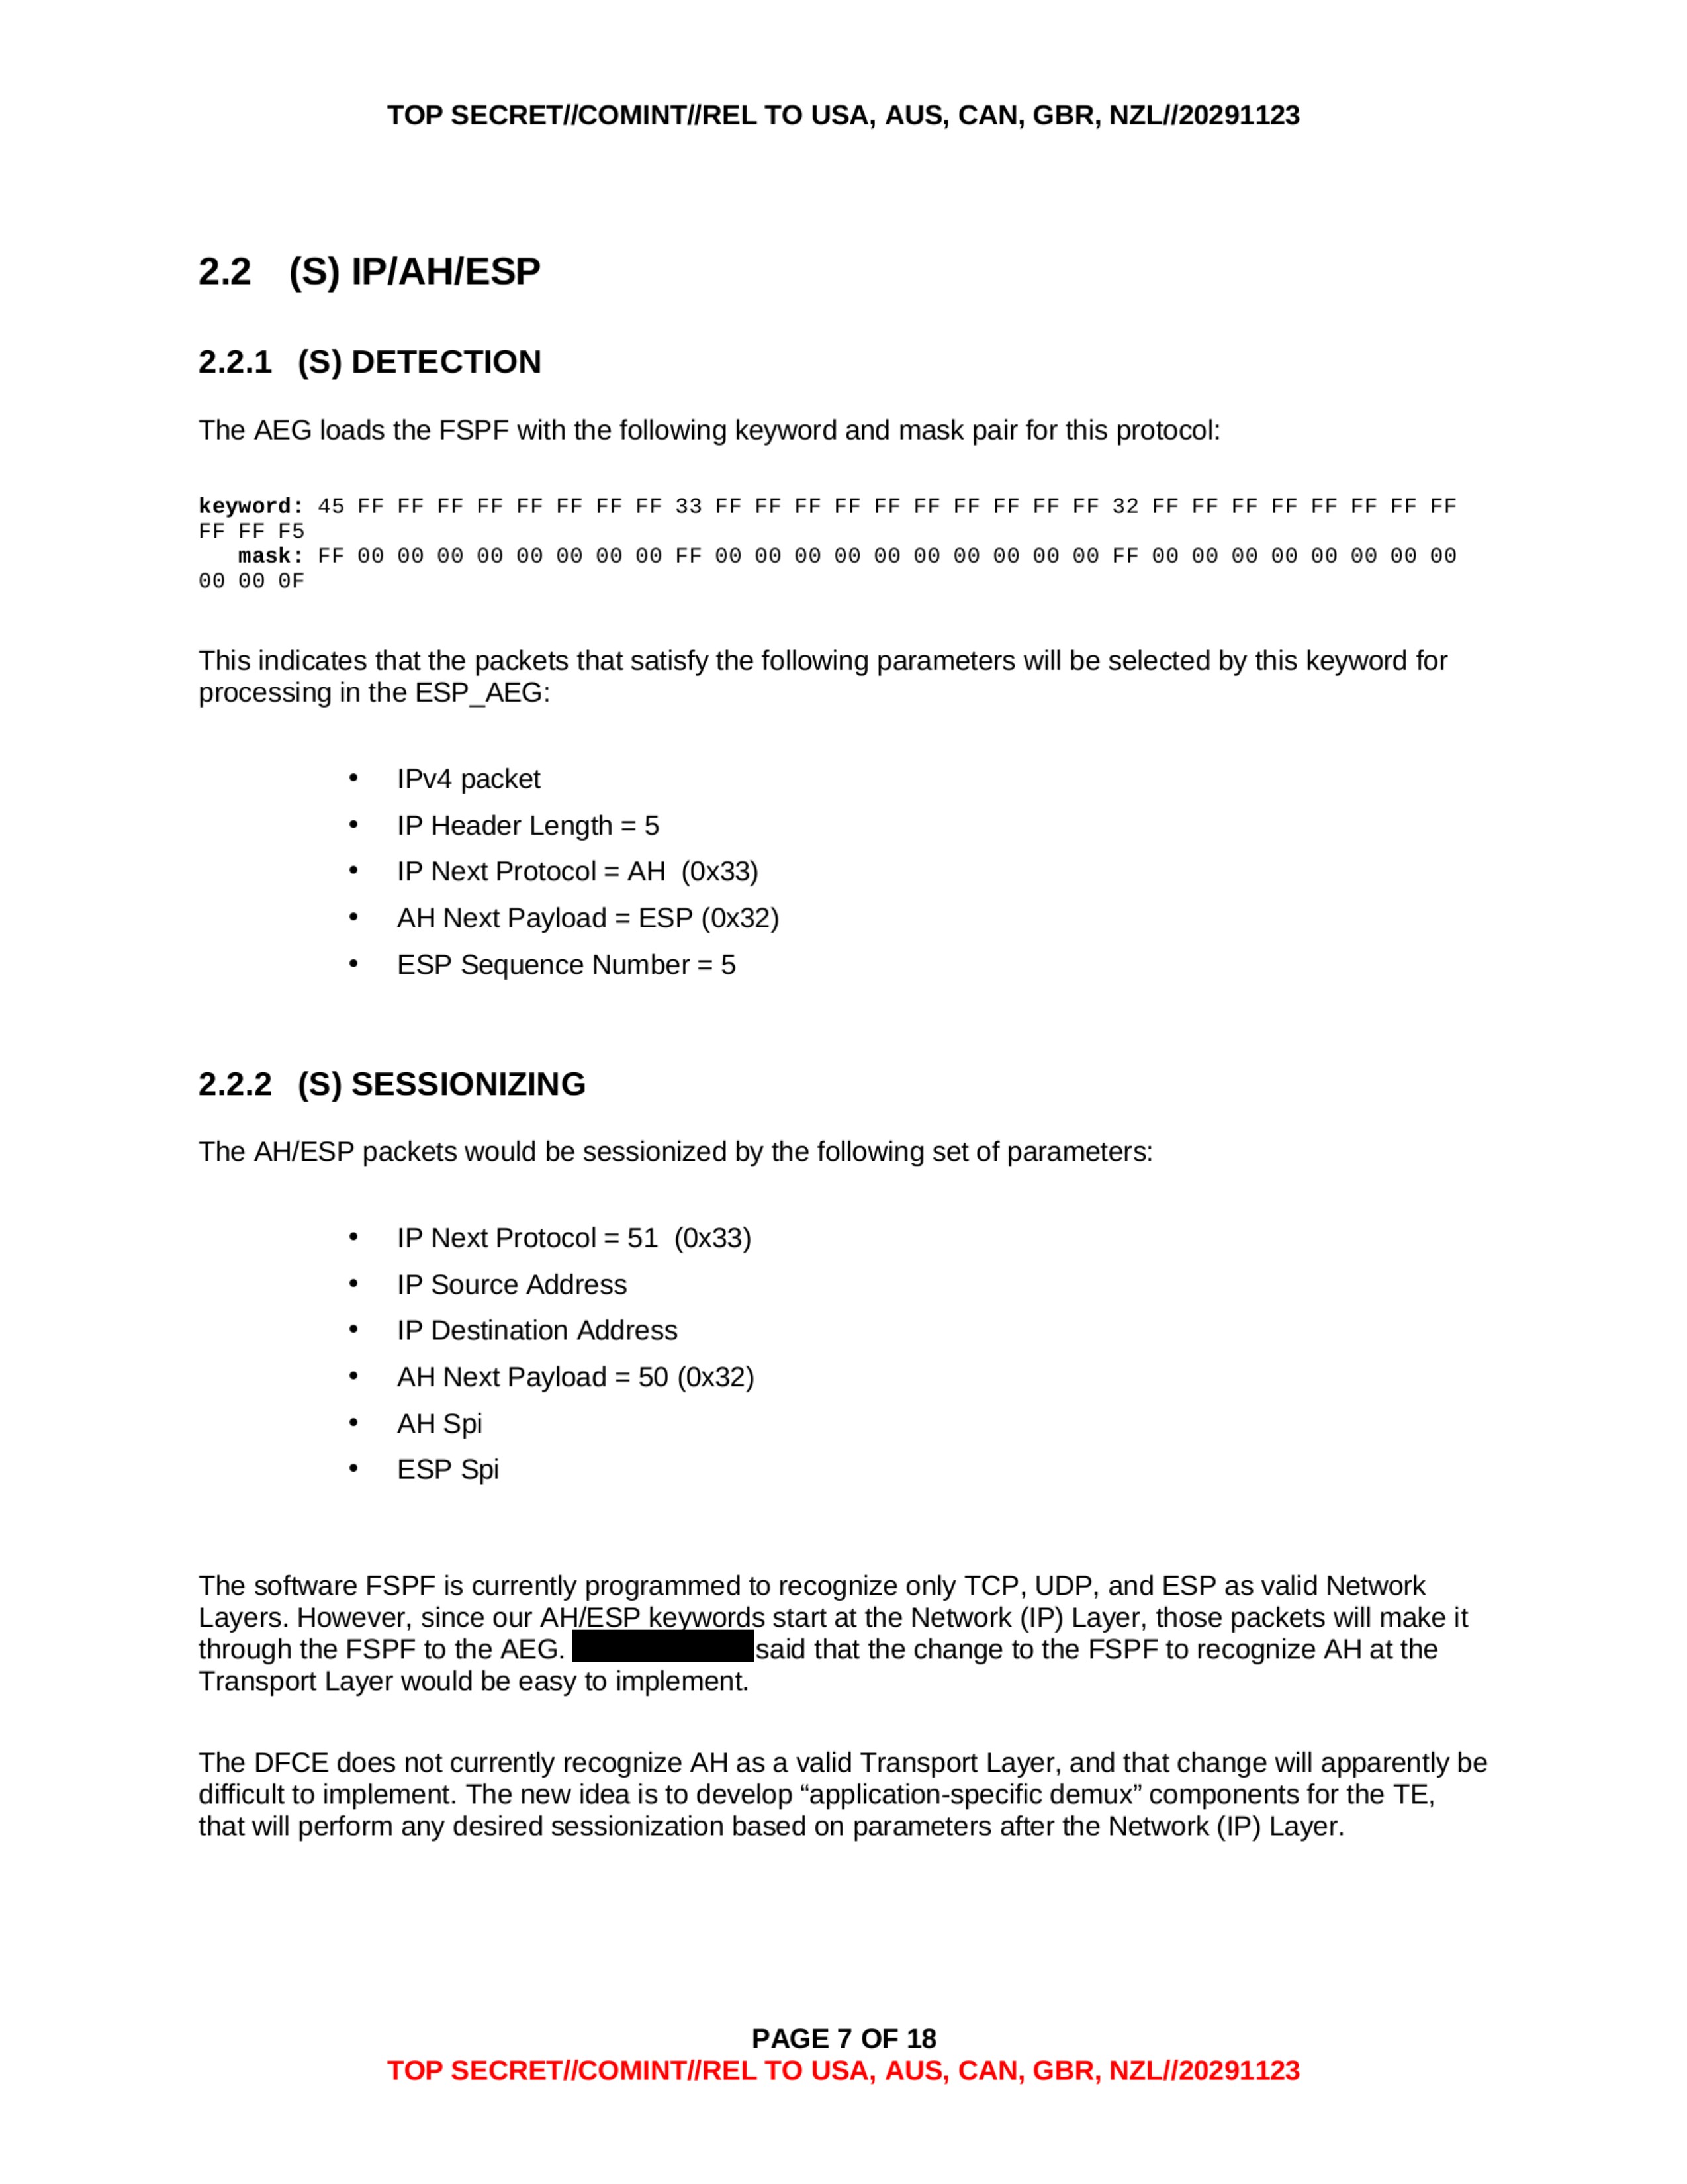
The AEG loads the FSPF with the following keyword and mask pair for this protocol:
keyword: 45 FF FF FF FF FF FF FF FF 33 FF FF FF FF FF FF FF FF FF FF 32 FF FF FF FF FF FF FF FF
FF FF F5
mask: FF 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00
00 00 0F
This indicates that the packets that satisfy the following parameters will be selected by this keyword for processing in the ESP_AEG:
- IPv4 packet
- IP Header Length = 5
- IP Next Protocol = AH (0x33)
- AH Next Payload = ESP (0x32)
- ESP Sequence Number = 5
2.2.2 (S) SESSIONIZING
The AH/ESP packets would be sessionized by the following set of parameters:
- IP Next Protocol = 51 (0x33)
- IP Source Address
- IP Destination Address
- AH Next Payload = 50 (0x32)
- AH Spi
- ESP Spi
The software FSPF is currently programmed to recognize only TCP, UDP, and ESP as valid Network Layers. However, since our AH/ESP keywords start at the Network (IP) Layer, those packets will make it through the FSPF to the AEG. [REDACTED] said that the change to the FSPF to recognize AH at the Transport Layer would be easy to implement.
The DFCE does not currently recognize AH as a valid Transport Layer, and that change will apparently be difficult to implement. The new idea is to develop "application-specific demux" components for the TE, that will perform any desired sessionization based on parameters after the Network (IP) Layer.
PAGE 7 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
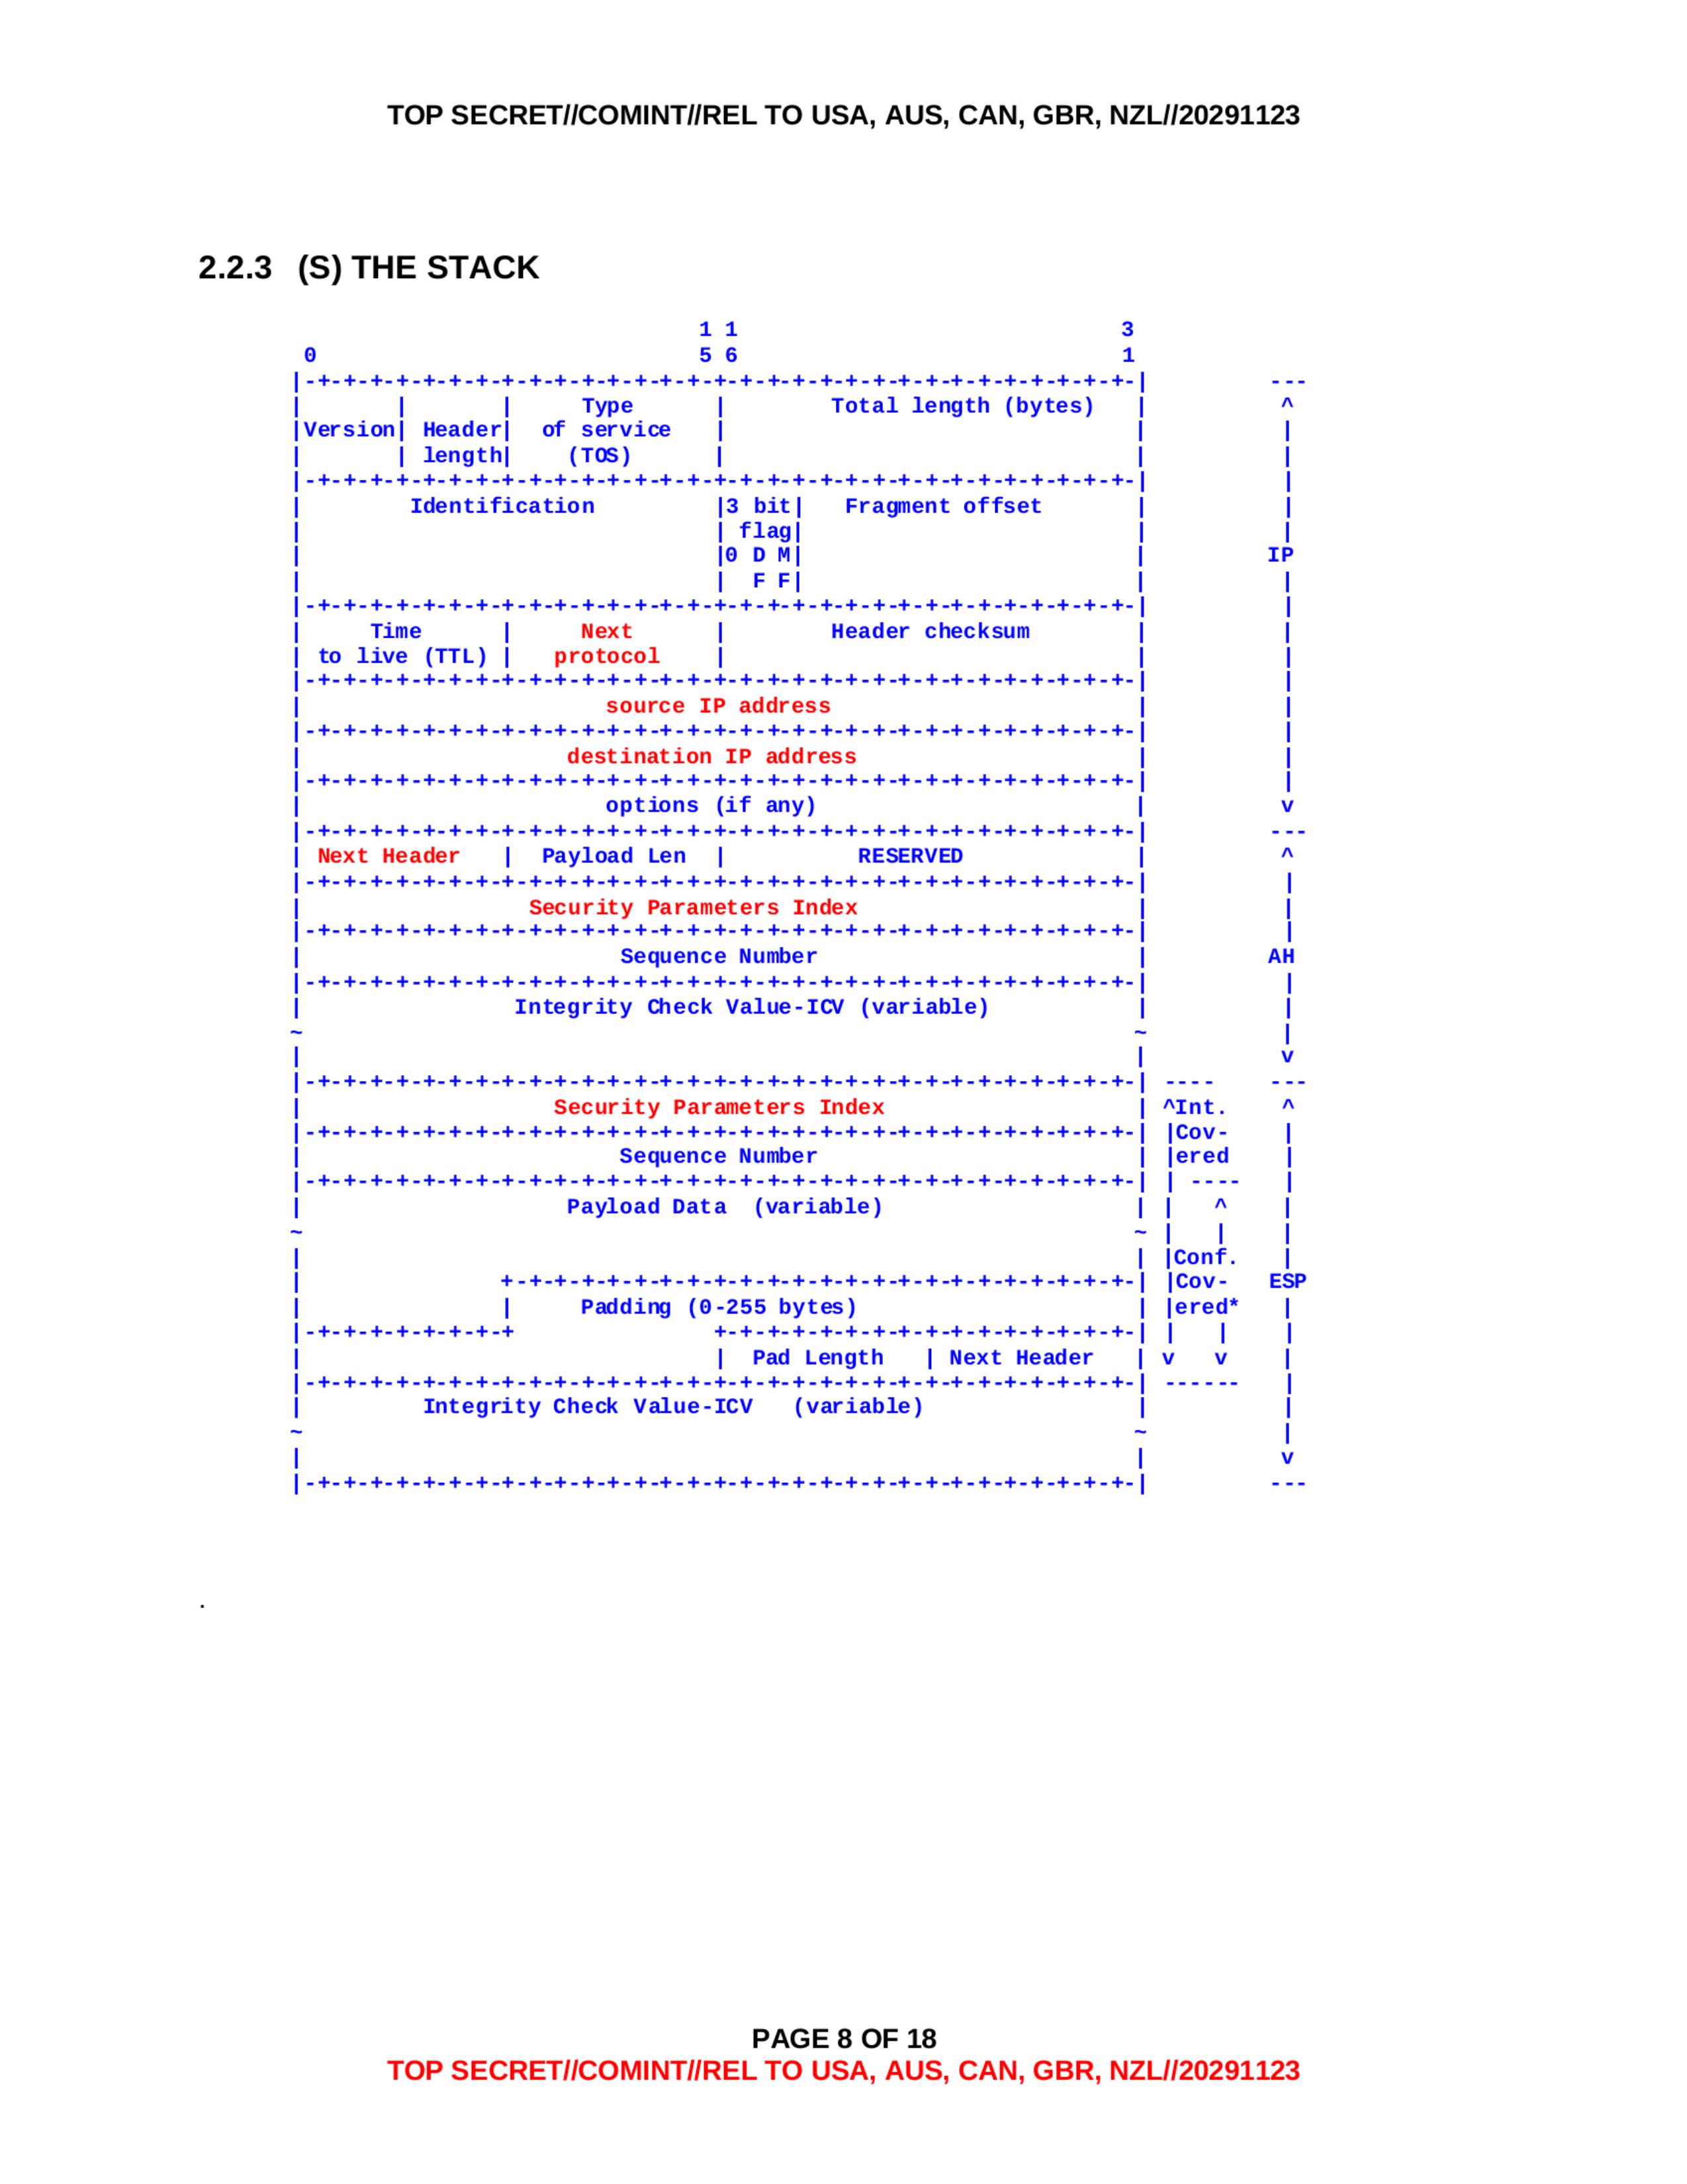
2.2.3 (S) THE STACK
0                               1 1                             3
                                5 6                             1
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|          ---
|Version| Header|     Type      |                               |           ^
|       | length| of service    |      Total length (bytes)     |           |
|       |       | (TOS)         |                               |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                               |3 bit|                         |           |
|        Identification         | flag|    Fragment offset      |           |
|                               |0 D M|                         |          IP
|                               |  F F|                         |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|    Time       |     Next      |                               |           |
| to live (TTL) |   protocol    |       Header checksum         |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                       source IP address                       |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                    destination IP address                     |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                        options (if any)                       |           v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|          ---
|  Next Header  |  Payload Len  |            RESERVED           |           ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                  Security Parameters Index                    |           |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                       Sequence Number                         |          AH
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|           |
|                                                               |           |
~              Integrity Check Value-ICV (variable)             ~           |
|                                                               |           v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| ----     ---
|                  Security Parameters Index                    | ^Int.     ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| |Cov-     |
|                       Sequence Number                         | |ered*    |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| | ----    |
|                                                               | |   ^     |
~                  Payload Data  (variable)                     ~ |   |     |
|                                                               | |Conf.    |
|       +-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| |Cov-    ESP
|       |                  Padding (0-255 bytes)                | |ered*    |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| |   |     |
|                               |  Pad Length   | Next Header   | v   v     |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-| ------    |
|                                                               |           |
~               Integrity Check Value-ICV  (variable)           ~           |
|                                                               |           v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|          ---
PAGE 8 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
3.0 (S) IKE SESSIONIZATION
3.1 (U) IP/UDP/ISAKMP
3.1.1 (S) DETECTION
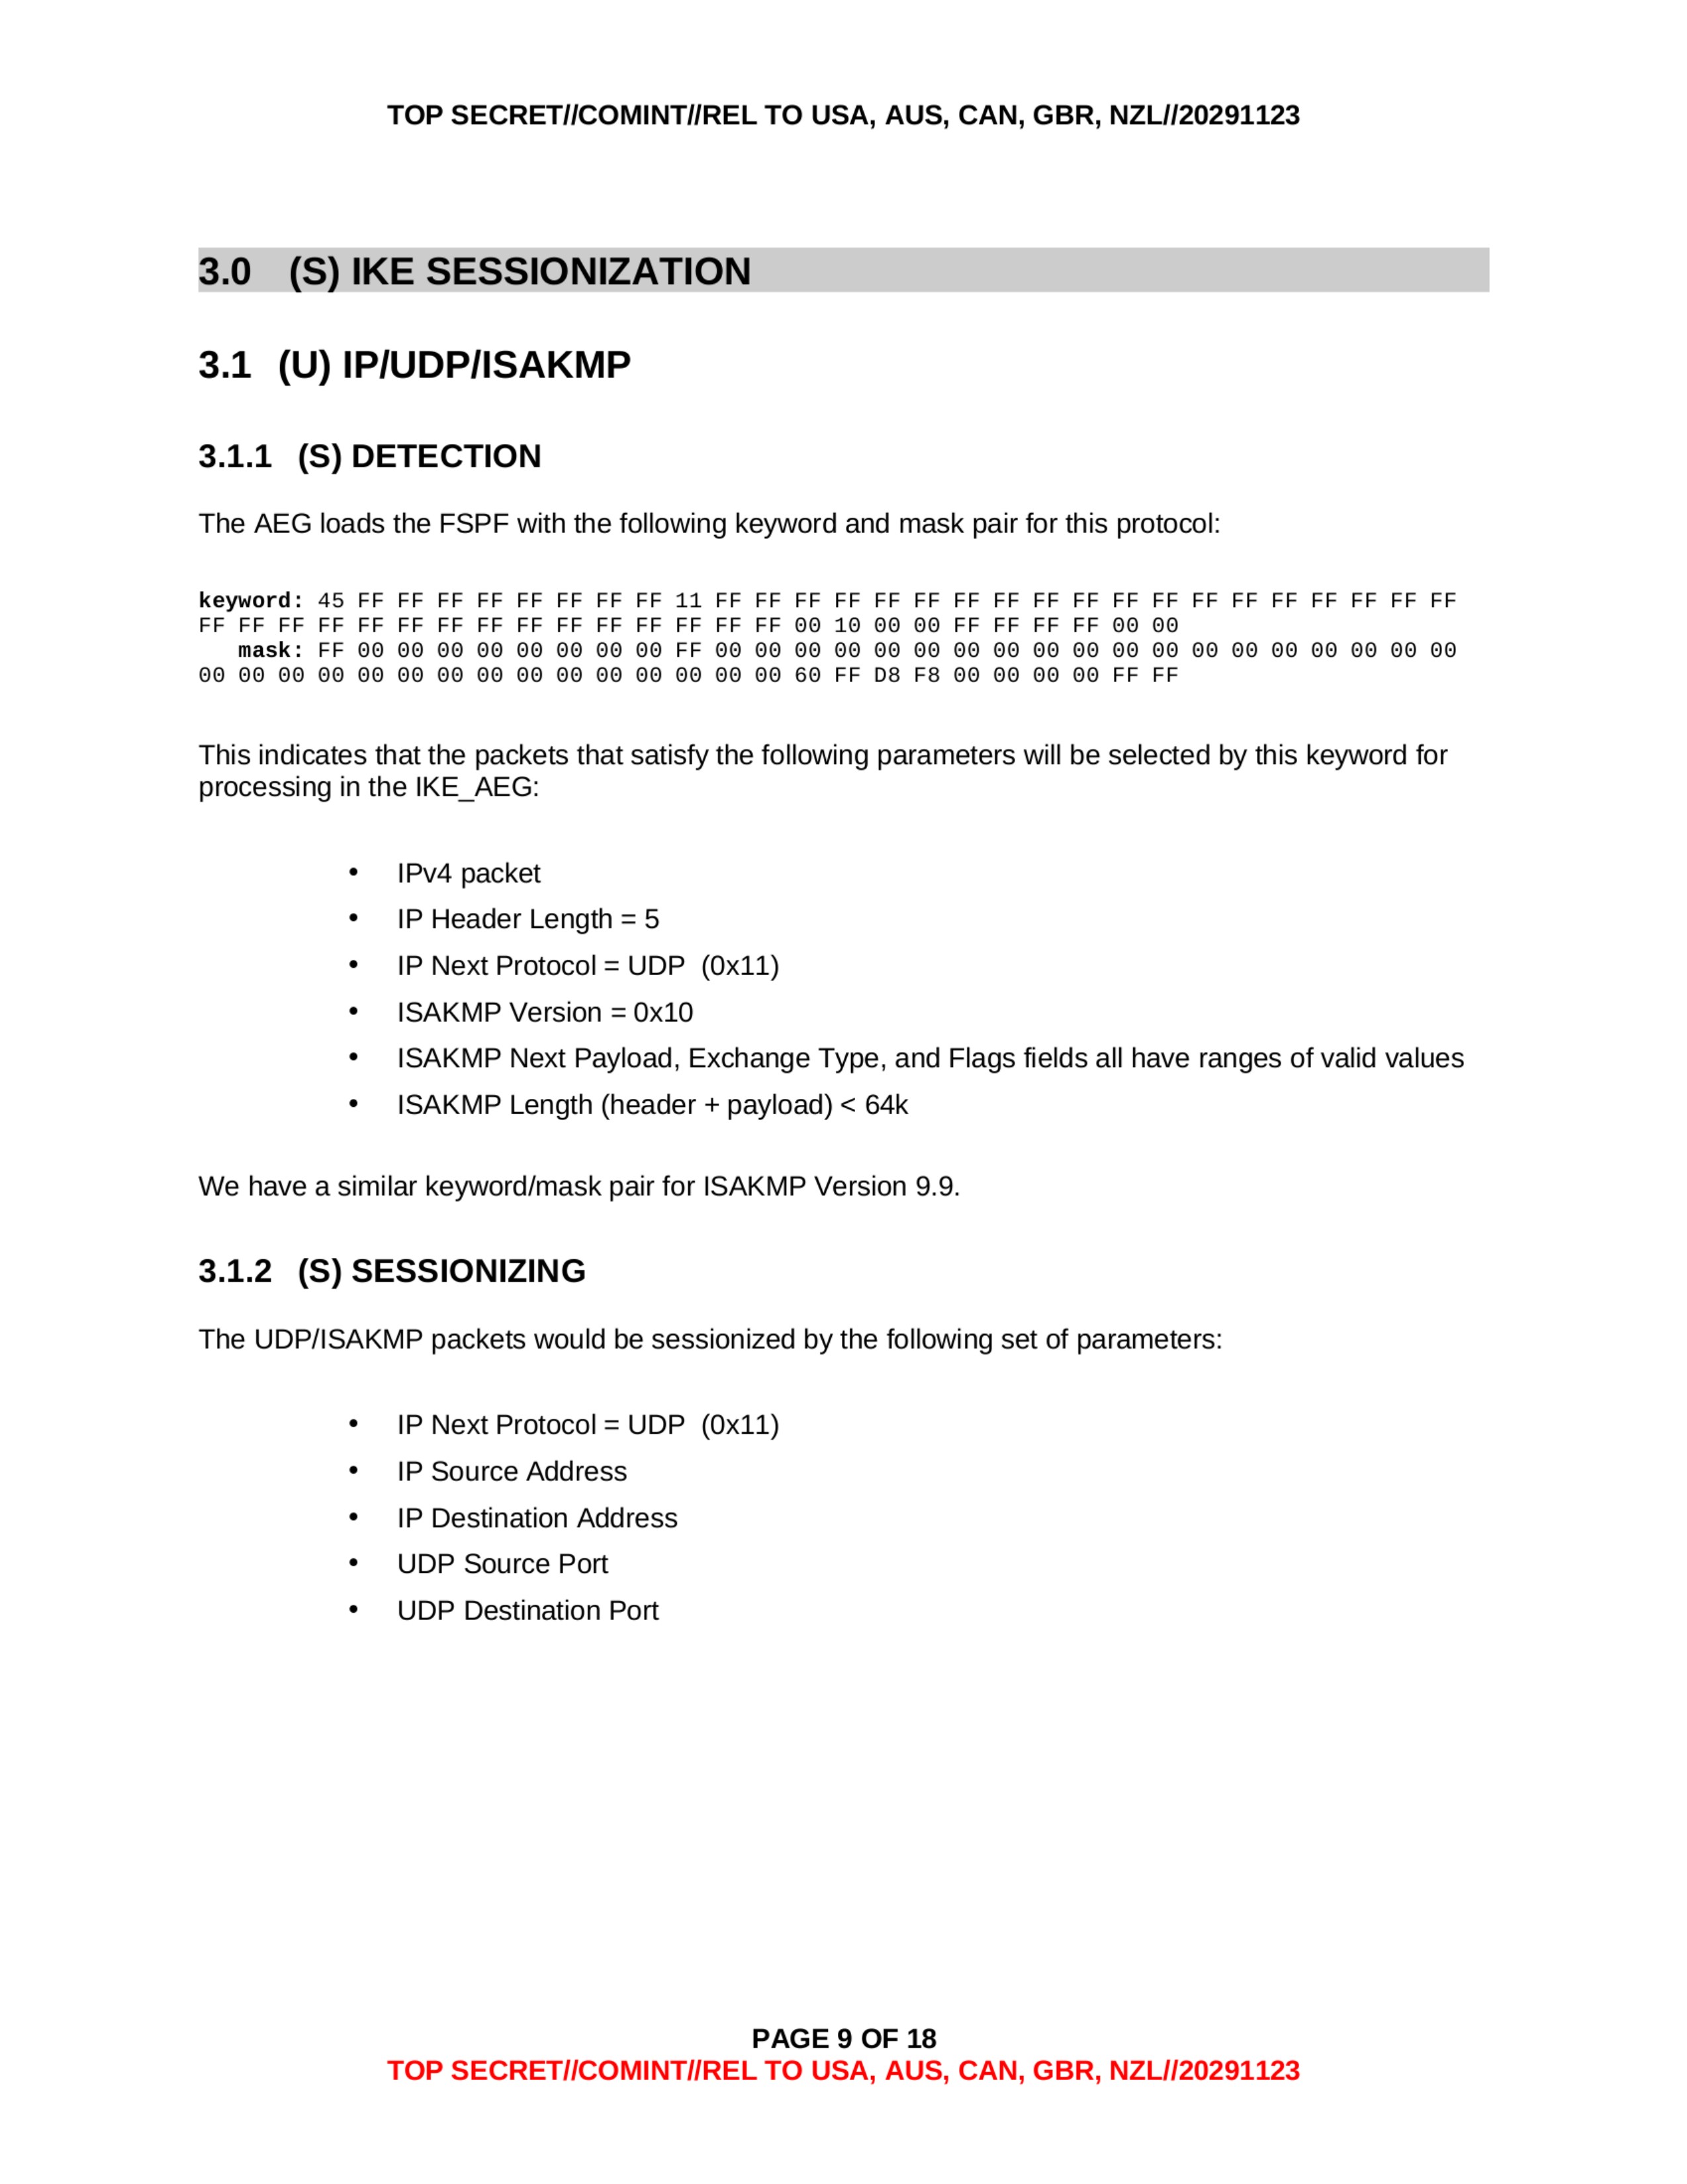
The AEG loads the FSPF with the following keyword and mask pair for this protocol:
keyword: 45 FF FF FF FF FF FF FF FF 11 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF
FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF 00 10 00 00 FF FF FF FF 00 00
mask: FF 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00
00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 60 FF D8 F8 00 00 00 00 FF FF
This indicates that the packets that satisfy the following parameters will be selected by this keyword for processing in the IKE_AEG:
- IPv4 packet
- IP Header Length = 5
- IP Next Protocol = UDP (0x11)
- ISAKMP Version = 0x10
- ISAKMP Next Payload, Exchange Type, and Flags fields all have ranges of valid values
- ISAKMP Length (header + payload) < 64k
We have a similar keyword/mask pair for ISAKMP Version 9.9.
3.1.2 (S) SESSIONIZING
The UDP/ISAKMP packets would be sessionized by the following set of parameters:
- IP Next Protocol = UDP (0x11)
- IP Source Address
- IP Destination Address
- UDP Source Port
- UDP Destination Port
PAGE 9 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
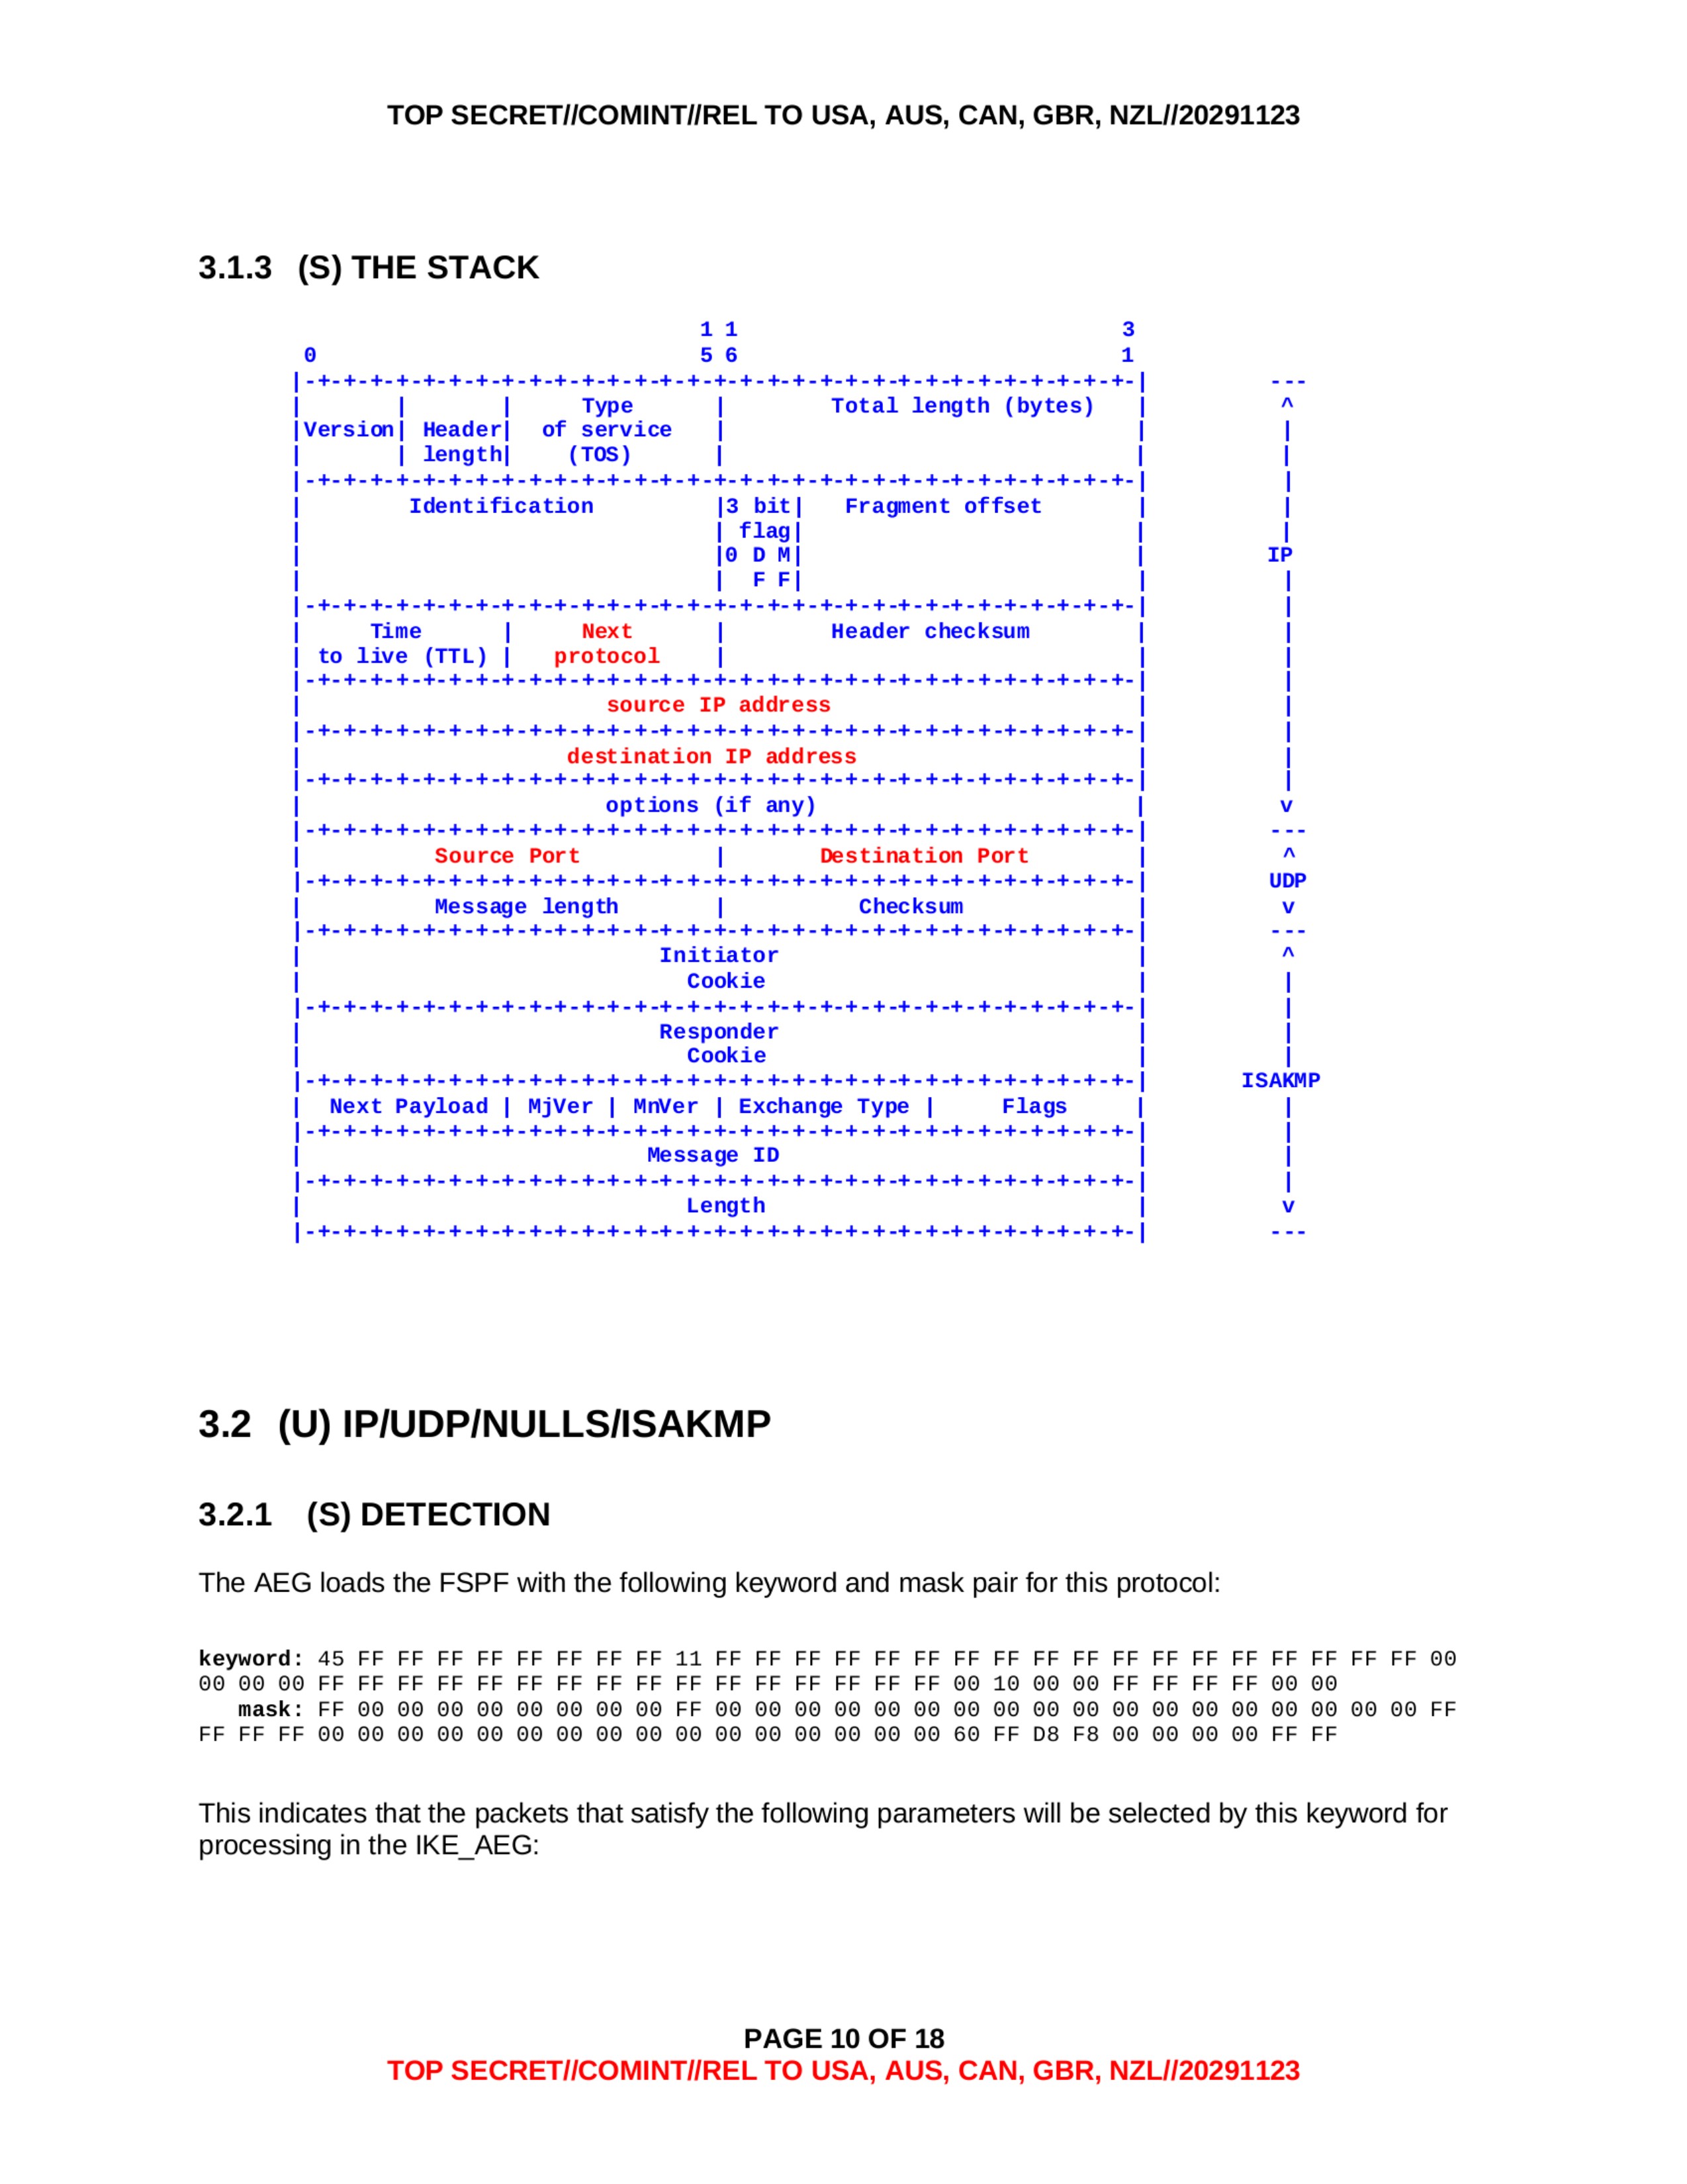
3.1.3 (S) THE STACK
0                               1 1                             3
                                5 6                             1
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        ---
|Version| Header|     Type      |                               |         ^
|       | length| of service    |      Total length (bytes)     |         |
|       |       | (TOS)         |                               |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                               |3 bit|                         |         |
|        Identification         | flag|    Fragment offset      |         |
|                               |0 D M|                         |        IP
|                               |  F F|                         |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|    Time       |     Next      |                               |         |
| to live (TTL) |   protocol    |       Header checksum         |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                       source IP address                       |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                    destination IP address                     |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                        options (if any)                       |         v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        ---
|          Source Port          |        Destination Port       |         ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        UDP
|          Message length       |            Checksum           |         v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        ---
|                          Initiator                            |         ^
|                           Cookie                              |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                          Responder                            |         |
|                           Cookie                              |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|      ISAKMP
| Next Payload  | MjVer | MnVer | Exchange Type |     Flags     |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                          Message ID                           |         |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|         |
|                            Length                             |         v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        ---
3.2 (U) IP/UDP/NULLS/ISAKMP
3.2.1 (S) DETECTION
The AEG loads the FSPF with the following keyword and mask pair for this protocol:
keyword: 45 FF FF FF FF FF FF FF FF 11 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF 00
00 00 00 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF 00 10 00 00 FF FF FF FF 00 00
mask: FF 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 FF
FF FF FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 60 FF D8 F8 00 00 00 00 FF FF
This indicates that the packets that satisfy the following parameters will be selected by this keyword for processing in the IKE_AEG:
PAGE 10 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
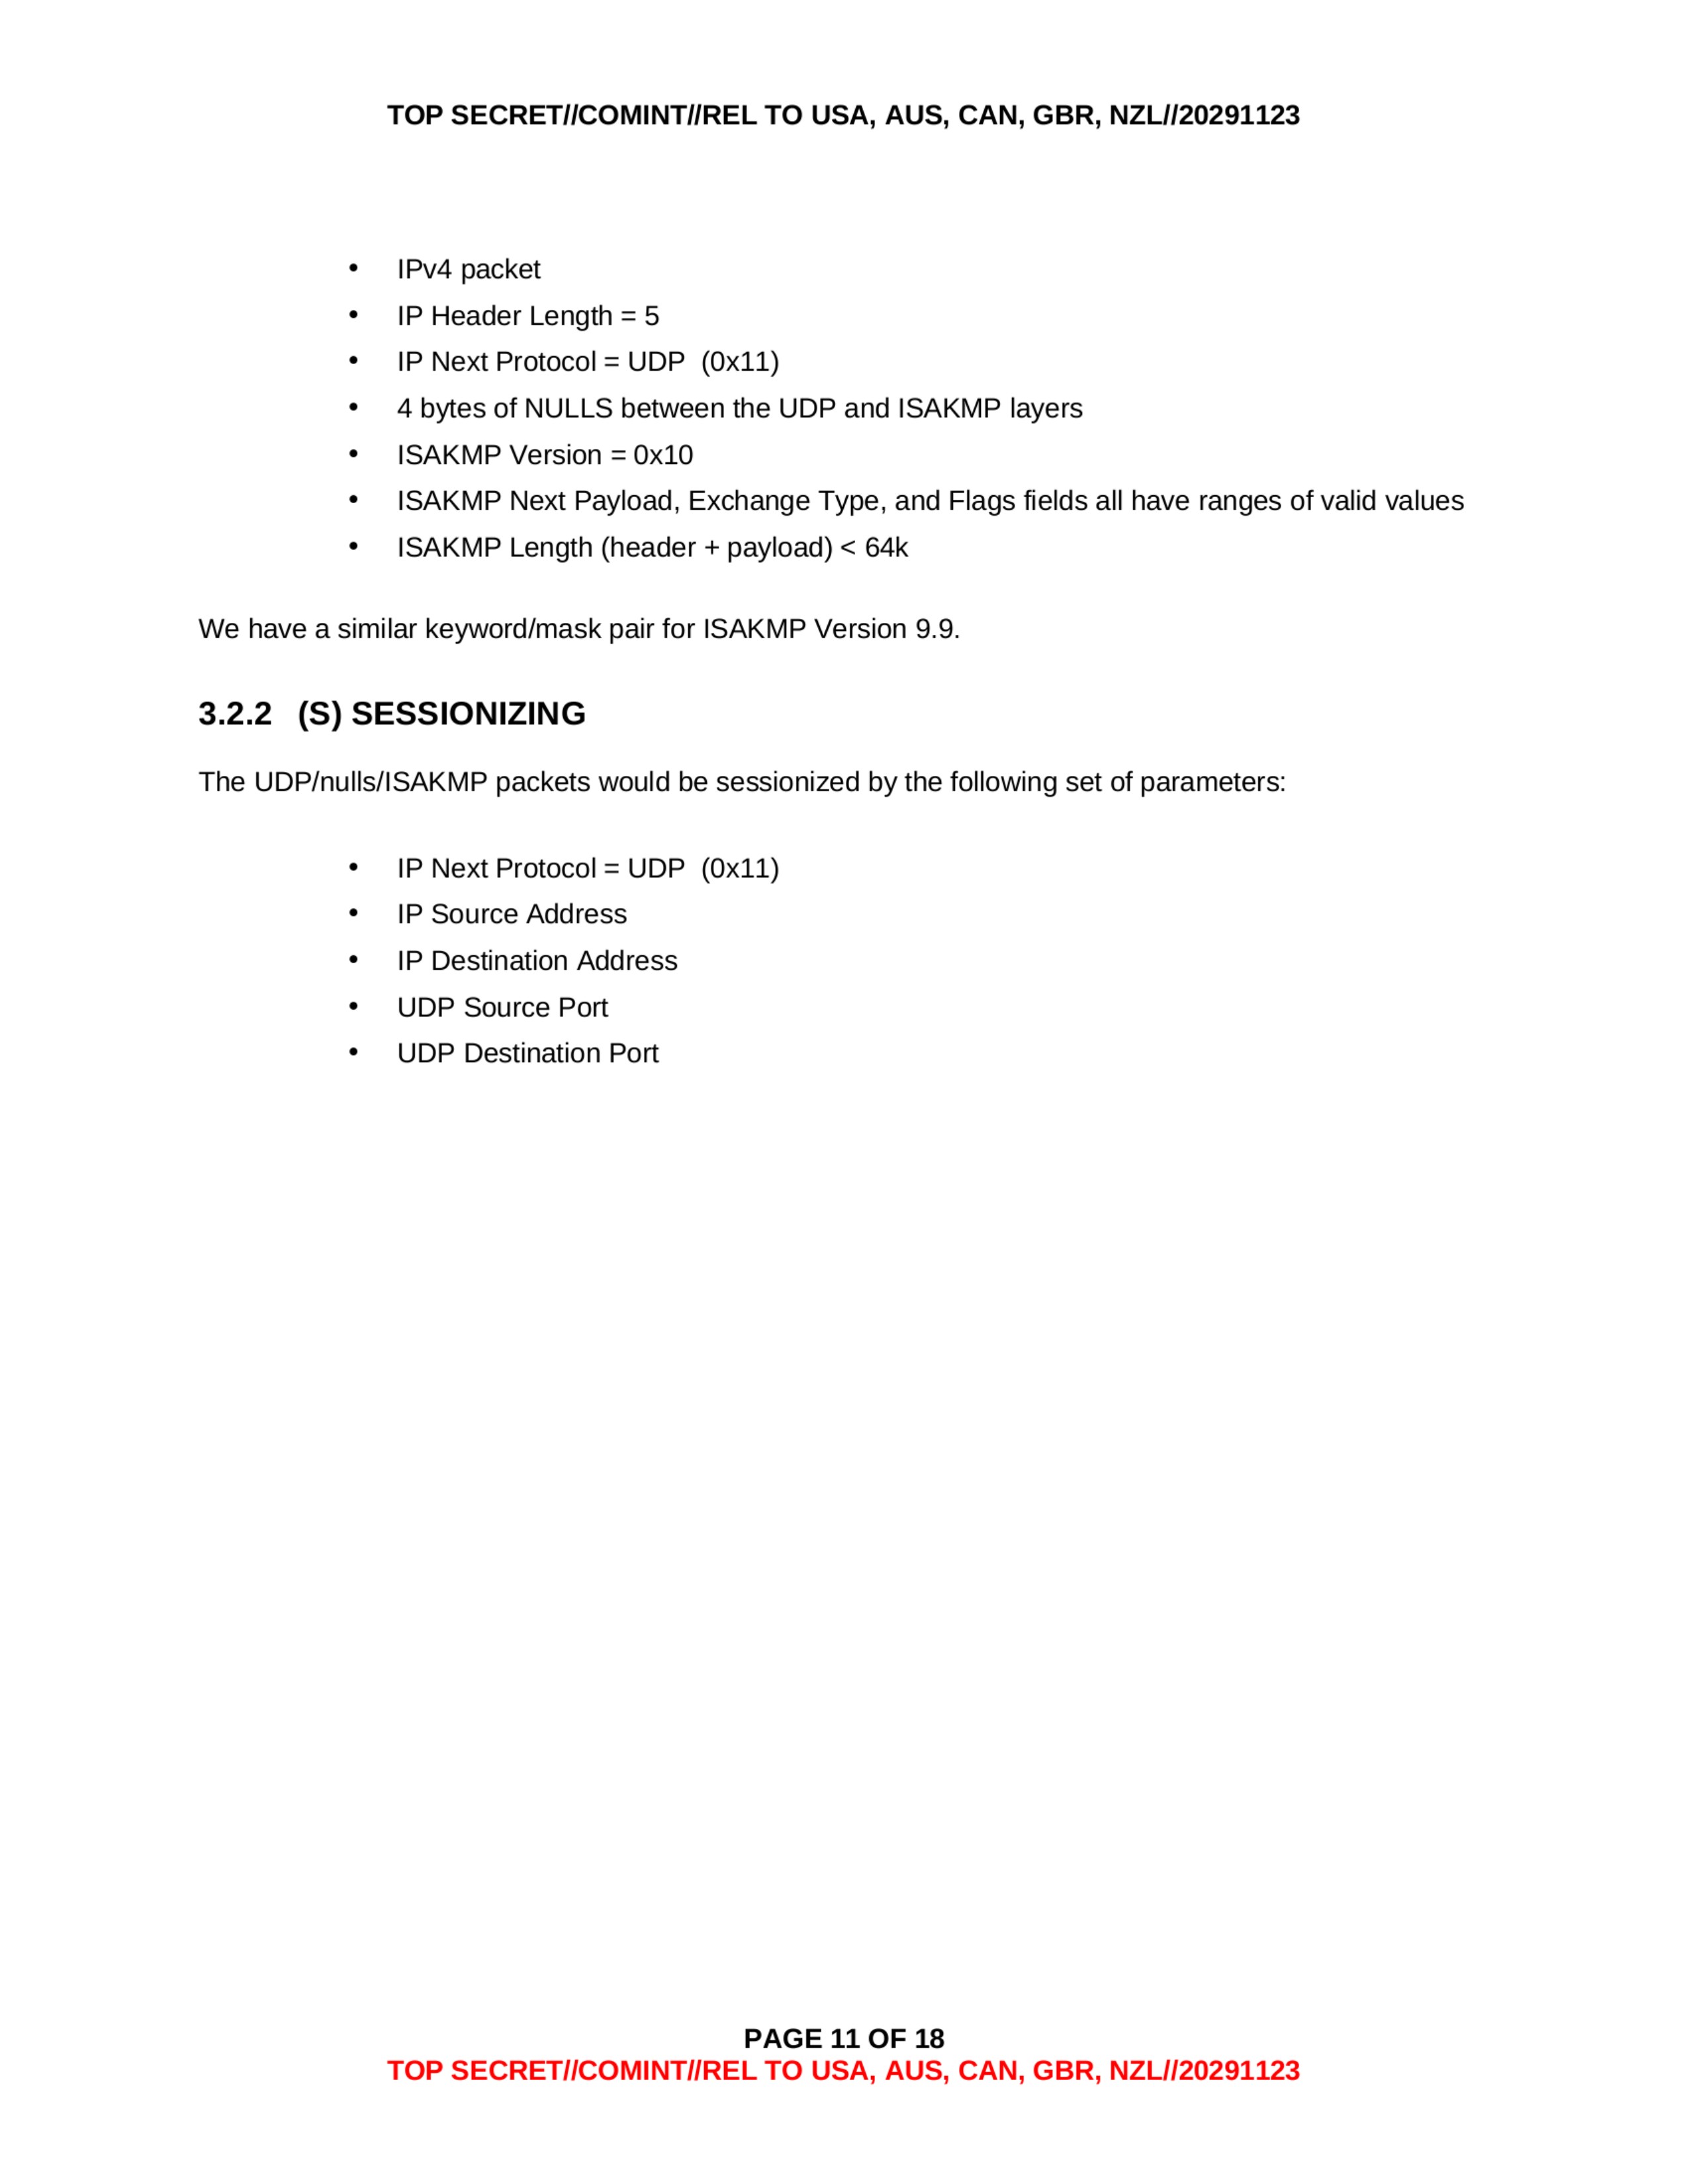
- IPv4 packet
- IP Header Length = 5
- IP Next Protocol = UDP (0x11)
- 4 bytes of NULLS between the UDP and ISAKMP layers
- ISAKMP Version = 0x10
- ISAKMP Next Payload, Exchange Type, and Flags fields all have ranges of valid values
- ISAKMP Length (header + payload) < 64k
We have a similar keyword/mask pair for ISAKMP Version 9.9.
3.2.2 (S) SESSIONIZING
The UDP/nulls/ISAKMP packets would be sessionized by the following set of parameters:
- IP Next Protocol = UDP (0x11)
- IP Source Address
- IP Destination Address
- UDP Source Port
- UDP Destination Port
PAGE 11 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
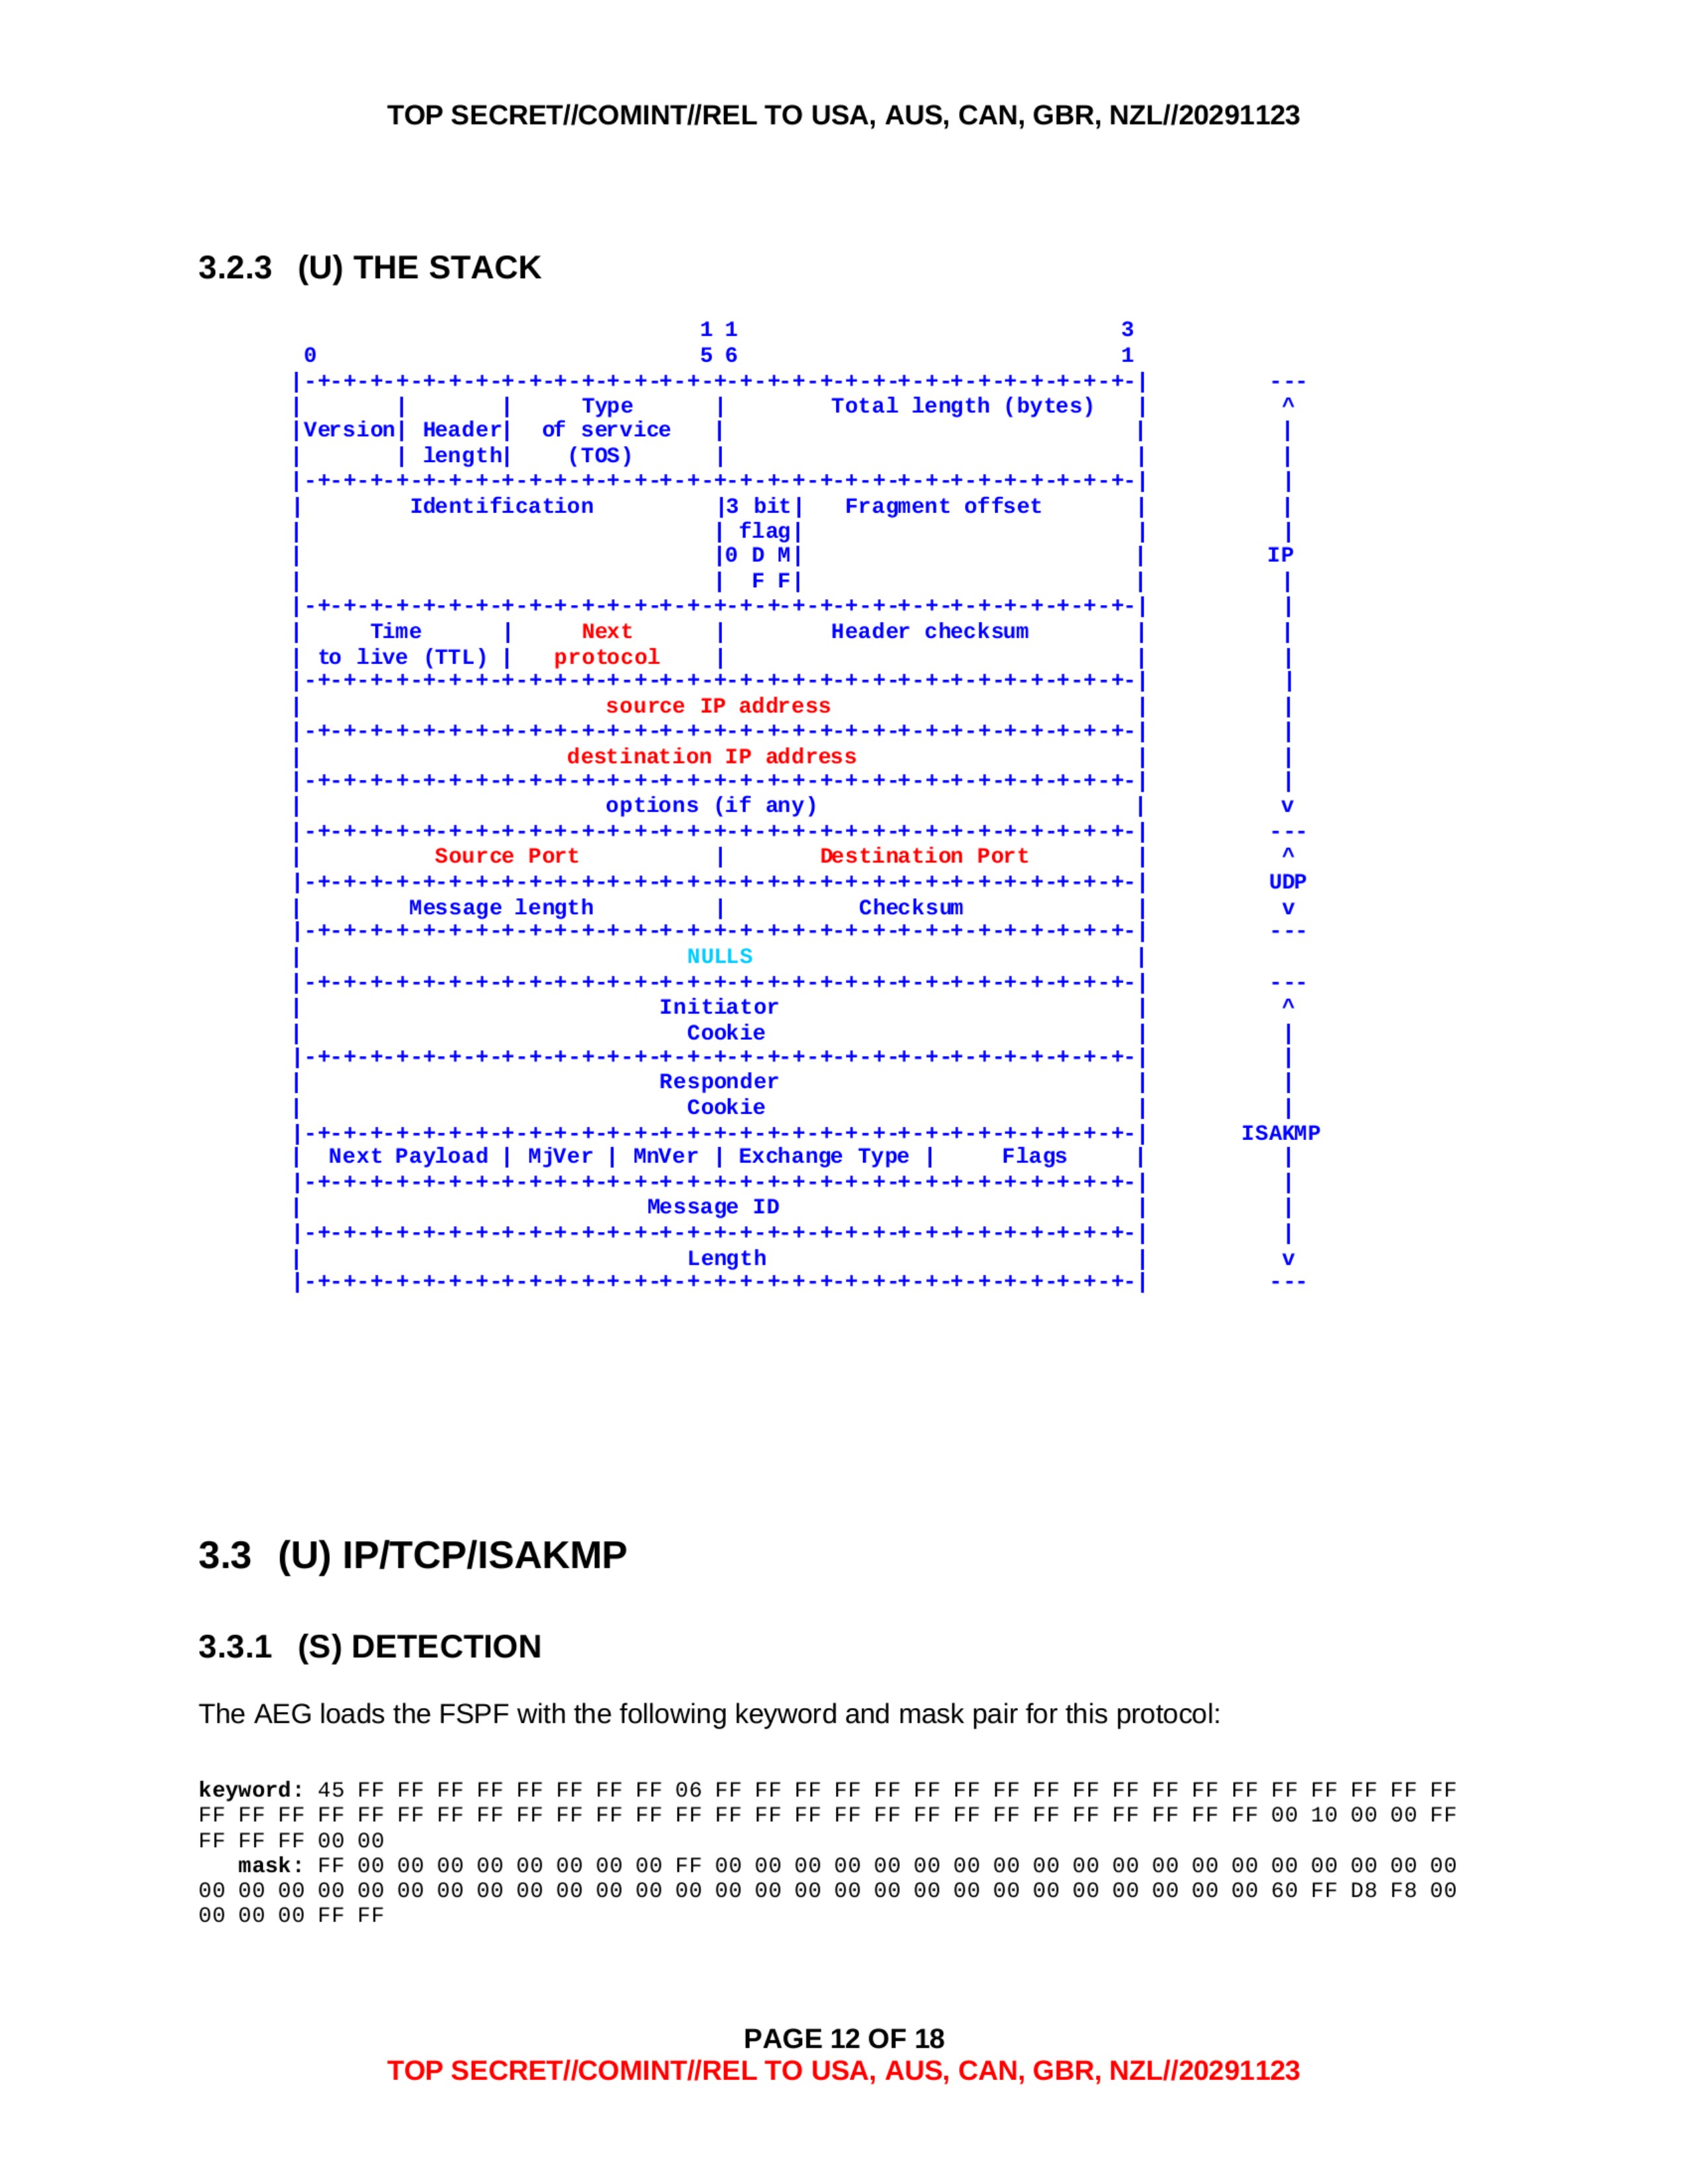
3.2.3 (U) THE STACK
0                               1 1                             3
                                5 6                             1
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|Version| Header|     Type      |                               |        ^
|       | length| of service    |      Total length (bytes)     |        |
|       |       | (TOS)         |                               |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                               |3 bit|                         |        |
|        Identification         | flag|    Fragment offset      |        |
|                               |0 D M|                         |       IP
|                               |  F F|                         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|    Time       |     Next      |                               |        |
| to live (TTL) |   protocol    |       Header checksum         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                       source IP address                       |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                    destination IP address                     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                        options (if any)                       |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|          Source Port          |        Destination Port       |        ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       UDP
|          Message length       |            Checksum           |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|                            NULLS                              |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|                          Initiator                            |        |
|                           Cookie                              |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                          Responder                            |        |
|                           Cookie                              |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|     ISAKMP
| Next Payload  | MjVer | MnVer | Exchange Type |     Flags     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                          Message ID                           |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                            Length                             |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
3.3 (U) IP/TCP/ISAKMP
3.3.1 (S) DETECTION
The AEG loads the FSPF with the following keyword and mask pair for this protocol:
keyword: 45 FF FF FF FF FF FF FF FF 06 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF
FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF 00 10 00 00 FF
FF FF FF 00 00
mask: FF 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00
00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 60 FF D8 F8 00
00 00 00 FF FF
PAGE 12 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
This indicates that the packets that satisfy the following parameters will be selected by this keyword for processing in the IKE_AEG:
- IPv4 packet
- IP Header Length = 5
- IP Next Protocol = TCP (0x06)
- ISAKMP Version = 0x10
- ISAKMP Next Payload, Exchange Type, and Flags fields all have ranges of valid values
- ISAKMP Length (header + payload) < 64k
We have a similar keyword/mask pair for ISAKMP Version 9.9.
3.3.2 (S) SESSIONIZING
The TCP/ISAKMP packets would be sessionized by the following set of parameters:
- IP Next Protocol = TCP (0x06)
- IP Source Address
- IP Destination Address
- TCP Source Port
- TCP Destination Port
PAGE 13 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
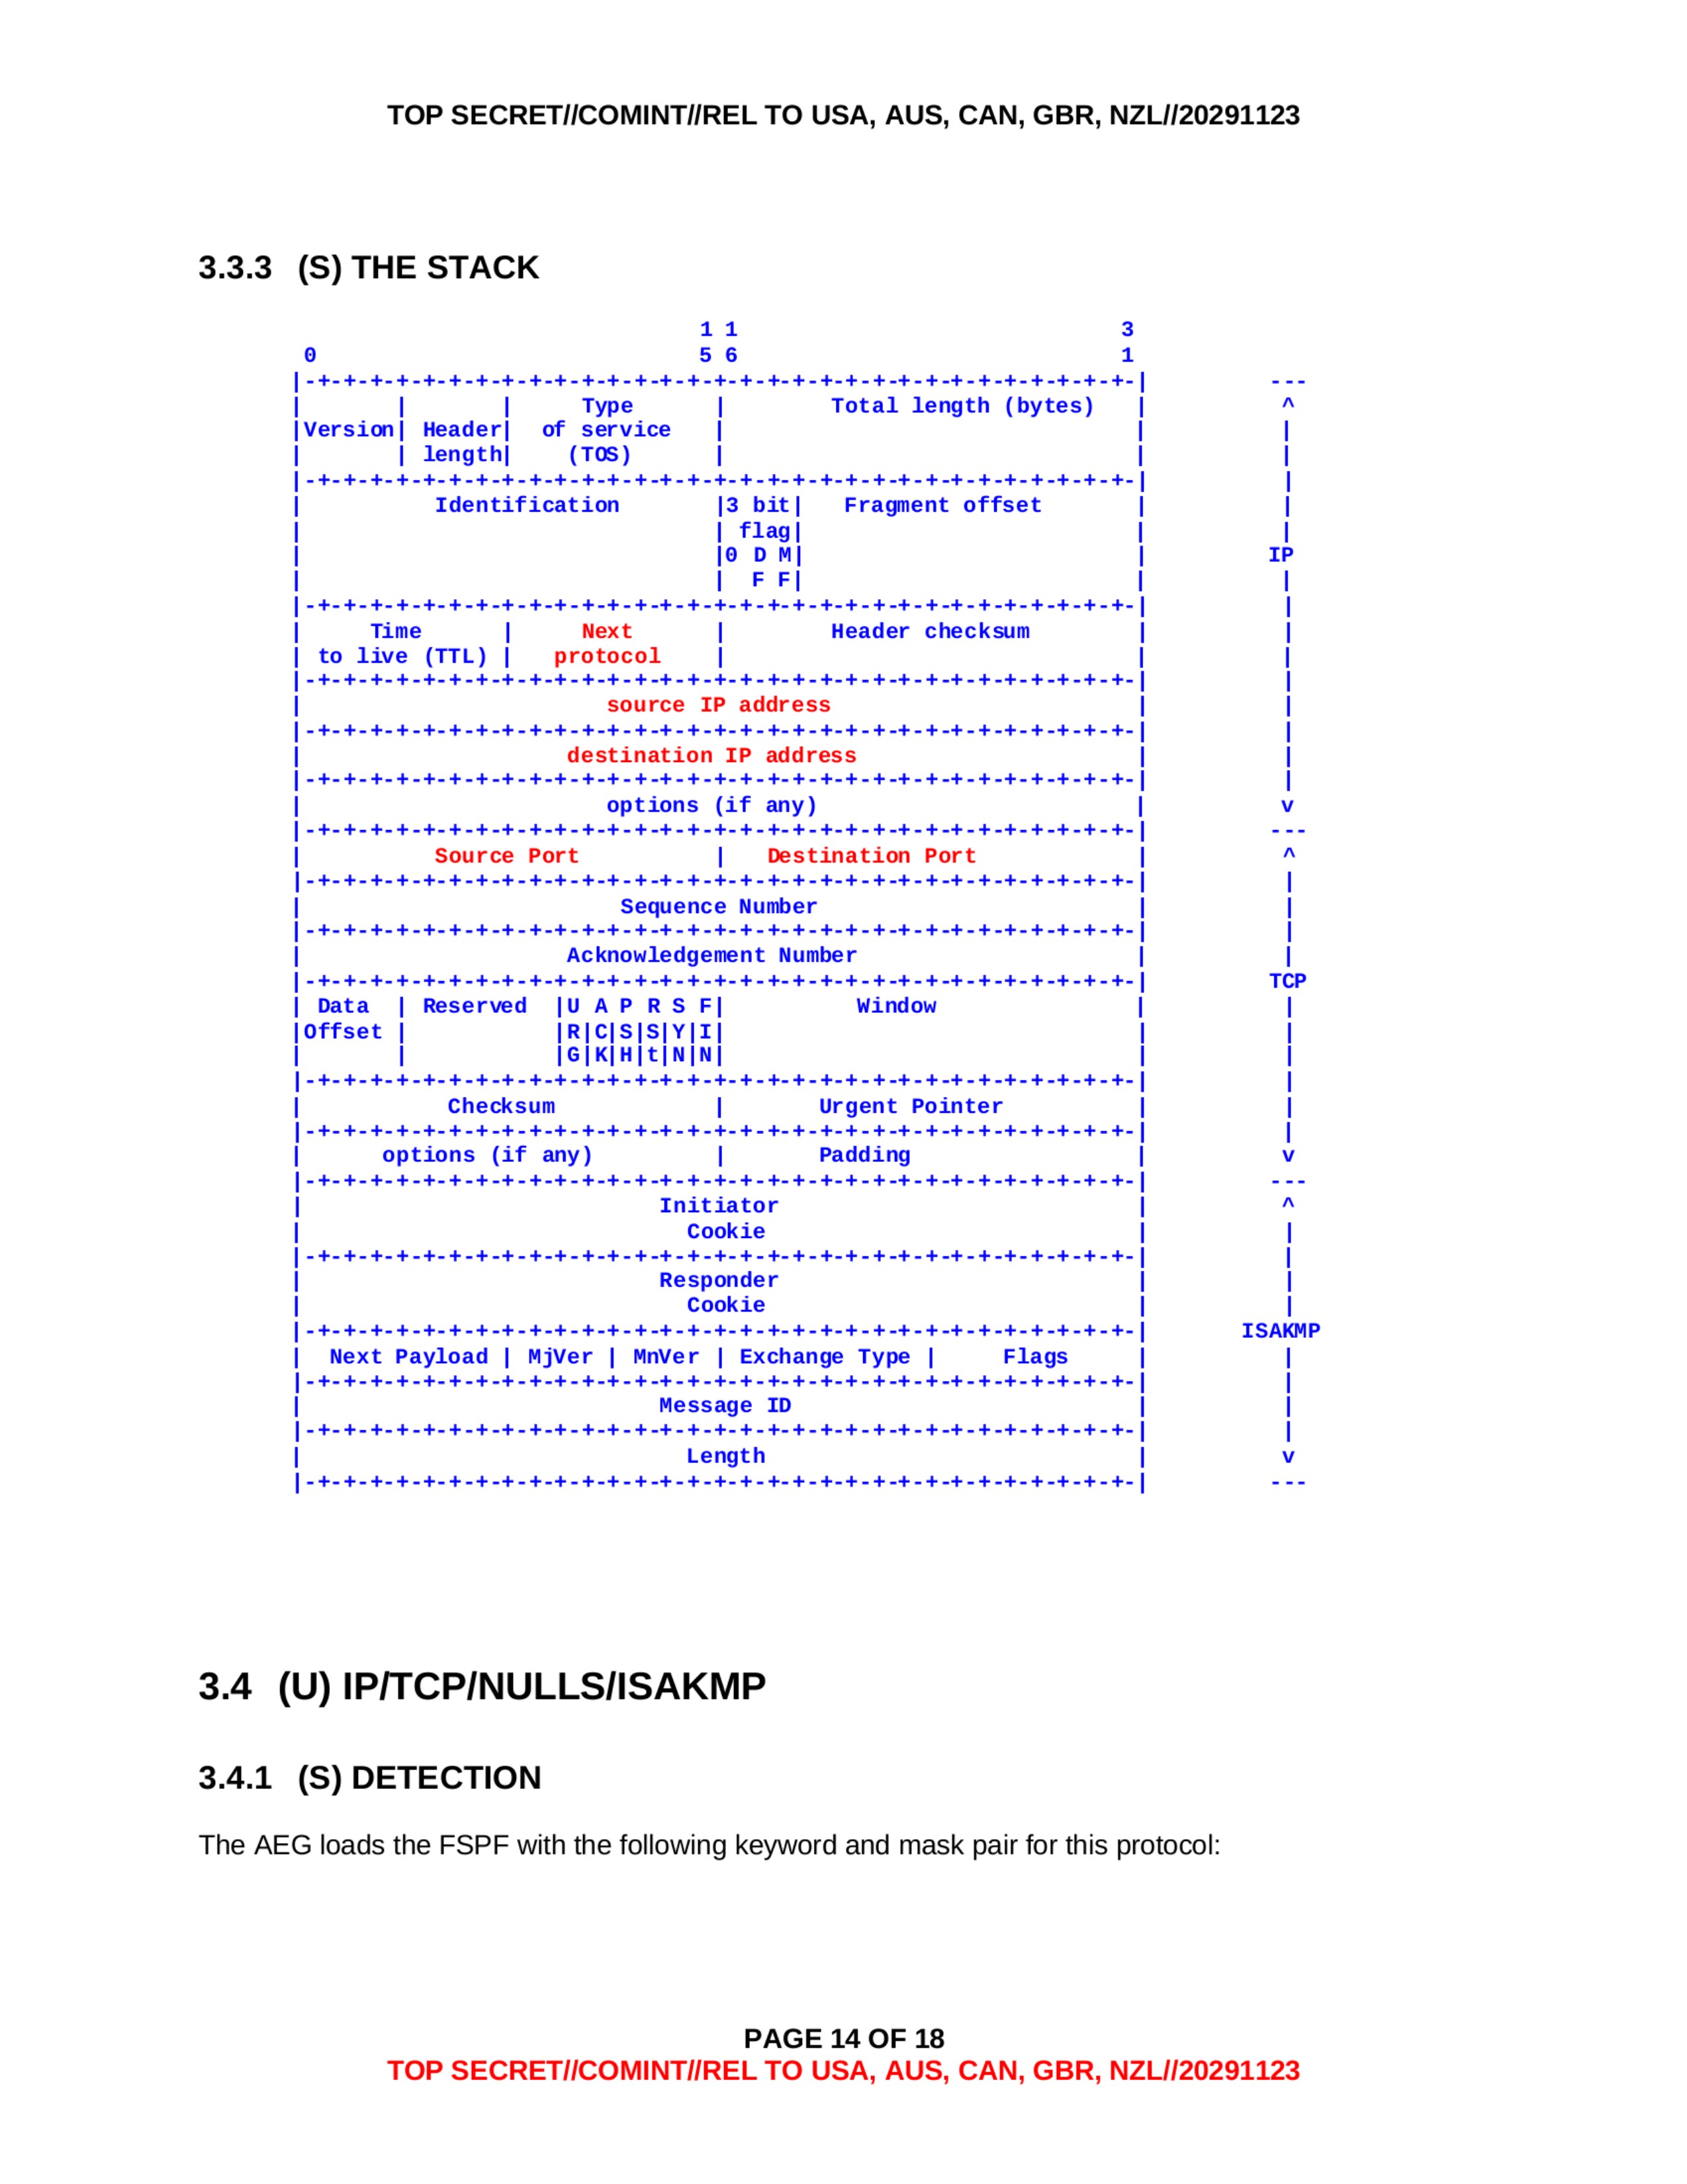
3.3.3 (S) THE STACK
0                               1 1                             3
                                5 6                             1
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|Version| Header|     Type      |                               |        ^
|       | length| of service    |      Total length (bytes)     |        |
|       |       | (TOS)         |                               |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                               |3 bit|                         |        |
|        Identification         | flag|    Fragment offset      |        |
|                               |0 D M|                         |       IP
|                               |  F F|                         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|    Time       |     Next      |                               |        |
| to live (TTL) |   protocol    |       Header checksum         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                       source IP address                       |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                    destination IP address                     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                        options (if any)                       |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|          Source Port          |        Destination Port       |        ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                       Sequence Number                         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                    Acknowledgement Number                     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       TCP
|  Data  |         |U A P R S F|                                |        |
|Offset  | Reserved|R C S S Y I|            Window              |        |
|        |         |G K H t N N|                                |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|            Checksum           |        Urgent Pointer         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|          options (if any)     |            Padding            |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|                          Initiator                            |        ^
|                           Cookie                              |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                          Responder                            |        |
|                           Cookie                              |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|     ISAKMP
| Next Payload  | MjVer | MnVer | Exchange Type |     Flags     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                          Message ID                           |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                            Length                             |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
3.4 (U) IP/TCP/NULLS/ISAKMP
3.4.1 (S) DETECTION
The AEG loads the FSPF with the following keyword and mask pair for this protocol:
PAGE 14 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
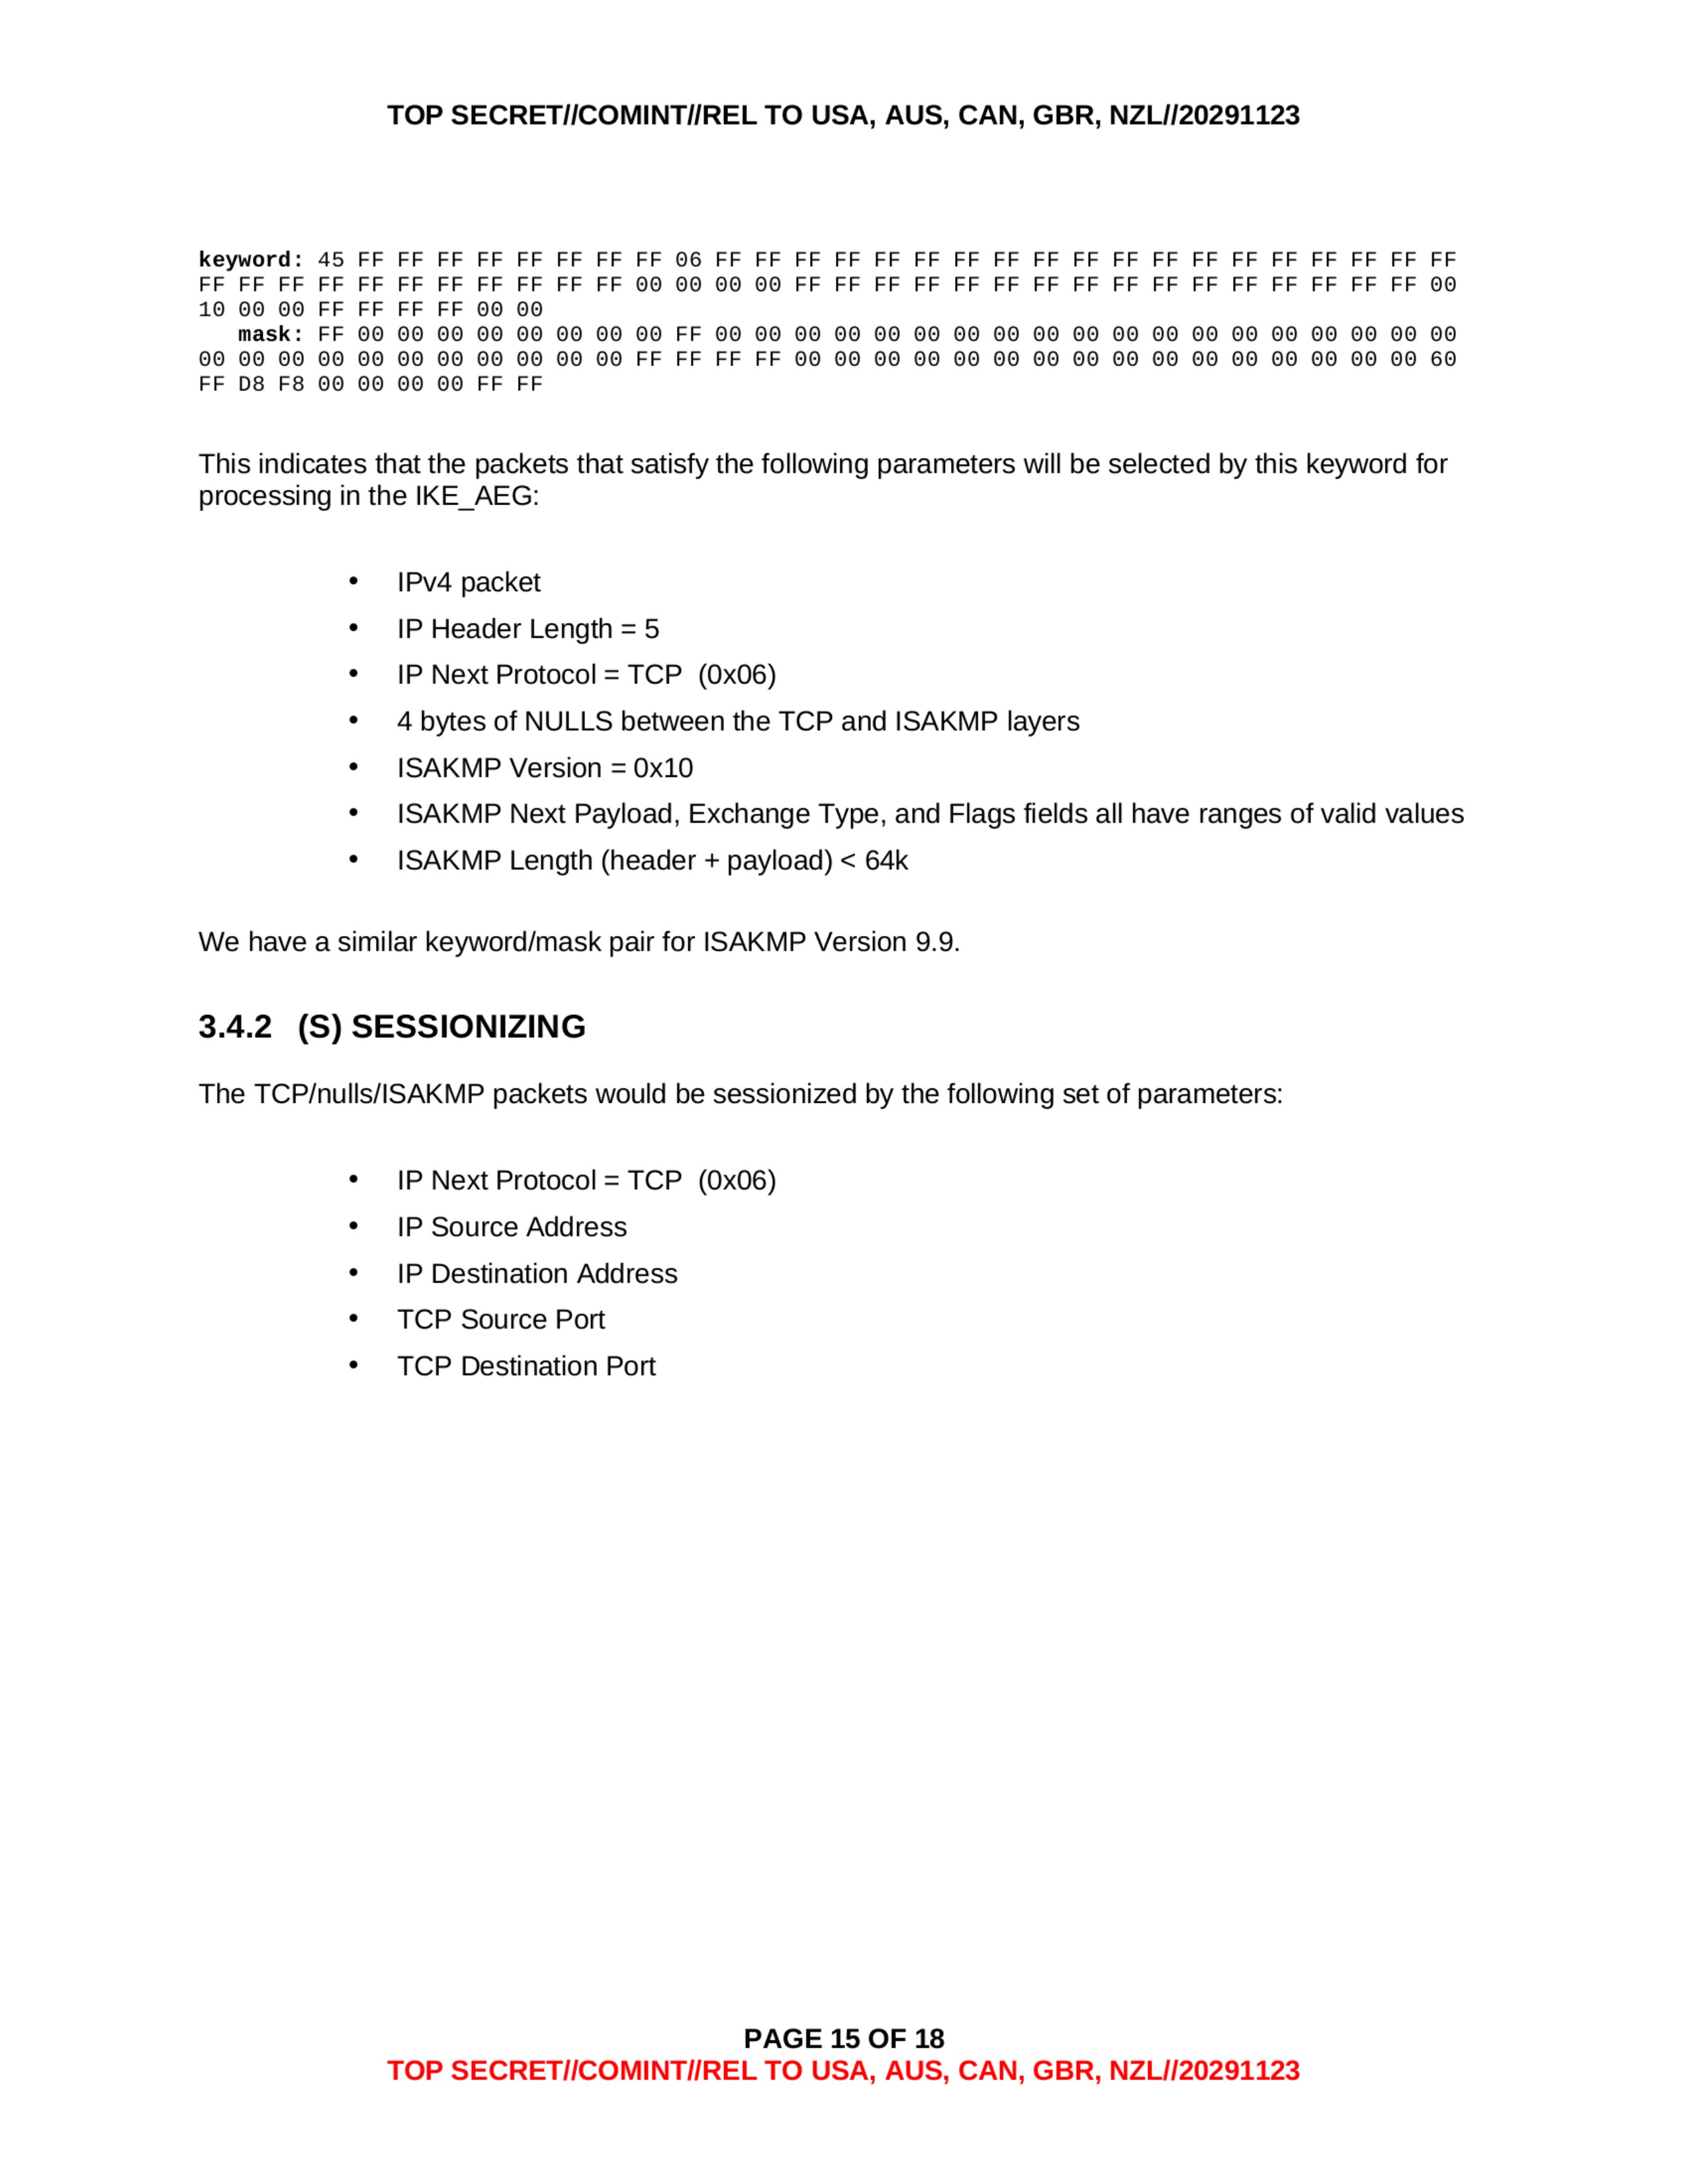
keyword: 45 FF FF FF FF FF FF FF FF 06 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF
FF FF FF FF FF FF FF FF FF FF FF 00 00 00 00 FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF FF 00
10 00 00 FF FF FF FF 00 00
mask: FF 00 00 00 00 00 00 00 00 FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00
00 00 00 00 00 00 00 00 00 00 00 FF FF FF FF 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 60
FF D8 F8 00 00 00 00 FF FF
This indicates that the packets that satisfy the following parameters will be selected by this keyword for processing in the IKE_AEG:
- IPv4 packet
- IP Header Length = 5
- IP Next Protocol = TCP (0x06)
- 4 bytes of NULLS between the TCP and ISAKMP layers
- ISAKMP Version = 0x10
- ISAKMP Next Payload, Exchange Type, and Flags fields all have ranges of valid values
- ISAKMP Length (header + payload) < 64k
We have a similar keyword/mask pair for ISAKMP Version 9.9.
3.4.2 (S) SESSIONIZING
The TCP/nulls/ISAKMP packets would be sessionized by the following set of parameters:
- IP Next Protocol = TCP (0x06)
- IP Source Address
- IP Destination Address
- TCP Source Port
- TCP Destination Port
PAGE 15 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
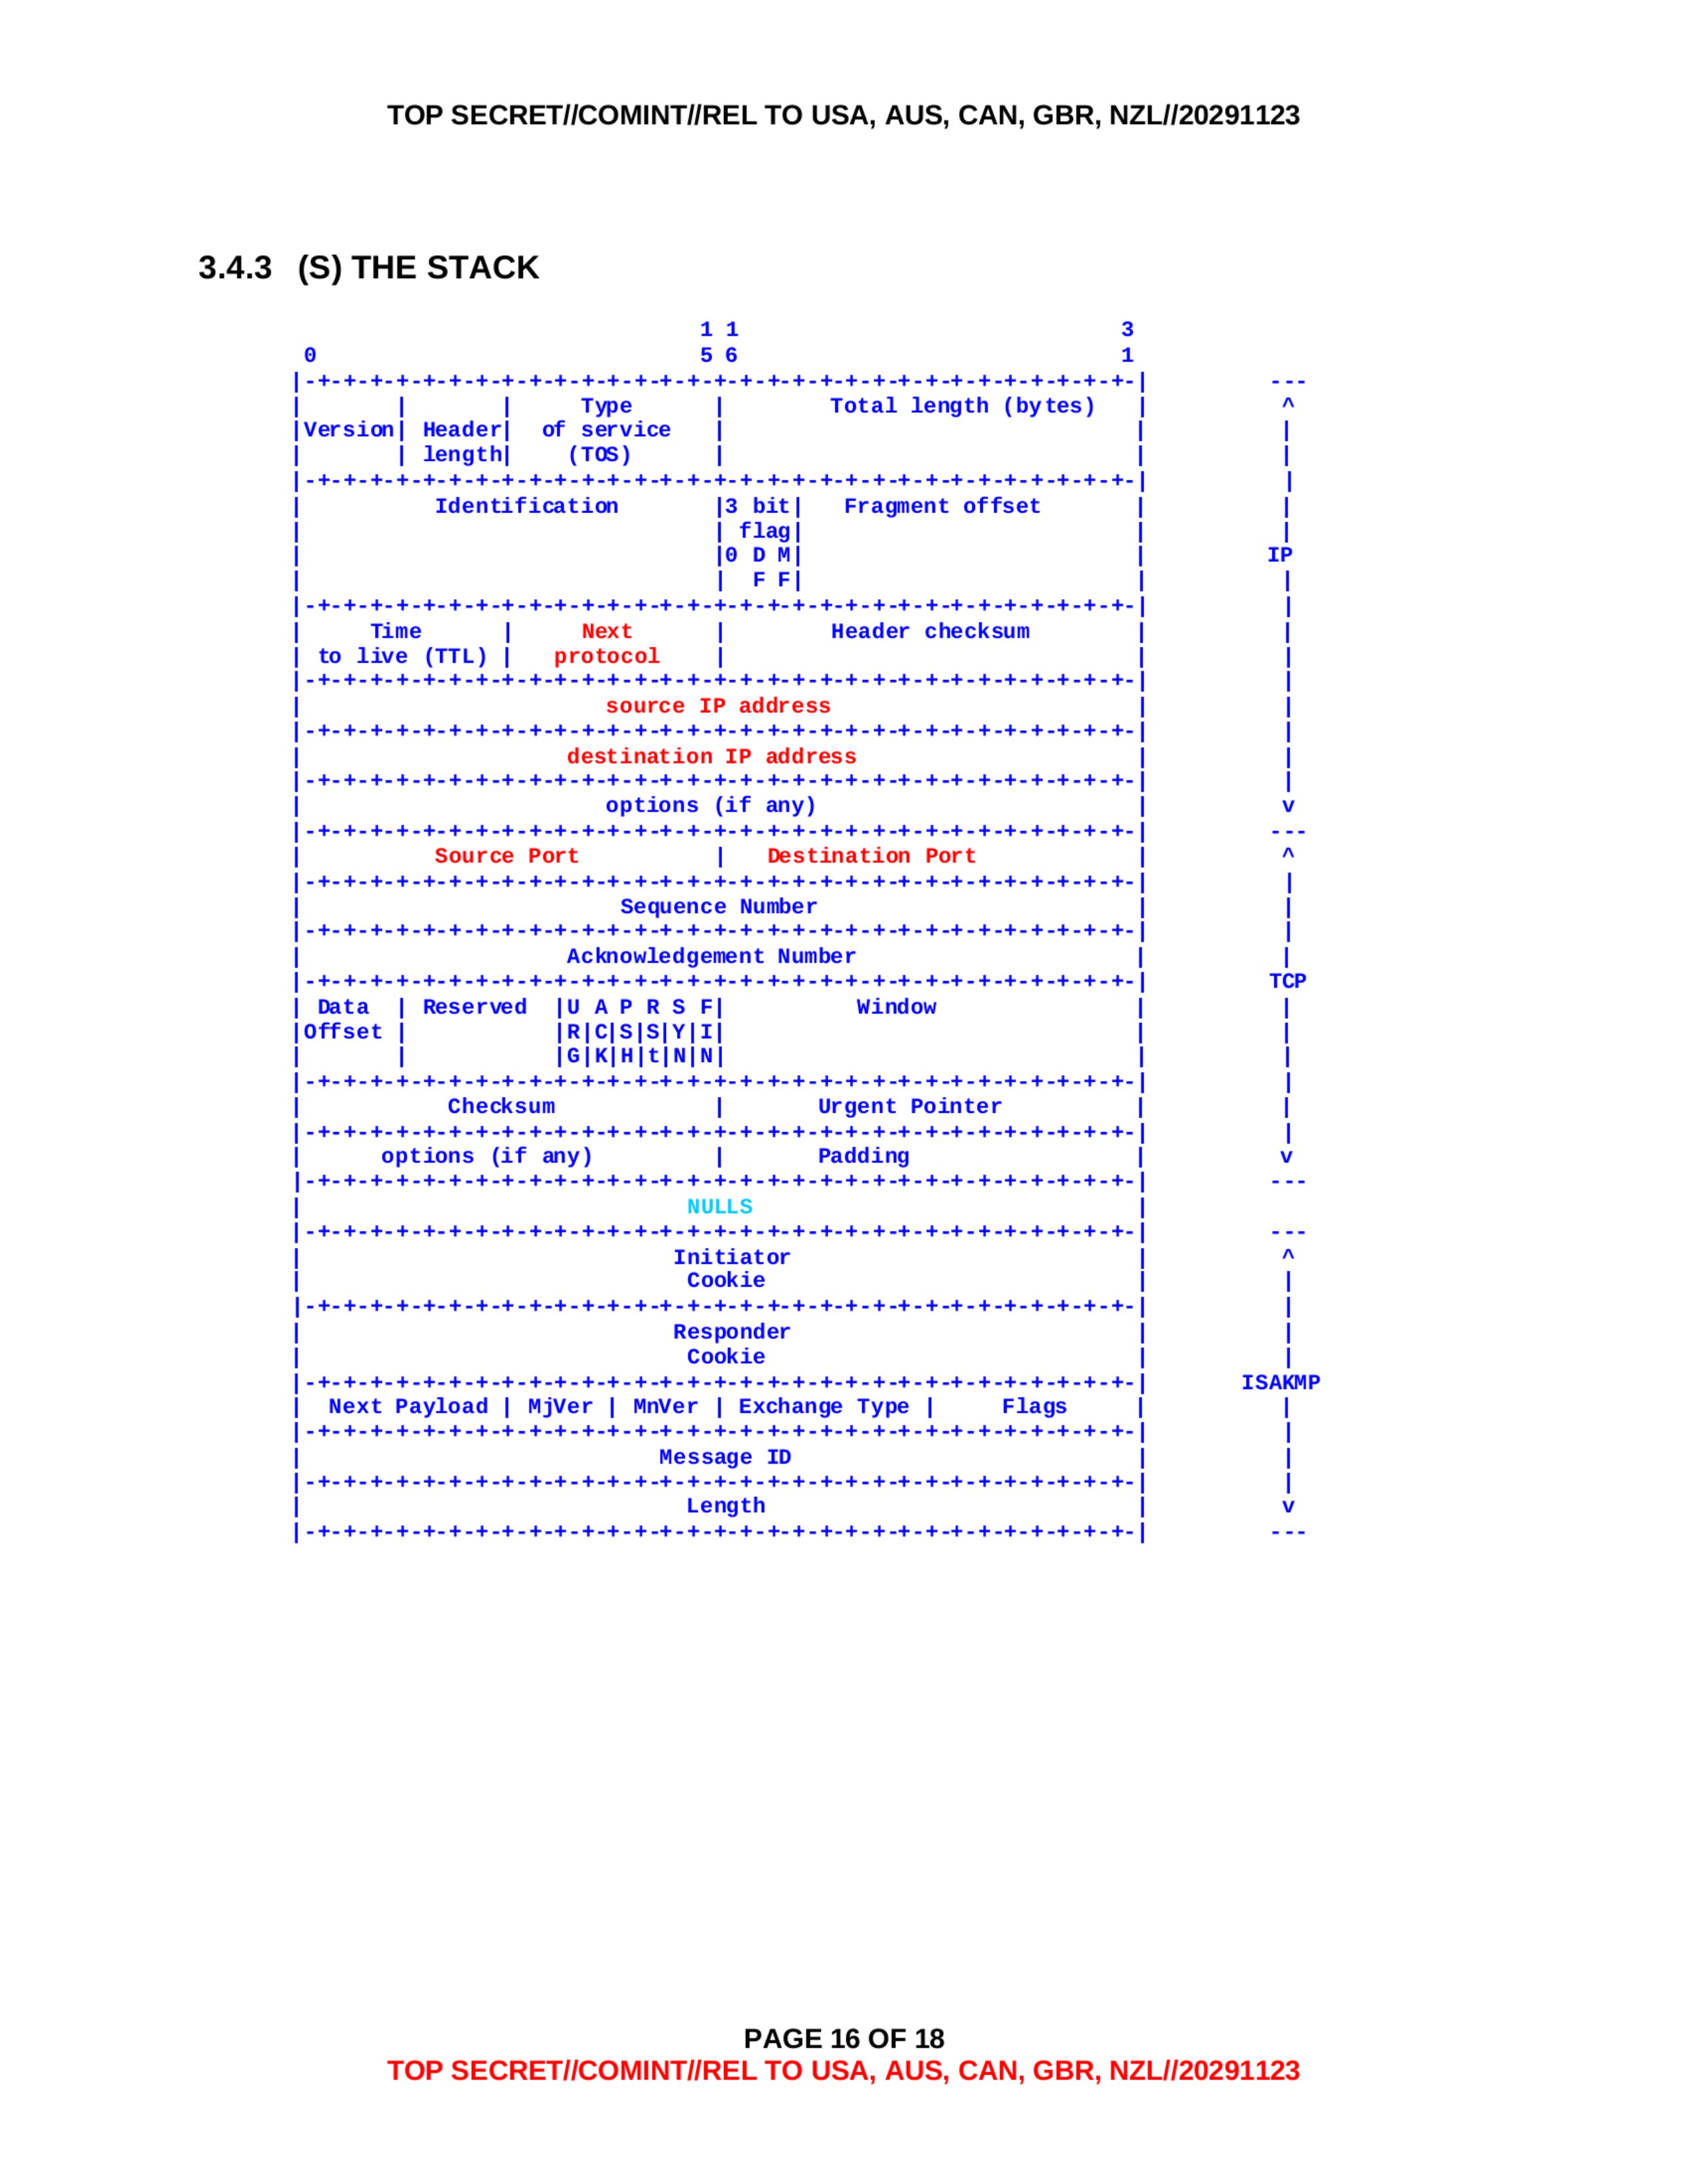
3.4.3 (S) THE STACK
0                               1 1                             3
                                5 6                             1
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|Version| Header|     Type      |                               |        ^
|       | length| of service    |      Total length (bytes)     |        |
|       |       | (TOS)         |                               |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                               |3 bit|                         |        |
|        Identification         | flag|    Fragment offset      |       IP
|                               |0 D M|                         |        |
|                               |  F F|                         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|    Time       |     Next      |                               |        |
| to live (TTL) |   protocol    |       Header checksum         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                       source IP address                       |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                    destination IP address                     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                        options (if any)                       |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|          Source Port          |        Destination Port       |        ^
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                       Sequence Number                         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                    Acknowledgement Number                     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       TCP
|  Data  |         |U A P R S F|                                |        |
|Offset  | Reserved|R C S S Y I|            Window              |        |
|        |         |G K H t N N|                                |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|            Checksum           |        Urgent Pointer         |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|          options (if any)     |            Padding            |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|                            NULLS                              |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
|                          Initiator                            |        ^
|                           Cookie                              |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                          Responder                            |        |
|                           Cookie                              |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|     ISAKMP
| Next Payload  | MjVer | MnVer | Exchange Type |     Flags     |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                          Message ID                           |        |
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|        |
|                            Length                             |        v
|-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-+-|       ---
PAGE 16 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
4.0 (U) SUMMARY
The FIP currently recognizes UDP, TCP, and ESP as valid Network Layer protocols, and currently sessionizes those packet types. The new requirement for IP/AH/ESP will require changes to the FIP to recognize AH as a valid layer, and will also require changes to the DFCE to allow those packets through.
There has been talk of having application-specific demuxes developed and inserted into the TE to perform any required sessionization beyond the Transport Layer. For example, the ESP demux would be responsible for sessionizing on Spi value.
The Table below summarizes the various protocol stacks, the parts of the stacks that are used in PPF keyword detection, and how the associated packets should be sessionized.
| Protocol Stack | Keyword Detection Layers | Sessionization Requirements |
|---|---|---|
| IP/ESP | IP, ESP | IP Next Protocol = 50 IP Source Address IP Destination Address ESP Spi |
| IP/AH/ESP | IP, AH, ESP | IP Next Protocol = 51 IP Source Address IP Destination Address AH Next Header = 50 AH Spi ESP Spi |
| IP/UDP/ISAKMP * we have separate keywords for ISAKMP Versions 1.0 and 9.9 |
IP, UDP, ISAKMP | IP Next Protocol = 17 IP Source Address IP Destination Address UDP Source Port UDP Destination Port |
| IP/UDP/nulls/ISAKMP * we have separate keywords for ISAKMP Versions 1.0 and 9.9 |
IP, UDP, ISAKMP | IP Next Protocol = 17 IP Source Address IP Destination Address UDP Source Port UDP Destination Port |
PAGE 17 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
| IP/TCP/ISAKMP * we have separate keywords for ISAKMP Versions 1.0 and 9.9 |
IP, TCP, ISAKMP | IP Next Protocol = 6 IP Source Address IP Destination Address TCP Source Port TCP Destination Port |
| IP/TCP/nulls/ISAKMP * we have separate keywords for ISAKMP Versions 1.0 and 9.9 |
IP, TCP, ISAKMP | IP Next Protocol = 6 IP Source Address IP Destination Address TCP Source Port TCP Destination Port |
PAGE 18 OF 18
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
Published in the Same Report
(10 of 43 documents)
-
BULLRUN CoI - Briefing Sheet [pdf]
A GCHQ briefing sheet introducing the BULLRUN Community of Interest — the access control framework protecting Five Eyes capabilities to defeat encryption across TLS/SSL, HTTPS, SSH, VPNs, IPSec, encrypted chat and encrypted VoIP — covering the classification structure, handling procedures and protective marking guidance for intelligence derived from cryptanalytic exploitation.
“N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Perlroth, Nicole · Larson, Jeff · Shane, Scott · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CLASSIFICATION GUIDE FOR CRYPTANALYSIS, 2-12 [pdf]
An NSA/CSS classification guide for cryptanalysis establishing the precise classification level for each type of information about NSA's capabilities to exploit commercial and indigenous encryption systems — from the unclassified acknowledgement that NSA exploits cryptographic devices, through to the Top Secret protection of cryptographic modifications made to commercial products to render them exploitable and industry relationships used to obtain cryptographic details.
“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Ball, James · Borger, Julian · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
TLS Trends: A roundtable discussion on current usage and future directions [pdf]
A presentation by Canada's Communications Security Establishment describing their TLS trend analysis programme, which systematically tracked SSL/TLS encryption parameters across warranted collection and Special Source access to identify cryptanalytic opportunities, monitor target behaviour and collaborate with GCHQ on exploiting weaknesses in widely-used encryption implementations.
-
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
TLS trends at GCHQ [pdf]
A GCHQ presentation describing their TLS trends analysis programme, which processed approximately 10 billion SSL/TLS Server Hello events per week from Special Source cable tapping and COMSAT collection to produce weekly trend reports, alongside two operational tools — TargeTLS for matching TLS events against BROAD OAK target profiles, and FLYING PIG, a TLS knowledge base enabling analysts to query certificate, IP and client data across the full intercept base.
-
TURMOIL/APEX/APEX High Level Description Document [pdf]
NSA WikiInfo page providing the high-level design description of APEX — the Active-Passive Integration capability integrating HAMMERMILL router implants with TURMOIL passive collection — enabling real-time exfiltration of targeted VPN (HAMMERSTEIN) and VoIP (HAMMERCHANT) traffic from compromised routers directly into NSA's passive collection and cryptanalytic attack infrastructure, with TURBINE providing automated command and control of the combined active-passive system.
Programs: TURMOIL · APEX · HAMMERMILL · HAMMERCHANT · HAMMERSTEIN · FASHIONCLEFT · TURBINE · TOYGRIPPE · METROTUBE · CHIMNEYPOOL · PIQBLADE · KEYCARD · FASCIA · ISLANDTRANSPORT · PRESSUREWAVE · ASDF · CONVEYANCE · TURBULENCE -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT







Related Documents
-
TURMOIL VPN PROCESSING [pdf]
A TURMOIL VPN Processing technical briefing from October 2009 describing the full architecture for intercepting and decrypting IPSec VPN traffic within the TURMOIL passive collection platform — covering IKE/ESP protocol handling, five distinct data flow types, the Dell LPT hardware implementation, and live operational metrics showing over 8 million packets decrypted at Menwith Hill and 1.4 million at SMOKYSINK during a single week in October 2009.
-
TURBULENCE - Fielded Capability: End-to-End VPN, SPIN 9 Design Review [pdf]
An NSA SPIN 9 design review presentation describing the transition of TURMOIL's VPN decryption capability from the legacy Red Architecture to the new Blue Architecture — covering the full end-to-end dataflow, component interfaces, test scenarios and detailed processing specifications for each system in the VPN decryption pipeline.
Programs: TURBULENCE · TURMOIL · KEYCARD · WEALTHYCLUSTER · TUBE · XKEYSCORE · PRESSUREWAVE · EXOPUMP · PWV · TOYGRIPPE · PICARESQUE · AGILITY · MAILORDER · ISLANDTRANSPORT · PIQBLADE · PINWALE · TRAFFICTHIEF · IBRIDGE · PPF · METROTUBE · FIP · SSO -
VALIANTSURF [pdf]
An NSA WikiInfo page for VALIANTSURF — the coverterm for NSA's IPSec VPN decryption capability within the TURMOIL collection platform — describing the four data flow types for intercepting and breaking encrypted VPN traffic, the full deployment roster across collection sites including Menwith Hill, SMOKYSINK, MUSCULAR, CROSSCUT and others, and the architectural taxonomy of the VALIANTSURF programme including its MALIBU and WAIMEA processing architectures and their relationship to LONGHAUL, POISONNUT and GALLANTWAVE.
Programs: VALIANTSURF · TURMOIL · TURBULENCE · HOOKED · HOOKEDHAND · CINDER · CINDERASH · CINDERTRACK · SCARLETFEVER · LONGHAUL · FALLOUT · TOYGRIPPE · PICARESQUE · XKEYSCORE · PRESSUREWAVE · ASDF · MAILORDER · TUBE · KEYCARD · POISONNUT · ISLANDHIDEAWAY · ISLANDTRANSPORT · EXOPUMP · CORALREEF · PINWALE · TUSCARORA · ONEROOF · CONVEYANCE · TURTLEPOWER · WDM · CADENCE · UTT · SCISSORS · FISHWAY · BTUBE · DNCA · ROMULANALE · GALLANTWAVE · ROMULANGAWK · ROMULANGOWL · MALIBU · WAIMEA · WAIMEAVISAGE · ROMULANVISAGE · WAIMEAVISE · ROMULANVISE · APEX · METROTUBE · MADFORGE · JSORCERER · CROSSCUT · CIET · LATTICE · STARQUAKE · SARATOGA · MUSCULAR · SMOKYSINK · SLACKKEY · TUMMS · PURGE · SURGE · NUCLEON · SPAGIC · PPF · SOAP · TUMULT · FIP · PIQBLADE · DEEPDIVE · IBRIDGE -
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
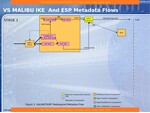
VS MALIBU IKE And ESP Metadata Flows [pdf]
A TOP SECRET four-slide architecture document describing MALIBU — NSA's system for intercepting and decrypting IPSec VPN traffic at the point where it crosses monitored internet cables — showing how intercepted VPN connections are processed, cryptographic keys recovered, traffic decrypted and results delivered to analysts, with separate diagrams for metadata collection, software decryption, full exploitation and survey modes.