Tag: cyber operations 26 documents
Search documents matching “cyber operations” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
AND THEY SAID TO THE TITANS: « WATCH OUT OLYMPIANS IN THE HOUSE! » [pdf]
This Top Secret CSEC “Olympia” document details a Canadian intelligence program that analyzed and tracked the Brazilian Ministry of Mines and Energy’s telecommunications, mapping IPs, servers, proxies, and mobile devices while automating data collection and network analysis to develop actionable intelligence. It outlines tools, workflows, and contacts used for surveillance, though the presentation does not explain the specific purpose of the operation.
Programs: OLYMPIA · QUOVA · PROMETHEUS · PEITHO · SLINGSHOT · LEVITATE · STRATOS · EVILOLIVE · GCHQ Geofusion · ATLAS · HYPERION · ATHENA · DANAUS · TIDALSURGE · BLACKPEARL · MARINA · STARSEARCH · PEPPERBOX · TRITON · PACKAGEDGOODS · ARK · TOYGRIPPE · FRIARTUCK · MASTERSHAKE · COEUS · STALKER · MAINWAY · FASCIA · SEDB · OCTSKYWARD · FASTBAT · TWINSERPENT · EONBLUE · DISHFIRE · GNDB“Read a CSEC document that was first acquired by Edward Snowden” - The Globe and Mail ↗ (2013-11-30) · “Ministério de Minas e Energia está na mira de espiões americanos e canadenses” - O Globo ↗ (2013-10-06) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Freeze, Colin · Bridi, Sônia · Greenwald, Glenn -
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
Black Budget: Cryptanalysis & Exploitation Services – Analysis of Target Systems [pdf]
This document is a budget justification for the NSA's Cryptanalysis & Exploitation Services project, which develops capabilities to defeat commercial encryption systems, exploit emerging communications technologies, and conduct vulnerability analysis against both foreign and domestic security products.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
CASCADE - Joint Cyber Sensor Architecture [pdf]
This presentation outlines the Communications Security Establishment’s (CSE) plans to unify and expand its cyber sensor networks (ITS and SIGINT) to create a comprehensive, multi-layered national cyber defense system, enabling threat detection, intelligence collection, and defensive operations across Canadian and foreign networks. It emphasizes standardizing sensor deployments, integrating analytic capabilities, and preparing for “Effects” operations to mitigate cyber threats by 2015. The presentation is duplicated from page 33 onwards - three slides of the duplicated slides have internal CSE comments.
Programs: CASCADE · PHOTONICPRISM · EONBLUE · INDUCTION · THIRDEYE · CRUCIBLE · CHOKEPOINT · SUNWHEEL · CASSIOPEIA · SCNET · JAZZFLUTE · GAZEBO · SEEDSPHERE · TEXPRO · SSO -
CNO Core Secrets Security Structure [pdf]
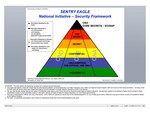
A 3-slide NSA presentation outlining the classification architecture of Sentry Eagle, a national cyber operations initiative, showing how its most sensitive components — covering network hacking, encryption sabotage, and covert industry relationships — are locked behind ECI and SAP designations accessible only to a tiny circle of government officials.
Programs: SENTRYEAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CSEC Cyber Threat Detection [pdf]
This document details the Communications Security Establishment’s (CSEC) cyber threat detection and intelligence infrastructure, including systems like EONBLUE, CROSSBOW, CRUCIBLE, and LODESTONE, which enable passive monitoring, anomaly detection, and botnet identification through metadata and deep packet inspection. It outlines how CSEC integrates SIGINT, cryptanalysis, and network forensics to detect and mitigate cyber intrusions using both SIGINT and domestic sensors, while collaborating with Five Eyes partners to enhance Canada’s cyber defense and situational awareness. The presentation is duplicated from page 7 onwards - one of the duplicated slide has internal CSE comments.
Programs: EONBLUE · SPECIALSOURCE · WARRANTEDACCESS · COVENANT · SEEDSPHERE · DIESELRATTLE · SIENNABLUE · DOWNGRADE · CROSSBOW · CRUCIBLE · LODESTONE -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
Demystifying NGE Rock Ridge [pdf]
This presentation outlines the ROCK RIDGE project, which delivers a suite of "Question Focused Databases" (QFDs) like MUTANT BROTH and KARMA POLICE to analyze massive internet event data. These specialized databases are designed to answer specific intelligence questions and are developed using the BLACK HOLE data repository, a key component of the ROUGH DIAMOND program.
Programs: ROCKRIDGE · ROUGHDIAMONG · BLACKHOLE · HAUSTORIUM · HRMAP · MUTANTBROTH · KARMAPOLICE · GOOBZS · INFINITEMONKEYS · AUTOASSOC · SOCIALANIMAL · MARBLEDGECKO · MEMORYHOLE · SAMUELPEPYS · SALAMANCA · MONOPOLY · RADIUS · HARBOURPILOT · LOOKINGGLASS · FIRESTORM · SUPERDRAKE · BLAZINGSADDLES · BLUESHIFT · SUPPORTINGINO · TERRAINS · GEOFUSION · NGEPeople: Lobban, Iain -
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
Expanding TAO's Operational Capabilities Out to the CCs SIDtoday [pdf]
NSA Cryptologic Centers in Hawaii, Texas, and Georgia can now conduct Computer Network Exploitation.
The Intercept ↗ (2019-05-29) -
FINAL Agenda SWEDUSA [pdf]
Detailed list of points and participants in the summit meeting between the top brass of the FRA and the NSA in April 2013.
Programs: TURTLEPOWER · TURMOIL · XKEYSCORE · WINTERLIGHT · QUANTUM · PARTNERMALL · VIVIAN · NAPA-3 · GCE · SSO -
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
FY 2013 Congressional Budget Justification, Volume I, National Intelligence Program Summary, February 2012 [pdf]
This document outlines the $52.6 billion “black budget,” detailing the structure, priorities, successes, and shortcomings of the 16 U.S. intelligence agencies. It reveals unprecedented insight into funding allocations, operations, and intelligence gaps—including the CIA’s dominant role, expanding cyber operations, and persistent challenges in areas such as North Korea and counterterrorism—while emphasizing the tension between secrecy and public accountability.
-
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
-
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe -
NSA Intelligence Relationship with Canada's Communications Security Establishment Canada (CSEC) [pdf]
This document describes the close, long-standing SIGINT partnership between the NSA and Canada’s CSEC, emphasizing cooperative efforts in global intelligence collection, cyber operations, information assurance, and critical infrastructure defense. It highlights mutual contributions, including CSEC’s unique geographic access, covert sites, cryptographic capabilities, and R&D collaboration, supporting U.S. and North American security objectives.
“Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Presidential Policy Directive/PPD-20 [pdf]
Eighteen-page presidential memo reveals how Barack Obama has ordered intelligence officials to draw up a list of potential overseas targets for US cyber attacks.
-
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R.