Project CAMBERDADA
Open PDFDocument date: -
Pages: 13
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, AUS, CAN, GBR, NZL
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
My notes
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
An Easy Win: Using SIGINT to Learn about New Viruses
Project CAMBERDADA
By [REDACTED], I412 (IAD)
& [REDACTED], V252
(NTOC)
Derived From: NSA/CSSM 1-52
Dated: 20070108
Declassify On: 20370301
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Overall classification
TOPSECRET//COMINT//
REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
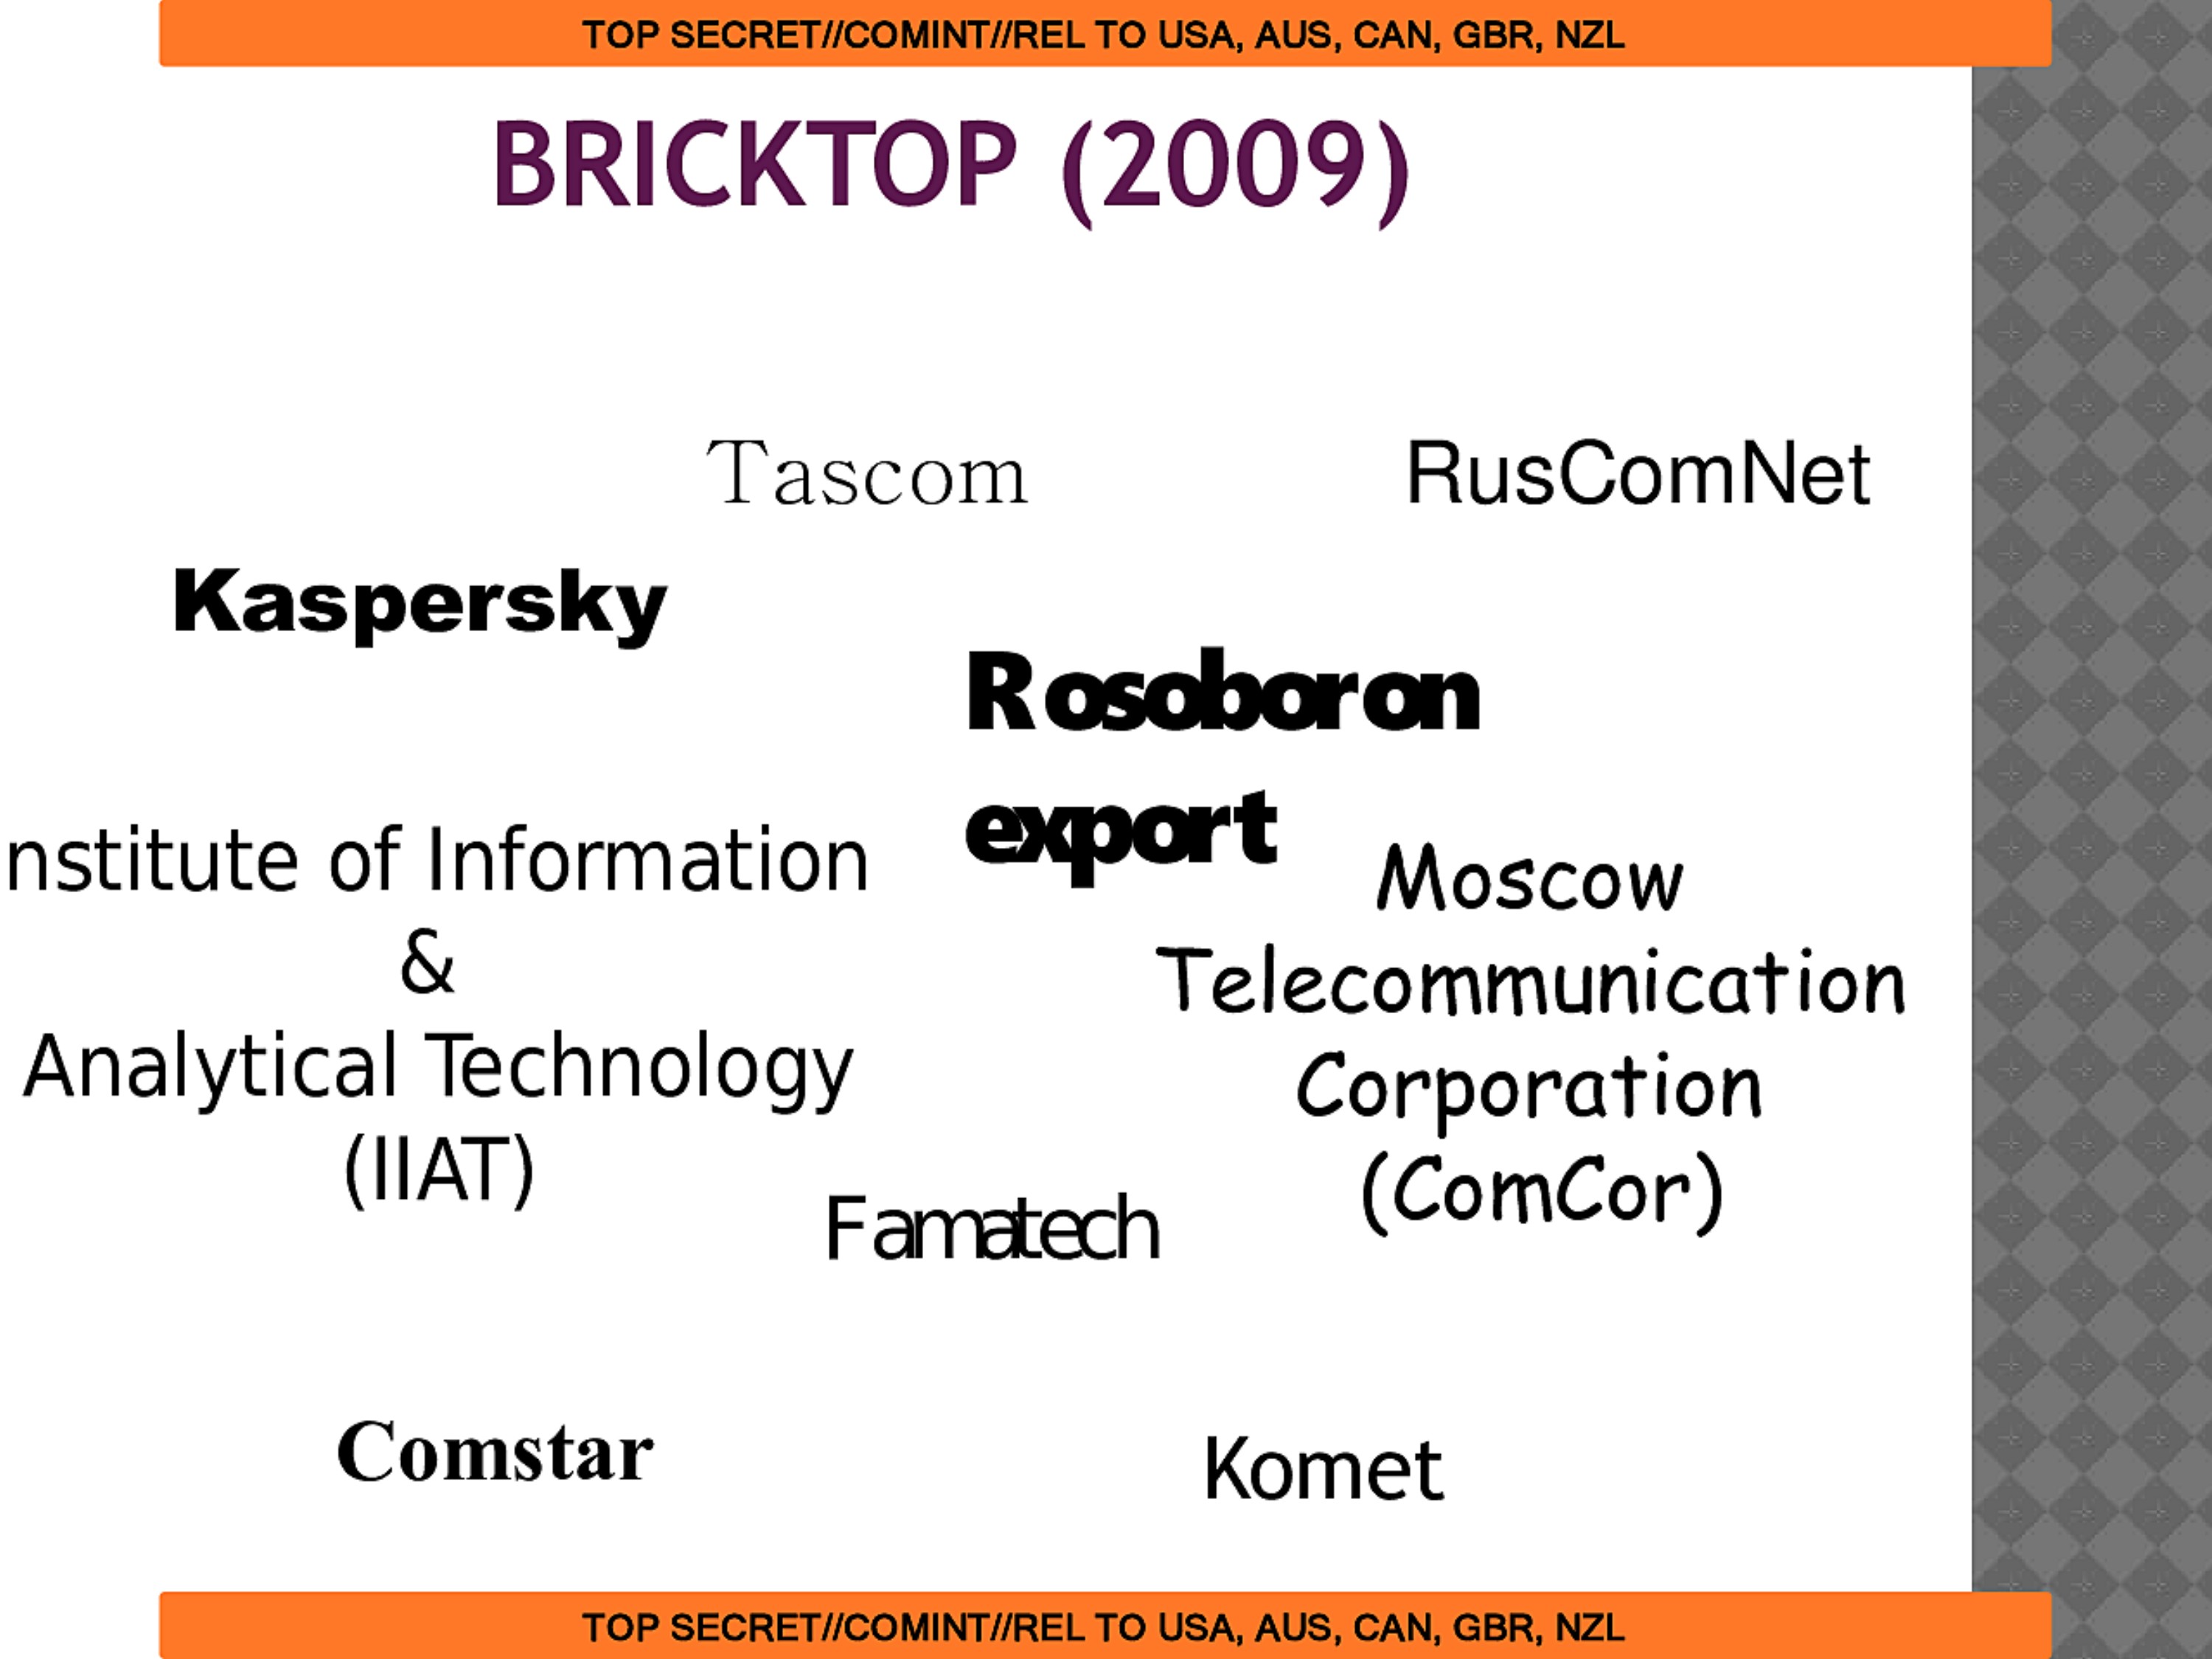
BRICKTOP (2009)
- Tascom
- RusComNet
- Kaspersky
- Rosoboron export
- nstitute of Information & Analytical Technology (IIAT)
- Moscow Telecommunication Corporation (ComCor)
- Famatech
- Comstar
- Komet
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
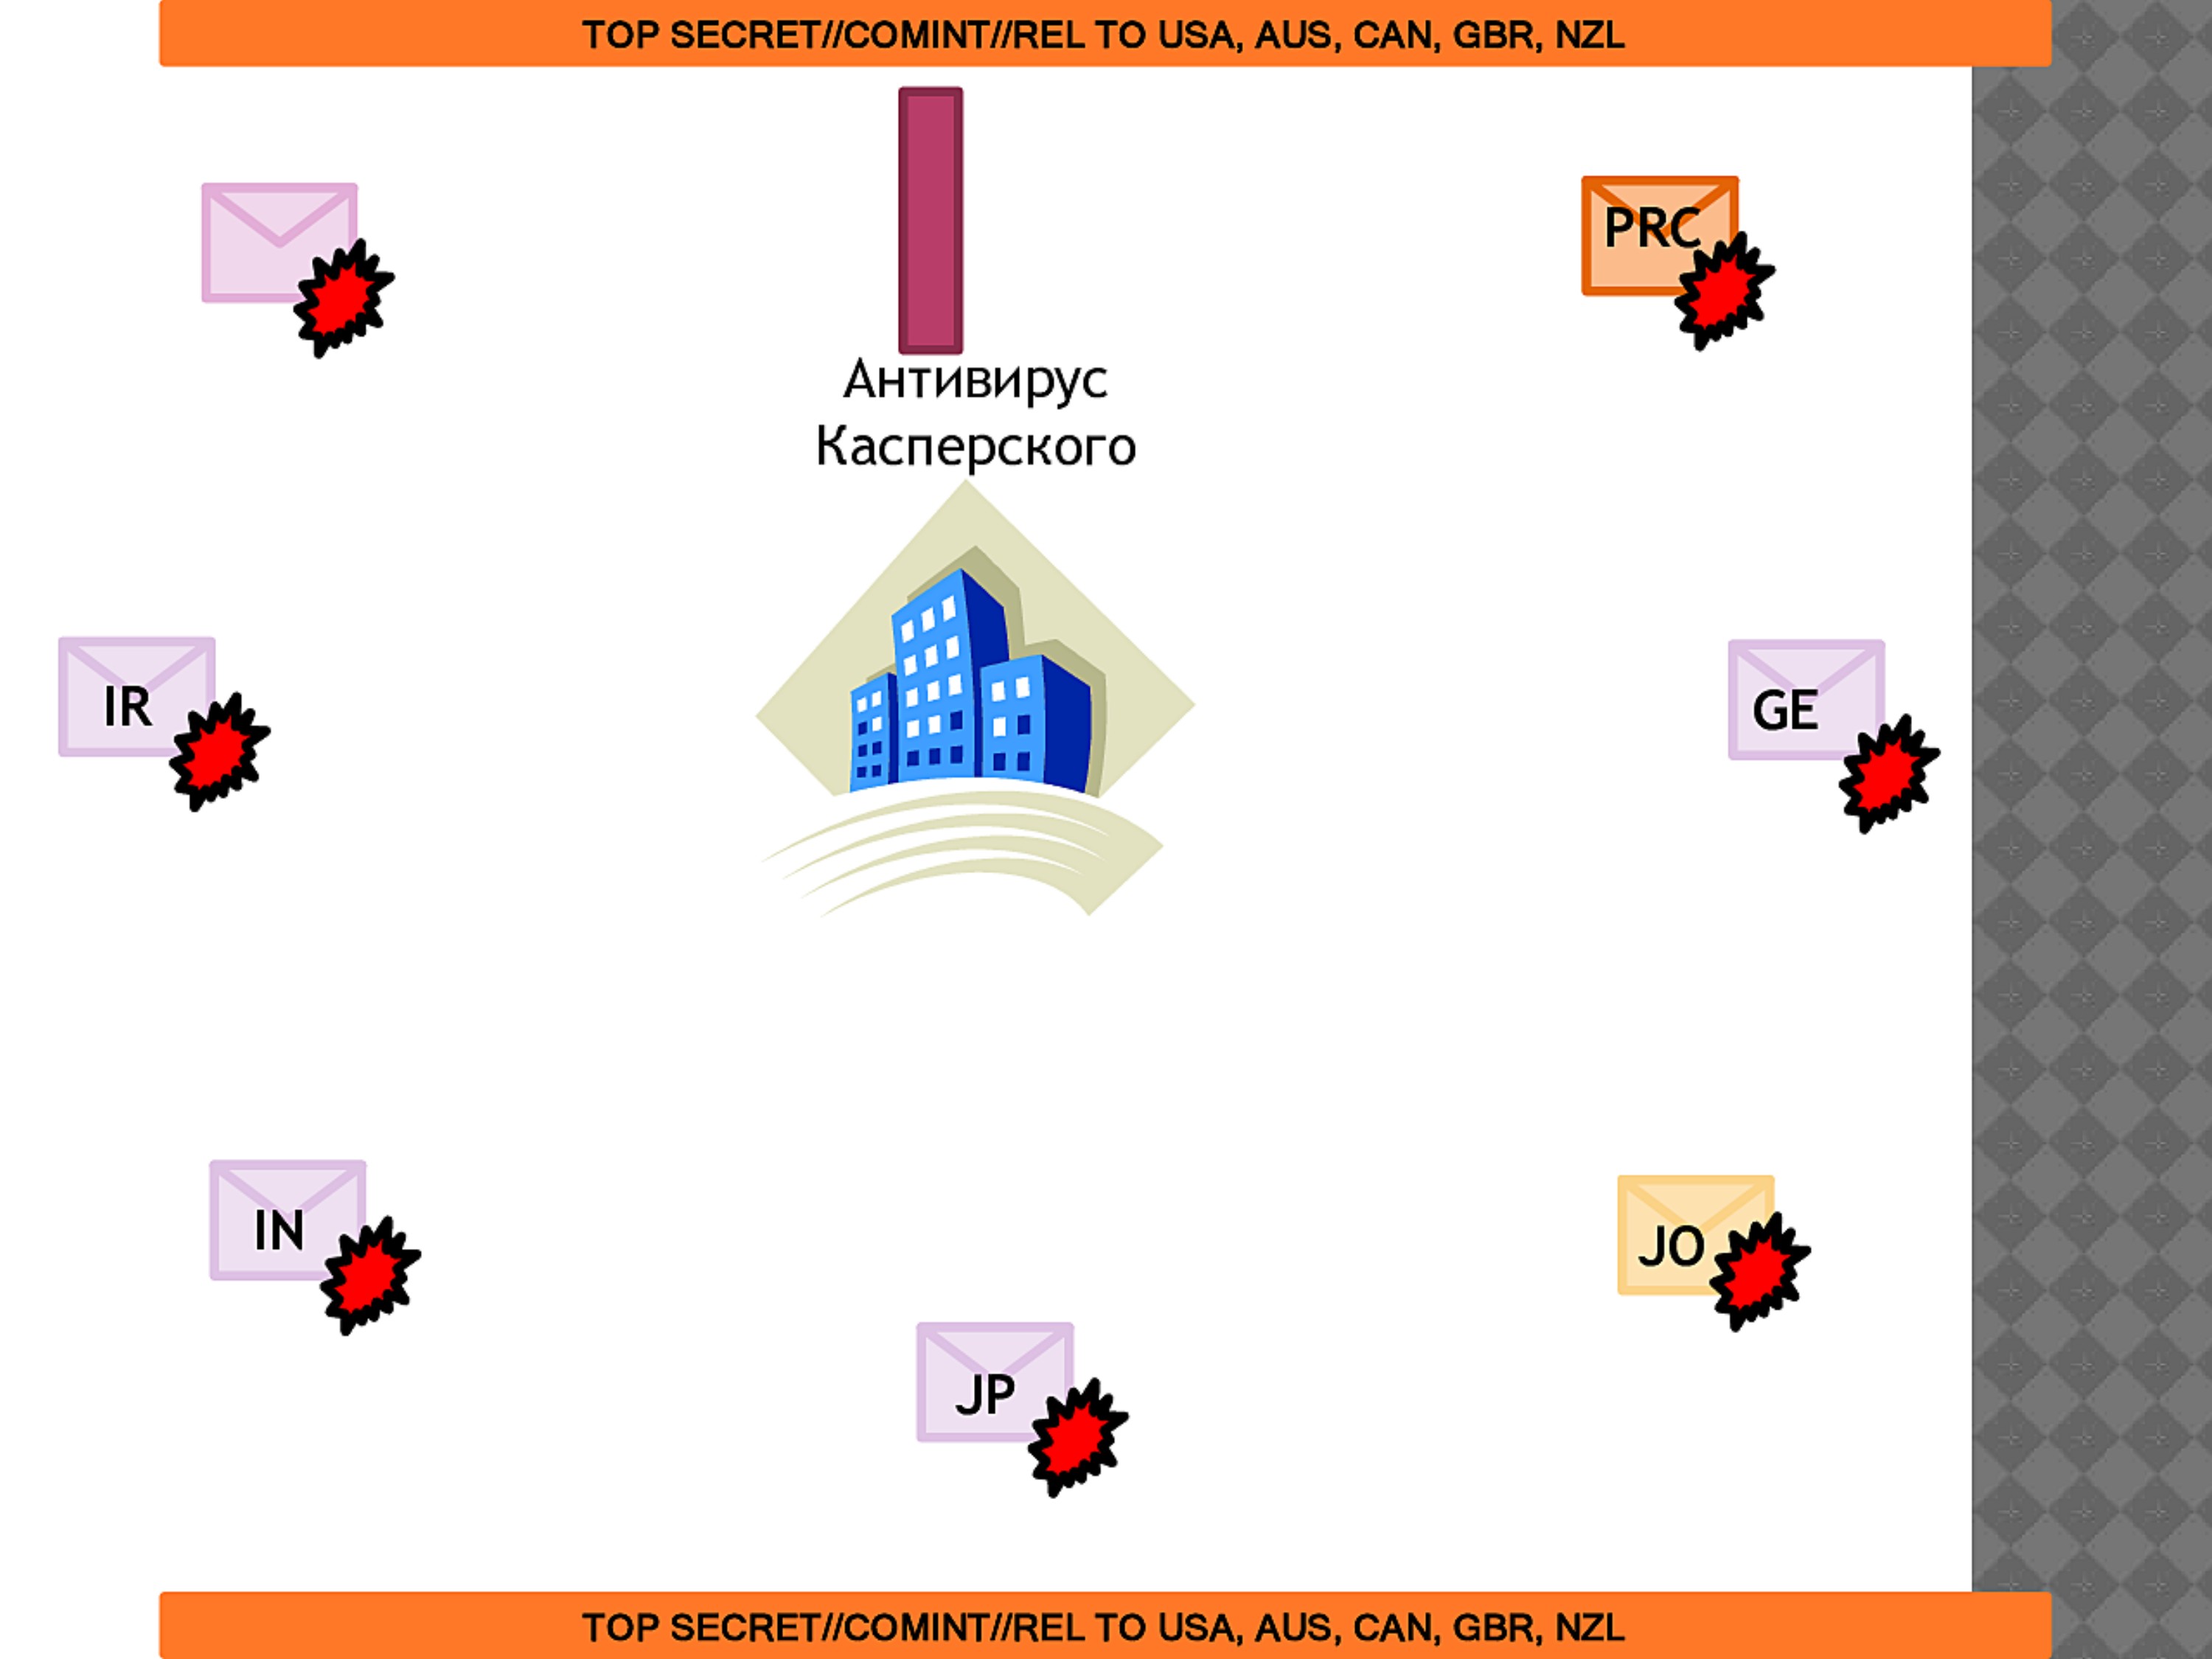
IR
IN
Антивирус
Касперского
JP
JO
PRC
GE
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
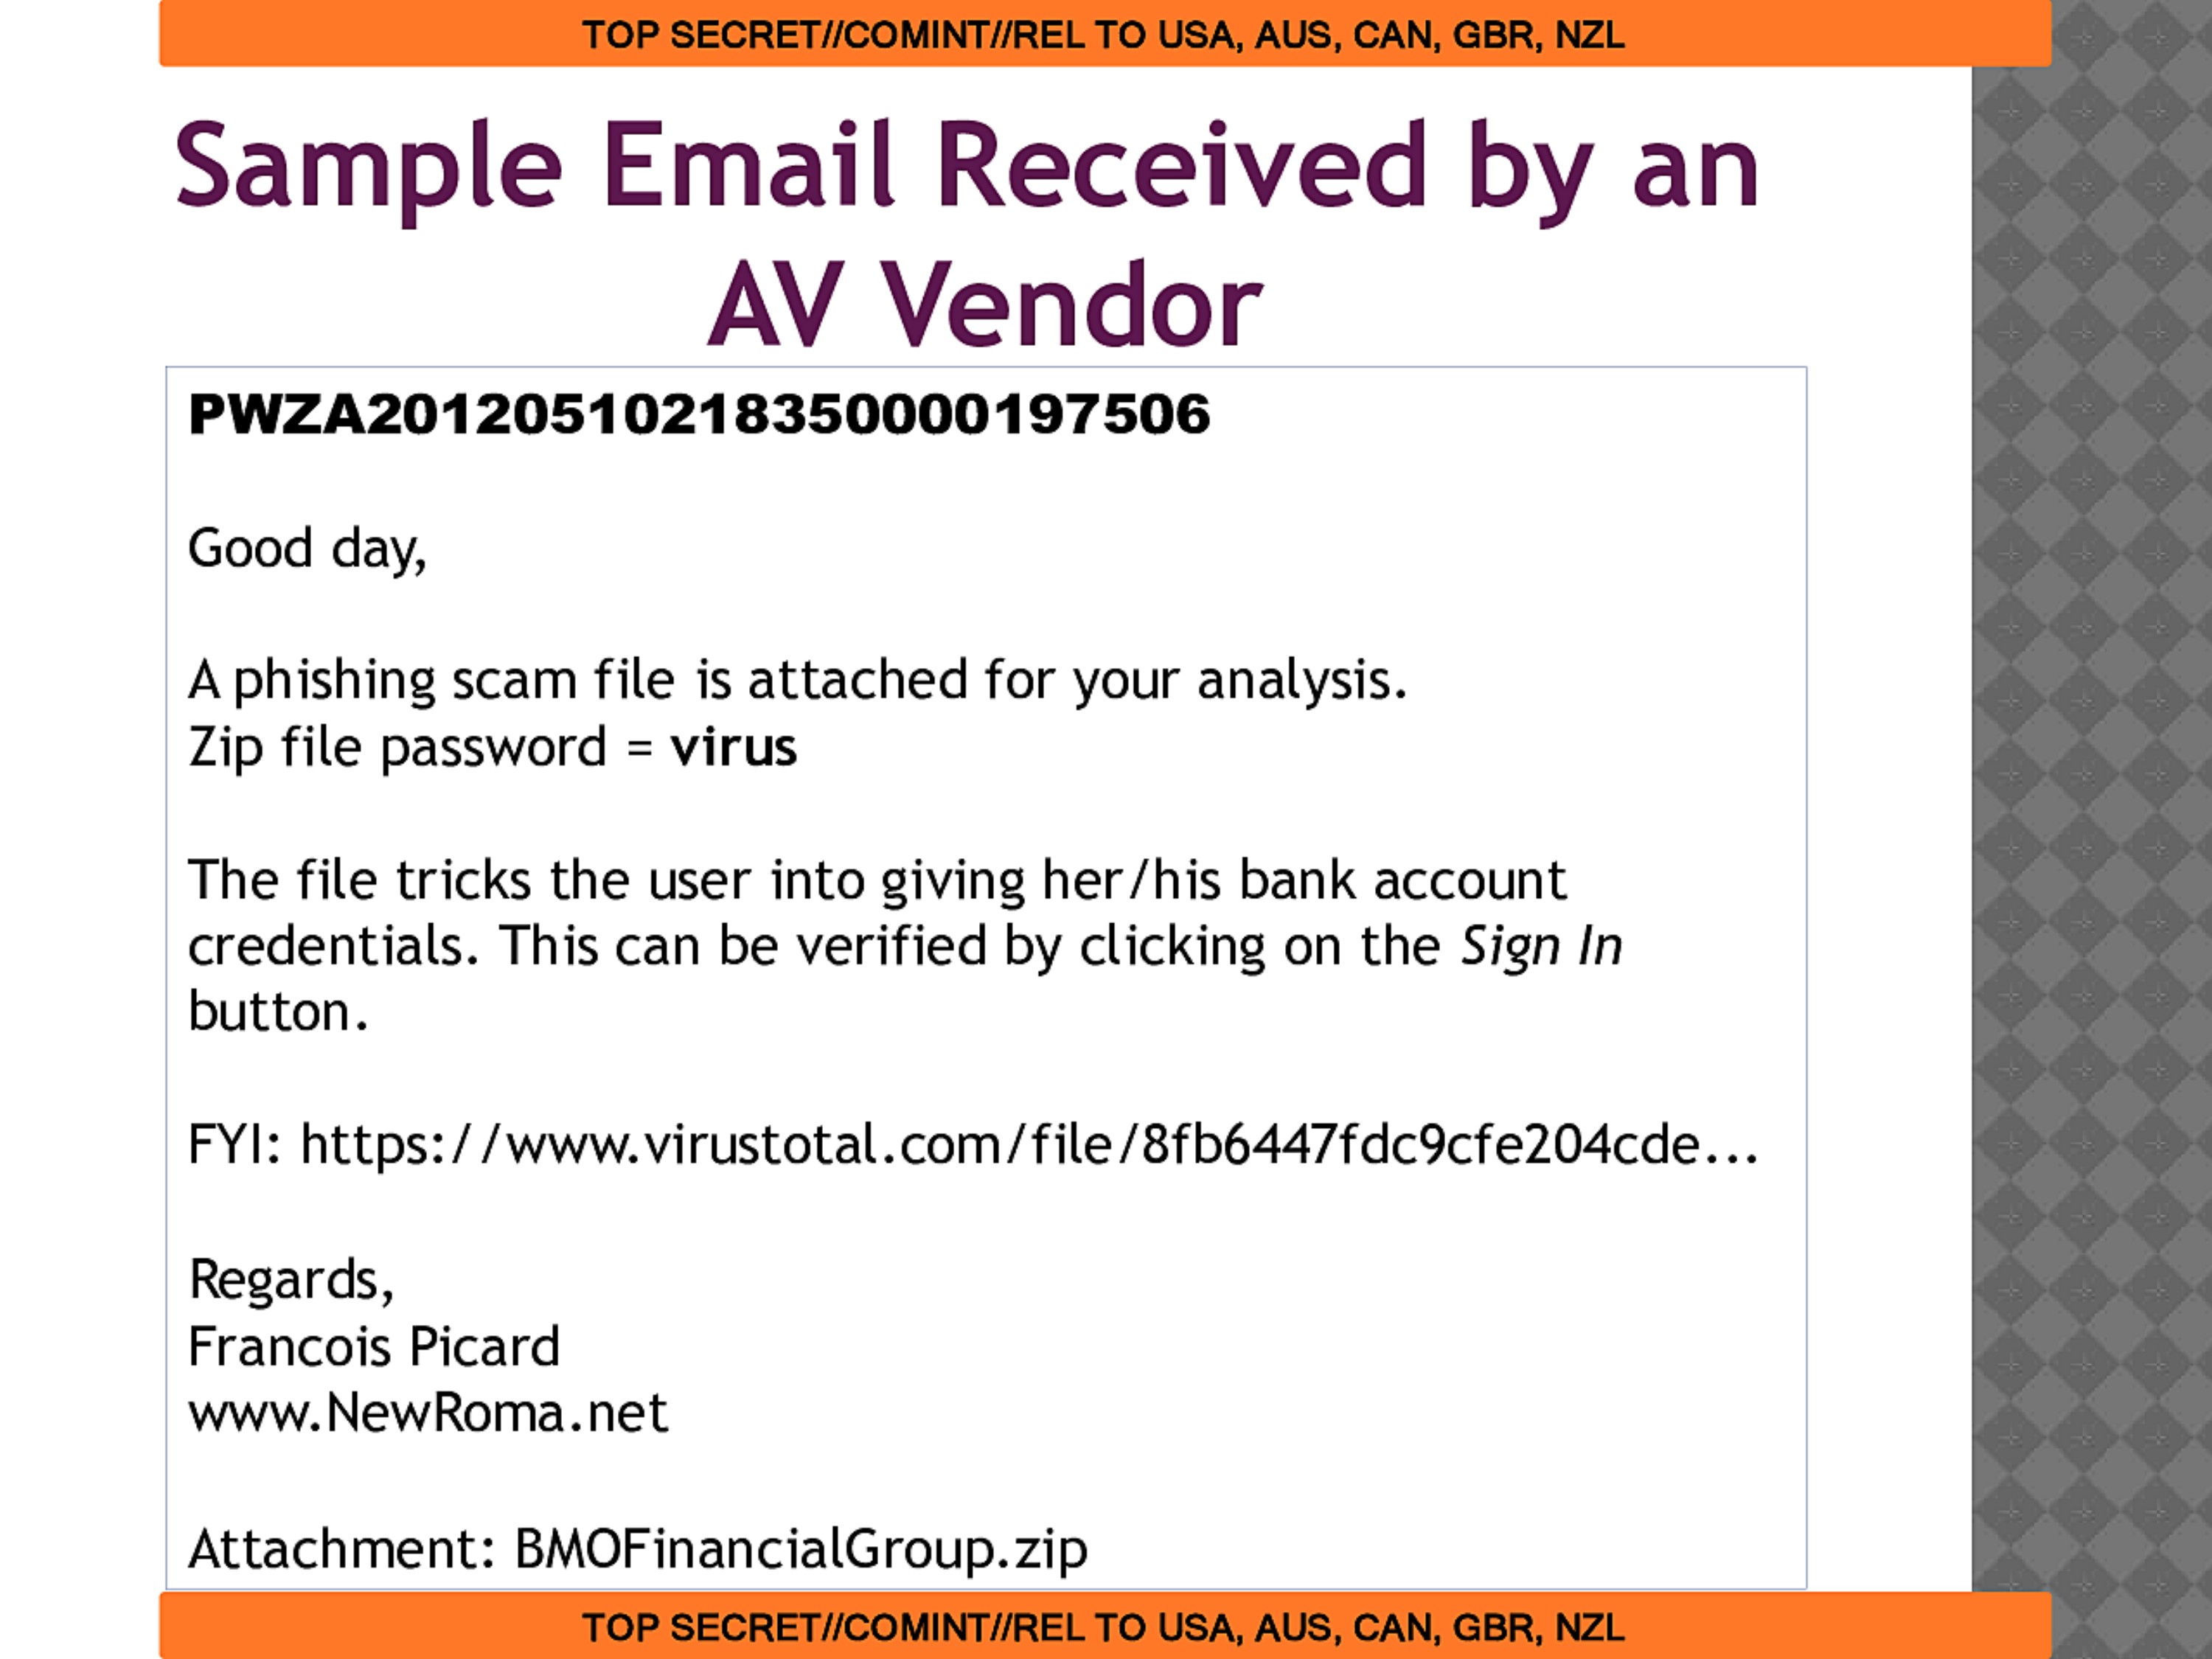
Sample Email Received by an AV Vendor
PWZA20120510218350000197506
Good day,
A phishing scam file is attached for your analysis.
Zip file password = virus
The file tricks the user into giving her/his bank account
credentials. This can be verified by clicking on the Sign In
button.
FYI: https://www.virustotal.com/file/8fb6447fdc9cfe204cde...
Regards,
Francois Picard
www.NewRoma.net
Attachment: BMOFinancialGroup.zip
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Duh
Duh
Duh
Duh
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
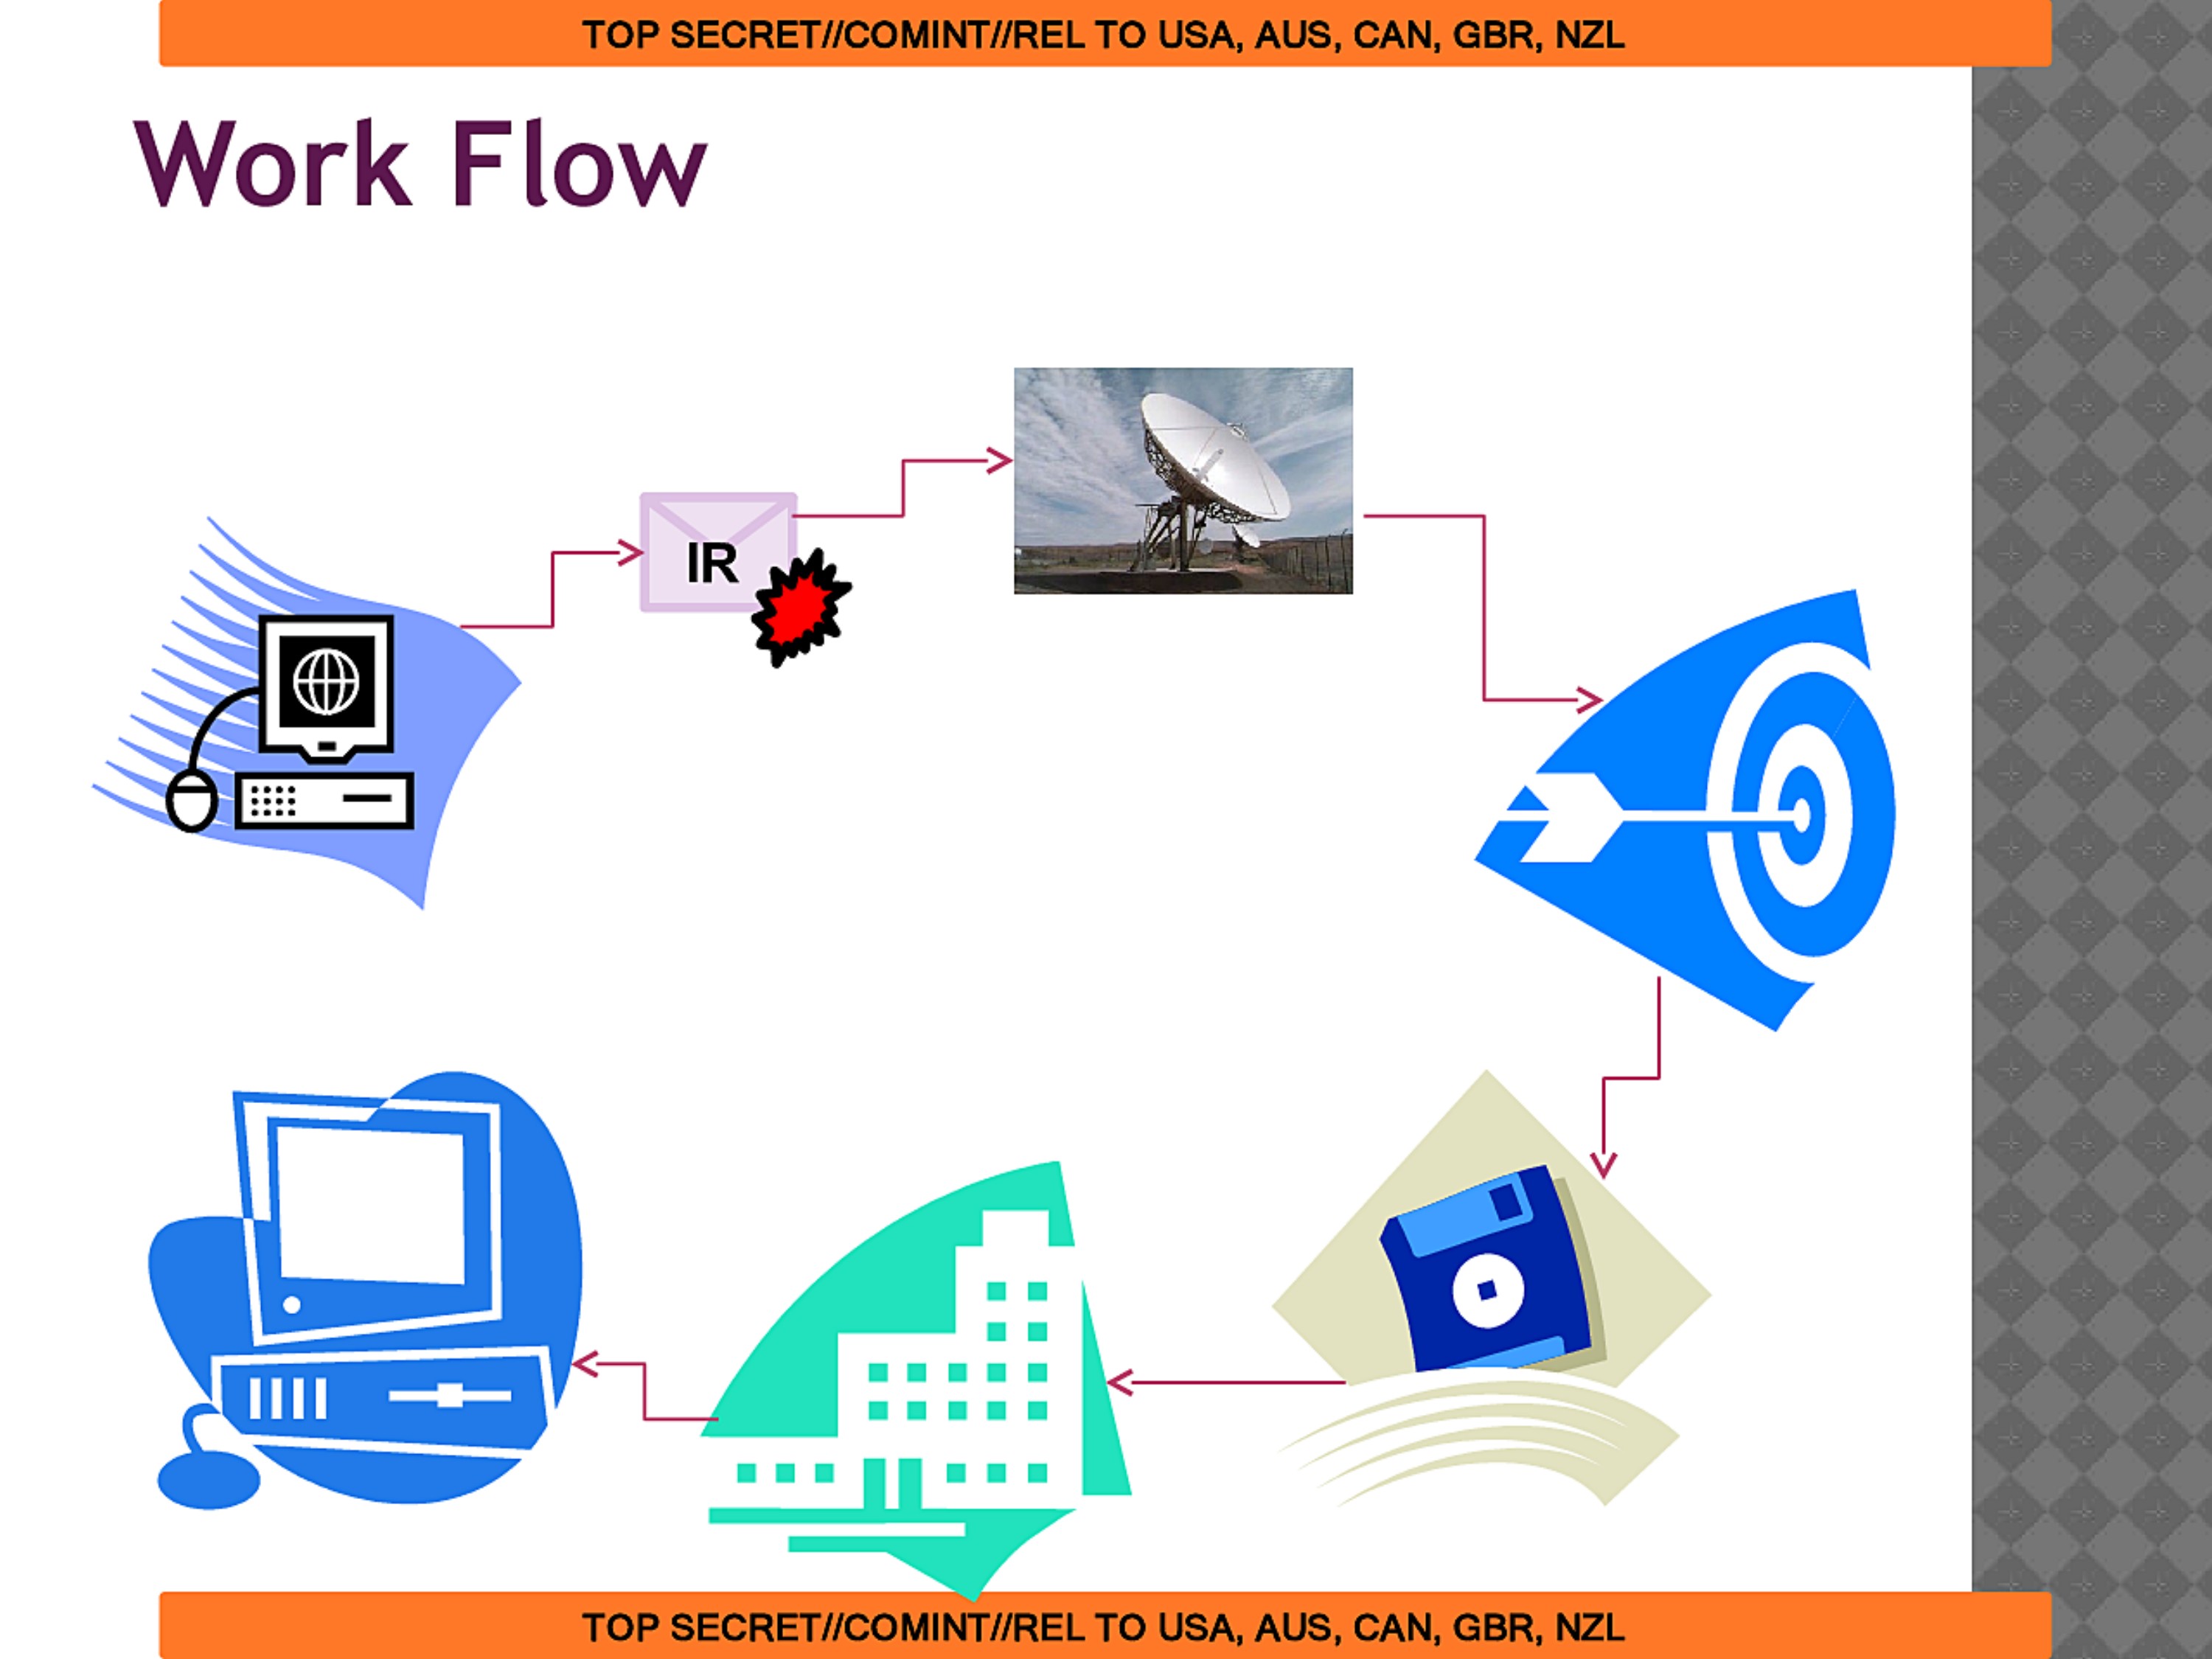
Work Flow
IR
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
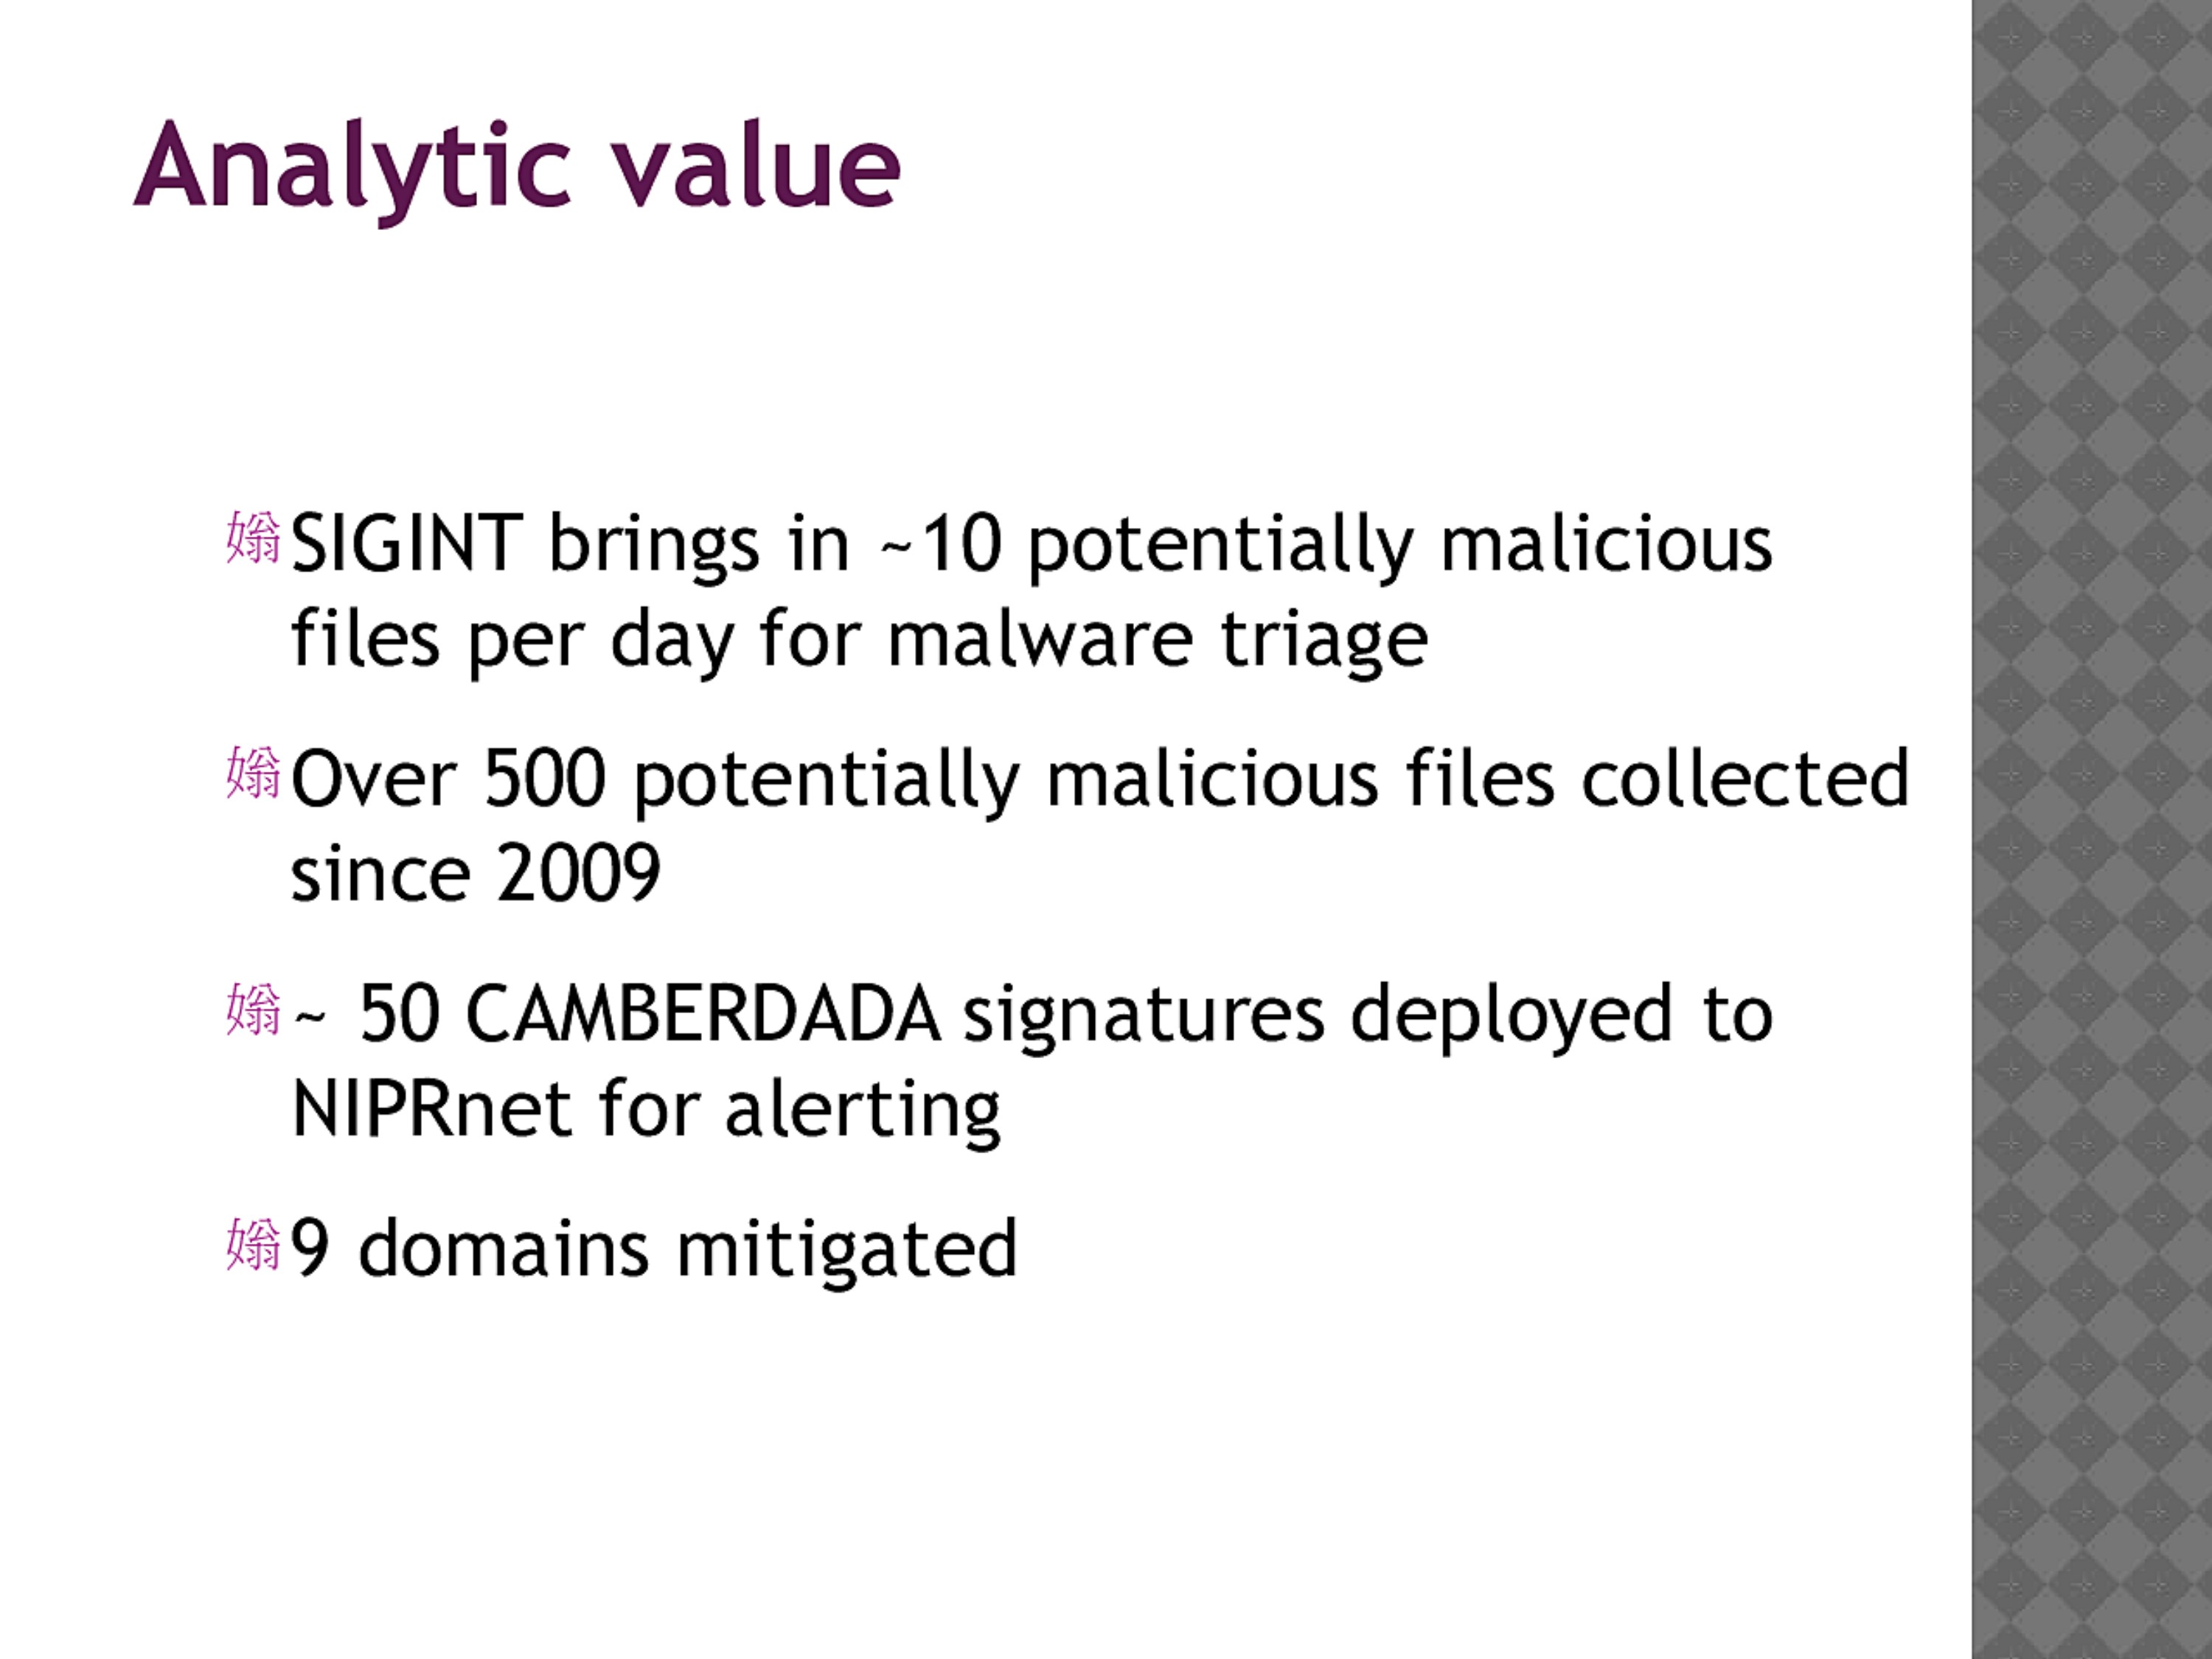
Analytic value
- SIGINT brings in ~10 potentially malicious files per day for malware triage
- Over 500 potentially malicious files collected since 2009
- ~ 50 CAMBERDADA signatures deployed to NIPRnet for alerting
- 9 domains mitigated
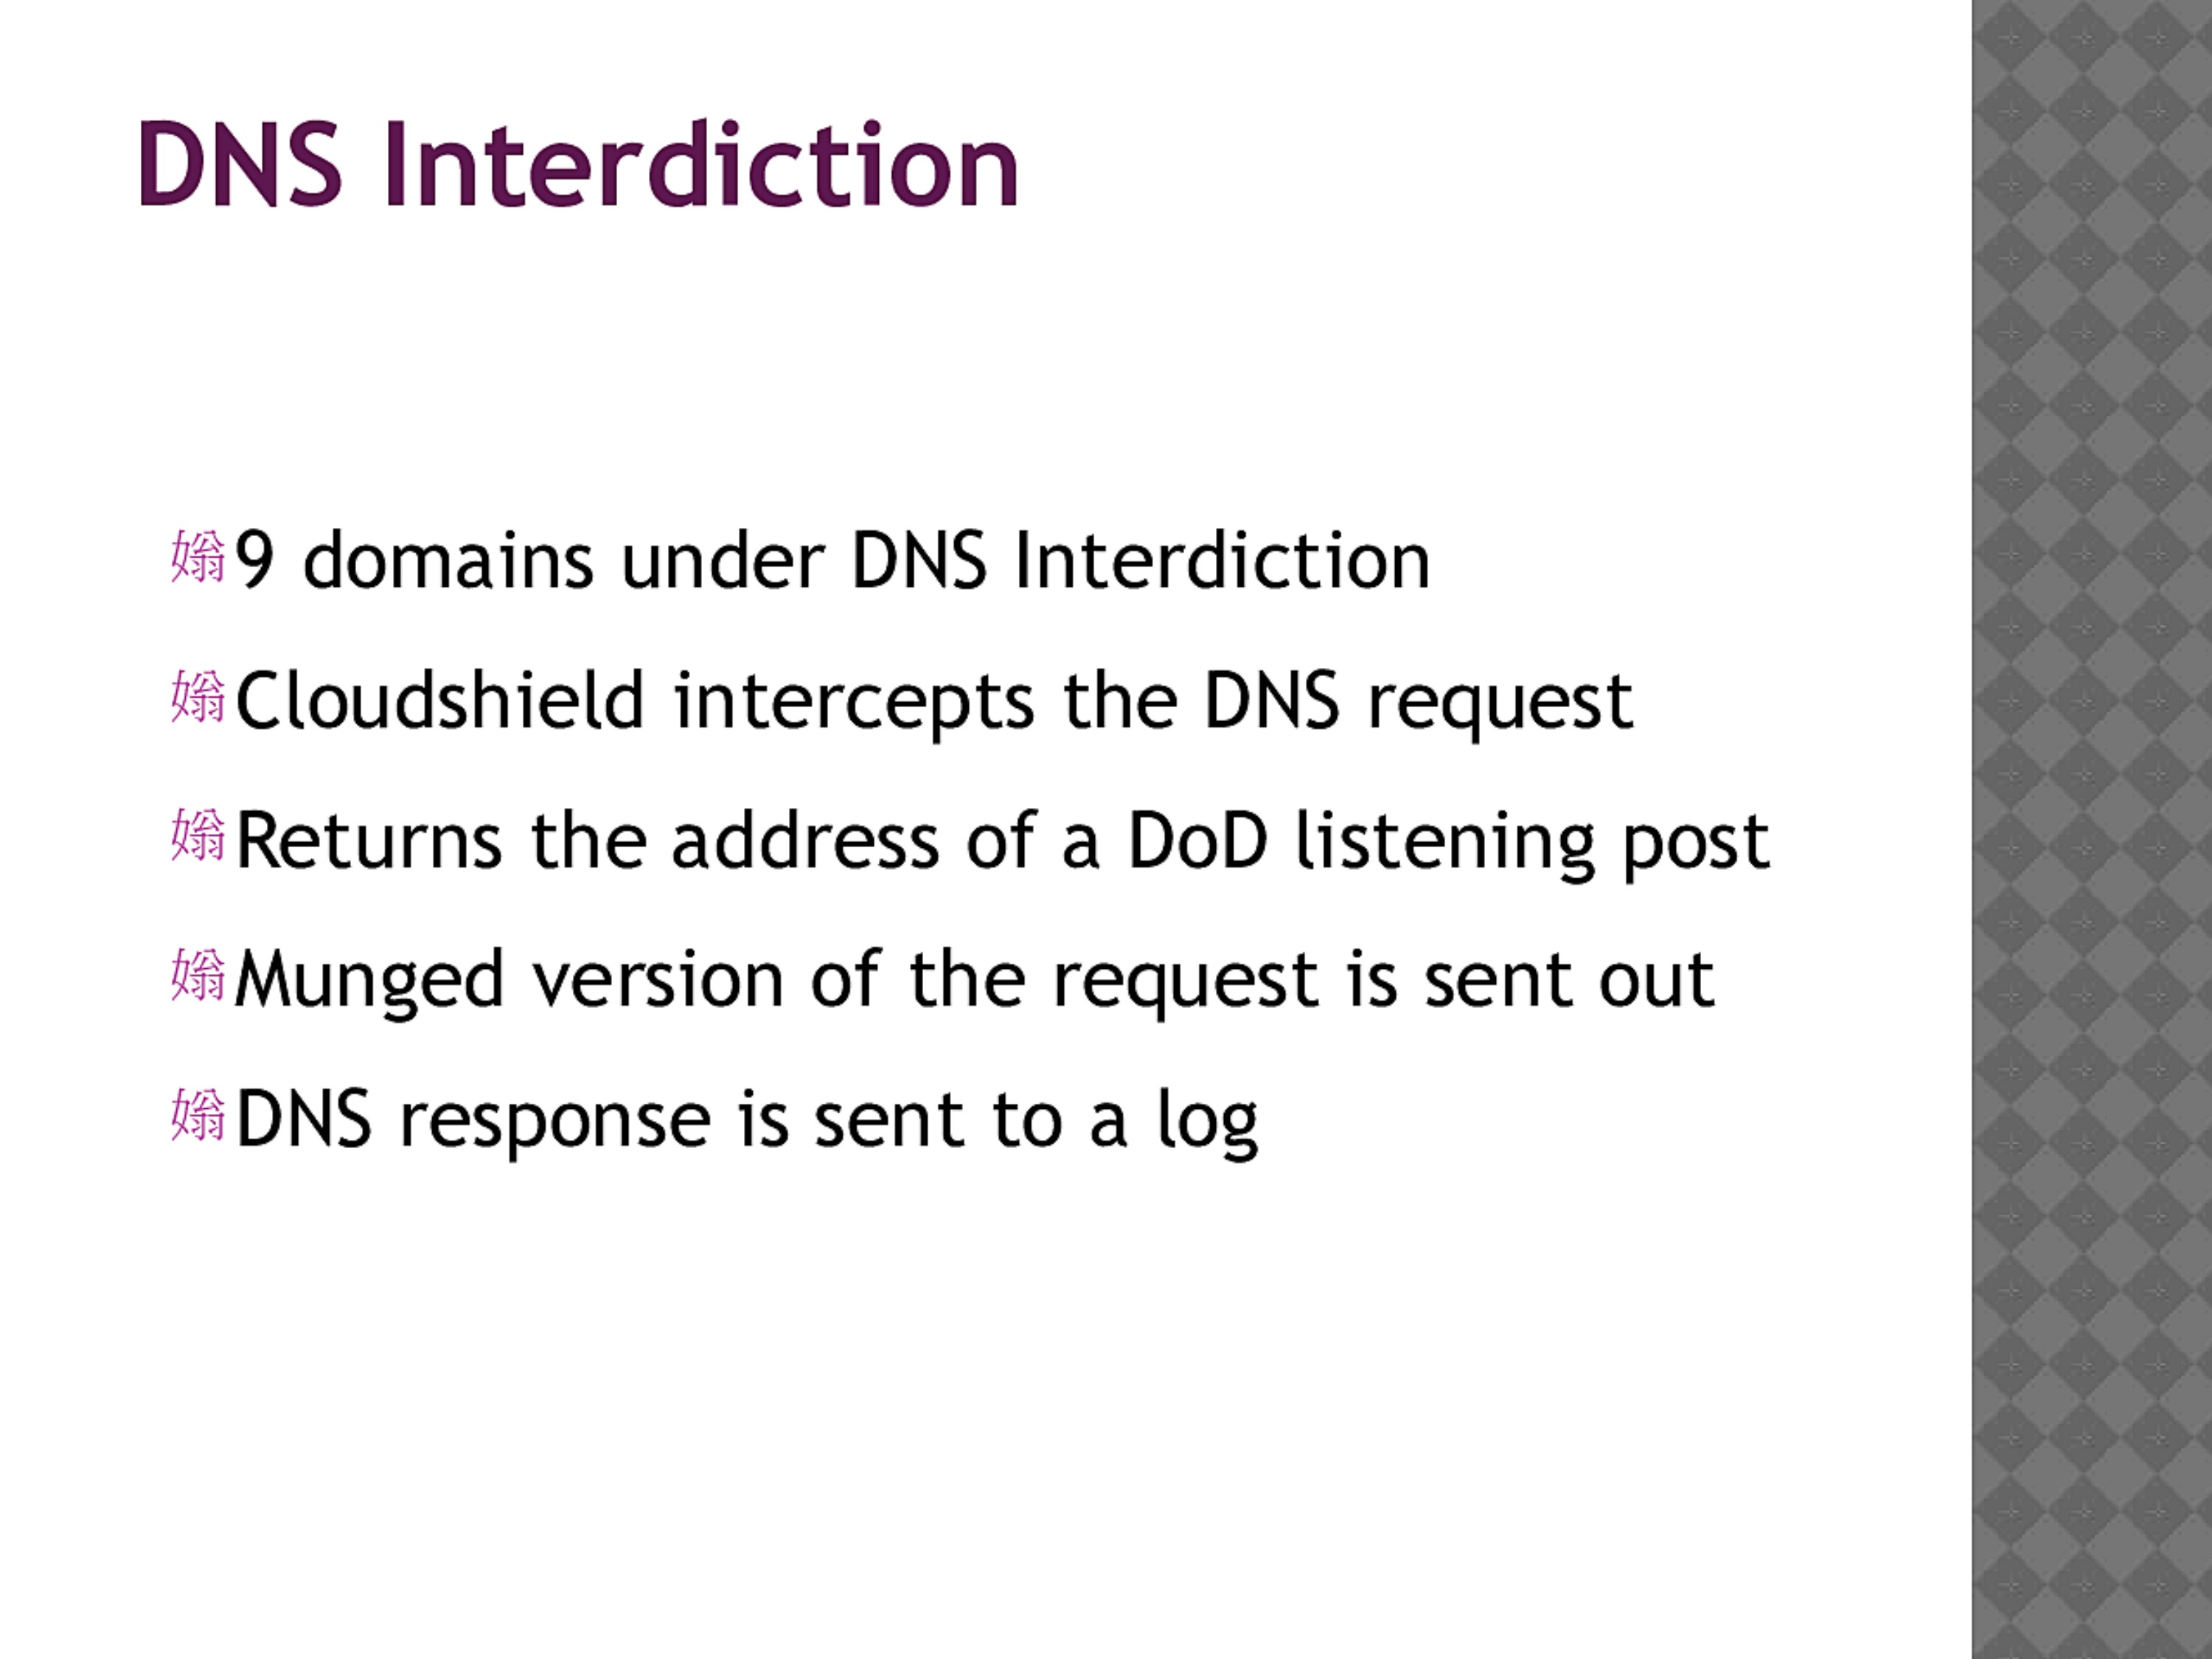
DNS Interdiction
- 9 domains under DNS Interdiction
- Cloudshield intercepts the DNS request
- Returns the address of a DoD listening post
- Munged version of the request is sent out
- DNS response is sent to a log
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
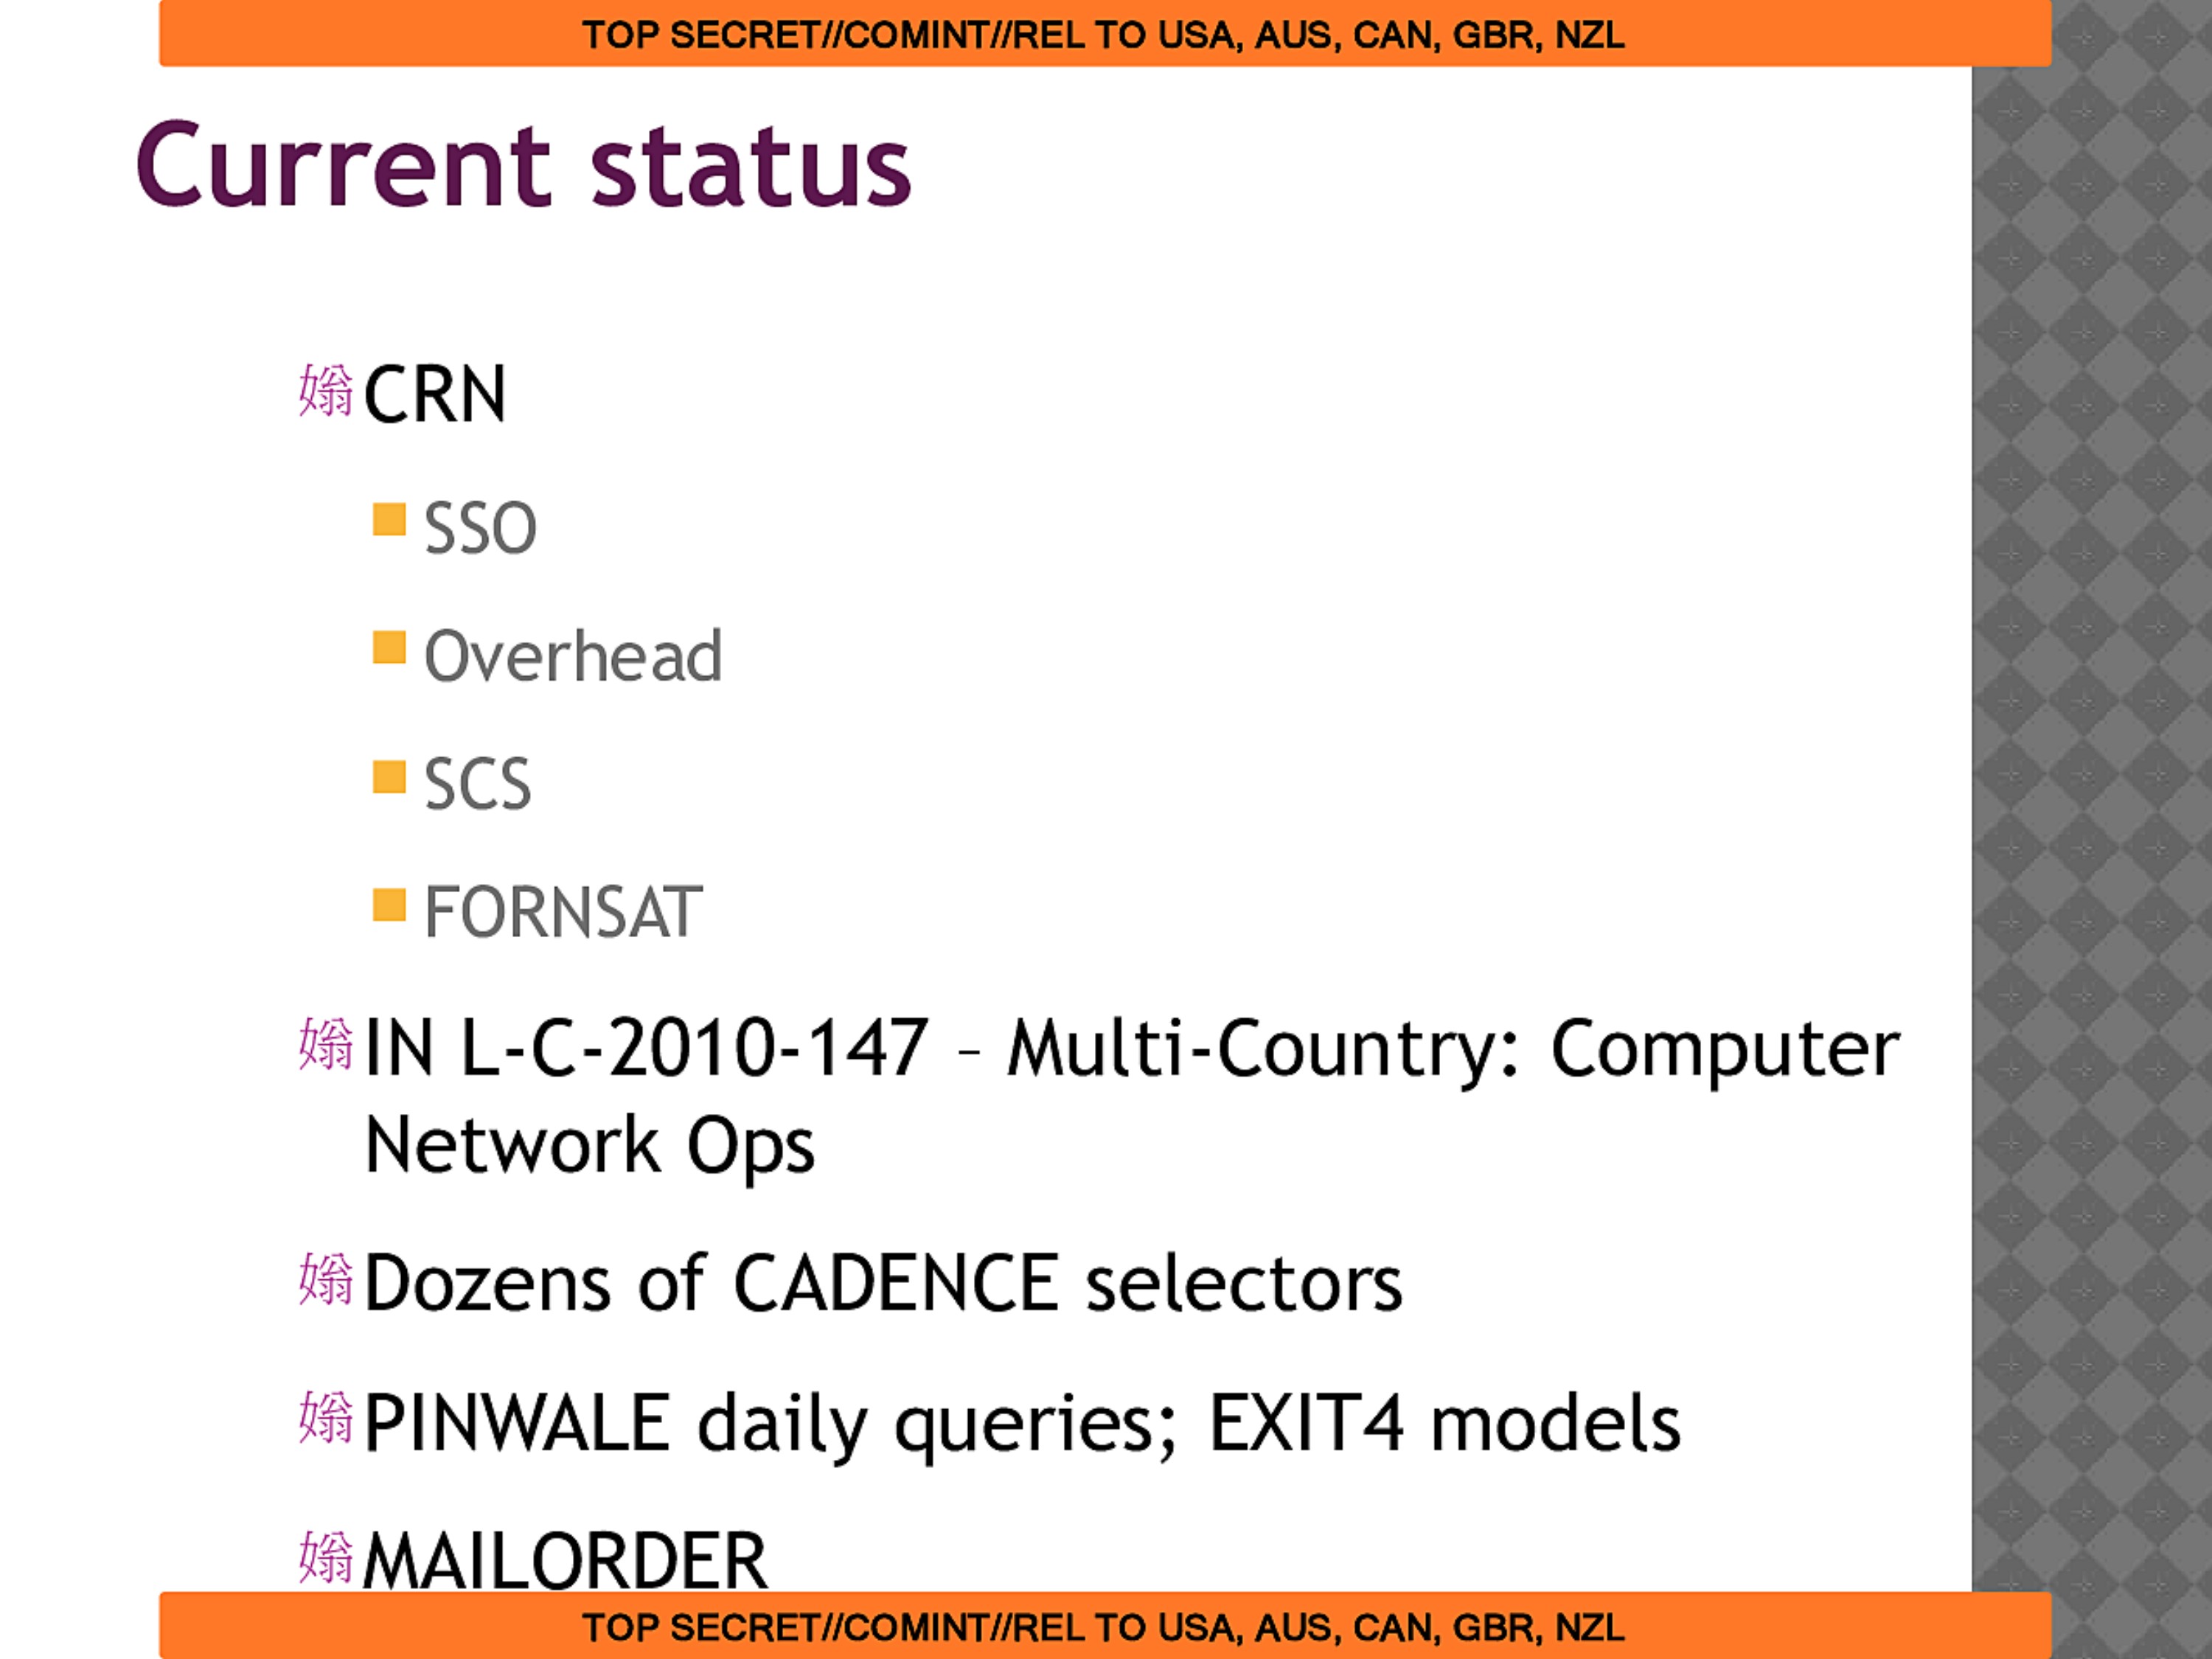
Current status
- CRN
- SSO
- Overhead
- SCS
- FORNSAT
- IN L-C-2010-147 - Multi-Country: Computer Network Ops
- Dozens of CADENCE selectors
- PINWALE daily queries; EXIT4 models
- MAILORDER
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
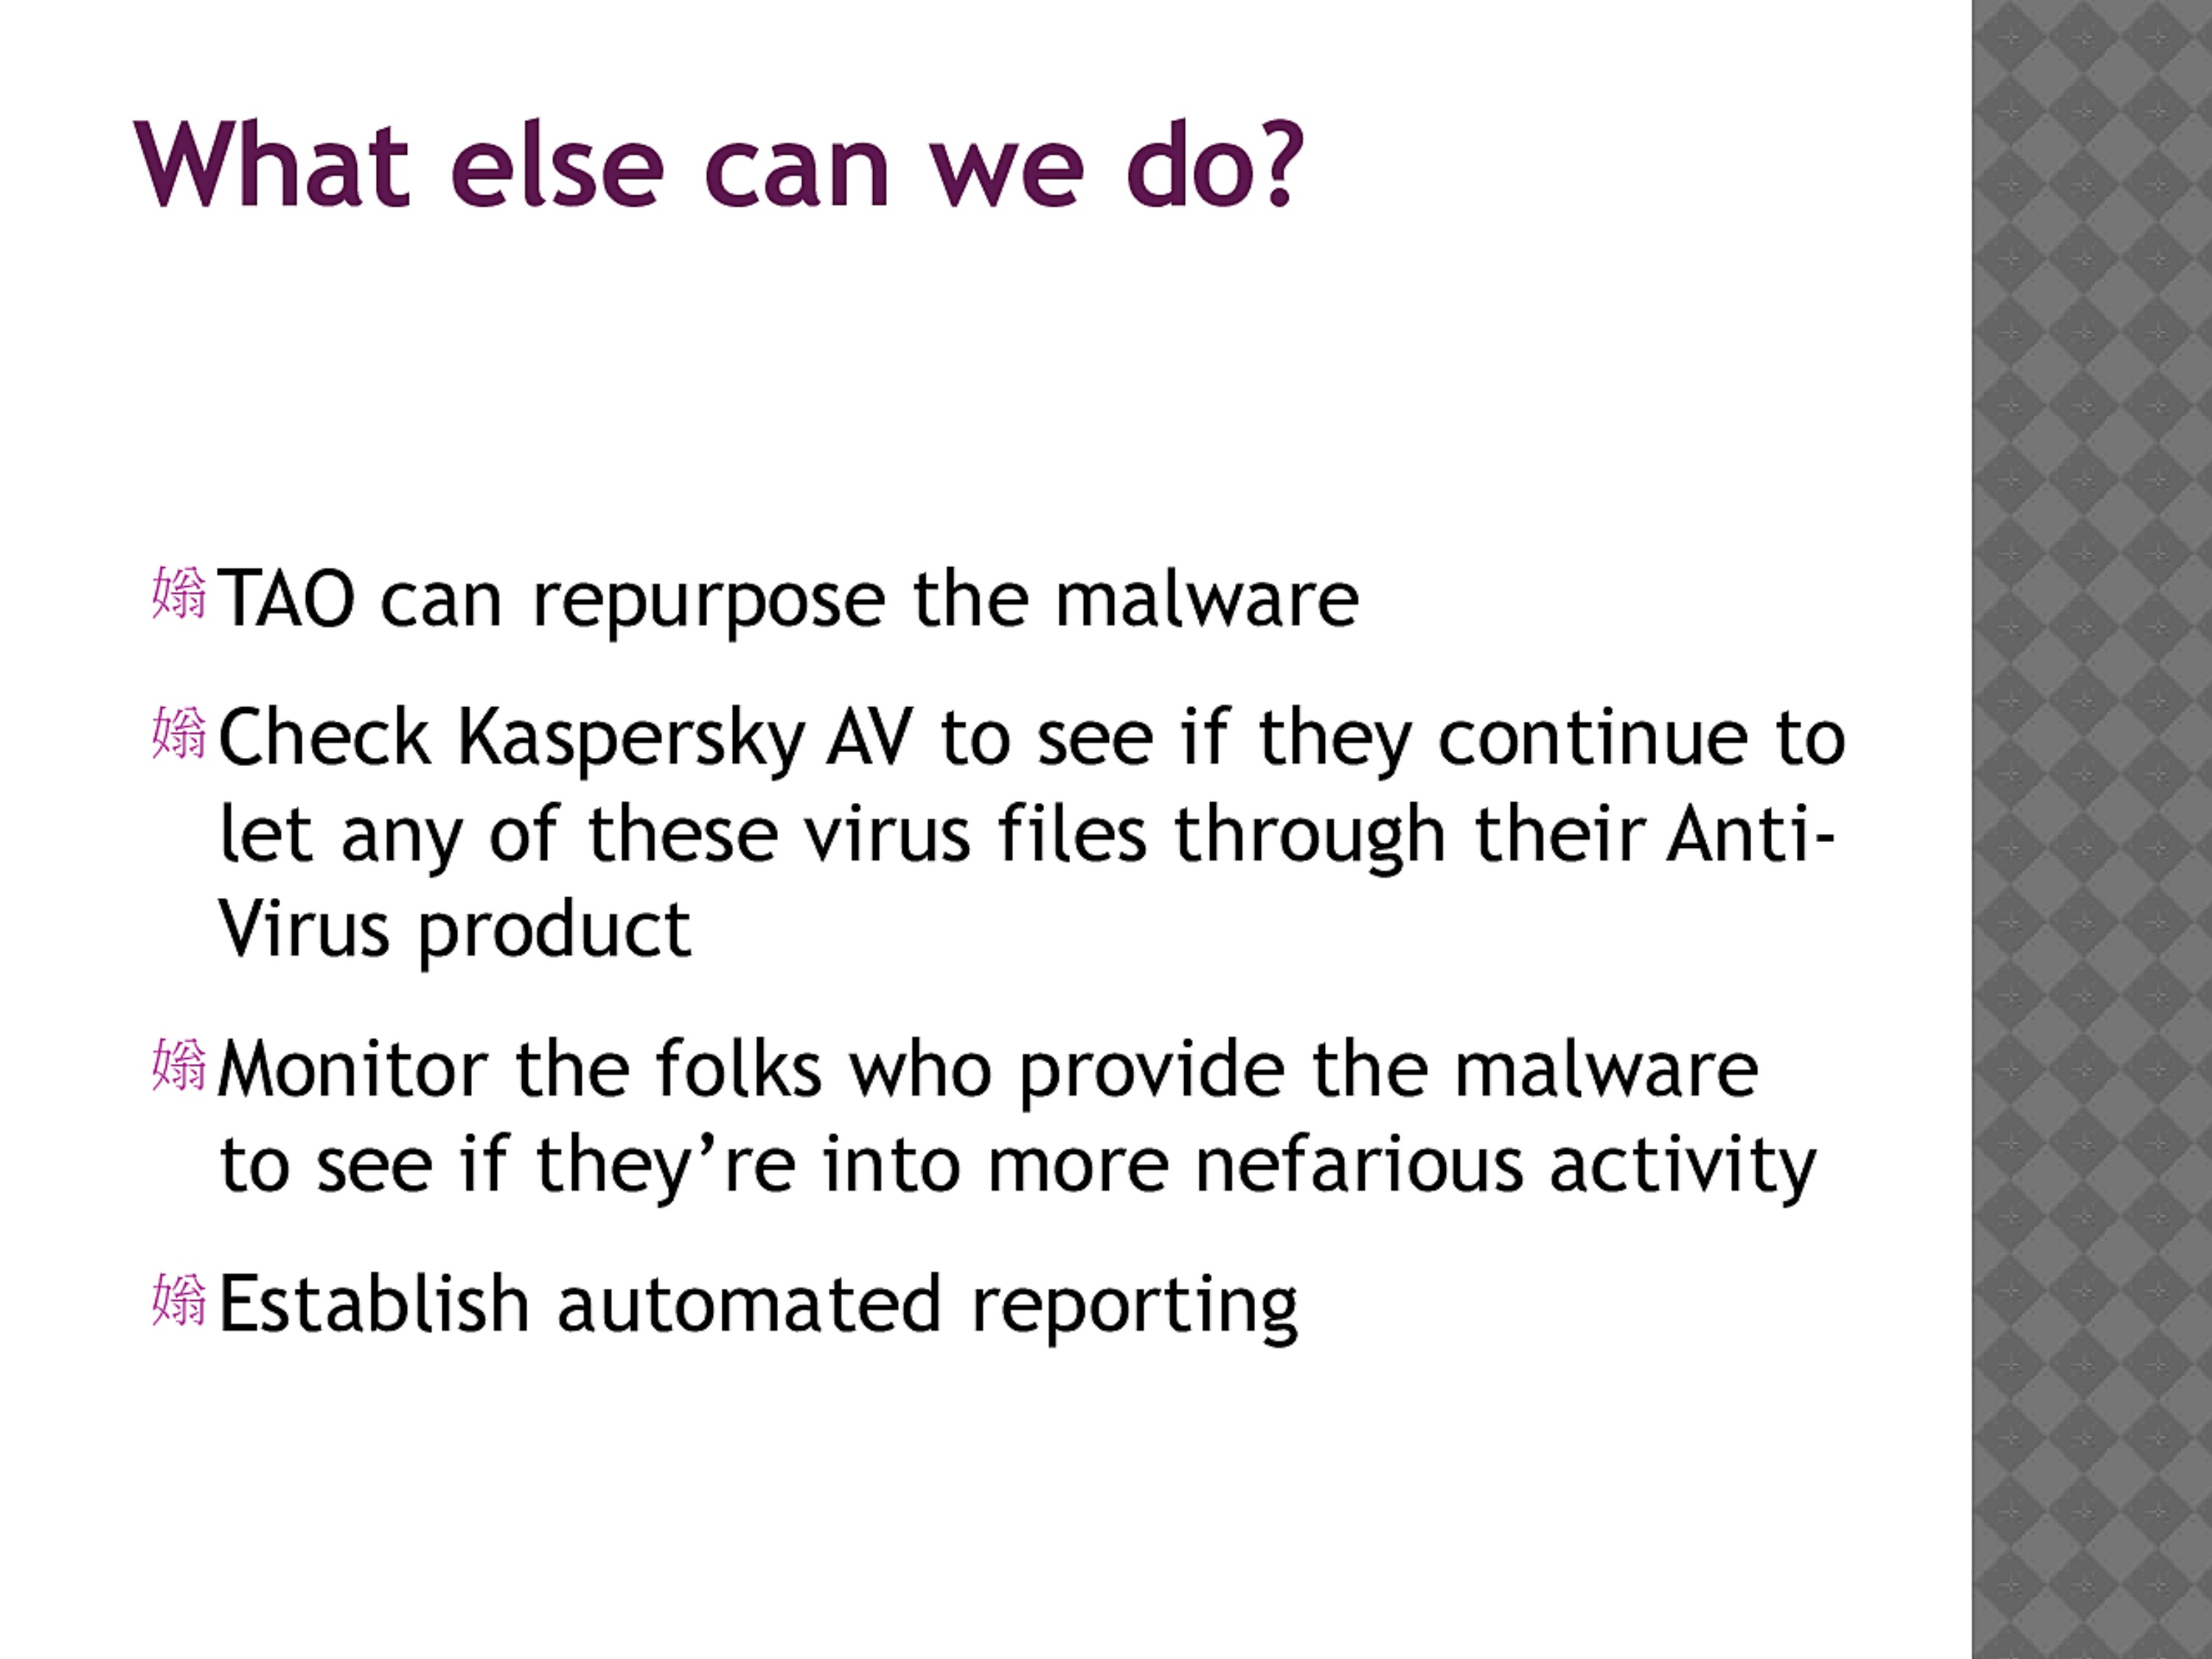
What else can we do?
- TAO can repurpose the malware
- Check Kaspersky AV to see if they continue to let any of these virus files through their Anti-Virus product
- Monitor the folks who provide the malware to see if they're into more nefarious activity
- Establish automated reporting
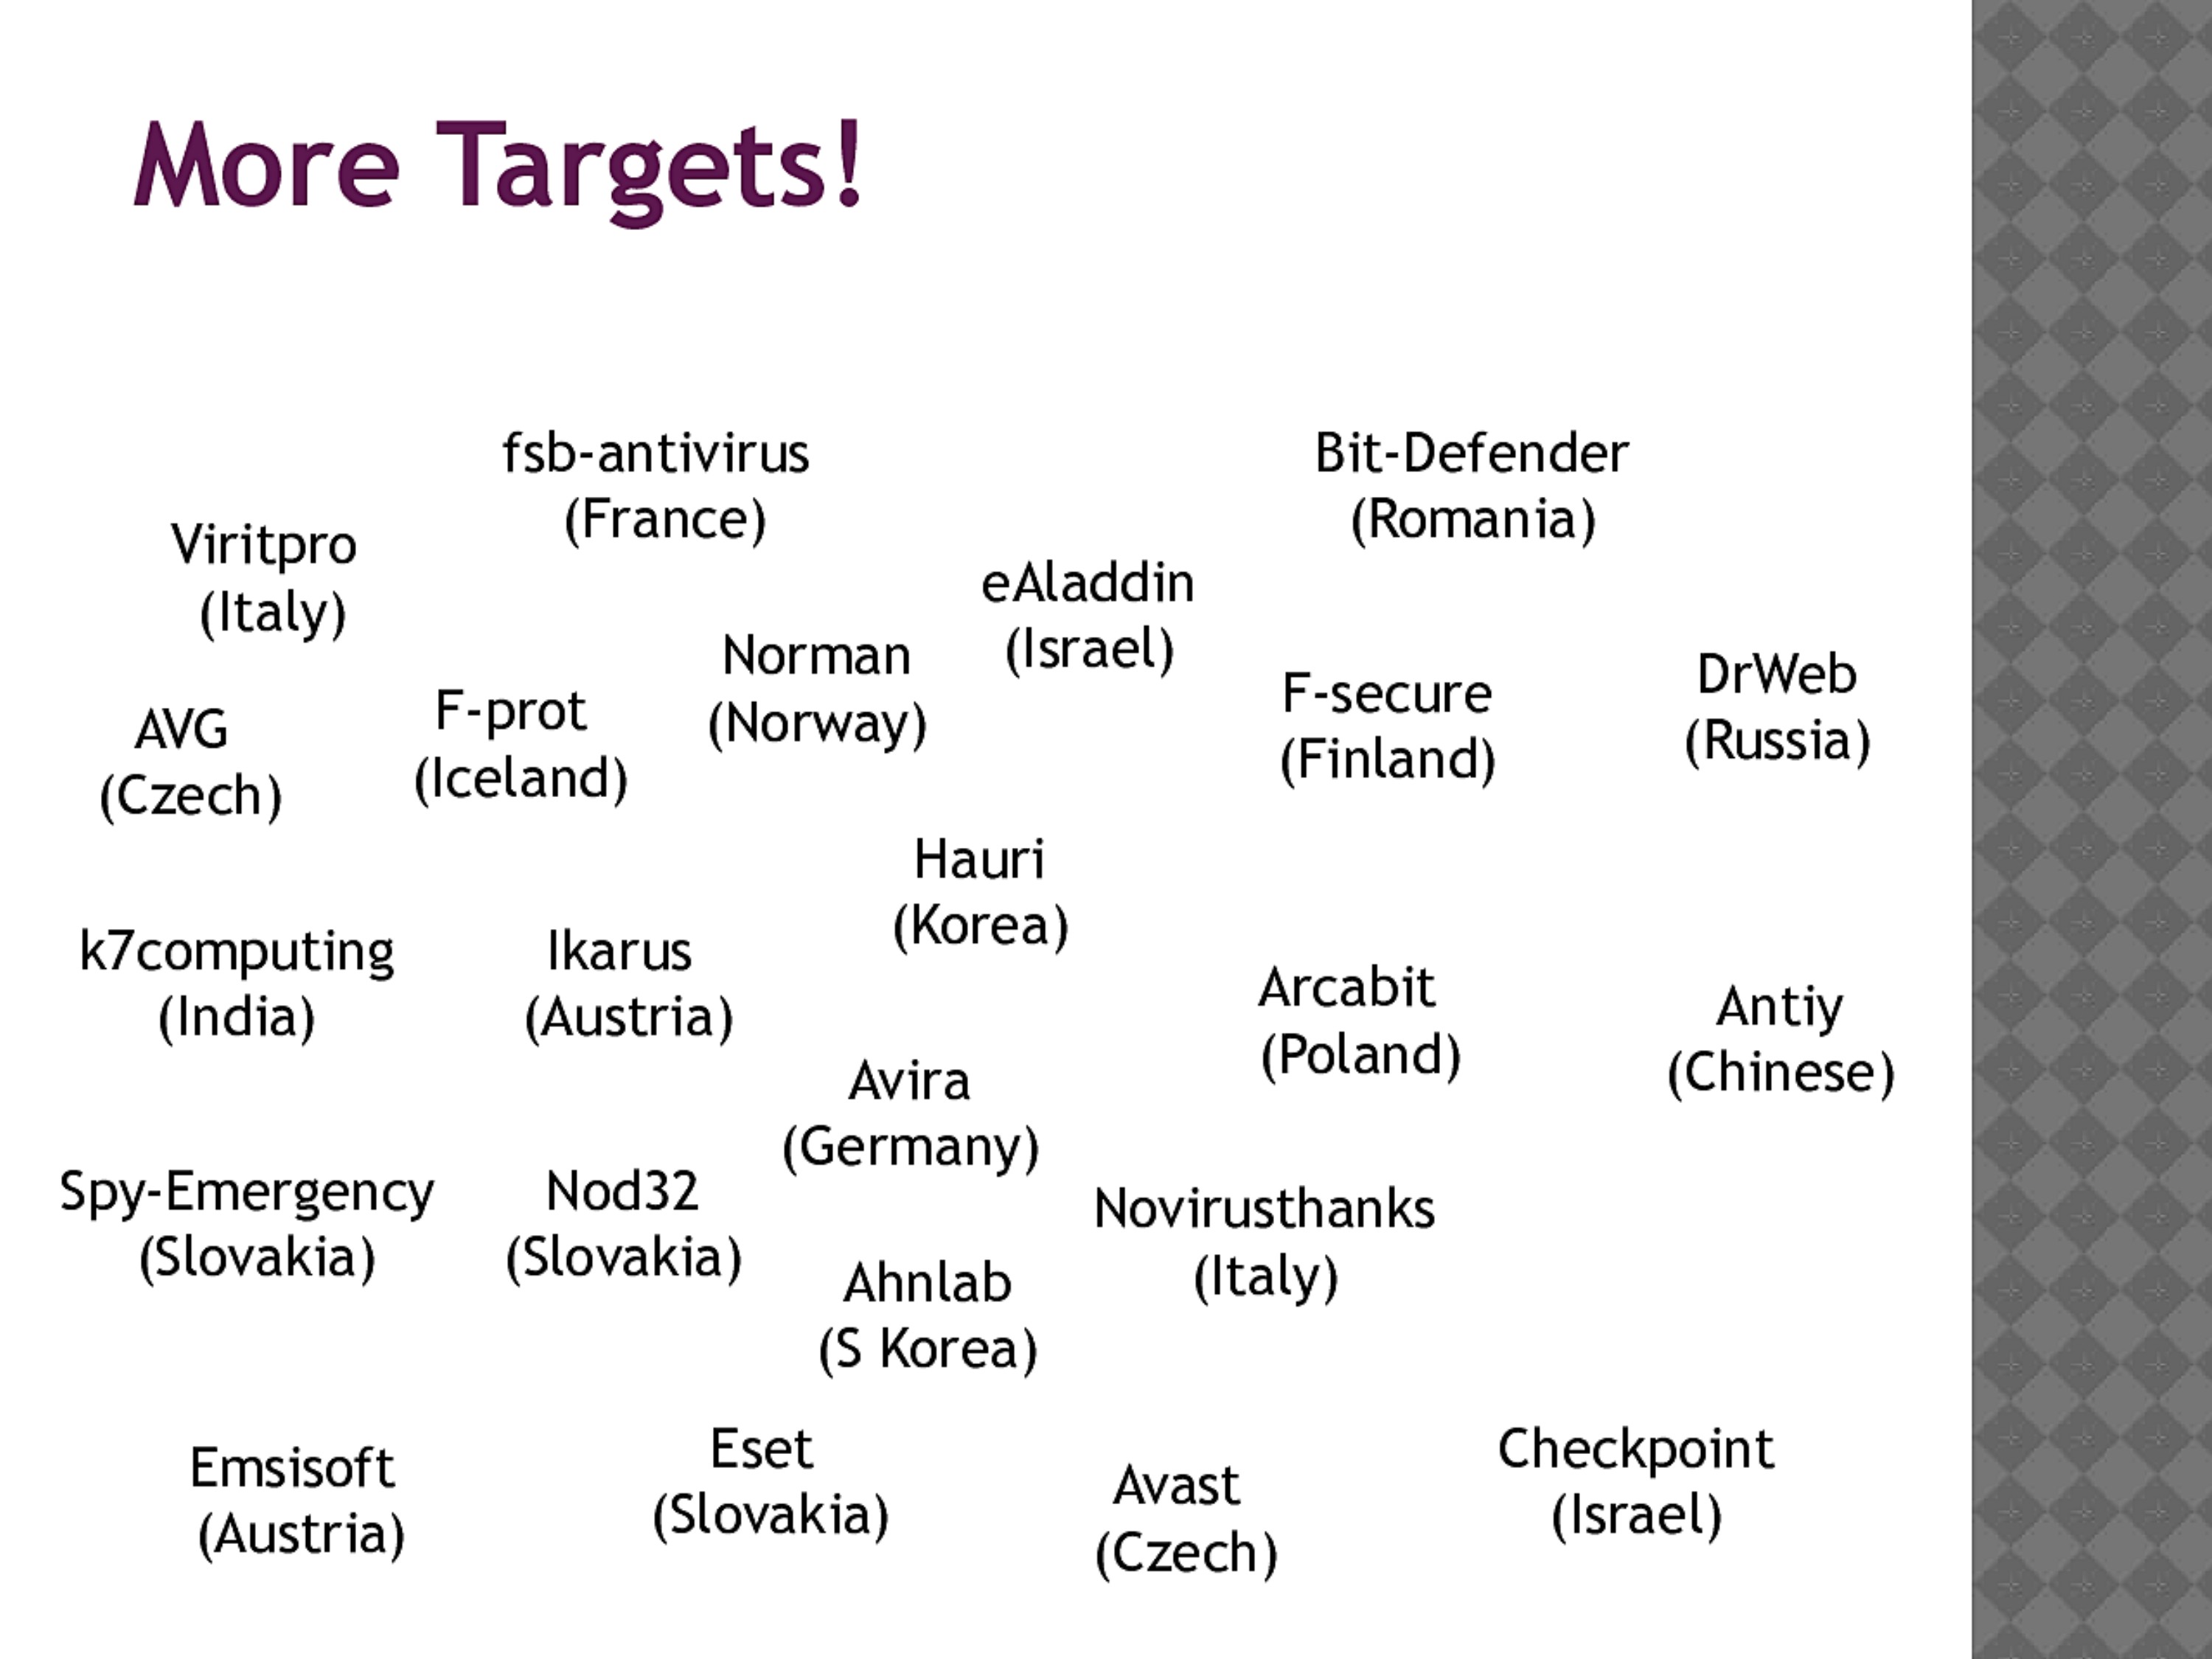
More Targets!
- fsb-antivirus (France)
- Bit-Defender (Romania)
- Viritpro (Italy)
- eAladdin (Israel)
- F-secure (Finland)
- AVG (Czech)
- F-prot (Iceland)
- Norman (Norway)
- DrWeb (Russia)
- k7computing (India)
- Ikarus (Austria)
- Hauri (Korea)
- Arcabit (Poland)
- Antiy (Chinese)
- Avira (Germany)
- Spy-Emergency (Slovakia)
- Nod32 (Slovakia)
- Ahnlab (S Korea)
- Novirusthanks (Italy)
- Emsisoft (Austria)
- Eset (Slovakia)
- Avast (Czech)
- Checkpoint (Israel)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
THANK YOU!
[REDACTED]
I4121
[REDACTED]
[REDACTED]
V252
[REDACTED]
[REDACTED](s)
[REDACTED](s)
Derived From: NSA/CSSM 1-52
Dated: 20070108
Declassify On: 20370301
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Published in the Same Report
(2 documents)
-
NDIST — GCHQ’s Developing Cyber Defence Mission [pdf]
GCHQ’s NDIST sets out a developing cyber defence mission to reduce vulnerability and harm while enabling prosperity, centered on building a global-level picture of strategic threats and sharing intelligence with allies. The team anchors this work in massive telemetry, claiming roughly 100 million malware events collected per day to drive situational awareness.
-
Kaspersky User-Agent Strings [pdf]
This September 2008 NSA technical report reveals that the agency discovered Kaspersky antivirus software's user-agent strings contain encoded serial numbers and can function as unique machine identifiers, allowing tracking of individual computers running the Russian security software across intercepted network traffic collected through the YACHTSHOP surveillance program.
Related Documents
-
X-KEYSCORE as a SIGDEV tool 2009 [pdf]
A 2009 TOP SECRET NSA presentation describing XKeyscore as a SIGINT development tool — explaining how it captures and temporarily stores the full content of internet traffic (the 95%+ that was previously dropped because it didn't match any target) across 125 sites worldwide, "slowing down the internet" so analysts can retroactively reconstruct a target's entire online session, discover new targets, and search the content of documents, web searches, emails and chats that contain no tasked selector.
Programs: XKEYSCORE · PINWALE · TRAFFICTHIEF · MARINA · AGILITY · PILBEAM · MAILORDER · CADENCE · NKB · PSC · SSO · UIS“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “FRA has access to controversial surveillance system” - SVT Nyheter ↗ (2013-12-11) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah · Bergman, Sven · Dyfvermark, Joachim · Gallagher, Ryan · Laurin, Fredrik · Struwe, Filip -
SSO dictionary relevant entries [pdf]
This document provides a detailed list of relevant entries related to NSA's Special Source Operations (SSO), highlighting various NSA surveillance and data collection systems used to monitor global communications. It includes descriptions of programs such as BIGBIRD and DISHFIRE, which focus on cable and SMS interception, as well as tools like LOPERS and COURIERSKILL for processing telephony metadata and refining target selection. The entries emphasize the extensive and automated nature of the NSA's intelligence-gathering operations, particularly in relation to undersea cables and telecommunication networks, and underscore the secretive and expansive scope of SSO's global surveillance activities.
Programs: ARTIFICE · BIGBIRD · FAIRVIEW · SSO · POORWILL · PINECONE · BLACKBELT · CADENCE · BLACKNIGHT · SHIPMASTER · COURIERSKILL · THEORYMASTER · WEALTHYCLUSTER · CLIFFSIDE · DISHFIRE · MARINA · MAINWAY · NUCLEON · PINWALE · FASCIA · BANYAN · LAMPSHADE · ASSOCIATION · HOMEBASE · SEDB · FRIAR · KEYCARD · TURMOIL · TURBULENCE · UTT · IRISHBEAUTY · OCTAVE · KOZYKOVE · LITHIUM · BLARNEY · LOPERS · MAILORDER · LUMBERYARD · MERLIN · NODDY · SAGUARO · NUTHATCH · CONTRAOCTAVE · XKEYSCORE · PLANK · RODEOSTAR · SAGURA · SERENADE · STARGATE · SILVERCOLLAM · SEALION · SEAGULL · SLIVER · SORA-2 · TITANPOINTE · TUBE · VPCS · STONEGATE“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “The Wiretap Rooms: The NSA’s Hidden Spy Hubs in Eight U.S. Cities” - The Intercept ↗ (2018-06-25) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
SSO Corporate Portfolio Overview [pdf]
A classified NSA training presentation providing analysts with a detailed overview of SSO's corporate collection portfolio — covering FAIRVIEW, STORMBREW, BLARNEY, MADCAPOCELOT, and OAKSTAR — including their legal authorities, collection capabilities, tasking procedures, and data repositories, with BLARNEY identified as contributing to over 60% of counterterrorism reporting and over 80% of all FAA reporting.
Programs: OCTAVE · UTT · CADENCE · BLARNEY · STORMBREW · FAIRVIEW · DARKTHUNDER · STEELFLAUTA · MONKEYROCKET · SHIFTINGSHADOW · ORANGECRUSH · YACHTSHOP · ORANGEBLOSSOM · SILVERZEPHYR · BLUEZEPHYR · COBALTFALCON · PINWALE · YANKEE · XKEYSCORE · MAINWAY · TOYGRIPPE · BLACKPEARL · TWISTEDPATH · NUCLEON · DISHFIRE · WHITESQUALL · MISTRALWIND · SERRATEDEDGE · PERFECTSTORM · MARINA · MADCAPOCELOT · FIST · MDCP · OAKSTAR · SSO · PRISM · TMM · COWBOY“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Greenwald, Glenn -
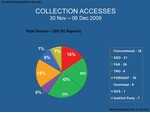
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO