Hackers are Humans too - Cyber leads to CI leads
Open PDFDocument date: 2011-01-01
Pages: 13
Genre: slides
Banner: TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Classification: TOP SECRET SI
Dissemination: REL TO CAN, AUS, GBR, NZL, USA
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
My notes
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Hackers are Humans too
Cyber leads to CI leads
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
1
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Introductions
- [REDACTED]
- Cyber-counter intelligence
- My primary focus is MAKERSMARK (Russia)
- CSEC – Covert Network Threat (CNT) group
- New name, same Cyber/CI group you know and love
- Cyber and traditional CI sitting side by side
- Focused on Foreign Intelligence, not Information Assurance
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
2
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Goals
- How do we attribute cyber intrusion sets?
- How do we go beyond the hacking face of a CNE program?
- Expose management structure, operators
- Requirements, technological advances
- This presentation portrays only one method
- Passive infrastructure tasking/contact chaining
- Many other are available
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
3
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Initial Seed
- Infrastructure tasking
- Mostly exposed through malware/content delivery
- Careful and manual monitoring of anomalous network sessions
- Nothing fancy
- Not Web 2.0, but it works
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
4
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Overview
- MAKERSMARK
- Misuse of Operational Infrastructure
- Poor OPSEC practices
[REDACTED]
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
5
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
MAKERSMARK (Russian CNE)
Designed by geniuses
Implemented by morons
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
6
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
MAKERSMARK
- The MAKERSMARK less attributed (LA) systems are really well designed
- This has not translated into security for MAKERSMARK operators
- Personal browsing through LA systems
- Workshops, ORBs, and controllers
- Development shop infected by crimeware
- 4th party collection
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
7
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
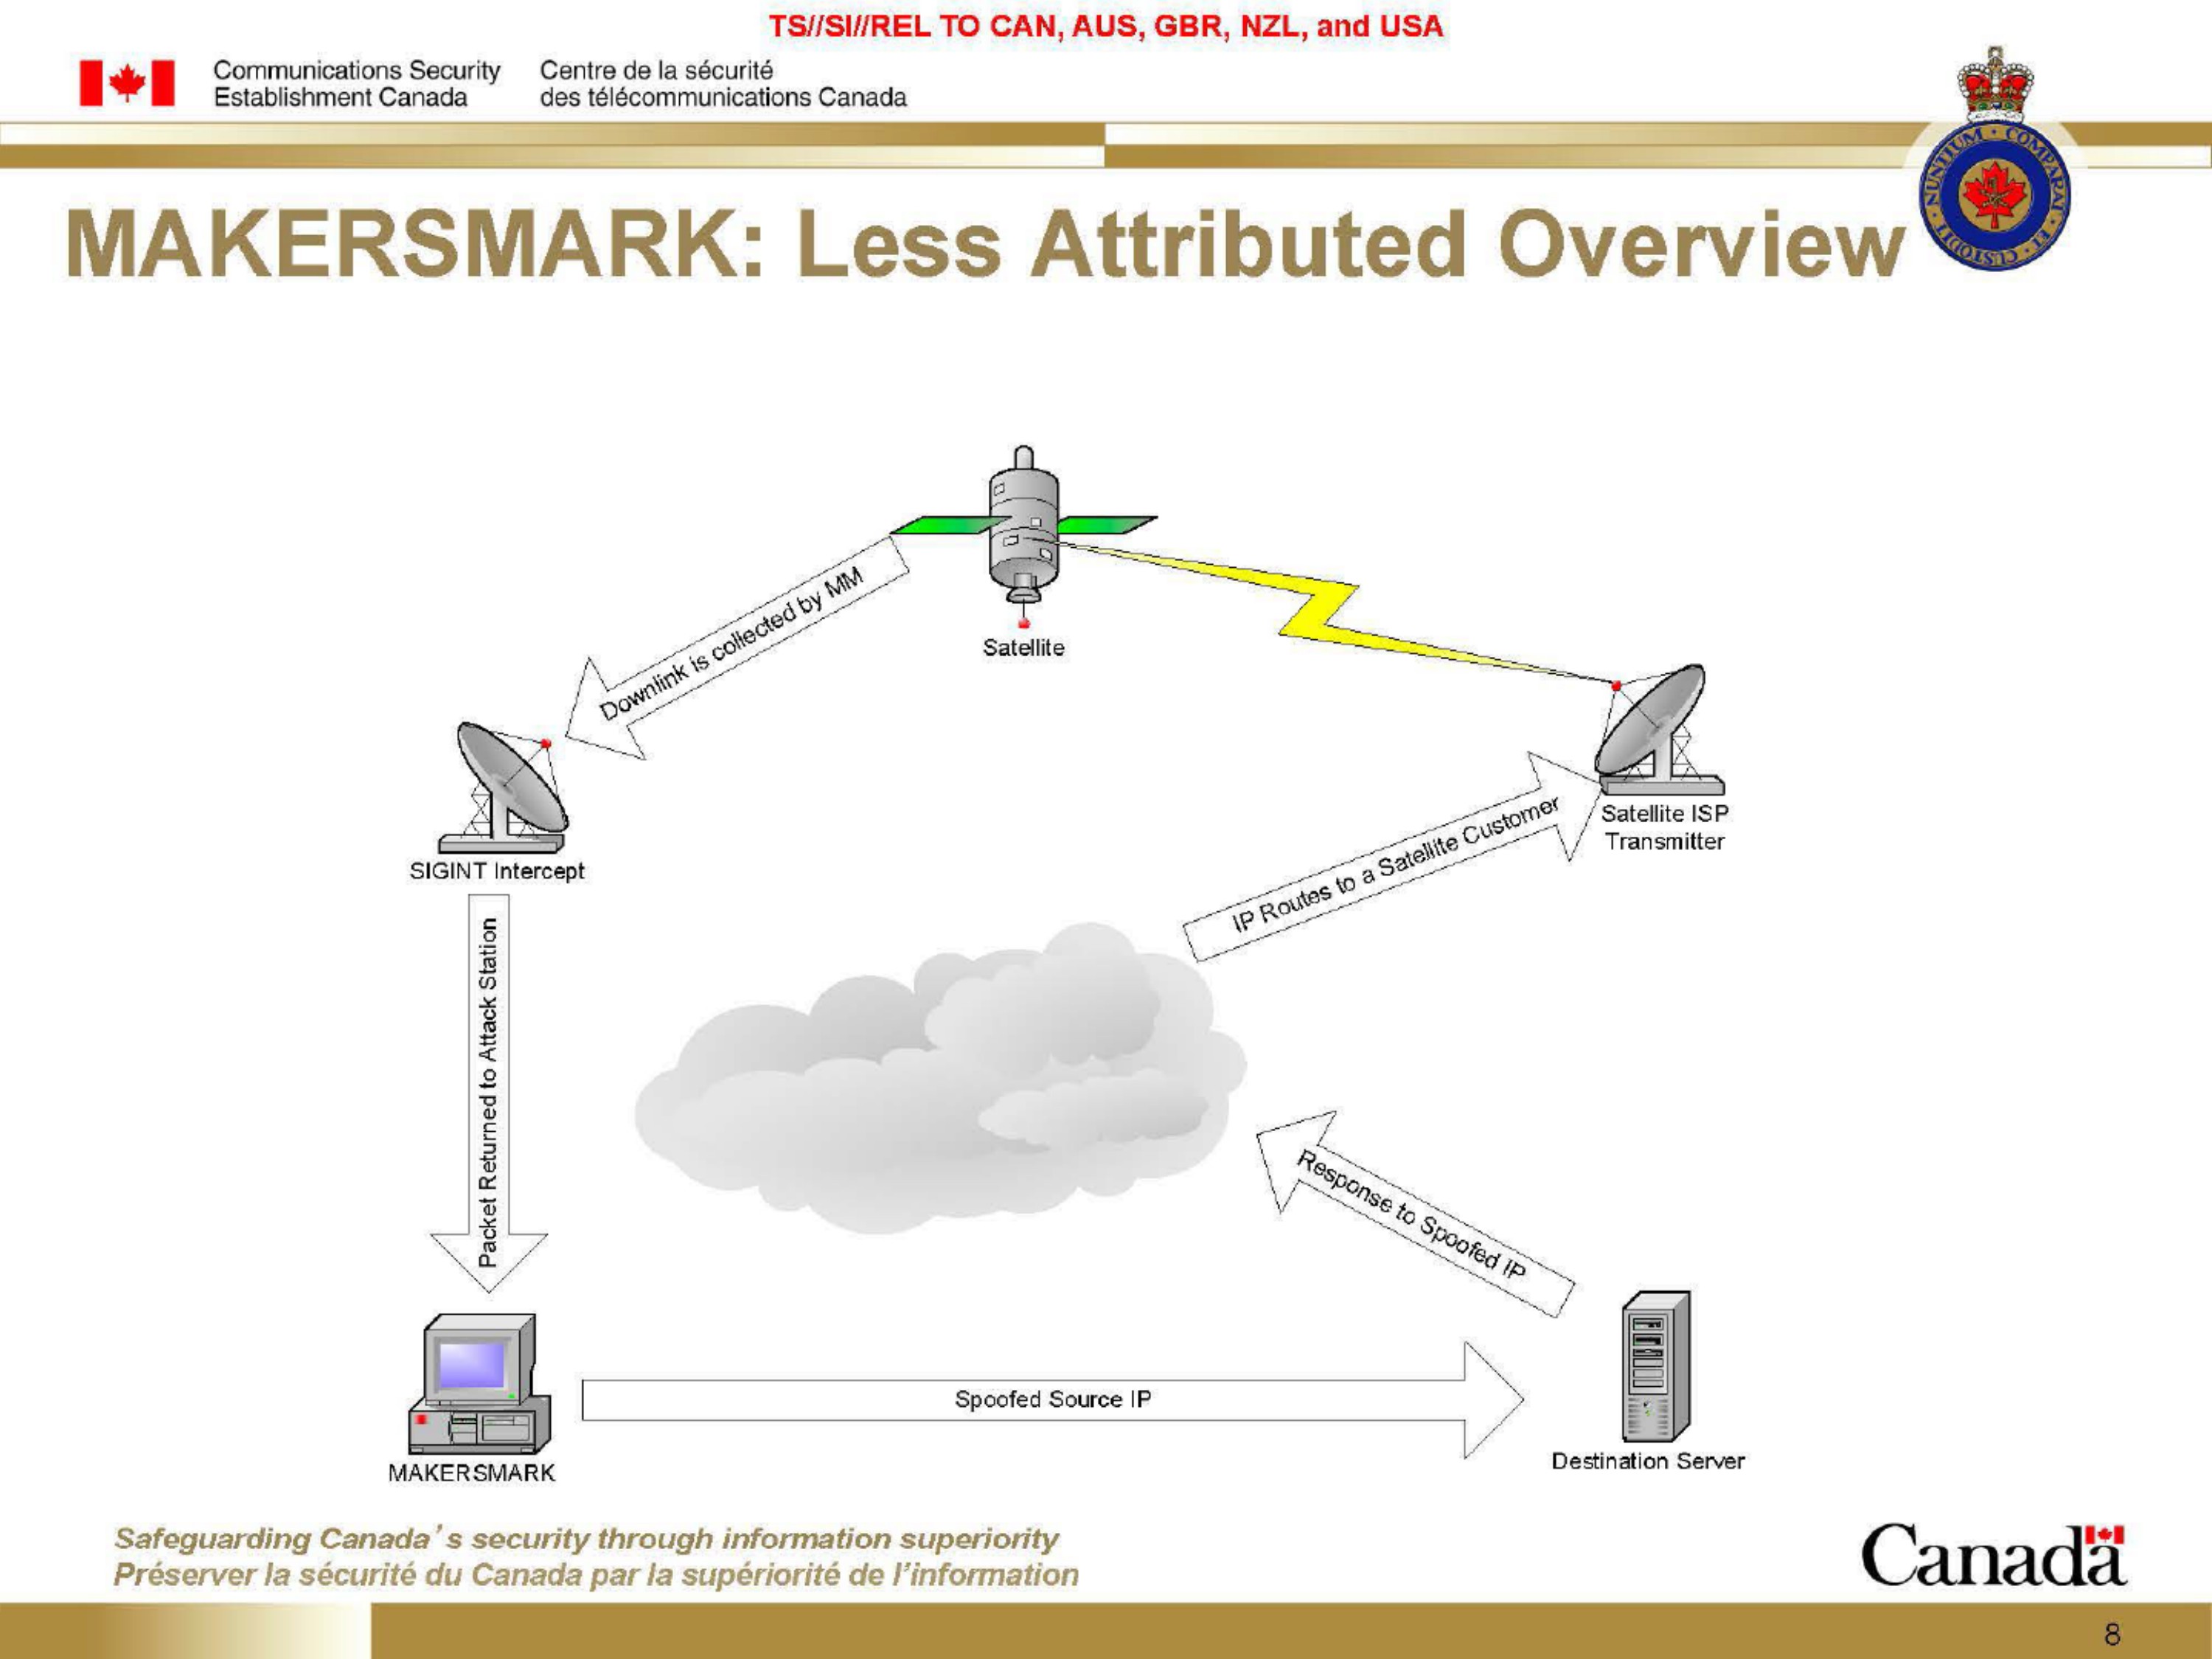
MAKERSMARK: Less Attributed Overview
Downlink is collected by MM
Satellite
SIGINT Intercept
Packet Returned to Attack Station
Spoofed Source IP
MAKERSMARK
IP Routes to a Satellite Customer
Satellite ISP Transmitter
Response to Spoofed IP
Destination Server
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
8
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
MAKERSMARK: Misuse of Infrastructure
- Less Attributable infrastructure used for highly attributable purposes:
- Hosting implant callback servers
- Live testing of new implant protocols
- Collecting exfiltration
- This is not CNE best practices
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
9
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
MAKERSMARK: Misuse of LA Systems
- Personal Social Networking
- Vkontakt
- (mail/inbox/bk).ru accounts
- Personal Email
- Webmail/POP
- Personal retrieval through masquerading infrastructure
- Personal web browsing
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
10
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
MAKERSMARK: 4th party collection
- Implant development shop infected by GUMBLAR botnet
- Crimeware
- Sends pharmaceutical spam
- Exfiltration to Canadian "bullet proof" host
- HTTP/FTP logins
- Collection of MM operator browsing habits
- MM LiveJournal accounts included in collection
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
11
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Closing Remarks
- You have to keep an eye out
- A lot of value can be lost by not following leads
- Typically the window to exploit information is short
- Knowing what to look for is half the battle
- These exploitation opportunities don't last forever
- As a CNE program matures, so will its OPSEC
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
24
TS//SI//REL TO CAN, AUS, GBR, NZL, and USA
Communications Security
Establishment Canada
Centre de la sécurité
des télécommunications Canada
Questions?
Safeguarding Canada's security through information superiority
Préserver la sécurité du Canada par la supériorité de l'information
Canada
25
Related Documents
-
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC Cyber Threat Detection [pdf]
This document details the Communications Security Establishment’s (CSEC) cyber threat detection and intelligence infrastructure, including systems like EONBLUE, CROSSBOW, CRUCIBLE, and LODESTONE, which enable passive monitoring, anomaly detection, and botnet identification through metadata and deep packet inspection. It outlines how CSEC integrates SIGINT, cryptanalysis, and network forensics to detect and mitigate cyber intrusions using both SIGINT and domestic sensors, while collaborating with Five Eyes partners to enhance Canada’s cyber defense and situational awareness. The presentation is duplicated from page 7 onwards - one of the duplicated slide has internal CSE comments.
Programs: EONBLUE · SPECIALSOURCE · WARRANTEDACCESS · COVENANT · SEEDSPHERE · DIESELRATTLE · SIENNABLUE · DOWNGRADE · CROSSBOW · CRUCIBLE · LODESTONE -
CASCADE - Joint Cyber Sensor Architecture [pdf]
This presentation outlines the Communications Security Establishment’s (CSE) plans to unify and expand its cyber sensor networks (ITS and SIGINT) to create a comprehensive, multi-layered national cyber defense system, enabling threat detection, intelligence collection, and defensive operations across Canadian and foreign networks. It emphasizes standardizing sensor deployments, integrating analytic capabilities, and preparing for “Effects” operations to mitigate cyber threats by 2015. The presentation is duplicated from page 33 onwards - three slides of the duplicated slides have internal CSE comments.
Programs: CASCADE · PHOTONICPRISM · EONBLUE · INDUCTION · THIRDEYE · CRUCIBLE · CHOKEPOINT · SUNWHEEL · CASSIOPEIA · SCNET · JAZZFLUTE · GAZEBO · SEEDSPHERE · TEXPRO · SSO -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan




