Program: SNORT 5 documents
Search documents matching “SNORT” →Codenames and programs recorded for each document.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Cyber Network Defence R&D Activities [pdf]
A September 2010 CSEC briefing to the Five Eyes 5IARC conference on cyber defence R&D, giving the full PONY EXPRESS email attachment scanning architecture and the PHOTONIC PRISM sensor, with speaker notes in which the presenter concedes CSEC does little research of its own.
Marking: SECRETPrograms: PHOTONICPRISM · PONYEXPRESS · SLIPSTREAM · POPQUIZ · 8BALL · SNORT · POPEYESEAR · FLOWPONY · SMTPPONY · MAILPONY · METAPONY · SCANPONY · AGGPONY · SYNCPONY · POOLTABLE · POOLCUE · CORNERPOCKET · TONTO · MULASSES · MULVAL · ASSETRANK · JNDMS · ARMOUR · SWAD · MINISSL · SSLFUZZER · N3C · N3 · CTEC · DCITS · 5IARC -
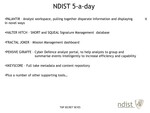
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe -
-
RWC Updater Readme [pdf]
A technical NSA manual describing the Royale with Cheese (RwC) Updater — the distribution system used to push XKEYSCORE dictionary updates, fingerprints, VoIP rules, IP geolocation tables and other configuration packages across the global hierarchical network of XKEYSCORE nodes on an hourly basis.
-
The Tale of Two Sources [pdf]
Programs: SUPERDRAKE · CROUCHINGSQUIRREL · HALTERHITCH · MVR · PPF · GORDIANKNOT · XKEYSCORE · SAMUELPEPYS · ALPINEBUTTERFLY · TRYST · FRACTALJOKER · TM · SPAY · BLACKHOLE · RAPIDTAPIR · HIDDENOTTER · SALTYOTTER · 8BALL · SORCERER · PACMAN · SNORT · WAFTER · CRIMSON · SHORTFALL · GCNET · BROADOAK · RAPTOR · GEOFUSION · MUGSHOT · HACIENDA · FOXTRAIL · FANNER · GLOBALSURGE · PENSIVEGIRAFFE · HRMAP · MUTANTBROTH · SAMPEPYS · INTEGERSPIN · MWX · MARBLEPOLLS · MOONRAKER · RT · DISTILLERY · SQUEAL · DEADSEA · GTE · WDM · TKB · TRAFFIC MASTER · CHOKEPOINT · CONTENT CLOUD · MAPREDUCE · EVENTS · CLOUD · AGILITY · PALANTIR