Journalist: Greenwald, Glenn 214 documents
Search documents matching “Greenwald, Glenn” →Journalists bylined on the stories that published these documents. Contributors credited without a byline are searchable but not listed here.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Introduction to XKS Application IDs and Fingerprints [pdf]
This August 2009 NSA training document introduces XKEYSCORE's Application IDs (AppIDs) and Fingerprints system, explaining how metadata tags are automatically applied to intercepted sessions to identify and categorize different types of Internet traffic, applications, and behaviors, evolving through four generations from simple keyword matching to sophisticated code-based metadata extraction.
-
Intrusion Analysis – GCHQ [pdf]
An internal GCHQ write-up defines the Intrusion Analysis team’s remit inside the Joint Electronic Attack Cell: all‑source analysis of emerging and active electronic attacks, stewardship of electronic attack signatures, and SIGINT‑driven targeting under EITT oversight. It details sources, reporting channels, legal authorities, and auditing controls that govern how signatures are deployed and how selectors are managed.
-
Iran – Current Topics, Interaction with GCHQ [pdf]
This NOFORN top secret April 2013 NSA document, shows how Iran significantly improved its offensive cyber capabilities by learning from cyberattacks against it, such as the April 2012 attack on its own oil industry, subsequently launching its own destructive attacks against Saudi Aramco and U.S. financial institutions.
-
Israel targets the U.S. government for invasive electronic surveillance [pdf]
Israel targets the U.S. government for invasive electronic surveillance, and does so more aggressively and threateningly than almost any other country in the world. Indeed, so concerted and aggressive are Israeli efforts against the U.S. that some key U.S. government documents — including the top secret 2013 intelligence budget — list Israel among the U.S.’s most threatening cyber-adversaries and as a “hostile” foreign intelligence service.
-
Israel targets US [pdf]
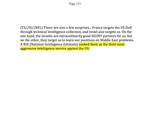
2 p.An NSA assessment noting that France targets the US Department of Defense and that Israel, while an extraordinarily good SIGINT partner, also targets the United States — ranked by a National Intelligence Estimate as the third most aggressive intelligence service against the US — and that the exchange has tilted heavily toward Israeli needs.
-
Israel-US 1999 Agreement [pdf]
This July 1999 top secret agreement between the U.S. Defense Intelligence Agency and Israel's Directorate of Military Intelligence establishes comprehensive intelligence-sharing arrangements covering Middle Eastern threats, terrorism, weapons of mass destruction, and foreign materiel exploitation, superseding previous agreements dating back to 1968 and including specific provisions for conferences, written requests, face-to-face analyst meetings, and security protocols.
-
-
JTRIG tools and techniques [pdf]
This document is an internal GCHQ wiki page from July 2012 detailing the capabilities of GCHQ’s Joint Threat Research Intelligence Group (JTRIG). It serves as an internal "Chinese menu" or catalog of digital tools and techniques used for engineering, intelligence collection, and "effects" (offensive operations).
Programs: JTRIG · CERBERUS · JTRIG RADIANTSPLENDOUR · ALLIUMARCH · ASTRALPROJECTION · TWILIGHTARROW · SPICEISLAND · POISONARROW · FRUITBOWL · NUTALLERGY · BERRYTWISTER · BERRYTWISTER+ · FORESTWARRIOR · JAZZFUSION · BRANDYSNAP · WINDFARM · BOMBAYROLL · COUNTRYFILE · TECHNOVIKING · JAZZFUSION+ · BUMBLEBEEDANCE · AIRBAG · EXPOW · AXLEGREASE · PODRACE · WATCHTOWER · REAPER · DIALd · DIRTYDEVIL · AIRWOLF · ANCESTRY · BEARTRAP · BIRDSONG · BIRDSTRIKE · BUGSY · DANCINGBEAR · DEVILSHANDSHAKE · DRAGON'SSNOUT · EXCALIBUR · FATYAK · FUSEWIRE · GLASSBACK · GODFATHER · GOODFELLA · HACIENDA · GEOFUSION · GLOBALSURGE · ICE · INSPECTOR · LANDINGPARTY · VIKINGPILLAGE · MINIATUREHERO · MOUTH · MUSTANG · PHOTONTORPEDO · RESERVOIR · SEBACIUM · SILVERSPECTER · SODAWATER · SPRINGBISHOP · DIRTYRAT · SYLVESTER · TANNER · TRACERFIRE · VIEWER · TOPHAT · ANGRYPIRATE · ARSONSAM · BUMPERCAR+ · BOMBBAY · BADGER · BURLESQUE · CANNONBALL · CLEANSWEEP · CLUMSYBEEKEEPER · CHINESEFIRECRACKER · BUMPERCAR · CONCRETEDONKEY · DEERSTALKER · GATEWAY · GAMBIT · GESTATOR · GLITTERBALL · IMPERIALBARGE · PITBULL · POISONEDDAGGER · PREDATORSFACE · ROLLINGTHUNDER · SCARLETEMPEROR · SCRAPHEAPCHALLENGE · SERPENTSTONGUE · SILENTMOVIE · SILVERBLADE · SILVERFOX · SILVERLORD · SKYSCRAPER · SLIPSTREAM · STEALTHMOOSE · SUNBLOCK · SWAMPDONKEY · TORNADOALLEY · UNDERPASS · VIPERSTONGUE · WARPATH · HOMEPORTAL · CYBERCOMMANDCONSOLE · NAMEJACKER · BABYLON · CRYOSTAT · ELATE · PRIMATE · JEDI · JILES · MIDDLEMAN · OUTWARD · TANGLEFOOT · SCREAMINGEAGLE · SLAMMER · EARTHLING · NEWPIN · BYSTANDER · CONDUIT · QUINCY · BEARSCRAPE · SFL · SNOOPY · MOBILEHOOVER · NEVIS · CHANGELING · HAVOK · MIRAGE · SHADOWCAT · SPACEROCKET · RANA · LUMP · GURKHASSWORD · CRINKLECUT · SHORTFALL · DEADPOOL · HUSK · LONGSHOT · MOLTEN-MAGMA · NIGHTCRAWLER · PISTRIX · WURLITZER -
JTRIG Wiki Highlights – August 2009 [pdf]
This August 2009 JTRIG report outlines the advanced planning phase of Operation QUITO, a pioneering "effects" operation led by GCHQ’s TSI unit. The mission was designed to support the UK Foreign and Commonwealth Office (FCO) in achieving strategic goals regarding Argentina and the Falkland Islands.
-
-
Legal issues UK regarding Sweden and Quantum [pdf]
An internal NSA document from April 2013 that describes the status of the relationship with a number of partners. It takes up a three-party agreement regarding the hacker programme Quantum, between the Swedish FRA, American NSA and British GCHQ, initiated by NSA chief Keith Alexander. The document shows that the project has so far resulted in a “proof of concept” – i.e., the system works, but it has not yet generated any substantial intelligence results. It also shows that the GCHQ are doubtful about continuing in the project because of restrictions in British legislation, but that the NSA’s intention all along has been to carry out the project with the Swedish FRA rather than GCHQ.
Programs: QUANTUM -
LEVITATION and the FFU Hypothesis [pdf]
This document describes LEVITATION, a top-secret Canadian Communications Security Establishment (CSE) project that monitors millions of daily file uploads and downloads from free file-sharing sites to identify potential extremist activity. It details the program’s data collection methods, analytical workflow, use of partner databases, and examples of successful discoveries related to terrorist materials and hostage videos.
-
LOVELY HORSE – GCHQ Wiki Overview [pdf]
This February 2012 GCWiki page describes LOVELY HORSE, a GCHQ initiative to collect, index, and distribute open-source intelligence from cybersecurity blogs and Twitter accounts to analysts on classified networks, utilizing JTRIG's BIRDSTRIKE architecture to scrape content from approximately 60 sources including security researchers, hacktivist groups like Anonymous and LulzSec, and cybersecurity companies, with legal approval from MP-LEG (Mission Policy-Legal).
Programs: LOVELYHORSE · HAPPYTRIGGER · BIRDSEED · JTRIG · BIRDSTRIKE · MERAPEAK · LEXHOUND · JEDI · DISCOVER -
Malware Analysis & Reverse Engineering – ACNO Skill Levels [pdf]
A GCHQ competency profile defines the “Malware Analysis & Reverse Engineering” skill (ACNO Skill 12), detailing required knowledge, hands-on abilities, and a graded proficiency ladder from novice to community-recognized expert. It codifies tradecraft spanning exploitation, static/dynamic analysis, anti-analysis countermeasures, and tooling (including IDA Pro), aligning outcomes from detection through mitigation advice.
Marking: SECRET -
Manhunting Timeline 2010 [pdf]
The Intellipedia manhunting timeline for 2010, recording the United States urging Australia, the United Kingdom and Germany on 10 August to consider criminal charges against WikiLeaks founder Julian Assange — described as focusing the legal element of national power on Assange and the network supporting WikiLeaks.
-
Memorandum Of Understanding between the NSA/CSS and the Israeli Sigint National Unit (ISNU) [pdf]
This document is a highly classified Memorandum of Understanding (MOU) between the NSA and the Israeli SIGINT National Unit (ISNU) regarding the sharing of raw, unminimized Signals Intelligence (SIGINT). The agreement establishes formal procedures to protect the privacy rights of U.S. persons contained within the data provided by the U.S. to Israel. While it mandates the "masking" of U.S. identities in Israeli reports, it notably allows Israel to receive and process massive streams of unevaluated data—including metadata and content—before the NSA has reviewed or filtered it.
Programs: CHIPPEWA -
Metadata-Driven Drone Strikes SIDtoday [pdf]
These documents describe the NSA and CIA’s use of geolocation technology, particularly via UAV-mounted systems like GILGAMESH and VICTORYDANCE, to track mobile devices for targeted drone strikes, including operations that killed U.S. citizen Anwar Nasser Aulaqi. These programs rely heavily on signals intelligence rather than human confirmation, raising concerns about reliability, civilian casualties, and the accuracy of targeting. See also: SIDtoday/documents/2005/2005-01-18_SIDToday_-_New_Tactical_Collection_System_Joins_the_War_on_Terroris
-
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
Microsoft releases new service, affects FAA 702 collection [pdf]
An SSO item on Microsoft's new outlook.com service encrypting web chat from 31 July 2012 and cutting off FAA 702 collection, and on the surveillance solution Microsoft built with the FBI, which went live on 12 December 2012 and needed no change to UTT tasking.
-
Minimization Procedures Used By The National Security Agency In Connection With Acquisitions Of Foreign Intelligence, Information Pursuant To Section 702 Of The Foreign Intelligence Court Surveillance Act Of 1978 [pdf]
The NSA’s Section 702 minimization rules expose how the agency can collect, keep, and use Americans’ communications without warrants, despite claiming to target only foreigners. While the document sets out procedures for handling U.S. data, it includes broad loopholes—like keeping “inadvertently” collected domestic messages for years, sharing unfiltered data with the FBI, CIA, and even foreign governments, and giving NSA analysts wide discretion over who gets surveilled—all under secret FISA Court approval.
People: Holder, Eric H. Jr.