Journalist: Greenwald, Glenn 214 documents
Search documents matching “Greenwald, Glenn” →Journalists bylined on the stories that published these documents. Contributors credited without a byline are searchable but not listed here.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
Elegant Chaos: collect it all, exploit it all [pdf]
This document outlines a classified project, "Elegant CHAOS," focused on advanced signals intelligence (SIGINT) collection, processing, and analysis using cutting-edge technologies like automated surveys and modems. It highlights goals such as real-time data analysis, collaboration with international partners, and integration with cloud-based platforms to manage massive data. See also the document with notes (by GCHQ): "Elegant-Chaos-collect-it-all-exploit-it-all-plus"
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · AMULETSTELLAR · CLOUD · WEALTHYCLUSTER · MVR · TINT · IPGEOTRAP · MARINA · PLUS -
Email Address vs User Activity [pdf]
This 2009 NSA training presentation explains how to use the XKEYSCORE system to search raw SIGINT, detailing the differences between the "Email Address" query, which finds email addresses in full content, and the more flexible "User Activity" query, which can search for selectors like cookies, usernames, and phone numbers.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Expanding Endpoint Operations SIDtoday [pdf]
Tailored Access Operations, NSA's elite hackers, are expanding their endpoint operations -- hacking directly into computers to steal information -- and are establishing the new endpoint operations remote operations center, scheduled to come online in the summer of 2005, that "is capable of managing and conducting endpoint operations on a scale that will dramatically expand collection." The physical office space of this new center will allow TAO to "grow from the current average of 20-25 of these operations per day to over 100 per day," and will allow TAO to increase the number of "active implants," or actively monitored pieces of malware, from 100-150 to thousands.
“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · The Intercept ↗ (2017-04-24) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Expanding PRISM Sharing With FBI and CIA [pdf]
An SSO item describing two projects that widened PRISM sharing with the FBI and CIA: PRINTAURA software that compiles the tasked-selector list every two weeks for both agencies, and weekly operational PRISM news and guidance from the mission programme manager.
-
Exploiting Facebook traffic in the passive environment to obtain specific information [pdf]
A GCHQ Global Telecommunications Exploitation presentation on extracting information about Facebook users from passively collected traffic: why online social networks are a rich source, how Facebook's use of the Akamai content delivery network exposes a user's ID inside image URLs, and how profile and album images are then obtained through SPRING BISHOP, GODFATHER and JTRIG.
-
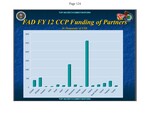
FAD FY 12 CCP Funding of Partners [pdf]
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
FAIRVIEW - Corp partner since 1985 [pdf]
1 p.A note describing FAIRVIEW as a corporate partnership dating to 1985 that gives access to international cables, routers and switches through a US company which is also “aggressively involved in shaping traffic to run signals of interest past our monitors”.
Programs: FAIRVIEW -
FASCIA: The NSA's huge trove of location records [pdf]
FASCIA is the National Security Agency's enormous database containing trillions of metadata records, many with device locations, that are collected from a variety of sources. This document shows the volume and types of device-location data collected by the agency.
“NSA tracking cellphone locations worldwide, Snowden documents show” - The Washington Post ↗ (2013-12-04) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gellman, Barton · Soltani, Ashkan · Greenwald, Glenn -
Ferguson NSA Visit Précis [pdf]
This internal NSA "Visit Précis" from March 2013 details a high-level courtesy call between Ambassador Roy Ferguson of New Zealand and the Director of the NSA. The meeting's primary objective was to discuss proposed legislative changes to New Zealand’s intelligence community, focusing on increased oversight in the wake of public controversies.
Programs: FIRSTLIGHTPeople: Ferguson, Roy · Cusick, James M. · Inglis, Chris · Fleisch, Fran · Kagan, Edgard · Wolfenson, Hugh · Dotcom, Kim · Alexander, Keith B. -
FINAL Agenda SWEDUSA [pdf]
Detailed list of points and participants in the summit meeting between the top brass of the FRA and the NSA in April 2013.
Programs: TURTLEPOWER · TURMOIL · XKEYSCORE · WINTERLIGHT · QUANTUM · PARTNERMALL · VIVIAN · NAPA-3 · GCE · SSO -
Finding and Querying Document Metadata [pdf]
This 2009 NSA training guide, created by Booz Allen Hamilton, explains how analysts can use the XKEYSCORE system to track targets by searching for "non-traditional selectors" embedded within documents, such as author names, company information, or even the hash values of company logos.
Programs: XKEYSCORE · TUNINGFORK · PINWALE · FOXACID · FOXBASE · CARBOY · CARDAMON · UNITEDRAKE · CADENCE -
Fisa court warrant authorising NSA surveillance procedures [pdf]
One-paragraph order, signed by a Fisa court judge, declares procedures submitted by the attorney general on behalf of the NSA are consistent with US law and fourth amendment
Marking: SECRET -
FISA dataflow [pdf]
This document describes the technical SIGINT architecture for FISA data processing, specifically detailing how the RAGTIME/SQF partition and PALMCARTE system utilize unique case notations and metadata tools to route and track intercepted communications.
-
FISA recap [pdf]
This document is a Top Secret NSA "FISA Recap" spreadsheet detailing electronic surveillance conducted between 2005 and 2008. It tracks specific email accounts targeted under the Foreign Intelligence Surveillance Act, listing the responsible agencies (NSA, FBI, and CIA), their legal "Case Notation," and the duration of collection. Notably, the log includes prominent U.S. Persons and organizations, such as the Council on American-Islamic Relations (CAIR), and features a 2005 formatting guide that uses a racial slur as a placeholder for a target's identity.
Programs: SQF -
Forwarding Selected MAILORDER Files Read Me [pdf]
An UNCLASSIFIED//FOR OFFICIAL USE ONLY XKEYSCORE administrator guide explaining how to configure an XKS cluster to forward selected intercepted sessions via MAILORDER, including category throttling limits, output directory configuration and the process setup required to switch all Digital Network Intelligence filtering and selection to the XKEYSCORE collection system.
-
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
Free File Uploaders [pdf]
This 2009 NSA training presentation for the XKEYSCORE system details how analysts can monitor Free File Uploader (FFU) websites like Zshare and RapidShare, which are difficult to track due to a lack of strong selectors. The guide introduces the "Web File Transfer" plug-in, a specialized tool designed to extract key metadata like original filenames and download/delete links from FFU web traffic.
-
Full Log vs HTTP [pdf]
This 2009 NSA training presentation explains the difference between using the "Full Log" and "HTTP Activity" queries in the XKEYSCORE surveillance system, showing analysts how to use both in tandem to gain a complete picture of a target's online activities, including identifying the use of anonymizing proxies.