Journalist: Greenwald, Glenn 214 documents
Search documents matching “Greenwald, Glenn” →Journalists bylined on the stories that published these documents. Contributors credited without a byline are searchable but not listed here.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
NSA Strategic Partnerships [pdf]
A slide on NSA's “alliances with over 80 major global corporations”, naming AT&T, Verizon, Qwest, Cisco, Microsoft, Oracle, Intel, IBM, HP, Motorola, Qualcomm and EDS across telecommunications, network infrastructure, hardware, operating systems, applications and security.
-
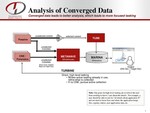
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
Offsensive Session: the Boundaries and Against Hacktivism [pdf]
GCHQ slides on “effects” operations against hacktivists: disruption in place of traditional law enforcement, denial-of-service attacks on key communications outlets during Op WEALTH in summer 2011, and a disruption playbook of infiltration, ruse, set-piece, false-flag, false-rescue, disruption and sting operations.
-
Operational Legalities – GCHQ Powerpoint Presentation [pdf]
GCHQ’s “Operational Legalities” deck is an internal compliance playbook that translates the UK’s surveillance laws into day‑to‑day SIGINT procedure—drilling staff on authorisation, necessity, and proportionality, and walking through warrants, targeting justifications, database queries, dissemination, and oversight. Half slides and half speaker notes, it shows how analysts are trained to document, audit, and defend operations under ISA, RIPA, HRA, and WTA while navigating edge cases like location, nationality, second‑party constraints, and “indirect targeting.”
-
ORANGECRUSH, part of the OAKSTAR program [pdf]
An SSO item reporting that ORANGECRUSH — the OAKSTAR access at a third-party partner site in Poland, known to the Poles only as BUFFALOGREEN — began forwarding metadata to NSA on 3 March and content on 25 March, with collection shared to Second Parties through TICKETWINDOW.
-
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
Peeling Back the Layers of TOR with EGOTISTICALGIRAFFE [pdf]
An NSA Tailored Access Operations presentation describing EGOTISTICALGIRAFFE and EGOTISTICALGOAT — Firefox browser exploits targeting Tor Browser Bundle users — covering fingerprinting Tor users via the TorButton BuildID, the EGOTISTICALGOAT type confusion vulnerability in Firefox's E4X implementation enabling remote code execution, and the FINKDIFFERENT/FUNNELOUT callback infrastructure used to exfiltrate data from exploited targets.
Programs: EGOTISTICALGIRAFFE · EGOTISTICALGOAT · ERRONEOUSINGENUITY · ERIN · EGGO · FINKDIFFERENT · FIDI · EGGI · FUNNELOUT -
Phone Number Extractor [pdf]
A top secret XKEYSCORE training document from October 2009 describing the Phone Number Extractor capability, which automatically identifies and extracts telephone numbers from intercepted internet traffic including website content, email signature blocks, HTTP GET requests from mobile devices, HTTP POST submissions, and converged DNR/DNI collection — with operational examples targeting Iran, Lebanon, and Pakistan.
-
Presidential Policy Directive/PPD-20 [pdf]
Eighteen-page presidential memo reveals how Barack Obama has ordered intelligence officials to draw up a list of potential overseas targets for US cyber attacks.
-
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
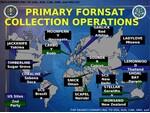
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
PRISM (US-984XN) expanded its impact [pdf]
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
PRISM/US-984XN Overview [pdf]
Blurry screengrabs from the "PRISM/US-984XN Overview" slide deck shown on the Fantástico O Globo broadcast. This document contains slides that are not incldued in the slides published by The Washington Post, The Guardian, Le Monde, and others.
-
Private Networks are Important [pdf]
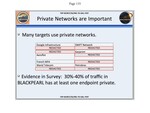
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
Procedures Used By The National Security Agency For Targeting Non-United States Persons Reasonably Believed To Be Located Outside The United States To Acquire Foreign Intelligence Court Information Pursuant To Section 702 Of The Foreign Intelligence Surveillance Act Of 1978 [pdf]
The NSA’s 2009 Section 702 targeting procedures lay out how analysts decide who can be surveilled without a warrant, supposedly limiting spying to foreigners abroad. In reality, the rules give the agency wide latitude to presume people are foreign, rely on vague “totality of the circumstances” tests, and allow broad technical methods like IP filters and metadata checks. Oversight is mostly internal and after-the-fact, creating significant potential for U.S. communications to be swept up with little accountability.
People: Holder, Eric H. Jr. -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
PROJECT BULLRUN Classification Guide [pdf]
This BULLRUN classification guide outlines the NSA’s highly secretive methods for undermining and exploiting encryption technologies through a combination of cryptanalysis, industry collaboration, covert implants, and network exploitation. It specifies strict classification protocols for capabilities against protocols like TLS/SSL, VPNs, VoIP, and webmail, emphasizing secrecy around sources, methods, and industry partnerships that make commercial encryption systems deliberately vulnerable.
Programs: BULLRUN · APERIODIC · AMBULANT · AUNTIE · PAINTEDEAGLE · PAWLEYS · PITCHFORD · PENDLETON · PICARESQUE · PIEDMONT“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · Ball, James · Borger, Julian · Greenwald, Glenn · Perlroth, Nicole · Larson, Jeff · Shane, Scott -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R. -
Quantum – from GCHQ documents dates October 2012 [pdf]
Portion of a document from the NSA’s British equivalent, the GCHQ, in which Sweden is not mentioned, but it describes an example of how Quantum has been used to attack computers in an African country where the users have visited extremist websites.