Microsoft releases new service, affects FAA 702 collection
Open PDFDocument date: 2012-12-26
Pages: 1
Genre: report
Classification: TOP SECRET SI
Dissemination: NOFORN
An SSO item on Microsoft's new outlook.com service encrypting web chat from 31 July 2012 and cutting off FAA 702 collection, and on the surveillance solution Microsoft built with the FBI, which went live on 12 December 2012 and needed no change to UTT tasking.
My notes
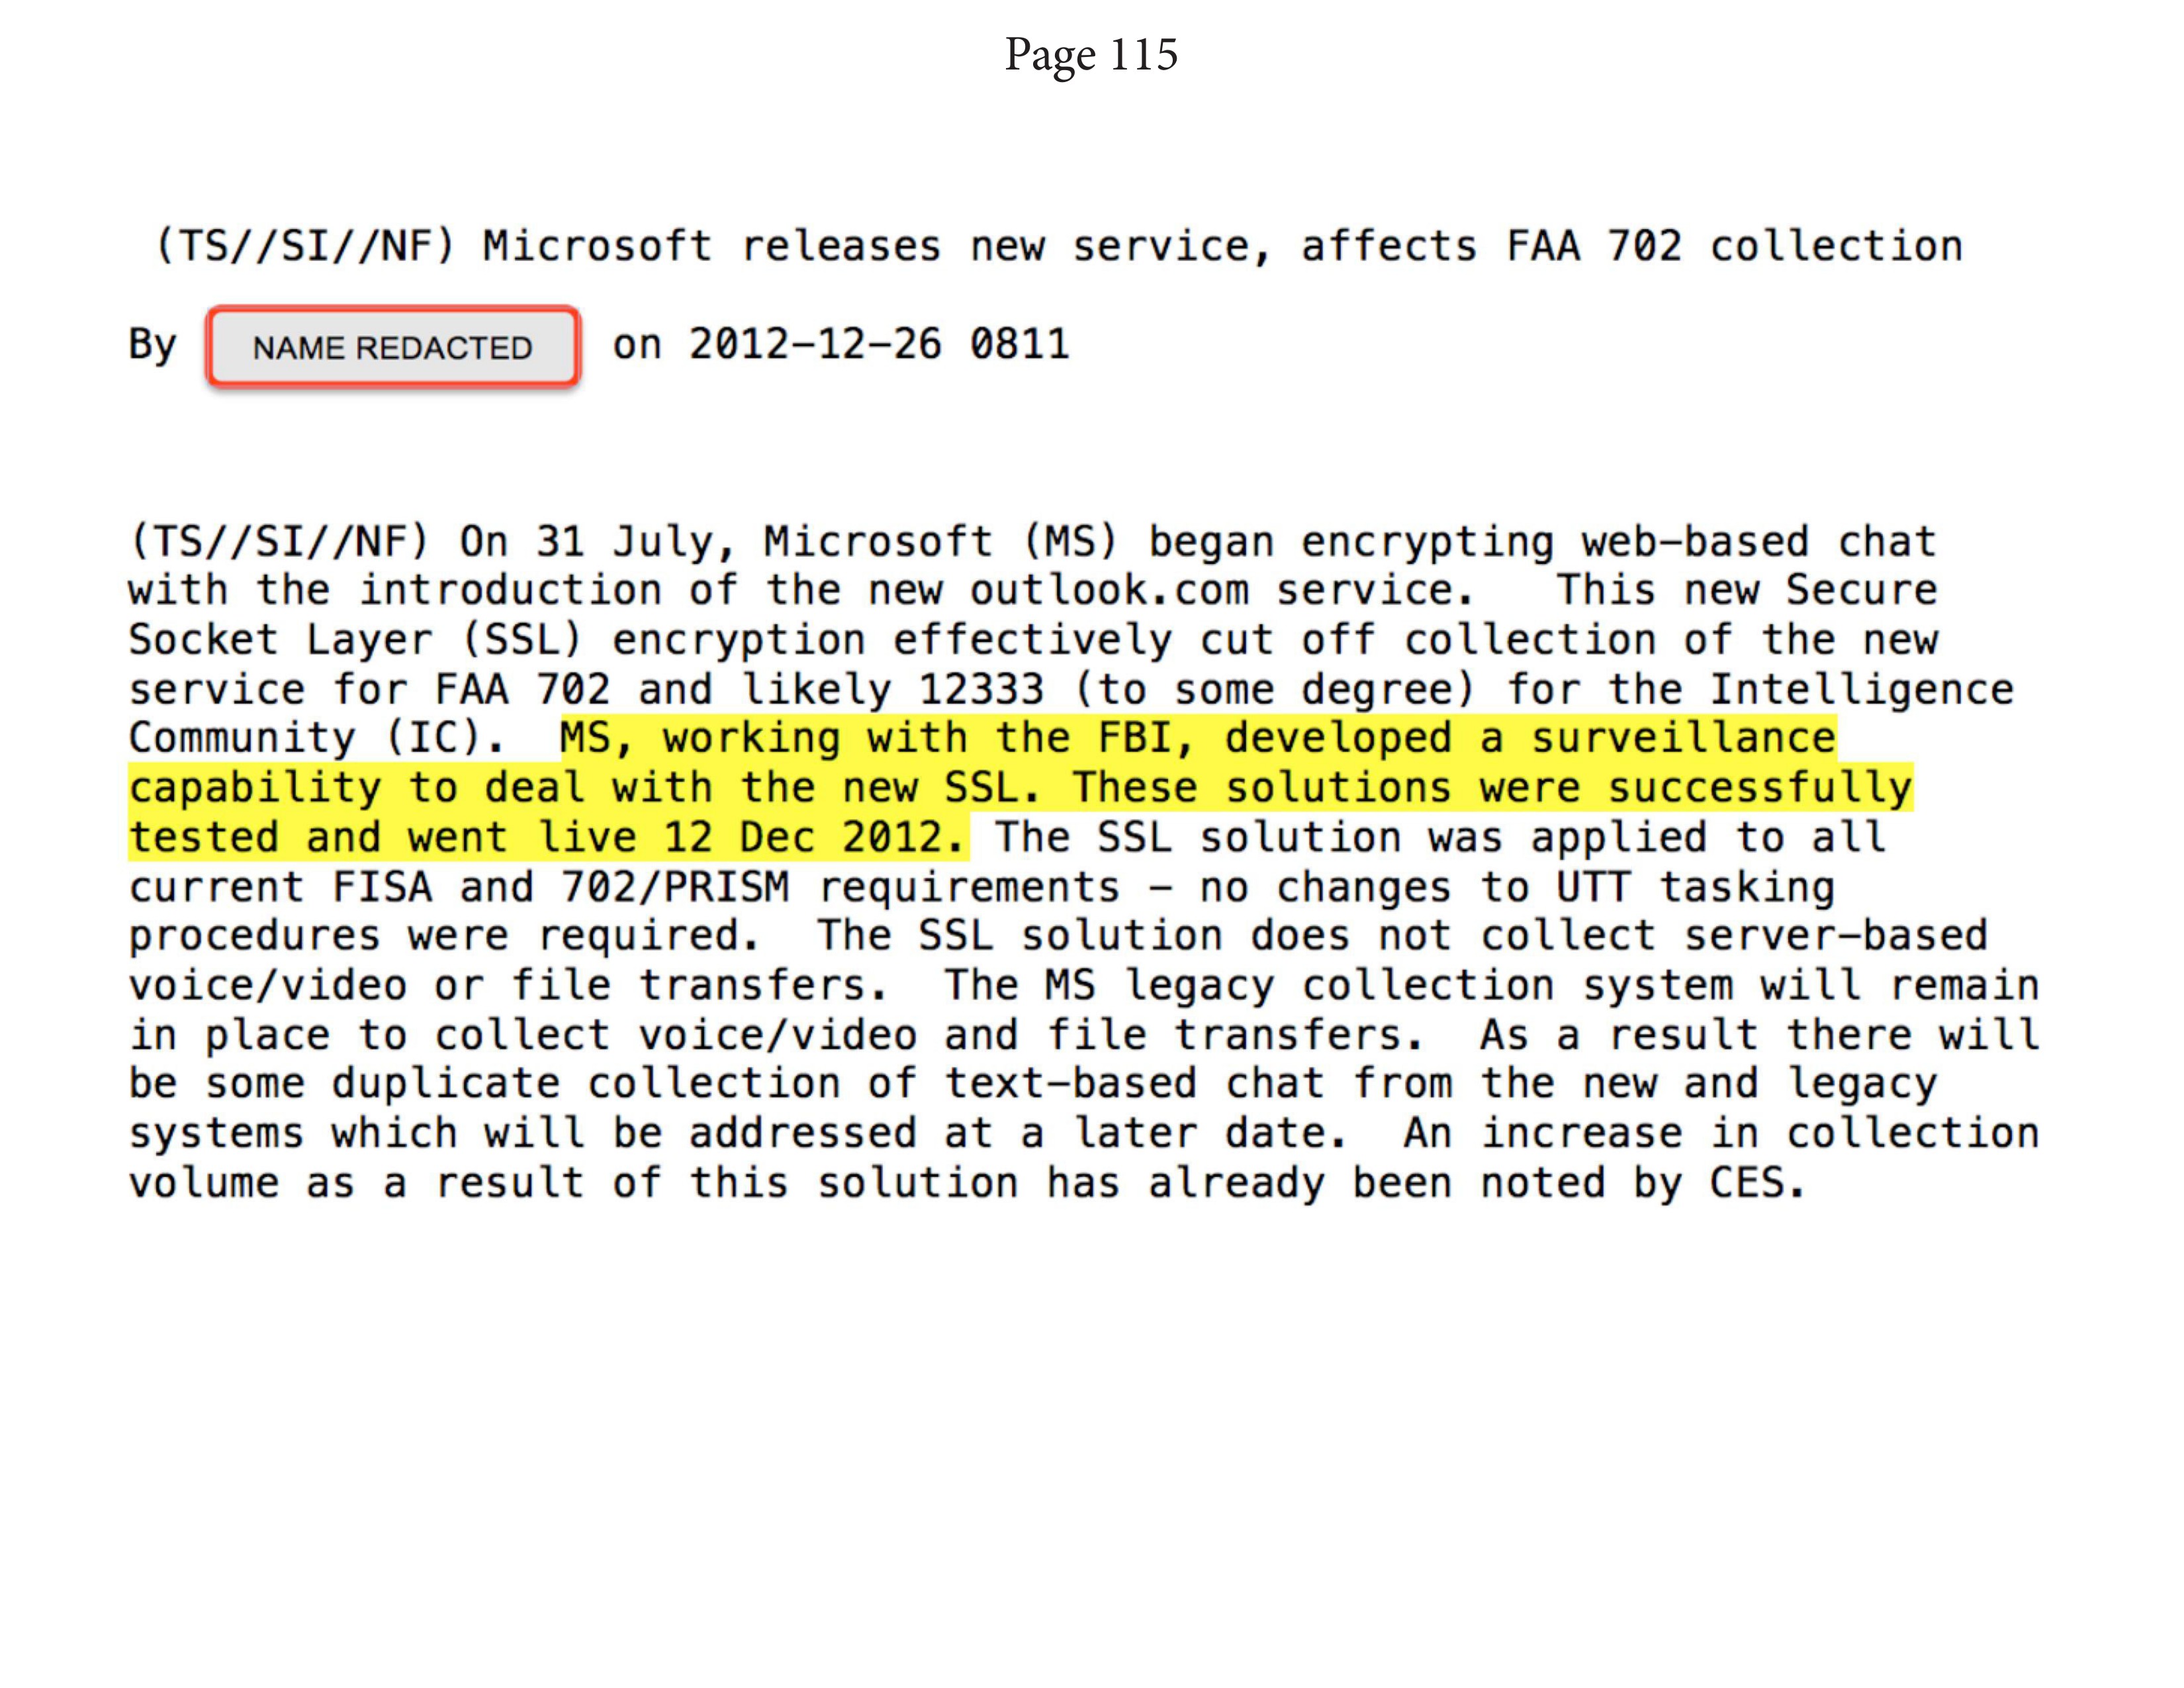
(TS//SI//NF) Microsoft releases new service, affects FAA 702 collection
By [REDACTED] on 2012-12-26 0811
(TS//SI//NF) On 31 July, Microsoft (MS) began encrypting web-based chat
with the introduction of the new outlook.com service. This new Secure
Socket Layer (SSL) encryption effectively cut off collection of the new
service for FAA 702 and likely 12333 (to some degree) for the Intelligence
Community (IC). MS, working with the FBI, developed a surveillance
capability to deal with the new SSL. These solutions were successfully
tested and went live 12 Dec 2012. The SSL solution was applied to all
current FISA and 702/PRISM requirements - no changes to UTT tasking
procedures were required. The SSL solution does not collect server-based
voice/video or file transfers. The MS legacy collection system will remain
in place to collect voice/video and file transfers. As a result there will
be some duplicate collection of text-based chat from the new and legacy
systems which will be addressed at a later date. An increase in collection
volume as a result of this solution has already been noted by CES.
Published in the Same Report
(10 of 62 documents)
-
NSA Intelligence Relationship with Canada's Communications Security Establishment Canada (CSEC) [pdf]
This document describes the close, long-standing SIGINT partnership between the NSA and Canada’s CSEC, emphasizing cooperative efforts in global intelligence collection, cyber operations, information assurance, and critical infrastructure defense. It highlights mutual contributions, including CSEC’s unique geographic access, covert sites, cryptographic capabilities, and R&D collaboration, supporting U.S. and North American security objectives.
“Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
Close Access SIGADS [pdf]
A 10 September 2010 NSA reference list of Close Access SIGADs revealing the codenames, locations and collection methods used to bug the embassies and UN missions of 38 targets — including US allies France, Italy, Greece, Japan, India, Mexico, South Korea and the EU — through implants, computer-screen capture, hard-drive imaging and electromagnetic emanation collection, most conducted against diplomatic facilities in Washington DC and New York.
Programs: KATEEL · POCOMOKE · MERCED · BANISTER · PERDIDO · MAGOTHY · BLACKFOOT · WABASH · NAVARRO · POWELL · KLONDIKE · NASHUA · OSAGE · OSWAYO · BRUNEAU · HEMLOCK · MULBERRY · ALAMITO · FLEMING · DOBIE · SULPHUR · REQUETTE · YUKON · WESTPORT · NAVAJO · PANTHER · LIFESAVER · HIGHLANDS · VAGRANT · MINERALIZ · DROPMIRE · PBX · MAGNETIC · OCEAN · GENIE · BLACKHEART · CRYPTOENABLED · CUSTOMS · DEWSWEEPER · RADON · MINERALIZE · COOP · STARRUBY · TRASHINT“No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Espionnage de la NSA : la diplomatie française était sur écoute aux Etats-Unis” - Le Monde ↗ (2013-10-22) · “Da qui ci spiano gli americani” - L'Espresso ↗ (2013-12-05) · Greenwald, Glenn · Follorou, Jacques · Maurizi, Stefania -
Cyber Integration [pdf]
The leaked 2012 GCHQ JTRIG presentation detail a wide range of offensive cyber and influence operations designed to “deny, disrupt, degrade, and deceive” targets, including hackers, foreign governments, companies, and individuals. Tactics include hacking, DDOS attacks, disinformation, honey traps, credential harvesting, and psychological operations, reflecting a shift from traditional surveillance to active disruption and manipulation campaigns.
“Exclusive: Snowden Docs Show British Spies Used Sex and 'Dirty Tricks'” - NBC News ↗ (2014-02-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Cole, Matthew · Esposito, Richard · Schone, Mark · Greenwald, Glenn -
XKEYSCORE intro [pdf]
A TOP SECRET NSA presentation from 2008 introducing XKeyscore — one of the earliest overview documents in the archive — describing the system as a globally distributed Linux cluster across approximately 150 sites and 700+ servers that stores a ~3-day rolling buffer of all unfiltered internet traffic, and demonstrating its core capabilities for finding previously unknown targets by mining metadata, tracking documents by embedded image hashes, detecting encryption and VPN use, and language tracking.
Programs: XKEYSCORE · TURMOIL · TURBULENCE · TRAFFICTHIEF · WEALTHYCLUSTER · MOONSHINE · SEARCHLIGHT · MARINA · PSC · SSO · TIMBERLINEPeople: bin Laden, Osama“'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · “XKeyscore: NSA tool collects 'nearly everything a user does on the internet'” - The Guardian ↗ (2013-07-31) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · Greenwald, Glenn · Bridi, Sônia · Marquis-Boire, Morgan · Lee, Micah -
Intelligently filtering your data: Brazil and Mexico case studies [pdf]
These documents reveal that the NSA conducted targeted surveillance operations against high-profile Brazilian and Mexican figures, including President Dilma Rousseff and presidential candidate Enrique Peña Nieto, using advanced contact-graph filtering and data analysis techniques to extract relevant intelligence from intercepted communications. These documents show how NSA analysts systematically developed intelligence on foreign leaders during election periods and diplomatic activities, framing it as “target development,” but in practice enabling deep political espionage under the guise of analytical innovation.
“Veja os documentos ultrassecretos que comprovam espionagem a Dilma” - O Globo ↗ (2013-09-02) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
Sharing Computer Network Operations Cryptologic Information with Foreign Partners [pdf]
The document is a secret NSA/CSS policy outlining guidelines for sharing Computer Network Operations (CNO) cryptologic information with foreign partners, including rules for cooperation in CNE and CND within existing intelligence relationships. The “Purpose and Scope” section on the first page appears to be unpublished elsewhere, while the Tier A and Tier B country lists match those publicly revealed in sources like Glenn Greenwald’s No Place to Hide.
“El CNI facilitó el espionaje masivo de EEUU a España” - El Mundo ↗ (2013-10-30) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn · Aranda, Germán -
NSA Spied On Porn Habits As Part Of Plan To Discredit 'Radicalizers' [pdf]
Top-secret document reveals how NSA has been gathering records of online sexual activity and evidence of visits to pornographic websites as part of a proposed plan to harm the reputations of those whom the agency believes are radicalizing others through incendiary speeches
-
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
Elegant Chaos: collect it all, exploit it all [pdf]
This document outlines a classified project, "Elegant CHAOS," focused on advanced signals intelligence (SIGINT) collection, processing, and analysis using cutting-edge technologies like automated surveys and modems. It highlights goals such as real-time data analysis, collaboration with international partners, and integration with cloud-based platforms to manage massive data. See also the document with notes (by GCHQ): "Elegant-Chaos-collect-it-all-exploit-it-all-plus"
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · AMULETSTELLAR · CLOUD · WEALTHYCLUSTER · MVR · TINT · IPGEOTRAP · MARINA · PLUS -
FASCIA: The NSA's huge trove of location records [pdf]
FASCIA is the National Security Agency's enormous database containing trillions of metadata records, many with device locations, that are collected from a variety of sources. This document shows the volume and types of device-location data collected by the agency.
“NSA tracking cellphone locations worldwide, Snowden documents show” - The Washington Post ↗ (2013-12-04) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gellman, Barton · Soltani, Ashkan · Greenwald, Glenn


Related Documents
-
SSO HIGHLIGHT - Microsoft Skydrive Collection Now Part of PRISM [pdf]
An SSO highlight announcing that from 7 March 2013 Microsoft SkyDrive data is collected as part of PRISM's standard stored-communications package for tasked FAA 702 selectors, the result of months of FBI work with Microsoft.
-
SSO Expands PRISM Skype Targeting Capability [pdf]
An SSO item reporting that from 15 March 2013 all Microsoft PRISM selectors, about 9,800 of them, are also tasked to Skype through PRINTAURA, so that users who log in with an address other than their Skype username are no longer missed.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
SSO Corporate Portfolio Overview [pdf]
A classified NSA training presentation providing analysts with a detailed overview of SSO's corporate collection portfolio — covering FAIRVIEW, STORMBREW, BLARNEY, MADCAPOCELOT, and OAKSTAR — including their legal authorities, collection capabilities, tasking procedures, and data repositories, with BLARNEY identified as contributing to over 60% of counterterrorism reporting and over 80% of all FAA reporting.
Programs: OCTAVE · UTT · CADENCE · BLARNEY · STORMBREW · FAIRVIEW · DARKTHUNDER · STEELFLAUTA · MONKEYROCKET · SHIFTINGSHADOW · ORANGECRUSH · YACHTSHOP · ORANGEBLOSSOM · SILVERZEPHYR · BLUEZEPHYR · COBALTFALCON · PINWALE · YANKEE · XKEYSCORE · MAINWAY · TOYGRIPPE · BLACKPEARL · TWISTEDPATH · NUCLEON · DISHFIRE · WHITESQUALL · MISTRALWIND · SERRATEDEDGE · PERFECTSTORM · MARINA · MADCAPOCELOT · FIST · MDCP · OAKSTAR · SSO · PRISM · TMM · COWBOY“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Greenwald, Glenn -
Special Source Operations corporate overview [pdf]
A classified NSA training presentation providing an in-depth operational overview of the FAIRVIEW program — the agency's largest corporate partner surveillance program — detailing its collection capabilities, legal authorities, TAO shaping operations, targeting tools, and productivity statistics, while revealing that BLARNEY/PRISM was the single most productive SSO program in 2012 with 806 serialized product reports.
Programs: FAIRVIEW · BLARNEY · PRISM · RAMPART-A · RAMPART-I · RAMPART-X · RAMPART-T · RAMPART-M · DGO · WINDSTOP · MYSTIC · PINWALE · XKEYSCORE · TURMOIL · STORMBREW · OAKSTAR · OCTAVE · UTT · CADENCE · COWBOY · YANKEE · MAINWAY · TOYGRIPPE · BLACKPEARL · TWISTEDPATH · NUCLEON · DISHFIRE · SPYDER · CARBONFURY · NATIVEFLORA · UNICORNSANDWICH · CROSSEYEDBEAR · SCORCHERSIX · TROPICTHUNDER · DARKTHUNDER · STEELFLAUTA · RAGTIME · SWEETSMACK2 · SOURSMACK2 · EVILOLIVE · SCALEABLE · FLEXIBLE · MONKEYROCKET · SHIFTINGSHADOW · ORANGECRUSH · YACHTSHOP · ORANGEBLOSSOM · SILVERZEPHYR · BLUEZEPHYR · COBALTFALCON · RAGTIME-A · RAGTIME-C · SSO · SURREY“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “The Wiretap Rooms: The NSA’s Hidden Spy Hubs in Eight U.S. Cities” - The Intercept ↗ (2018-06-25) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan