Tag: Computer Network Exploitation 143 documents
Search documents matching “Computer Network Exploitation” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Stargate CNE requirements [pdf]
This document is an internal GCHQ wiki page for collecting software requirements for a Computer Network Exploitation (CNE) tool called STARGATE, outlining features operators need for viewing files, searching systems, and visualizing operational data.
Programs: STARGATE · MAD · KITCHENSINK · MARVALICE · IRONINGBOARD · TINREVERIE · SORCERER · FEDEX · VORPALSWORD · CLOTHO2 · ROYALMANTLE · ERIDANUS · CHEYENNEMOUNTAIN · CHEYENNEMOUNTAIN2 · UDAQ · OUTSIDEIN · QUICKVIEW · AQUILA · BIGBUS · DAREDEVIL · THICKISHALPHA · LEGSPIN“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Tailored Access Operations [pdf]
A classified NSA Texas Cryptologic Center presentation introducing the TAO unit's staffing, operations, facilities, and growth plans — including detailed statistics on hacking operations, a breakdown of Operation WHITETAMALE targeting Mexico's Public Security Secretariat, and a personnel expansion plan projecting growth from 57 to 270 employees by FY2015.
Programs: WHITETAMALE · FREEZEPOST · DOCKETDICTATE · BACONRIDGE · OLYMPUS · SHARPFOCUS · PARCHDUSK · FOXACID -
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.
-
Tailored Access Operations, FOXACID, QUANTUM [pdf]
These NSA presentation slides detail "QUANTUM," a sophisticated system that allows the agency to intercept internet traffic and inject malware onto target computers with up to 80% success rates, far exceeding traditional spam-based methods. The system works by monitoring internet traffic for specific identifiers (like Yahoo or Facebook cookies), then racing to inject malicious code before legitimate web servers can respond, thereby compromising targets' computers without their knowledge and establishing persistent backdoor access.
Programs: FOXACID · QUANTUM · QUANTUMTHEORY · QUANTUMBISCUIT · VALIDATOR · OLYMPUS · UNITEDRAKE · OLYMPUSFIRE · SSO · FORESTPLACE -
TECA Product Centre — Wiki [pdf]
The TECA Product Centre is a GCHQ unit, within the Technical Enabling Covert Access group (TEA), whose mission is to develop and exploit specialist technologies and physical access methods to gain intelligence or SIGINT access where conventional methods fail. It works closely with SIS (MI6) on technical operations and deployment, offering bespoke managed services rather than direct products.
-
The ROC: NSA's Epicenter for Computer Network Operations SIDtoday [pdf]
The Remote Operations Center (ROC) conducts computer network operations against U.S. adversaries and foreign governments. Its motto is: "Your data is our data, your equipment is our equipment, anytime, any place, by any legal means."
The Intercept ↗ (2019-05-29) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
The Wizards of OZ II: Looking Over the Shoulder of a Chinese C2C Operation SIDtoday [pdf]
A survey team discovers that Chinese hackers have compromised computers at the Indian Embassy in Beijing, exfiltrating "sensitive Indian diplomatic files" to public drop boxes on the internet. Seizing on this unique opportunity to look their colleagues over the shoulders, the team sets up "sustained collection" before returning home.
Programs: MUSKETEERThe Intercept ↗ (2019-05-29) -
'Top 5' SIDtoday Articles of November SIDtoday [pdf]
The most read SIDtoday article in November was a first-person account of the attack on the US Embassy in Damascus, Syria in September 2006.
People: Shea, Teresa H.The Intercept ↗ (2019-05-29) -
Tor Stinks [pdf]
A June 2012 joint NSA-GCHQ presentation titled "Tor Stinks" detailing the two agencies' attempts to de-anonymize Tor users through analytics, exploitation, and network disruption — candidly admitting they will never be able to identify all Tor users, but outlining a range of techniques including cookie leakage tracking, QUANTUM attacks, circuit reconstruction, timing analysis, and deliberate network degradation.
Programs: REMATION · EPICFAIL · QUANTUM · NEWTONSCRADLE · QUICKANT · GREATEXPECTATIONS · RONIN · ONIONBREATH · QUANTUMCOOKIE · SHORTSHEET · FOXACID -
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR -
TURBINE description [pdf]
These document excerpts introduces TURBINE, a revolutionary "Expert System" designed to solve the problem of scale in global hacking operations. Managed by the Tailored Access Operations (TAO) division, TURBINE marks the transition from manual, human-driven exploitation to automated, industrial-scale "Active SIGINT." While traditional "Passive SIGINT" involves eavesdropping on existing signals, Active SIGINT involves "intervention"—actively compromising target devices to extract data from within. TURBINE’s mission is to expand the NSA’s reach from a few thousand manual infections to a global network of millions of covert implants.
-
User-agents: Why and How and How to [pdf]
A TOP SECRET NSA training presentation from 2010 teaching analysts how to use browser user-agent strings — the identifying information your web browser automatically sends to every website you visit — to track surveillance targets across the internet, link their known email activity to their anonymous web browsing, and identify opportunities for hacking their computers based on their operating system and software versions.
-
Using XKEYSCORE to Enable TAO [pdf]
A TOP SECRET training presentation from 2009, authored by a Booz Allen Hamilton contractor, teaching NSA analysts how to use XKeyscore to harvest the login credentials, router configurations, browser versions and server software details that the Tailored Access Operations hacking unit needs to break into foreign computer networks — with worked examples stealing Cisco router passwords, Iranian government webmail logins and jihadi web forum credentials directly from intercepted internet traffic.
-
Welcome to SID's Data Acquisition Directorate SIDtoday [pdf]
Introduction to the Data Acquisition Directorate and summary of articles in the Data Acquisition series.
People: Cusick, JimThe Intercept ↗ (2016-08-10) -
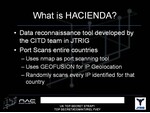
What is HACIENDA? [pdf]
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).
-
What is the path an email takes when it is sent on the internet? [pdf]
This undated NSA training document, created by Booz Allen Hamilton contractor personnel, provides technical diagrams explaining email transmission paths and network administrator traffic flows for NSA/Five Eyes collection purposes, specifically highlighting how to identify and exploit login credentials, passwords, configuration files, and communications transiting through U.S.-based webmail servers like Hotmail and Yahoo.
The Intercept (2015-06-29) -
What’s the worst that could happen? [pdf]
This GCHQ document from March 2010 presents a checklist of factors analysts should consider before going ahead with an operation to infiltrate a communications network, by physical or other means.
-
Who's Who in HR for SID SIDtoday [pdf]
List of SID HR personnel and their roles following a reorganization.
The Intercept ↗ (2016-05-16) -
XKEYSCORE for Counter-CNE [pdf]
A TOP SECRET presentation from March 2011 describing how NSA uses XKeyscore for counter-CNE — detecting and exploiting foreign hacking operations — including ingesting NSA's own TAO implant data, hunting for foreign intrusion sets like DISGRUNTLEDDUCK, and a success story in which Menwith Hill used TAO-stolen Iranian implant encryption keys to decrypt and read keylogger data the Iranian Revolutionary Guard's hackers were stealing from their own victims.
Programs: XKEYSCORE · DISGRUNTLEDDUCK · GENESIS · DANDERSPRITZ · SIMBAR · DONUT · AMULETSTELLAR · TRANGRESSION · TRANSGRESSION -
XKEYSCORE Search Forms [pdf]
A secret XKeyscore reference guide from March 2009 cataloguing all of the system's search forms — one entry per metadata plug-in — revealing the full breadth of what XKeyscore extracts and indexes from intercepted internet traffic, from emails, logins, passwords, phone numbers and documents to Cisco router passwords, TOR routers, VoIP calls, WLAN data, Blackberry PINs, satellite terminals, passport images, internet café addresses, and exfiltrated data from TAO hacking operations.
Programs: XKEYSCORE · TRAFFICTHIEF · DECODEORDAIN · CADENCE · JUGGERNAUT · FASCIA · CERF · DURT · MOONSHINE · SPOTBEAM · RADIUS“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “FRA has access to controversial surveillance system” - SVT Nyheter ↗ (2013-12-11) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah · Bergman, Sven · Dyfvermark, Joachim · Gallagher, Ryan · Laurin, Fredrik · Struwe, Filip