Tag: Computer Network Exploitation 143 documents
Search documents matching “Computer Network Exploitation” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Pull Steering Group Minutes [pdf]
A top secret STRAP1 GCHQ PullThrough Steering Group meeting record from February 2008 documenting the approval process for five surveillance and intelligence prototypes including KARMA POLICE — the mass internet browsing profiling system — alongside ORB FINDER for CNE operational relay box identification, SALTY OTTER for cross-media timing analysis, MOOSE MILK for telephone kiosk surveillance, and LIGHTWOOD for email address extraction used by JTRIG.
Programs: MYOFIBRIL · SALTYOTTER · PRIMETIME · KARMAPOLICE · ORBFINDER · MOOSEMILK · LIGHTWOOD · JTRIG · MERAPEAK · MONTEVISTA · KED -
QFD BLACKHOLE Technology Behind INOC [pdf]
A UK SECRET STRAP2 COMINT ORCON GCHQ Applied Research presentation from March 2009 documenting the BLACK HOLE bulk data repository's scale and structure, and the suite of analytical tools — MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS and MARBLED GECKO — built on top of it to answer specific intelligence questions about online presence, browsing activity, forum usage and geolocation searches.
Programs: BLACKHOLE · MESME · NETEZZA · CLOUDS · MUTANTBROTH · KARMAPOLICE · INFINITEMONKEYS · MARBLEDGECKO · GOOB · AUTOASSOC · PSOUP · SOCIALANIMAL · SAMUELPEPYS · MEMORYHOLE · HRMAP · PSOUPALERT · LAUGHINGHYENA -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R. -
Quantum – from GCHQ documents dates October 2012 [pdf]
Portion of a document from the NSA’s British equivalent, the GCHQ, in which Sweden is not mentioned, but it describes an example of how Quantum has been used to attack computers in an African country where the users have visited extremist websites.
-
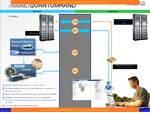
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
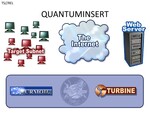
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
QUANTUMTHEORY CT Successes [pdf]
This document details a successful NSA counterterrorism cyber operation in which analysts used QUANTUM techniques to deploy the UNITEDRAKE implant—equipped with keylogging and USB collection tools—against Al-Qaeda coordinator Muhsin al-Fadhli in Iran, even after detecting Kaspersky antivirus software on the target system. The operation yielded significant intelligence on Al-Qaeda communications, document forgery activities, and associated operatives.
Programs: QUANTUMTHEORY · ANCIENTBREW · VALIDATOR · QUANTUM · QUANTUMCOWBOY · UNITEDRAKE · GROK · SALVAGERABBITPeople: al-Fadhli, Muhsin -
Report on Architectural Risk 2012 - Summary [pdf]
This 2012 GCHQ report identifies that a historical under-investment in IT architecture has created significant risk, especially with new challenges like massive data growth, cyber defense, and increased partnering. The document recommends immediate, prioritized investment in big data strategies, integrated analytics frameworks, and security services to address the strain on the system.
Programs: BLACKHOLE -
Roger Dingledine at NSA NOV 2007 [pdf]
An NSA internal wiki page summarising a talk given at NSA on 1 November 2007 by Roger Dingledine, one of Tor's inventors, covering who Tor's users are, anonymity system design concepts, and Tor's weaknesses.
People: Dingledine, Roger -
ROYAL CONCIERGE [pdf]
This document describes GCHQ’s top‑secret “ROYAL CONCIERGE program, an automated SIGINT system that mines hotel reservation emails and links to them from government (gov.xx) addresses to produce daily tip‑offs about diplomats’ travel and hotel stays. Those alerts enable a range of follow‑on options — from technical attacks (network/hotel room exploitation and XKeyScore fingerprinting) to HUMINT, and even attempts to influence or cancel visits.
-
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX -
Shaping Diagram [pdf]
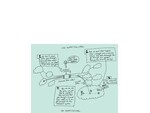
This hand-drawn diagram detail an NSA methodology for intercepting and redirecting internet traffic. The approach involves manipulating data flows through a controlled fiber cable, leveraging Computer Network Exploitation (CNE) to capture and replicate target communications for SIGINT processing, all framed in a tongue-in-cheek, yet highly classified, presentation style.
-
Sharing Computer Network Operations Cryptologic Information with Foreign Partners [pdf]
The document is a secret NSA/CSS policy outlining guidelines for sharing Computer Network Operations (CNO) cryptologic information with foreign partners, including rules for cooperation in CNE and CND within existing intelligence relationships. The “Purpose and Scope” section on the first page appears to be unpublished elsewhere, while the Tier A and Tier B country lists match those publicly revealed in sources like Glenn Greenwald’s No Place to Hide.
“El CNI facilitó el espionaje masivo de EEUU a España” - El Mundo ↗ (2013-10-30) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn · Aranda, Germán -
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO -
Slides Describe Mission Involving Huawei [pdf]
This document details an NSA-led strategic initiative to target Huawei due to its dominance in global telecommunications infrastructure. The operation (codenamed "Shotgiant") aims to exploit Huawei hardware to maintain access to target communications while investigating the company’s potential role in facilitating People’s Republic of China (PRC) signals intelligence and supply chain subversion.
-
SNIPs of SIGINT [pdf]
A monthly notes entry from June 2012 by an NSA analyst on exchange at DSD Australia, describing two CNA/CNE tool development projects — PITIEDFOOL, a Windows file system destruction suite that kills the MFT and volume shadow copies and was successfully tested inside FUZZYEBOLA, and PANT SPARTY, an OpenSSH daemon backdoor granting covert root access while suppressing log entries — alongside a briefing to the US Ambassador to Australia on CNA/CNE work and TAO collaboration.
-
SNOWGLOBE: From Discovery to Attribution [pdf]
This document describes how CSEC identified and analyzed the SNOWGLOBE intrusion set, using passive collection, implant reverse engineering, and infrastructure analysis to attribute the campaign with moderate confidence to a French intelligence service targeting Iranian and international scientific, diplomatic, and political organizations.
Programs: SNOWGLOBE · WARRIORPRIDE · REPLICANTFARM · SNOWBALL · SNOWMAN · EONBLUE · SPECIALSOURCE · CANDLEGLOWPeople: Roshal, Alexander“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Quand les Canadiens partent en chasse de « Babar »” - Le Monde ↗ (2014-03-21) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Follorou, Jacques · Untersinger, Martin -
SPINALTAP, Tracking Courier Use of Secure Digital Cards, and QUANTUMFALCON [pdf]
Three NSA presentations published as a single file. SPINALTAP, from Menwith Hill Station, extracts selectors from TAO, SFC and GCHQ endpoint accesses and translates them into XKEYSCORE fingerprints so that machines held by active operations can be recognised again in passive collection. Tracking Courier Use of Secure Digital Cards, from the NSA SIGINT Forensics Center, uses volume serial numbers and volume labels to identify SD cards and USB media that carry no USB controller, and reports identification information for 36 devices not seized during the UBL raid. QUANTUMFALCON summarises selector activity to triage targets for QUANTUM operations: see the Der Spiegel article The Digital Arms Race: NSA Preps America for Future Battle, 17 January 2015.
Programs: AARDVARKSTAKE · ABSOLINEDELTA · ACRIDMINI · AFTERBOOTSOLE · AFTERCLIFFDIVE · AFTERDOGHOUSE · AFTERGASSTATION · AFTERLASTTEAM · AFTERRICHGEAR · AFTERSHORTRUN · AFTERTANKERTRUCK · AFTERTREEFORM · AFTERWAYBACK · AFTERWINDBLOWN · AFTERYARDARM · ANCIENTBREW · APACHERIVER · ARMOREDCONDOR · ASDF · ATOMICCANNON · ATOMICFIREBALL · ATOMICFOG · ATOMICMONKEY · ATOMICPUNCH · ATOMICSTRIKE · AZTECTOMB · BACKSNARF · BEDOUINSTRIKE · BEEFCAKE · BLACK ALCHEMY · BLACKAMETHYST · BLACKMESA · BLOODDIAMOND · BROKENTHOUGHT · BULLETTOOTH · CAFFEINECRASH · CHOCOLATESHIP · COBALTGUPPY · COCOAMELTDOWN · CRISPWARE · CRYPTICSENTINEL · CUDDLYBADGER · CYGNUSOLOR · DANDERSPRITZ · DARKFIRE · DARKHELMET · DARKINTENT · DARKRAVEN · DARKRAZOR · DARKSCREW · DARKTHUNDER · DEADDRUMMER · DEPUTYSHIP · DETASSELJANICE · DIRTDIVER · DISTORTAFFECT · DOUBLETAP · DRINKMINT · DRINKMINTAA · DRUMBEAT · EDITIONHAZE · EFFABLELAMBDA · ELECTRONSWORD · EMPTYMOCHA · FIREBRUSH · FIREEATER · FIRESWAMP · FOXACID · FOXBASE · FRANTICDANCER · FREEACIDRAIN · FREEAIRFARE · FREEARCADEZONE · FREEBACKGAMMON · FREEBADFIBER · FREEBADRENT · FREEBALLROOM · FREEBATTLEZONE · FREEBEACHTREE · FREEBIGBOSS · FREEBITTERCLOUD · FREEBLACKCLOUD · FREEBLOODYWOLF · FREEBLOWNTURBO · FREEBLUEMAT · FREEBRASSBRUSH · FREEBUTTERCLOUD · UTT · FREECANALLOCK · FREECANESUGAR · FREECATBOX · FREECEMENTBLOCK · FREECHERRYCOLA · FREECHESSBOARD · FREECLEARTAPE · FREECOLDTEA · FREECORNHUSK · FREECORNMAZE · FREECREEKMOOR · FREECRUSHEDDISK · FREEDARKSUIT · FREEDATALOSS · FREEDEADBATTERY · FREEDETOURSIGN · FREEDIRTYTRICK · FREEDISCOVERY · FREEDISKBRAKE · FREEDOGCRATE · FREEDOMECUPOLA · FREEDOVETAIL · FREEEMUFARM · FREEENERGYTAX · FREEFAMILYTIE · FREEFASTCAR · FREEFIBERBOARD · FREEFILEDELETE · FREEFLATFIBER · FREEFLOWCHART · FREEFLOWERPEOPLE · FREEFRIEZEFRESCO · FREEGEMSTONE · FREEGLASSTUBE · FREEGLUESTRIP · FREEHAVEFUN · FREEHOMEBASE · FREEHOOKHANDLE · FREEHOOPDREAM · FREEJETFUEL · FREEKIDPOOL · FREEKINGSPAWN · FREEKNOCKOUT · FREELANDLINE · FREELEADSHOT · FREELEADSINGER · FREELIFERAFT · FREELIKESAME · FREELINEDOWN · FREELOLLYPOP · FREEMARBLEBASIN · FREEMETALCRATE · FREEMETALFILE · FREEMETALSHARD · FREEMINETUNNEL · FREEMINTJELLY · FREENAVYBLUE · FREENIGHTTRAIN · FREEOBLIQUECASE · FREEOILLEAK · FREEOILPAINT · FREEOLDBIKE · FREEOUTRUN · FREEPAINTBALL · FREEPICKLEBRINE · FREEPINEPLANK · FREEPLASTICCASE · FREEPONGPLAYER · FREEPOSTMARK · FREEPOWERFAILURE · FREEPUFFYCLOUD · FREEPULLCHAIN · FREERAINCLOUD · FREERAVENTICKET · FREEREDBEER · FREEREDERASER · FREEREDMARKER · FREEREDSHIRT · FREEREDSTAIN · FREERIDEAROUND · FREERIGHTWHALE · FREERIPPINGBLADE · FREEROCKSONG · FREESAFEKEY · FREESALTTRUCK · FREESASHCORD · FREESCHOOLLOCKER · FREESCREENDOOR · FREESEADADDY · FREESHORTCARD · FREESHORTPASS · FREESINEWAVE · FREESLOWFAST · FREESMALLSPACE · FREESMOKESCREEN · FREESNOWCLOUD · FREESNOWSHOVEL · FREESPACEFLIGHT · FREESPEEDTRAP · FREESTATEWARD · FREESTONESHIP · FREESTORAGEROOM · FREETANKSTAND · FREETESTSHEET · FREETHUNDERCLOUD · FREETICKETBOOTH · FREETIMELEGEND · FREETIMESHARE · FREETINYTANK · FREETRICKYKICK · FREETROUTSTREAM · FREETRUEPINBALL · FREETWINBEE · FREEVINYLMESH · FREEWARRIORPAINT · FREEWATERBED · FREEWATERGLASS · FREEWATERTANK · FREEWATERTOWER · FREEWAVECREST · FREEWAYPOINT · FREEWHEELCOVER · FREEWHEELNUT · FREEWINDCLOUD · FREEWINDSHEAR · FREEWOODENSTICK · FURRYEWOK · GHOSTMACHINE · GMPLACE · GOODMONKEY · HAMMERBROTHERS · HASTYCOBRA · HORSEWRAP · ICEBLOCK · IMPUREHOLSTER · INDEPENDENCEPIE · INQUIRY · JAVAFRESCO · JEALOUSJOKER · JEEPFLEA · JEEPFLEAMARKET · JOLLYROGER · KIDSHIPAA · KOOPATROOPA · KUKRISTEEL · LIQUIDSTEEL · LUTEUSASTRO · MAGNUMOPUS · MAGNUMOPUSCC · MARINA · MAXRANKLE · MICEFUR · MIDNIGHTSCORPION · MILKSTEAK · MIRACLEMAX · MUSHROOMKINGDOM · NAPALAN · NATIVEFLORA · OBSCUREBLAZE · OFFICELINEBACKER · OFFICEQUARTERBACK · OPTIMUSPRIME · PARLAYBUFFET · PHANTOMSTARFISH · PLUMREVOLVER · PRETZELDOG · QBISCUIT · QDIRK · QUANTUM · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUMFALCON · REACTOR · ROLLEDHAT · SANDPALACE · SCARFSLOOP · SHADYNINJA · SHAKEWEIGHT · SHATTEREDSHIELD · SILENTTONGUES · SILLYBUNNY · SILVERJUMP · SKYJACKBRAD · SLYNINJA · SLYSNOW · SLYWIZARD · SNAPKEY · SPARTANFURY · SPIKEYFARM · SPINALTAP · STARPROC · STEELSKY · STEELSKYDELTA · STEELSKYECHO · STEELSKYFOXTROT · STEELSKYGOLF · STONEHENGE · STRAITLACED · SWITCHDOWN · SWITCHDOWNIRAW · SWITCHDOWNIRBR · SWITCHDOWNIRCD · THIEVESQUARTER · TOADYTEAL · TOTALDAGGER · TOXICSNOW · TROPICALSTORM · UMBRAGESPIDER · UNITEDRAKE · UPPERMUTANT · VALIDATOR · VEILEDMAGIC · WATERCASKET · WATERWINGS · WAXCHIP · WICKEDAMP · WILDCHOCOBO · WITHEREDFRUIT · WOLFACID · WOLFACIDANISE · WOLFACIDARGON · WOLFACIDBARIUM · WOLFACIDCHILI · WOLFACIDIODINE · WOLFACIDIRON · WOLFACIDJUPITER · WOLFACIDLEAD · WOLFACIDPRECIOUS · WOLFACIDTIN · WOLFACIDURANIUM · WOLFACIDZINC · XKEYSCORE · YELLOWFAN · MUSCULAR · INCENSER · DANCINGOASIS · MAPREDUCE“Documents Reveal Top NSA Hacking Unit” - Der Spiegel ↗ (2013-12-29) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Poitras, Laura · Rosenbach, Marcel · Stöcker, Christian · Schindler, Jörg · Stark, Holger · Gallagher, Ryan · Greenwald, Glenn · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
SSO news excerpts [pdf]
These SSO news exceprts describe the successful deployment of QUANTUMTHEORY and QUANTUMINSERT capabilities by the NSA’s Tailored Access Operations (TAO) team, in collaboration with Special Source Operations (SSO), to exploit high-value targets, including key figures in the Haqqani network. Using a combination of signal case notations and real-time exploitation via QUANTUMHAND, TAO was able to implant malicious software on the target's computer, enabling further intelligence collection and exploitation.
Programs: QUANTUMTHEORY · QUANTUM · QUANTUMINSERT · FOXACID · DANCINGOASIS · FOXCONTACT · VALIDATOR · SARATOGA · TURMOIL · QUANTUMHAND · SSOPeople: Haqqani, Badruddin