Using XKEYSCORE to Enable TAO
Open PDFDocument date: 2009-07-16
Pages: 47
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, AUS, CAN, GBR, NZL
A TOP SECRET training presentation from 2009, authored by a Booz Allen Hamilton contractor, teaching NSA analysts how to use XKeyscore to harvest the login credentials, router configurations, browser versions and server software details that the Tailored Access Operations hacking unit needs to break into foreign computer networks — with worked examples stealing Cisco router passwords, Iranian government webmail logins and jihadi web forum credentials directly from intercepted internet traffic.
My notes
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
Using XKEYSCORE to Enable TAO
[REDACTED]
Booz | Allen | Hamilton SDS Analyst
16 July 2009
Derived From: NSA/CSSM 1-52
Dated: 20070108
Declassify On: 20291123
DERIVED FROM: NSA/CSSM 1-52
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL//20291123
08
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Purpose of This Briefing
- To show S2 Analysts how to use XKS to enable TAO operations
- The material covers some of the more common searches in XKS, and shows you how to retrieve valuable SIGINT data that S3/TAO finds useful to exploit a target
- It's NOT designed to teach you about TAO (there are many other briefings for that)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Agenda
- What TAO needs from analysts
- TELNET Sessions in XKS
- Identifying Browers
- Web Forum Logins / Passwords
- Webmail Logins / Passwords
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Agenda
- What TAO needs from analysts
- TELNET Sessions in XKS
- Identifying Browsers
- Web Forum Logins / Passwords
- Webmail Logins / Passwords
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
What does TAO need?
- Network Information
- Logins and Passwords
- Router configuration information
- Software Information
- Browser
- Version Numbers
- Operating Systems
- NOTE: If target device is under a satellite hop, please consult your TAO Liaison on how to proceed.
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
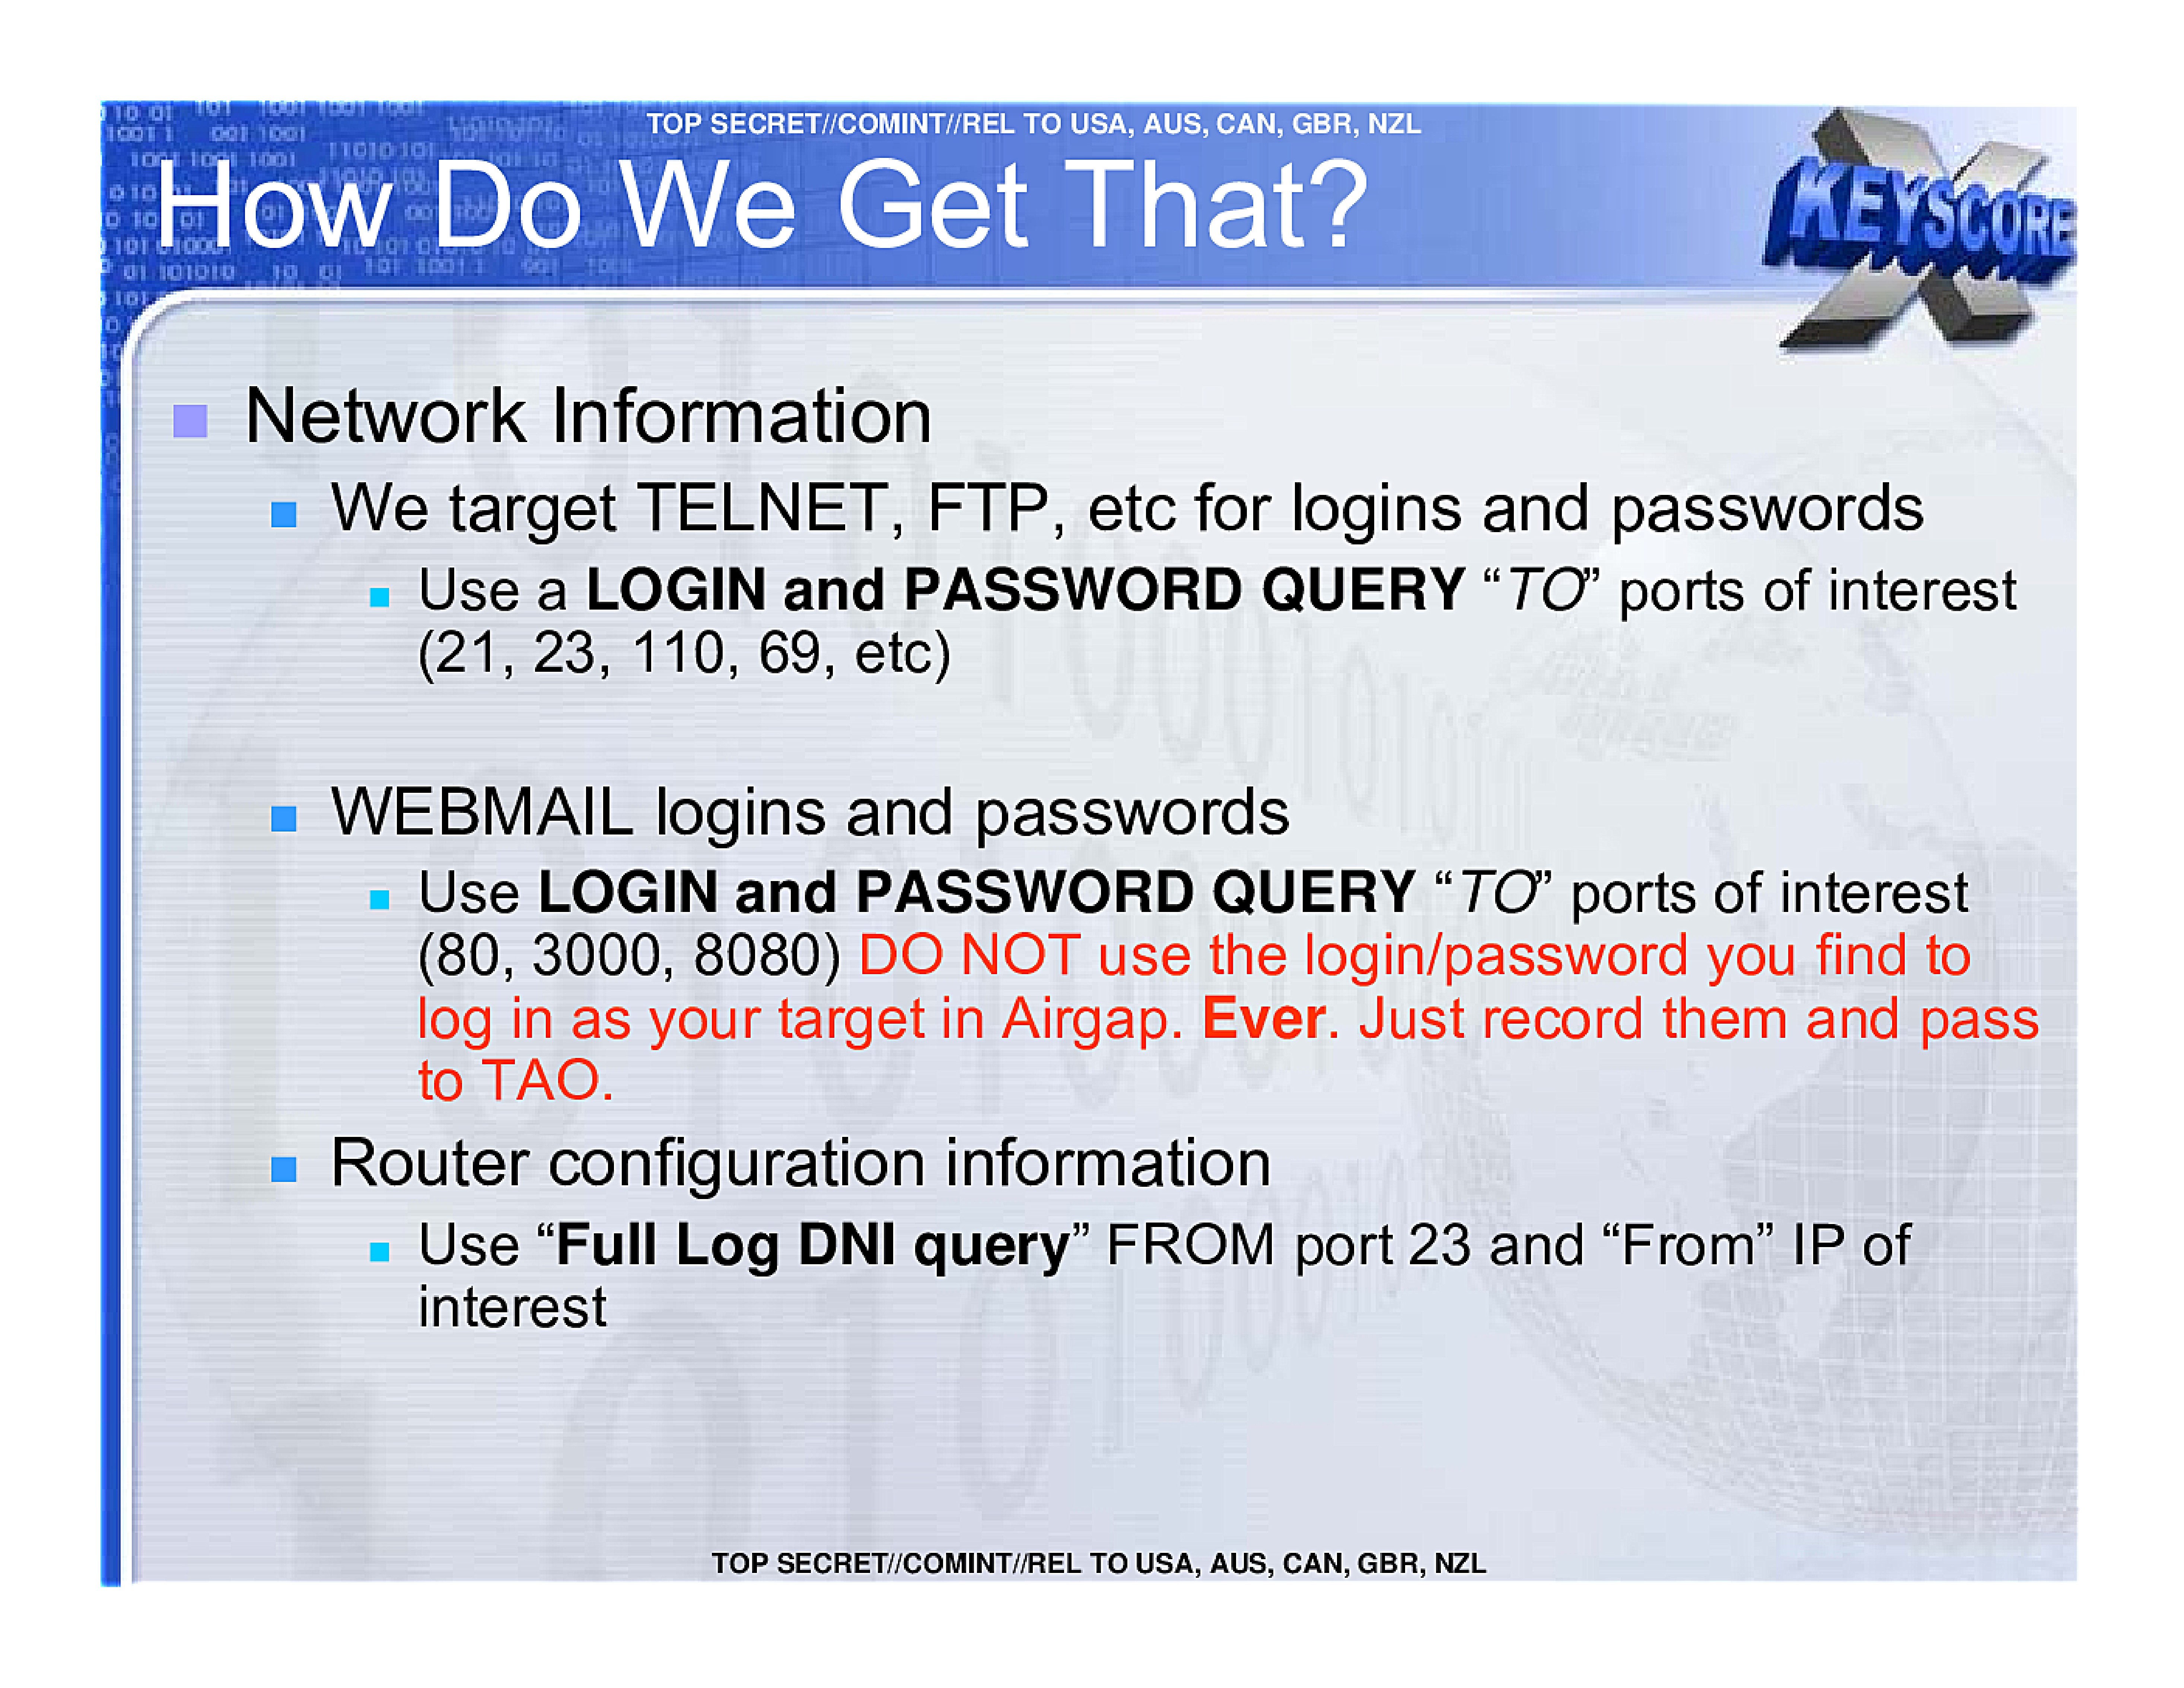
How Do We Get That?
- Network Information
- We target TELNET, FTP, etc for logins and passwords
- Use a LOGIN and PASSWORD QUERY "TO" ports of interest (21, 23, 110, 69, etc)
- We target TELNET, FTP, etc for logins and passwords
- WEBMAIL logins and passwords
- Use LOGIN and PASSWORD QUERY "TO" ports of interest (80, 3000, 8080) **DO NOT use the login/password you find to log in as your target in Airgap. Ever. Just record them and pass to TAO.
- Router configuration information
- Use "Full Log DNI query" FROM port 23 and "From" IP of interest
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
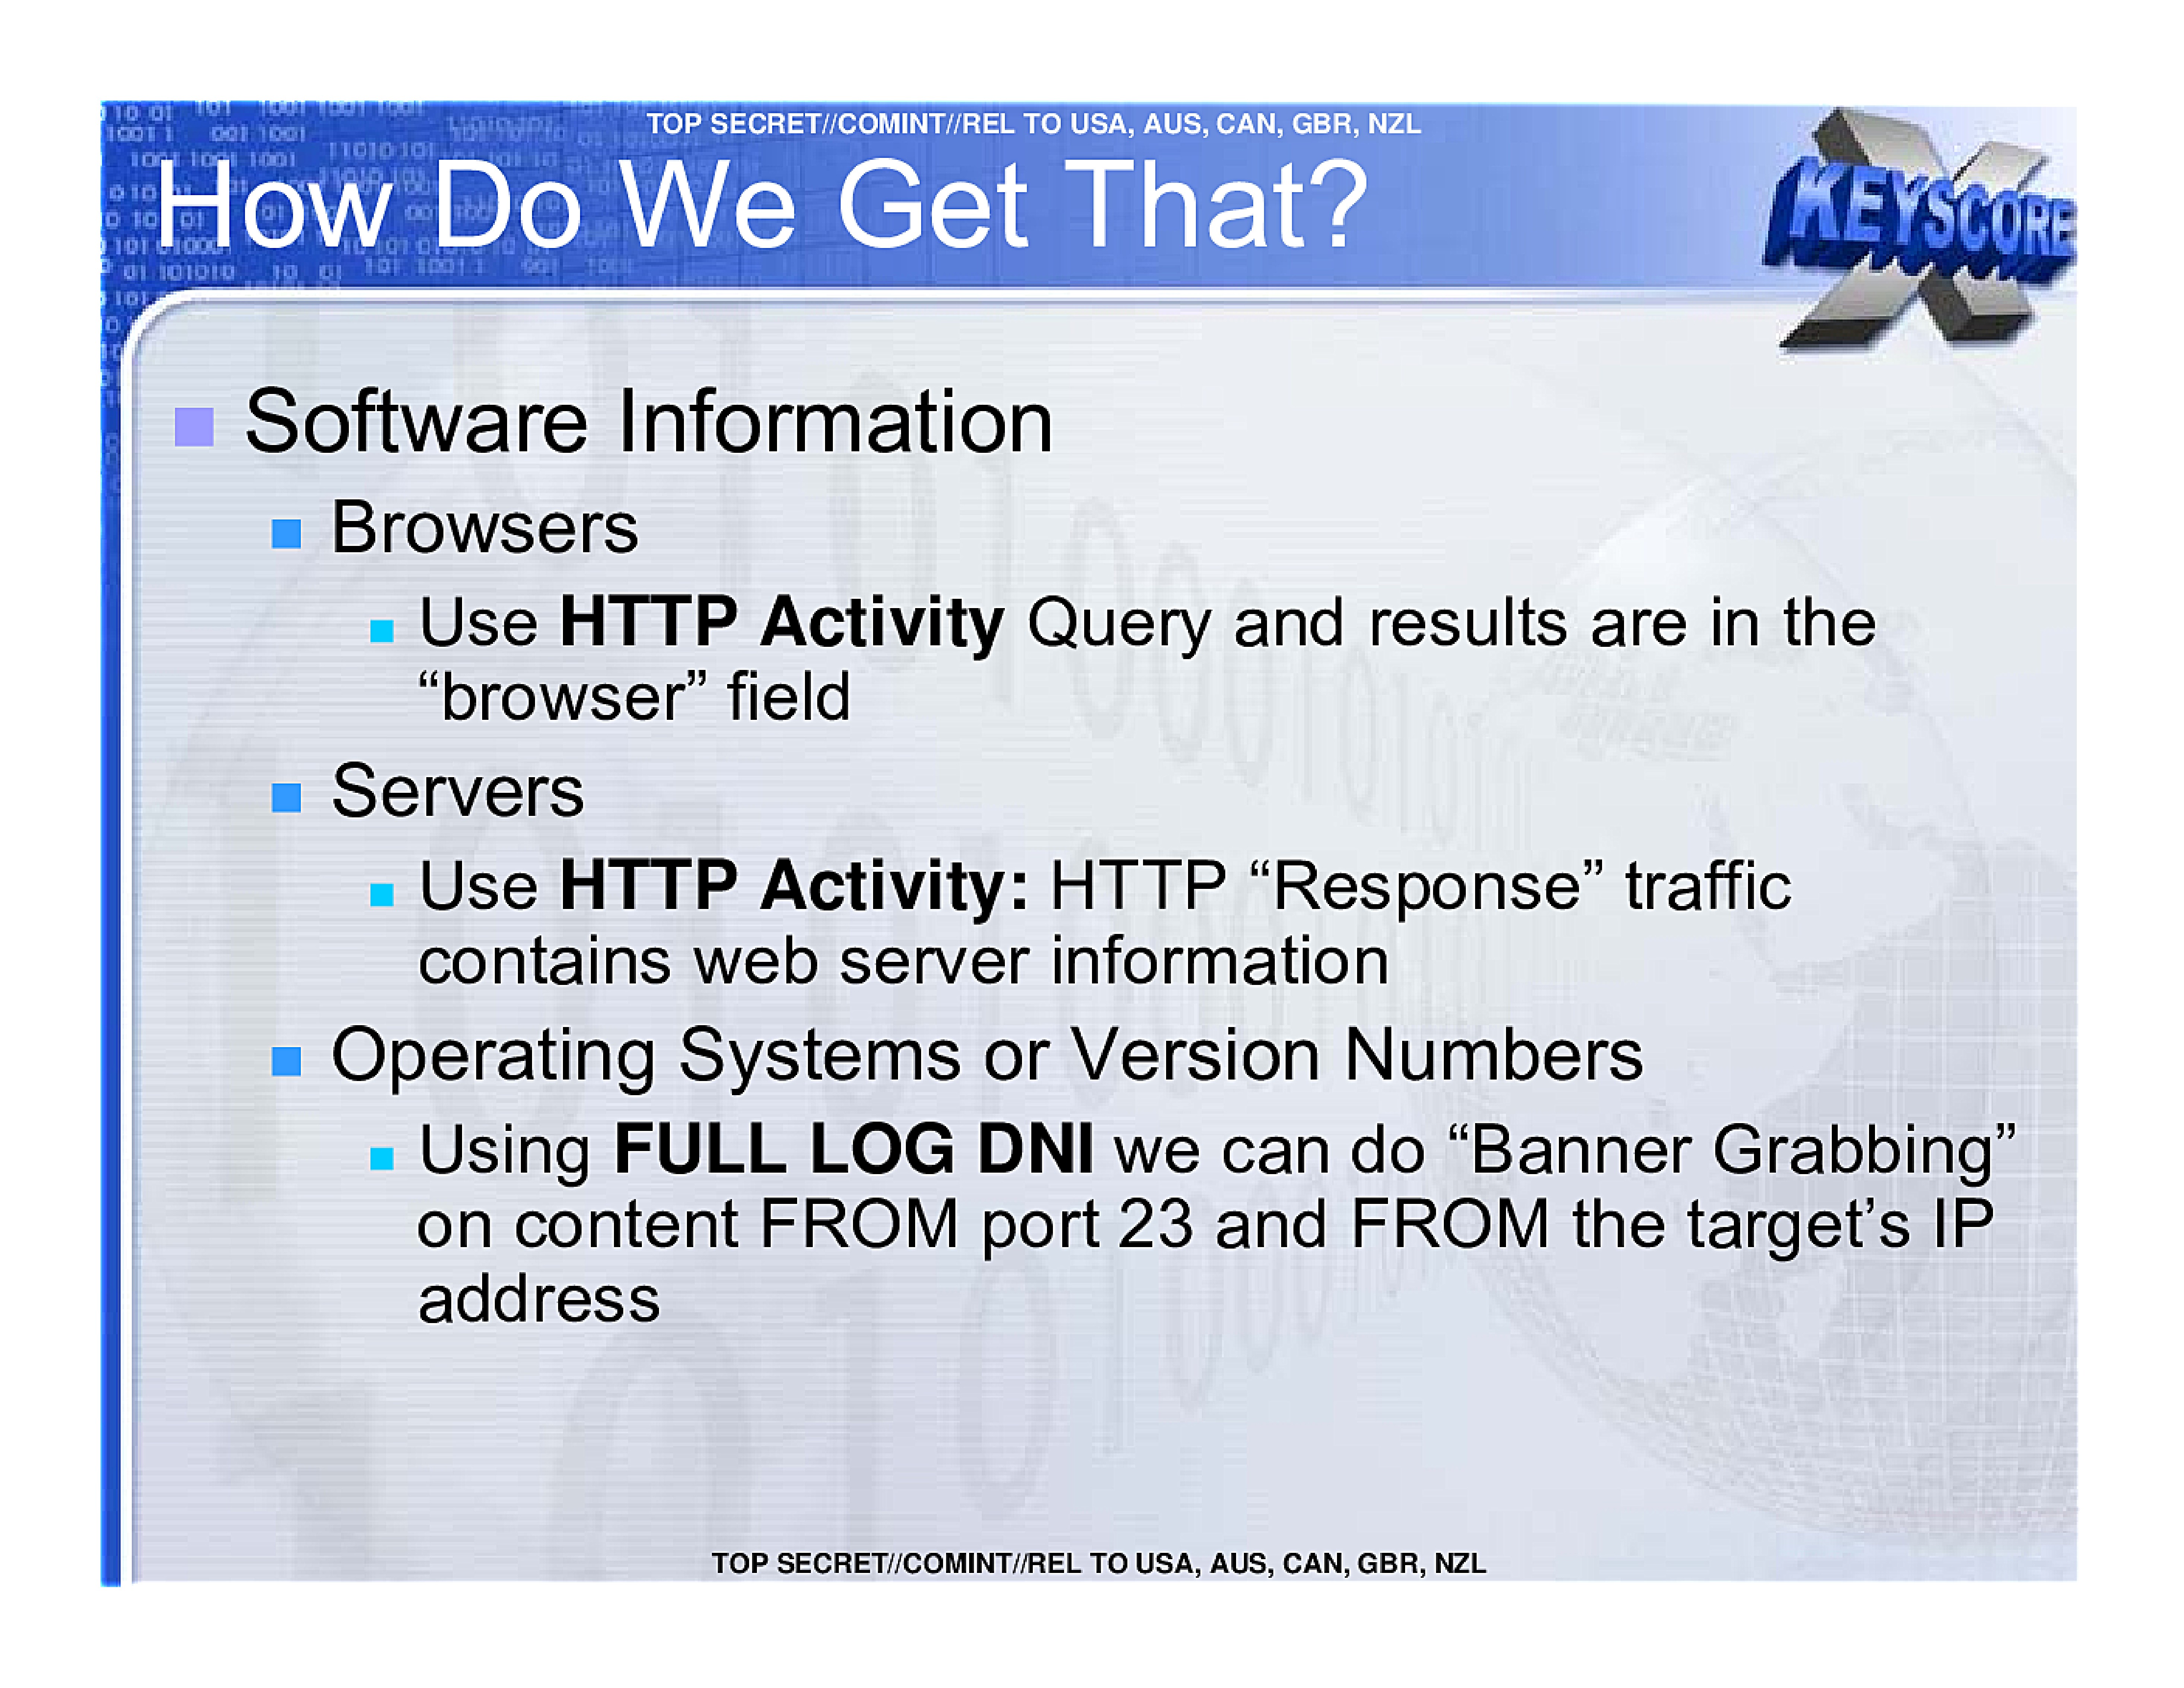
How Do We Get That?
- Software Information
- Browsers
- Use HTTP Activity Query and results are in the "browser" field
- Servers
- Use HTTP Activity: HTTP "Response" traffic contains web server information
- Operating Systems or Version Numbers
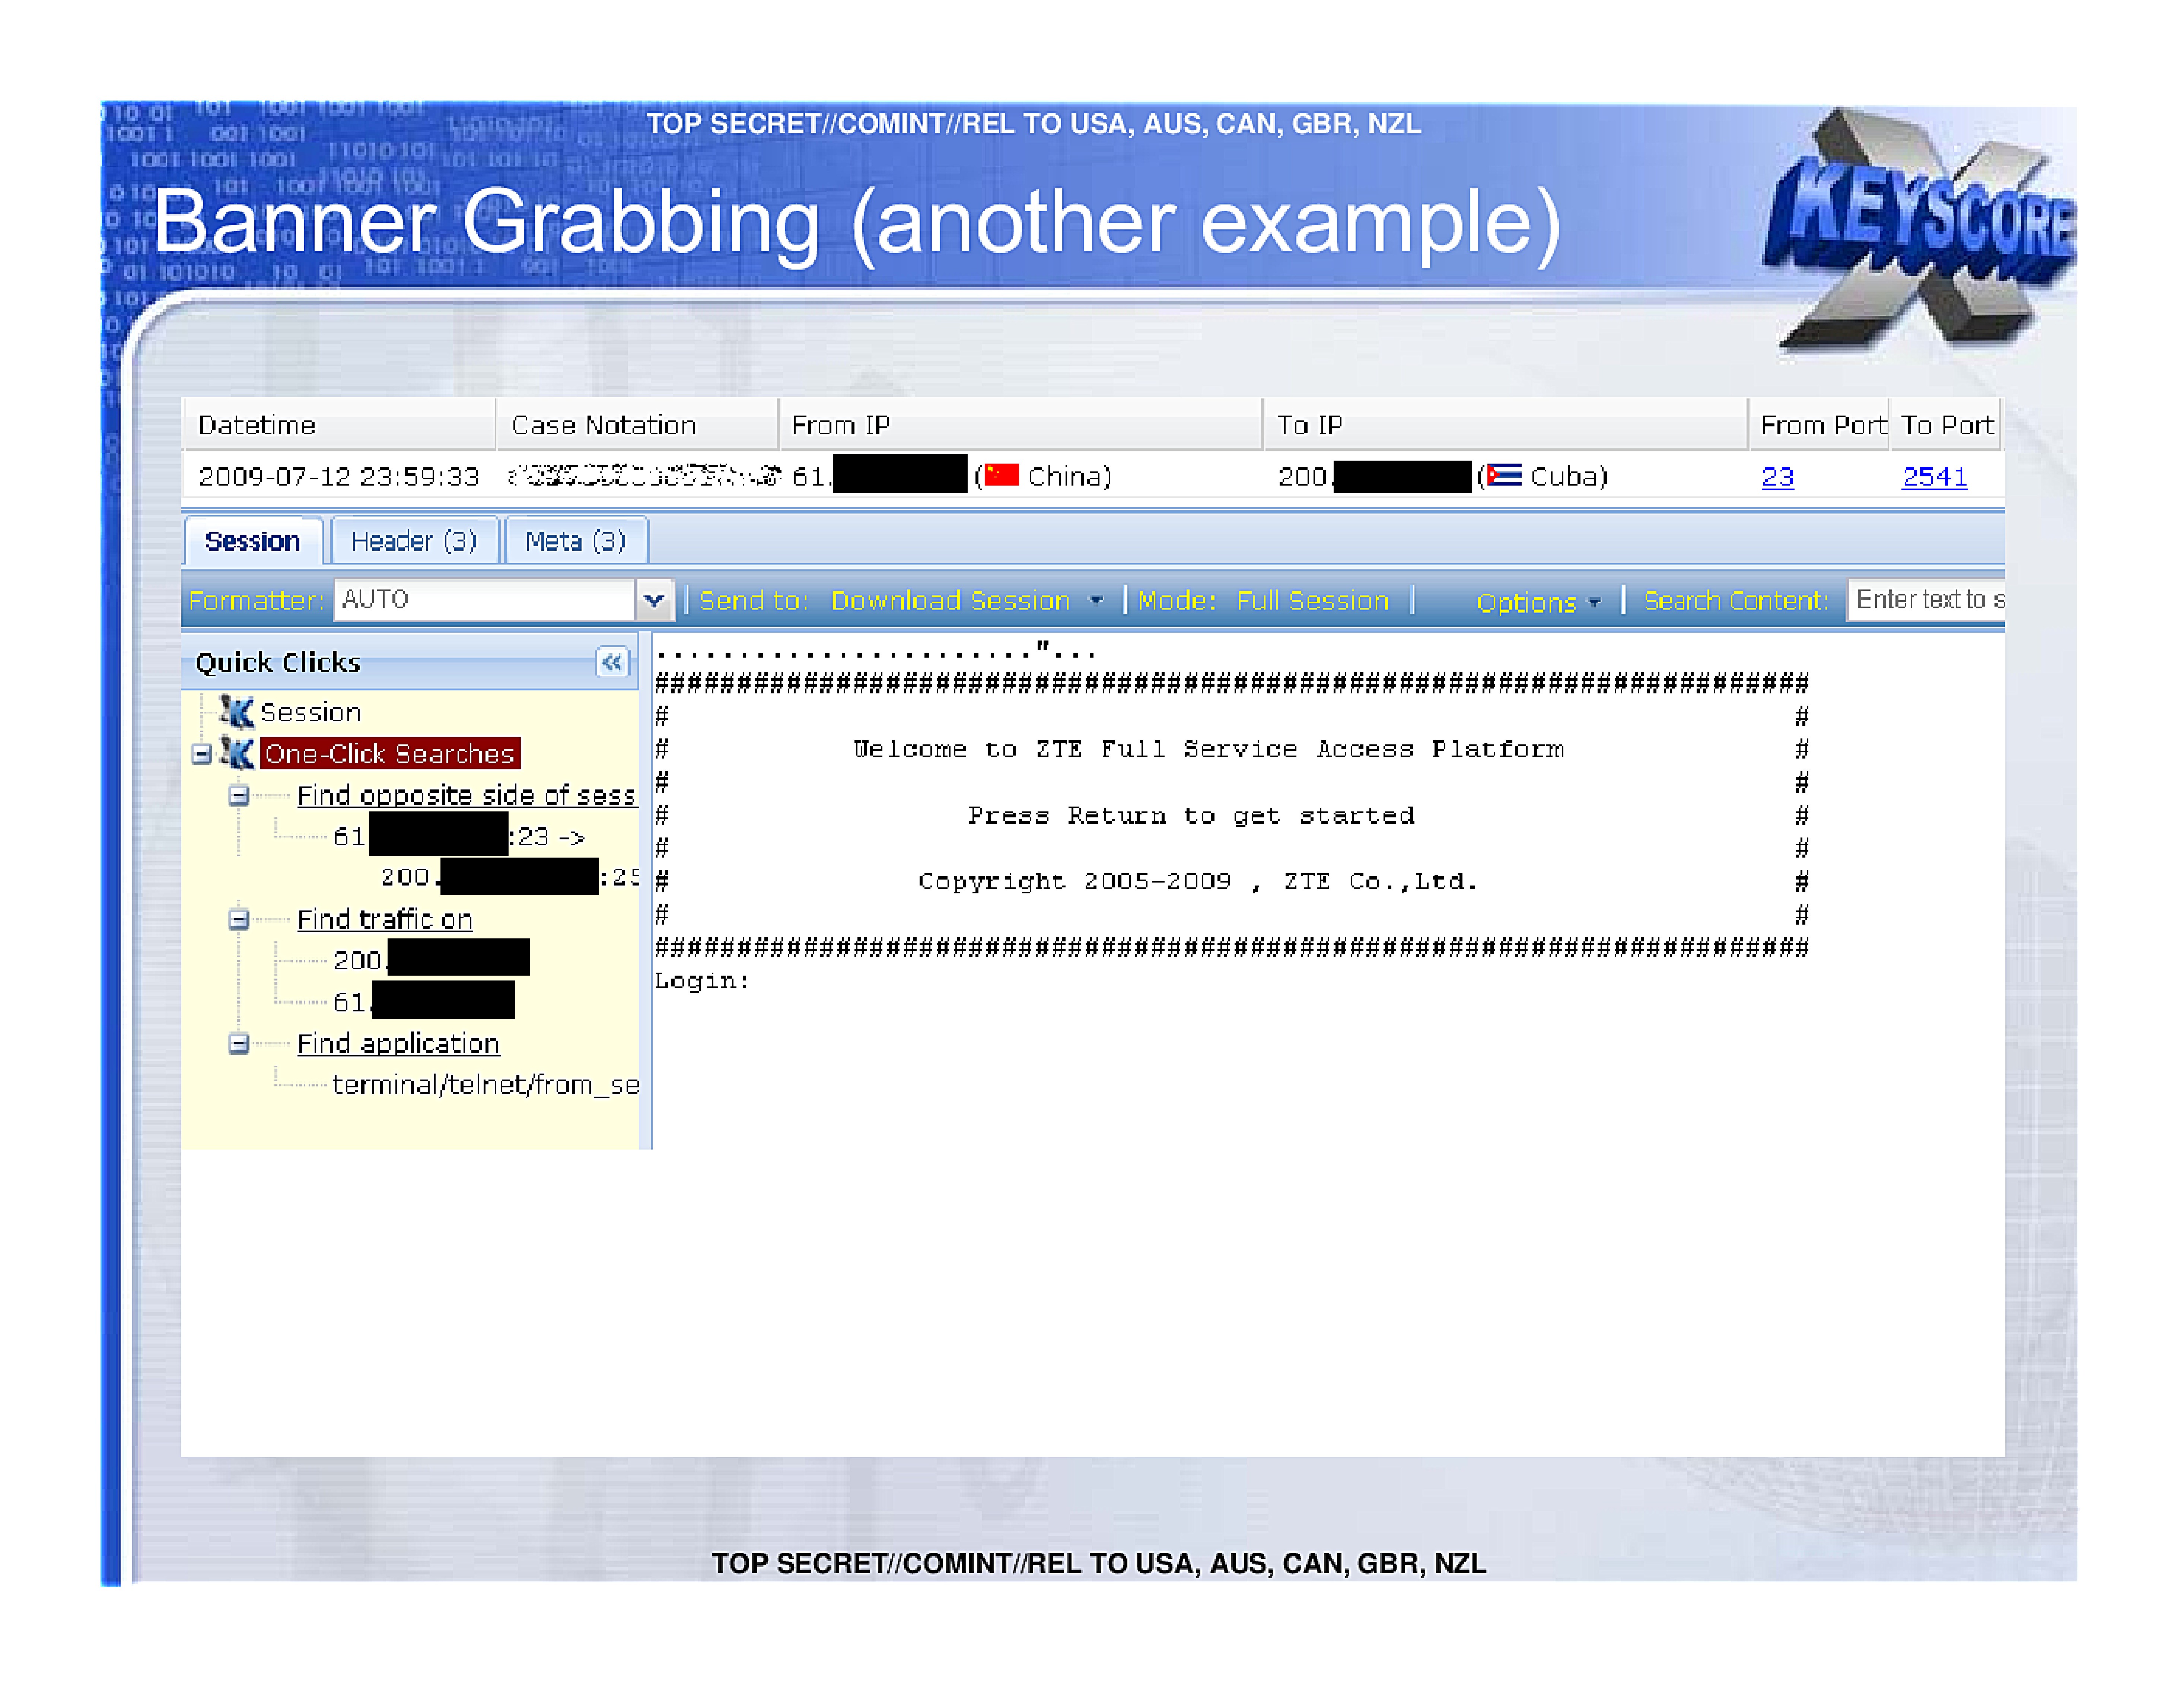
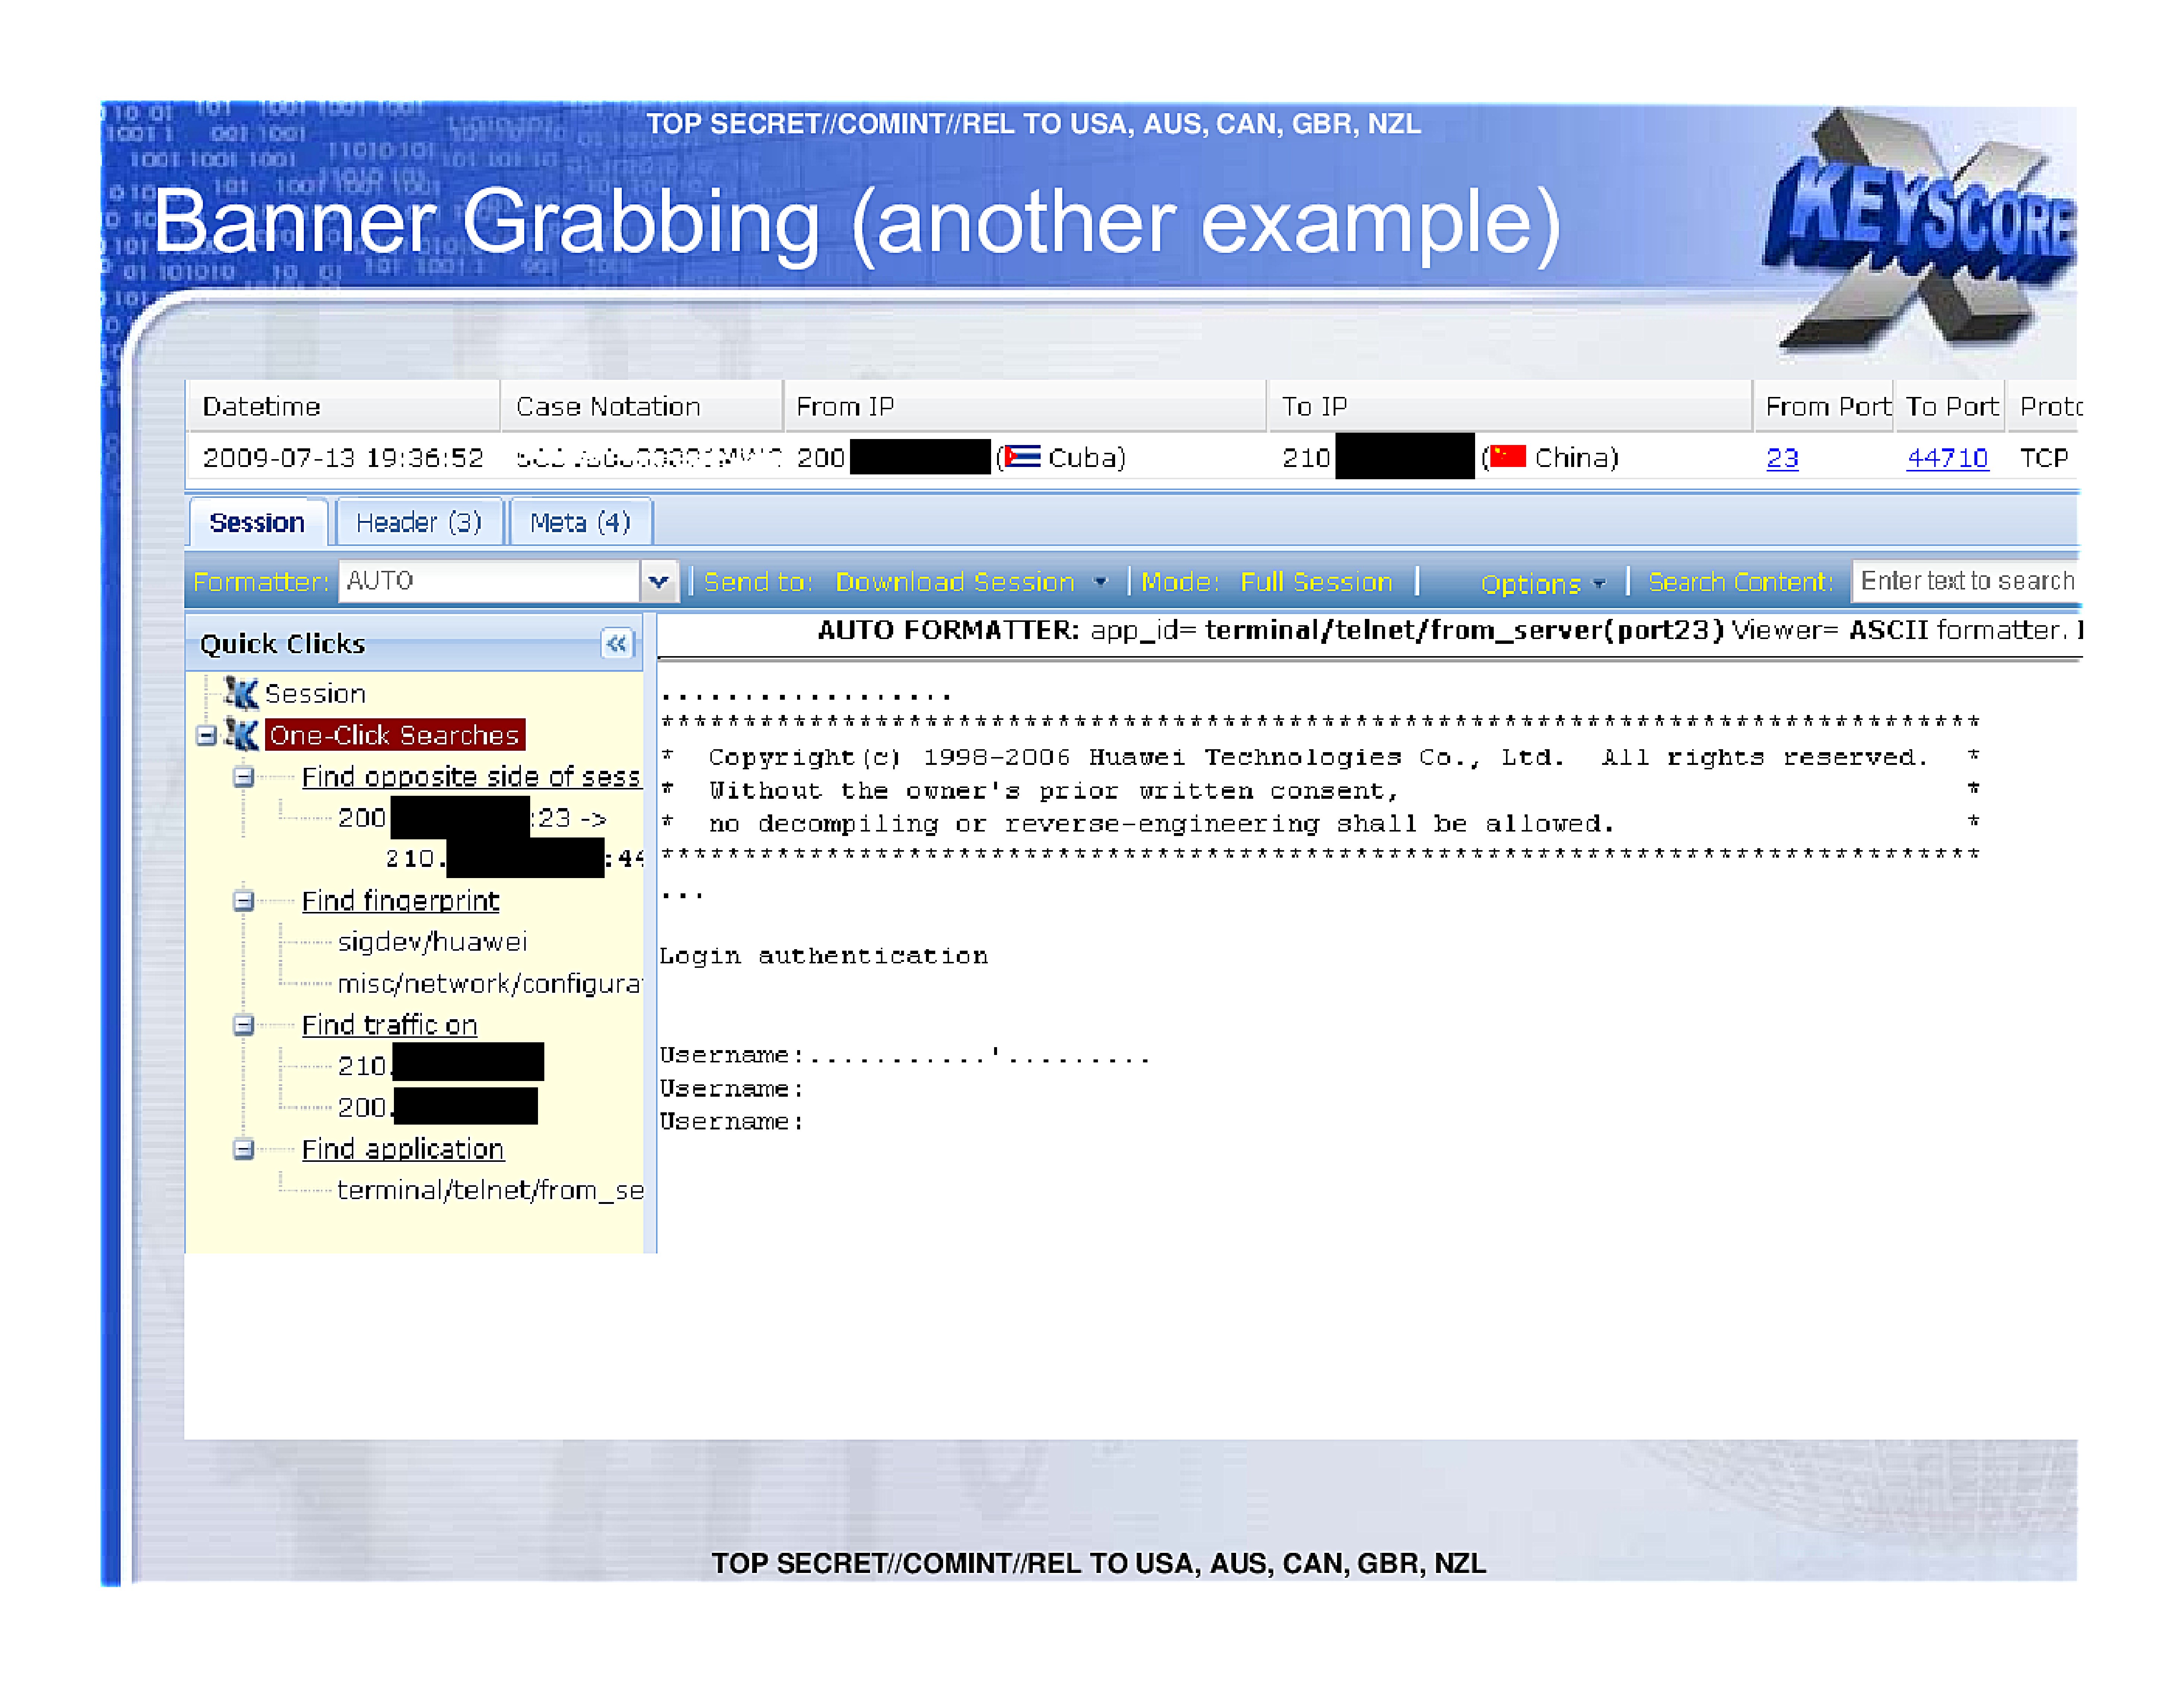
- Using FULL LOG DNI we can do "Banner Grabbing" on content FROM port 23 and FROM the target's IP address
- Browsers
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Agenda
- What TAO needs from analysts
- TELNET Sessions in XKS
- Identifying Browers
- Web Forum Logins / Passwords
- Webmail Logins / Passwords
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
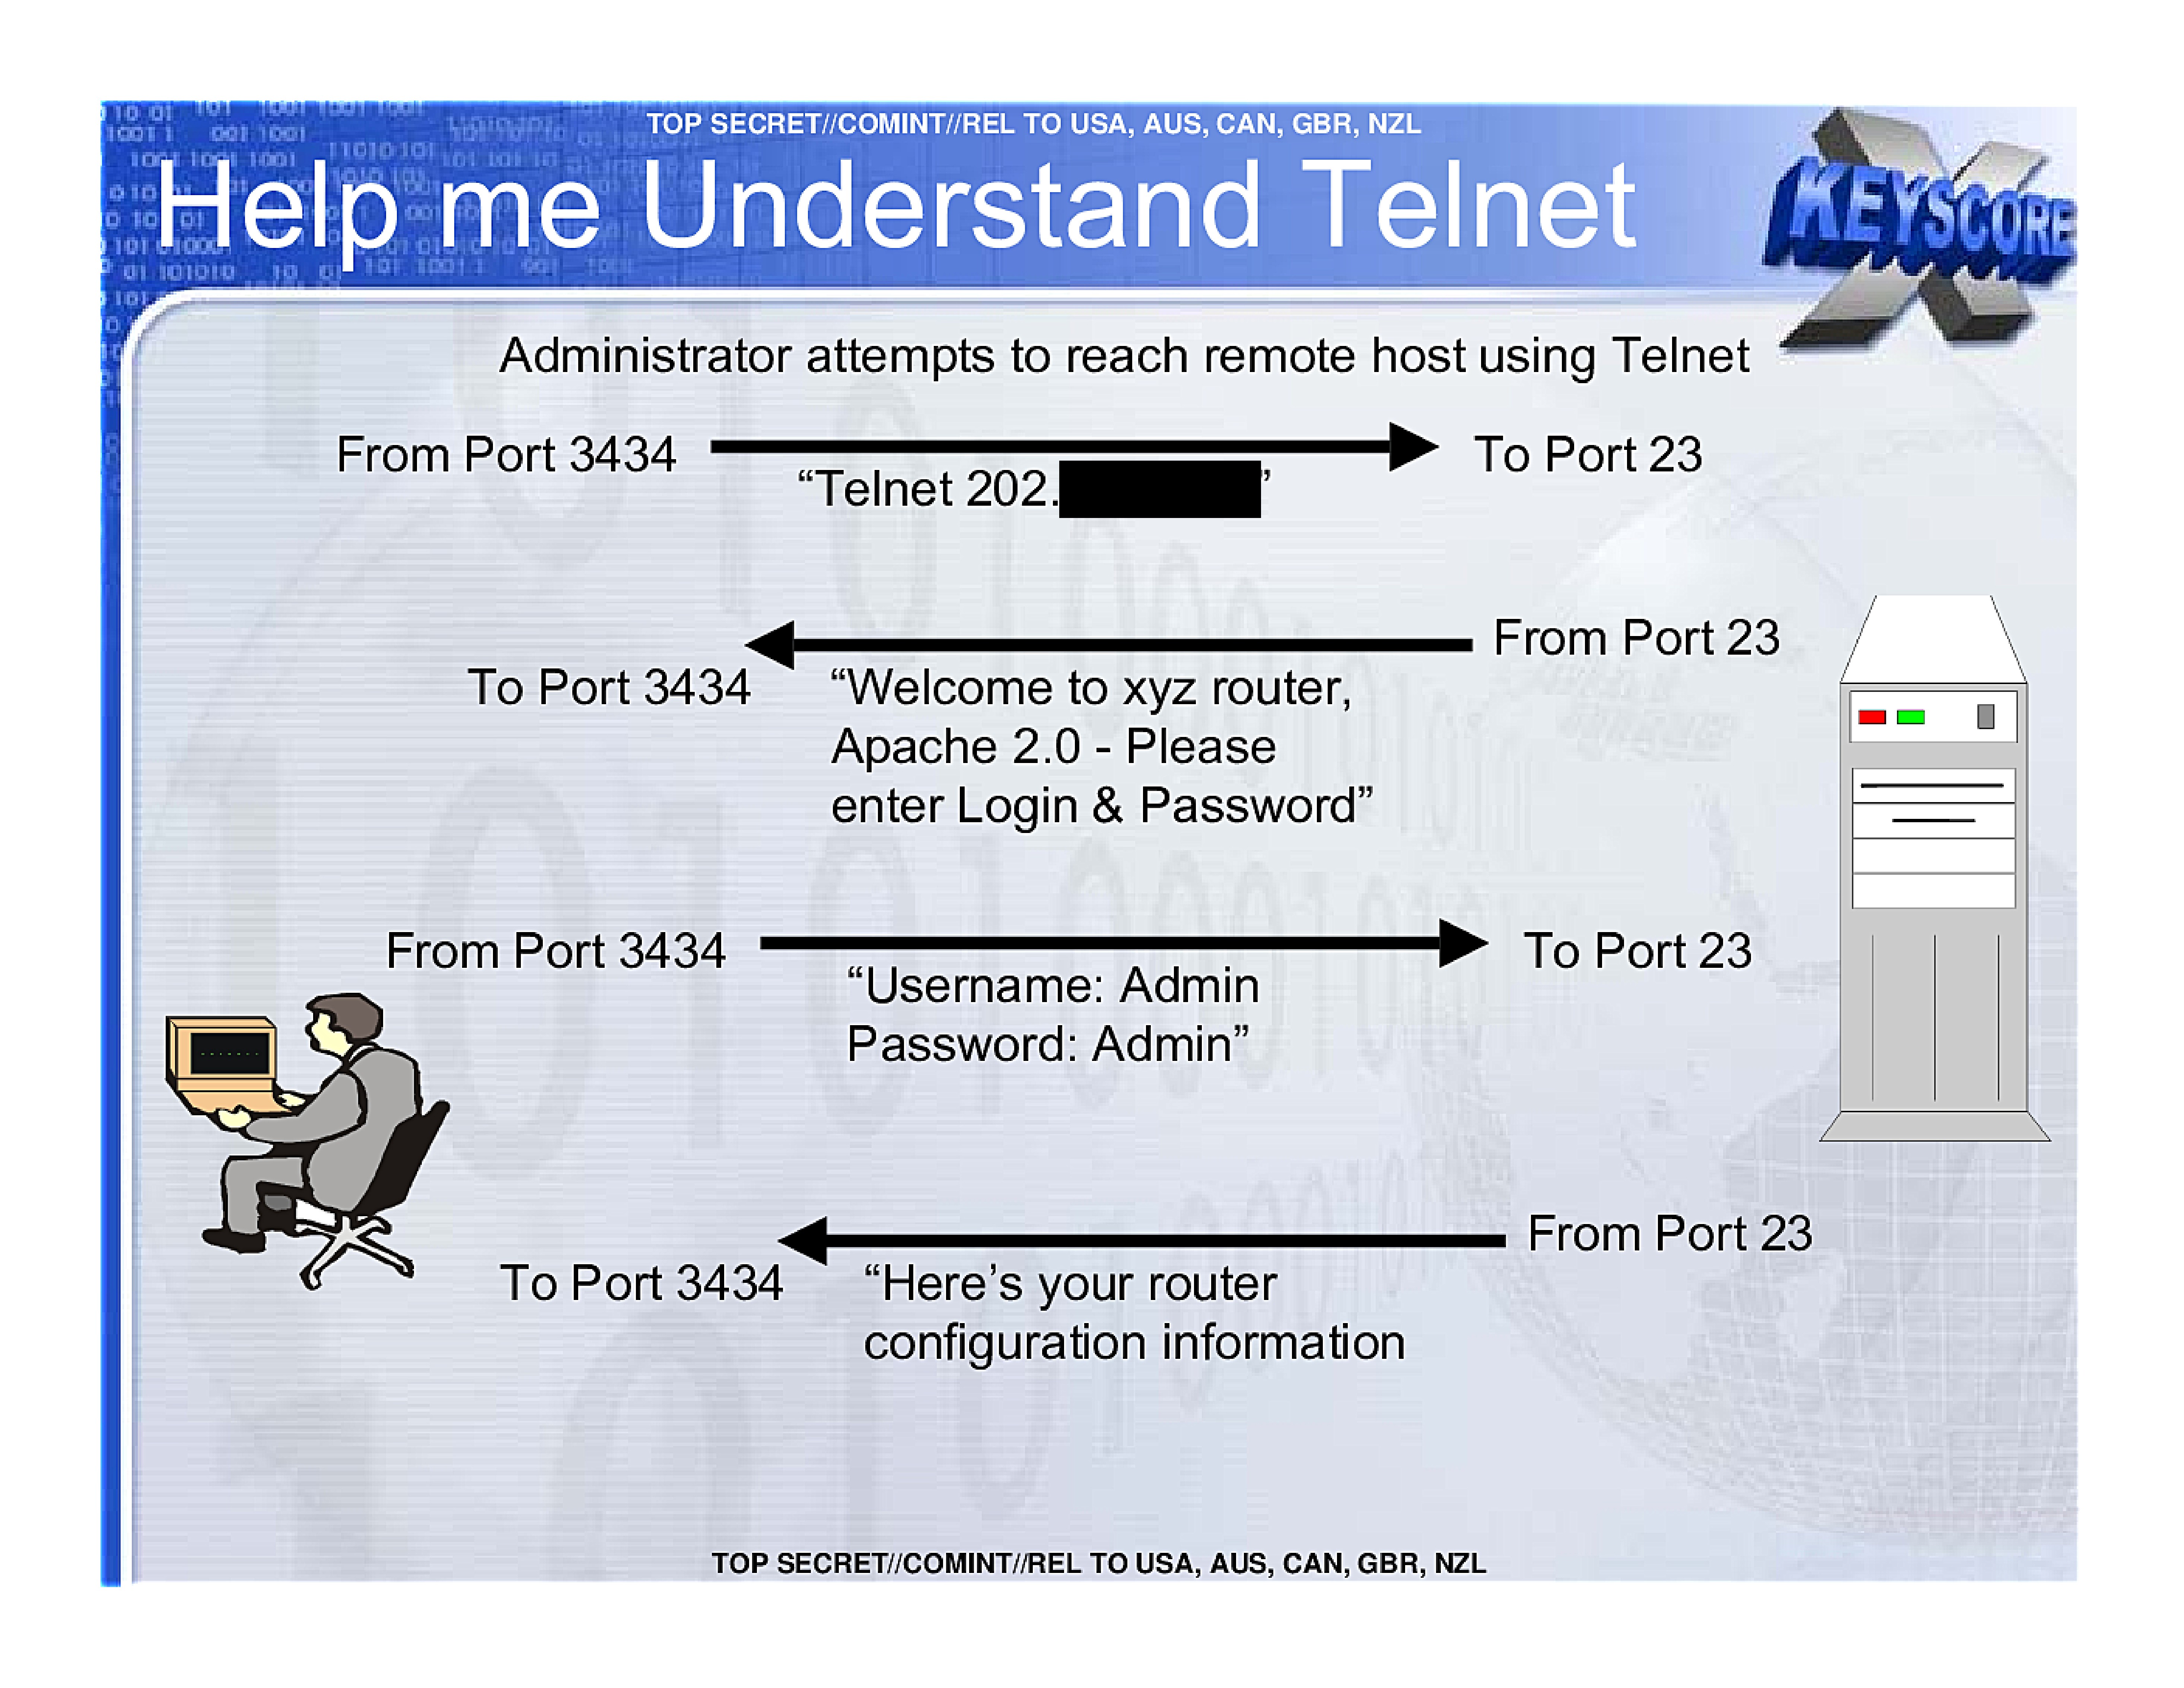
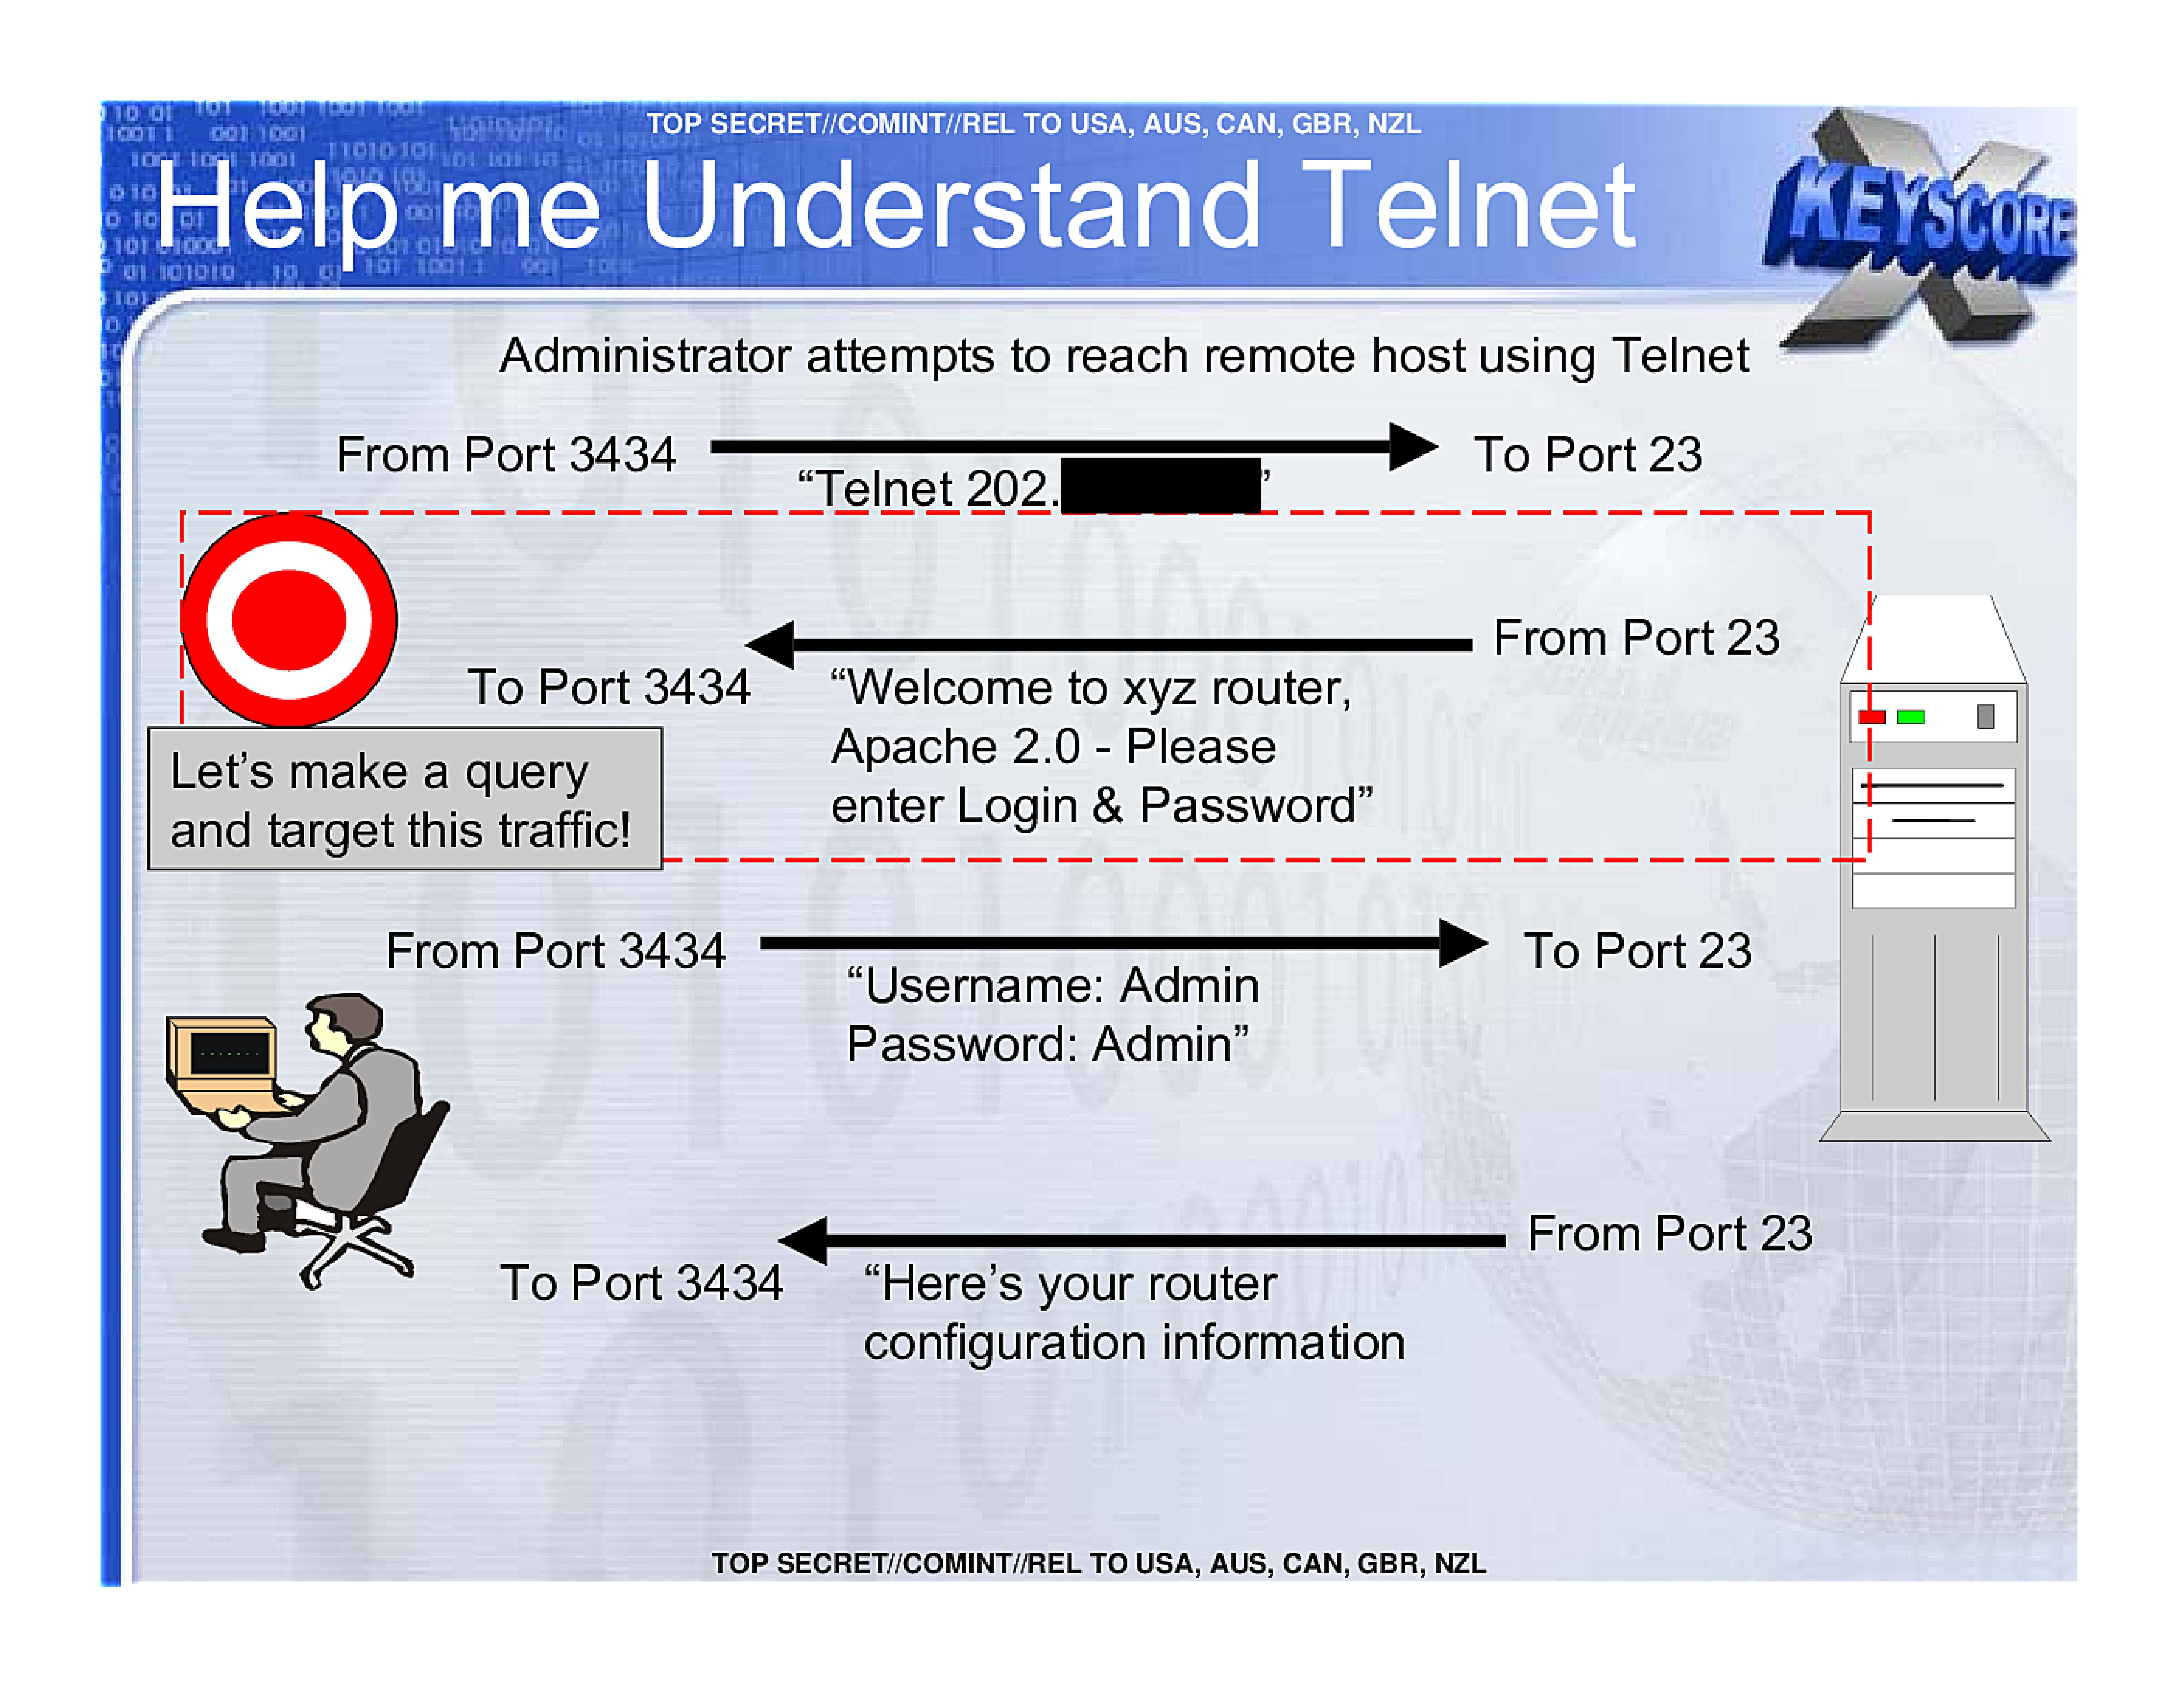
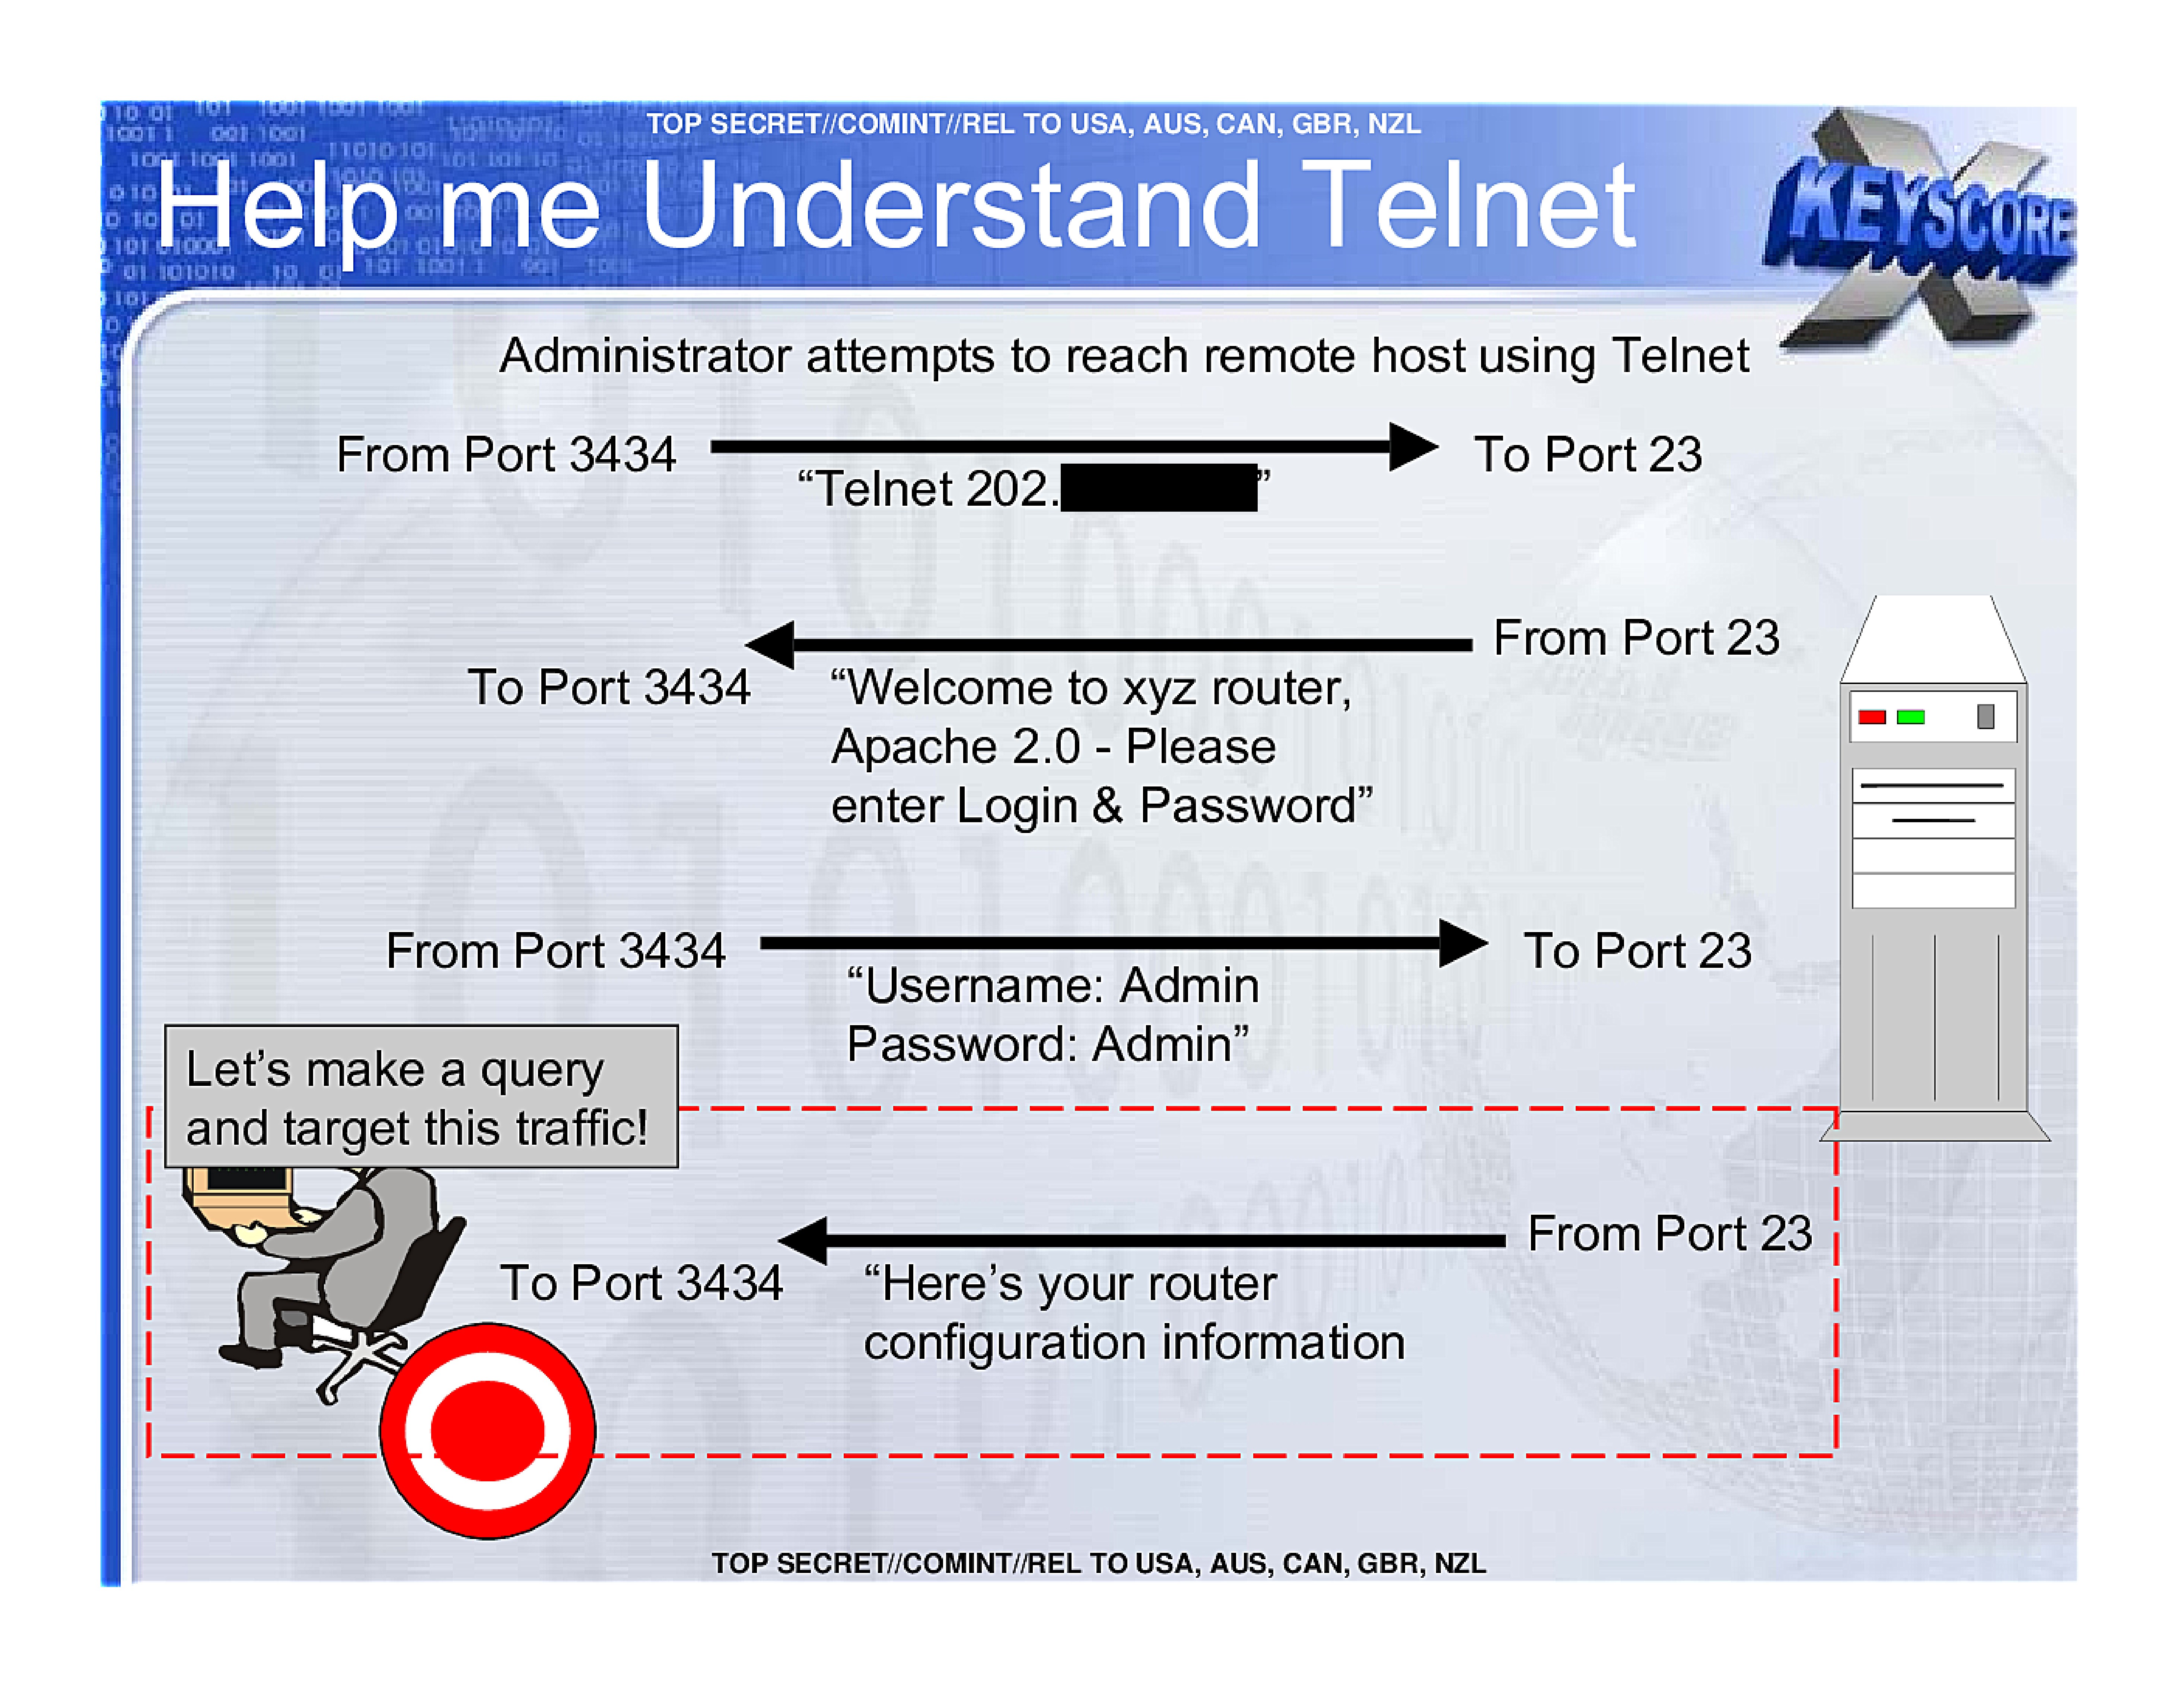
Help me Understand Telnet
Administrator attempts to reach remote host using Telnet
From Port 3434
"Telnet 202.[REDACTED]
To Port 23
To Port 3434
From Port 23
"Welcome to xyz router,
Apache 2.0 - Please
enter Login & Password"
From Port 3434
To Port 23
"Username: Admin
Password: Admin"
To Port 3434
From Port 23
"Here's your router
configuration information
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Help me Understand Telnet
Administrator attempts to reach remote host using Telnet
From Port 3434
"Telnet 202.[REDACTED]
To Port 23
Let's make a query
and target this traffic!
To Port 3434
From Port 23
"Welcome to xyz router,
Apache 2.0 - Please
enter Login & Password"
From Port 3434
To Port 23
"Username: Admin
Password: Admin"
To Port 3434
From Port 23
"Here's your router
configuration information
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
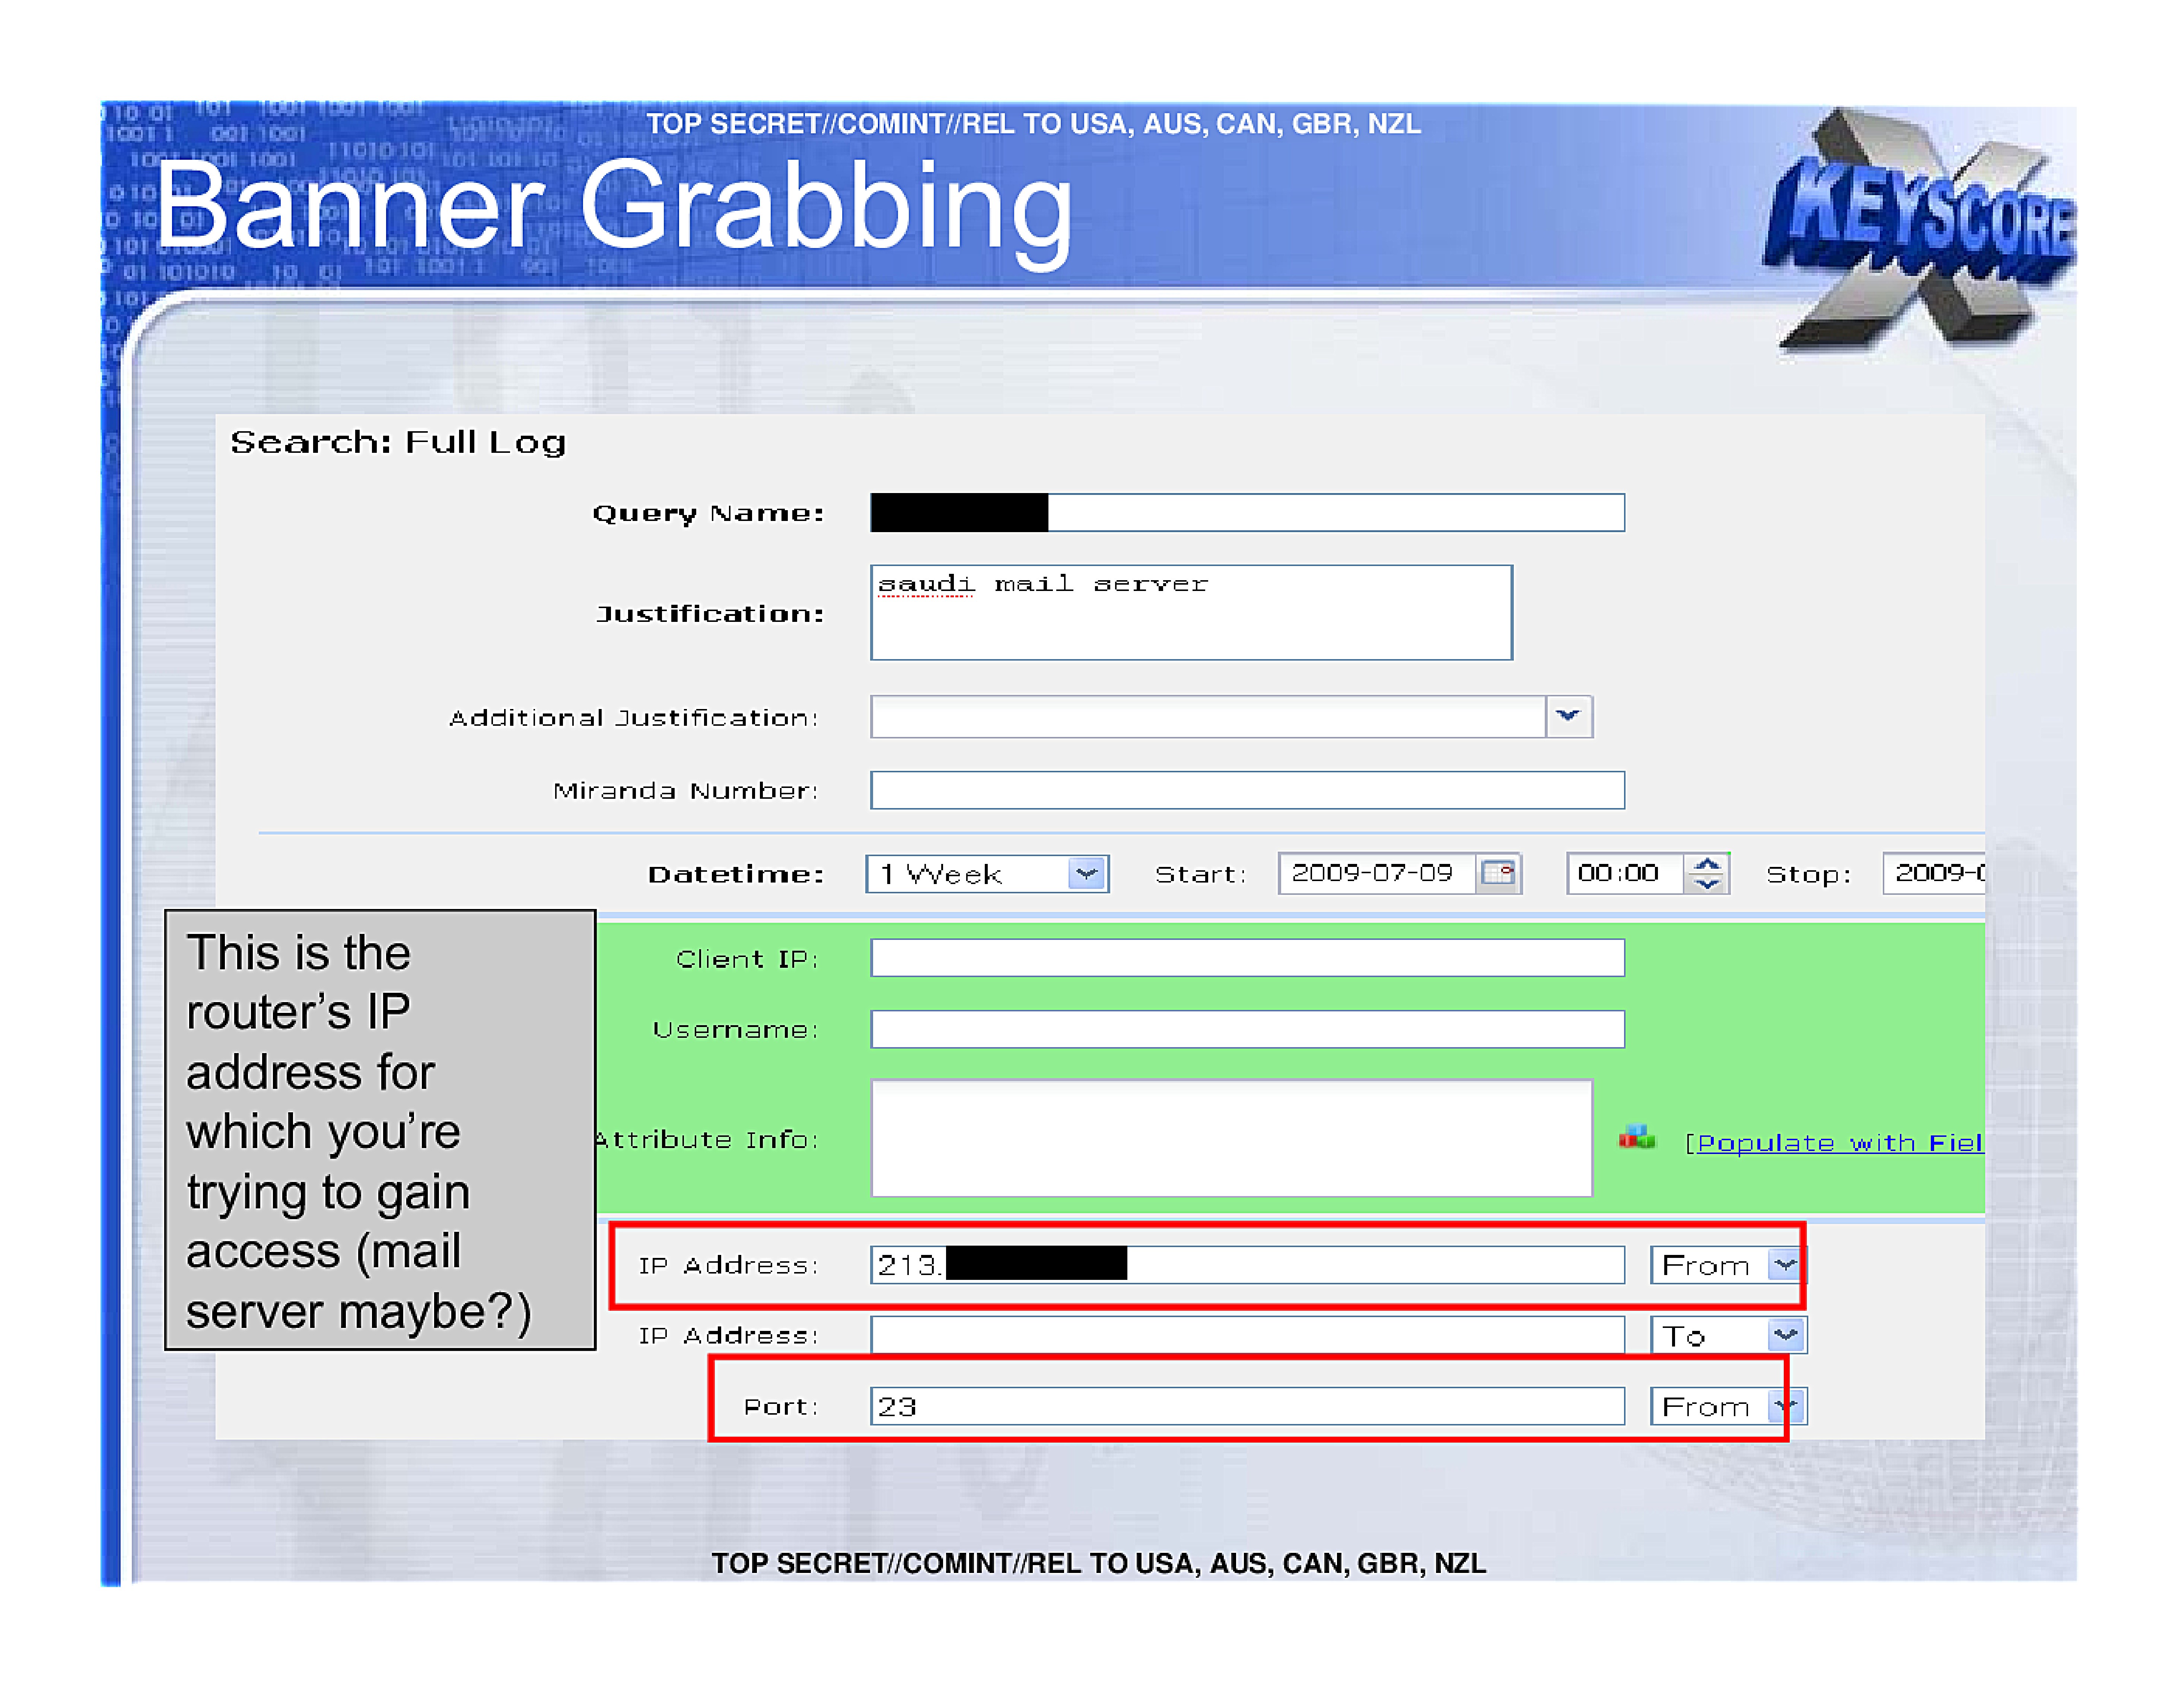
Banner Grabbing
Search: Full Log
Query Name: [REDACTED]
Justification: saudi mail server
Additional Justification:
Miranda Number:

Datetime: 1 Week Start: 2009-07-09 00:00 Stop: 2009-0

This is the
router's IP
address for
which you're
trying to gain
access (mail
server maybe?)

Client IP:
Username:
Attribute Info: [Populate with Fiel
IP Address: 213.[REDACTED] From
IP Address: To
Port: 23 From
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
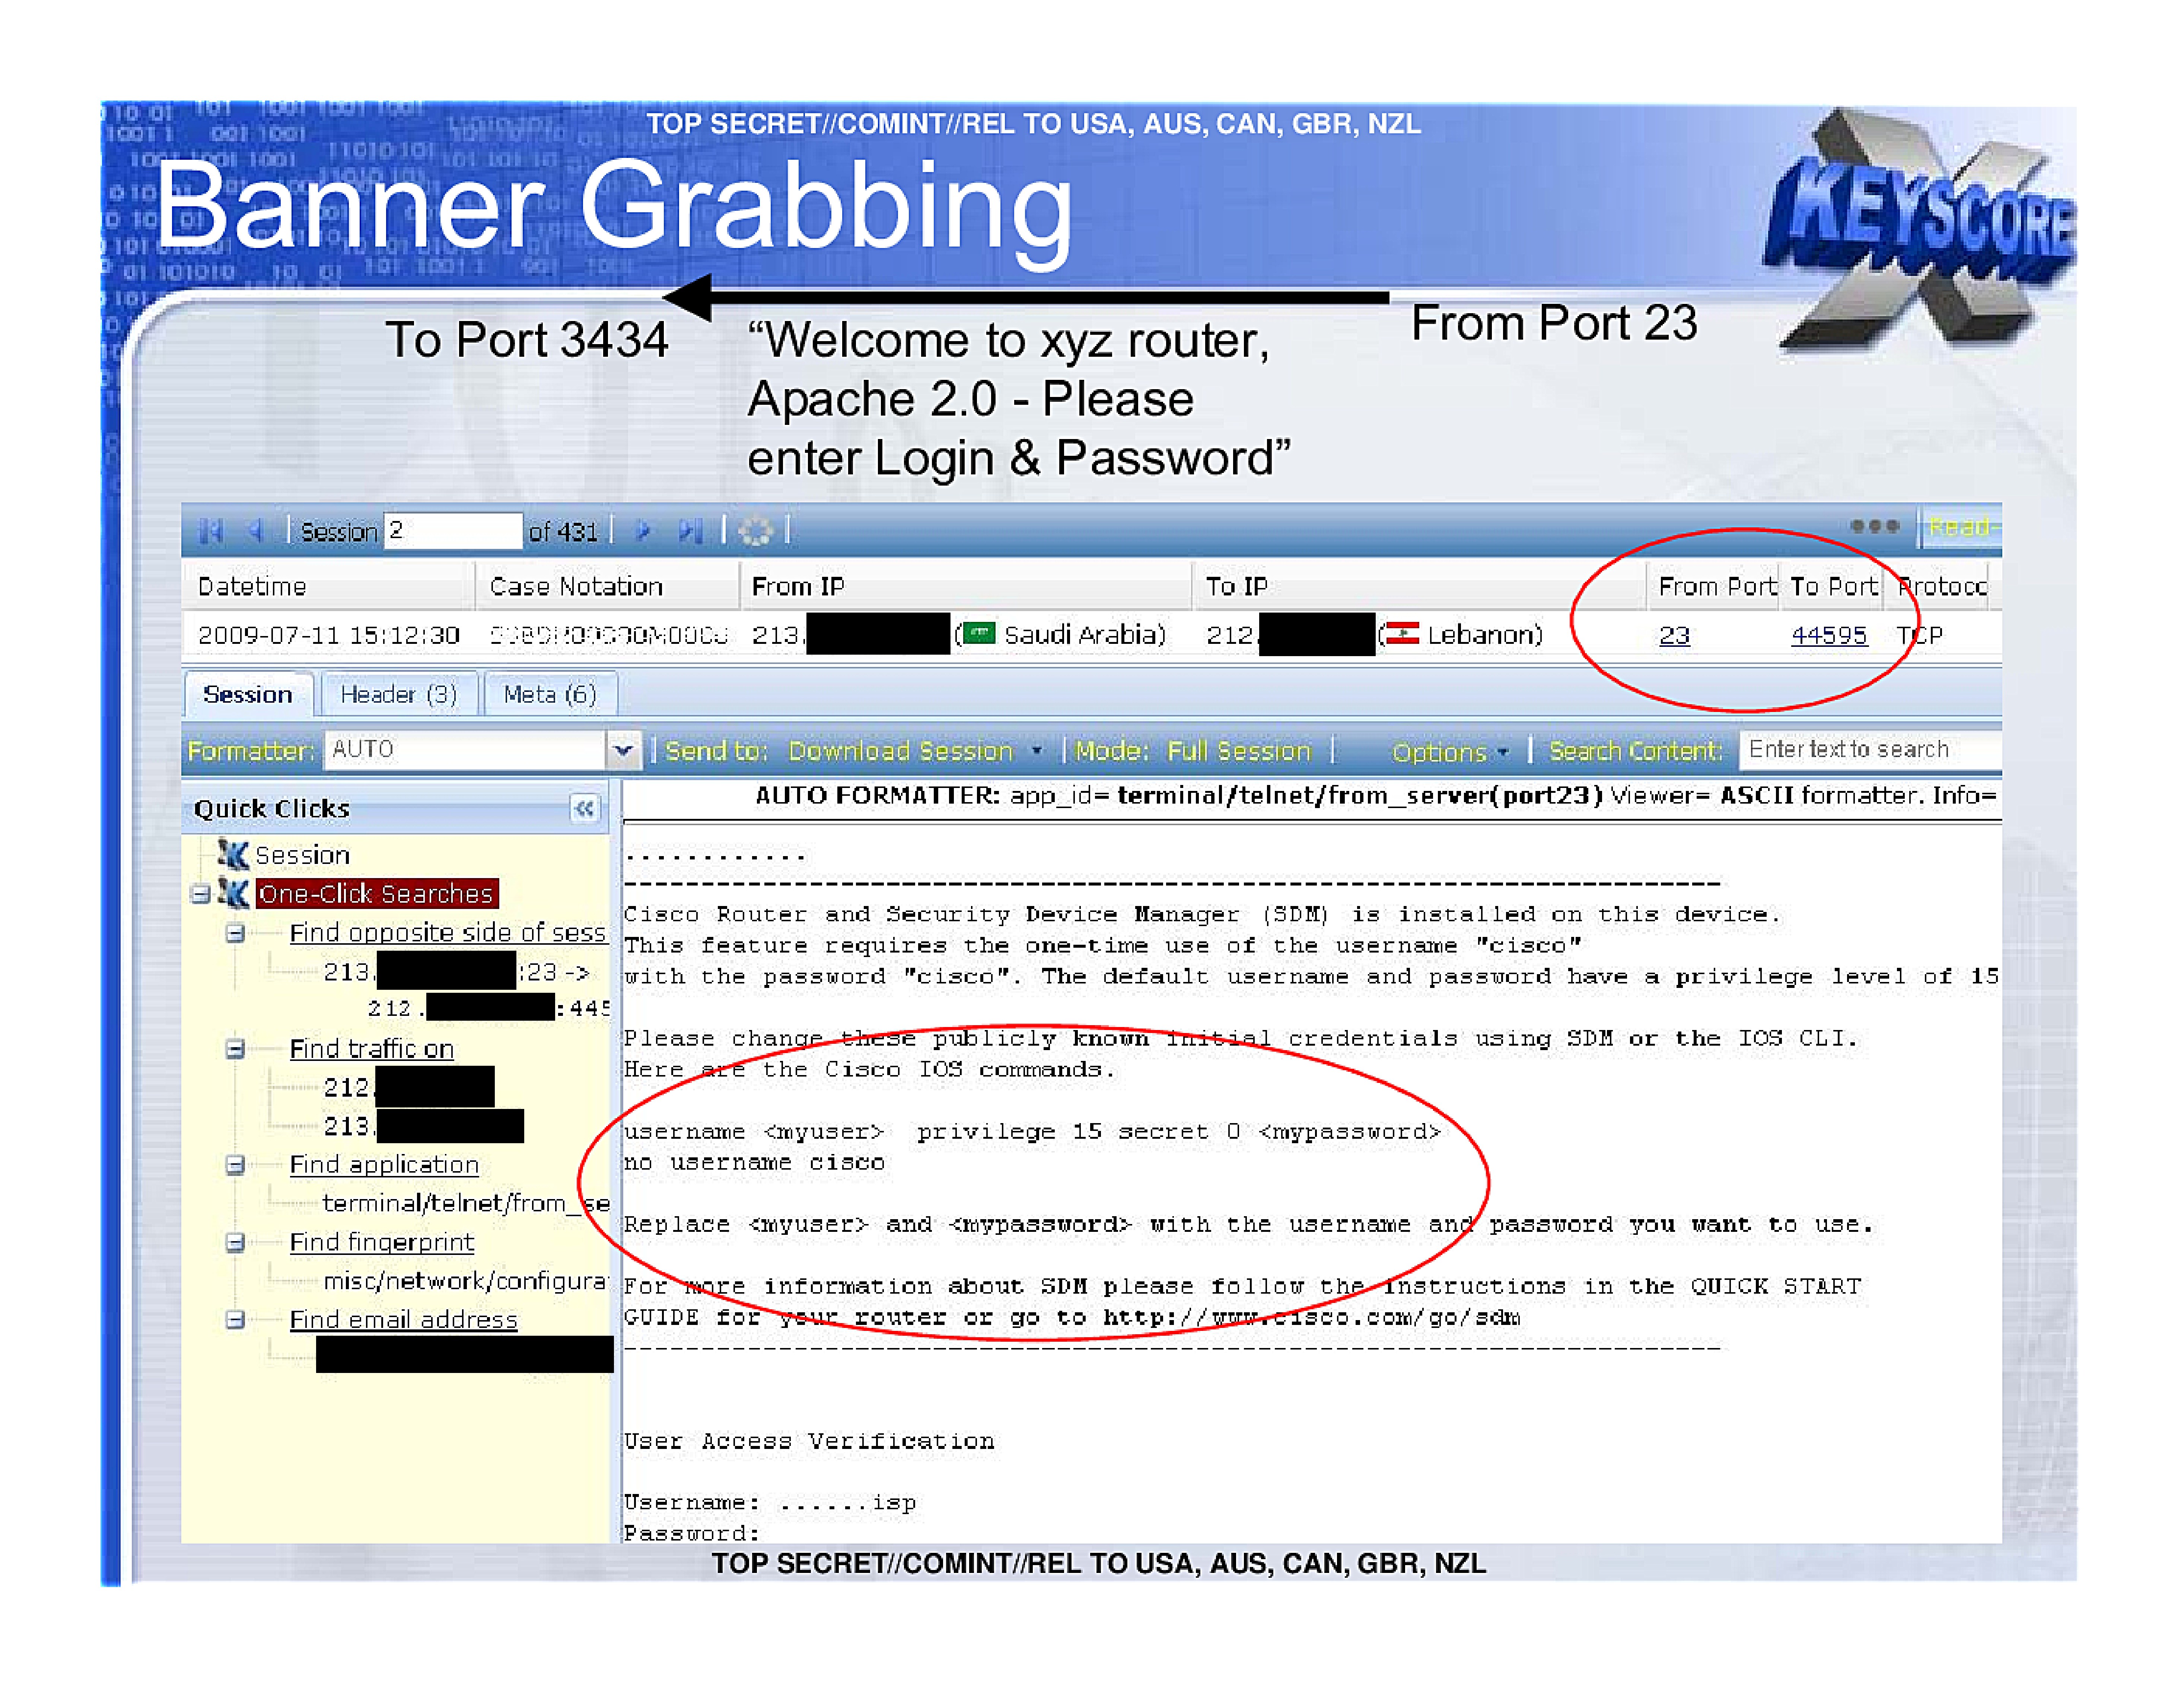
Banner Grabbing
To Port 3434
"Welcome to xyz router,
Apache 2.0 - Please
enter Login & Password"
From Port 23
Session 2 | of 431
Datetime | Case Notation | From IP | To IP | From Port | To Port | Protocol |
2009-07-11 15:12:30 | [REDACTED] | 213.[REDACTED] (Saudi Arabia) | 212.[REDACTED] (Lebanon) | 23 | 44595 | TCP |

Session | Header (3) | Meta (6)

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to search

Quick Clicks
*   Session
*   One-Click Searches
    *   Find opposite side of sess
       * 213.[REDACTED]:23 ->
          * 212.[REDACTED]:445
    *   Find traffic on
       * 212.[REDACTED]
       * 213.[REDACTED]
    *   Find application
       * terminal/telnet/from_se
    *   Find fingerprint
       * misc/network/configura
    *   Find email address
       * [REDACTED]

AUTO FORMATTER: app_id=terminal/telnet/from_server(port23) Viewer= ASCII formatter. Info=
..............
------------------------------------------------------------------------
Cisco Router and Security Device Manager (SDM) is installed on this device.
This feature requires the one-time use of the username "cisco"
with the password "cisco". The default username and password have a privilege level of 15

Please change these publicly known initial credentials using SDM or the IOS CLI.
Here are the Cisco IOS commands.

username <myuser> privilege 15 secret 0 <mypassword>
no username cisco

Replace <myuser> and <mypassword> with the username and password you want to use.
For more information about SDM please follow the instructions in the QUICK START
GUIDE for your router or go to http://www.cisco.com/go/sdm
------------------------------------------------------------------------

User Access Verification
Username: ......isp
Password:
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
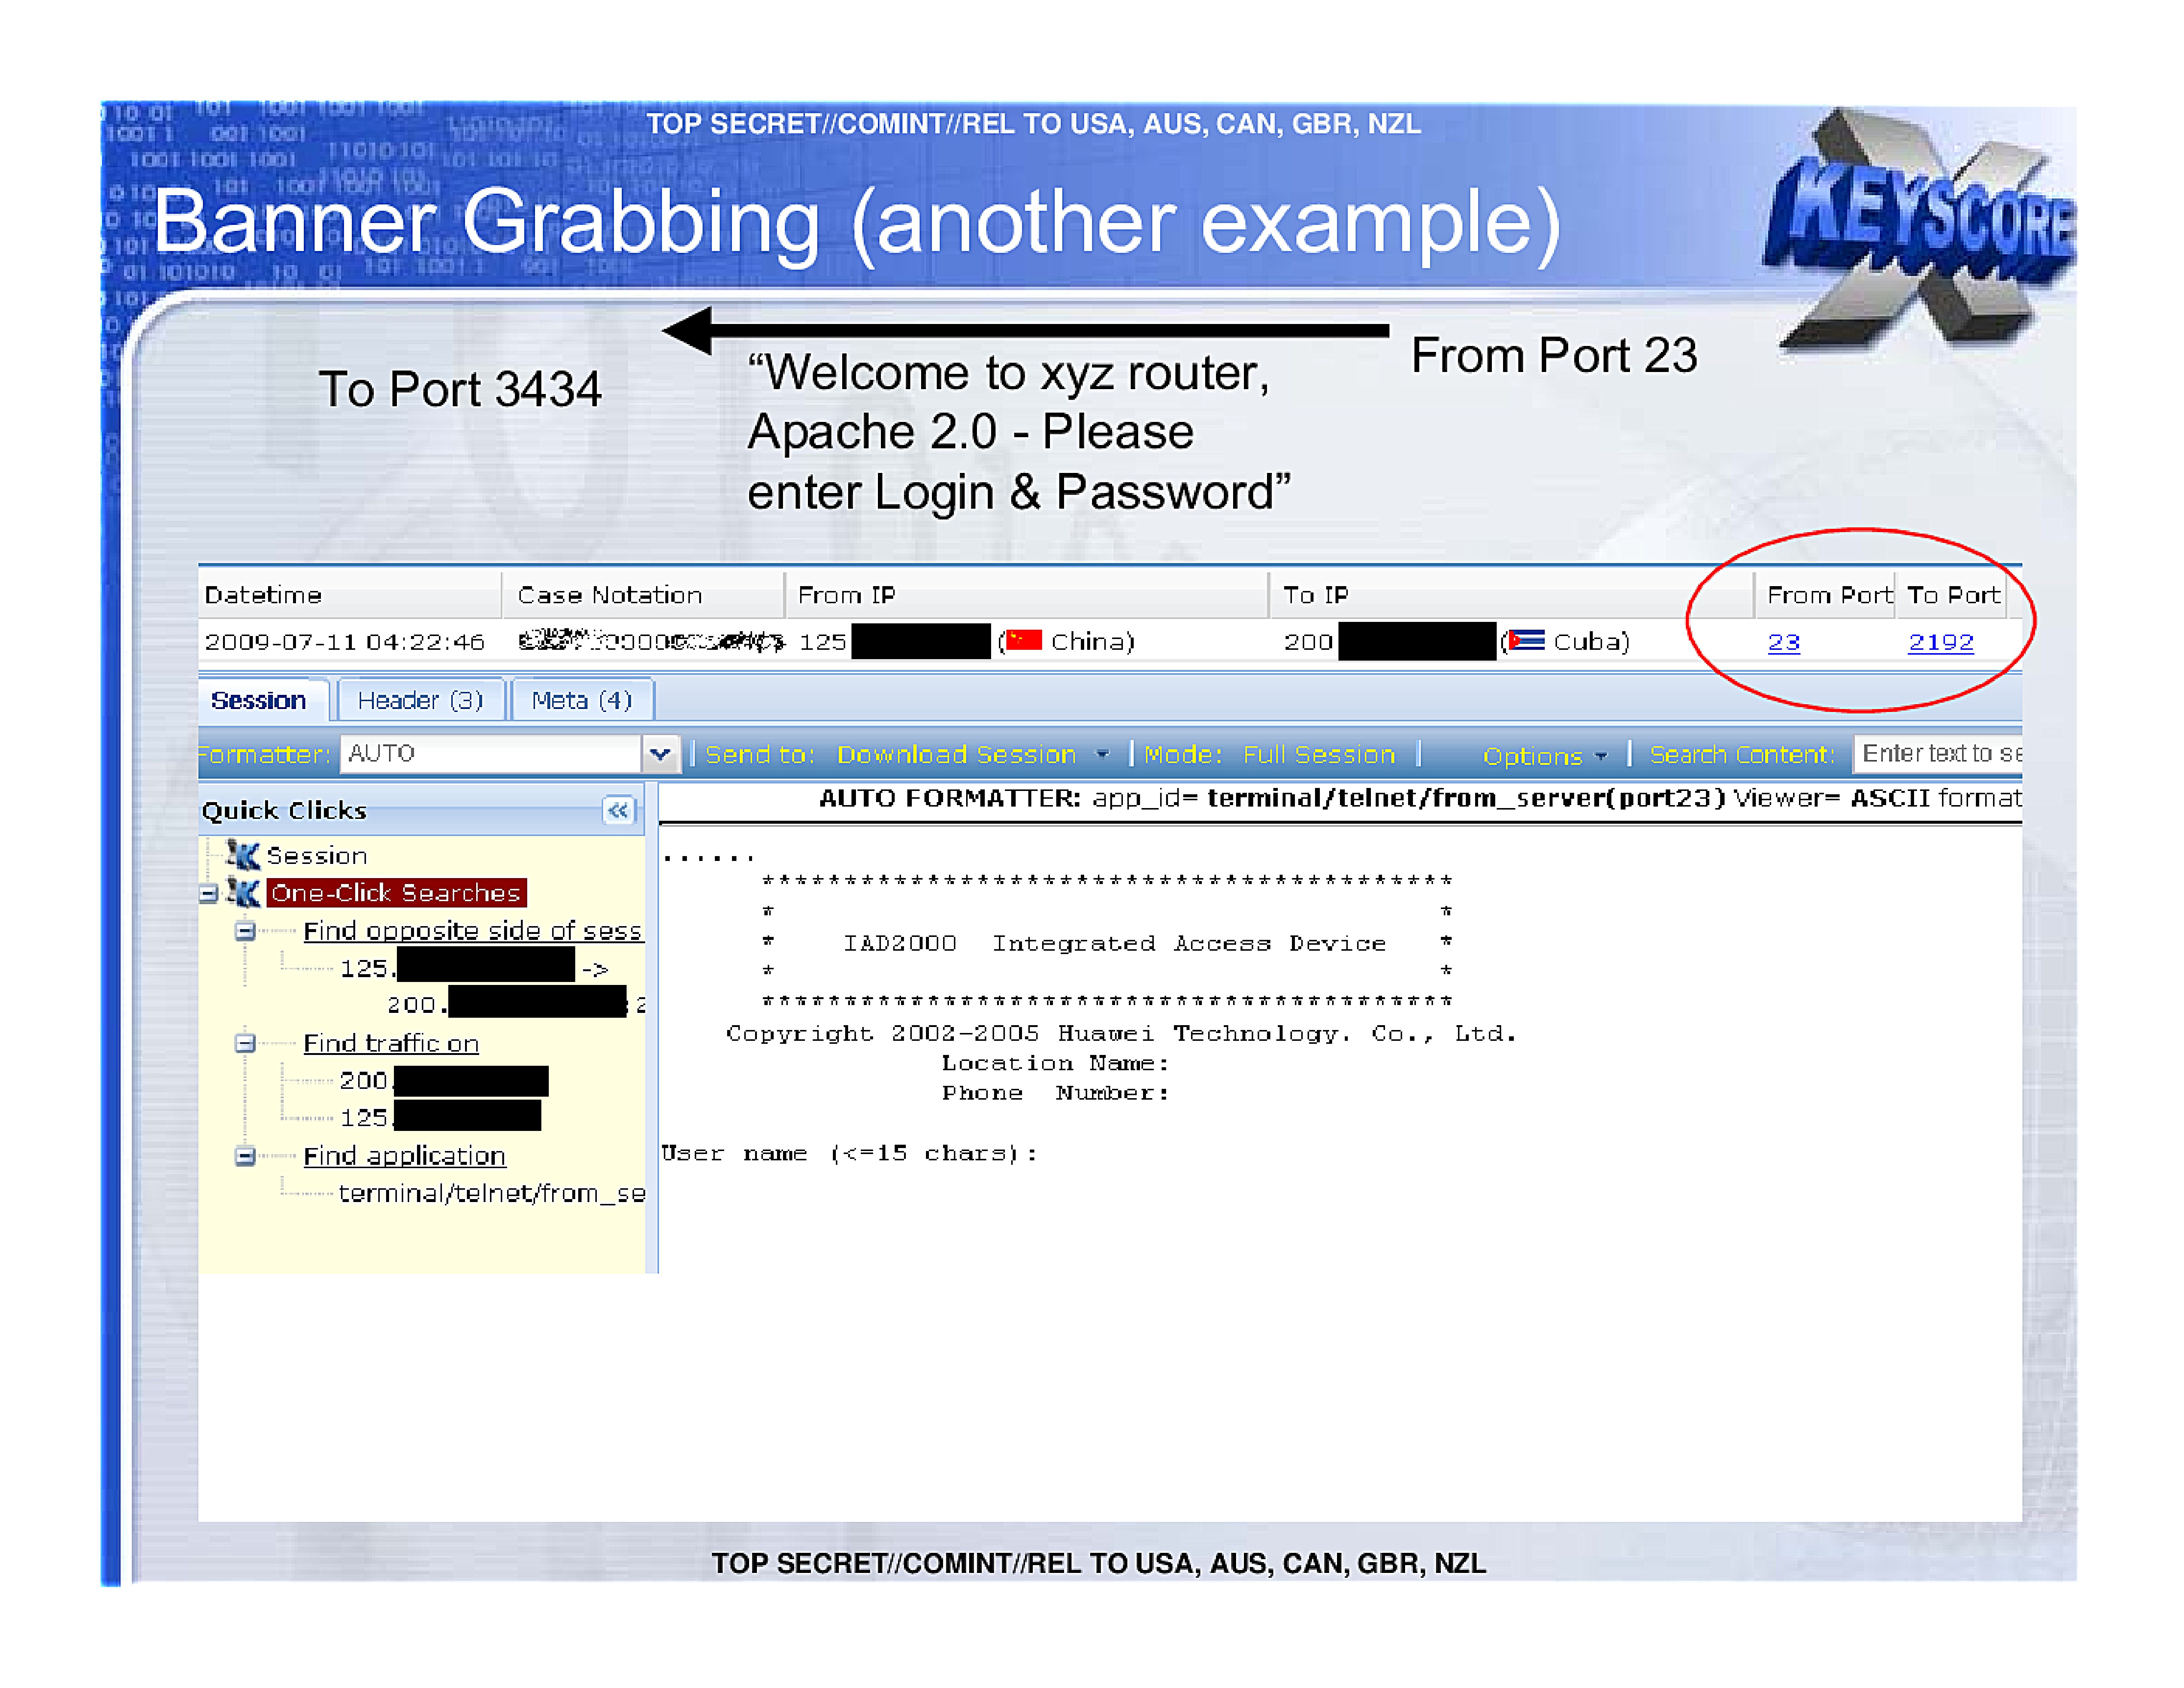
Banner Grabbing (another example)
To Port 3434
"Welcome to xyz router,
Apache 2.0 - Please
enter Login & Password"
From Port 23

Datetime | Case Notation | From IP | To IP | From Port | To Port |
2009-07-11 04:22:46 | [REDACTED]| 125[REDACTED] (China) | 200[REDACTED] (Cuba) | 23 | 2192

Session | Header (3) | Meta (4) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to se

Quick Clicks
*   Session
*   One-Click Searches
    *   Find opposite side of sess
       * 125.[REDACTED] ->
          * 200.[REDACTED]:2
    *   Find traffic on
       * 200.[REDACTED]
       * 125.[REDACTED]
    *   Find application
       * terminal/telnet/from_se

AUTO FORMATTER: app_id= terminal/telnet/from_server(port23) Viewer= ASCII format
.....
    *******************************************
    *                                         *
    *    IAD2000 Integrated Access Device     *
    *                                         *
    *******************************************
  Copyright 2002-2005 Huawei Technology. Co., Ltd.
               Location Name:
               Phone Number:
User name (<=15 chars):
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Banner Grabbing (another example)
| Datetime | Case Notation | From IP | To IP | From Port | To Port | Proto |
2009-07-12 23:59:33 | [REDACTED] | 61.[REDACTED] (China) | 200[REDACTED] (Cuba) | 23 | 2541 |

| Session | Header (3) | Meta (3) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to s

Quick Clicks
*   Session
*   One-Click Searches
    *   Find opposite side of sess
       * 61.[REDACTED]:23 ->
          * 200.[REDACTED]:25
    *   Find traffic on
       * 200.[REDACTED]
       * 61.[REDACTED]
    *   Find application
       * terminal/telnet/from_se

........."...
######################################################################
#          Welcome to ZTE Full Service Access Platform               #
#          Press Return to get started                               #
#          Copyright 2005-2009 , ZTE Co.,Ltd.                        #
######################################################################
Login:
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Banner Grabbing (another example)
Datetime | Case Notation | From IP | To IP | From Port | To Port | TCP |
2009-07-13 19:36:52 | [REDACTED] | 200[REDACTED] (Cuba) | 210[REDACTED] (China) | 23 | 44710 | TCP |

Session | Header (3) | Meta (4) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to search

Quick Clicks
*   Session
*   One-Click Searches
    *   Find opposite side of sess
       * 200[REDACTED]:23 ->
          * 210.[REDACTED]:44
    *   Find fingerprint
       * sigdev/huawei
       * misc/network/configura
    *   Find traffic on
       * 210.[REDACTED]
       * 200.[REDACTED]
    *   Find application
       * terminal/telnet/from_se

AUTO FORMATTER: app_id= terminal/telnet/from_server(port23) Viewer= ASCII formatter. I

...........
*********************************************************************************
*   Copyright (c) 1998-2006 Huawei Technologies Co., Ltd. All rights reserved.  *
*   Without the owner's prior written consent,                                  *
*   no decompiling or reverse-engineering shall be allowed.                     *
*********************************************************************************
Login authentication

Username:............'.......
Username:
Username:
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
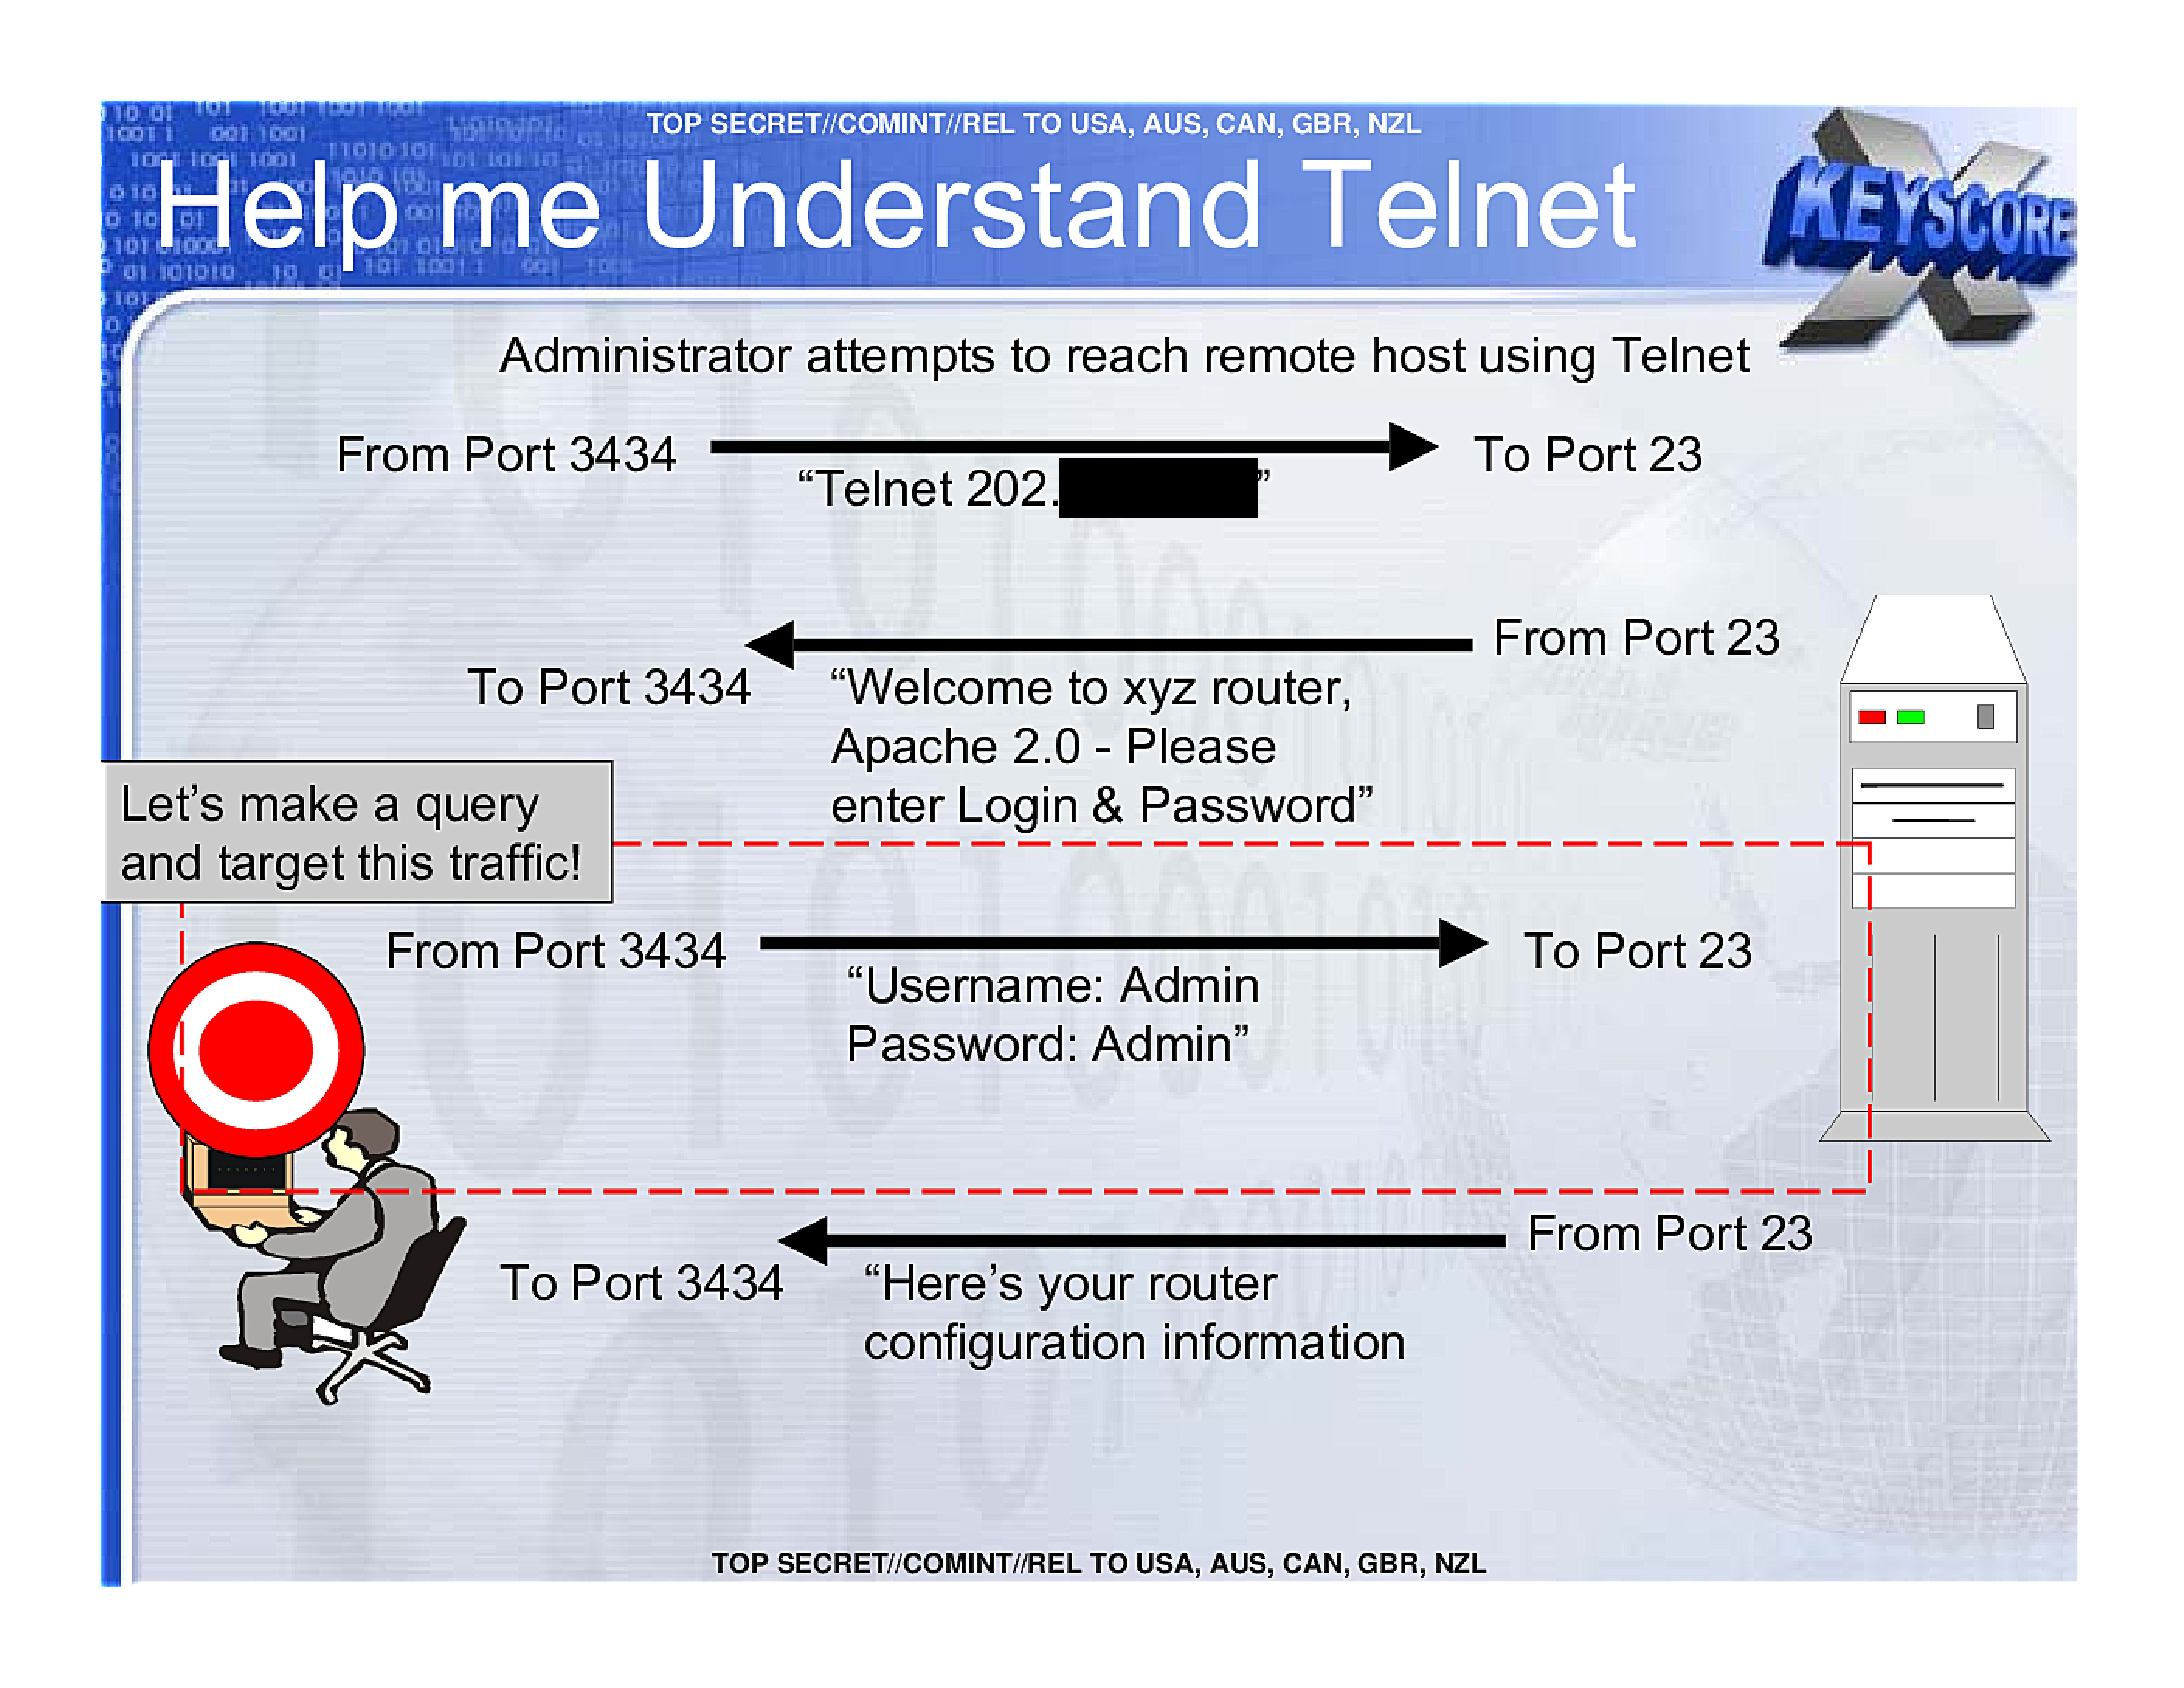
Help me Understand Telnet
Administrator attempts to reach remote host using Telnet
From Port 3434
"Telnet 202.[REDACTED]
To Port 23
From Port 23
To Port 3434
"Welcome to xyz router,
Apache 2.0 - Please
enter Login & Password"
From Port 3434
To Port 23
"Username: Admin
Password: Admin"
Let's make a query
and target this traffic!
To Port 3434
From Port 23
"Here's your router
configuration information
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
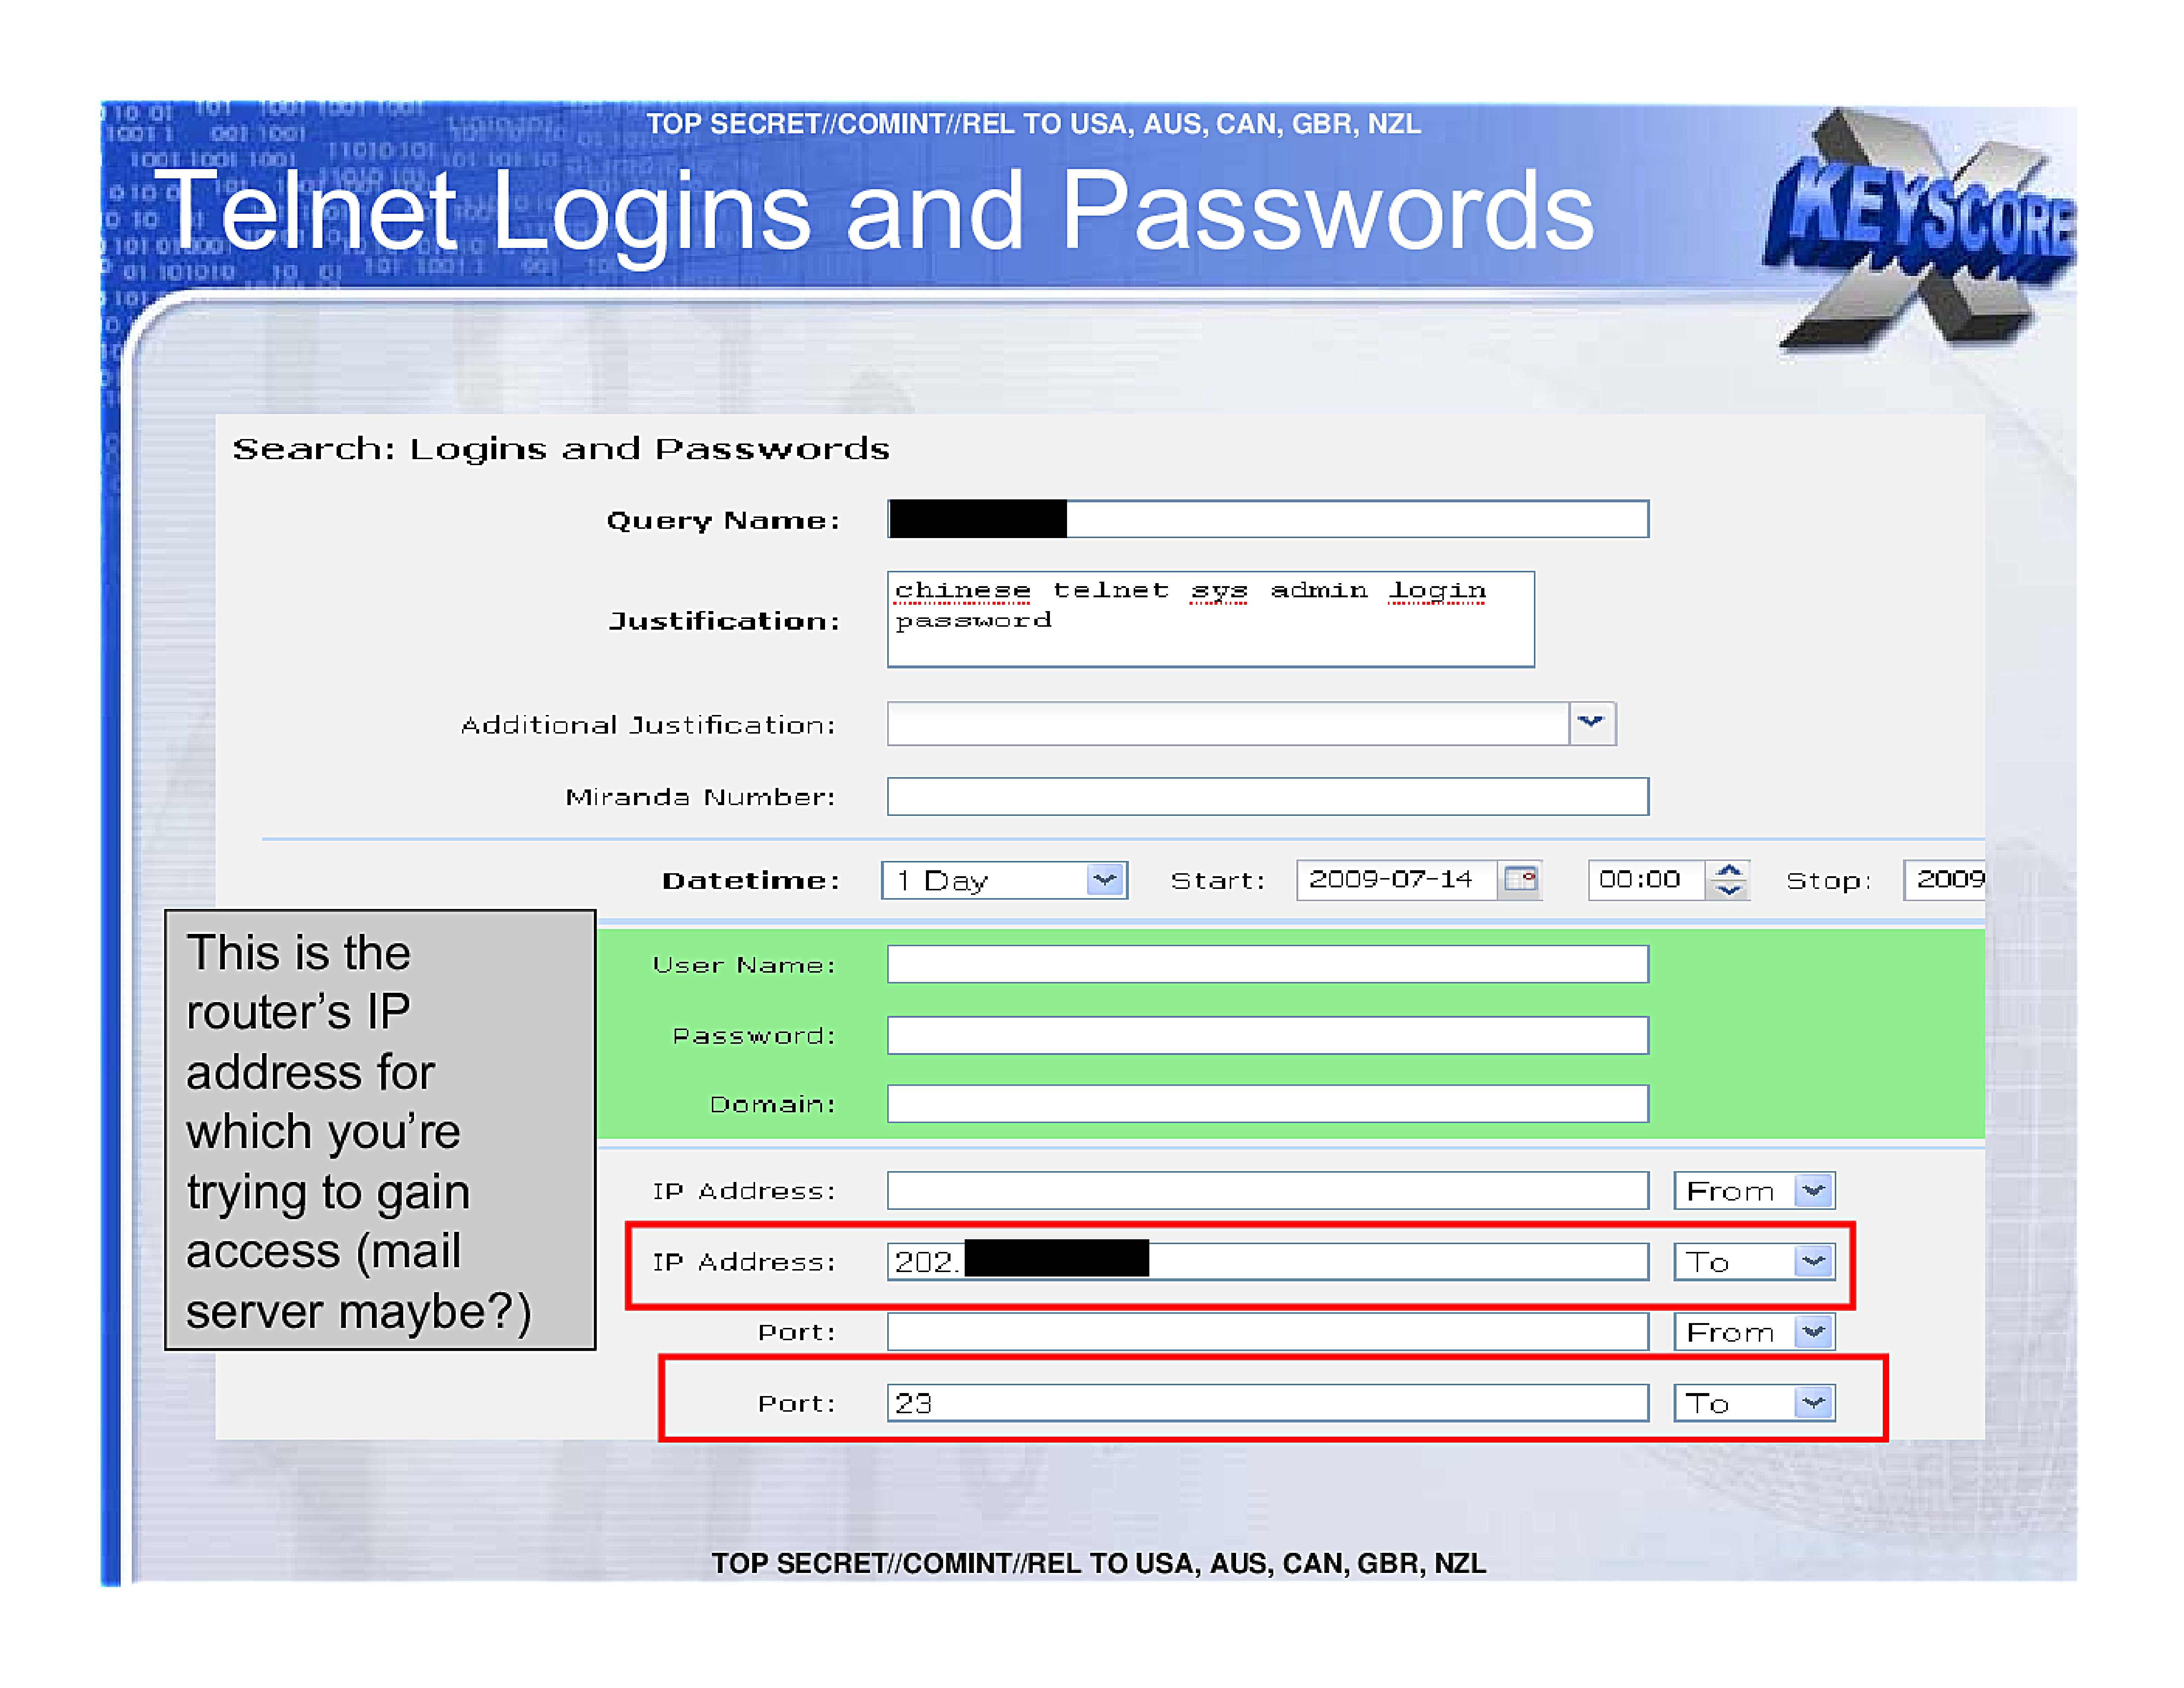
Telnet Logins and Passwords
Search: Logins and Passwords
Query Name: [REDACTED]
Justification: chinese telnet sys admin login password
Additional Justification:
Miranda Number:

Datetime: 1 Day Start: 2009-07-14 00:00 Stop: 2009

This is the
router's IP
address for
which you're
trying to gain
access (mail
server maybe?)

User Name:
Password:
Domain:

IP Address: From
IP Address: 202.[REDACTED] To
Port: From
Port: 23 To
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
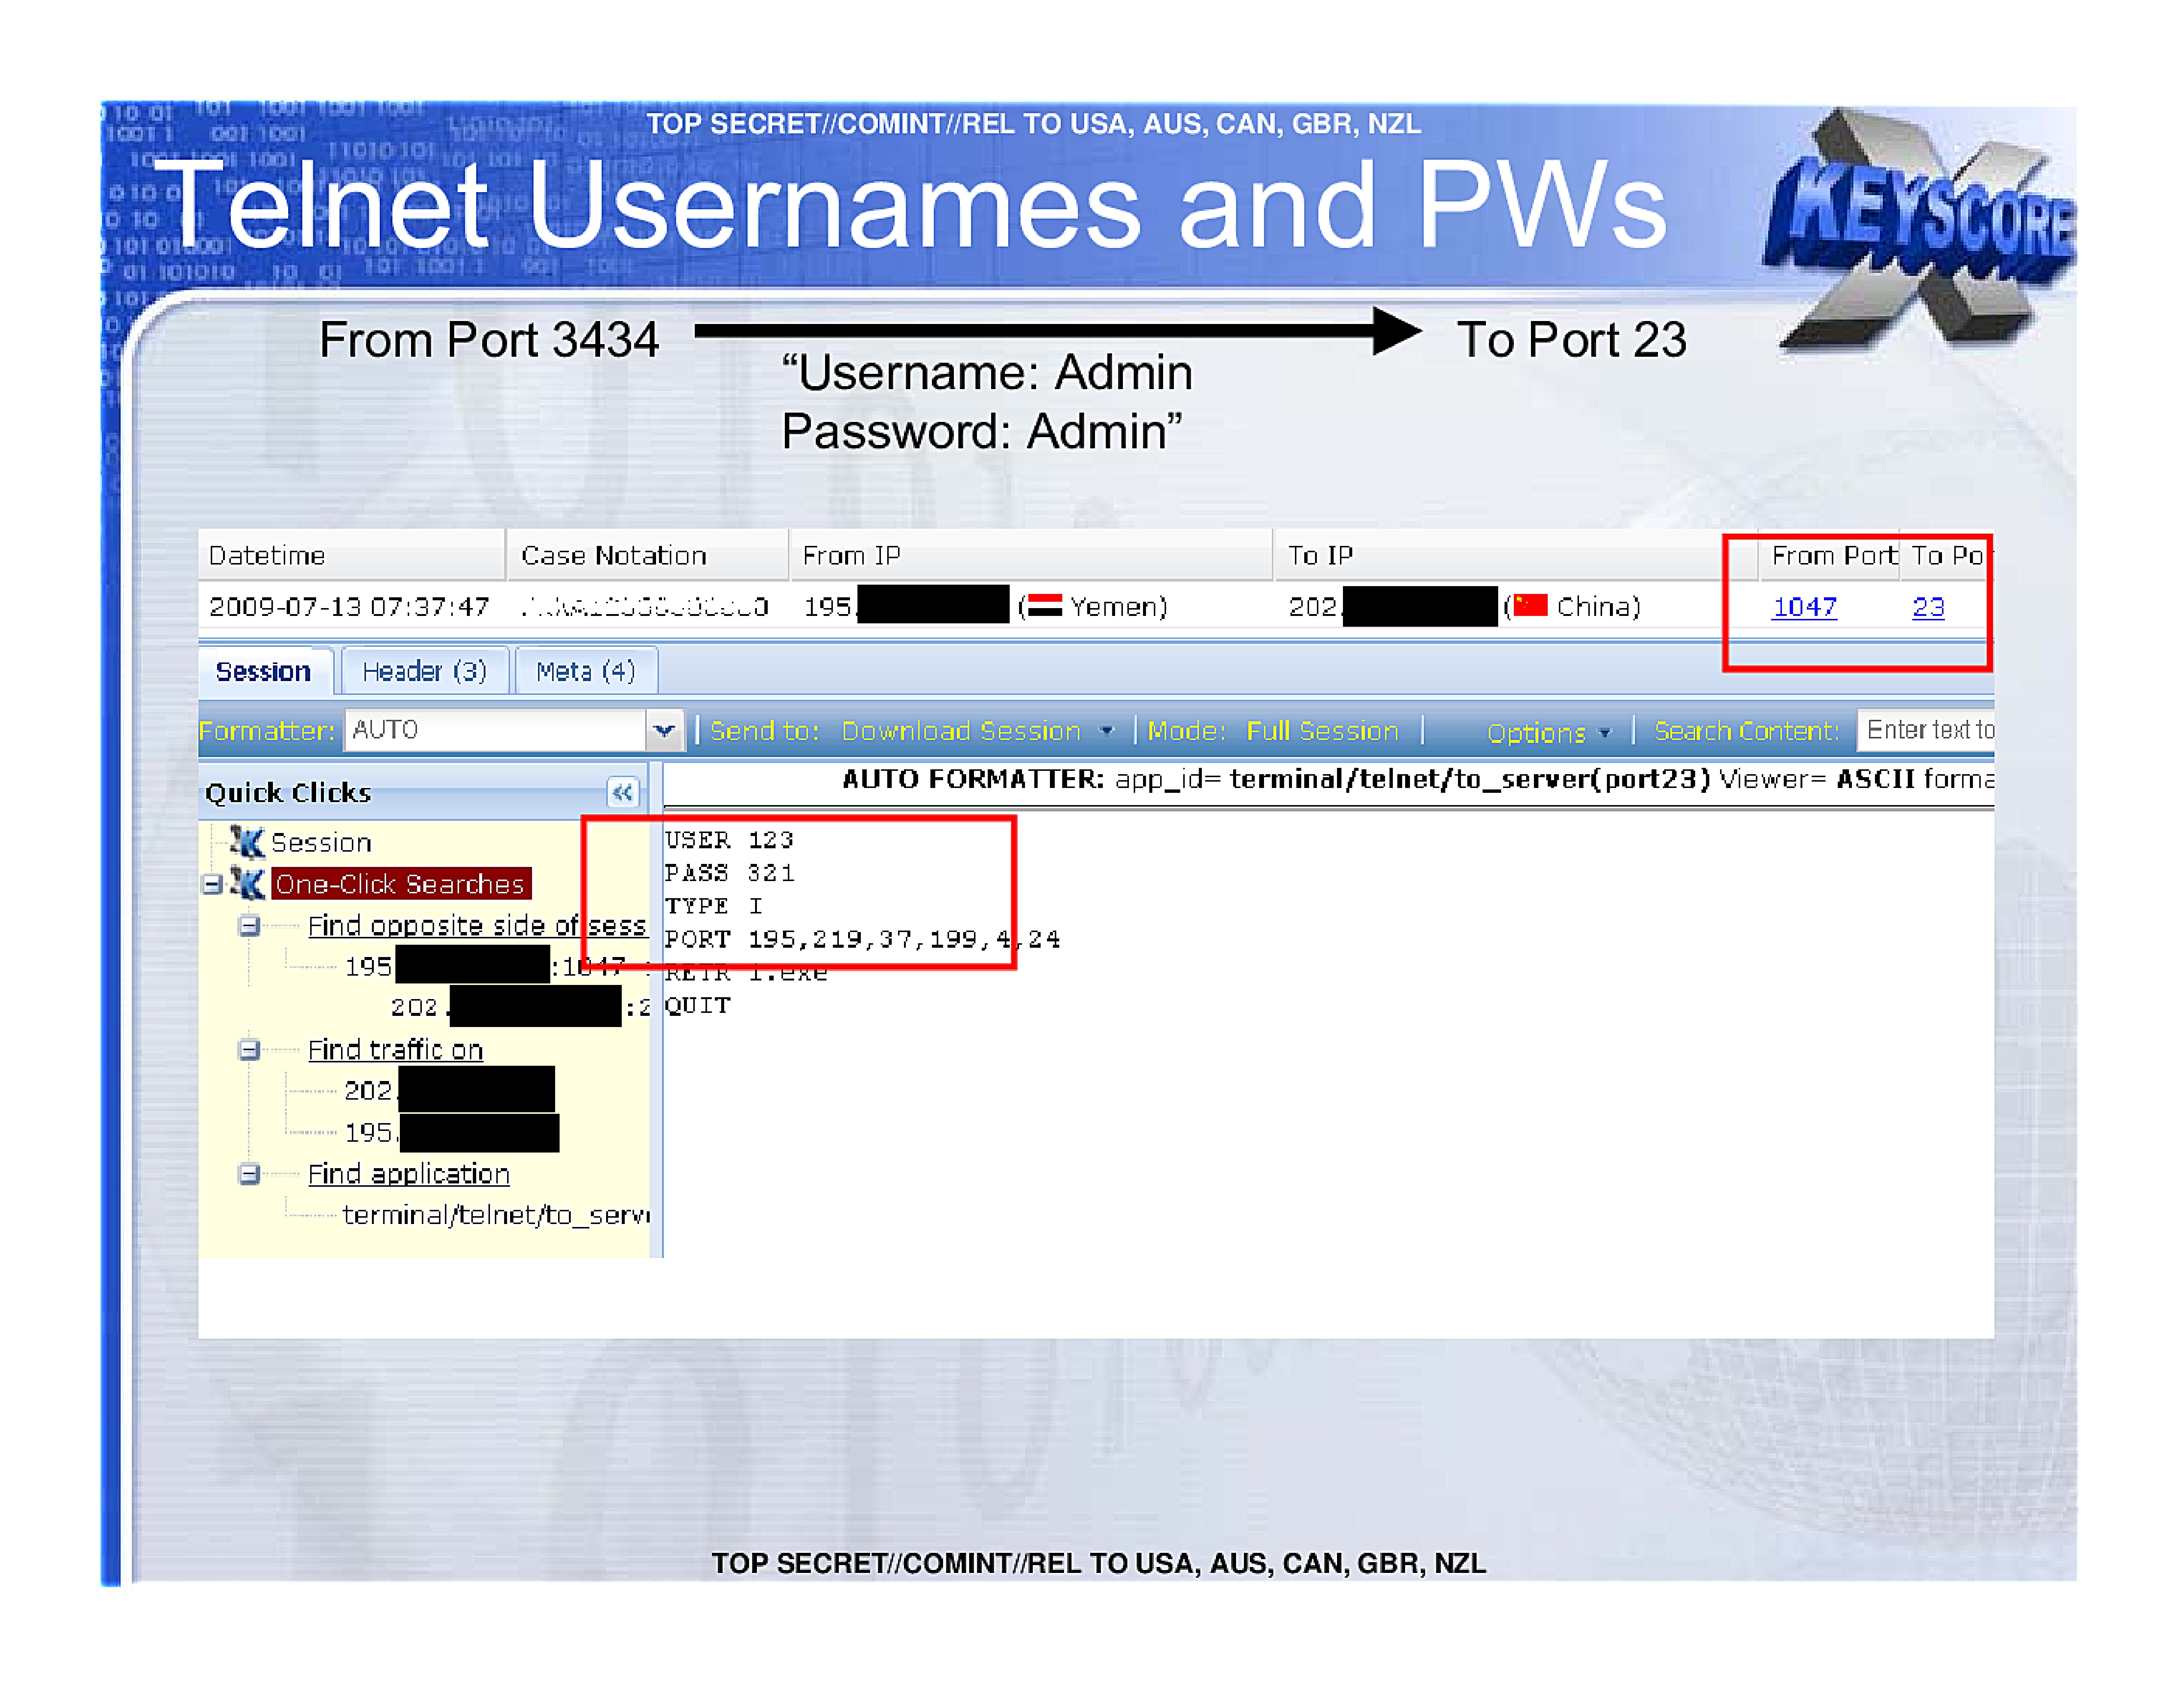
Telnet Usernames and PWs
From Port 3434
"Username: Admin
Password: Admin"
To Port 23
Datetime | Case Notation | From IP | To IP | From Port | To Po |
2009-07-13 07:37:47 | [REDACTED] | 195.[REDACTED] (Yemen) | 202.[REDACTED] (China) | 1047 | 23 |

| Session | Header (3) | Meta (4) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to


Quick Clicks
*   Session
*   One-Click Searches
    *   Find opposite side of sess
       * 195.[REDACTED]:1047
          * 202.[REDACTED]:2
    *   Find traffic on
       * 202.[REDACTED]
       * 195.[REDACTED]
    *   Find application
       * terminal/telnet/to_serv

AUTO FORMATTER: app_id= terminal/telnet/to_server(port23) Viewer= ASCII forma
USER 123
PASS 321
TYPE I
PORT 195,219,37,199,4,24
RETR 1.exe
QUIT
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Help me Understand Telnet
Administrator attempts to reach remote host using Telnet
From Port 3434
"Telnet 202.[REDACTED]"
To Port 23
From Port 23
To Port 3434
"Welcome to xyz router,
Apache 2.0 - Please
enter Login & Password"
From Port 3434
To Port 23
"Username: Admin
Password: Admin"
Let's make a query
and target this traffic!
To Port 3434
From Port 23
"Here's your router
configuration information
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
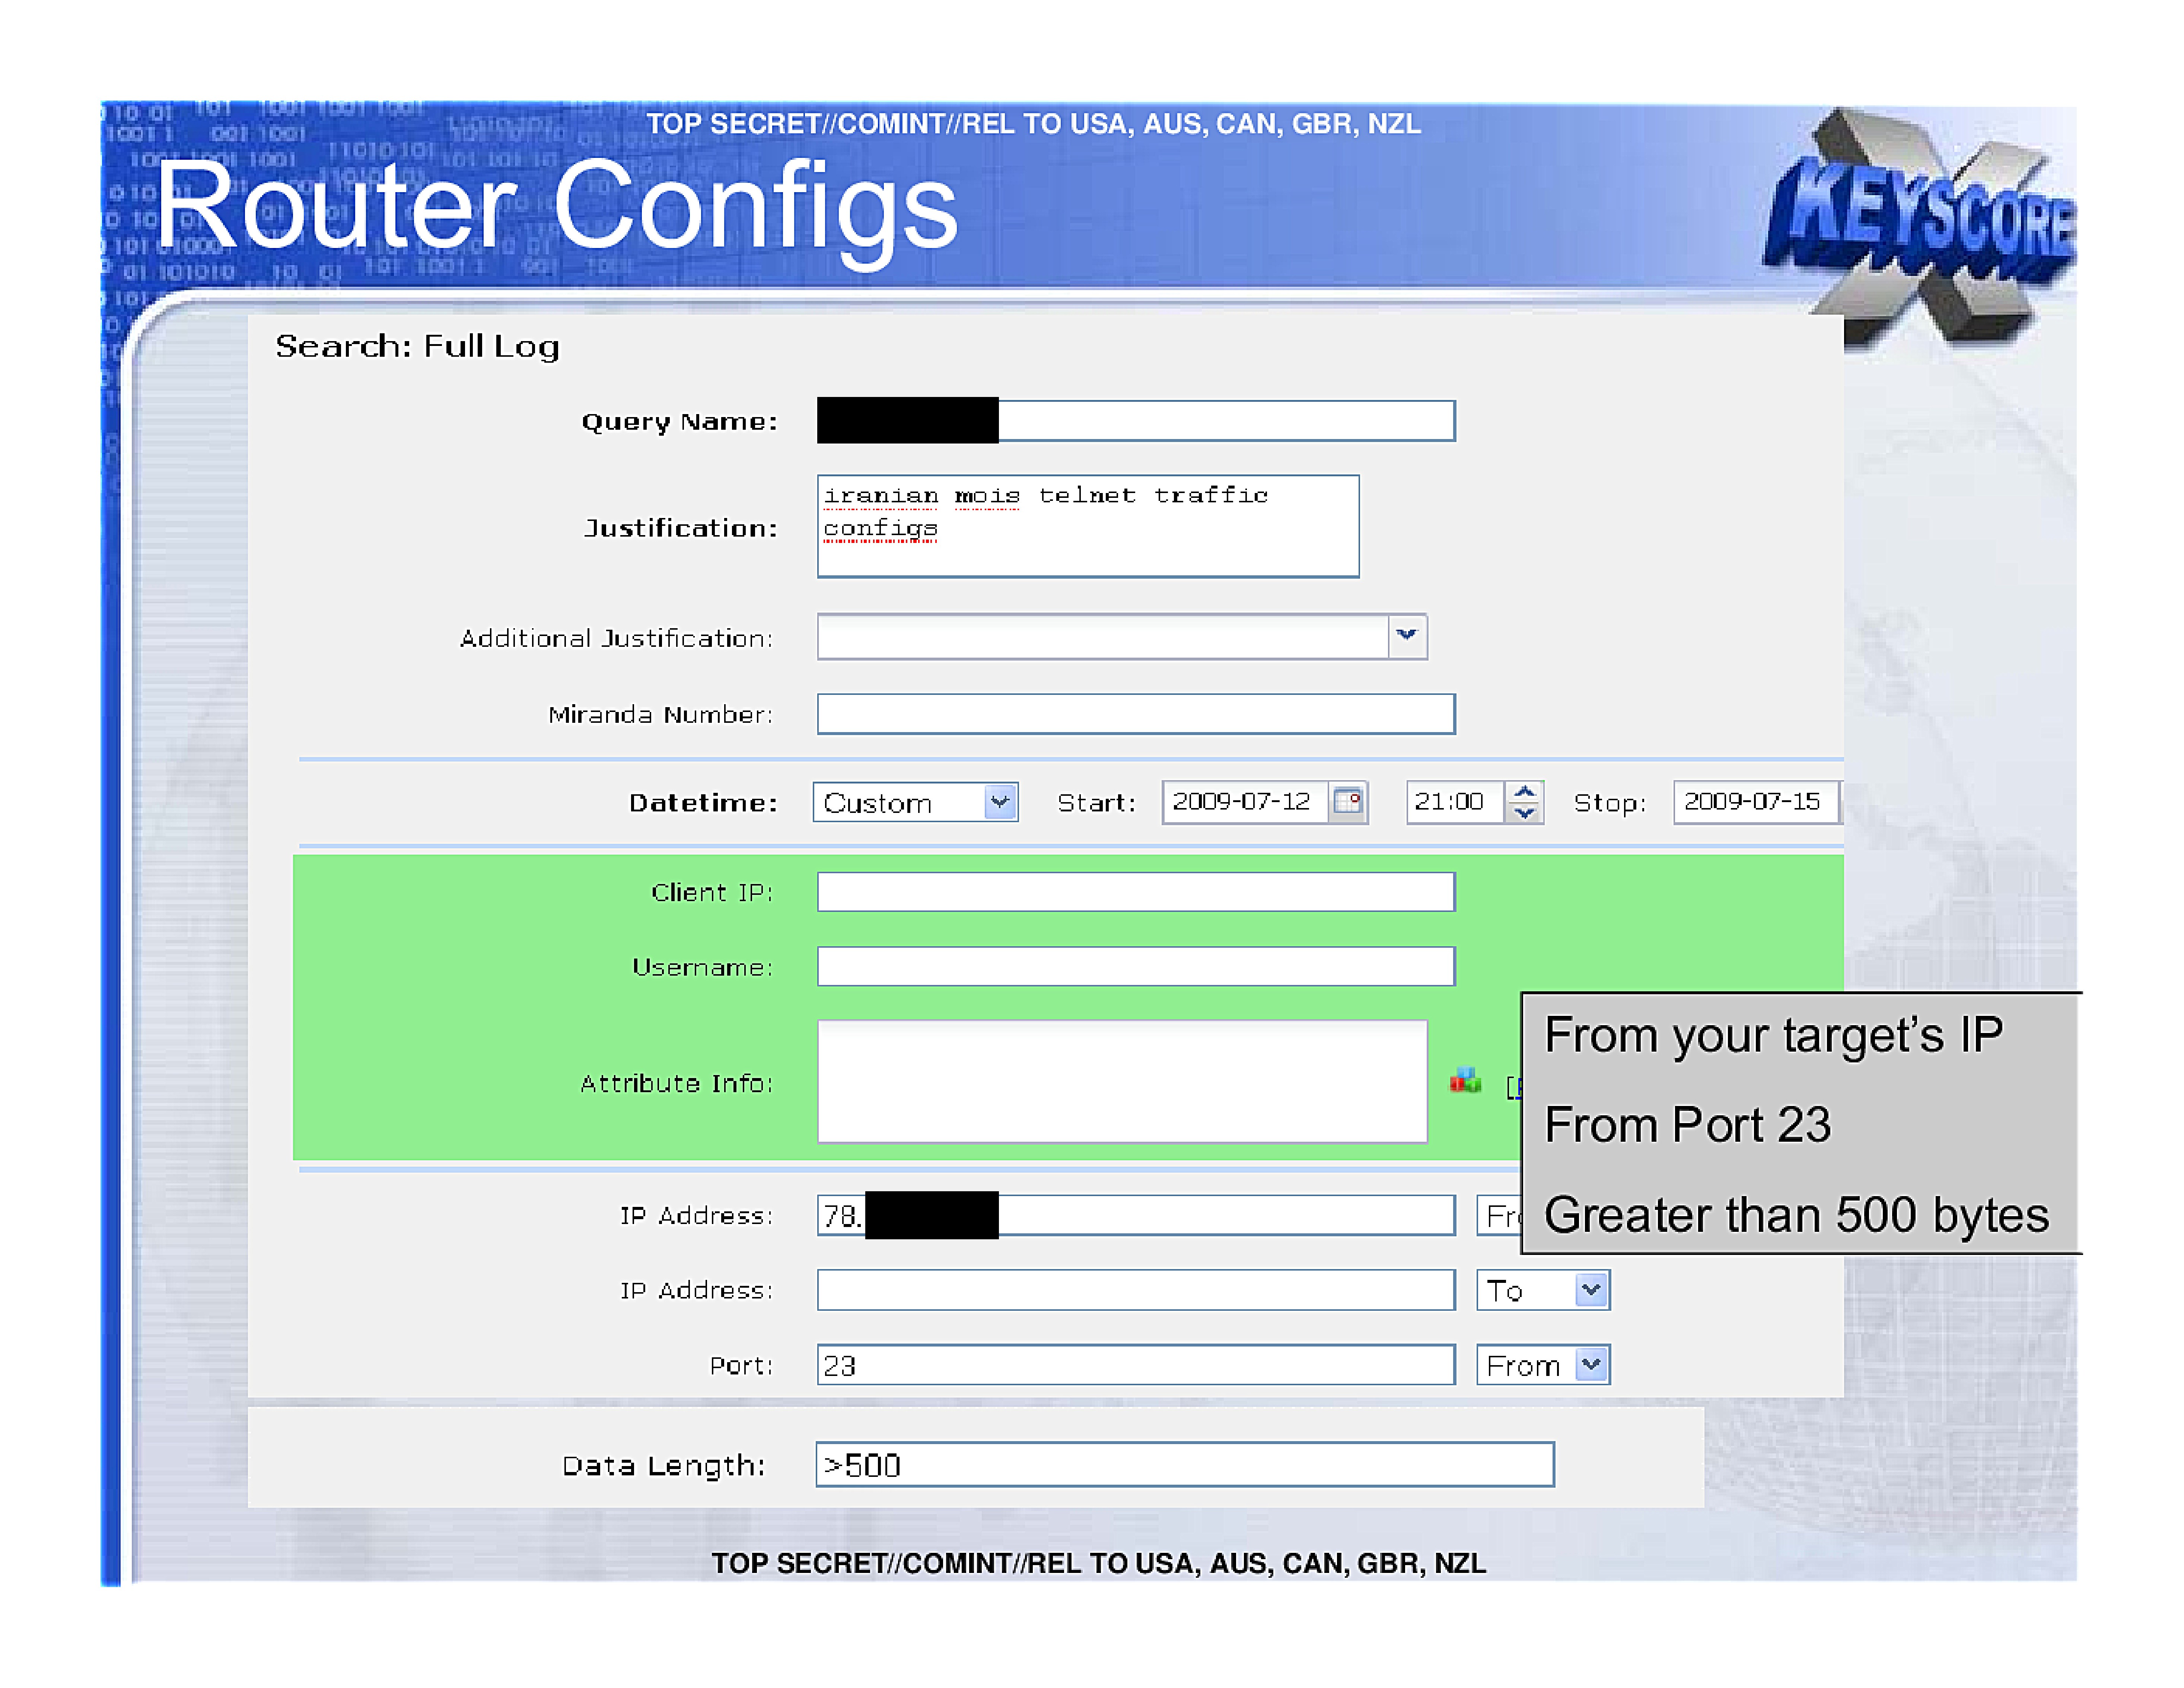
Router Configs
Search: Full Log
Query Name: [REDACTED]
Justification: iranian mois telnet traffic configs
Additional Justification:
Miranda Number:

Datetime: Custom Start: 2009-07-12 21:00 Stop: 2009-07-15

Client IP:
Username:
Attribute Info:

IP Address: 78.[REDACTED] Fr
IP Address: To
Port: 23 From
Data Length: >500

From your target's IP
From Port 23
Greater than 500 bytes
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
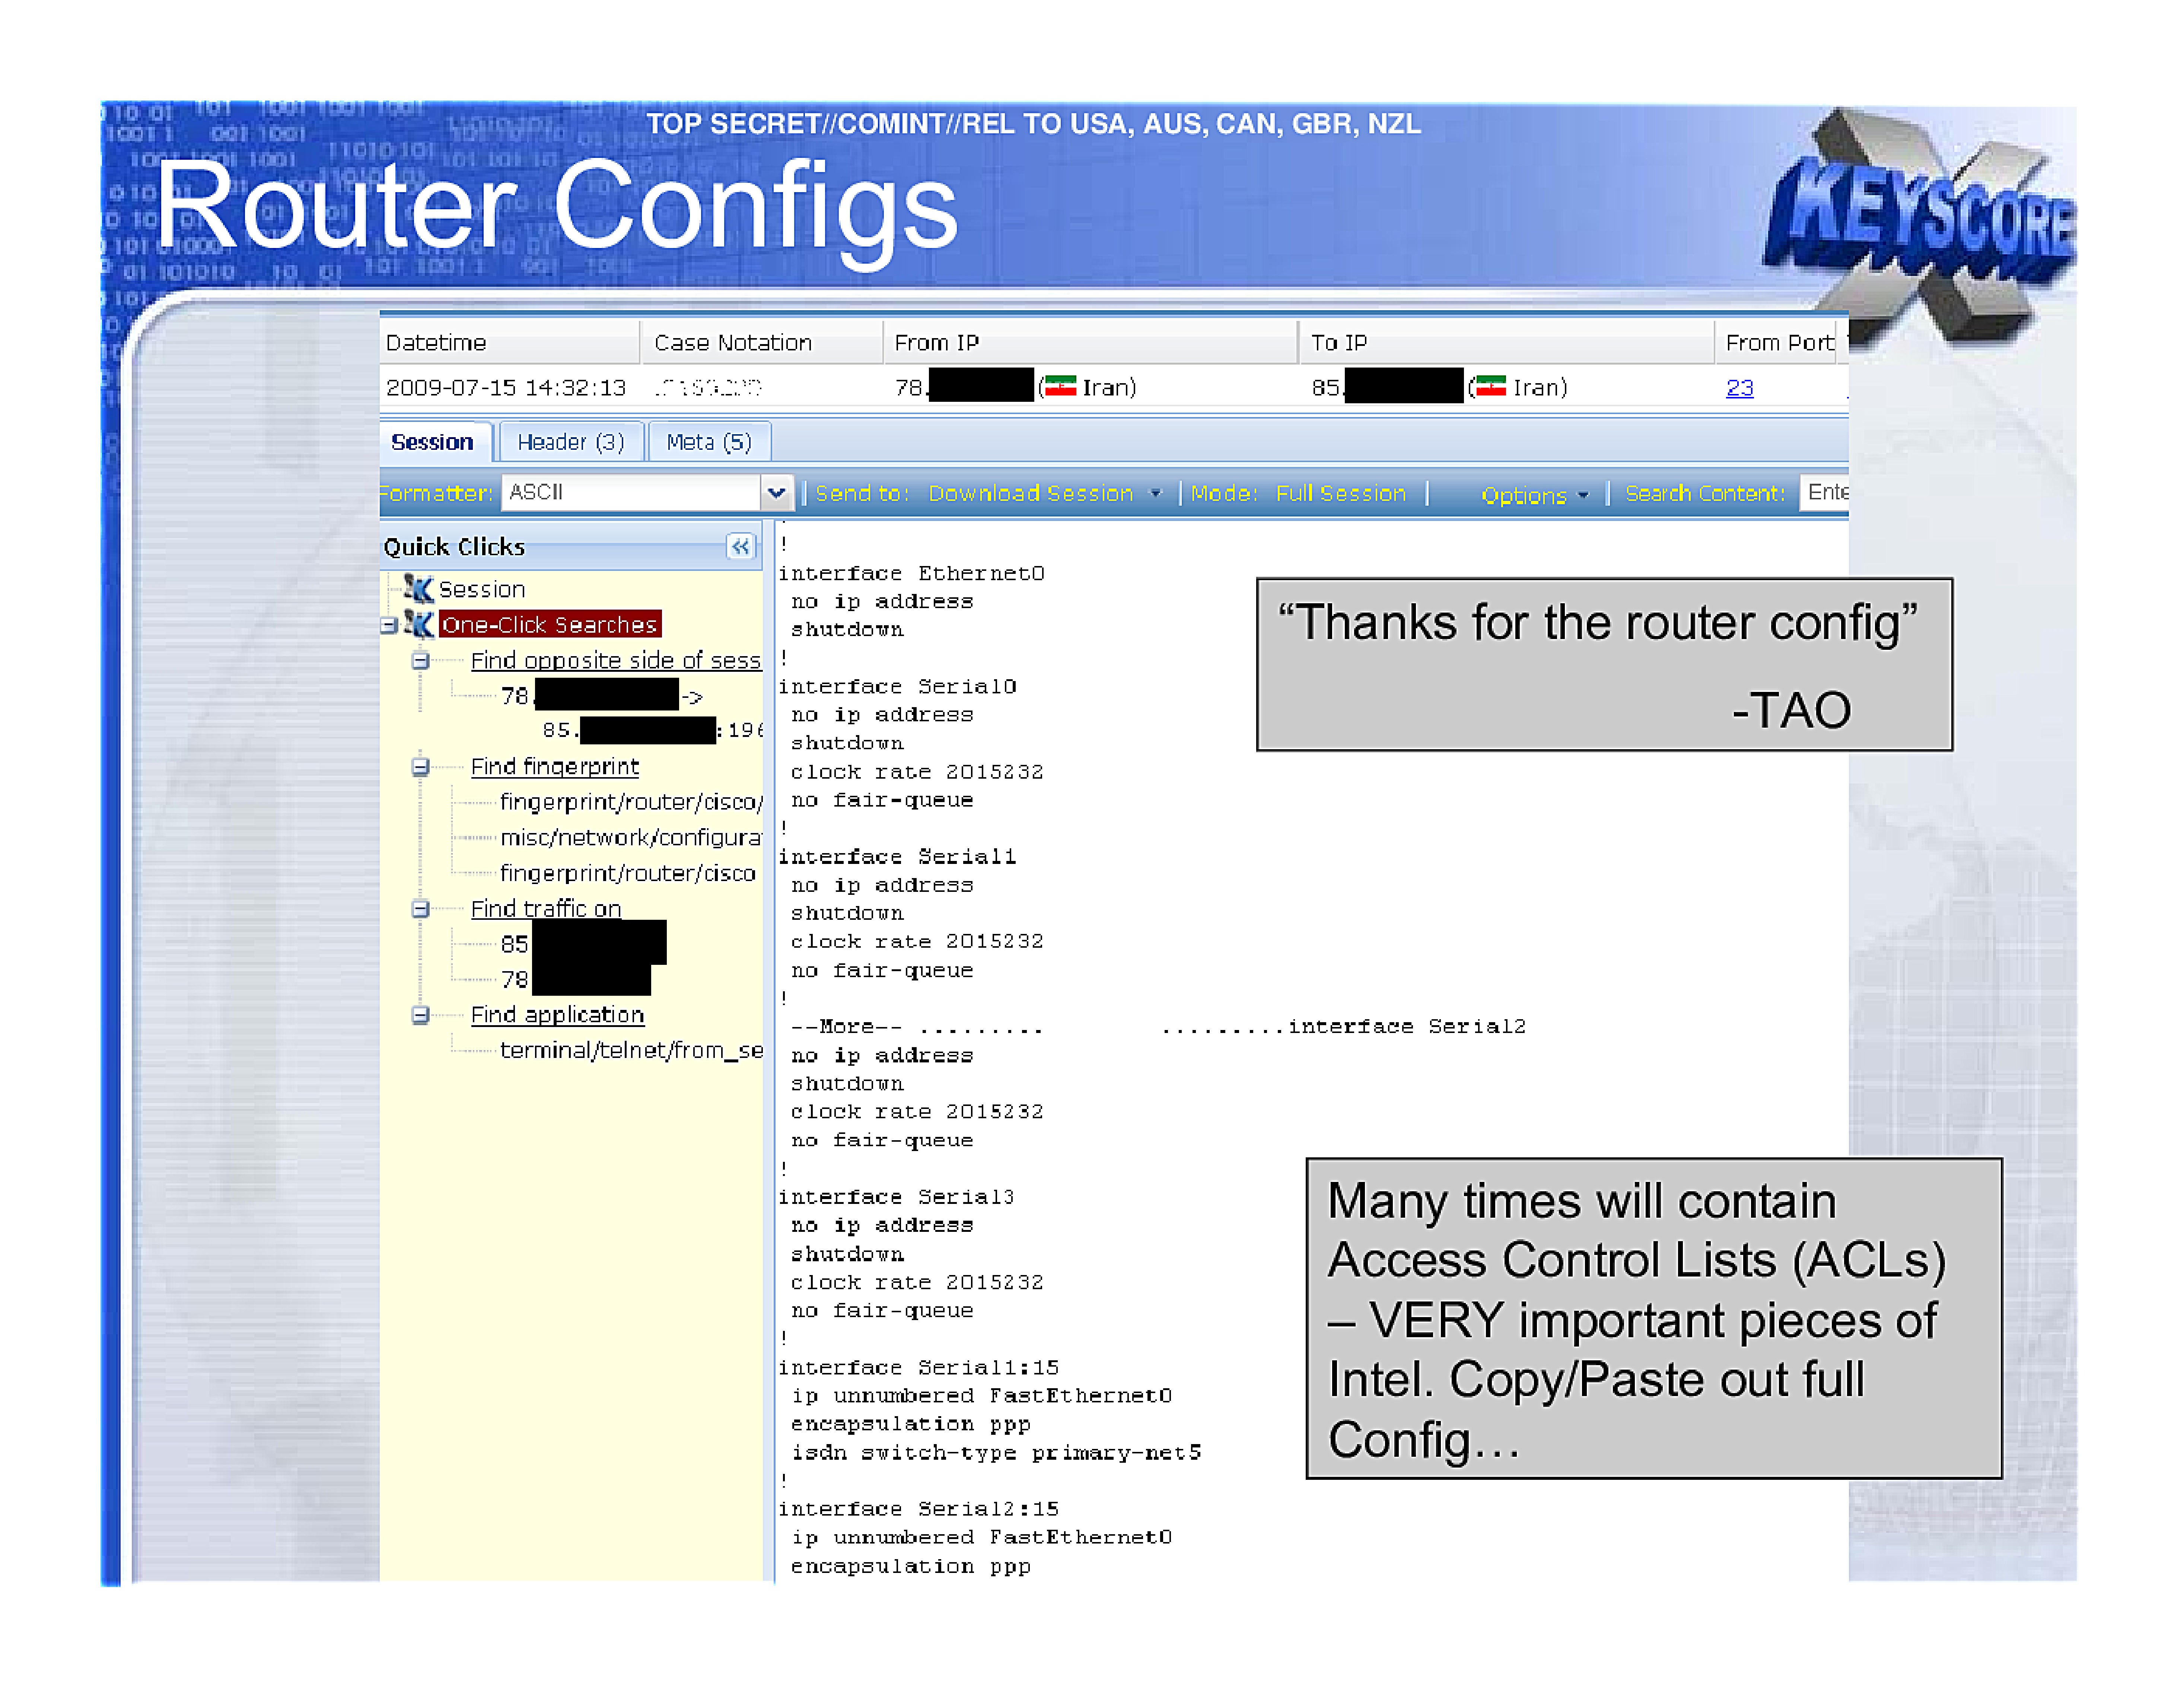
Router Configs
Datetime | Case Notation | From IP | To IP | From Port |
2009-07-15 14:32:13 | 515920 | 78.[REDACTED] (Iran) | 85.[REDACTED] (Iran) | 23 |

Session | Header (3) | Meta (5) |

Formatter: ASCII | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter

Quick Clicks
*   Session
*   One-Click Searches
    *   Find opposite side of sess
       * 78.[REDACTED]->
       * 85.[REDACTED]:196->
    *   Find fingerprint
       * fingerprint/router/cisco/
       * misc/network/configura
       * fingerprint/router/cisco
    *   Find traffic on
       * 85[REDACTED]
       * 78[REDACTED]
    *   Find application
       * terminal/telnet/from_se

"Thanks for the router config"
-TAO

Many times will contain
Access Control Lists (ACLs)
- VERY important pieces of
Intel. Copy/Paste out full
Config...

!
interface Ethernet0
 no ip address
 shutdown
!
interface Serial0
 no ip address
 shutdown
 clock rate 2015232
 no fair-queue
1
interface Serial
 no ip address
 shutdown
 clock rate 2015232
 no fair-queue
!
--More-- ......... ............interface Serial2
 no ip address
 shutdown
 clock rate 2015232
 no fair-queue
!
interface Serial3
 no ip address
 shutdown
 clock rate 2015232
 no fair-queue
!
interface Serial1:15
 ip unnumbered FastEthernet0
 encapsulation ppp
 isdn switch-type primary-net5
!
interface Serial2:15
 ip unnumbered FastEthernet0
 encapsulation ppp
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Agenda
- What TAO needs from analysts
- TELNET Sessions in XKS
- Identifying Browsers
- Web Forum Logins / Passwords
- Webmail Logins and Passwords
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Identifying Web Browsers
- Why?
- TAO can exploit the browsers that lack strong security
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
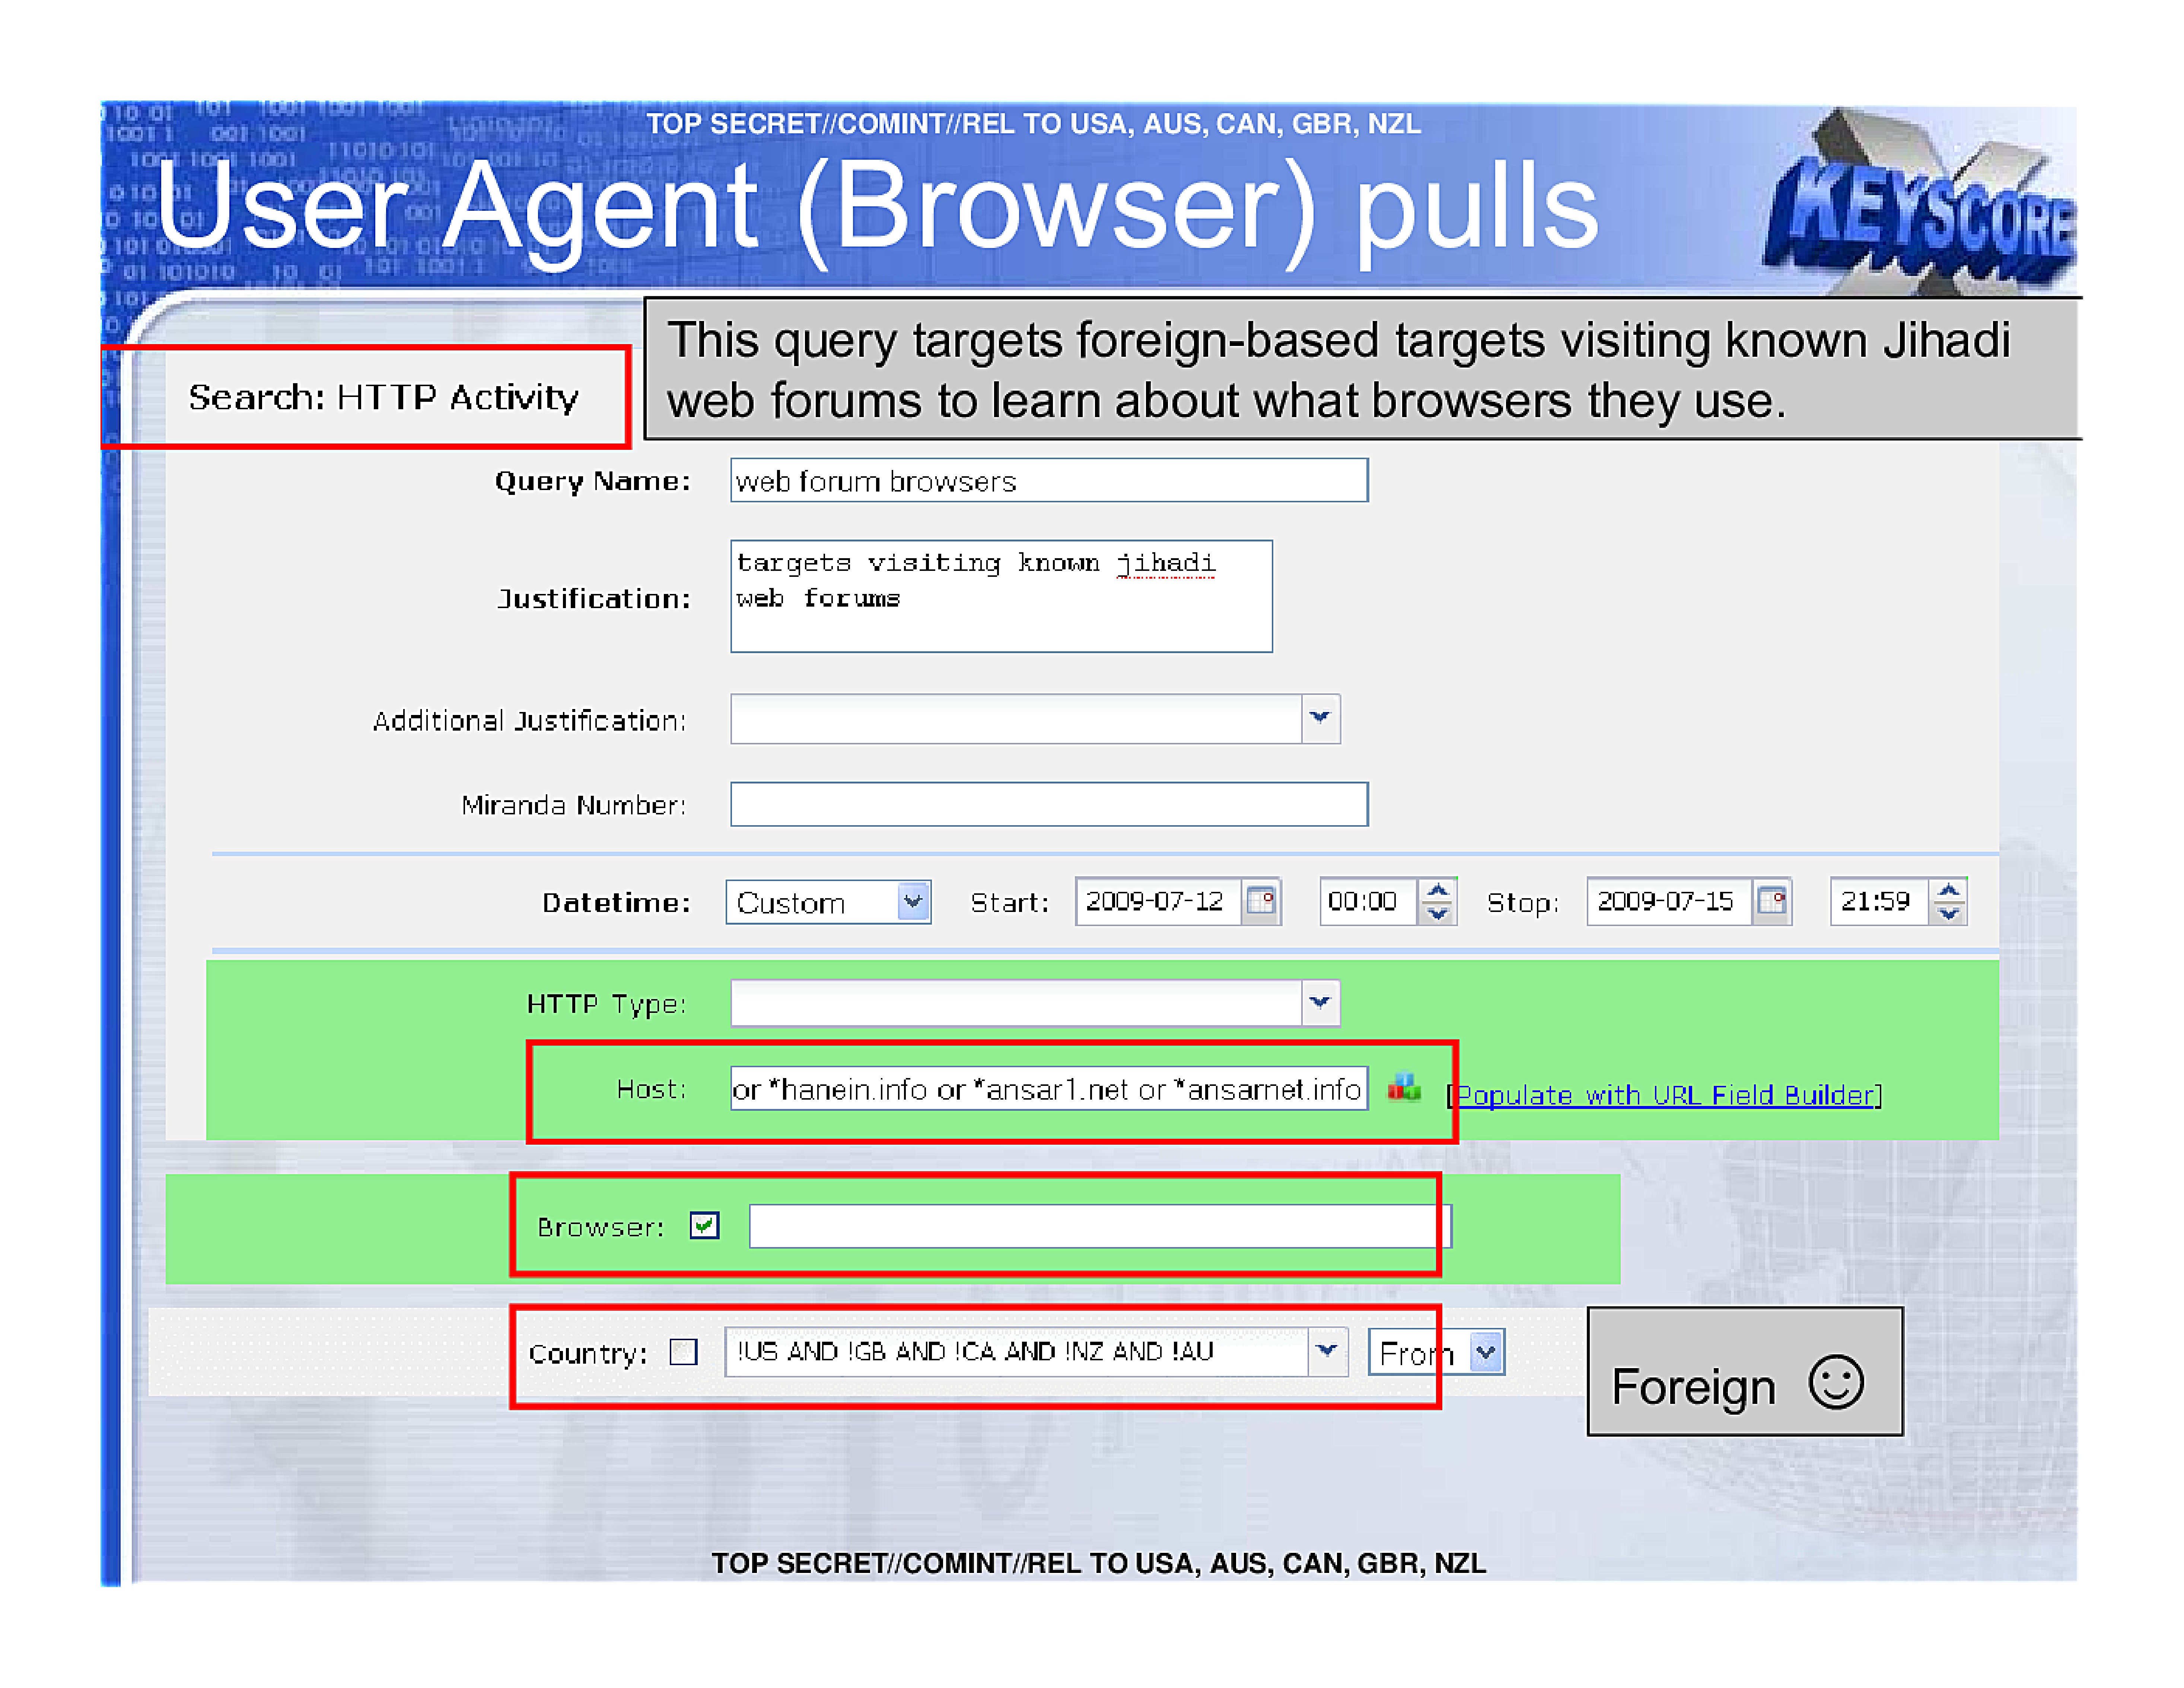
User Agent (Browser) pulls
This query targets foreign-based targets visiting known Jihadi
web forums to learn about what browsers they use.
Search: HTTP Activity
Query Name: web forum browsers
Justification: targets visiting known jihadi web forums
Additional Justification:
Miranda Number:

Datetime: Custom Start: 2009-07-12 00:00 Stop: 2009-07-15 21:59

HTTP Type:
Host: or *hanein.info or *ansar1.net or *ansarnet.info [Populate with URL Field Builder]
Browser:
Country: !US AND !GB AND !CA AND !NZ AND !AU From

Foreign :)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
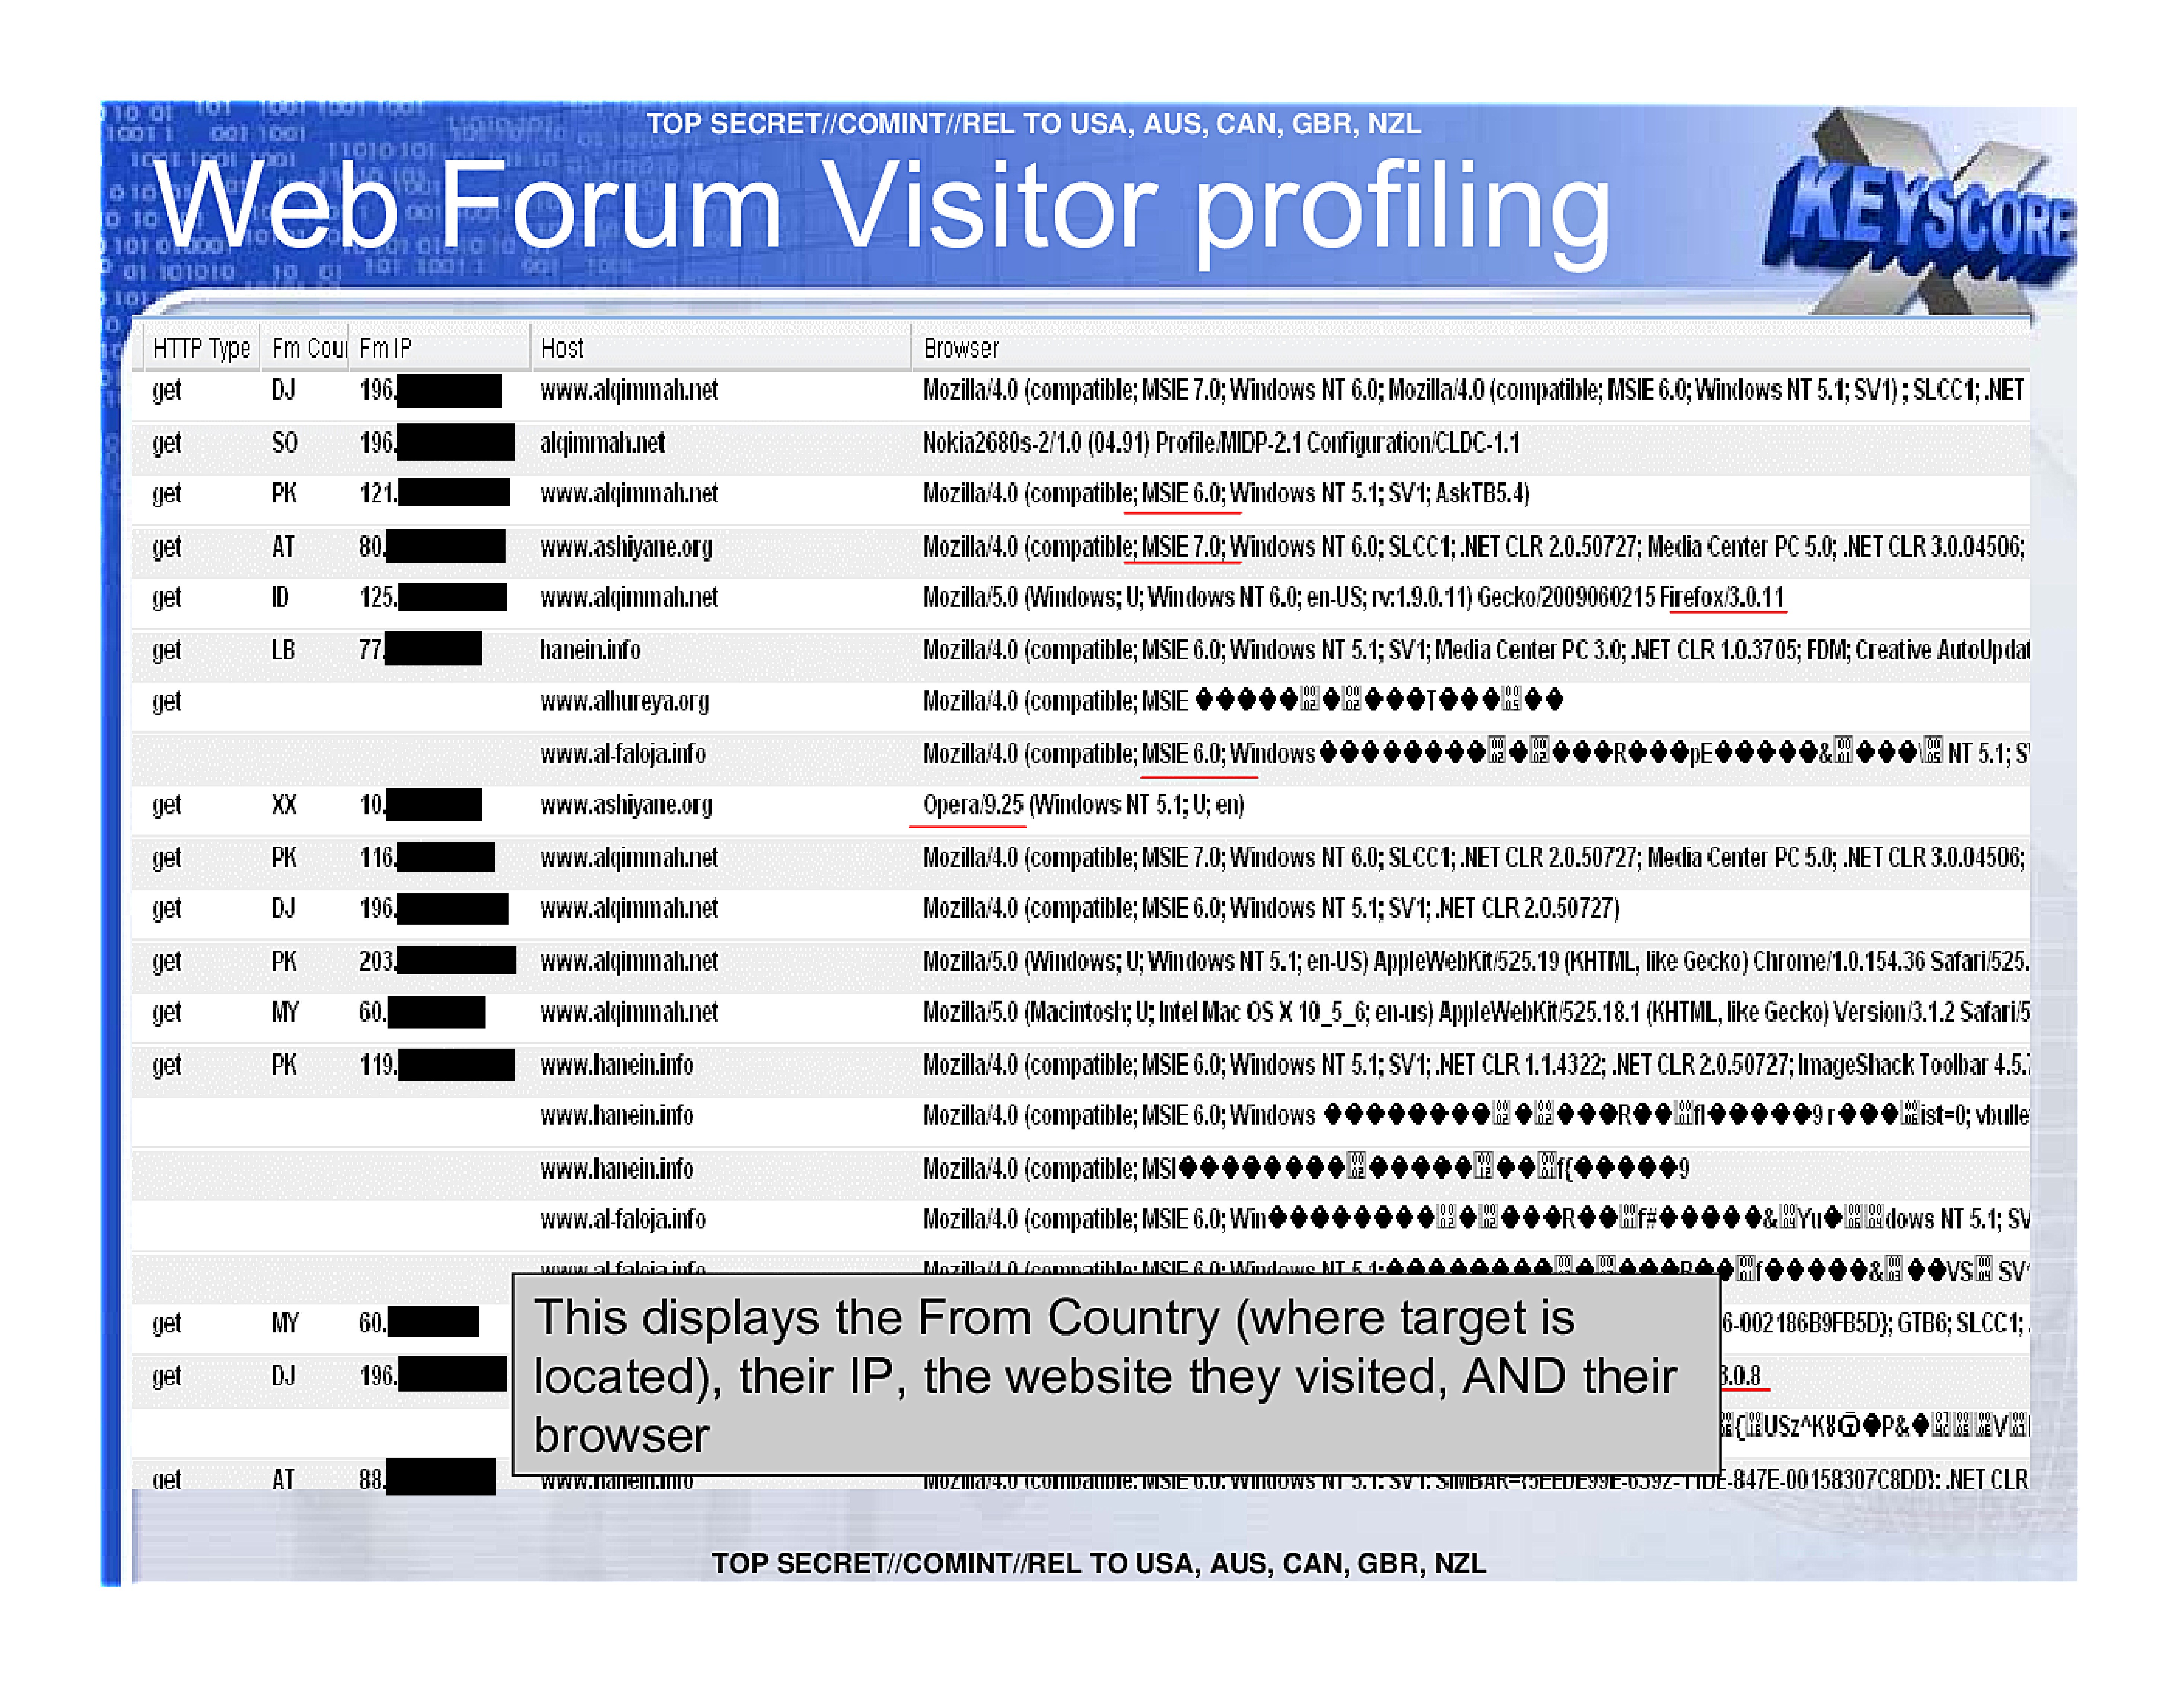
Web Forum Visitor profiling
| HTTP Type | Fm Cou | Fm IP | Host | Browser |
|---|---|---|---|---|
| get | DJ | 196. | www.alqimmah.net | Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 6.0; Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1); SLCC1; .NET |
| get | SO | 196 | alqimmah.net | Nokia2680s-2/1.0 (04.91) Profile/MIDP-2.1 Configuration/CLDC-1.1 |
| get | PK | 121. | www.alqimmah.net | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; AskTB5.4) |
| get | AT | 80. | www.ashiyane.org | Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 6.0; SLCC1; .NET CLR 2.0.50727; Media Center PC 5.0; .NET CLR 3.0.04506; |
| get | ID | 125. | www.alqimmah.net | Mozilla/5.0 (Windows; U; Windows NT 6.0; en-US; rv:1.9.0.11) Gecko/2009060215 Firefox/3.0.11 |
| get | LB | 77 | hanein.info | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; Media Center PC 3.0; .NET CLR 1.0.3705; FDM; Creative AutoUpdat |
| get | www.alhureya.org | Mozilla/4.0 (compatible; MSIE | ||
| get | www.al-faloja.info | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; S | ||
| get | XX | 10. | www.ashiyane.org | Opera/9.25 (Windows NT 5.1; U; en) |
| get | PK | 116. | www.alqimmah.net | Mozilla/4.0 (compatible; MSIE 7.0; Windows NT 6.0; SLCC1; .NET CLR 2.0.50727; Media Center PC 5.0; .NET CLR 3.0.04506; |
| get | DJ | 196 | www.alqimmah.net | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727) |
| get | PK | 203. | www.alqimmah.net | Mozilla/5.0 (Windows; U; Windows NT 5.1; en-US) AppleWebKit/525.19 (KHTML, like Gecko) Chrome/1.0.154.36 Safari/525. |
| get | MY | 60. | www.alqimmah.net | Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10_5_6; en-us) AppleWebKit/525.18.1 (KHTML, like Gecko) Version/3.1.2 Safari/5 |
| get | PK | 119. | www.hanein.info | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0.50727; ImageShack Toolbar 4.5.1 |
| www.hanein.info | Mozilla/4.0 (compatible; MSIE 6.0; Windows ist=0;vbulle | |||
| www.hanein.info | Mozilla/4.0 (compatible; MSI | |||
| www.al-faloja.info | Mozilla/4.0 (compatible; MSIE 6.0; Win dows NT 5.1; SV | |||
| www.alqimmah.net | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1) | |||
| get | MY | 60. | 4.02 186B9FB5D); GTB6; SLCC1;. | |
| get | DJ | 196. | 3.0.8 | |
| get | AT | DEEVEYYE-VOYZ-TIDE-847E-00158307C8DD):.NET CLR |
This displays the From Country (where target is
located), their IP, the website they visited, AND their
browser
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
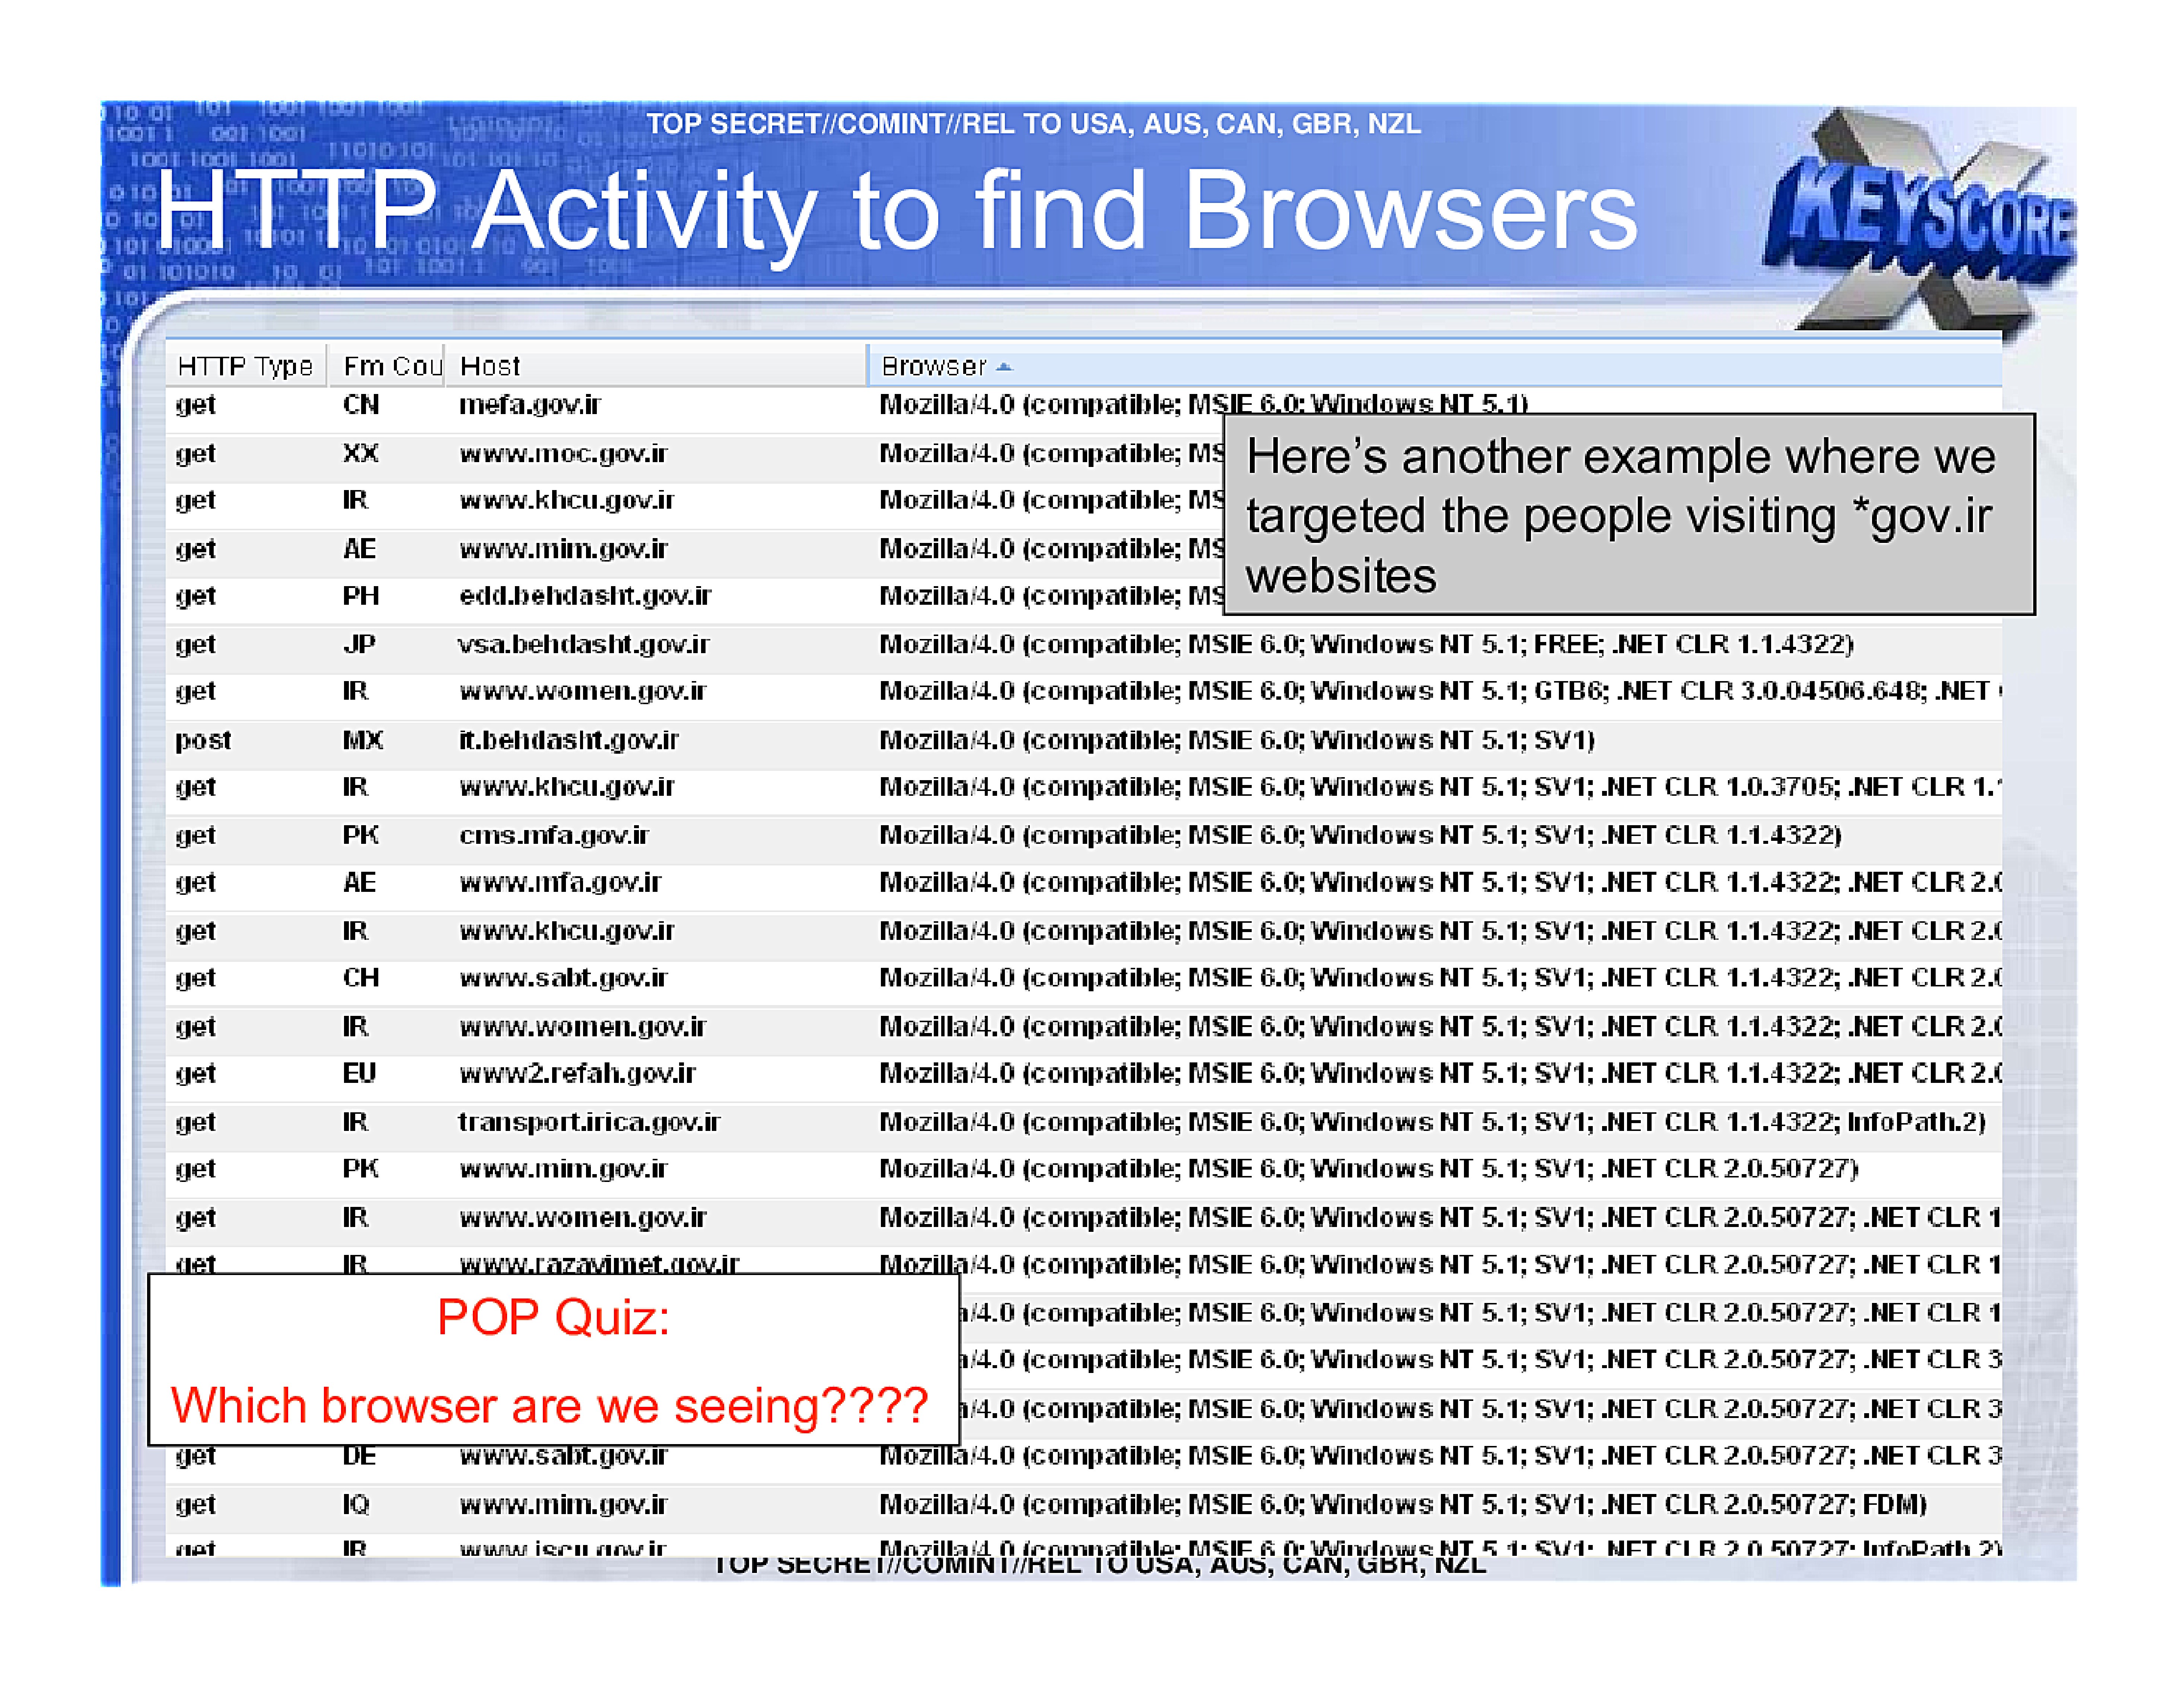
HTTP Activity to find Browsers
Here's another example where we
MS targeted the people visiting *gov.ir
websites
| HTTP Type | Fm Cou | Host | Browser |
|---|---|---|---|
| get | CN | mefa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1) |
| get | XX | www.moc.gov.ir | Mozilla/4.0 (compatible; Ms |
| get | IR | www.khcu.gov.ir | Mozilla/4.0 (compatible; |
| get | AE | www.mim.gov.ir | Mozilla/4.0 (compatible; MS |
| get | PH | edd.behdasht.gov.ir | Mozilla/4.0 (compatible; MS |
| get | JP | vsa.behdasht.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; FREE; .NET CLR 1.1.4322) |
| get | IR | www.women.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; GTB6; .NET CLR 3.0.04506.648; .NET |
| post | MX | it.behdasht.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1) |
| get | IR | www.khcu.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.0.3705; .NET CLR 1. |
| get | PK | cms.mfa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322) |
| get | AE | www.mfa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | IR | www.khcu.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | CH | www.sabt.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | IR | www.women.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | EU | www2.refah.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | IR | transport.irica.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; InfoPath.2) |
| get | PK | www.mim.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727) |
| get | IR | www.women.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 1 |
| get | IR | www.razavimet.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 1 |
| 1/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 1 | |||
| 1/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 3 | |||
| /4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 3 | |||
| get | DE | www.sabt.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 3 |
| get | IR | www.mim.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; FDM) |
| get | IR | www.iscu.gov.ir | Mozillaid (compatible MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; InfoPath 21 |
POP Quiz:
Which browser are we seeing????
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
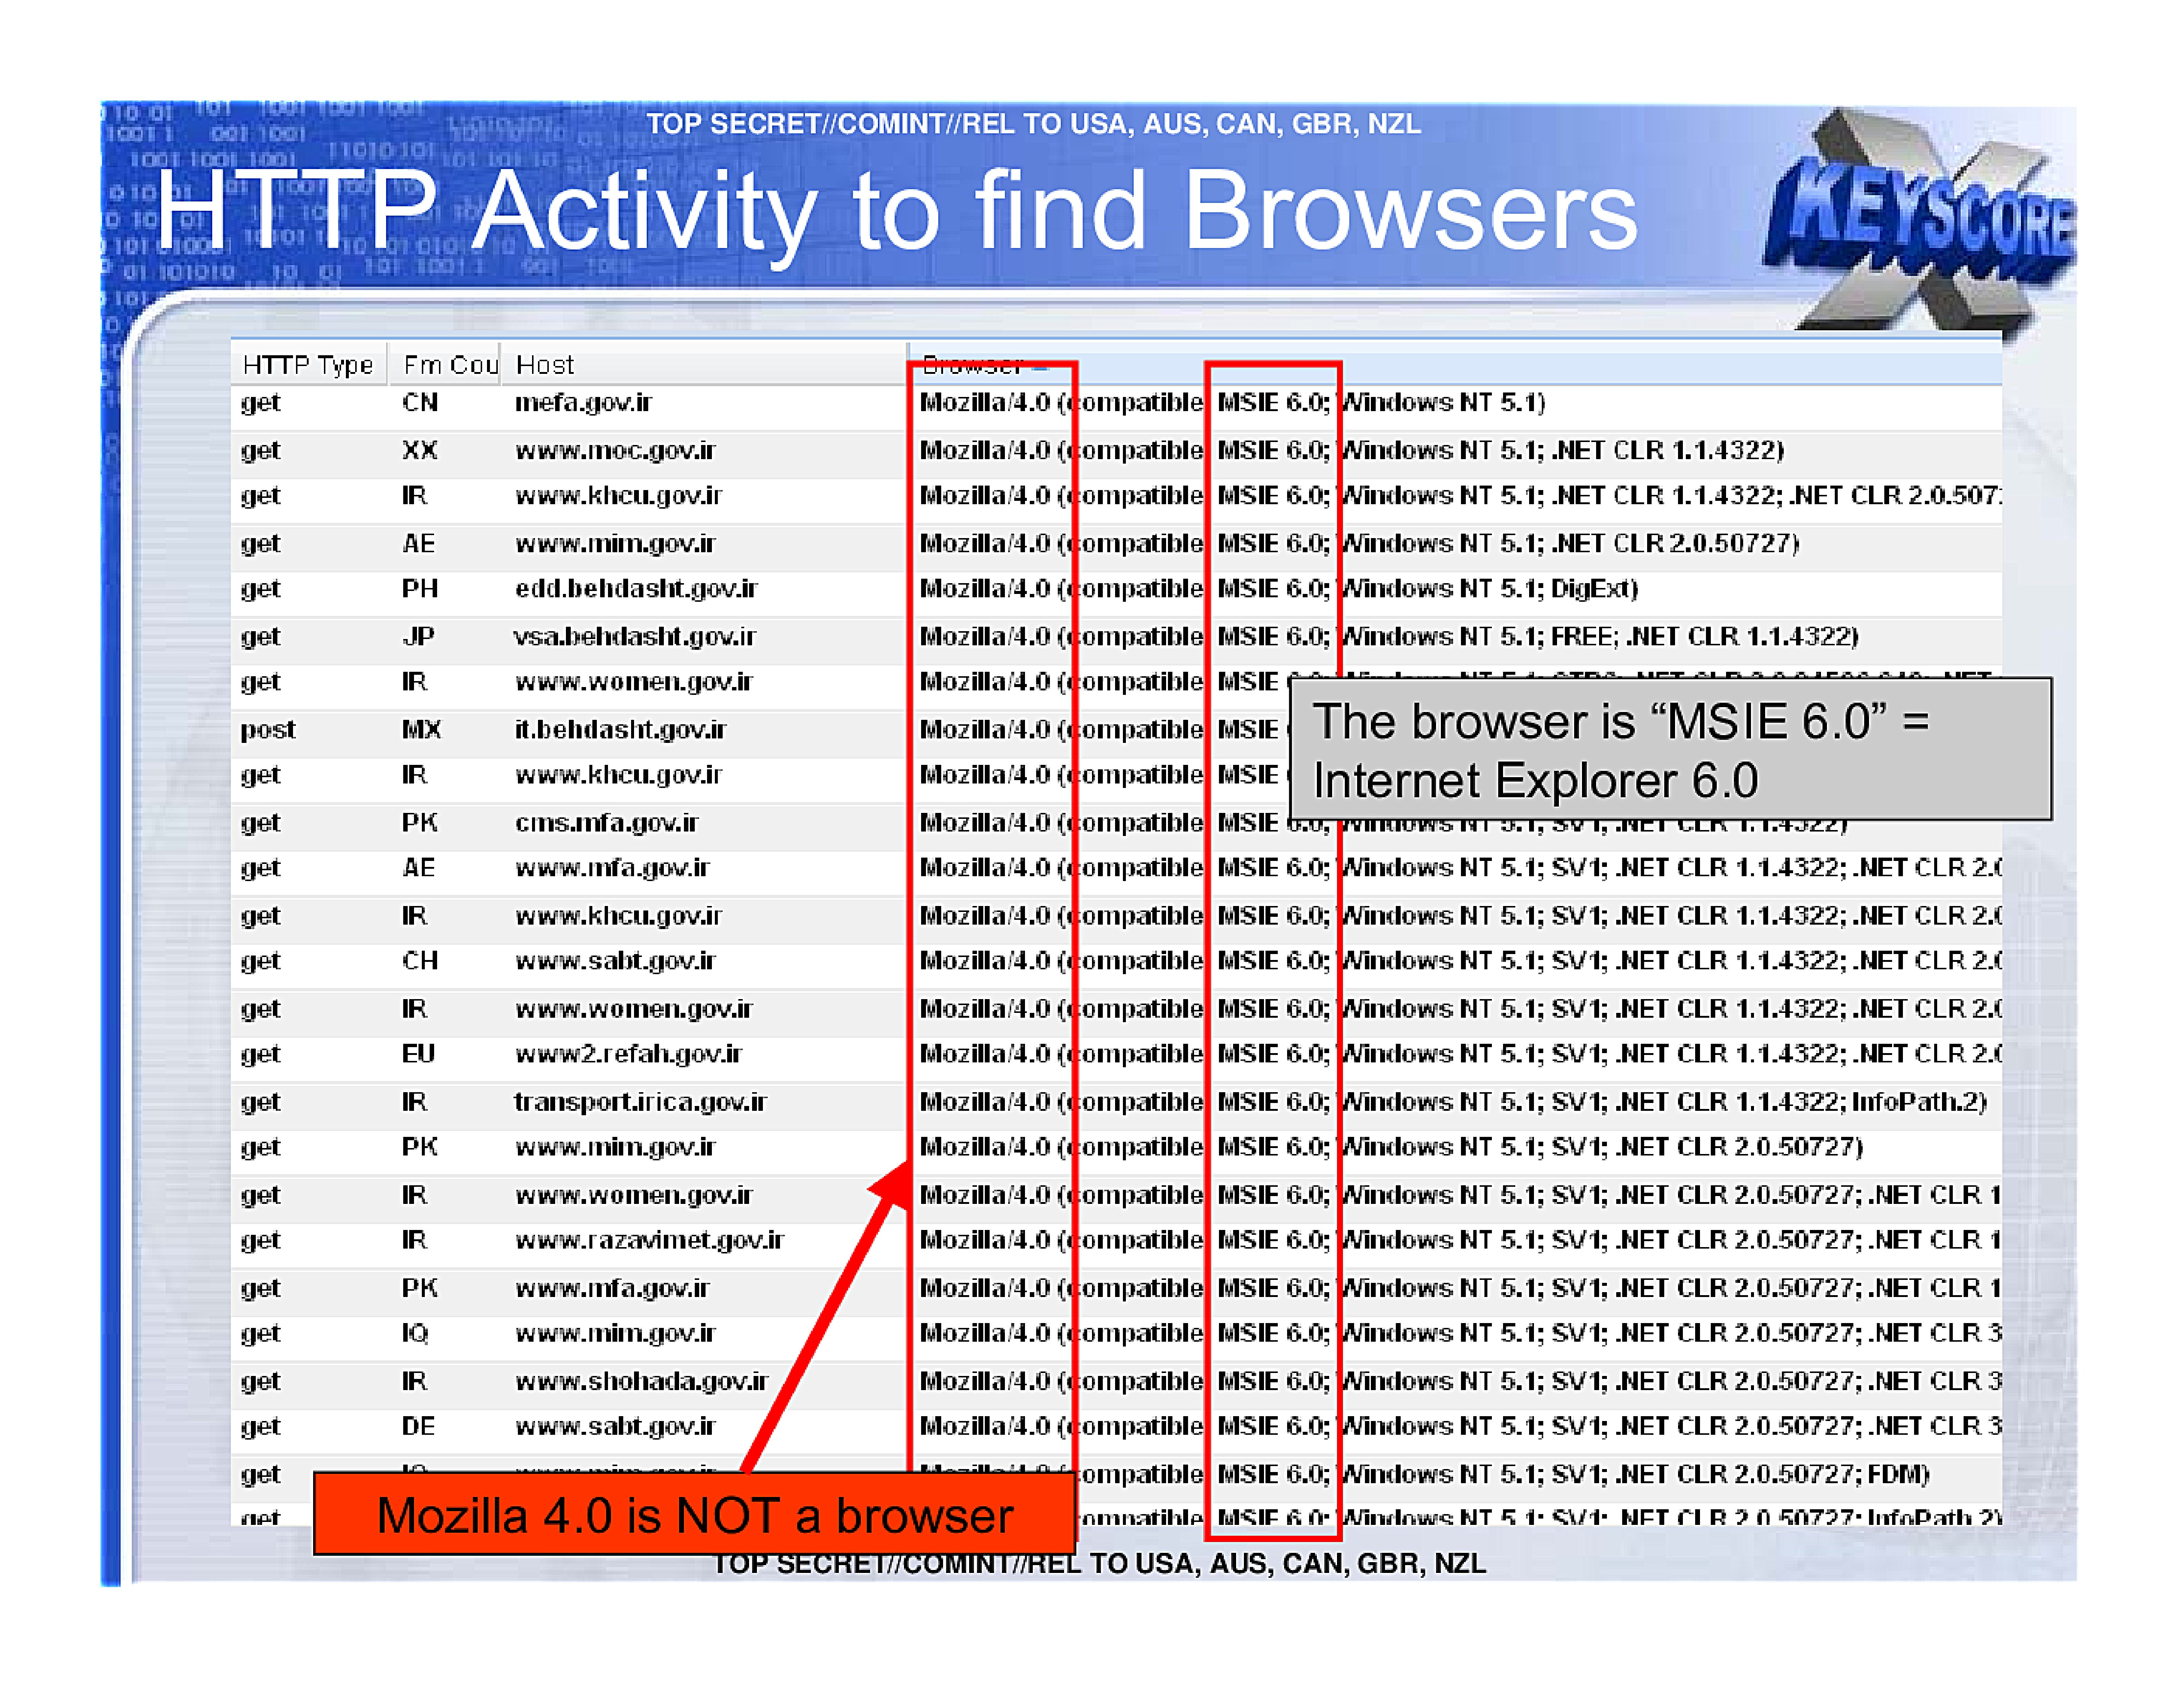
HTTP Activity to find Browsers
| HTTP Type | Fm Cou | Host | Browser |
|---|---|---|---|
| get | CN | mefa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1) |
| get | XX | www.moc.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; .NET CLR 1.1.4322) |
| get | IR | www.khcu.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; .NET CLR 1.1.4322; .NET CLR 2.0.507. |
| get | AE | www.mim.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; .NET CLR 2.0.50727) |
| get | PH | edd.behdasht.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; DigExt) |
| get | JP | vsa.behdasht.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; FREE; .NET CLR 1.1.4322) |
| get | IR | www.women.gov.ir | Mozilla/4.0 (compatible; MSIE |
| post | MX | it.behdasht.gov.ir | Mozilla/4.0 (compatible; MSIE |
| get | IR | www.khcu.gov.ir | Mozilla/4.0 (compatible; MSIE |
| get | PK | cms.mfa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV I, JNCT ULIK 1.1.43221 |
| get | AE | www.mfa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | IR | www.khcu.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | CH | www.sabt.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | IR | www.women.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2. |
| get | EU | www2.refah.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; .NET CLR 2.0 |
| get | IR | transport.irica.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 1.1.4322; InfoPath.2) |
| get | PK | www.mim.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727) |
| get | IR | www.women.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 1 |
| get | IR | www.razavimet.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 1 |
| get | PK | www.mfa.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 1 |
| get | IQ | www.mim.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 3 |
| get | IR | www.shohada.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 3 |
| get | DE | www.sabt.gov.ir | Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; .NET CLR 3 |
| get | compatible MSIE 6.0; Windows NT 5.1; SV1; .NET CLR 2.0.50727; FDM) | ||
| get | Compatible MSIER Windows NT 51-51 NET CLR 2050727- InfoPath 21 |
The browser is "MSIE 6.0" =
Internet Explorer 6.0
Mozilla 4.0 is NOT a browser
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
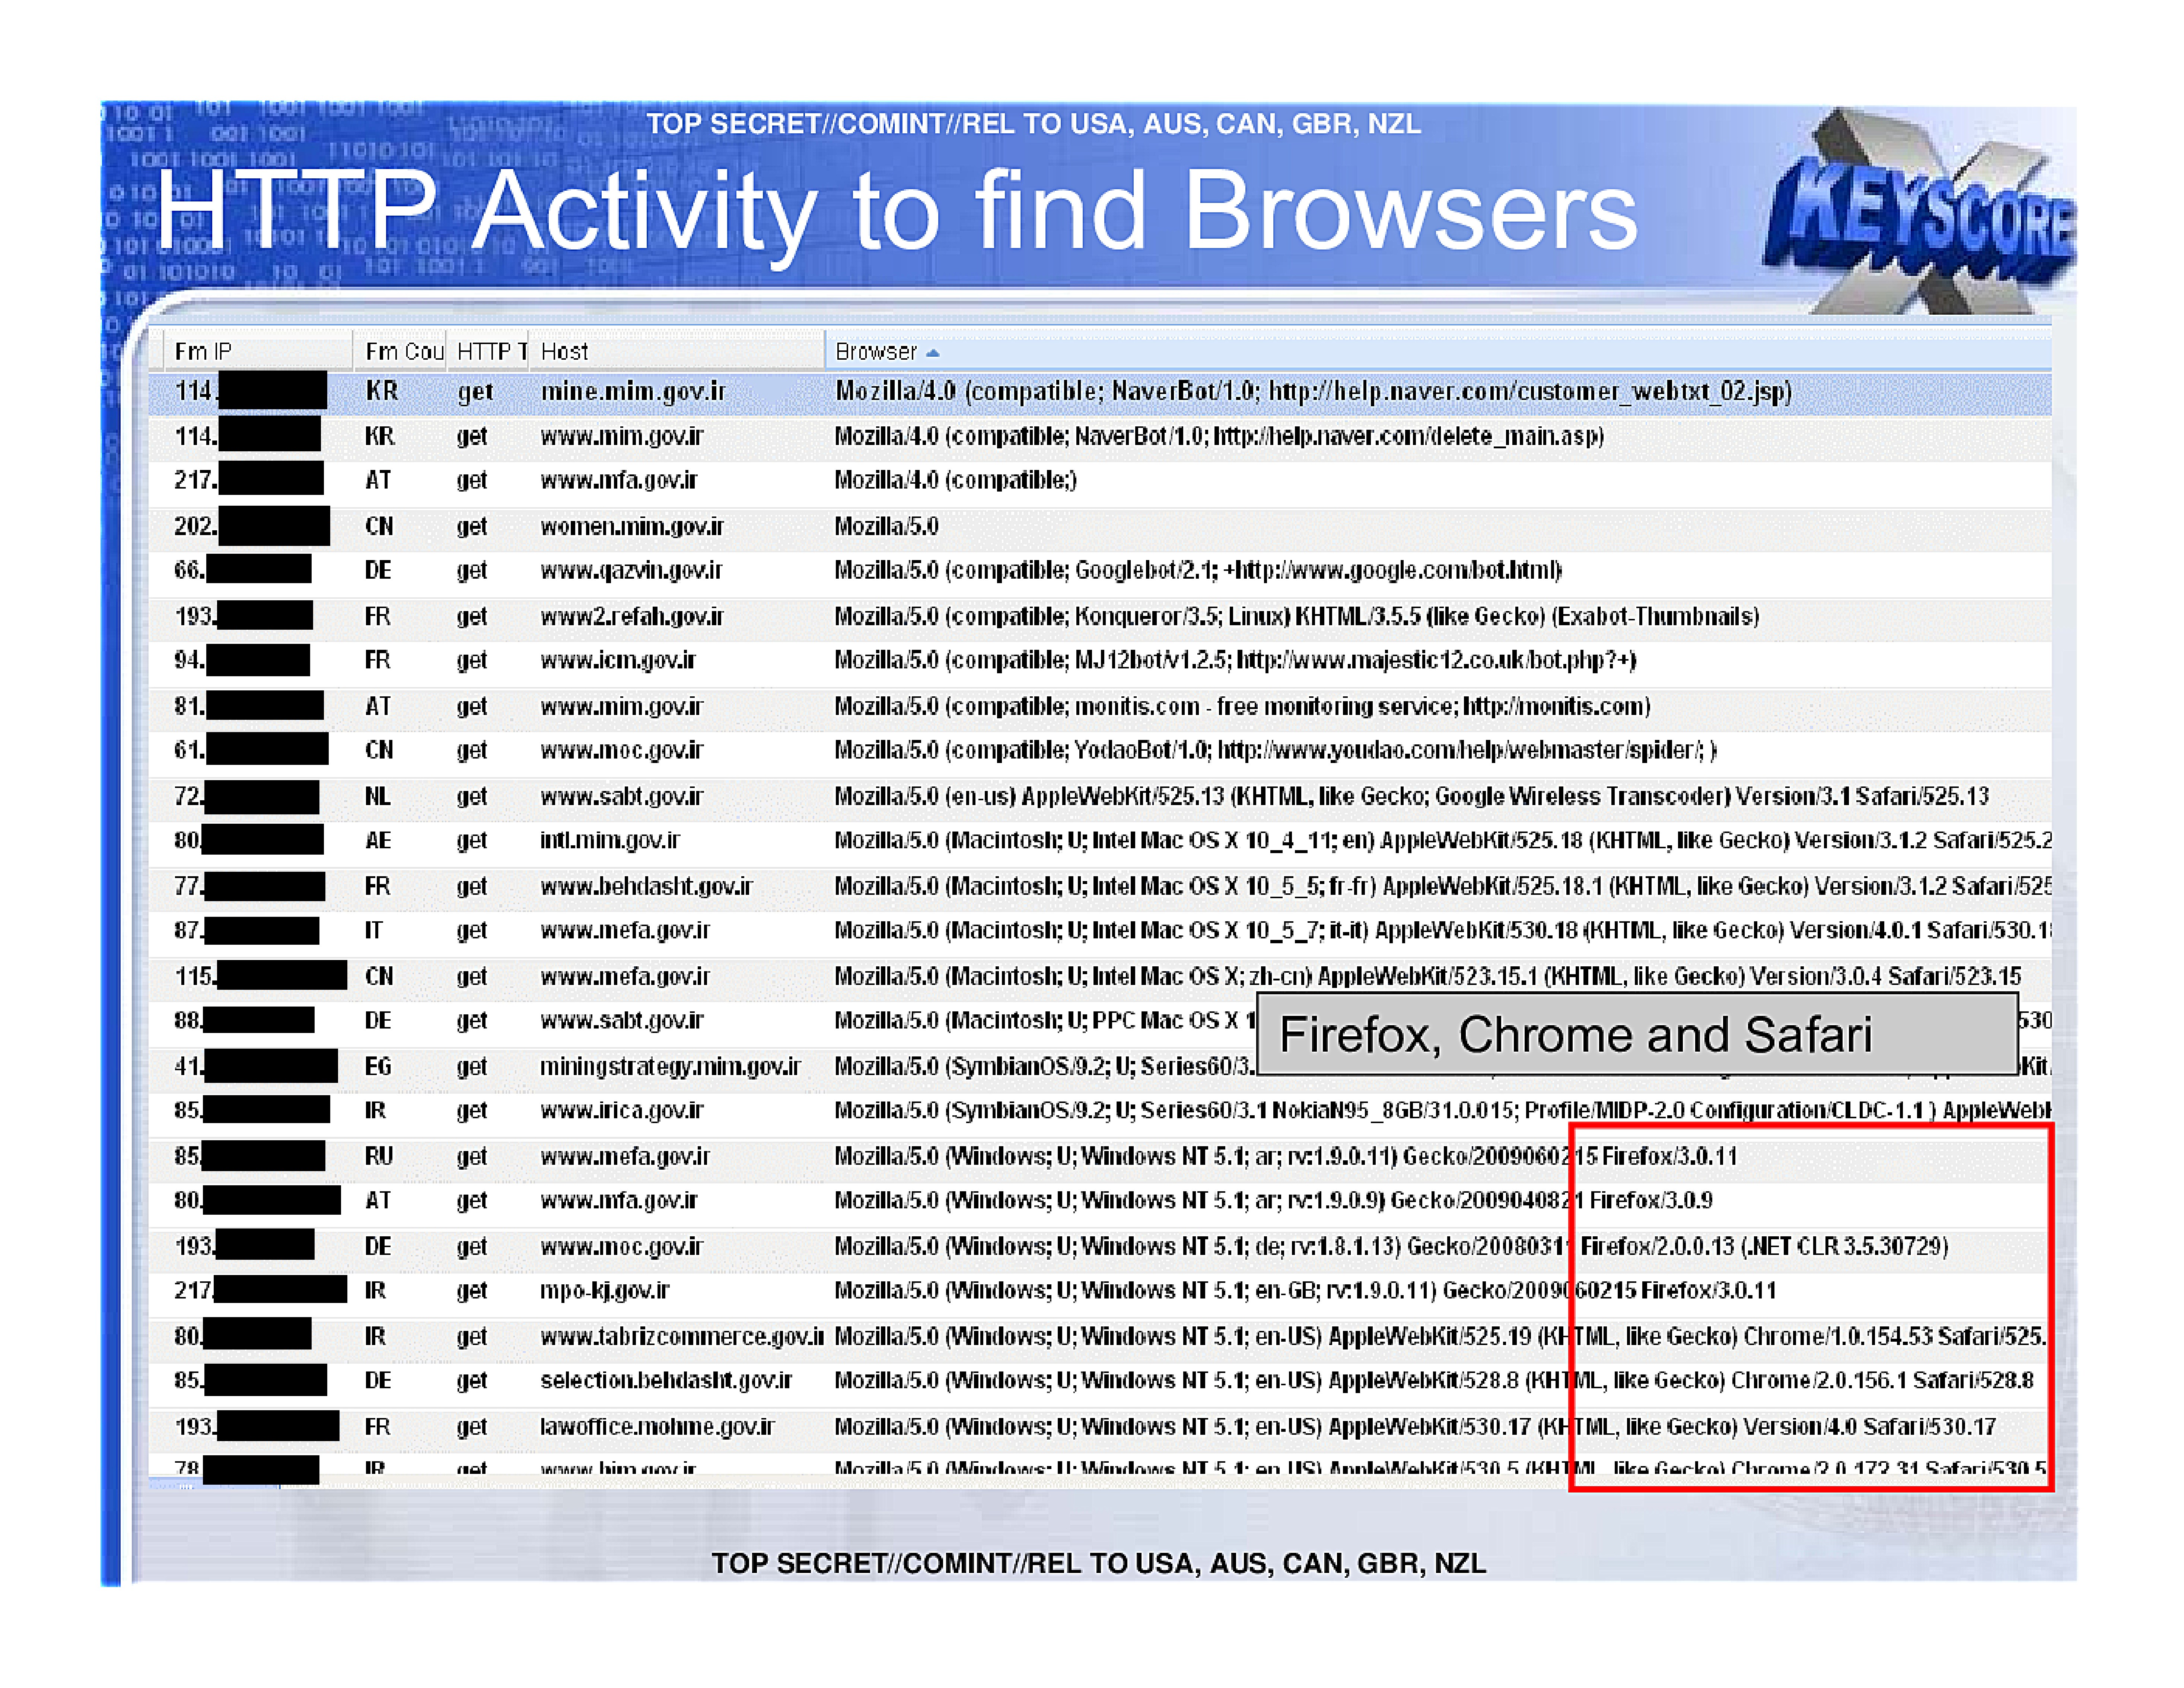
HTTP Activity to find Browsers
| Fm IP | Fm Cou | HTTP T | Host | Browser |
|---|---|---|---|---|
| 114.[REDACTED] | KR | get | mine.mim.gov.ir | Mozilla/4.0 (compatible; NaverBot/1.0; http://help.naver.com/customer_webtxt_02.jsp) |
| 114.[REDACTED] | KR | get | www.mim.gov.ir | Mozilla/4.0 (compatible; NaverBot/1.0; http://help.naver.com/delete_main.asp) |
| 217.[REDACTED] | AT | get | www.mfa.gov.ir | Mozilla/4.0 (compatible;) |
| 202.[REDACTED] | CN | get | women.mim.gov.ir | Mozilla/5.0 |
| 66.[REDACTED] | DE | get | www.qazvin.gov.ir | Mozilla/5.0 (compatible; Googlebot/2.1; +http://www.google.com/bot.html) |
| 193.[REDACTED] | FR | get | www2.refah.gov.ir | Mozilla/5.0 (compatible; Konqueror/3.5; Linux) KHTML/3.5.5 (like Gecko) (Exabot-Thumbnails) |
| 94.[REDACTED] | FR | get | www.icm.gov.ir | Mozilla/5.0 (compatible; MJ12bot/v1.2.5; http://www.majestic12.co.uk/bot.php?+) |
| 81.[REDACTED] | AT | get | www.mim.gov.ir | Mozilla/5.0 (compatible; monitis.com - free monitoring service; http://monitis.com) |
| 61.[REDACTED] | CN | get | www.moc.gov.ir | Mozilla/5.0 (compatible; YodaoBot/1.0; http://www.youdao.com/help/webmaster/spider) |
| 72.[REDACTED] | NL | get | www.sabt.gov.ir | Mozilla/5.0 (en-us) AppleWebKit/525.13 (KHTML, like Gecko; Google Wireless Transcoder) Version/3.1 Safari/525.13 |
| 80.[REDACTED] | AE | get | intl.mim.gov.ir | Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10_4_11; en) AppleWebKit/525. 18 (KHTML, like Gecko) Version/3.1.2 Safari/525.2 |
| 77.[REDACTED] | FR | get | www.behdasht.gov.ir | Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10_5_5; fr-fr) AppleWebKit/525.18.1 (KHTML, like Gecko) Version/3.1.2 Safari/525 |
| 87.[REDACTED] | IT | get | www.mefa.gov.ir | Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10_5_7; it-it) AppleWebKit/530.18 (KHTML, like Gecko) Version/4.0.1 Safari/530.1 |
| 115.[REDACTED] | CN | get | www.mefa.gov.ir | Mozilla/5.0 (Macintosh; U; Intel Mac OS X; zh-cn) AppleWebKit/523.15.1 (KHTML, like Gecko) Version/3.0.4 Safari/523.15 |
| 88.[REDACTED] | DE | get | www.sabt.gov.ir | Mozilla/5.0 (Macintosh; U; PPC Mac OS X 1 |
| 41.[REDACTED] | EG | get | miningstrategy.mim.gov.ir | Mozilla/5.0 (Symbian OS/9.2; U; Series60/3. Kit |
| 85.[REDACTED] | IR | get | www.irica.gov.ir | Mozilla/5.0 (SymbianOS/9.2; U; Series60/3.1 Nokia N95_8GB/31.0.015; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebt |
| 85.[REDACTED] | RU | get | www.mefa.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; ar; rv:1.9.0.11) Gecko/2009060215 Firefox/3.0.11 |
| 80.[REDACTED] | AT | get | www.mfa.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; ar; rv:1.9.0.9) Gecko/2009040821 Firefox/3.0.9 |
| 193.[REDACTED] | DE | get | www.moc.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; de; rv:1.8.1.13) Gecko/2008031 Firefox/2.0.0.13 (.NET CLR 3.5.30729) |
| 217.[REDACTED] | IR | get | mpo-kj.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; en-GB; rv:1.9.0.11) Gecko/2009060215 Firefox/3.0.11 |
| 80.[REDACTED] | IR | get | www.tabrizcommerce.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; en-US) AppleWebKit/525.19 (KHTML, like Gecko) Chrome/1.0.154.53 Safari/525. |
| 85.[REDACTED] | DE | get | selection.behdasht.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; en-US) AppleWebKit/528.8 (KHTML, like Gecko) Chrome/2.0.156.1 Safari/528.8 |
| 193.[REDACTED] | FR | get | lawoffice.mohme.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; en-US) AppleWebKit/530.17 (KHTML, like Gecko) Version/4.0 Safari/530.17 |
| 78[REDACTED] | IR | get | www.bin.gov.ir | Mozilla/5.0 (Windows; U; Windows NT 5.1; en-US) AppleWebKit/530.5 (KHTML, like Gecko) Chrome/2.0.172.31 Safari/530.5 |
Firefox, Chrome and Safari
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
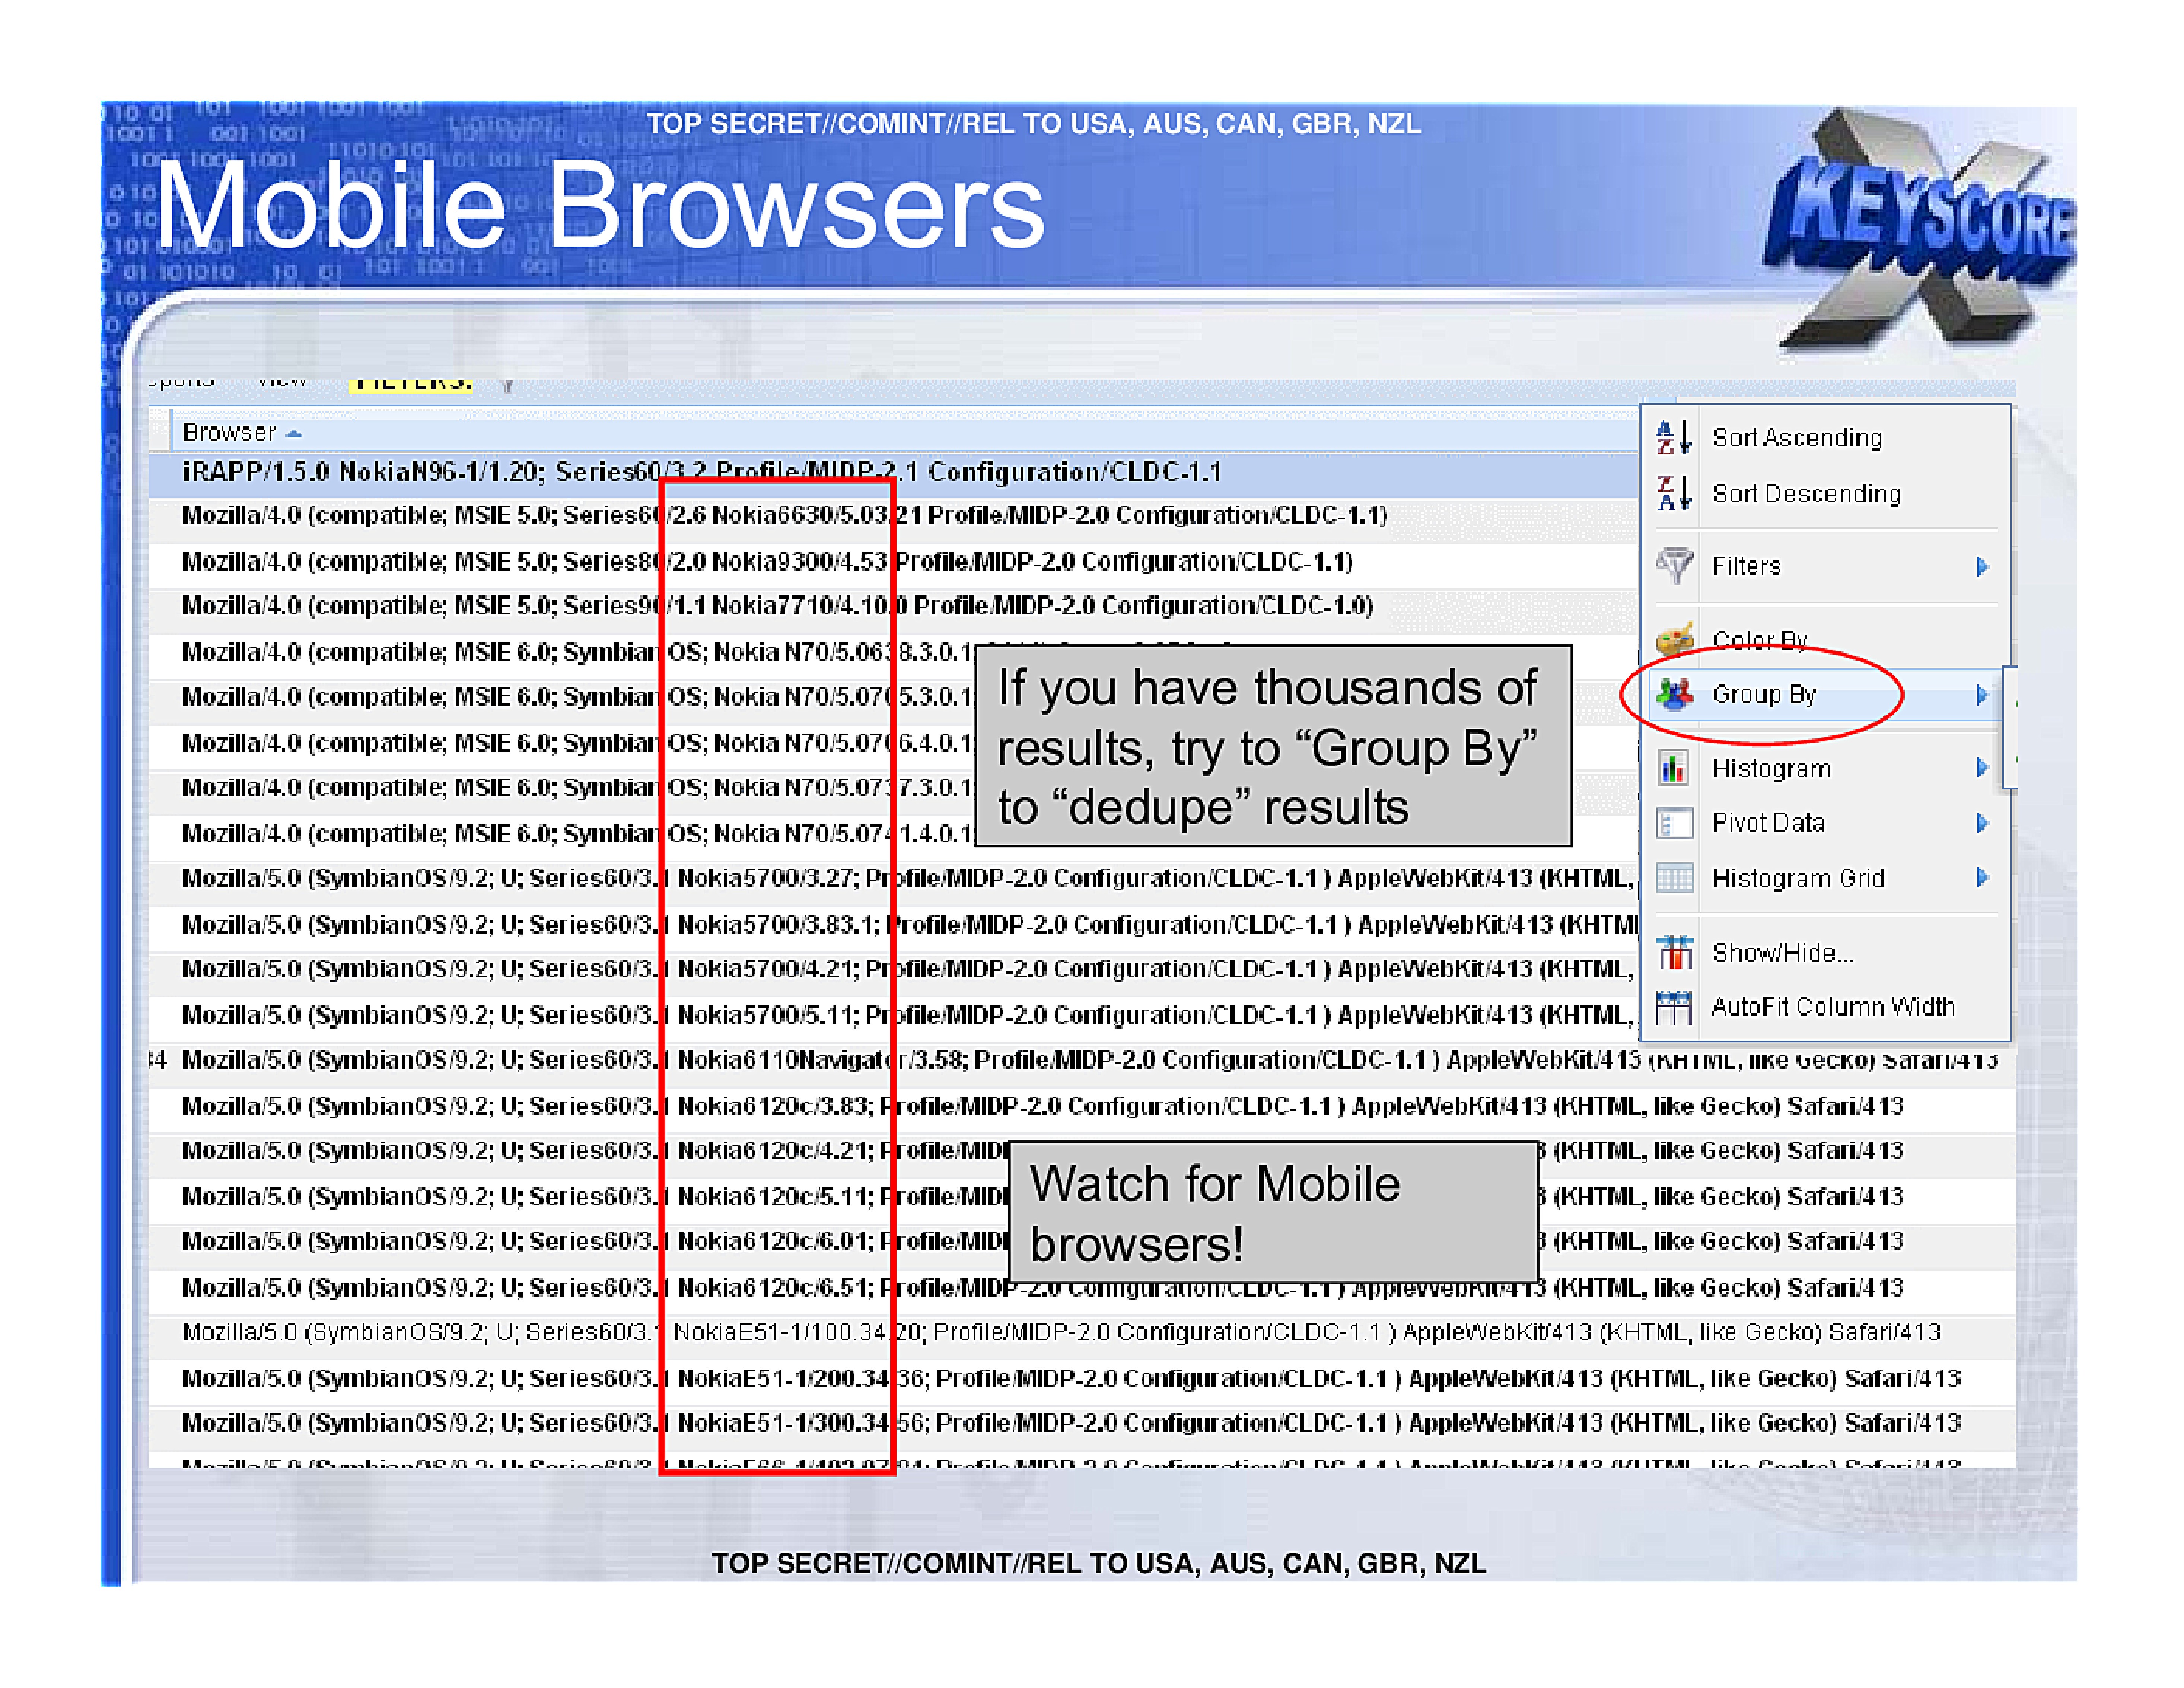
Mobile Browsers
Browser
IRAPP/1.5.0 NokiaN96-1/1.20; Series60/3.2 Profile/MIDP-2.1 Configuration/CLDC-1.1
Mozilla/4.0 (compatible; MSIE 5.0; Series60/2.6 Nokia6630/5.03.21 Profile/MIDP-2.0 Configuration/CLDC-1.1)
Mozilla/4.0 (compatible; MSIE 5.0; Series80/2.0 Nokia9300/4.53 Profile/MIDP-2.0 Configuration/CLDC-1.1)
Mozilla/4.0 (compatible; MSIE 5.0; Series90/1.1 Nokia7710/4.10.0 Profile/MIDP-2.0 Configuration/CLDC-1.0)
Mozilla/4.0 (compatible; MSIE 6.0; Symbian OS; Nokia N70/5.063 8.3.0.1
Mozilla/4.0 (compatible; MSIE 6.0; Symbian OS; Nokia N70/5.0705.3.0.1
Mozilla/4.0 (compatible; MSIE 6.0; Symbian OS; Nokia N70/5.0706.4.0.1
Mozilla/4.0 (compatible; MSIE 6.0; Symbian OS; Nokia N70/5.0737.3.0.1
Mozilla/4.0 (compatible; MSIE 6.0; Symbian OS; Nokia N70/5.0741.4.0.1
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia5700/3.27; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML,
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia5700/3.83.1; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTMI
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia5700/4.21; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML,
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia5700/5.11; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML,
4 Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia6110Navigator/3.58; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML, like Gecko) Safari/413
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia6120c/3.83; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML, like Gecko) Safari/413
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia6120c/4.21; Profile/MIDI
Mozilla/5.0 (SymbianOS/9.2; U; Series60/3.1 Nokia6120c/5.11; Profile/MIDI
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia6120c/6.01; Profile/MIDI
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 Nokia6120c/6.51; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 NokiaE51-1/100.34.20; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML, like Gecko) Safari/413
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 NokiaE51-1/200.34.36; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML, like Gecko) Safari/413
Mozilla/5.0 (Symbian OS/9.2; U; Series60/3.1 NokiaE51-1/300.34.56; Profile/MIDP-2.0 Configuration/CLDC-1.1) AppleWebKit/413 (KHTML, like Gecko) Safari/413

If you have thousands of
results, try to "Group By"
to "dedupe" results

Watch for Mobile
browsers!

Sort Ascending
Sort Descending
Filters
Color By
Group By
Histogram
Pivot Data
Histogram Grid
Show/Hide...
AutoFit Column Width
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Agenda
- What TAO needs from analysts
- TELNET Sessions in XKS
- Identifying Browers
- Web Forum Logins / Passwords
- Webmail Logins / Passwords
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
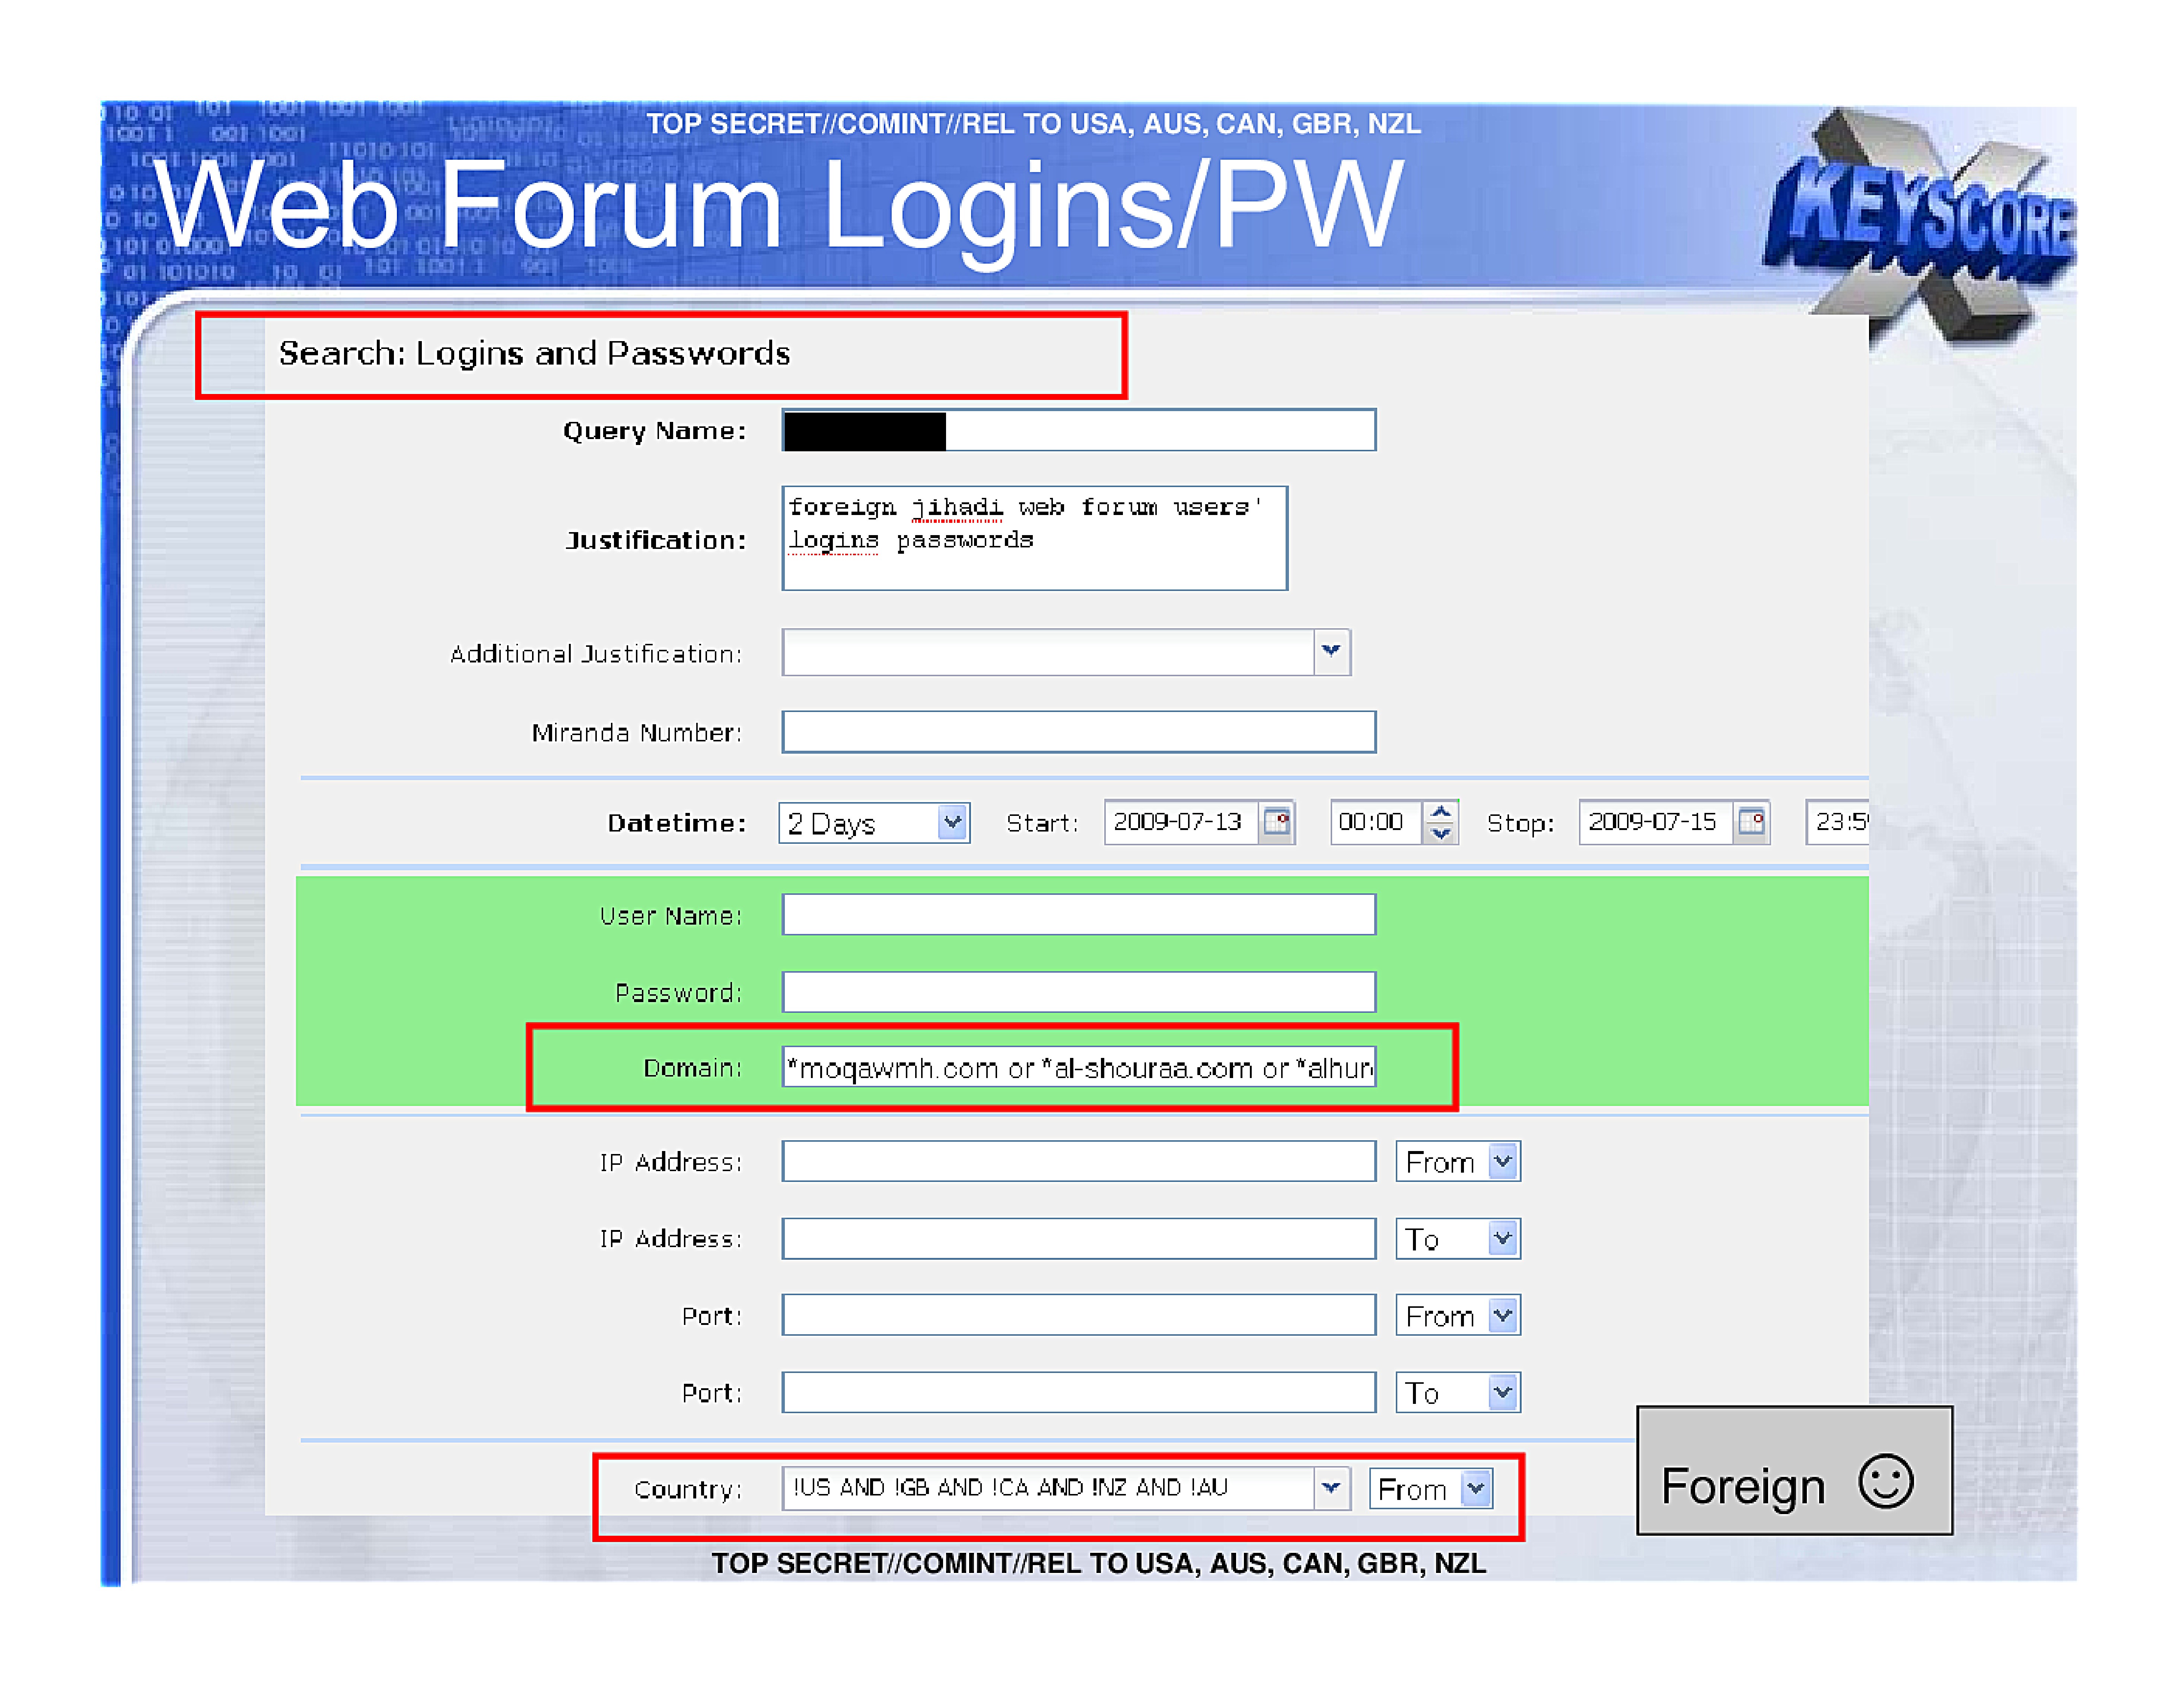
Web Forum Logins/PW
Search: Logins and Passwords
Query Name: [REDACTED]
Justification: foreign jihadi web forum users' logins passwords
Additional Justification:
Miranda Number:
Datetime: 2 Days Start: 2009-07-13 00:00 Stop: 2009-07-15 23:5
User Name:
Password:
Domain: *moqawmh.com or *al-shouraa.com or *alhur
IP Address: From
IP Address: To
Port: From
Port: To
Country: !US AND !GB AND !CA AND !NZ AND !AU From

Foreign :)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
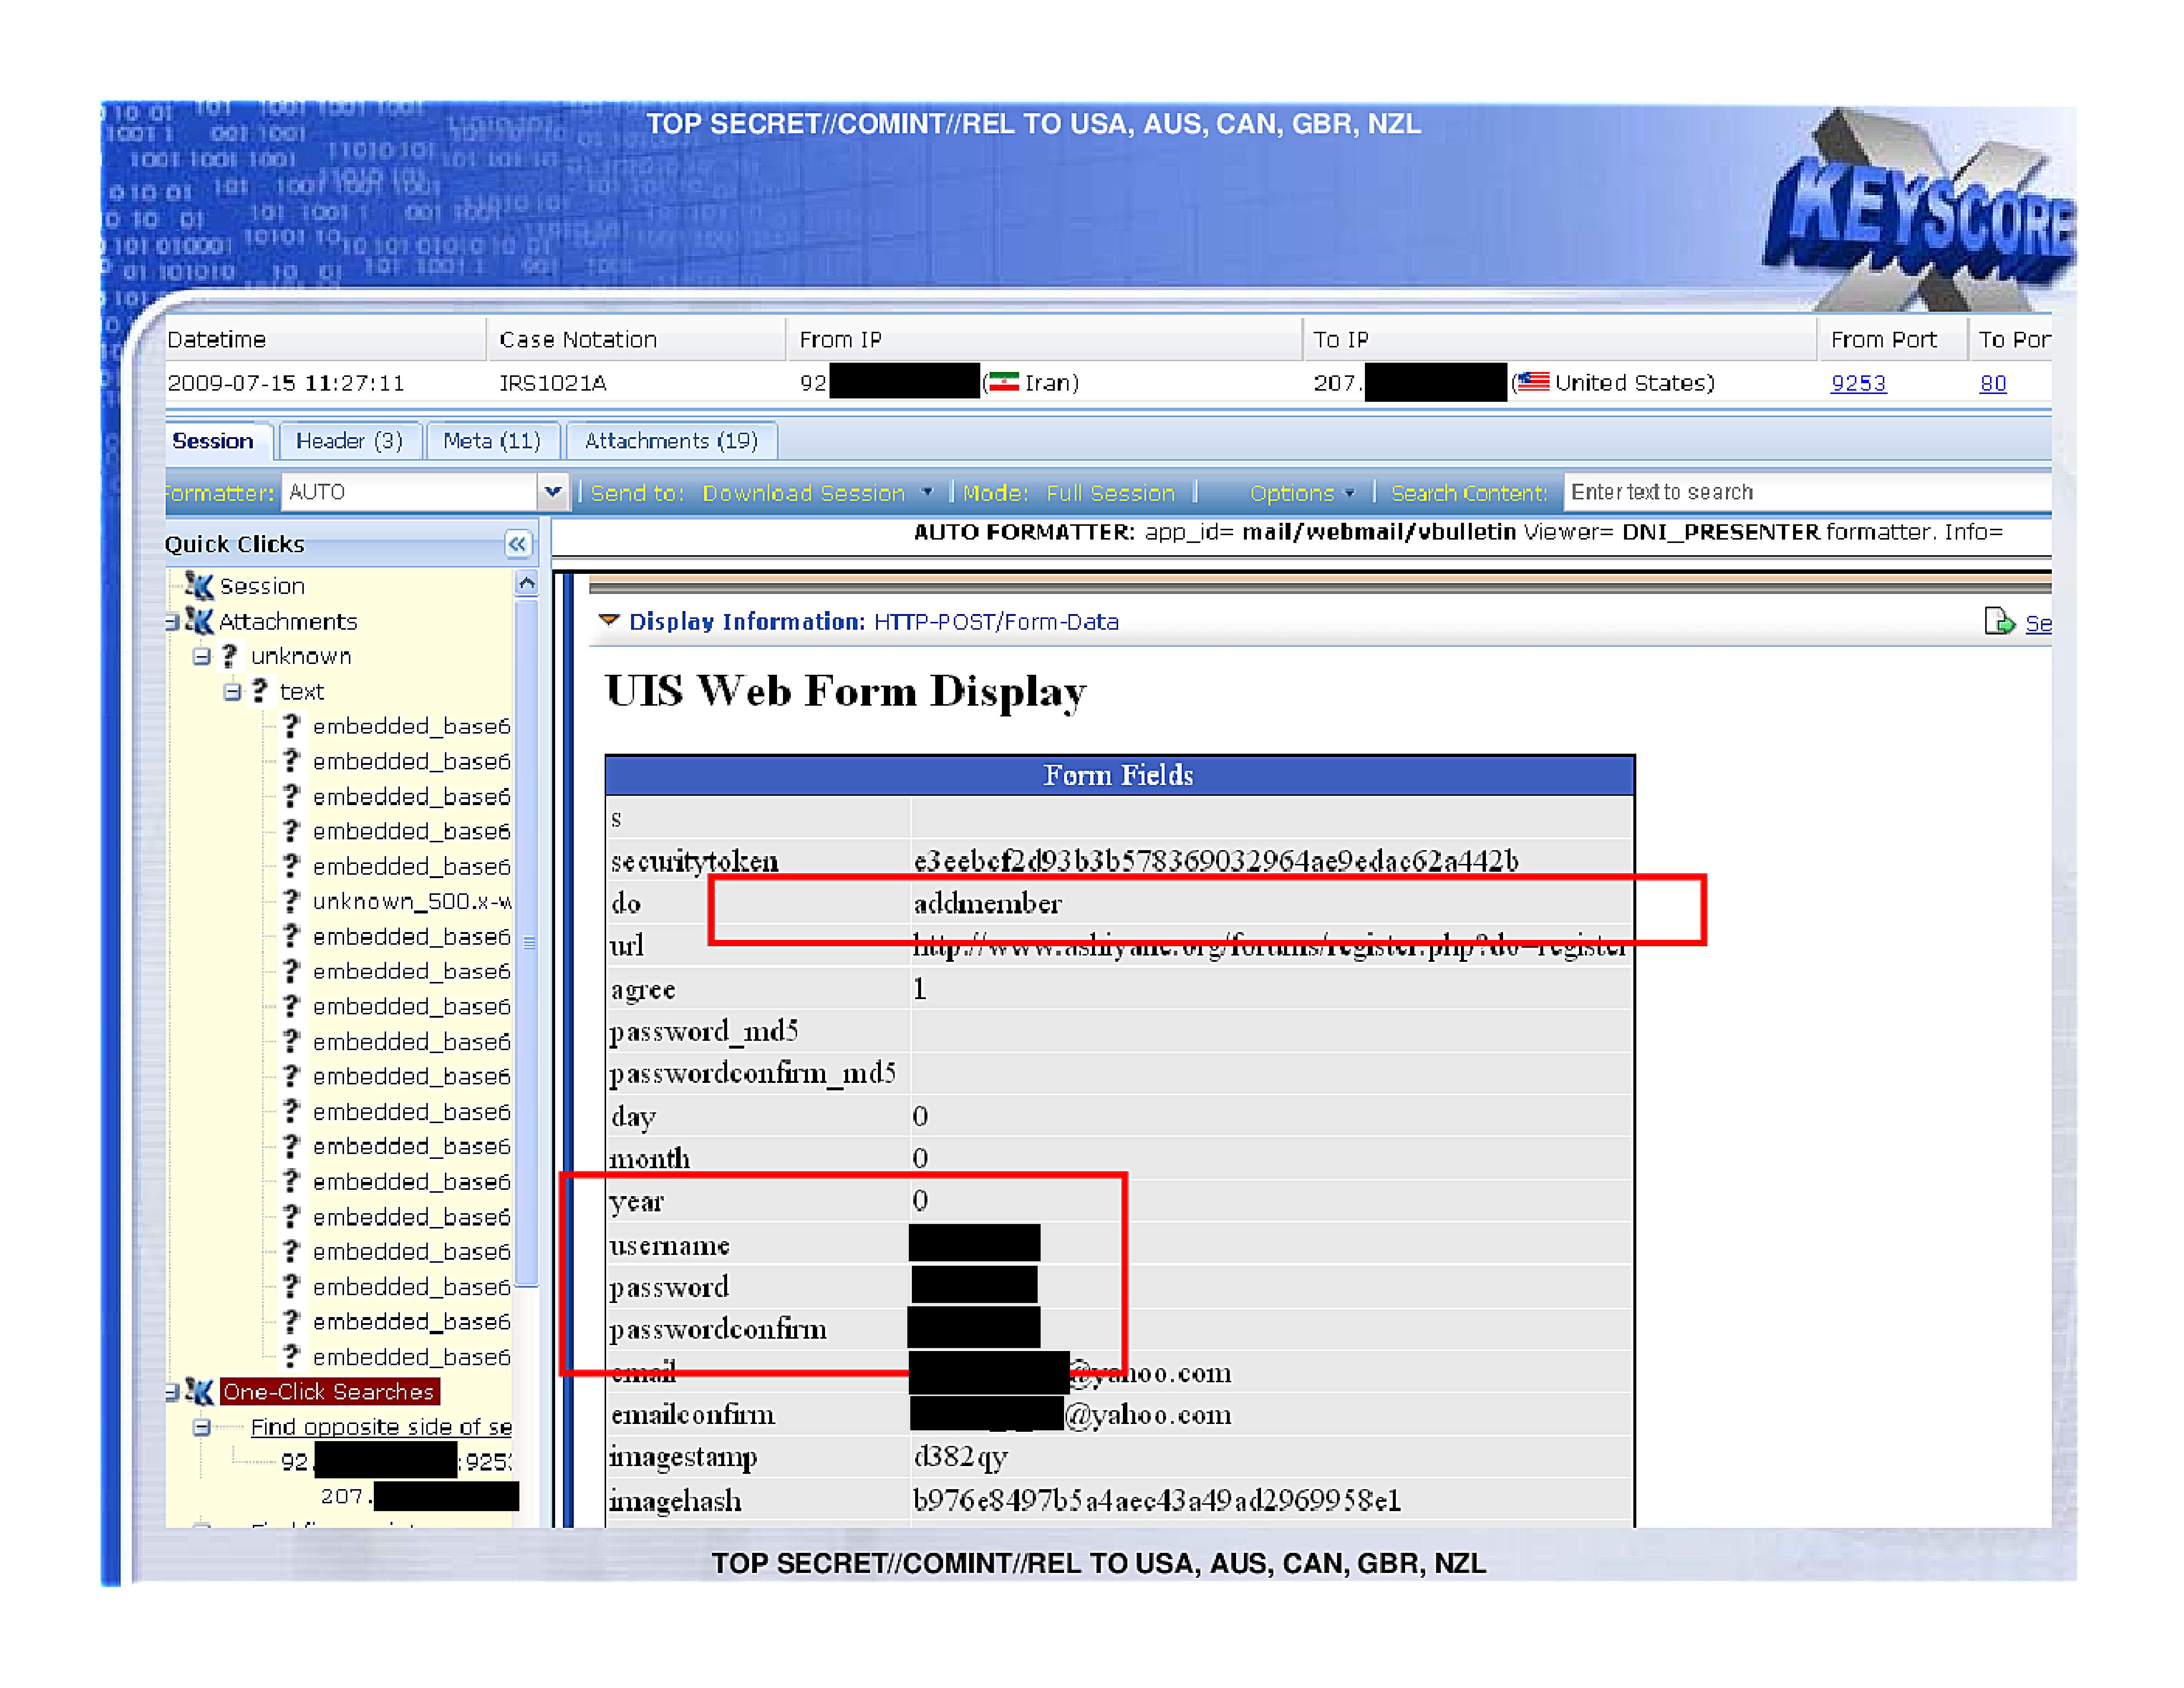
Datetime | Case Notation | From IP | To IP | From Port | To Por
2009-07-15 11:27:11 | IRS1021A | 92[REDACTED] (Iran) | 207.[REDACTED] (United States) | 9253 | 80

Session | Header (3) | Meta (11) | Attachments (19)
Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to search

Quick Clicks
Session
* Attachments
   * unknown
      * text
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * unknown_500.x-w
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
         * embedded_base6
* One-Click Searches
   * Find opposite side of se
      * 92.[REDACTED]:925
         * 207.[REDACTED]

AUTO FORMATTER: app_id=mail/webmail/vbulletin Viewer= DNI_PRESENTER formatter. Info=

Display Information: HTTP-POST/Form-Data Se
UIS Web Form Display
Form Fields
s
securitytoken e3eebcf2d93b3b578369032964ae9edac62a442b
do addmember
url http://www.ashiyane.org/forums/register.php?do=register
agree 1
password_md5
passwordconfirm_md5
day 0
month 0
year 0
username [REDACTED]
password [REDACTED]
passwordconfirm [REDACTED]
email [REDACTED]@yahoo.com
emailconfirm [REDACTED]@yahoo.com
imagestamp d382qy
imagehash b976e8497b5a4aec43a49ad2969958e1
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Agenda
- What TAO needs from analysts
- TELNET Sessions in XKS
- FTP Sessions in XKS
- Identifying Browers
- Web Forum Logins / Passwords
- Webmail Logins / Passwords
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Webmail Logins – Why?
- Masquerade as user and read mail
- Useful, but secondary to...
- Potentially use Login/PW to get full access to web server itself
- Port 80 is useful but...
- Port 3000 has XDaemon traffic (woo hoo! Let's take a look)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
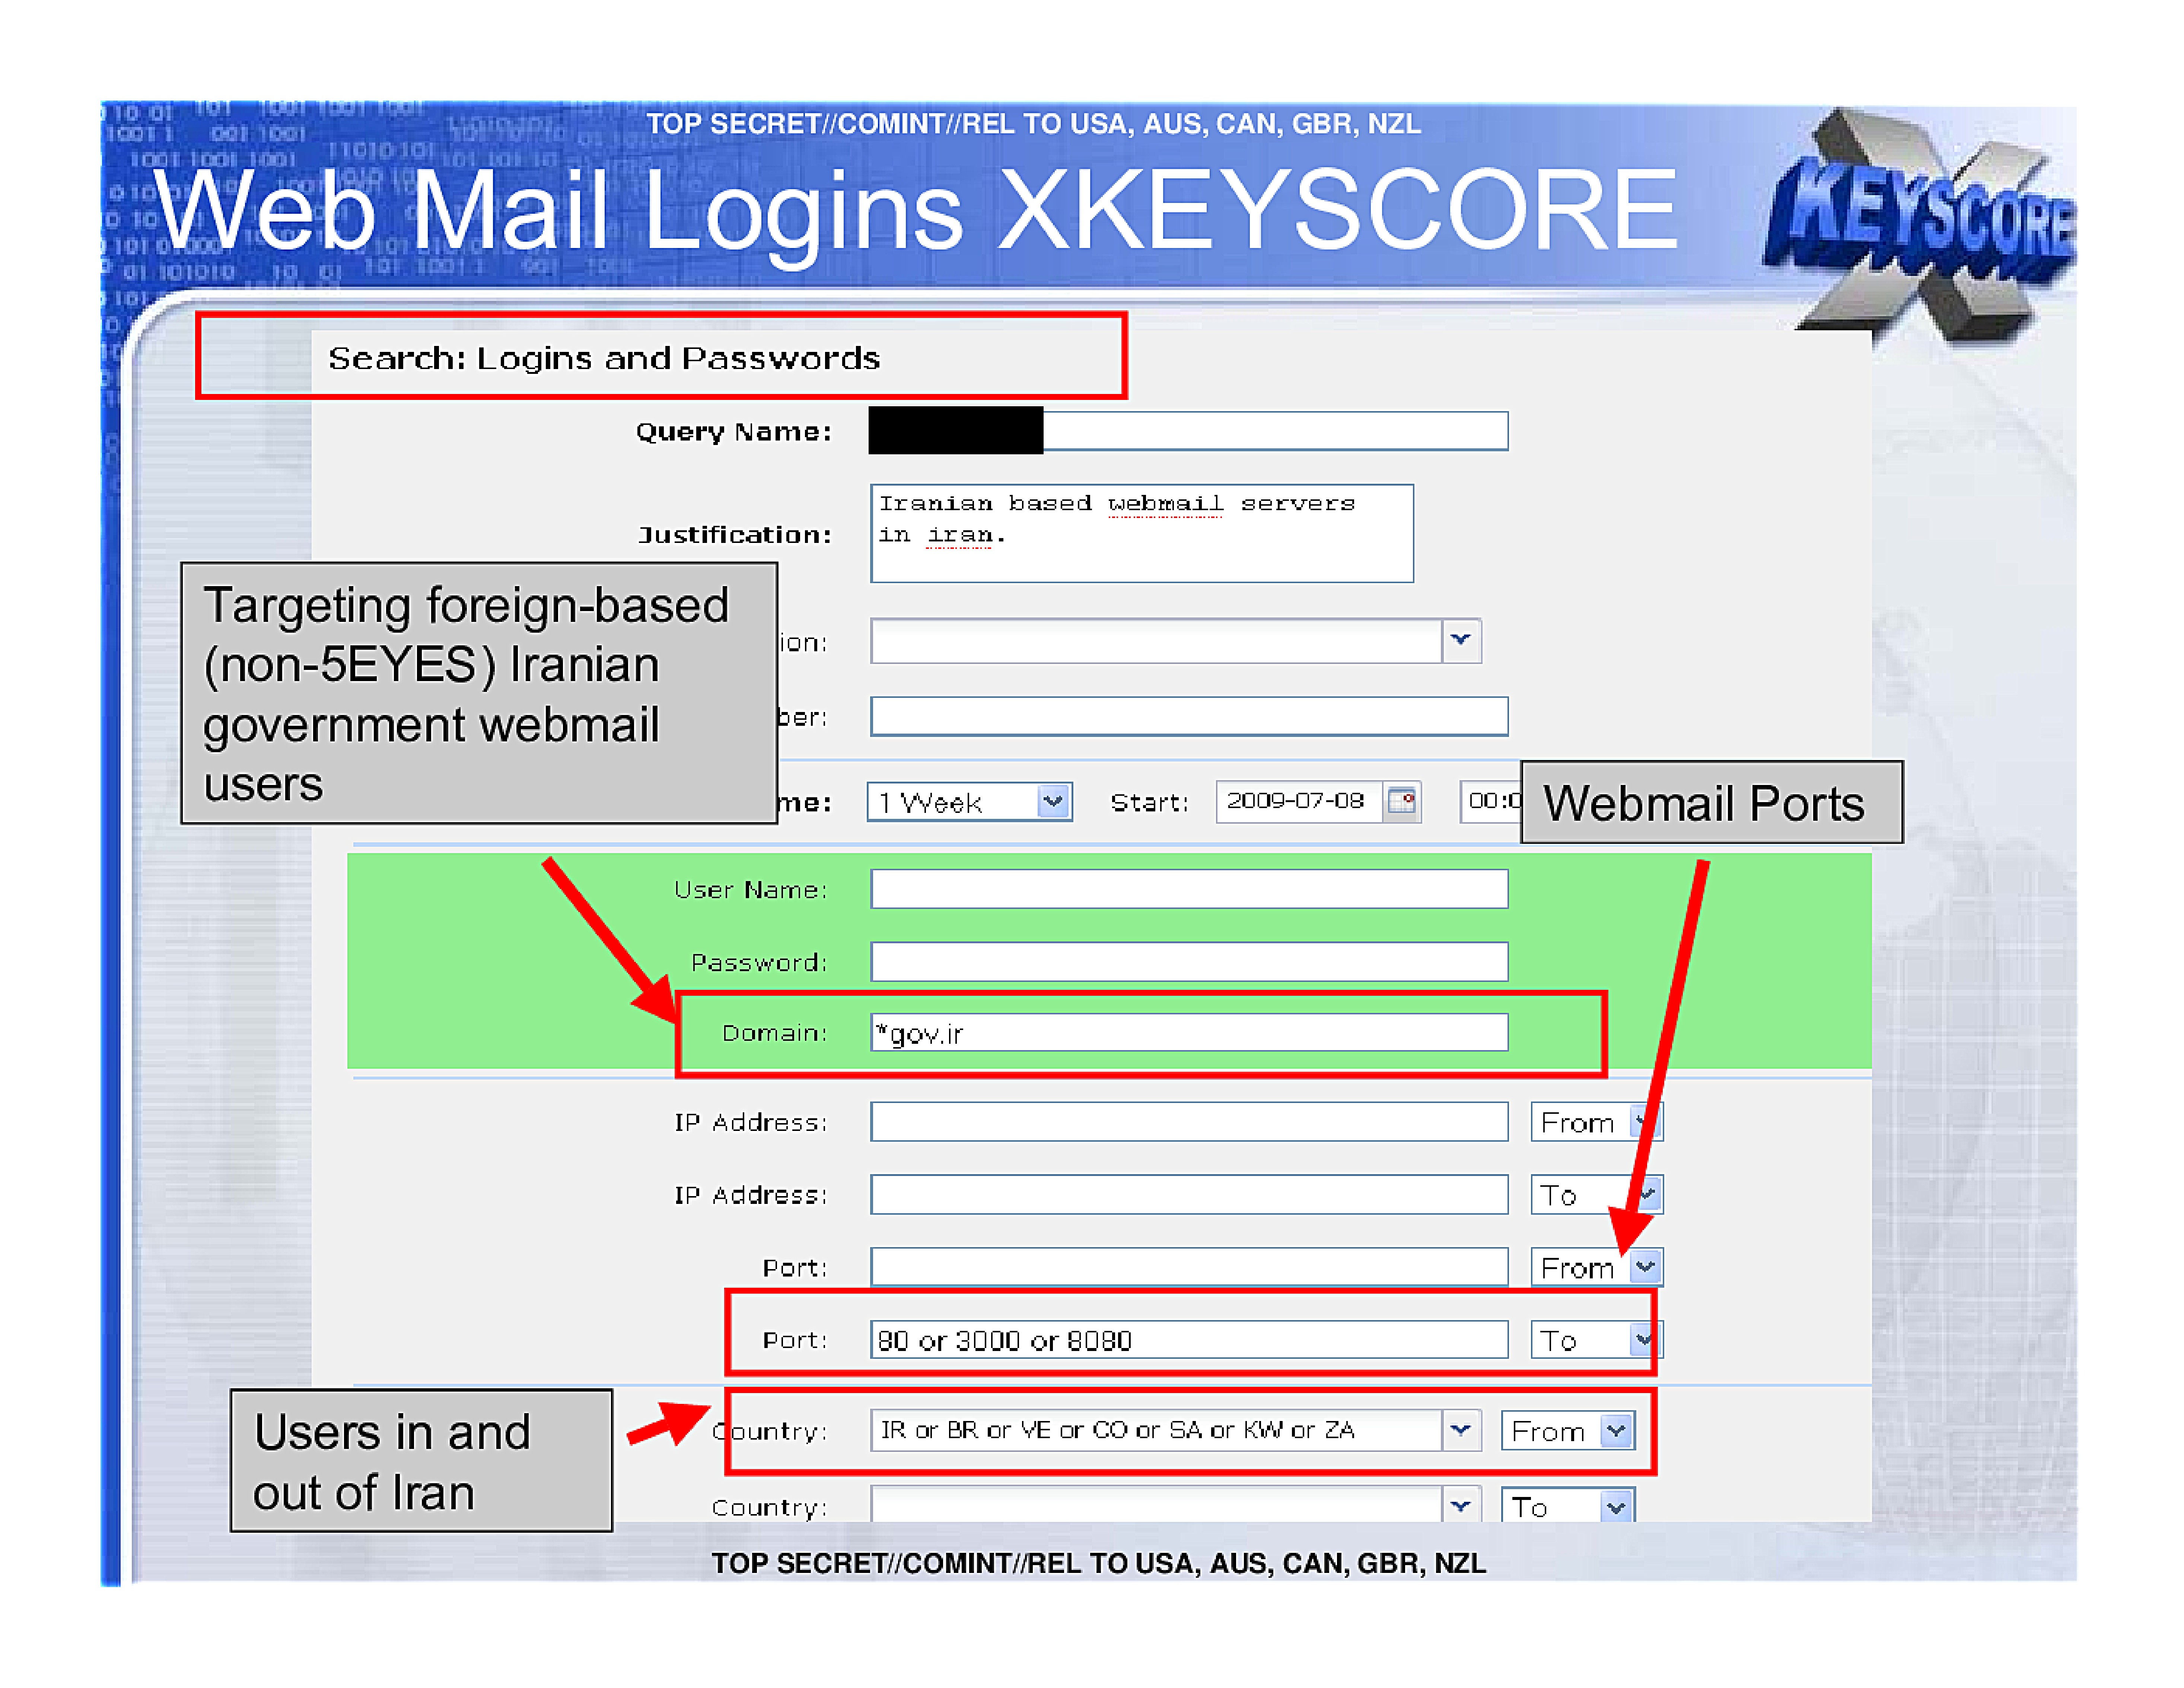
Web Mail Logins XKEYSCORE
Targeting foreign-based (non-5EYES) Iranian government webmail users

Webmail Ports

Users in and out of Iran

Search: Logins and Passwords
Query Name: [REDACTED]
Justification: Iranian based webmail servers in iran.
ion:
er:
me: 1 Week Start: 2009-07-08 00:0
User Name:
Password:
Domain: *gov.ir
IP Address: From
IP Address: To
Port: From
Port: 80 or 3000 or 8080 To
Country: IR or BR or VE or CO or SA or KW or ZA From
Country To
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
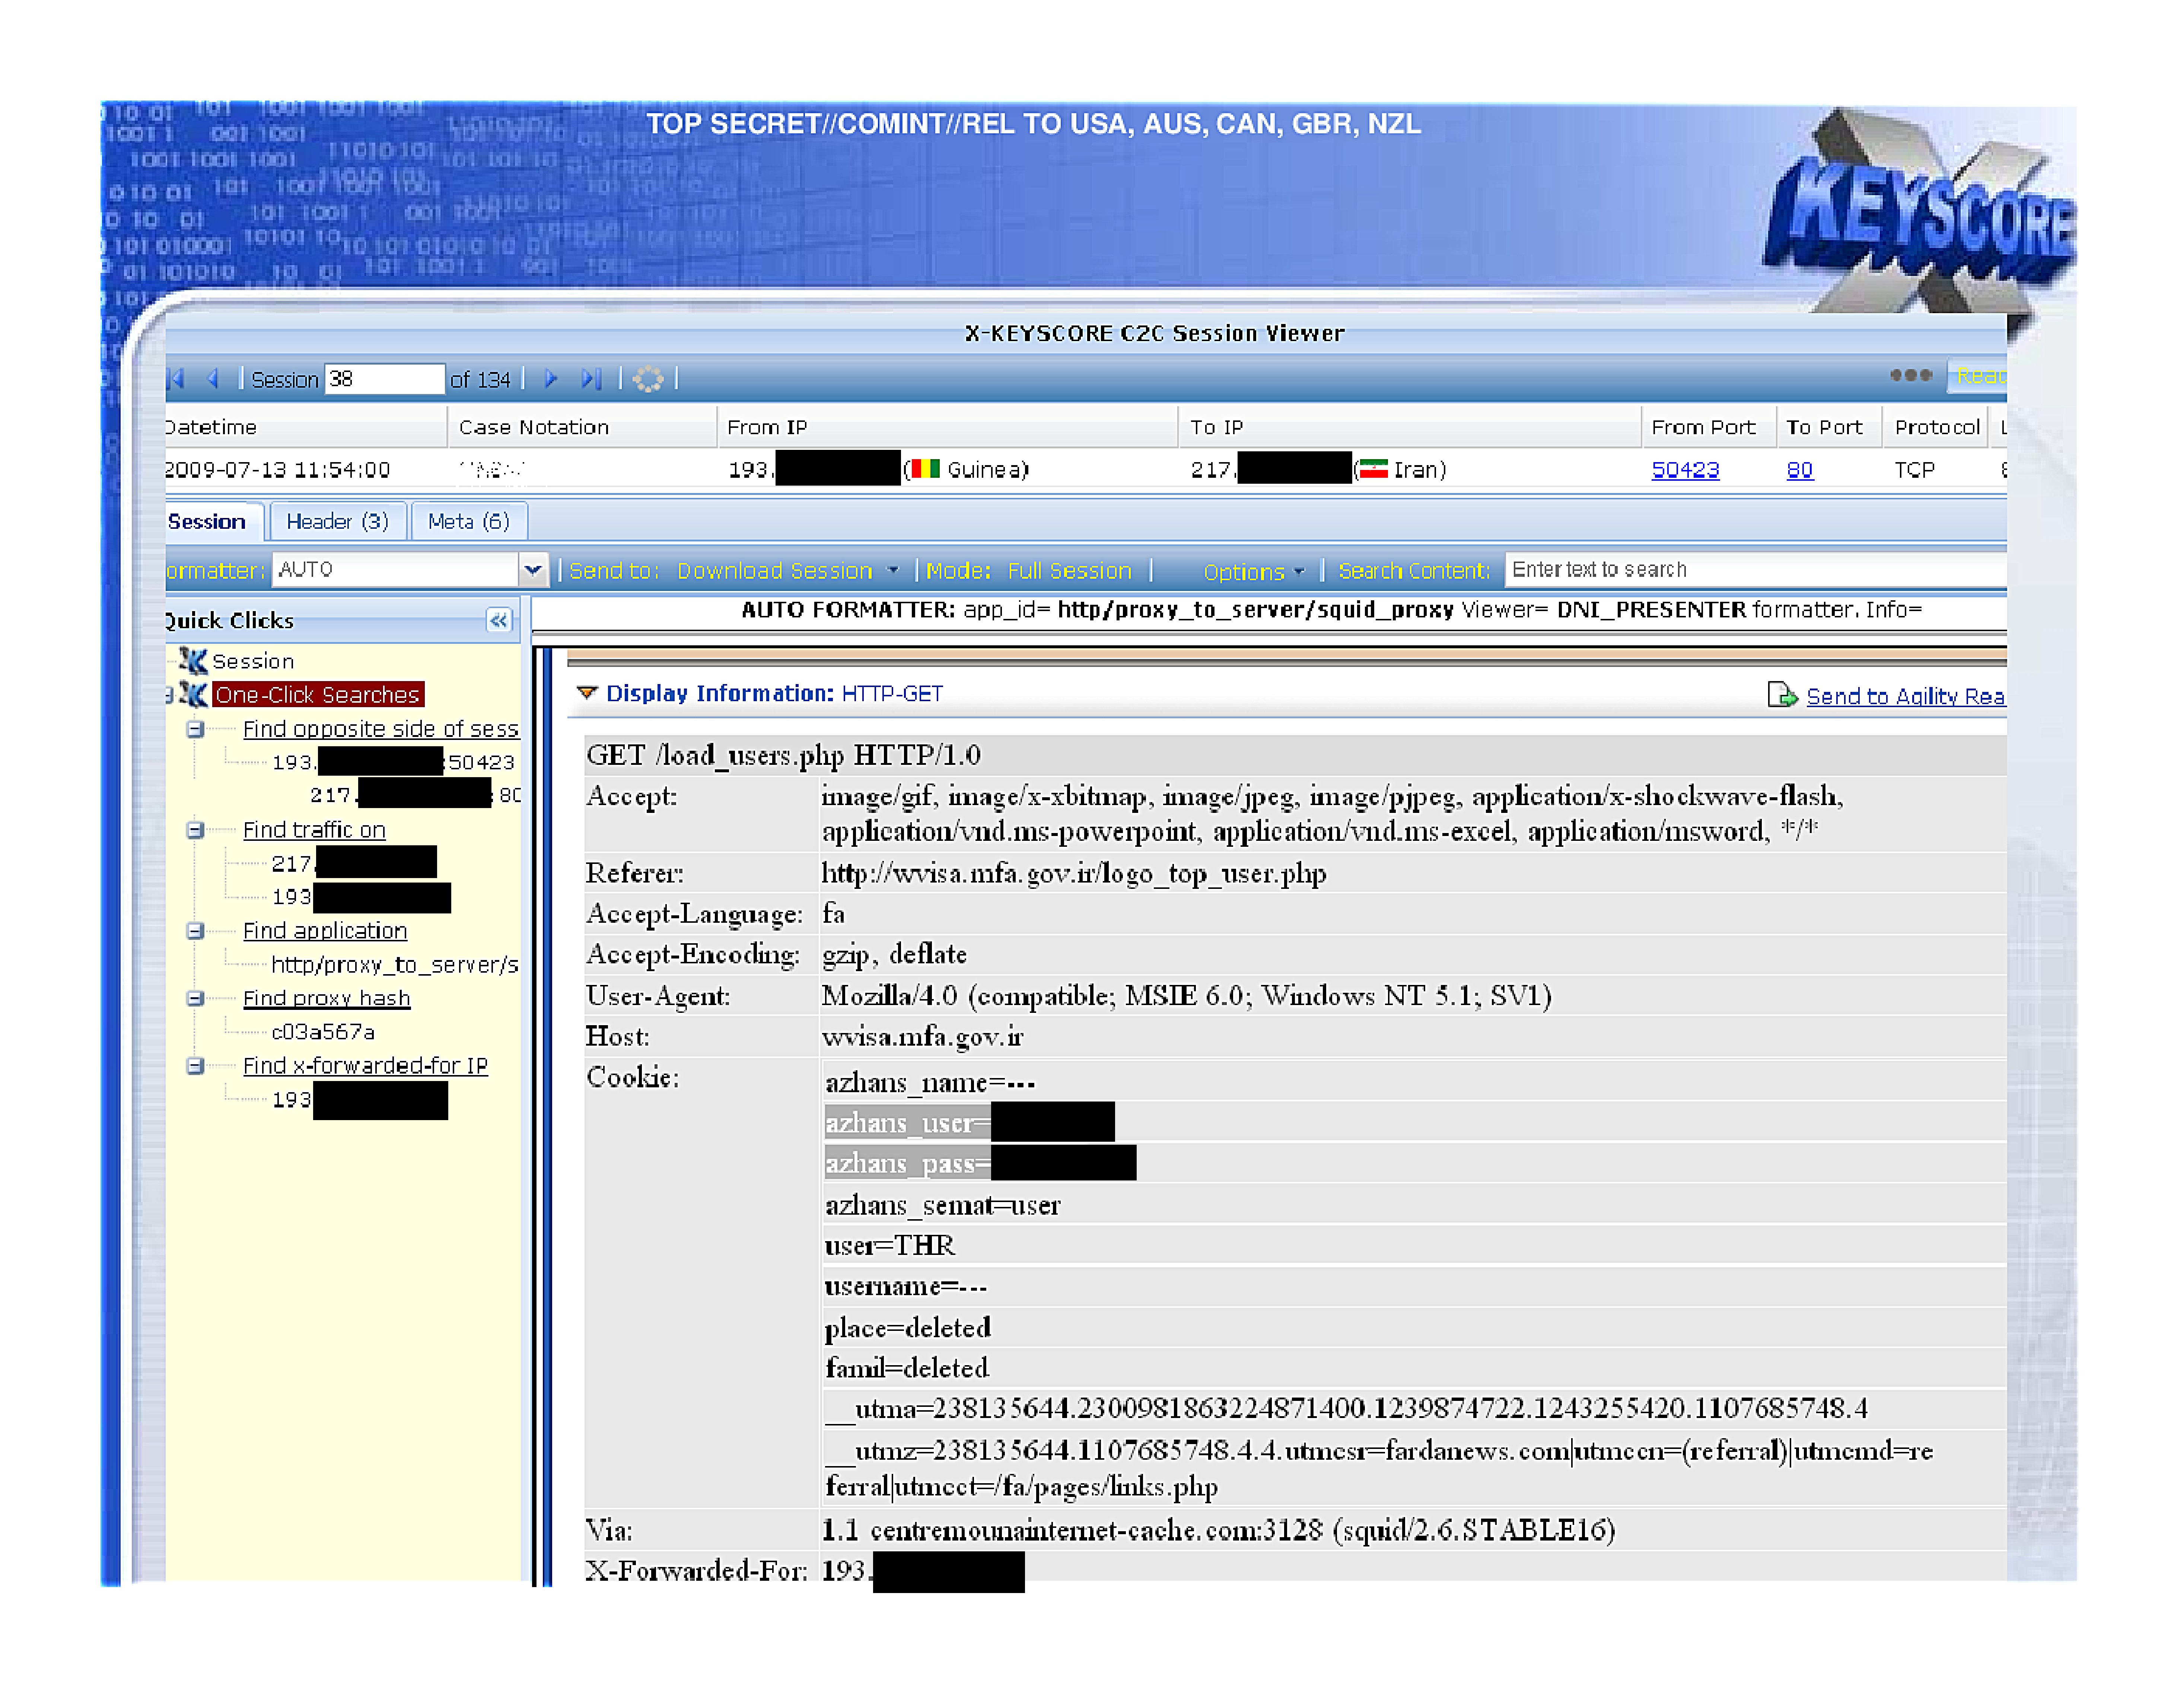
Session 38 of 134 Read
Datetime | Case Notation | From IP | To IP | From Port | To Port | Protocol |
2009-07-13 11:54:00 | [REDACTED] | 193.[REDACTED] (Guinea) | 217.[REDACTED] (Iran) | 50423 | 80 | TCP |
Session | Header (3) | Meta (6)
ormatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to search

Quick Clicks
Session
One-Click Seachers
   * Find opposite side of sess
      * 193.[REDACTED]:50423
         * 217.[REDACTED]:80
   * Find traffic on
      * 217.[REDACTED]
      * 193.[REDACTED]
   * Find application
      * http/proxy_to_server/s
   * Find proxy hash
      * c03a567a
   * Find x-forwarded-for IP
      * 193[REDACTED]

AUTO FORMATTER: app_id=http/proxy_to_server/squid_proxy Viewer=DNI_PRESENTER formatter.Info=

Display Information: HTTP-GET
GET /load_users.php HTTP/1.0
Accept: image/gif, image/x-xbitmap, image/jpeg, image/pjpeg, application/x-shockwave-flash,
application/vnd.ms-powerpoint, application/vnd.ms-excel, application/msword, */*
Referer: http://wvisa.mfa.gov.ir/logo_top_user.php
Accept-Language: fa
Accept-Encoding: gzip, deflate
User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SV1)
Host: wvisa.mfa.gov.ir
Cookie: azhans_name=...
azhans_user=[REDACTED]
azhans_pass=[REDACTED]
azhans_semat=user
user=THR
username=---
place=deleted
famil=deleted
_utma=238135644.2300981863224871400.1239874722.1243255420.1107685748.4
_utmz=238135644.1107685748.4.4.utmcsr=fardanews.com|utmccn=(referral)|utmcmd=re
ferral|utmcct=/fa/pages/links.php
Via: 1.1 centremounainternet-cache.com:3128 (squid/2.6.STABLE16)
X-Forwarded-For: 193.[REDACTED]
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Webmail Logins
- More webmail examples...
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
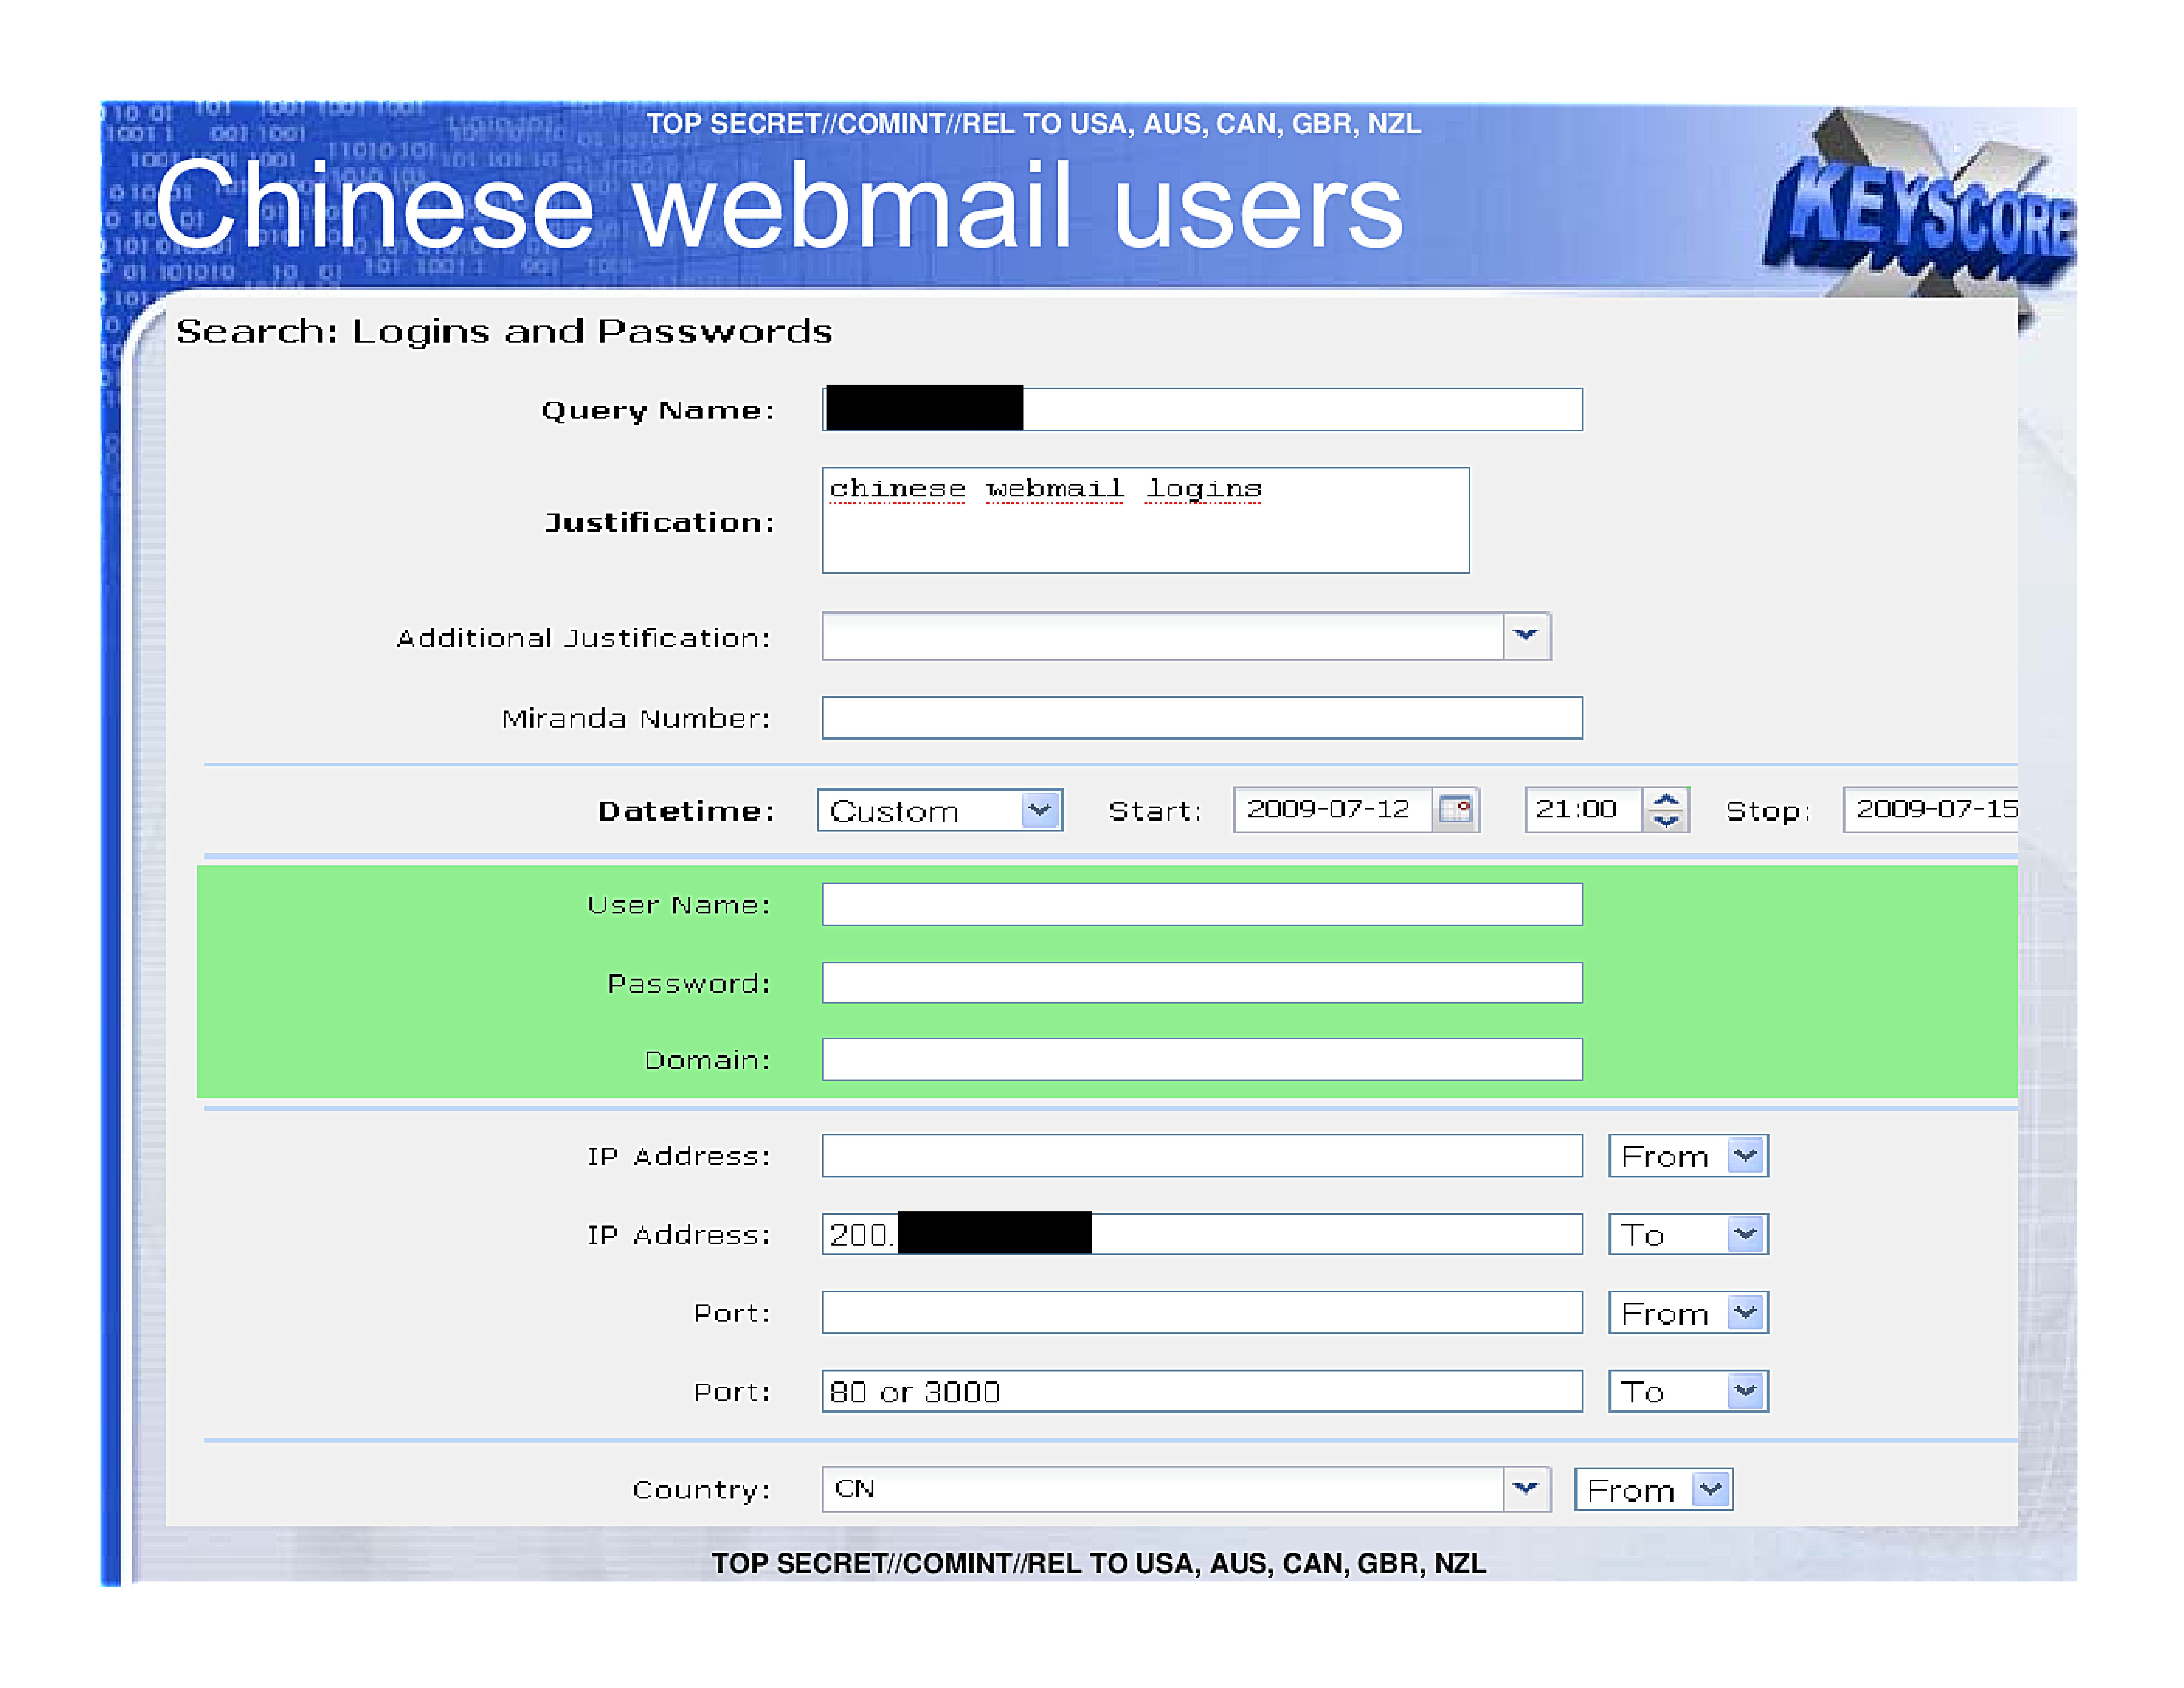
Chinese webmail users
Search: Logins and Passwords
Query Name: [REDACTED]
Justification: chinese webmail logins
Additional Justification:
Miranda Number:

Datetime: Custom Start: 2009-07-12 21:00 Stop: 2009-07-15

User Name:
Password:
Domain:

IP Address: From
IP Address: 200.[REDACTED] To
Port:
Port: 80 or 3000 To
Country: CN From
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
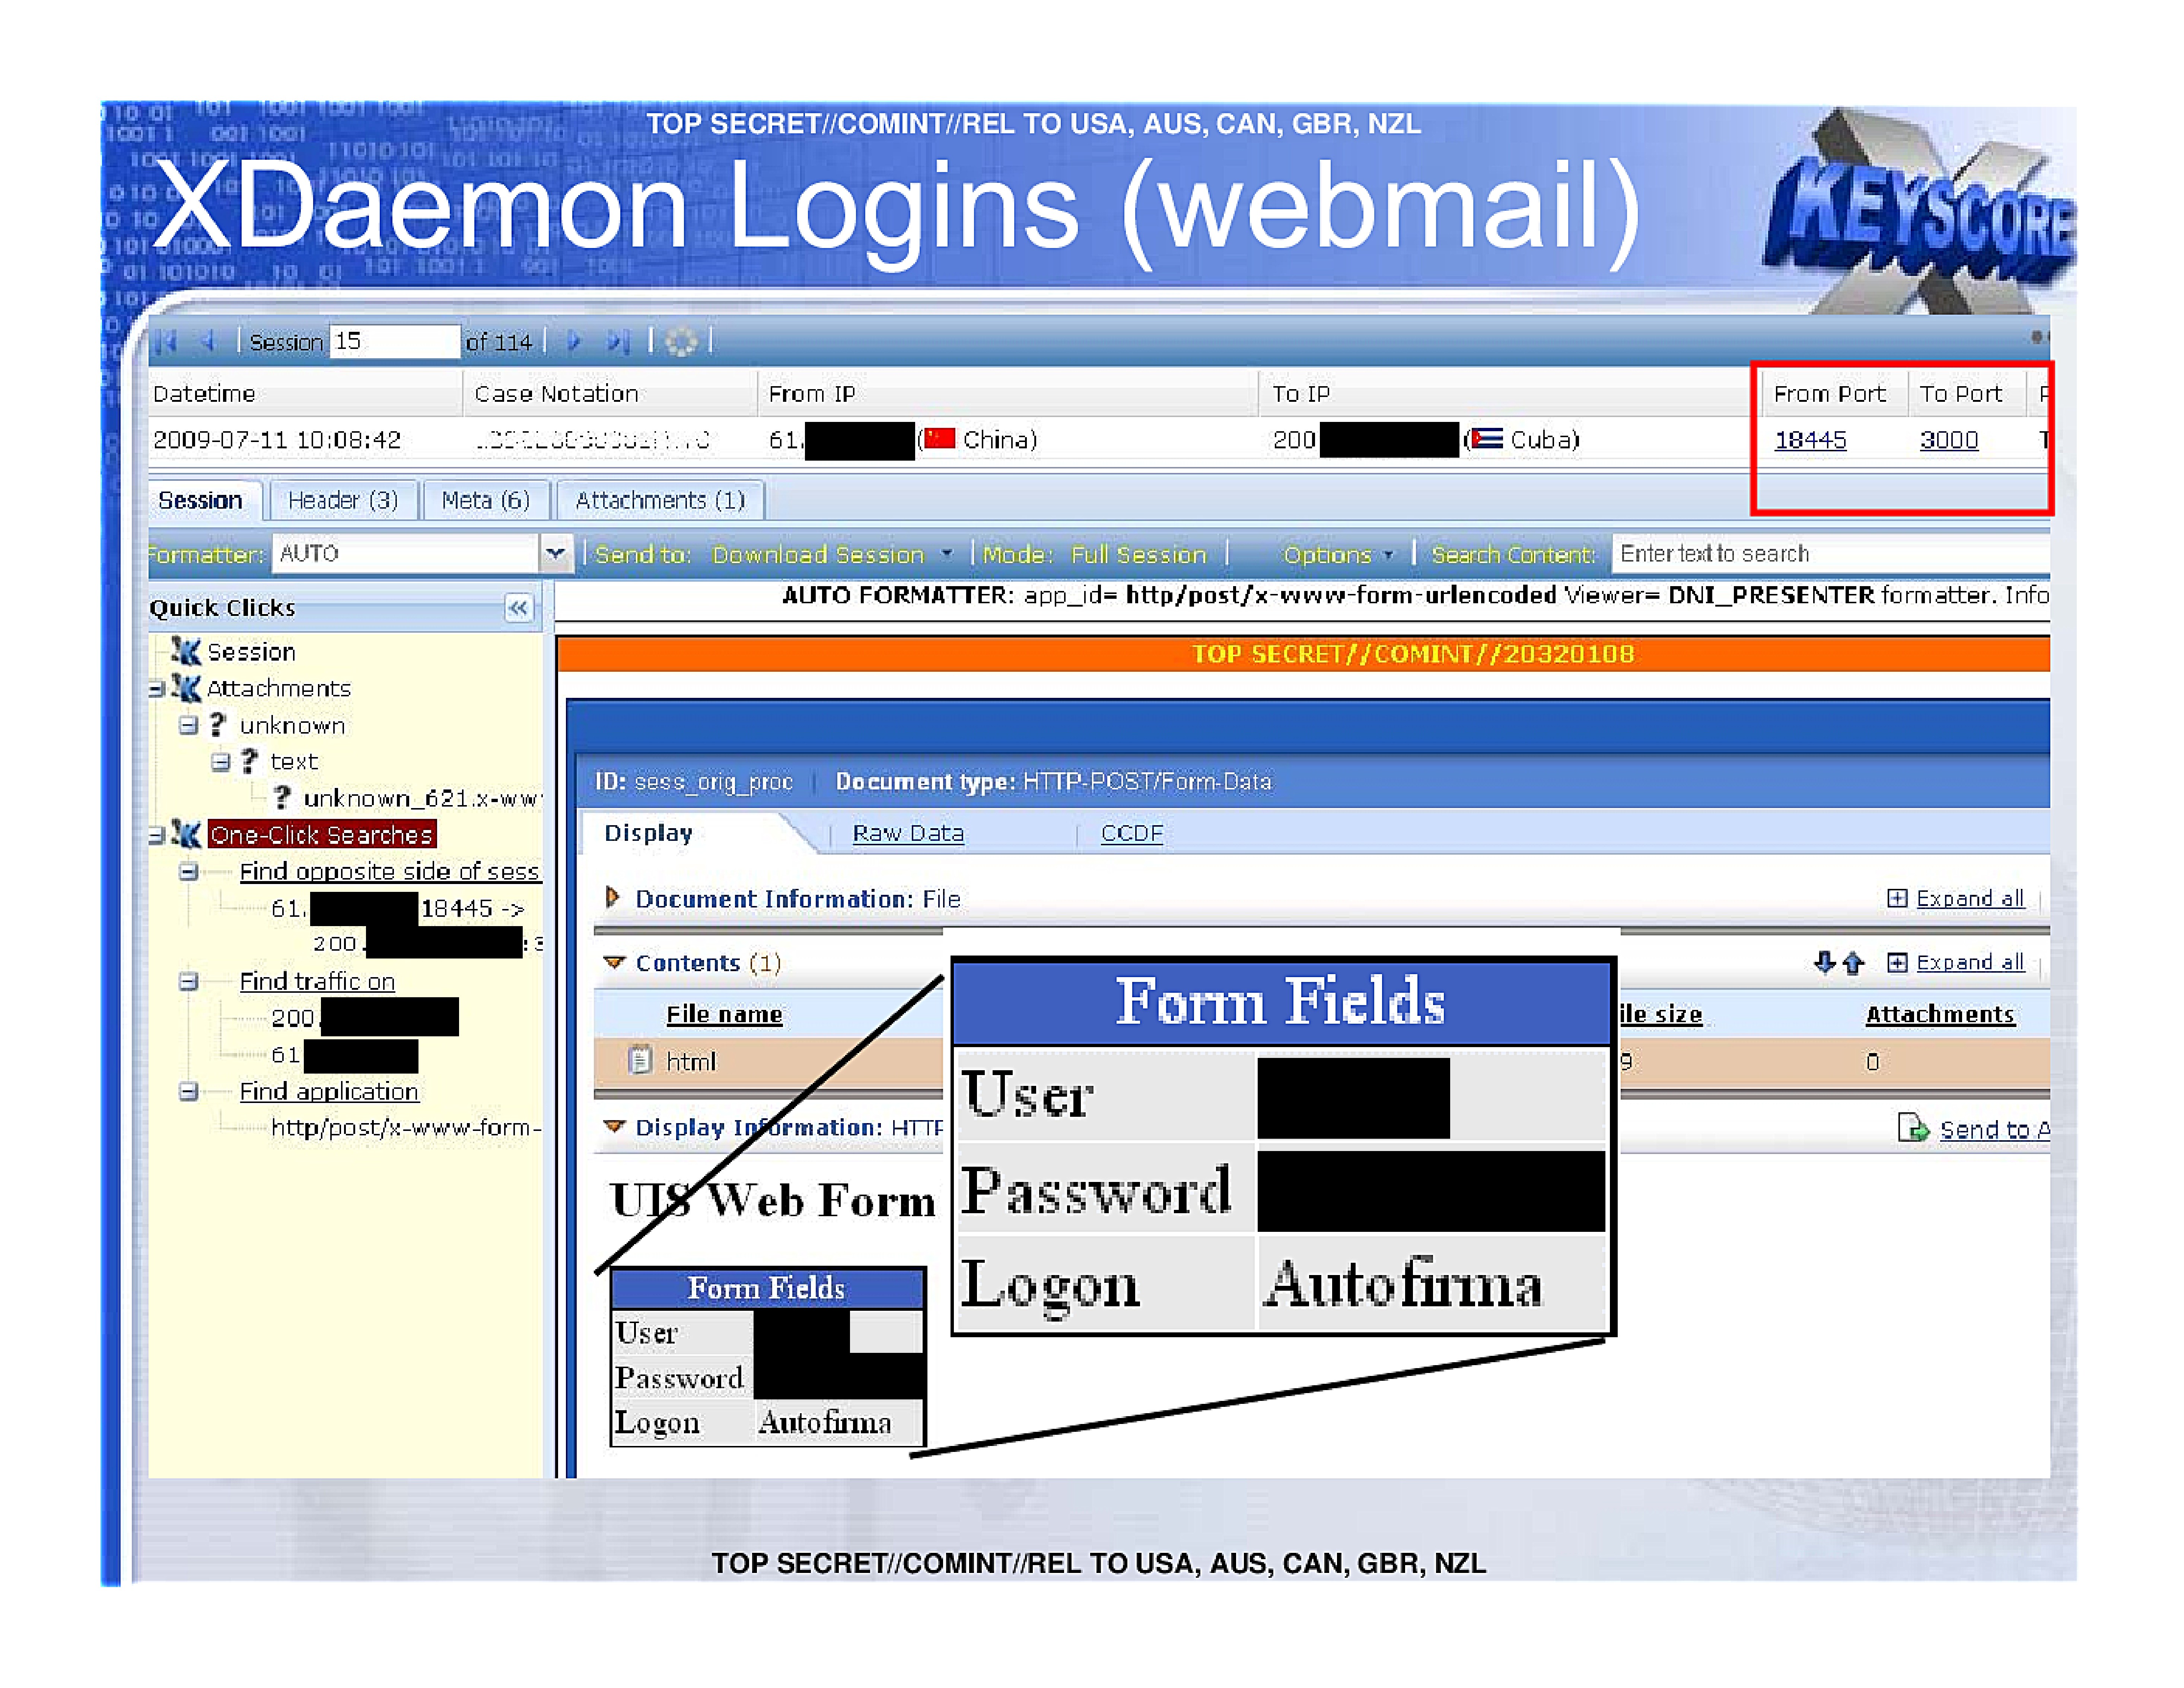
XDaemon Logins (webmail)
Session 15 of 114
Datetime | Case Notation | From IP | To IP | From Port | To Port |
2009-07-11 10:08:42 | [REDACTED] | 61.[REDACTED] (China) | 200.[REDACTED] (Cuba) | 18445 | 3000 |

Session | Header (3) | Meta (6) | Attachments (1) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Contents Enter text to search

Quick Clicks
*   Session
*   Attachments
     *   unknown
        *   text
           *   unknown_621.x-ww
*   One-Click Searches
     *   Find opposite side of sess
        * 61.[REDACTED]18445 ->
           * 200.[REDACTED]:3
        *   Find traffic on: 200.***.***.***, 61.***.***.***
     *   Find application
        * http/post/x-www-form-

AUTO FORMATTER: app_id= http/post/x-www-form-urlencoded Viewer= DNI_PRESENTER formatter. Info=

TOP SECRET//COMINT//20320108
ID: sess_orig_proc | Document type: HTTP-POST/Form-Data
Display Information: HTTP-POST/Form-Data
Display | Raw Data | CCDF
Document Information: File Expand All
Contents
File name ile size Attachments
html 9 0
UIS Web Form
Form Fields
User [REDACTED]
Password [REDACTED]
Logon Autofirma

Form Fields
User [REDACTED]
Password [REDACTED]
Logon Autofirma
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
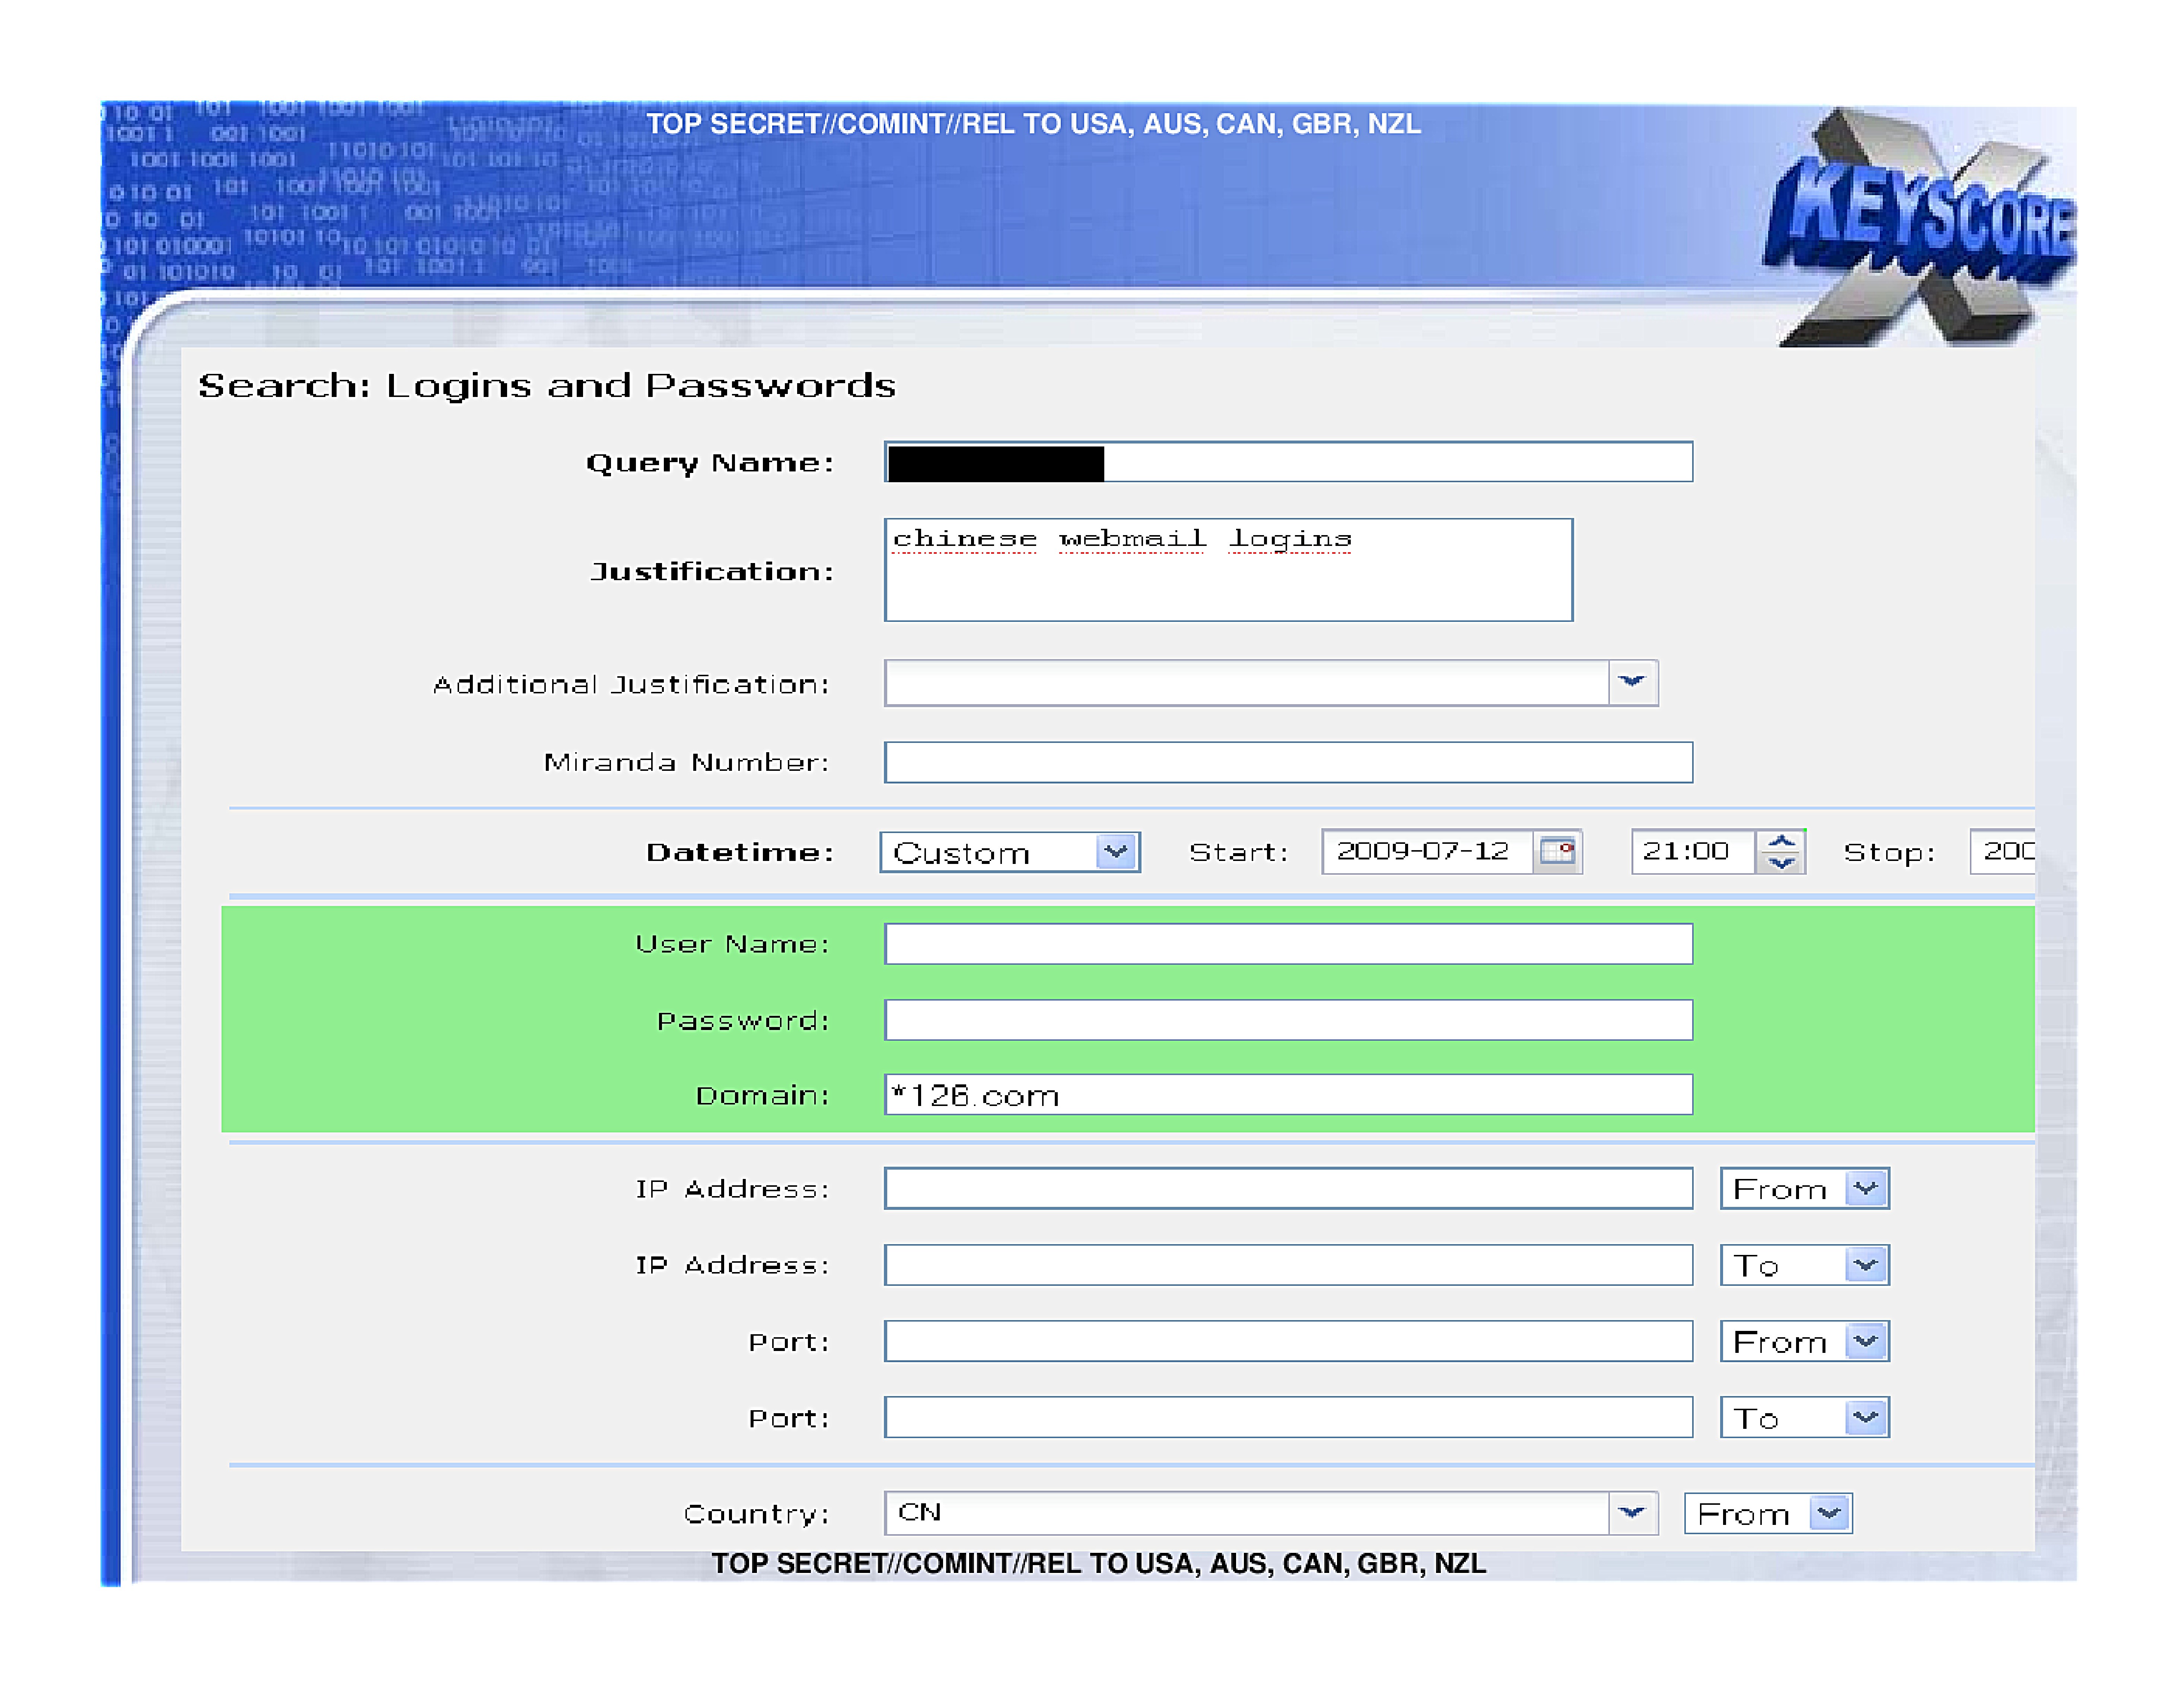
Search: Logins and Passwords
Query Name: [REDACTED]
Justification: chinese webmail logins
Additional Justification:
Miranda Number:

Datetime: Custom Start: 2009-07-12 21:00 Stop: 200

User Name:
Password:
Domain: *126.com

IP Address: From
IP Address: To
Port: From
Port: To
Country: CN From
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
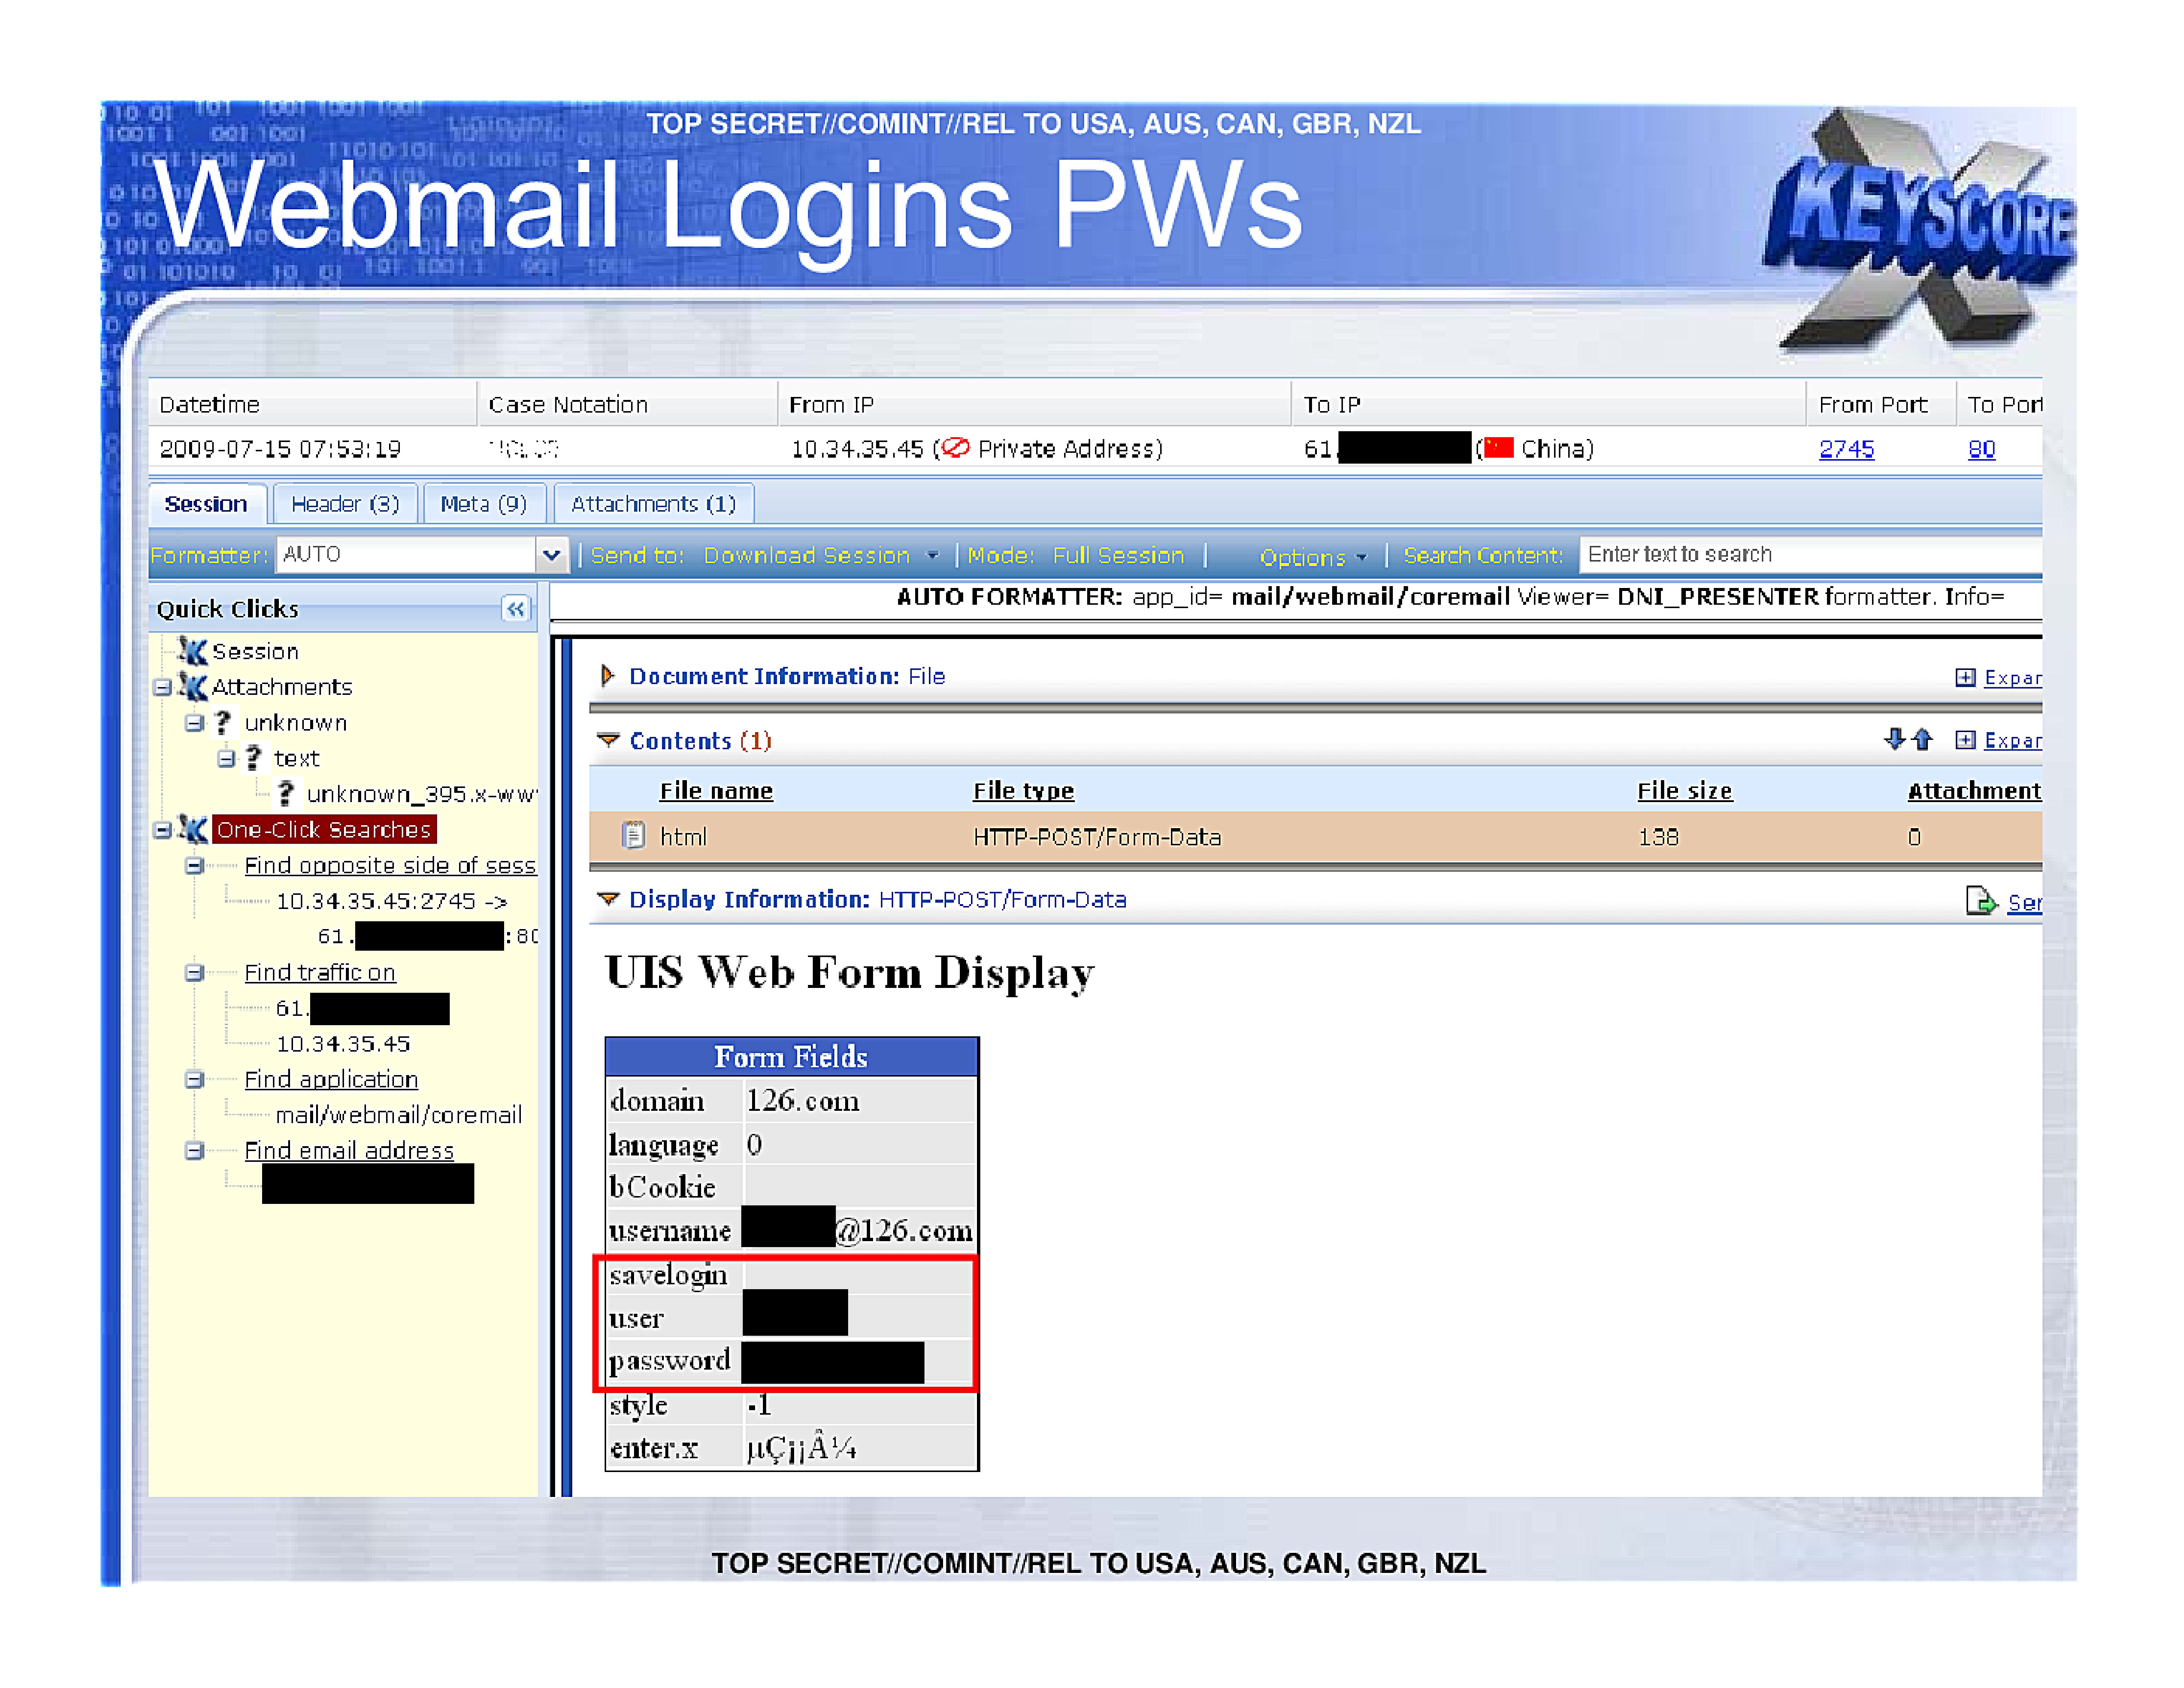
Webmail Logins PWs
| Datetime | Case Notation | From IP | To IP | From Port | To Port |
| 2009-07-15 07:53:19 | [REDACTED] | 10.34.35.45 (Private Address) | 61.[REDACTED] (China) | 2745 | 80 |

Session | Header (3) | Meta (9) | Attachments (1) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to search

Quick Clicks
*   Session
*   Attachments
   *   unknown
      *   text
         *   unknown_395.x-ww
*   One-Click Searches
   *   Find opposite side of sess
      * 10.34.35.45:2745 ->
         * 61.[REDACTED]:80
   *   Find traffic on
      * 61.[REDACTED]
      * 10.34.35.45
   *   Find application
      * mail/webmail/coremail
   *   Find email address
      * [REDACTED]

AUTO FORMATTER: app_id= mail/webmail/coremail Viewer= DNI_PRESENTER formatter. Info=

Document Information: File
Contents (1)
File name | File type | File size | Attachment |
| html | HTTP-POST/Form-Data | 138 | 0 |

Display Information: HTTP-POST/Form-Data
UIS Web Form Display

Form Fields
| domain | 126.com |
| language | 0 |
| bCookie | |
| username | [REDACTED]@126.com |
| savelogin | |
| user | [REDACTED] |
| password | [REDACTED] |
| style | -1 |
| enter.x | µÇ¡Á |
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
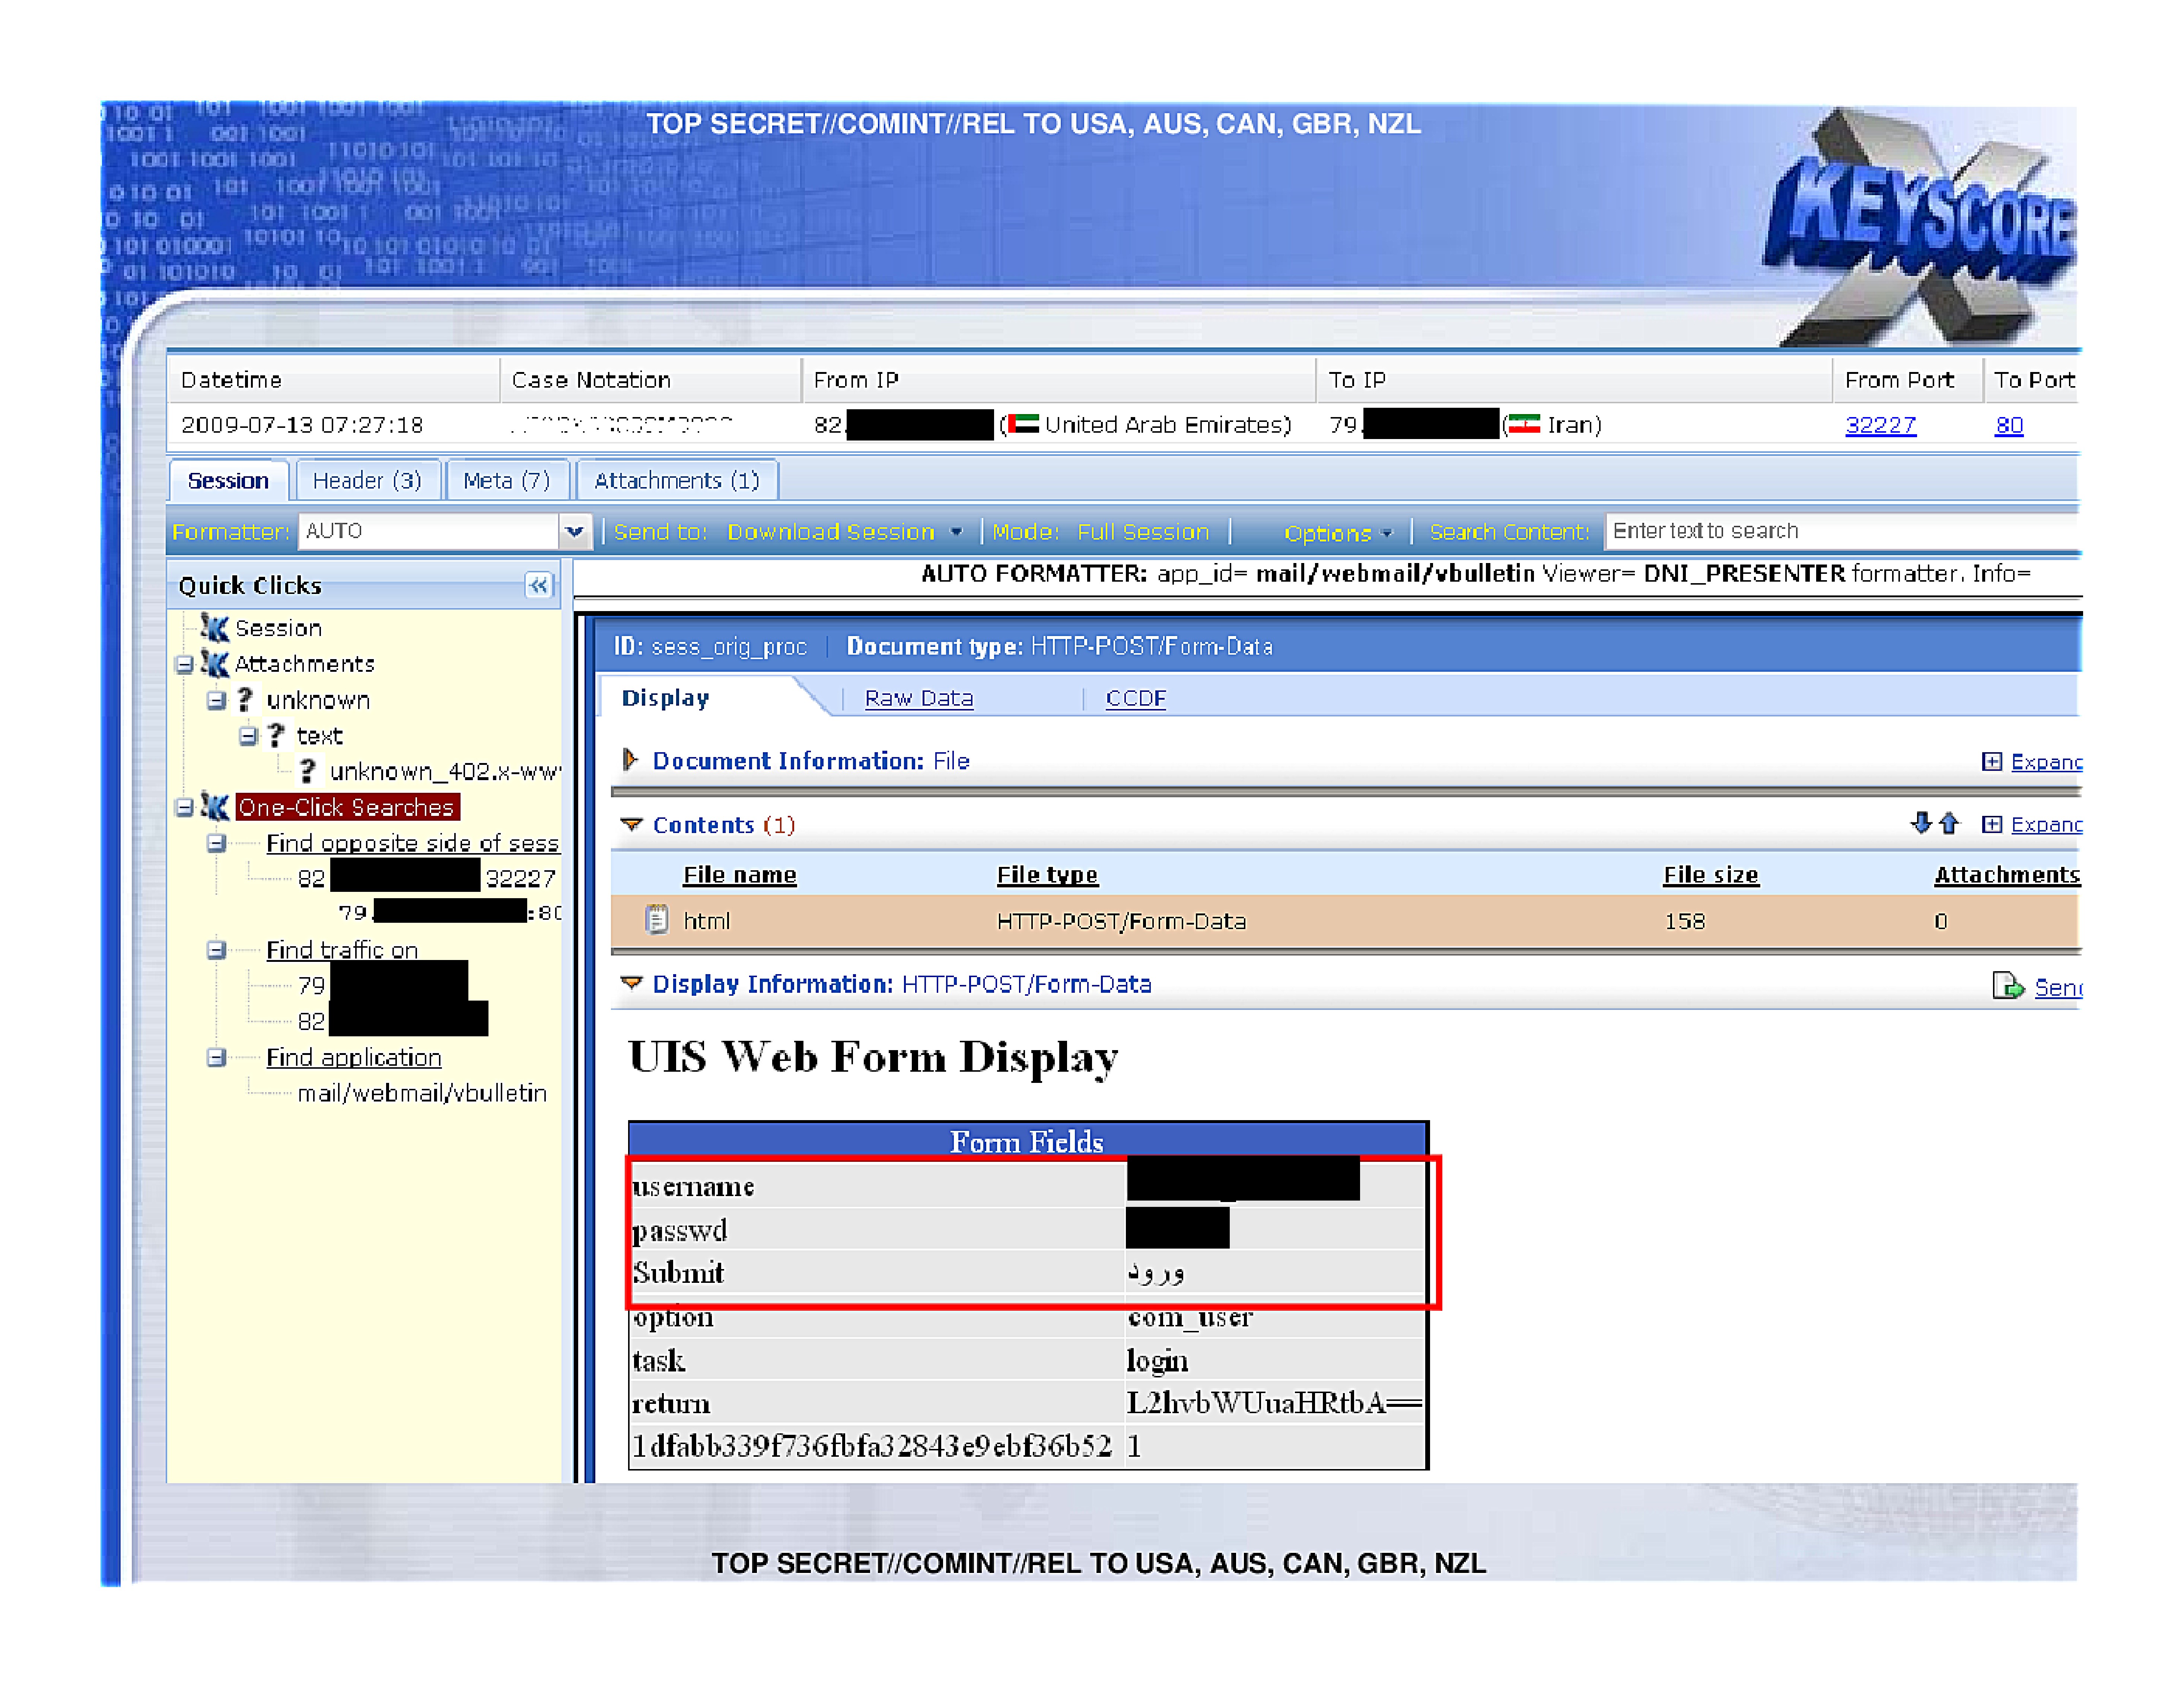
| Datetime | Case Notation | From IP | To IP | From Port | To Port |
| 2009-07-13 07:27:18 | [REDACTED] | 82[REDACTED] (United Arab Emirates) | 79[REDACTED] (Iran) | 32227 | 80 |

| Session | Header (3) | Meta (7) | Attachments (1) |

Formatter: AUTO | Send to: Download Session | Mode: Full Session | Options | Search Content: Enter text to search

Quick Clicks
*   Session
*   Attachments
   *   unknown
      *   text
         *   unknown_402.x-ww
*   One-Click Searches
   *   Find opposite side of sess
      * 82.[REDACTED]32227
         * 79.[REDACTED]:80
   *   Find traffic on
      * 79[REDACTED]
      * 82[REDACTED]
   *   Find application
      * mail/webmail/vbulletin

AUTO FORMATTER: app_id=mail/webmail/vbulletin Viewer= DNI_PRESENTER formatter. Info=

ID: sess_orig_proc | Document type: HTTP-POST/Form-Data
Display | Raw Data | CCDF

Document Information: File
Contents (1)
File name | File type | File size | Attachments |
| html | HTTP-POST/Form-Data | 158 | 0 |

Display Information: HTTP-POST/Form-Data
UIS Web Form Display

Form Fields
| username | [REDACTED] |
| passwd | [REDACTED] |
| Submit | ورود |
| option | com_user |
| task | login |
| return | L2hvbWUuaHRtbA== |
| 1dfabb339f736fbfa32843e9ebf36b52 | 1 |
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Identifying Servers
- Web Servers run particular software
- E.g. Apache, Microsoft IIS, Unix, et...
- TAO has exploits for particular ones
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
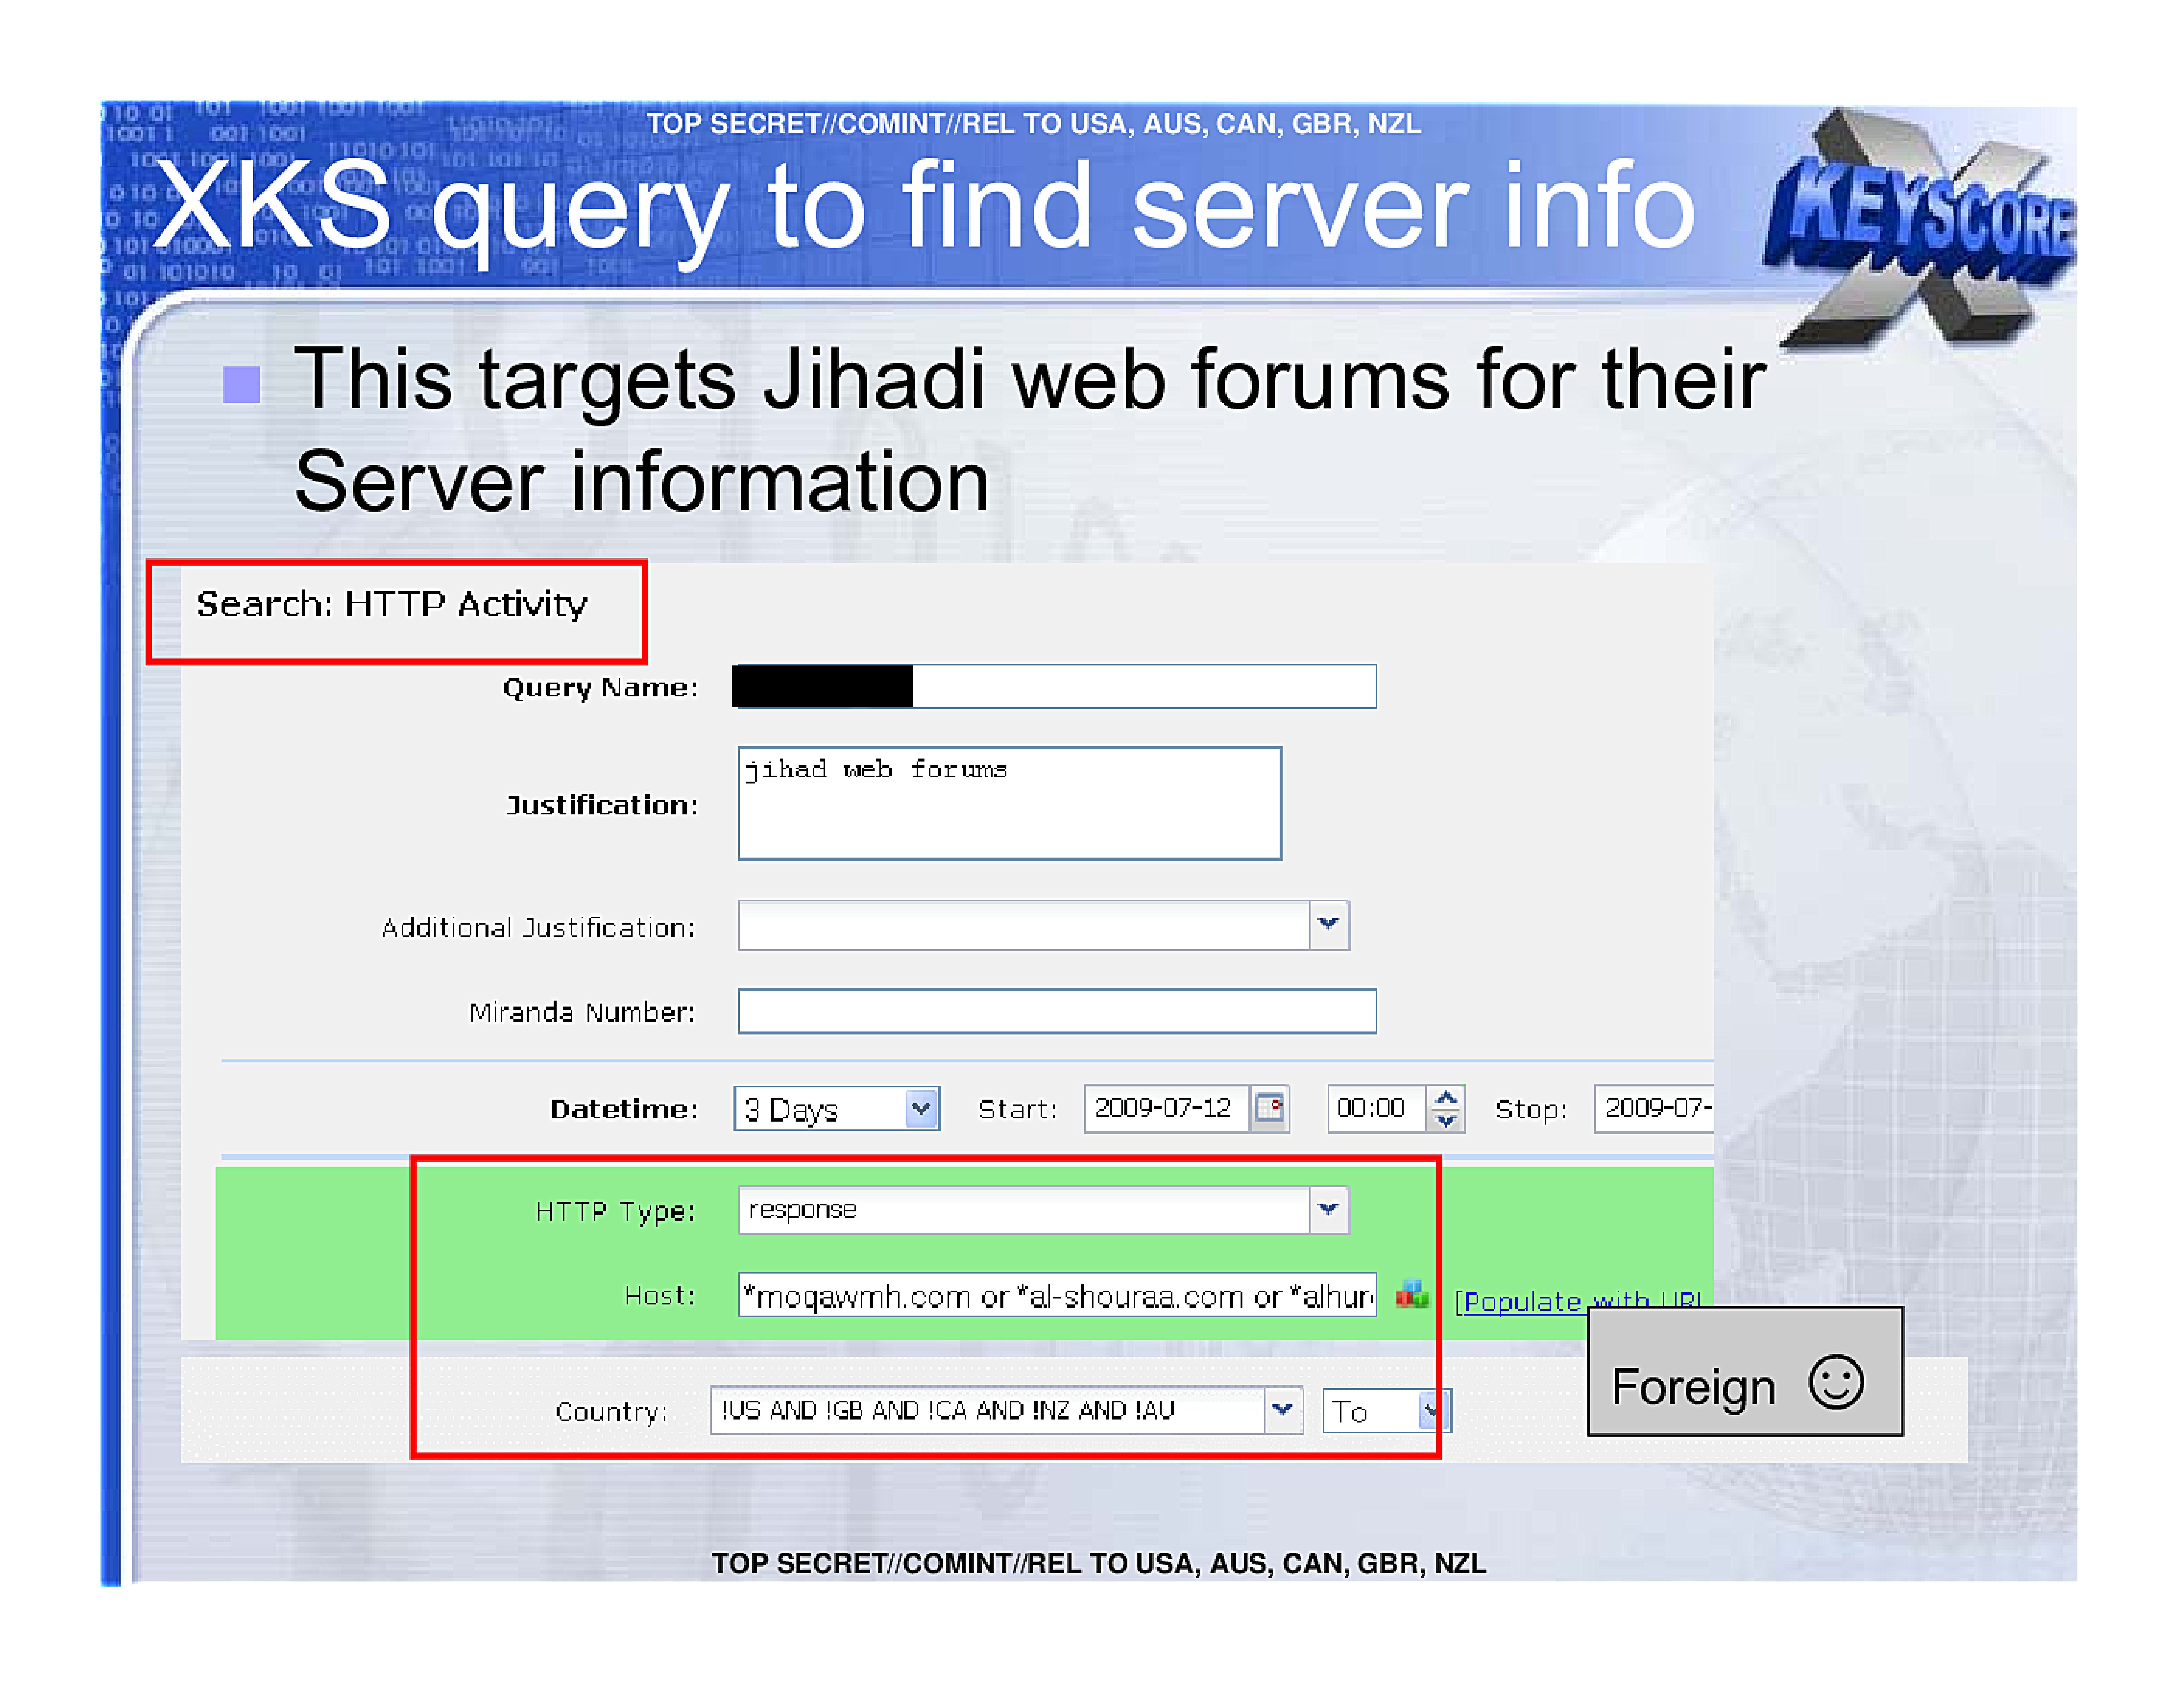
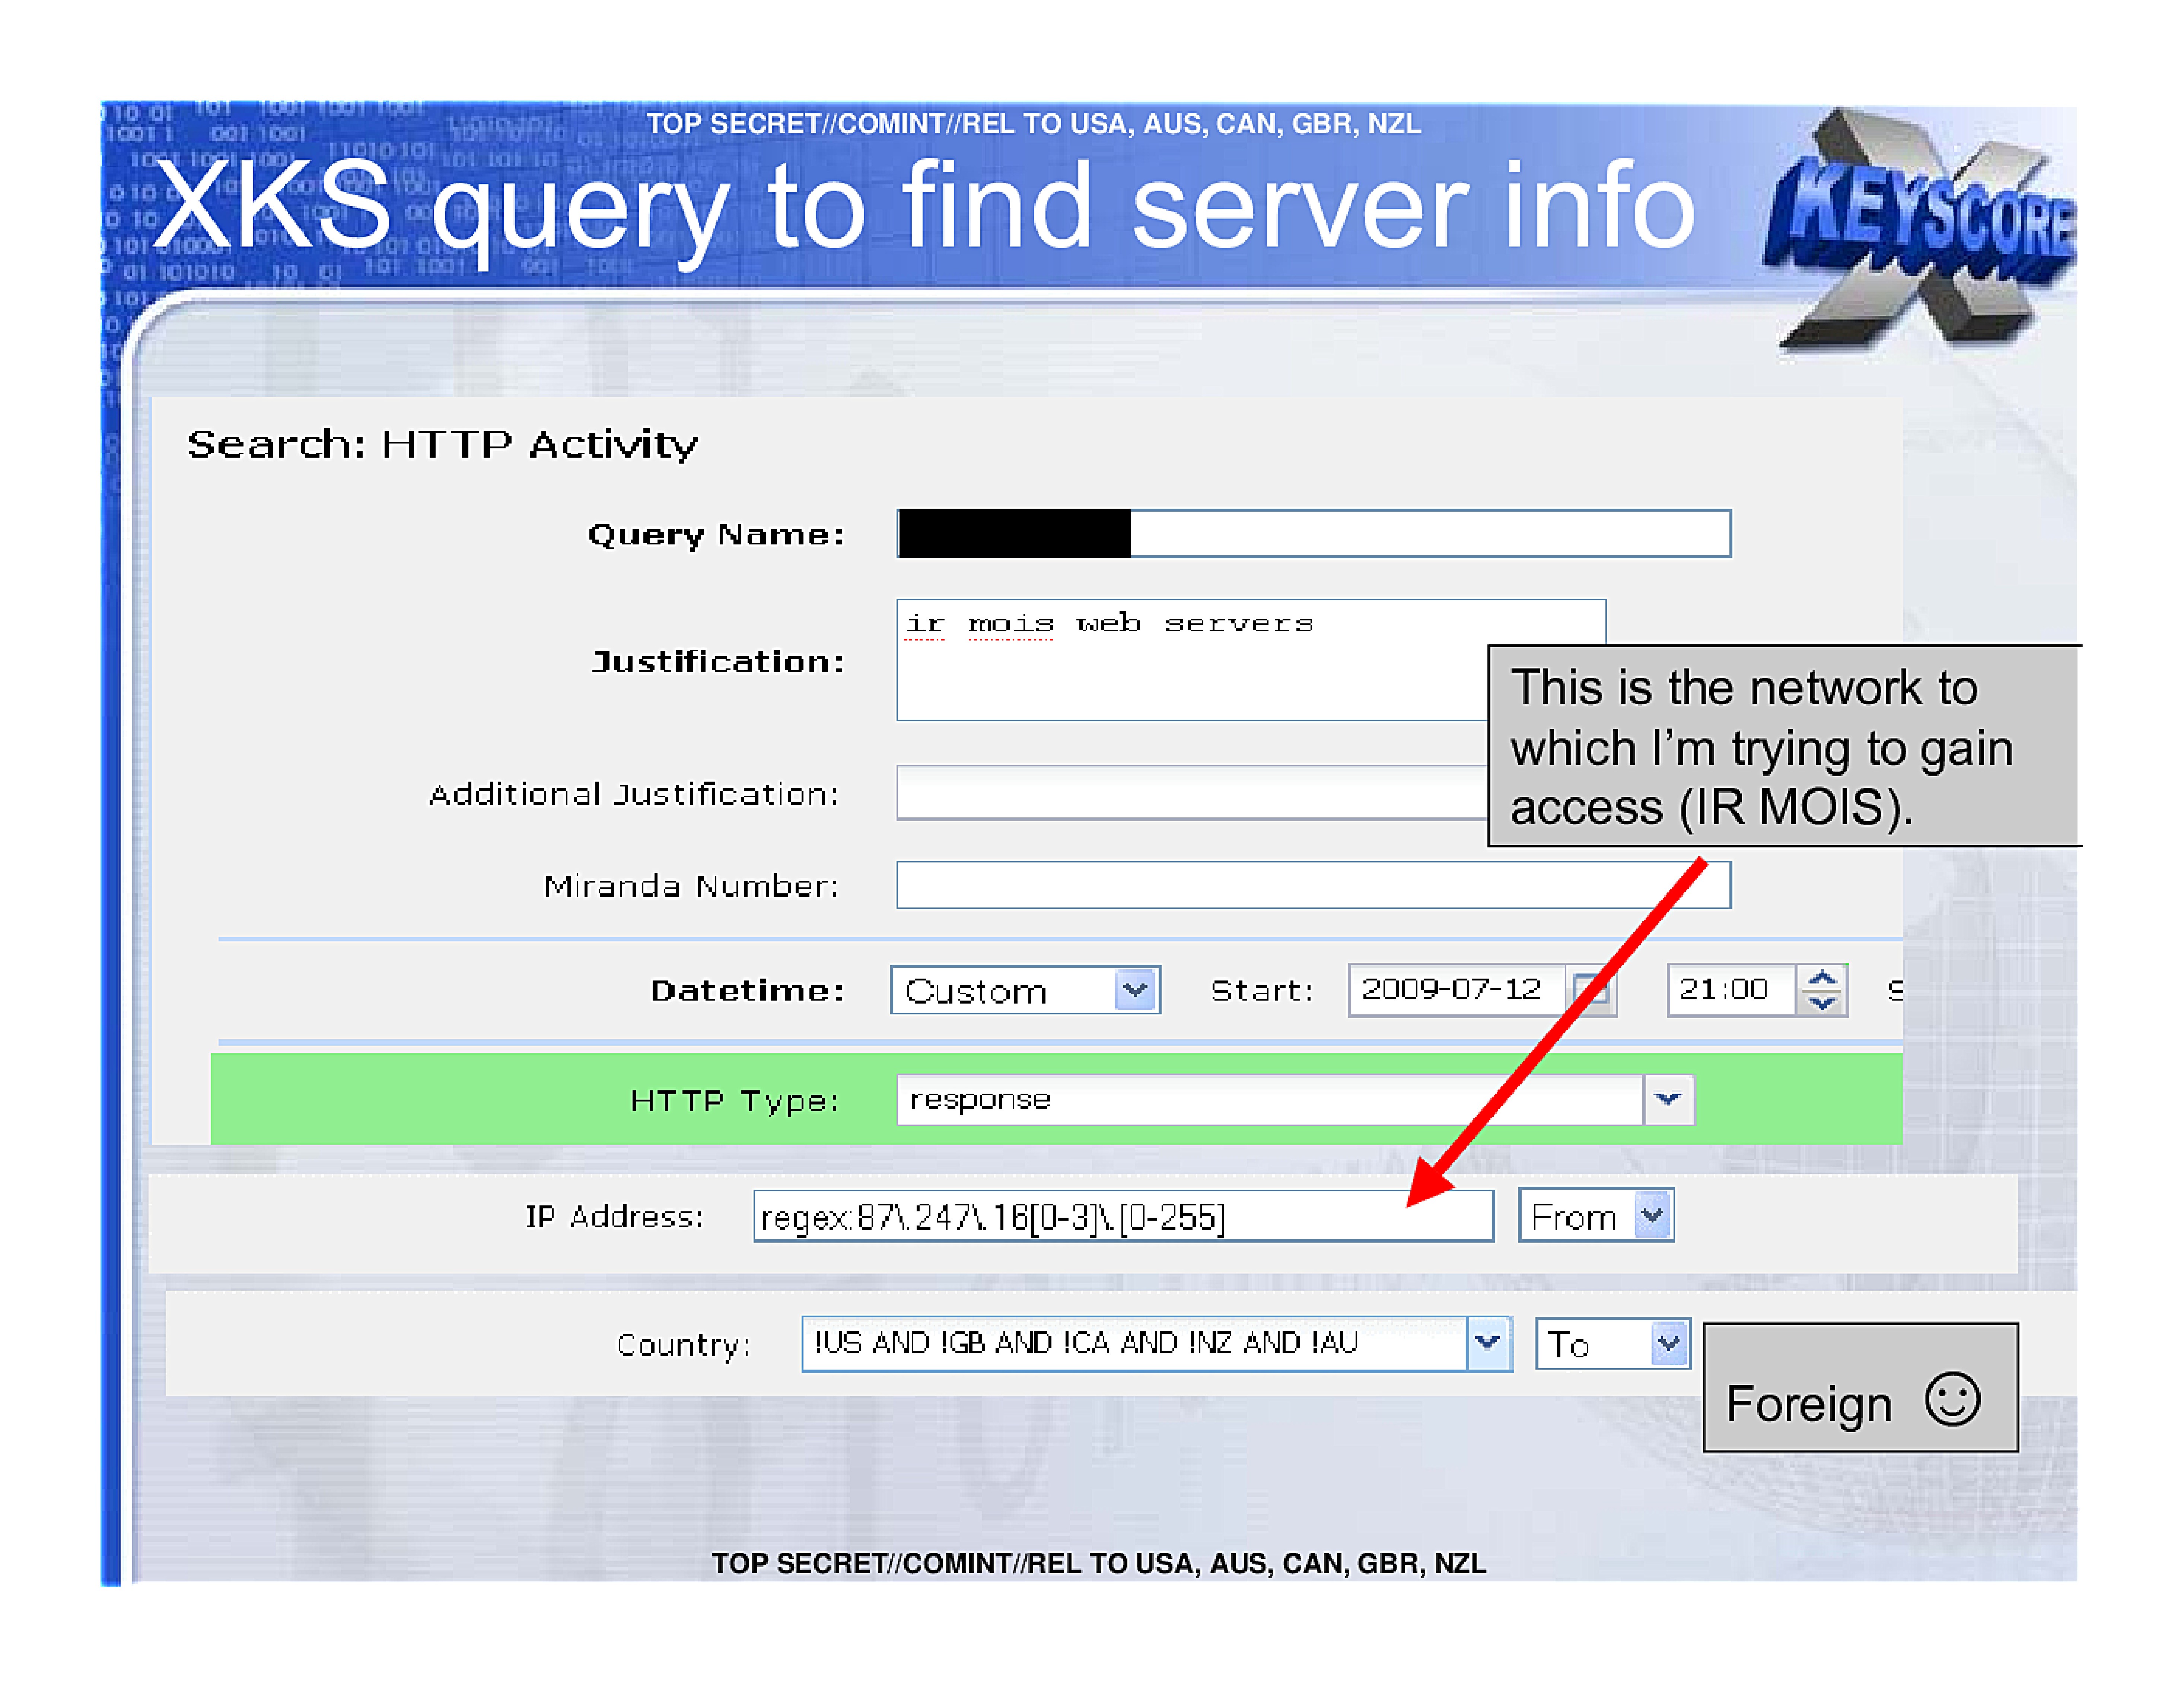
XKS query to find server info
- This targets Jihadi web forums for their Server information
Search: HTTP Activity
Query Name: [REDACTED]
Justification: jihad web forums
Additional Justification:
Miranda Number:

Datetime: 3 Days Start: 2009-07-12 00:00 Stop: 2009-07-

HTTP Type: response
Host: *moqawmh.com or *al-shouraa.com or *alhur [Populate with URL]
Country: !US AND !GB AND !CA AND !NZ AND !AU To

Foreign :)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
XKS query to find server info
This is the network to
which I'm trying to gain
access (IR MOIS).
Search: HTTP Activity
Query Name: [REDACTED]
Justification: ir mois web servers
Additional Justification:
Miranda Number:

Datetime: Custom Start: 2009-07-12 21:00 S

HTTP Type: response
IP Address: regex:87\.247\.16[0-3]\.[0-255] From
Country: !US AND !GB AND !CA AND !NZ AND !AU To

Foreign :)
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
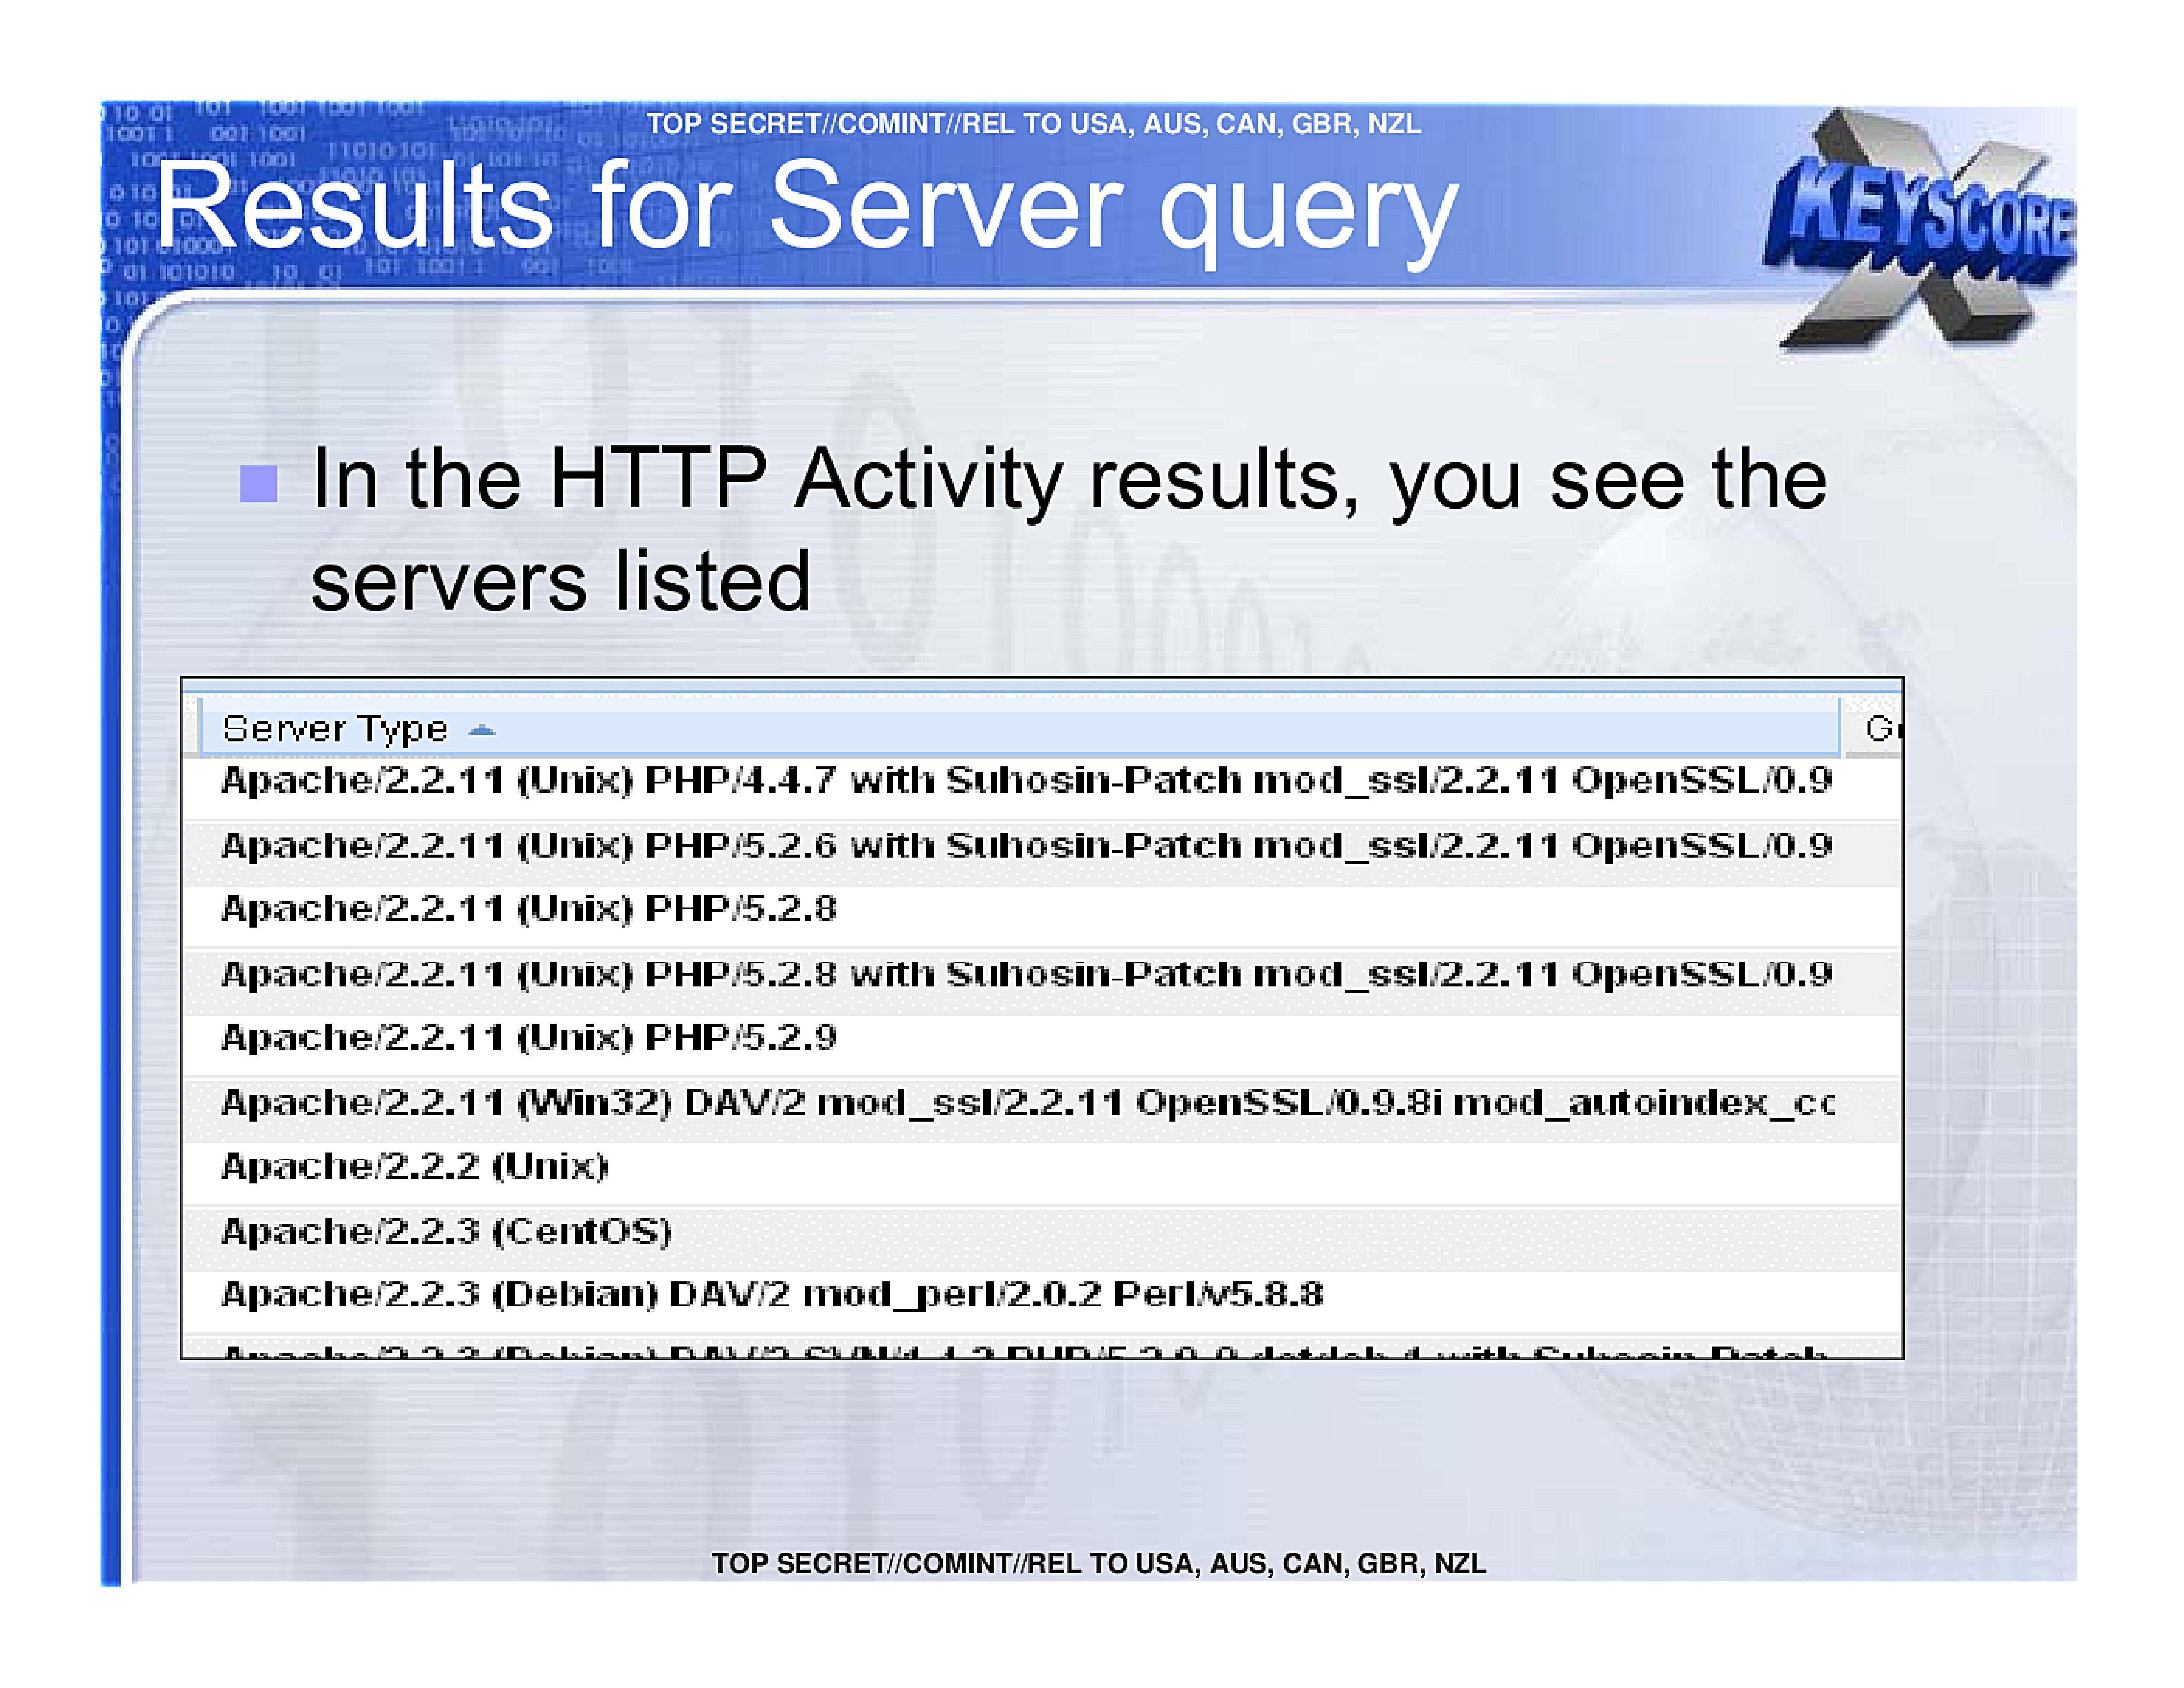
Results for Server query
- In the HTTP Activity results, you see the servers listed
| Server Type |
|---|
| Apache/2.2.11 (Unix) PHP/4.4.7 with Suhosin-Patch mod_ssl/2.2.11 OpenSSL/0.9 |
| Apache/2.2.11 (Unix) PHP/5.2.6 with Suhosin-Patch mod_ssl/2.2.11 OpenSSL/0.9 |
| Apache/2.2.11 (Unix) PHP/5.2.8 |
| Apache/2.2.11 (Unix) PHP/5.2.8 with Suhosin-Patch mod_ssl/2.2.11 OpenSSL/0.9 |
| Apache/2.2.11 (Unix) PHP/5.2.9 |
| Apache/2.2.11 (Win32) DAV/2 mod_ssl/2.2.11 OpenSSL/0.9.8i mod_autoindex_cc |
| Apache/2.2.2 (Unix) |
| Apache/2.2.3 (CentOS) |
| Apache/2.2.3 (Debian) DAV/2 mod_perl/2.0.2 Perl/v5.8.8 |
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Summary
- Many times when we task TAO we have back/forth conversations about how to exploit the target. These slides should help you find the things that TAO needs from S2 Analysts. It's difficult to cover all of the examples of how XKS can help, but this is a good start..
- Good luck.
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Published in the Same Report
(10 of 46 documents)
-
XKEYSCORE intro [pdf]
A TOP SECRET NSA presentation from 2008 introducing XKeyscore — one of the earliest overview documents in the archive — describing the system as a globally distributed Linux cluster across approximately 150 sites and 700+ servers that stores a ~3-day rolling buffer of all unfiltered internet traffic, and demonstrating its core capabilities for finding previously unknown targets by mining metadata, tracking documents by embedded image hashes, detecting encryption and VPN use, and language tracking.
Programs: XKEYSCORE · TURMOIL · TURBULENCE · TRAFFICTHIEF · WEALTHYCLUSTER · MOONSHINE · SEARCHLIGHT · MARINA · PSC · SSO · TIMBERLINEPeople: bin Laden, Osama“'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · “XKeyscore: NSA tool collects 'nearly everything a user does on the internet'” - The Guardian ↗ (2013-07-31) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · Greenwald, Glenn · Bridi, Sônia · Marquis-Boire, Morgan · Lee, Micah -
Advanced HTTP Activity Analysis [pdf]
This NSA training document from 2009 teaches intelligence analysts how to analyze HTTP internet traffic and exploit it using the XKEYSCORE surveillance system to monitor and identify internet users globally.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Analyzing Mobile/Cellular DNI in XKEYSCORE, May 2009 [pdf]
The XKEYSCORE document explains how the agency analyzes mobile/cellular device internet usage by collecting and processing both converged DNI/DNR data within cellular networks and traditional internet traffic, using various tools and indicators to identify mobile users even when their device type isn't immediately evident. The document demonstrates how the system can track mobile internet activity across applications like Yahoo Mail and identifies devices through various technical "hints" including MSISDN codes, browser fingerprints, and user agent strings.
-
Atomic SIGINT Data Format (ASDF) Configuration Read Me [pdf]
This document is a technical configuration guide for setting up XKEYSCORE surveillance systems to generate and forward metadata in the Atomic SIGINT Data Format (ASDF) to various data repositories including MARINA, which tracks users' browser activity and online behavior.
Marking: SECRET -
CADENCE Read Me [pdf]
This NSA engineering manual details how to configure XKEYSCORE—the agency's sprawling surveillance system—to integrate with CADENCE, an automated keyword scanning tool that filters intercepted communications and routes intelligence based on search terms submitted by analysts.
-
How to configure category throttling in XKEYSCORE [pdf]
An NSA technical guide explains how to configure "category throttling" in XKEYSCORE—a feature that automatically stops forwarding intercepted communications once analyst-defined collection targets hit predetermined data volume or session count limits, allowing the surveillance system to continue processing but prevent overflow from high-volume targets.
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
Communications System - How To Guide [pdf]
A TOP SECRET and sensitive compartmented information (SCI) how-to document for the NSA’s XKEYSCORE “Comms” backbone, laying out ports, peer/allow rules, bandwidth pools, and proxy classifications that stitch clusters to central control—a scalable architecture for moving surveillance data with security markings baked in. It also walks through firewall exceptions, HTTPS port-sharing, and a MAILORDER file pipeline, exposing the nuts‑and‑bolts of how collection flows across sites, proxies, and viewers.
-
DEEPDIVE Readme [pdf]
This document is a confidential technical guide that provides step-by-step procedures for configuring an XKEYSCORE server to function as a DEEPDIVE server. DEEPDIVE enhances XKEYSCORE by adding a front-end filter and a rolling buffer of all unfiltered data, creating a federated query system that can scan all collection sites with a single query.
-
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS



Related Documents
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
User-agents: Why and How and How to [pdf]
A TOP SECRET NSA training presentation from 2010 teaching analysts how to use browser user-agent strings — the identifying information your web browser automatically sends to every website you visit — to track surveillance targets across the internet, link their known email activity to their anonymous web browsing, and identify opportunities for hacking their computers based on their operating system and software versions.
-
X-KEYSCORE as a SIGDEV tool 2009 [pdf]
A 2009 TOP SECRET NSA presentation describing XKeyscore as a SIGINT development tool — explaining how it captures and temporarily stores the full content of internet traffic (the 95%+ that was previously dropped because it didn't match any target) across 125 sites worldwide, "slowing down the internet" so analysts can retroactively reconstruct a target's entire online session, discover new targets, and search the content of documents, web searches, emails and chats that contain no tasked selector.
Programs: XKEYSCORE · PINWALE · TRAFFICTHIEF · MARINA · AGILITY · PILBEAM · MAILORDER · CADENCE · NKB · PSC · SSO · UIS“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “FRA has access to controversial surveillance system” - SVT Nyheter ↗ (2013-12-11) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah · Bergman, Sven · Dyfvermark, Joachim · Gallagher, Ryan · Laurin, Fredrik · Struwe, Filip -
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.