Tag: Computer Network Exploitation 143 documents
Search documents matching “Computer Network Exploitation” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
NAC BUDE Partnership - SATELLITE TELEPORT KNOWLEDGE (GCHQ) [pdf]
A top secret GCHQ Network Analysis Centre document from GCHQ Bude detailing comprehensive intelligence profiles of three German satellite teleport operators — Stellar, Ce-Tel, and IABG — including their network infrastructure, router configurations, IP ranges, employee identities, satellite customers, and login credentials, compiled to identify access chokepoints for SIGINT collection against German IP transit infrastructure.
People: Steffen, Christian · Sommer, Christoph · Fares, Ali · Grave, Richard · Steffen, Simona · Skaletz, Oliver -
National Intelligence Estimate 2009 Global Cyber Threat – Supply Chain Excerpts [pdf]
These Supply Chain Excerpts from the 2009 National Intelligence Estimate, assesses that the U.S. faces a growing cyber threat from state actors, particularly Russia and China, who have the capability and strategic intent to exploit or disrupt U.S. and allied information systems. It emphasizes vulnerabilities from supply chains, insider threats, and technology trends that favor offensive operations, while noting the difficulty of detecting and fully defending against these sophisticated cyber threats.
-
NATO Civilian Intelligence Council – Cyber Panel – US Talking Points [pdf]
This 2011 US intelligence assessment for NATO identifies cyber espionage as the principal threat to Alliance networks, ranking Russia and China as the most significant nation-state actors and advocating for a shift to a consequence-based defense model that prioritizes the protection of NATO's most critical data.
-
New Staff Supports Network Attack SIDtoday [pdf]
In the summer of 2004, DIRNSA got new responsibilities. In addition to computer network exploitation, which involved hacking networks and extracting information, NSA will be in charge of computer network attack, which are "operations to disrupt, deny, degrade, or destroy information resident in computers and computer networks, or the computers and networks themselves." Lt. Gen. Michael Hayden established the Network Attack Support Staff organization to support these responsibilities.
The Intercept ↗ (2017-04-24) -
Notes for Dutch SIGINT/Cyber Analytic Exchange [pdf]
This document provides top-secret notes between the NSA and the Dutch intelligence services (AIVD and MIVD). This document outlines a significant restructuring of the Dutch intelligence community, including the creation of a unified SIGINT and Cyber Division and a Single Point of Contact (SPOC) at AIVD headquarters in Zoetermeer. The briefing details the operational challenges of the newly formed National Cyber Security Center (NCSC), the development of the National Detection Network (NDN) for cyber sensors, and the shared technical interests between the two nations regarding malware detection, Tor (The Onion Router) exploitation, and the analysis of web forums via Computer Network Exploitation (CNE).
Programs: TUTELAGE -
NSA ANT Catalog [pdf]
The NSA ANT catalog is a leaked confidential collection of sophisticated surveillance and hacking tools developed by the agency’s Tailored Access Operations unit (TAO), detailing hardware and software implants capable of covertly infiltrating computers, networks, and mobile devices. It revealed the NSA’s ability to conduct remote surveillance, implant malware, and maintain persistent access to targeted systems without users’ knowledge.
Programs: IRONCHEF · PROTOSS · STRONGMITE · GECKO II · STRAITBIZARRE · WAGONBED · UNITEDRAKE · DEITYBOUNCE · ARKSTREAM · TUNING FORK · GODSURGE · FLUXBABBITT · JETPLOW · BANANAGLEE · HALLUXWATER · TURBOPANDA · FEEDTROUGH · ZESTYLEAK · GOURMETTROUGH · SOUFFLETROUGH · HEADWATER · HAMMERMILL · HIT · SIERRAMONTANA · VALIDATOR · SCHOOLMONTANA · STUCCOMONTANA · CTX4000 · PHOTOANGLO · LOUDAUTO · ANGRYNEIGHBOR · NIGHTWATCHER · VIEWPLATE · LFS-2 · TAWDRYYARD · RAGEMASTER · CROSSBEAM · CHIMNEYPOOL · ROCKYKNOB · CANDYGRAM · CYCLONE Hx9 · TYPHON · EBSR · LANDSHARK · ENTOURAGE · HOLLOWPOINT · GALAXY · GENESIS · NEBULA · TYPHON HX · WATERWITCH · NIGHTSTAND · SPARROW II · BLINDDATE · DROPOUTJEEP · ARTEMIS · DROPMIRE · STRAITBIZZARE · FREEFLOW · TURBULENCE · GOPHERSET · MONKEYCALENDAR · TOTECHASER · TOTEGHOSTLY · PICASSO · TOTEGHOSTLY 2.0 · FRIEZERAMP · GENIE · VAGRANT · GOTHAM · SURLYSPAWN · GINSU · BULLDOZER · KONGUR · OMNIGAT · IRATEMONK · SERUM · SLICKERVICAR · RETURNSPRING · WISTFULTOLL · JIMSQ · SEAGULLFARO · SWAP · SNEAKERNET · TWISTEDKILT · HOWLERMONKEY · SUTURESAILOR · YELLOWPIN · CONJECTURE · SPECULATION · JUNIORMINT · MAESTRO · MAESTRO-II · SOMBERKNAVE · OLYMPUS · TRINITY · COTTONMOUTH-I · COTTONMOUTH-II · TURBINE · COTTONMOUTH-III · FIREWALK · DANDERSPRITZ -
NSA Intelligence Relationship with Norway [pdf]
This document details the long-standing SIGINT partnership between the NSA and Norway’s NIS, formalized under the NORUSA agreement in 1954, highlighting collaboration on intelligence collection, analysis, and technology modernization, particularly against Russian, counterterrorism, and counter-proliferation targets. It emphasizes mutual contributions, including SIGINT, geolocation data, FORNSAT metadata, and computer network exploitation, with Norway recognized as a top NSA partner and significant contributor to coalition intelligence efforts in Afghanistan.
“Norway Used NSA Technology for Potentially Illegal Spying” - The Intercept ↗ (2018-03-01) · “Norway´s secret surveillance of Russian politics for the NSA” - Dagbladet ↗ (2013-12-17) · “The antennas that collect data on Norwegian citizens” - NRK ↗ (2018-03-01) · Moltke, Henrik · Halvorsen, Arne · Blindheim, Anne Marte · Klungtveit, Harald S. · Sørenes, Kjetil Magne · Bergsaker, Tore · Hultgreen, Gunnar · Skille, Øyvind Bye · Hansen, Ståle Ellingsgard · Døvik, Olav · Lied, Henrik · Jansson, Harald K. -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
NSA Supply Chain Attack From PMR 4-24-13 [pdf]
This document is a top-secret NSA report detailing a SIGINT development operation in which a classified Voice-over-IP network shipment was intercepted and subjected to a supply-chain interdiction, allowing NSA and its intelligence community partners to gain access to the hardware and intelligence. It describes the operational process, including tracking the shipment through China, coordinating with Tailored Access Operations (TAO), and using tools like XKEYSCORE to identify targeting selectors, ultimately enabling detailed surveillance and future operational opportunities.
-
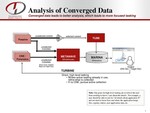
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
NSA Video Games Paper [pdf]
The NSA paper entitled “Games: A Look at Emerging Trends, Uses, Threats, and Opportunities in Influence Activities” stresses the risk of leaving gaming communities under-monitored and how the NSA and GCHQ are conducting surveillance in various online games, collecting gamers' chat data, and deploying agents into World of Warcraft and Second Life.
People: Garite, Matt · Prasad, Kaira · Castronova, Edward · DeBenedictis, Steven · Robbins, Brian · Dunin, Elonka · Estanislao, Jon · James, Daniel · Valadares, Jeferson · Kushner, David · Ondrejka, Corey · Bonk, Curtis J. · Dennen, Vanessa P. · Lindstrom, Martin · Yee, Nick · Jayaganthan, Rengaswamy · Tawil-Souri, Helga · Soussi, Alasdair · Baertlein, Lisa · Brachman, Jarret M. · Rolston, David · Dille, Flint · Bilson, David S. · Bray, Hiawatha · Morgan, Dan · Henry, Dean · Halper, Keith · Pardew, Leslie A. · Betrus, Anthony D. · Steinkuehler, Constance A. · Gupta, Shankar · Joshi, Mahesh P. · Fong, Gwenda · Andersen, John · Reid, David · Kramer, Stephen E. · Brown, Seely · Thomas, Douglas · Phillips, Andrea · Thompson, Brooke · Alexander, Bryan · Dena, Christy · Barlow, Nova · Weimann, Gabriel · Mace, Michael · Knight, Will · Gibson, Erin · Langley, Hugh · Huang, Shih-Lian · Ruff, Chris · Gibson, Ben · Cialdini, Robert B. · Johnson, Steven · Tulloch, Paul · McLundie, Martin · Galles, Kara · Berkowitz, Jeff · May, William · Leonard, David J. · Williams, Dmitri“World of Spycraft: NSA and CIA Spied in Online Games” - ProPublica ↗ (2013-12-09) · “Spies Infiltrate a Fantasy Realm of Online Games” - The New York Times ↗ (2013-12-09) · “Xbox Live among game services targeted by US and UK spy agencies” - The Guardian ↗ (2013-12-09) · Elliott, Justin · Mazzetti, Mark · Ball, James -
NSA's Offensive and Defensive Missions: The Twain Have Met SIDtoday [pdf]
The document outlines a case where NSA’s defensive malware analysis enabled offensive SIGINT teams to gain sustained access to a Chinese command-and-control server, allowing NSA to intercept intelligence China had stolen from the United Nations through a method known as fourth-party collection.
-
NSA's Technical Analysis of CNE Collection Goes Global -- A Success Story SIDtoday [pdf]
The Network Information Exploitation Target Analysis branch has six employees in Georgia who support their colleagues at the NSA’s headquarters. Recently, they took over coverage of top priority targets during a snowstorm at HQ.
The Intercept ↗ (2018-08-15) -
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
Op MULLENIZE and beyond - Staining machines 10/10/12 [pdf]
This 2012 report from the NSA's British counterpart, the GCHQ, describes a method of "staining" electronic traffic to distinguish otherwise anonymous users. It is used to unmask Tor users and devices on networks in which many computers share the same Internet address. The method relies on planting code in a web browser to change the "user agent," which is the way the browser identifies itself on the web. In a two month period, the report says, GCHQ managed to implant about 200 computers with uniquely identifying stains.
-
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
Partner Cables [pdf]
A classified table mapping which GCHQ cable interception programs had access to specific undersea fiber optic cables worldwide, revealing the codenames and access types — either Direct Cable Order or Indefeasible Right of Use/Landing Capacity — of seven surveillance programs across dozens of international cable systems, with Cable & Wireless (GERONTIC) providing access to the largest number.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM