XKEYSCORE for Counter-CNE
Open PDFDocument date: 2011-03-01
Pages: 21
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, FVEY
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, FVEY
A TOP SECRET presentation from March 2011 describing how NSA uses XKeyscore for counter-CNE — detecting and exploiting foreign hacking operations — including ingesting NSA's own TAO implant data, hunting for foreign intrusion sets like DISGRUNTLEDDUCK, and a success story in which Menwith Hill used TAO-stolen Iranian implant encryption keys to decrypt and read keylogger data the Iranian Revolutionary Guard's hackers were stealing from their own victims.
My notes
TOP SECRET//COMINT//REL TO USA, FVEY
XKEYSCORE for Counter-CNE
"Using the XKS CNE dataset and a
DISGRUNTLEDDUCK fingerprint, we now see at least
21 TAO boxes with evidence of this intrusion set, most
of which are associated with projects aimed at Iran
WMD targets." -- MHS, July 2010
March, 2011
[REDACTED]
xks-cne@r1.r.nsa
TOP SECRET//COMINT//REL TO USA, FVEY
UNCLASSIFIED//FOUO
Overall Classification
The overall classification of this presentation is:
TOP SECRET//COMINT//REL TO USA, FVEY
UNCLASSIFIED//FOUO
SECRET//COMINT//REL TO USA, FVEY
What is XKEYSCORE?
- A suite of software running on a Linux host
- Classically, used for DNI processing, selection and survey
- A distributed hierarchy of servers at field sites and headquarters
- Extract and tag metadata & content from traffic
- Servicing analyst queries and workflows
- Web and programmatic front-ends
SECRET//COMINT//REL TO USA, FVEY
SECRET//COMINT//REL TO USA, FVEY
What is XKEYSCORE?
- A suite of software running on a Linux host
- Classically, used for DNI processing, selection and survey
- A distributed hierarchy of servers at field sites and headquarters
- Extract and tag metadata & content from traffic
- Servicing analyst queries and workflows
- Web and programmatic front-ends
SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
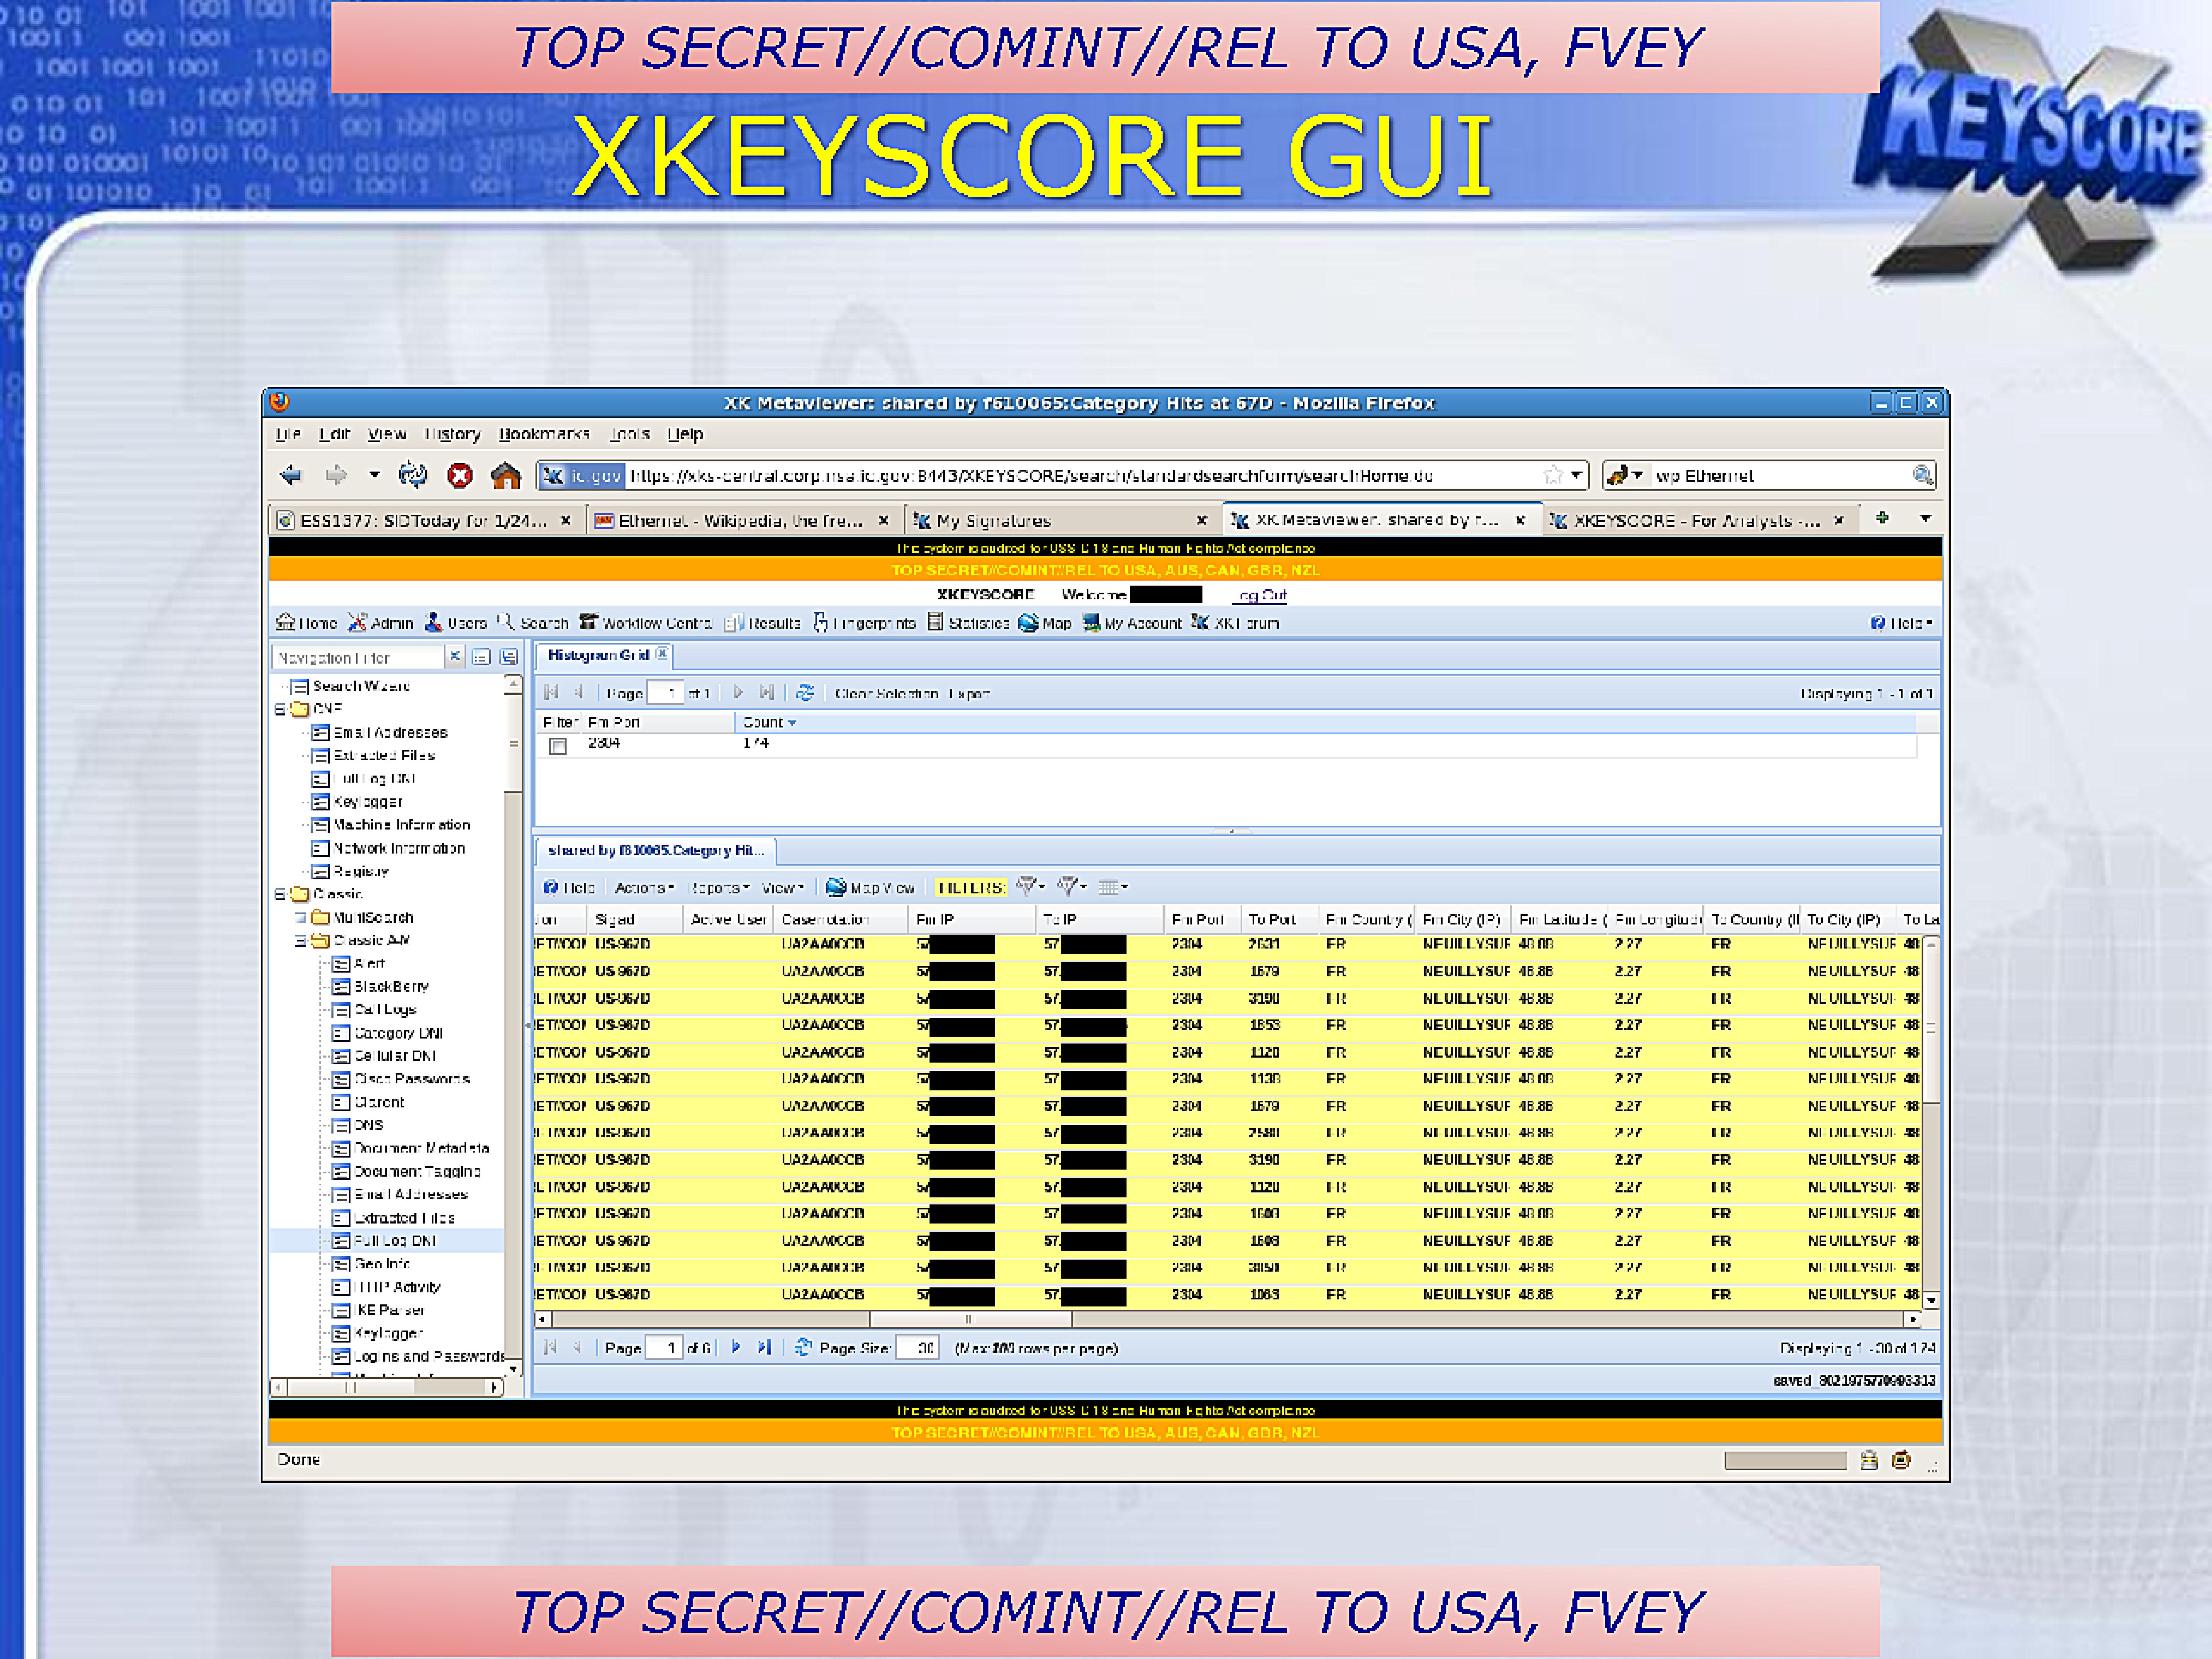
XKEYSCORE GUI
XK Metaviewer: shared by f610065: Category Hits at 67D - Mozilla Firefox
File Edit View History Bookmarks Tools Help
ic.gov https://xks-central.corp.nsa.iv.gov:8113/XKEYSCORE/search/standardSearch/searchHome wp Ethernet
ESS1377: SIDToday for 1/24... | Ethernet - Wikipedia, the fre... | My Signatures | XK Metaviewer shared by ... | XKEYSCORE - For Analysts ...

This system is audited for USSID 18 and Human Rights Act compliance
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
X-KEYSCORE Welcome [REDACTED] og Out
Home Admin Users Search Workflow Central Results Fingerprints Statistics Map My Account XK Help
Navigation
SearchWizard
CNE
  EmailAddresses
  Extracted Files
  Full Log DNI
  Keylogger
  Machine Information
  Network Information
  Registry
Classic
  MultiSearch
  Classic A-M
    Alert
    BlackBerry
    CallLogs
    Category DNI

    Cisco Passwords

    DNS
    Document metadata
    Document tagging
    Email Addresses
    Extracted Files
    FullLog DNI
    Geo Info
    HTTP Activity
    KEParser
    Keylogger
    Logins and Passwords

Histogram Grid
Page 1 of 1 Clear Searcher Displaying 1- 1 of 1
Filter Fm Port Count Displaying 1 - 1 of 3
2804 174

shared by f810085 Category Hit...
Help Actions Reports View MapView FILTERS
| Sigad | Active User | Casenotation | Full IP | To IP | Fm Port | To Port | Fm Country | Fm City (IP) | Fm Latitude | Fm Longti | To Country ( | To City (IP) | To L |
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 2631 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1679 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 3190 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-987D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1853 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1120 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1138 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1579 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-987D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 7581 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 3190 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1120 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1603 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-967D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 1603 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 | |
| US-987D | UA2AA0DCB | 57[REDACTED] | 57[REDACTED] | 2304 | 3050 | FR | NEUILLYSUR | 48.88 | 2.27 | FR | NEUILLYSUR | 48 |
Page 1 of 6 Page Size: 30 (Max 200 rows per page) Displaying 1 - 30 of 174
saved_802197577093313
This system is audited for USSID 18 and Human Rights Act compliance
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
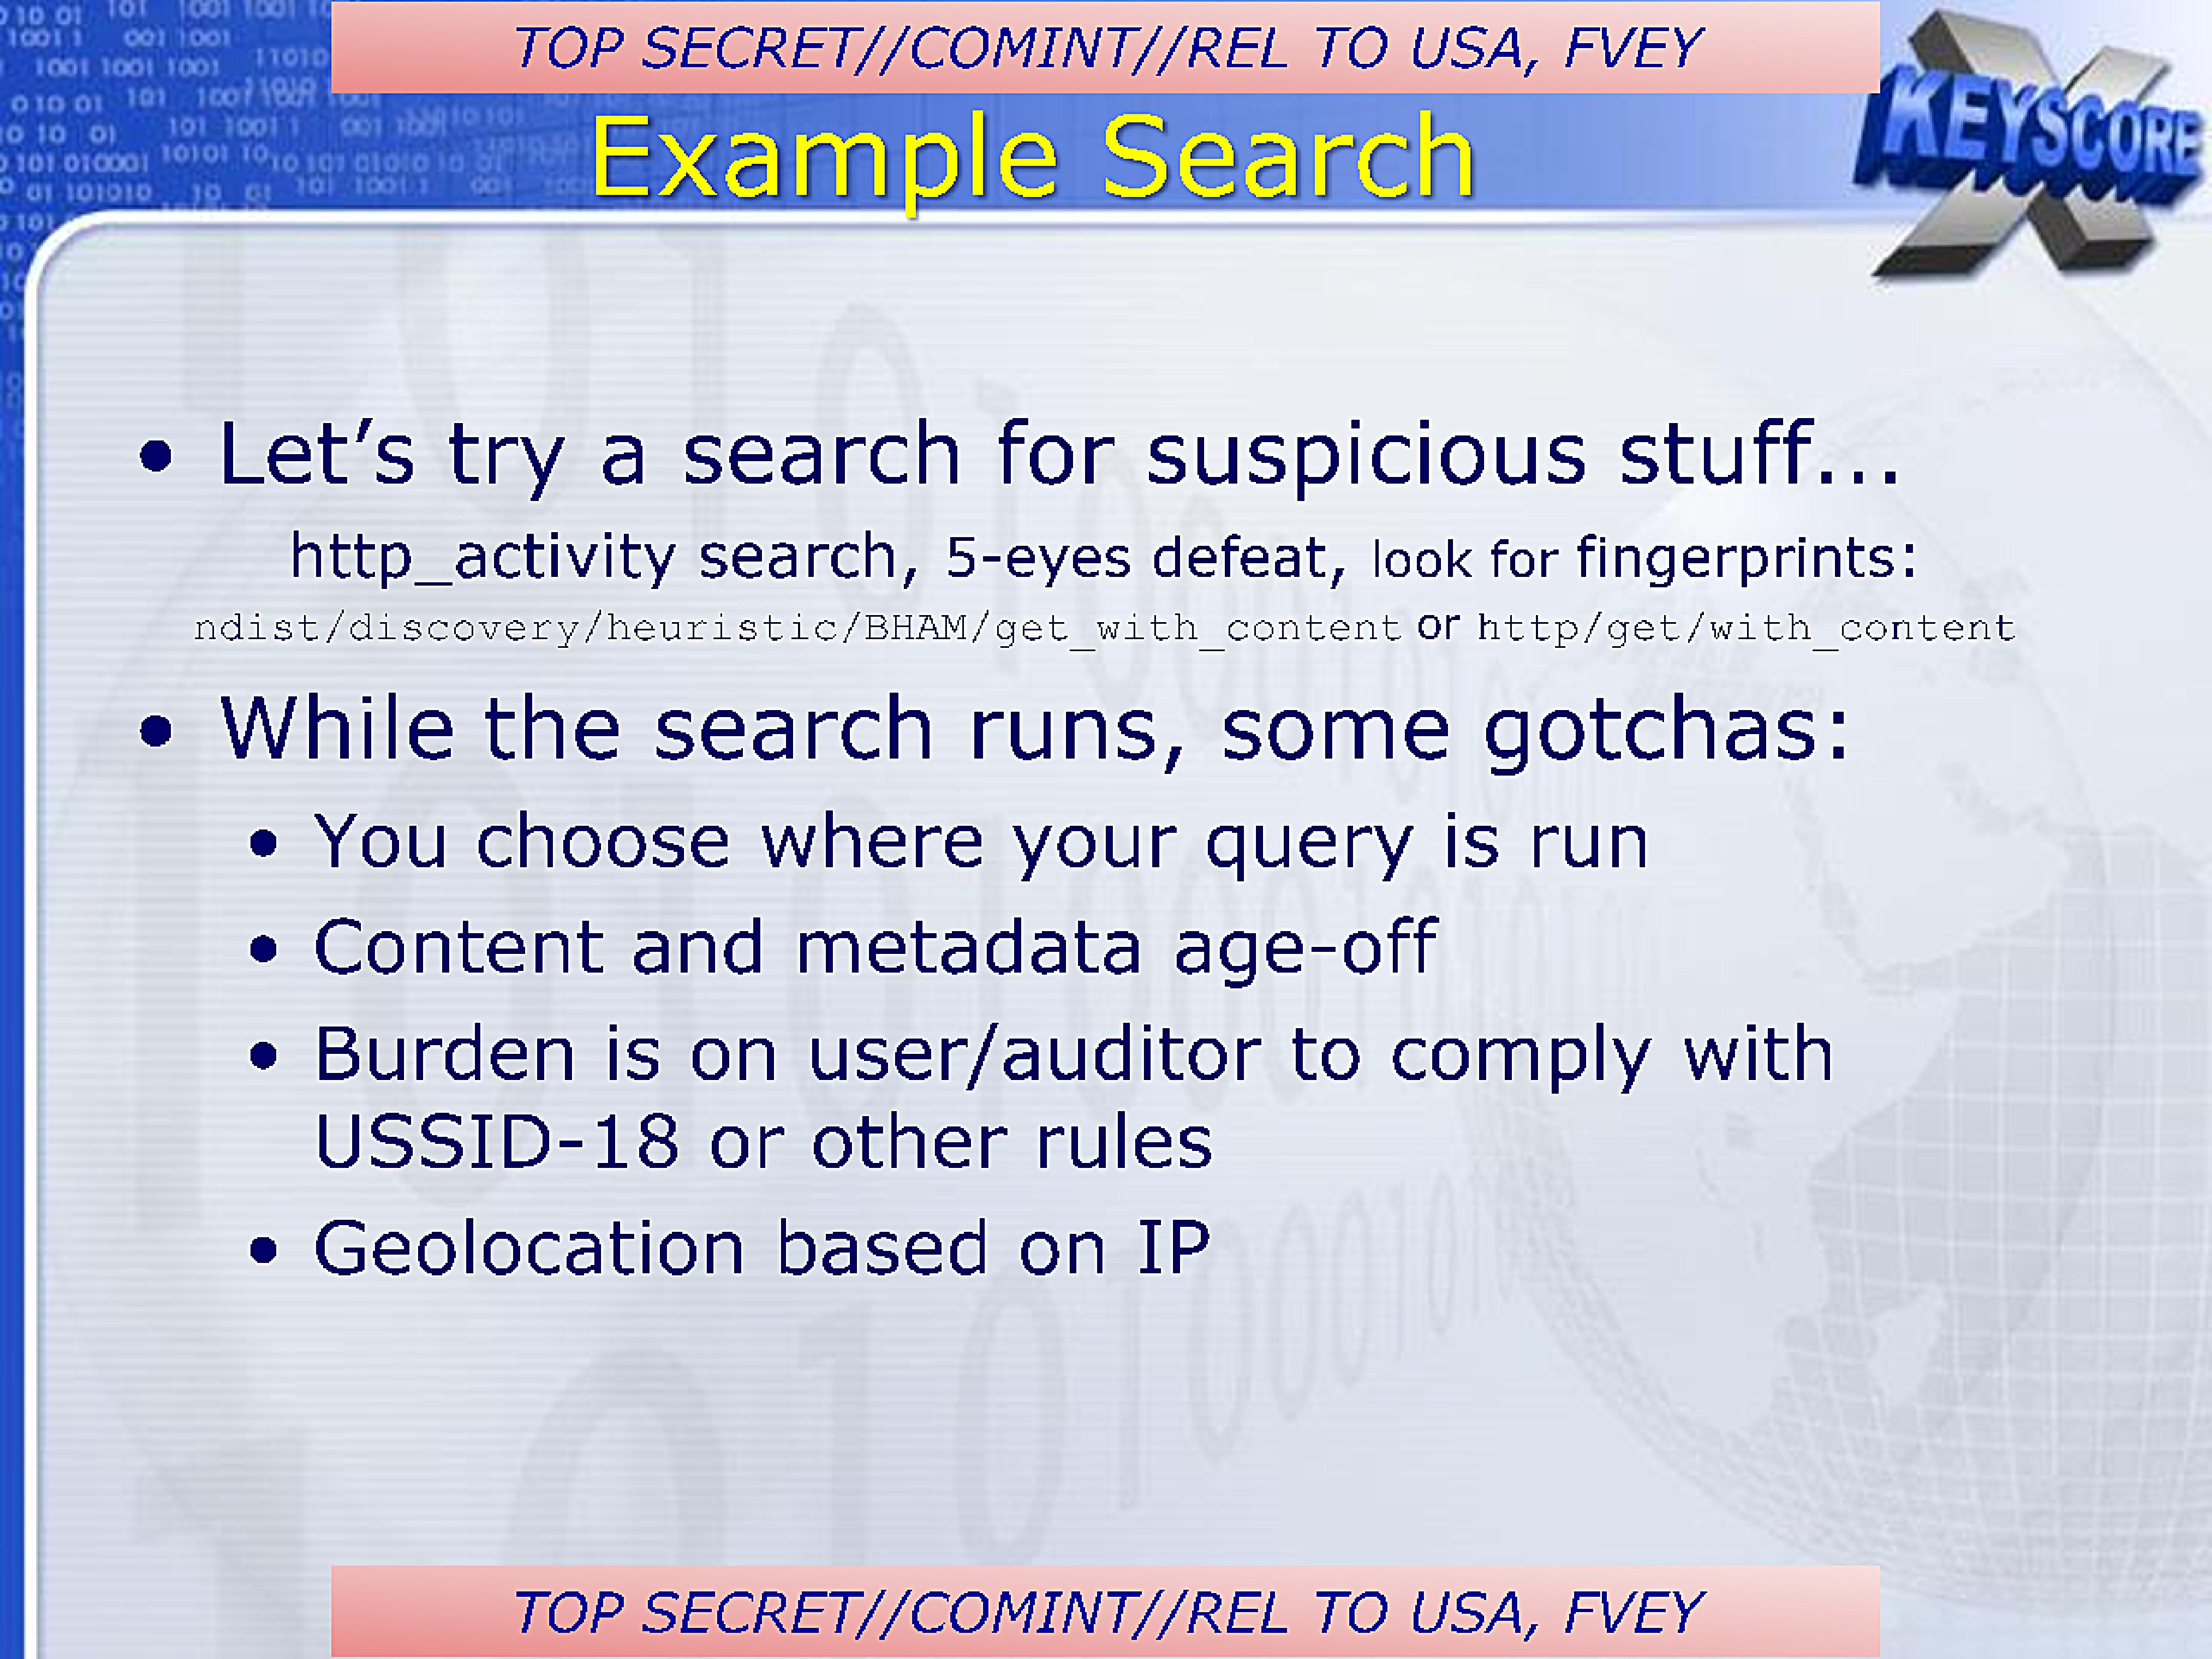
Example Search
- Let's try a search for suspicious stuff...
http_activity search, 5-eyes defeat, look for fingerprints:
ndist/discovery/heuristic/BHAM/get_with_content or http/get/with_content
- While the search runs, some gotchas:
- You choose where your query is run
- Content and metadata age-off
- Burden is on user/auditor to comply with USSID-18 or other rules
- Geolocation based on IP
TOP SECRET//COMINT//REL TO USA, FVEY
SECRET//COMINT//REL TO USA, FVEY
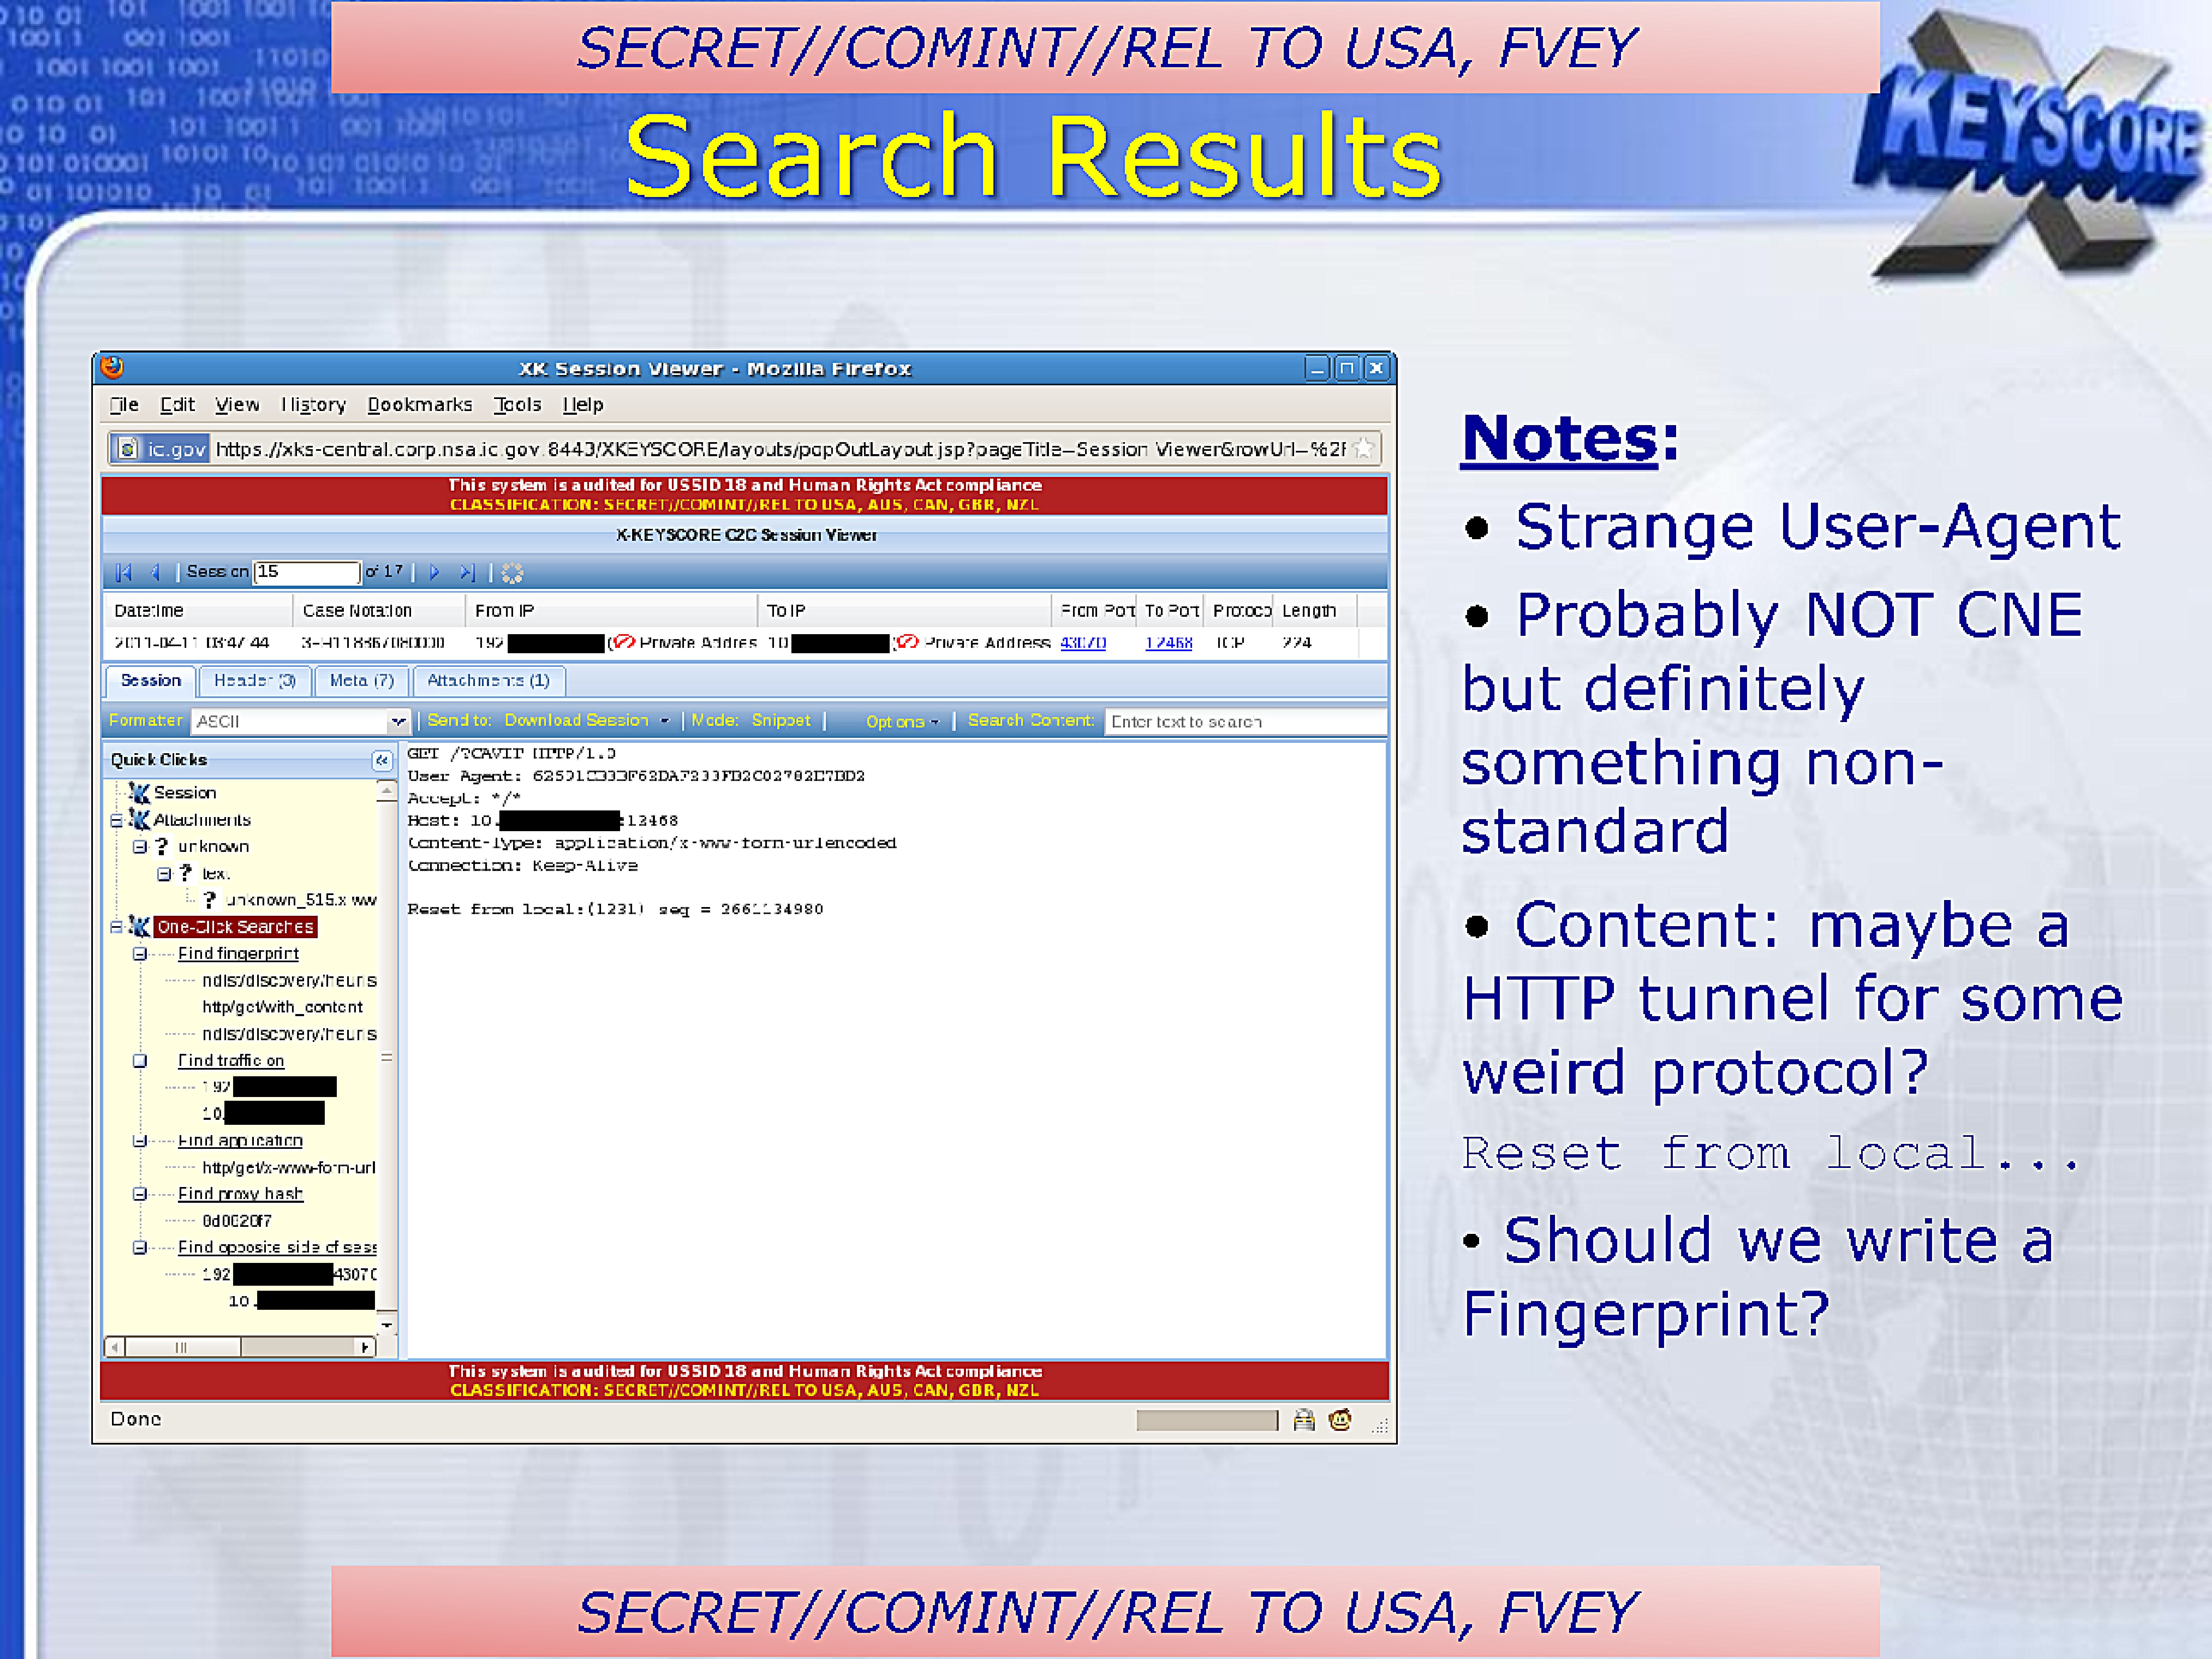
Search Results
XK Session Viewer - Mozilla Firefox
File Edit Views History Bookmarks Tools Help
ic.gov https://xks-central.corp.nsa.ic.gov:8443/XKEYSCORE/layouts/popOutLayout.jsp?pageTitle=Session Viewer&rowUrl=5621
This system is audited for USSID 18 and Human Rights Act compliance
CLASSIFICATION: SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
X-KEYSCORE C2C Session Viewer
Session 15 of 17
Datetime | Case Notation | From IP | To IP | From Port | To Port | Protocol | Length
2011-04-11 08:47:44 | 3 441836   | 192[REDACTED] (Private Address | TO [REDACTED] Private Address | 4370 | 12468 | TCP | 224 |

Formatter ASCII | Send to: Download Session | Mode: Snippet | Options | Search Content: Enter text to search
Quick Clicks
Session
Attachments
  unknown
    text
      unknown_515.xww
One-Click Searches
  Find fingerprint
    nd/discovery
    http/gc/with_content
    ndis/discovery
  Find traffic on
    192[REDACTED]
    10[REDACTED]
  Find application
    http//get/x-www-form-url
  Find proxy hash
    0d0020f7
  Find opposite side of sess
    192[REDACTED]4307
      10.[REDACTED]
GET /?CAVIT HTTP/1.0
User-Agent: 62591C333F62DA7333FB2C02702B7BD2
Accept: */*
Host: 10.[REDACTED]:12466
Content-Type: application/w-www-form-urlencoded
Connection: Keep-Alive

Reset from local: (1231) seq = 2662134980
This system is audited for USSID 18 and Human Rights Act compliance
CLASSIFICATION: SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Done
Notes:
- Strange User-Agent
- Probably NOT CNE but definitely something non-standard
- Content: maybe a HTTP tunnel for some weird protocol?
- Reset from local...
- Should we write a Fingerprint?
SECRET//COMINT//REL TO USA, FVEY
SECRET//COMINT//REL TO USA, FVEY
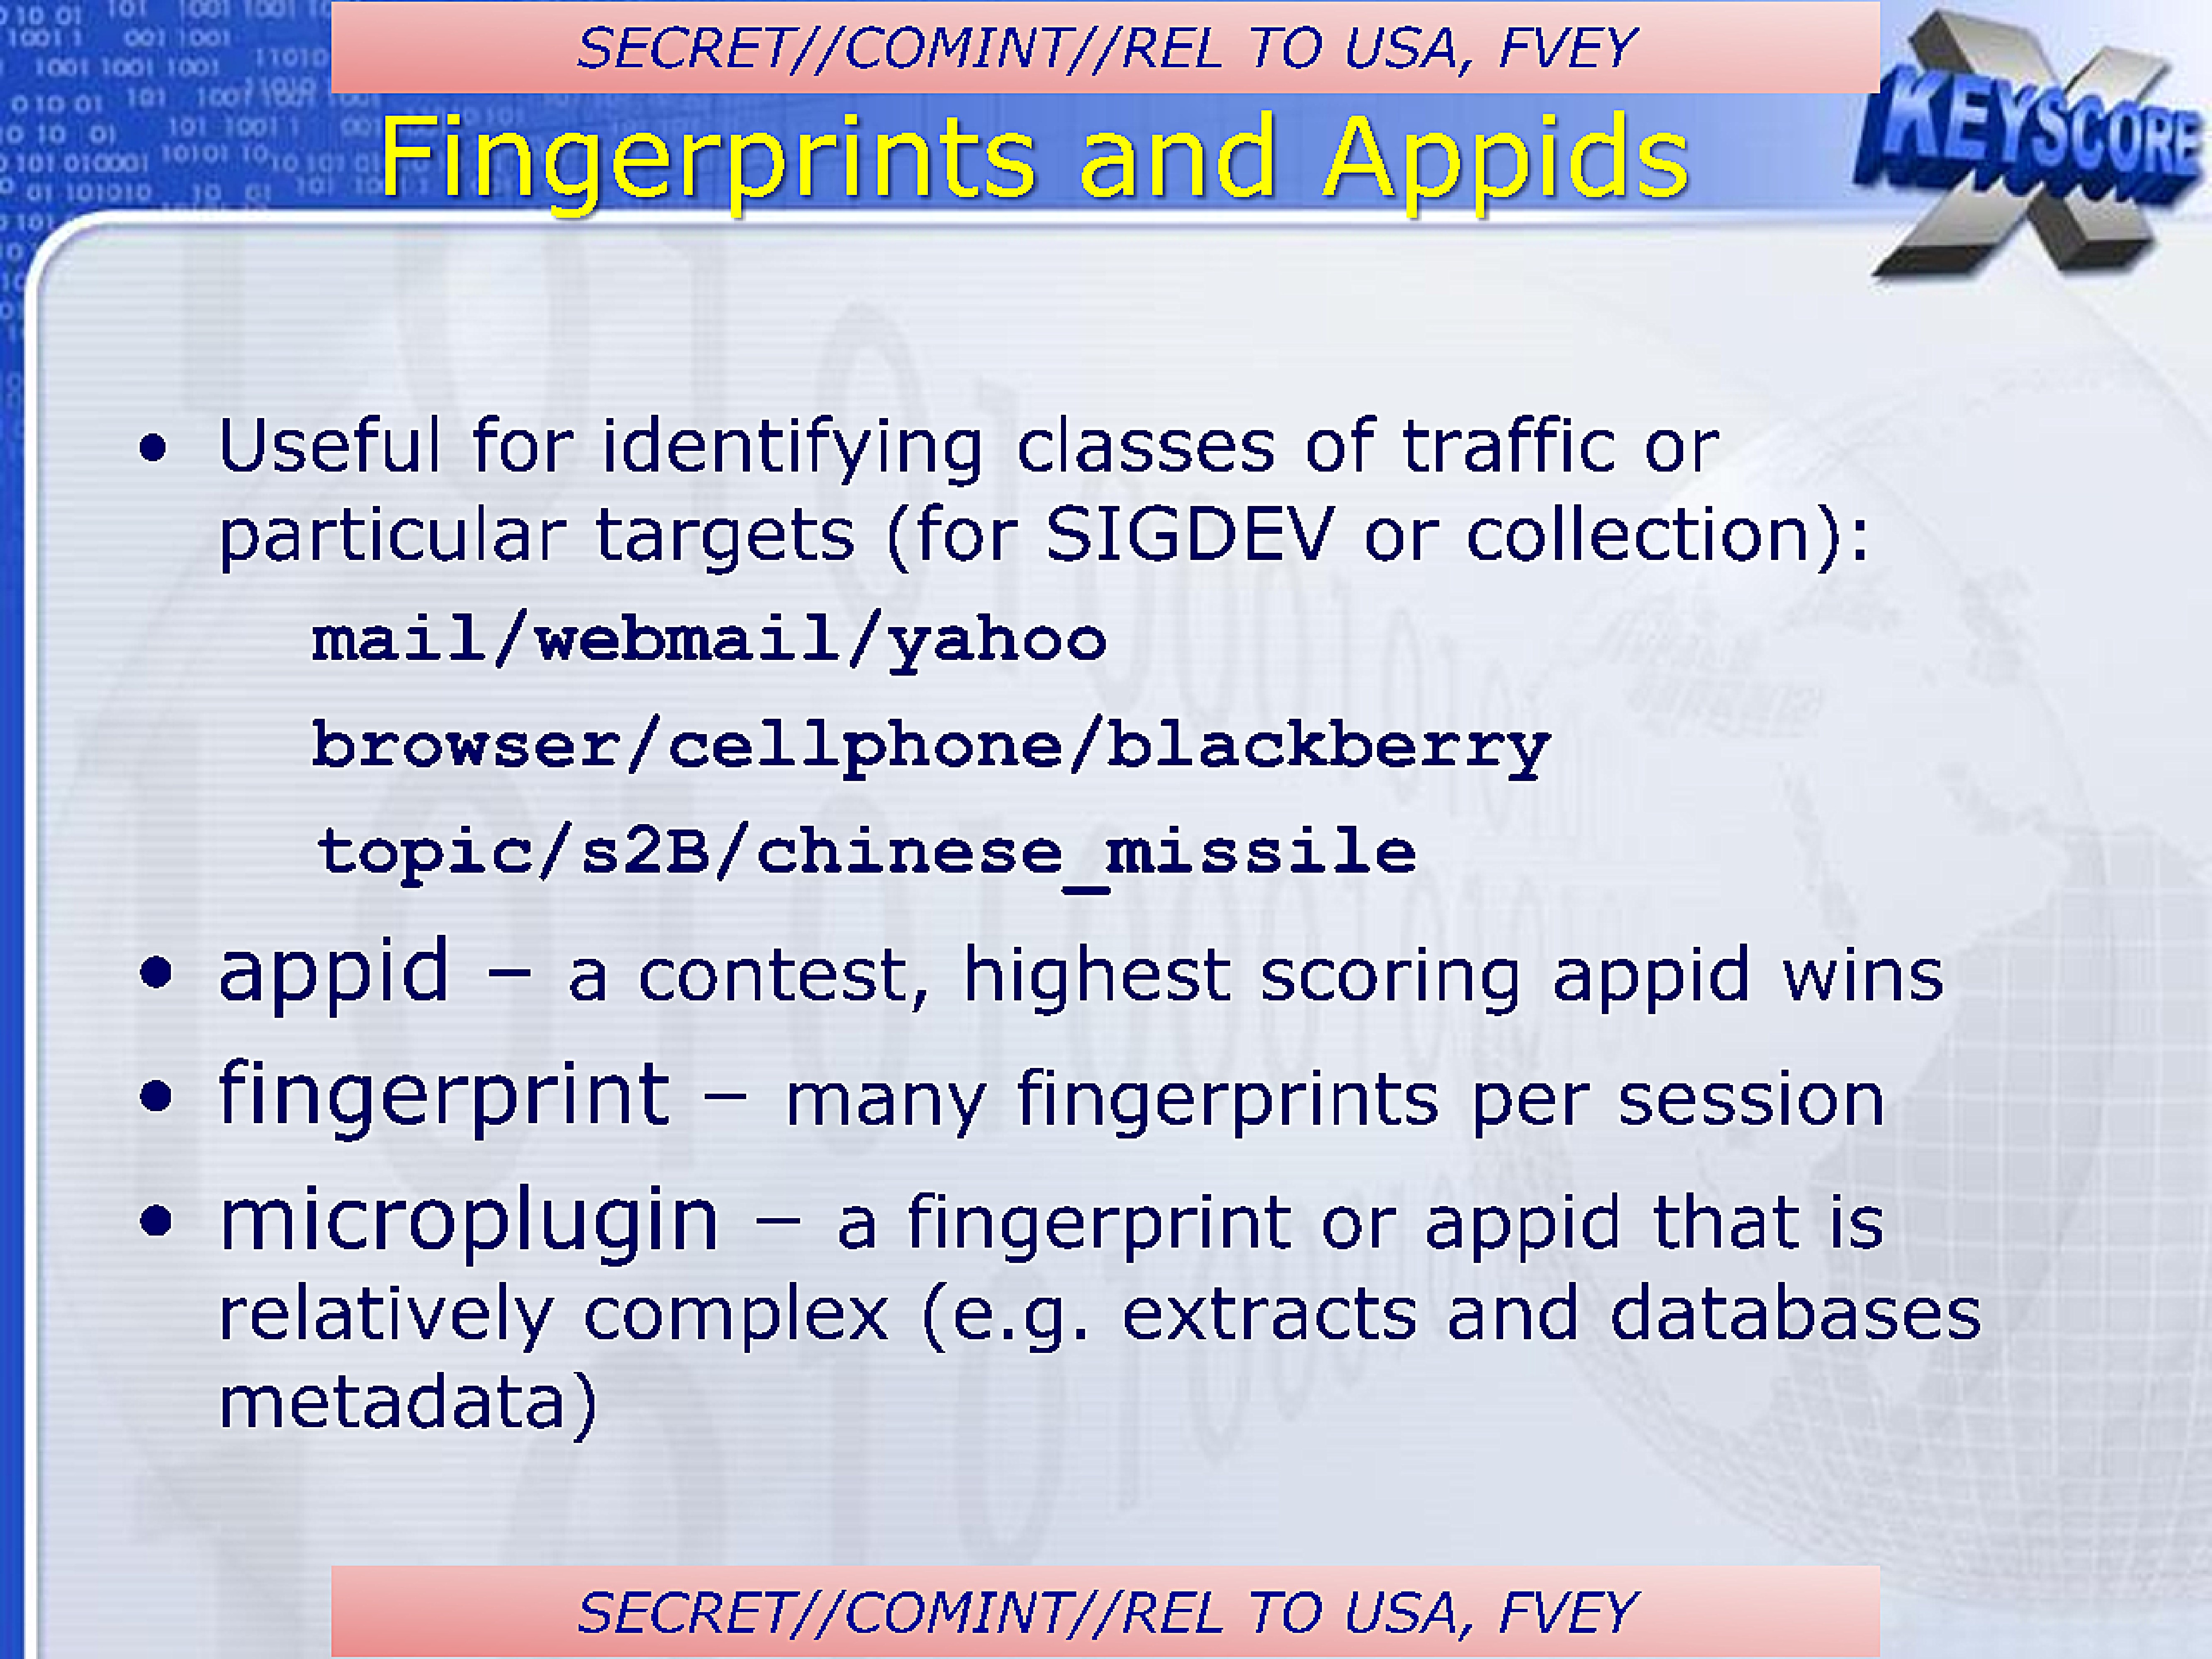
Fingerprints and Appids
- Useful for identifying classes of traffic or particular targets (for SIGDEV or collection):
mail/webmail/yahoo
browser/cellphone/blackberry
topic/s2B/chinese_missile
- appid – a contest, highest scoring appid wins
- fingerprint – many fingerprints per session
- microplugin – a fingerprint or appid that is relatively complex (e.g. extracts and databases metadata)
SECRET//COMINT//REL TO USA, FVEY
SECRET//COMINT//REL TO USA, FVEY
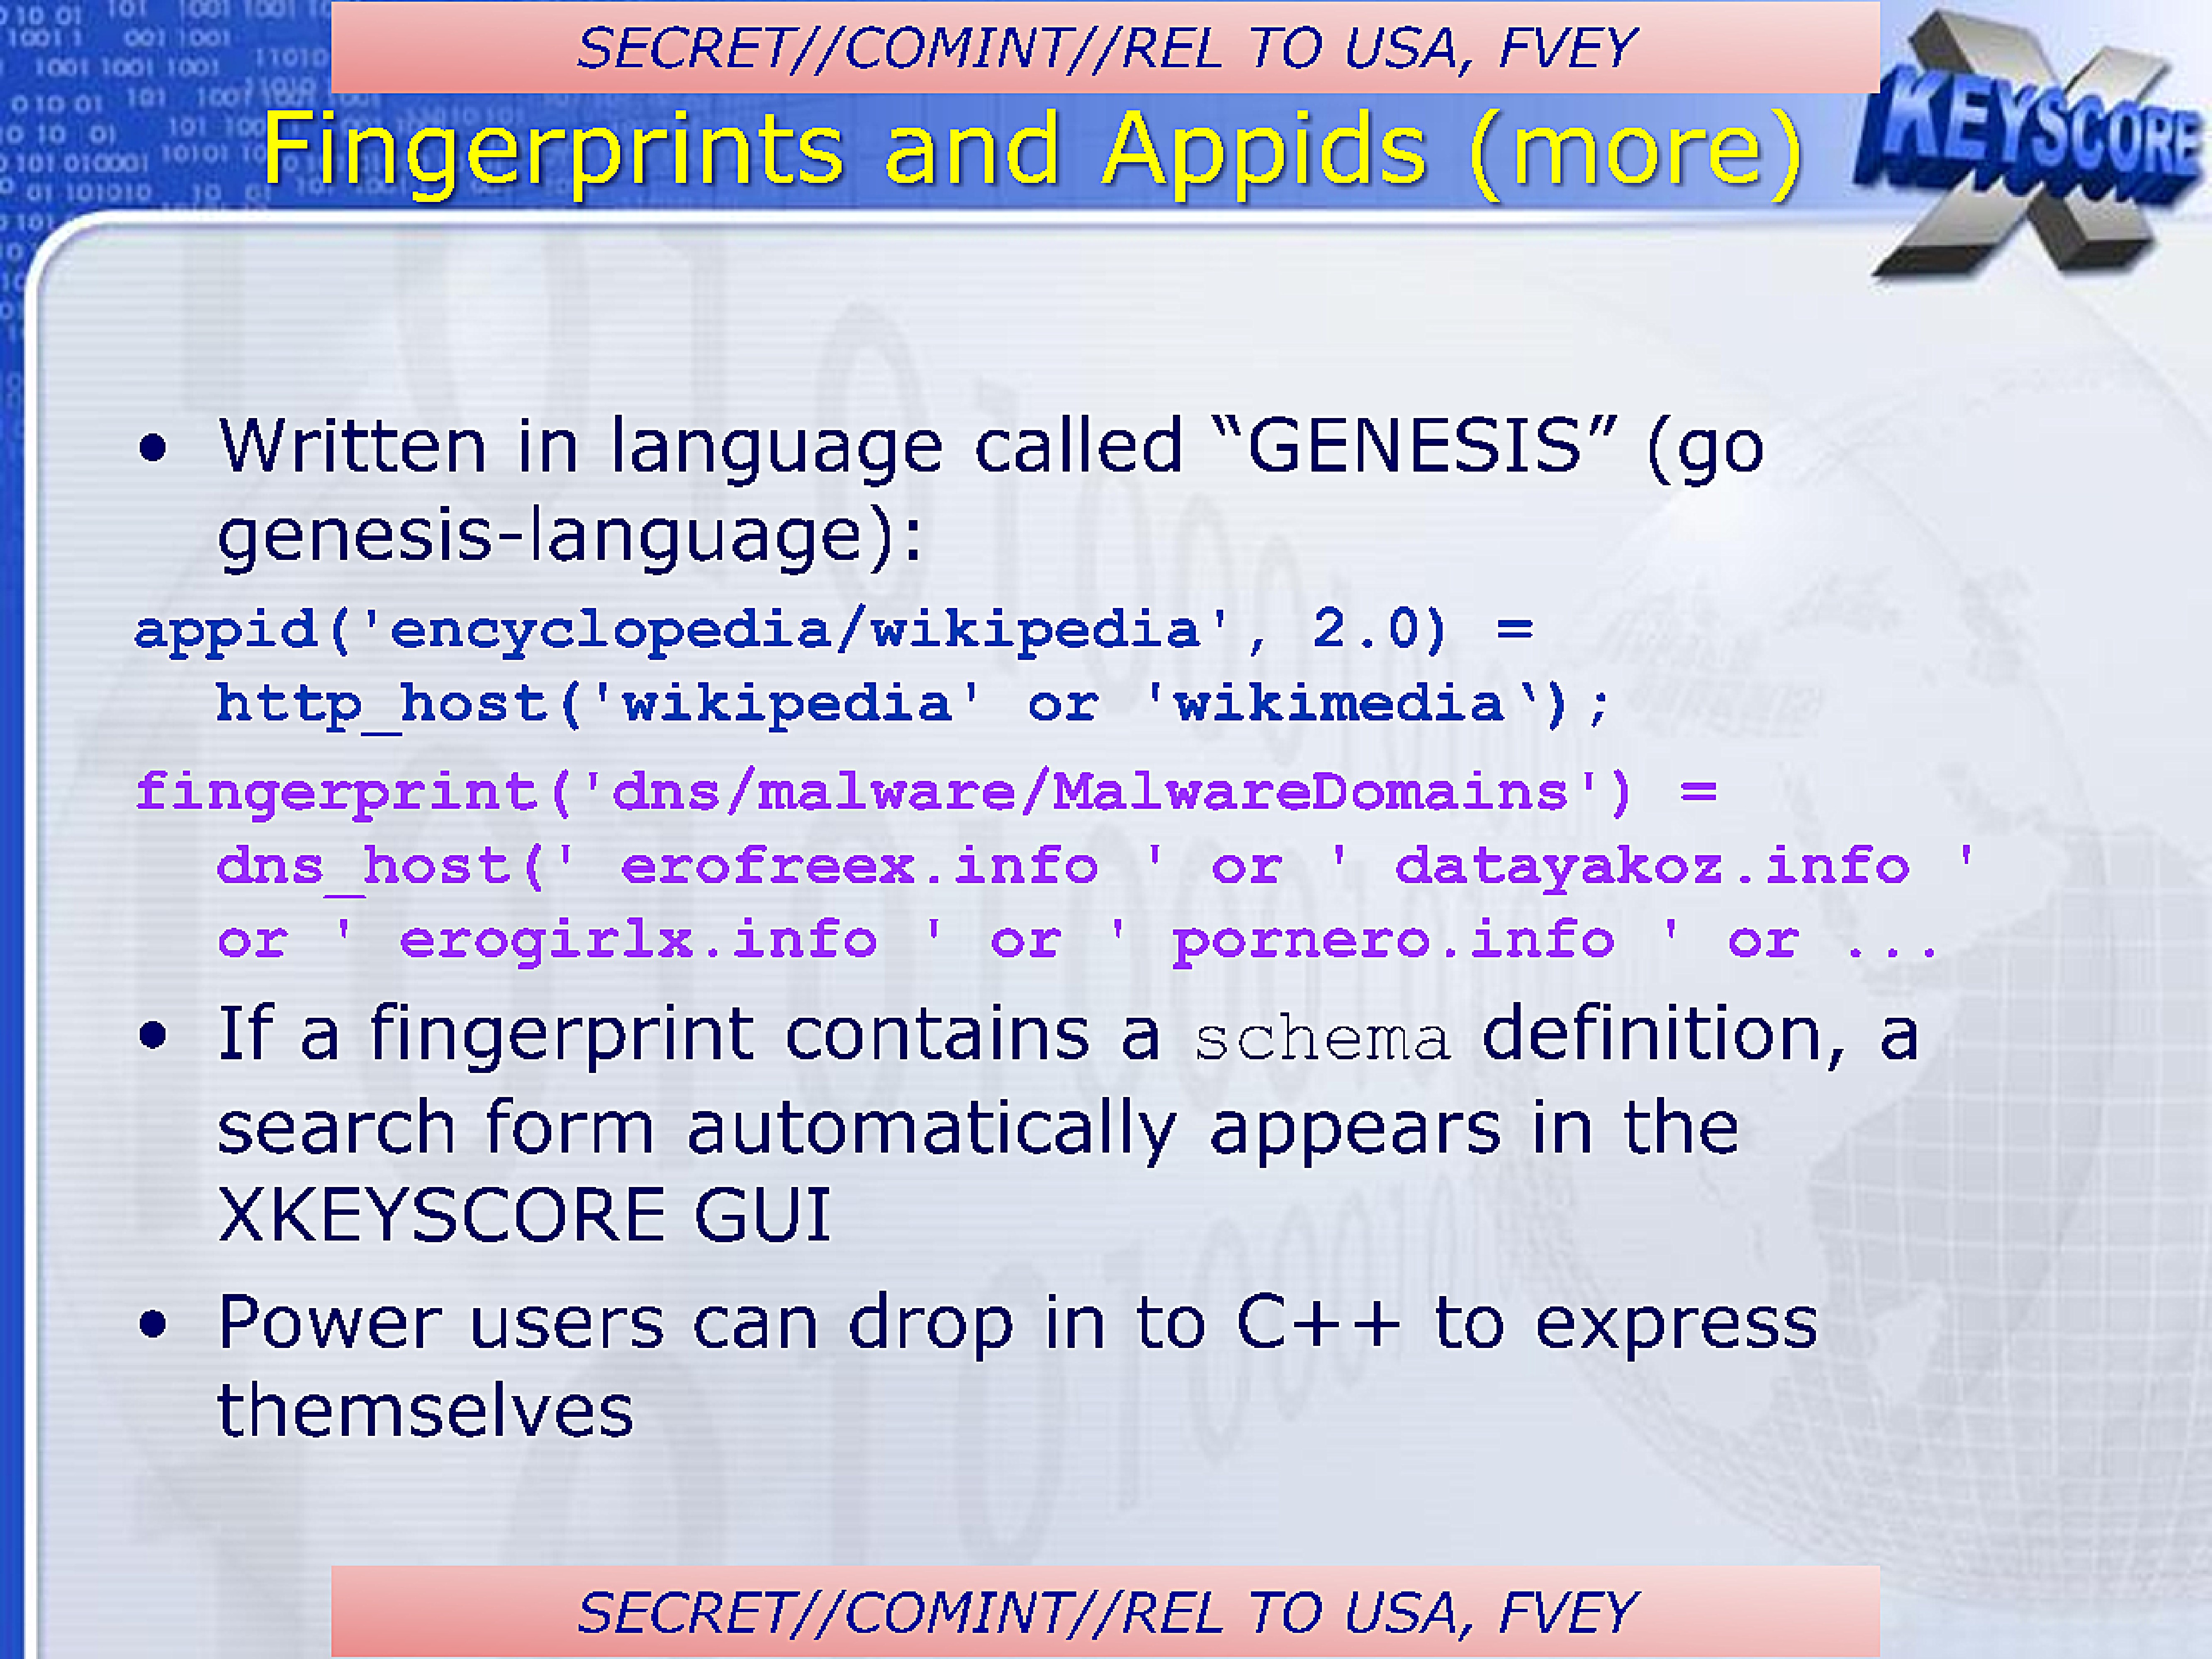
Fingerprints and Appids (more)
- Written in language called “GENESIS" (go genesis-language):
  appid('encyclopedia/wikipedia', 2.0) =
    http_host('wikipedia' or 'wikimedia`);
  fingerprint('dns/malware/MalwareDomains') =
    dns_host('erofreex.info' or 'datayakoz.info'
    or 'erogirlx.info' or 'pornero.info' or ...
- If a fingerprint contains a schema definition, a search form automatically appears in the XKEYSCORE GUI
- Power users can drop in to C++ to express themselves
SECRET//COMINT//REL TO USA, FVEY
SECRET//COMINT//REL TO USA, FVEY
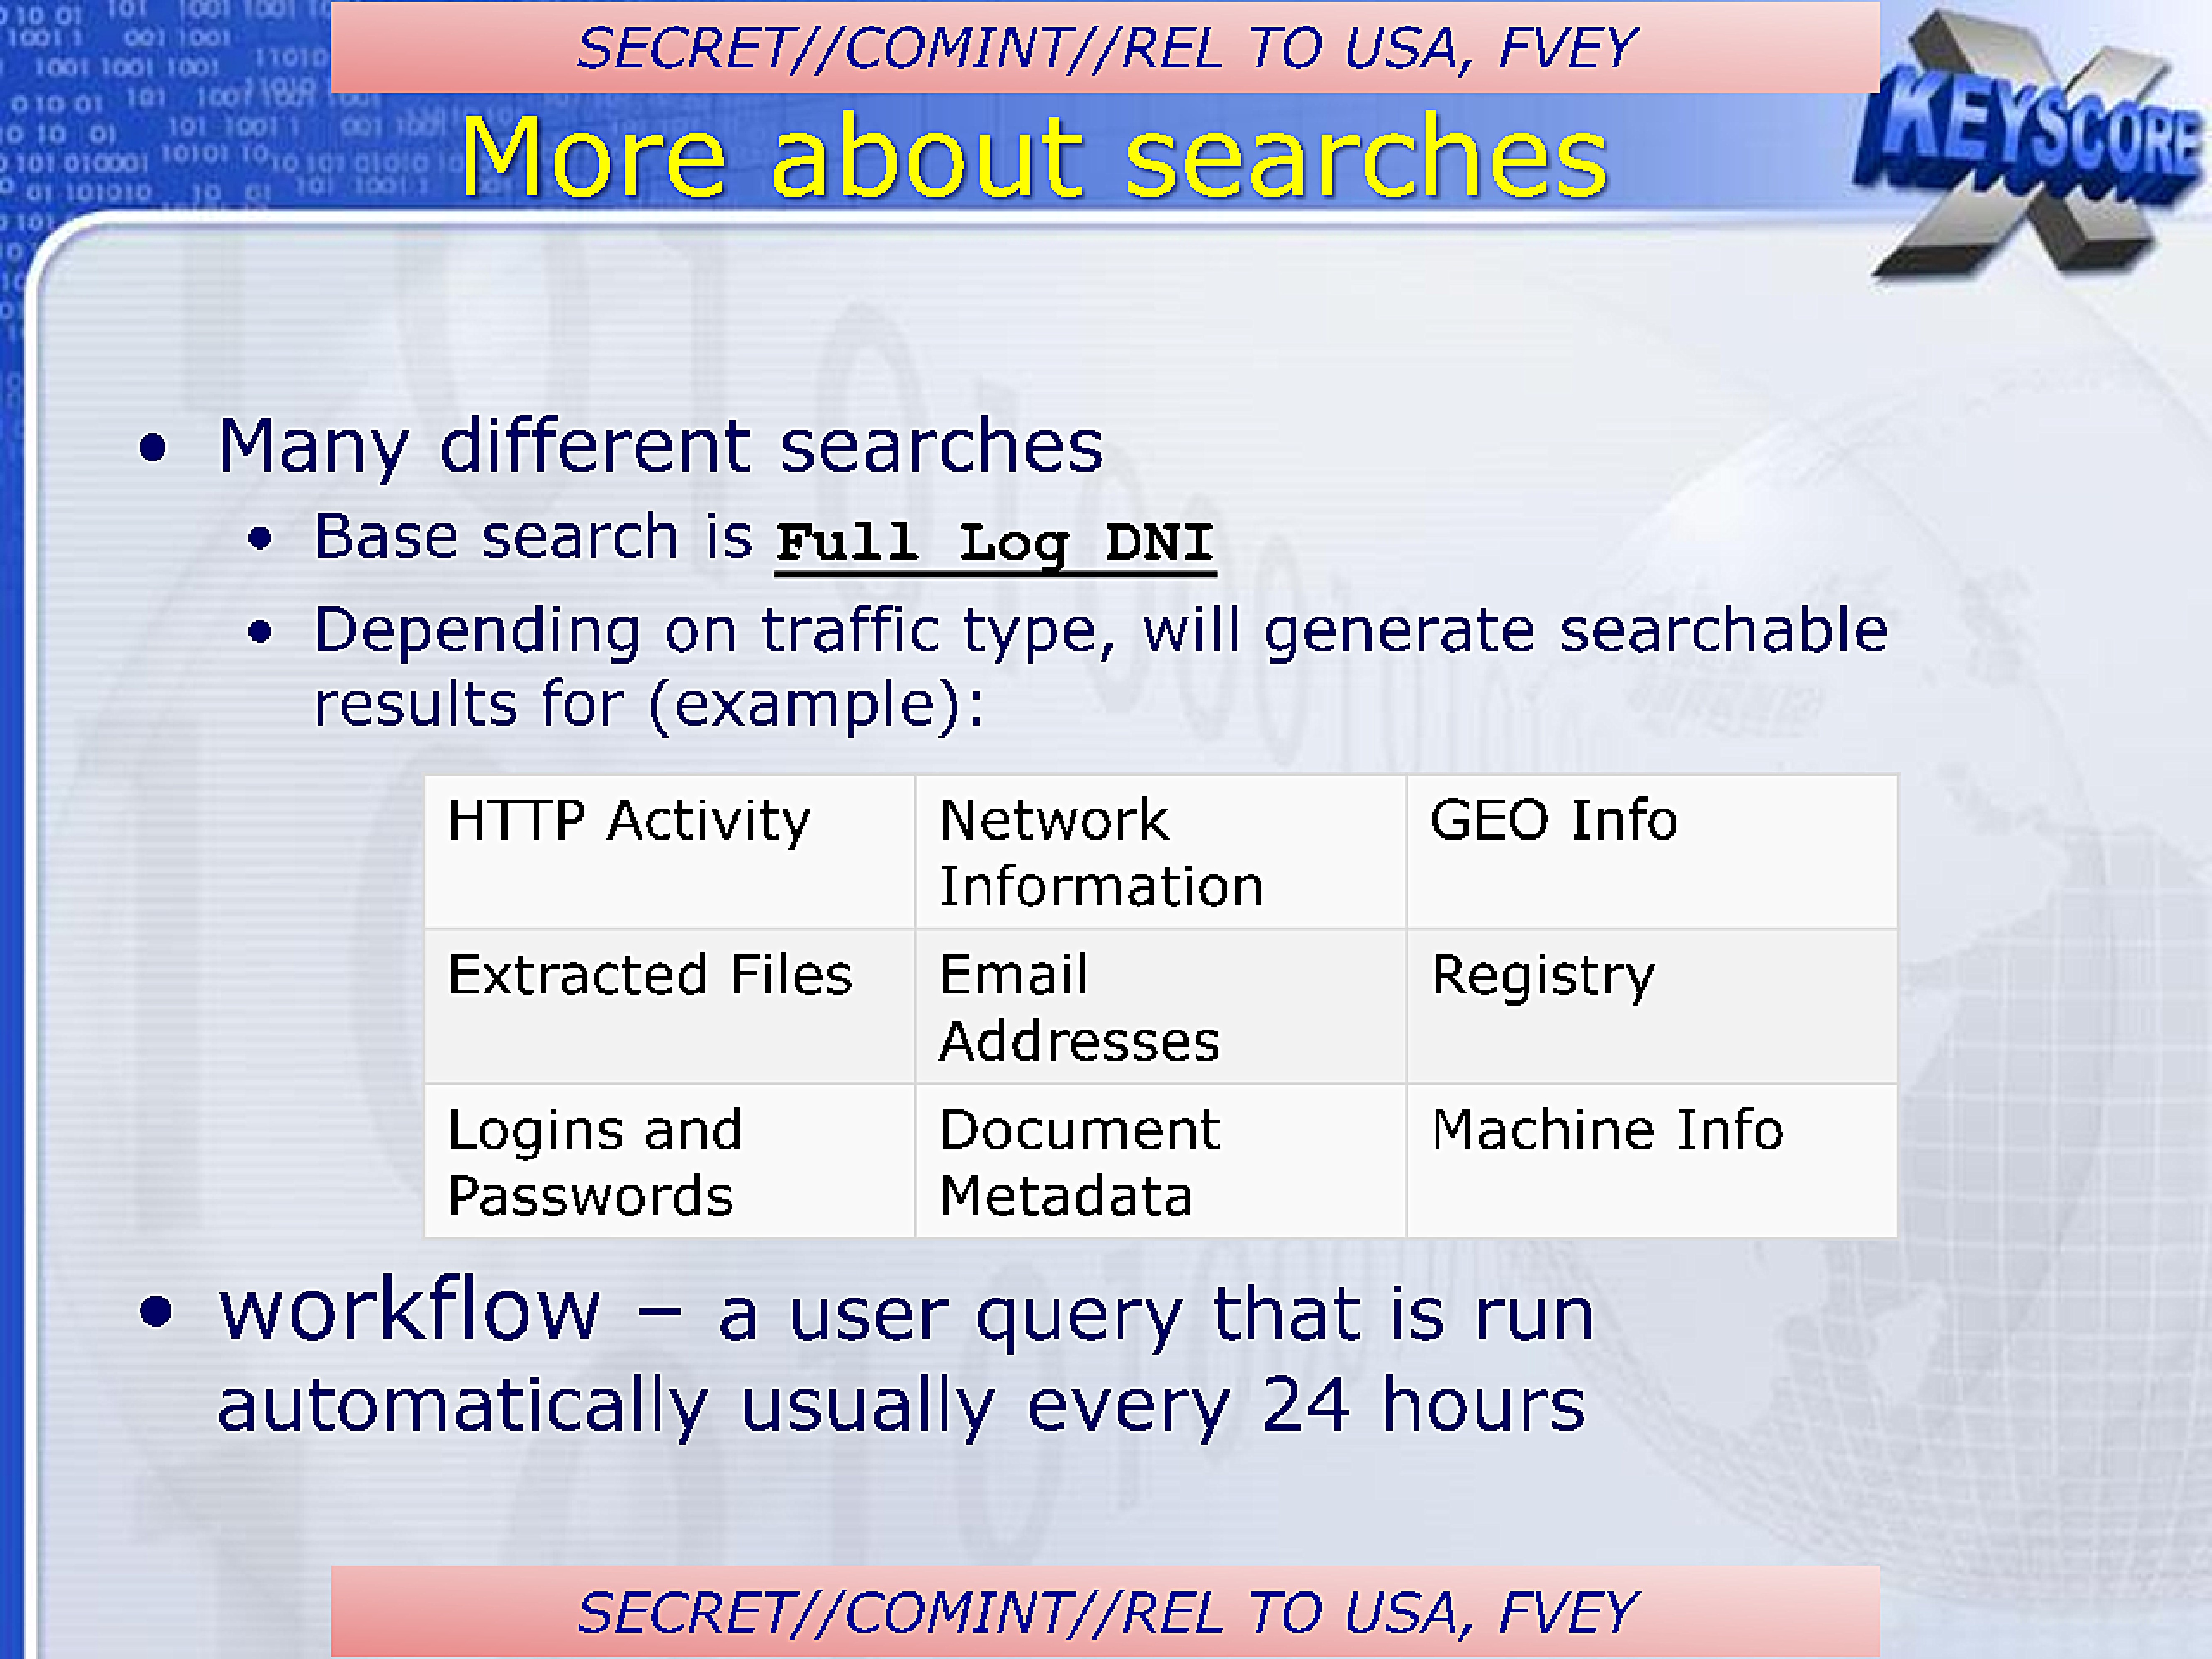
More about searches
- Many different searches
- Base search is Full Log DNI
- Depending on traffic type, will generate searchable results for (example):
| HTTP Activity | Network Information | GEO Info |
|---|---|---|
| Extracted Files | Email Addresses | Registry |
| Logins and Passwords | Document Metadata | Machine Info |
- workflow – a user query that is run automatically usually every 24 hours
SECRET//COMINT//REL TO USA, FVEY
SECRET//COMINT//REL TO USA, FVEY
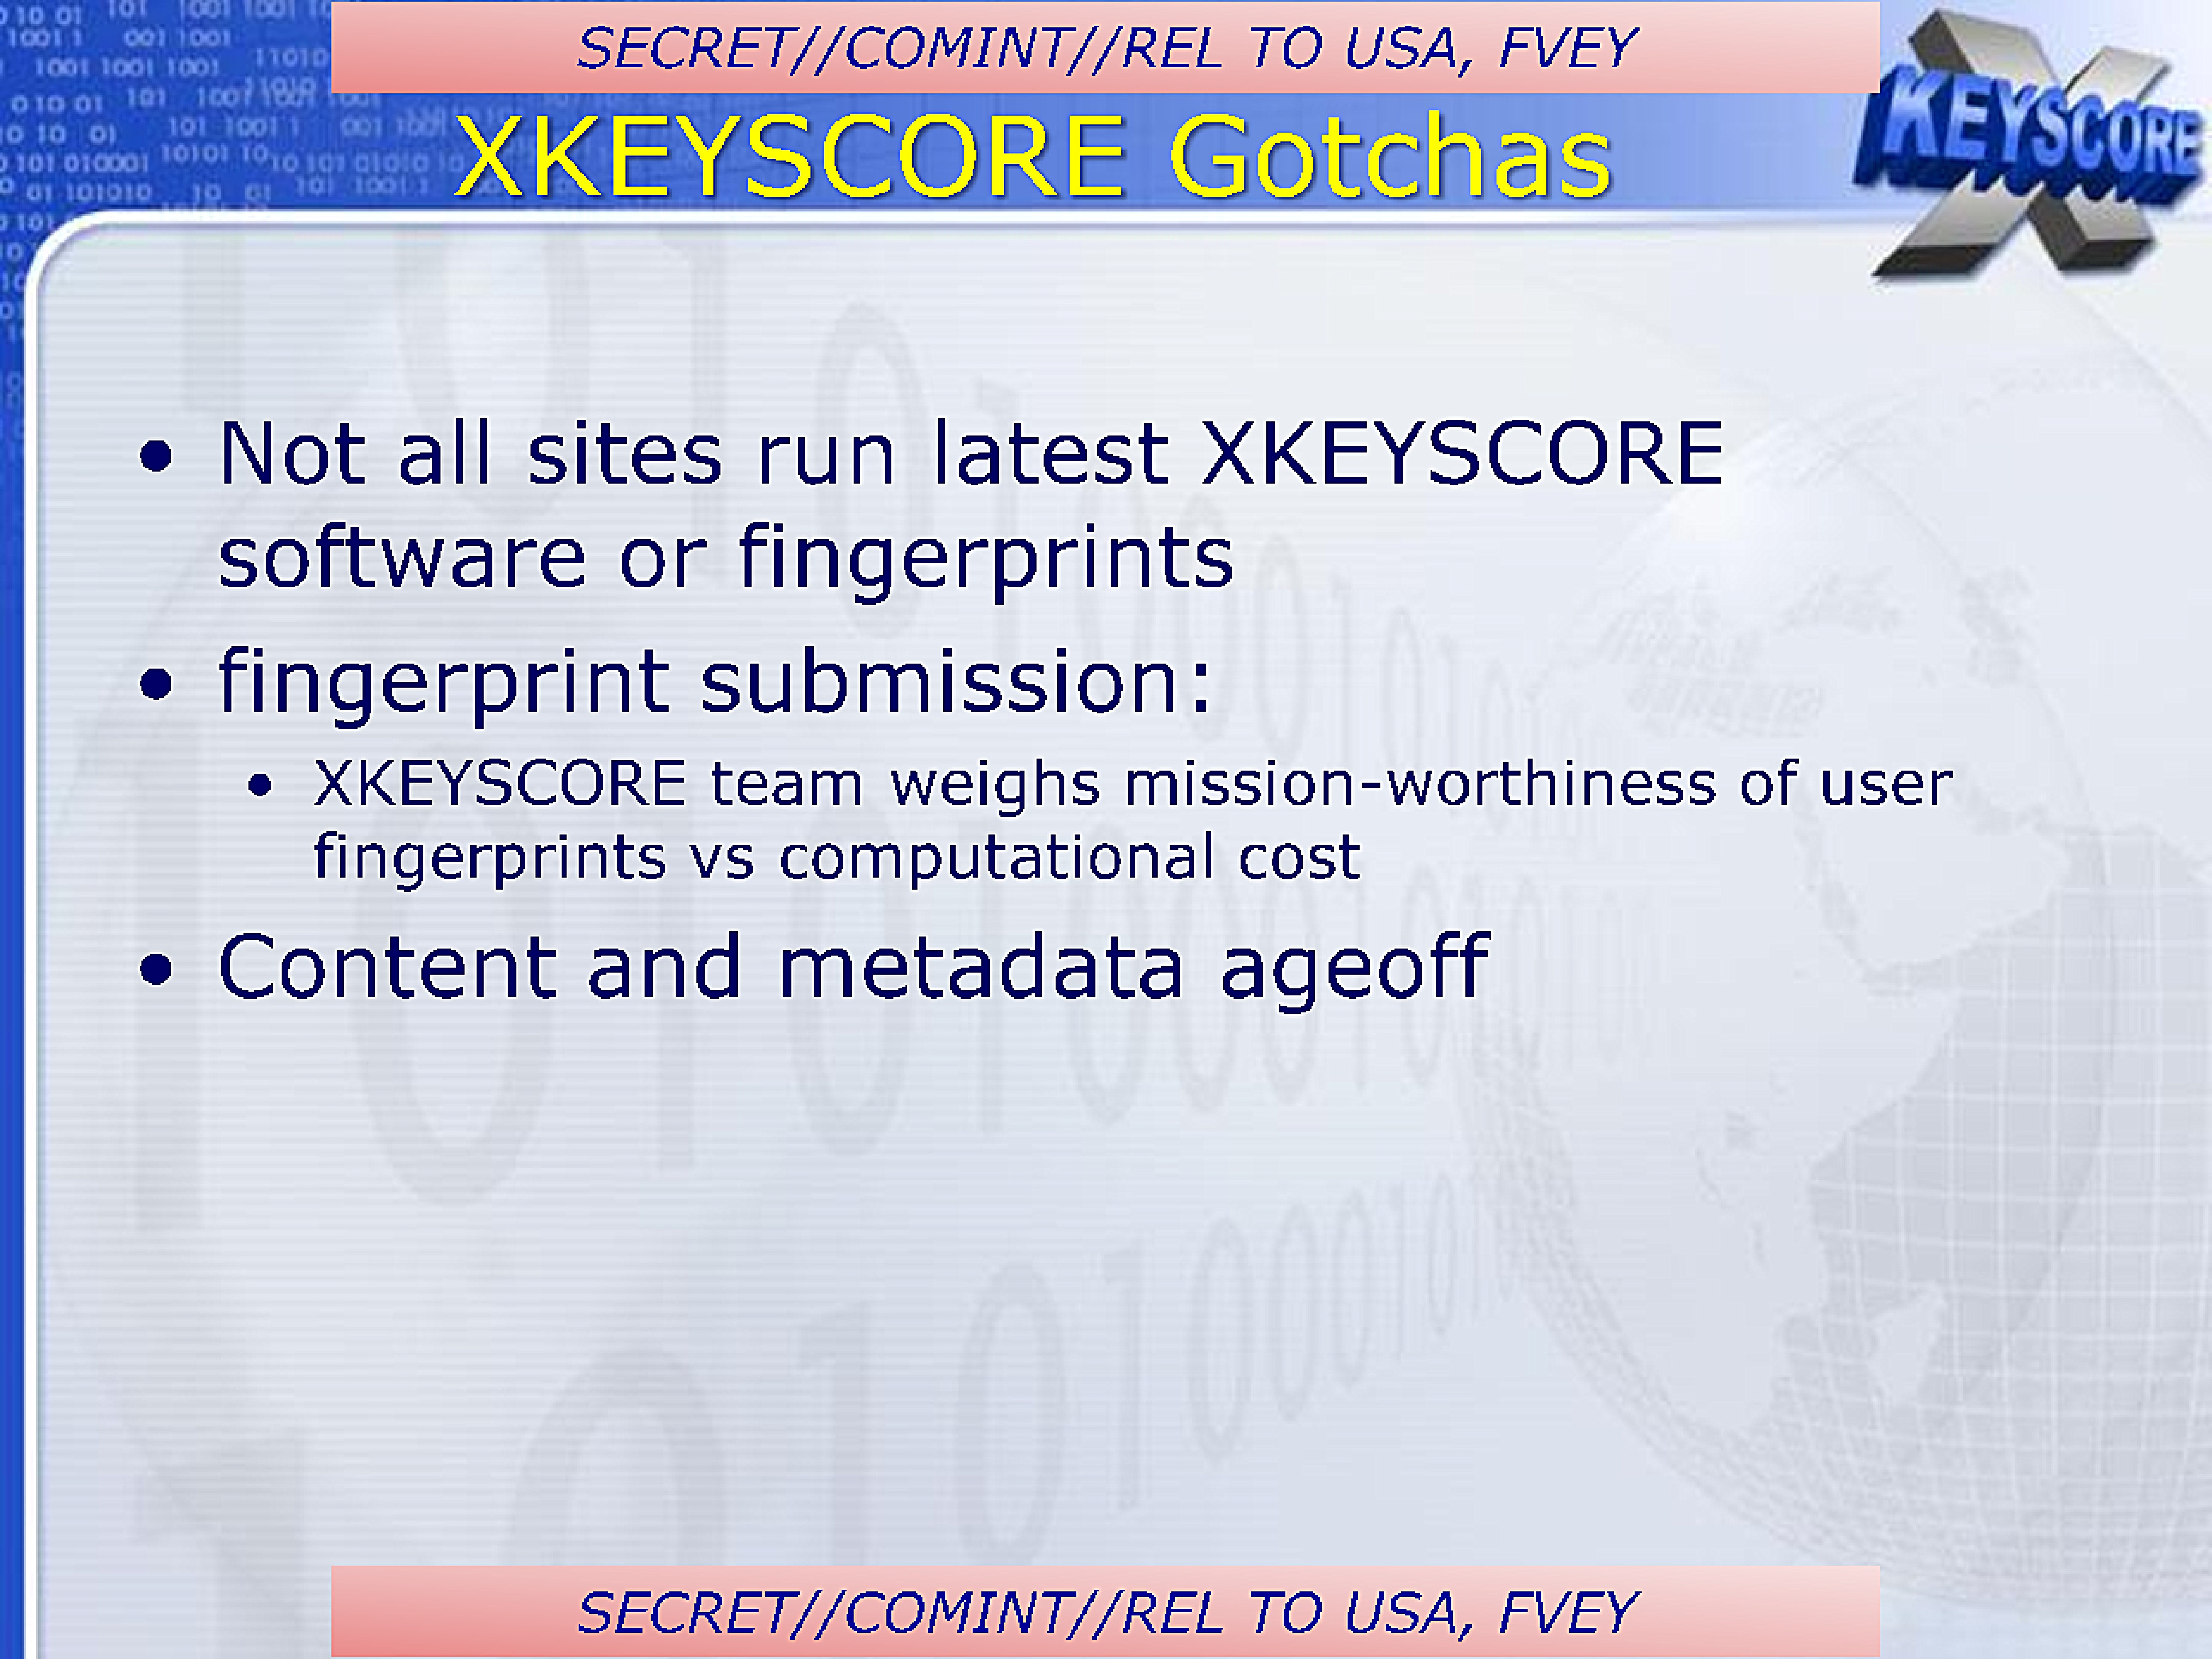
XKEYSCORE Gotchas
- Not all sites run latest XKEYSCORE software or fingerprints
- fingerprint submission:
- XKEYSCORE team weighs mission-worthiness of user fingerprints vs computational cost
- Content and metadata ageoff
SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
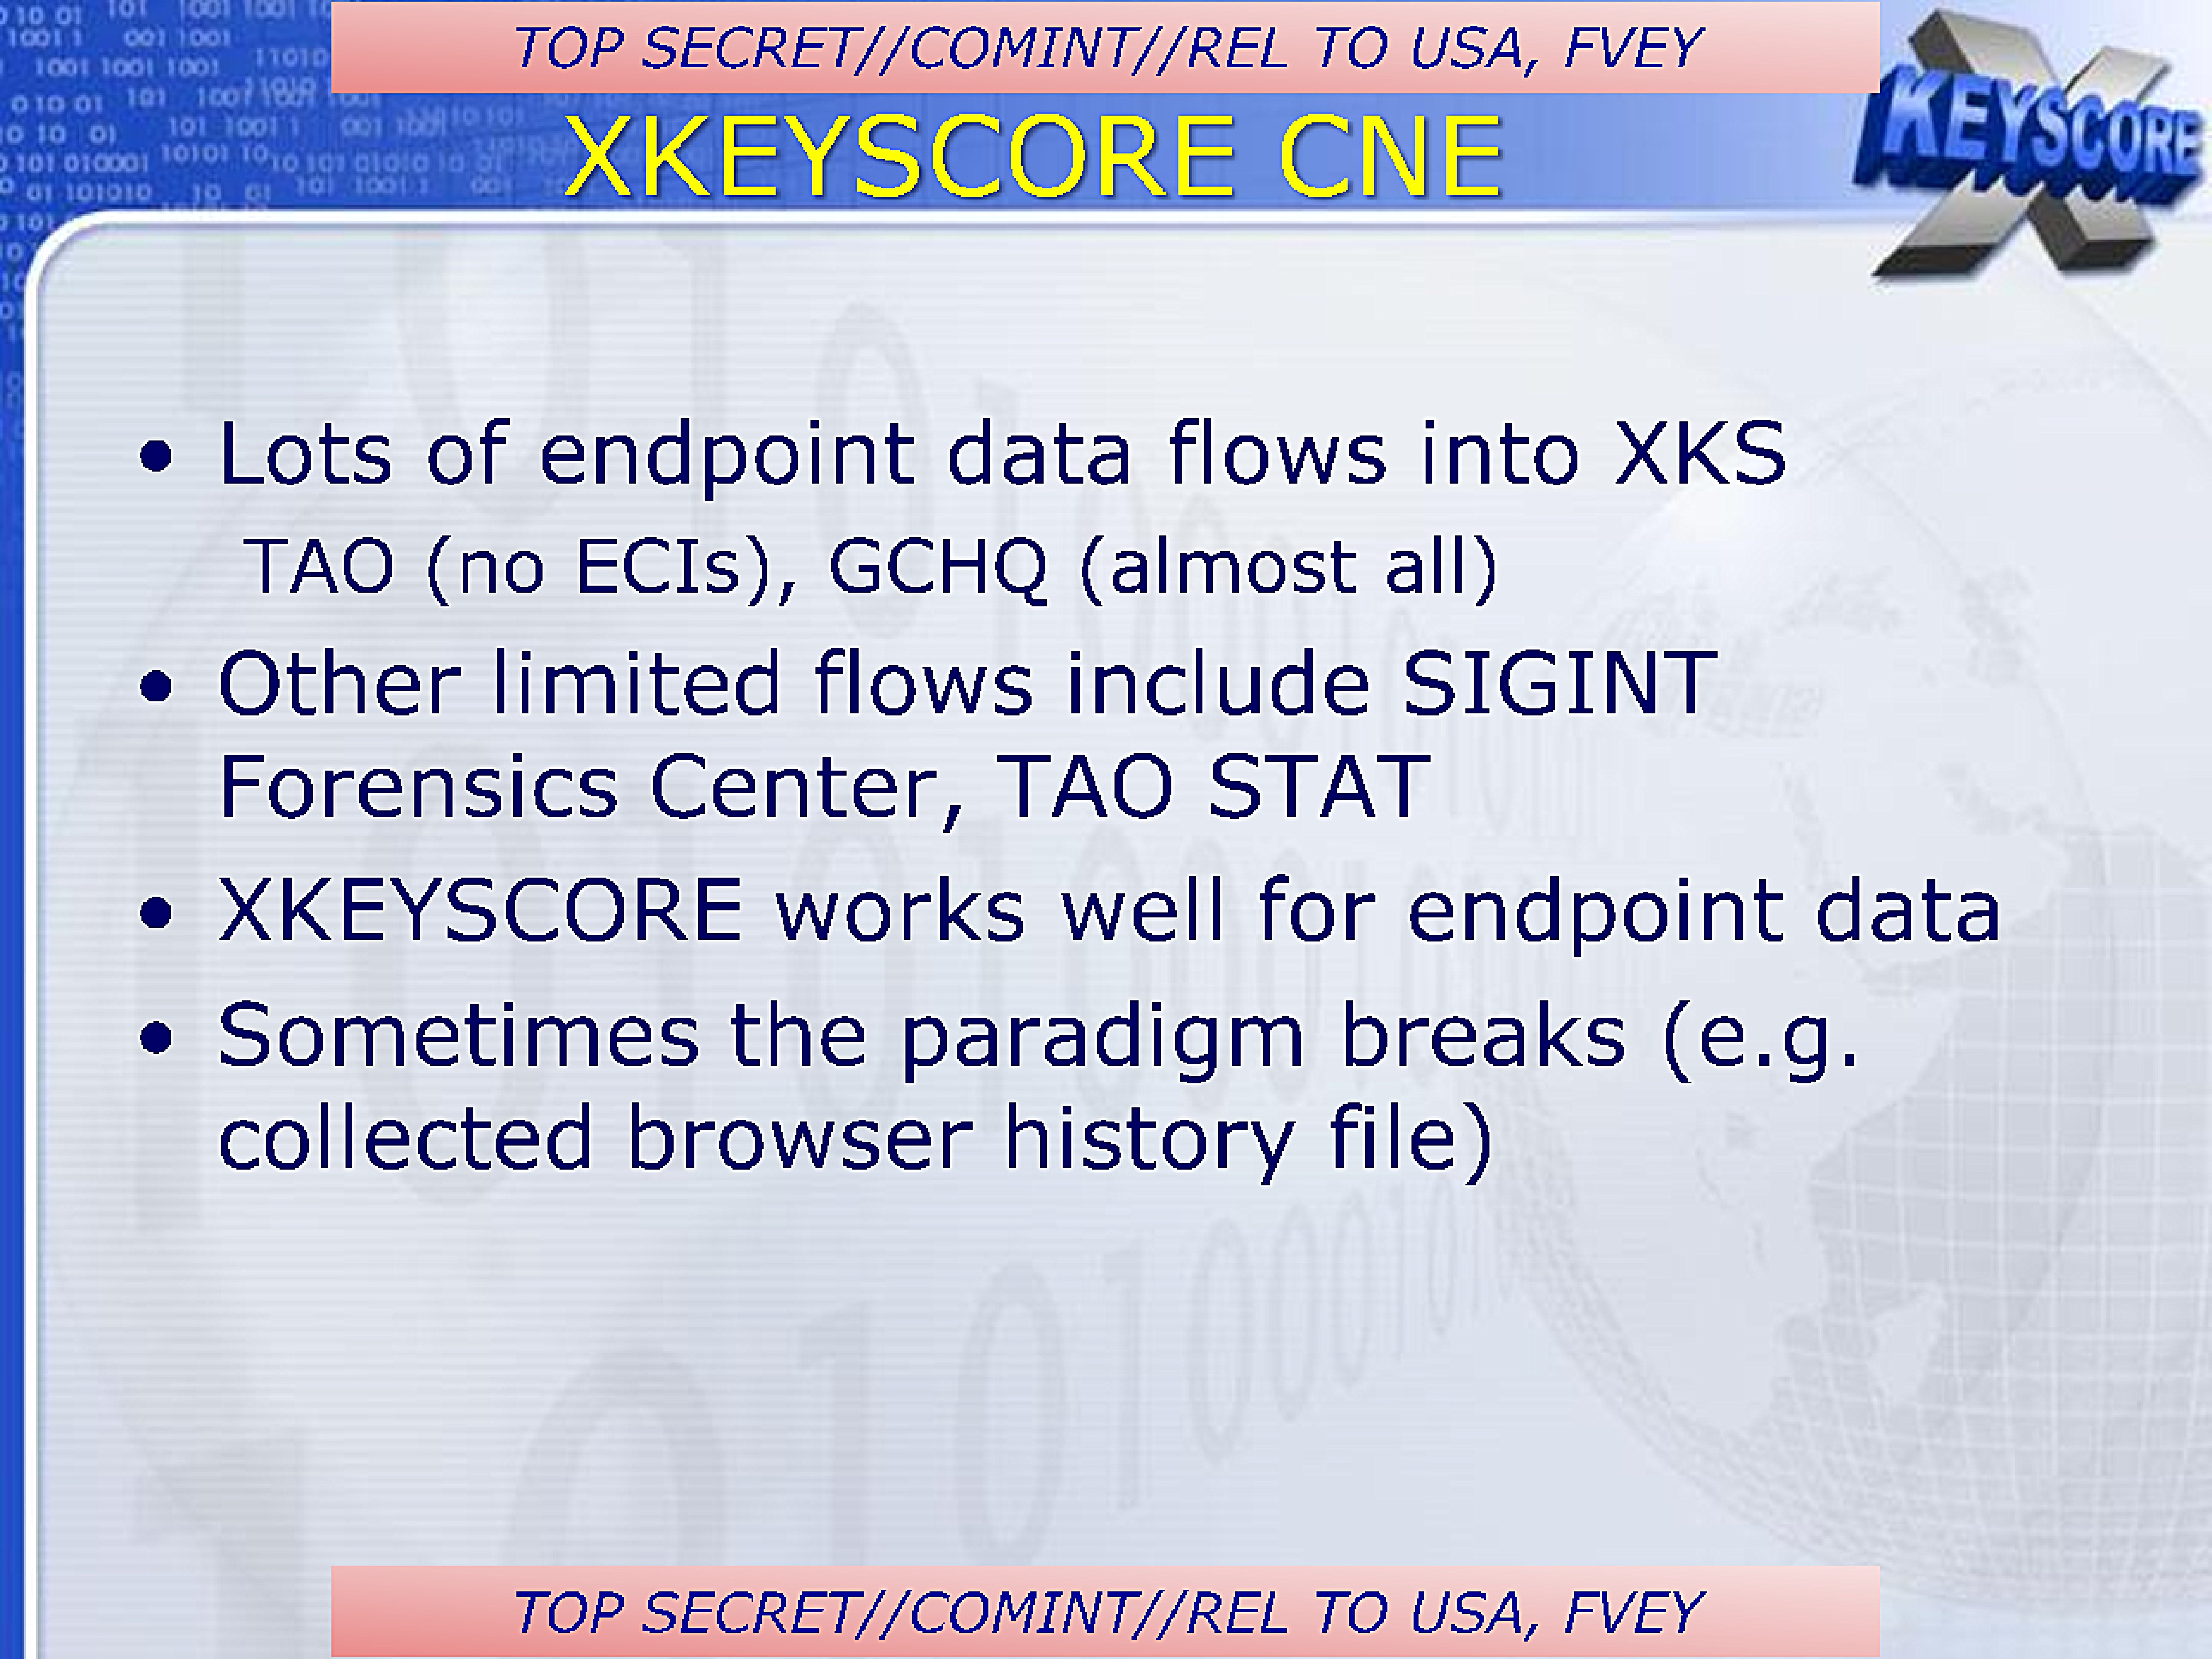
XKEYSCORE CNE
- Lots of endpoint data flows into XKS
- TAO (no ECIs), GCHQ (almost all)
- Other limited flows include SIGINT Forensics Center, TAO STAT
- XKEYSCORE works well for endpoint data
- Sometimes the paradigm breaks (e.g. collected browser history file)
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
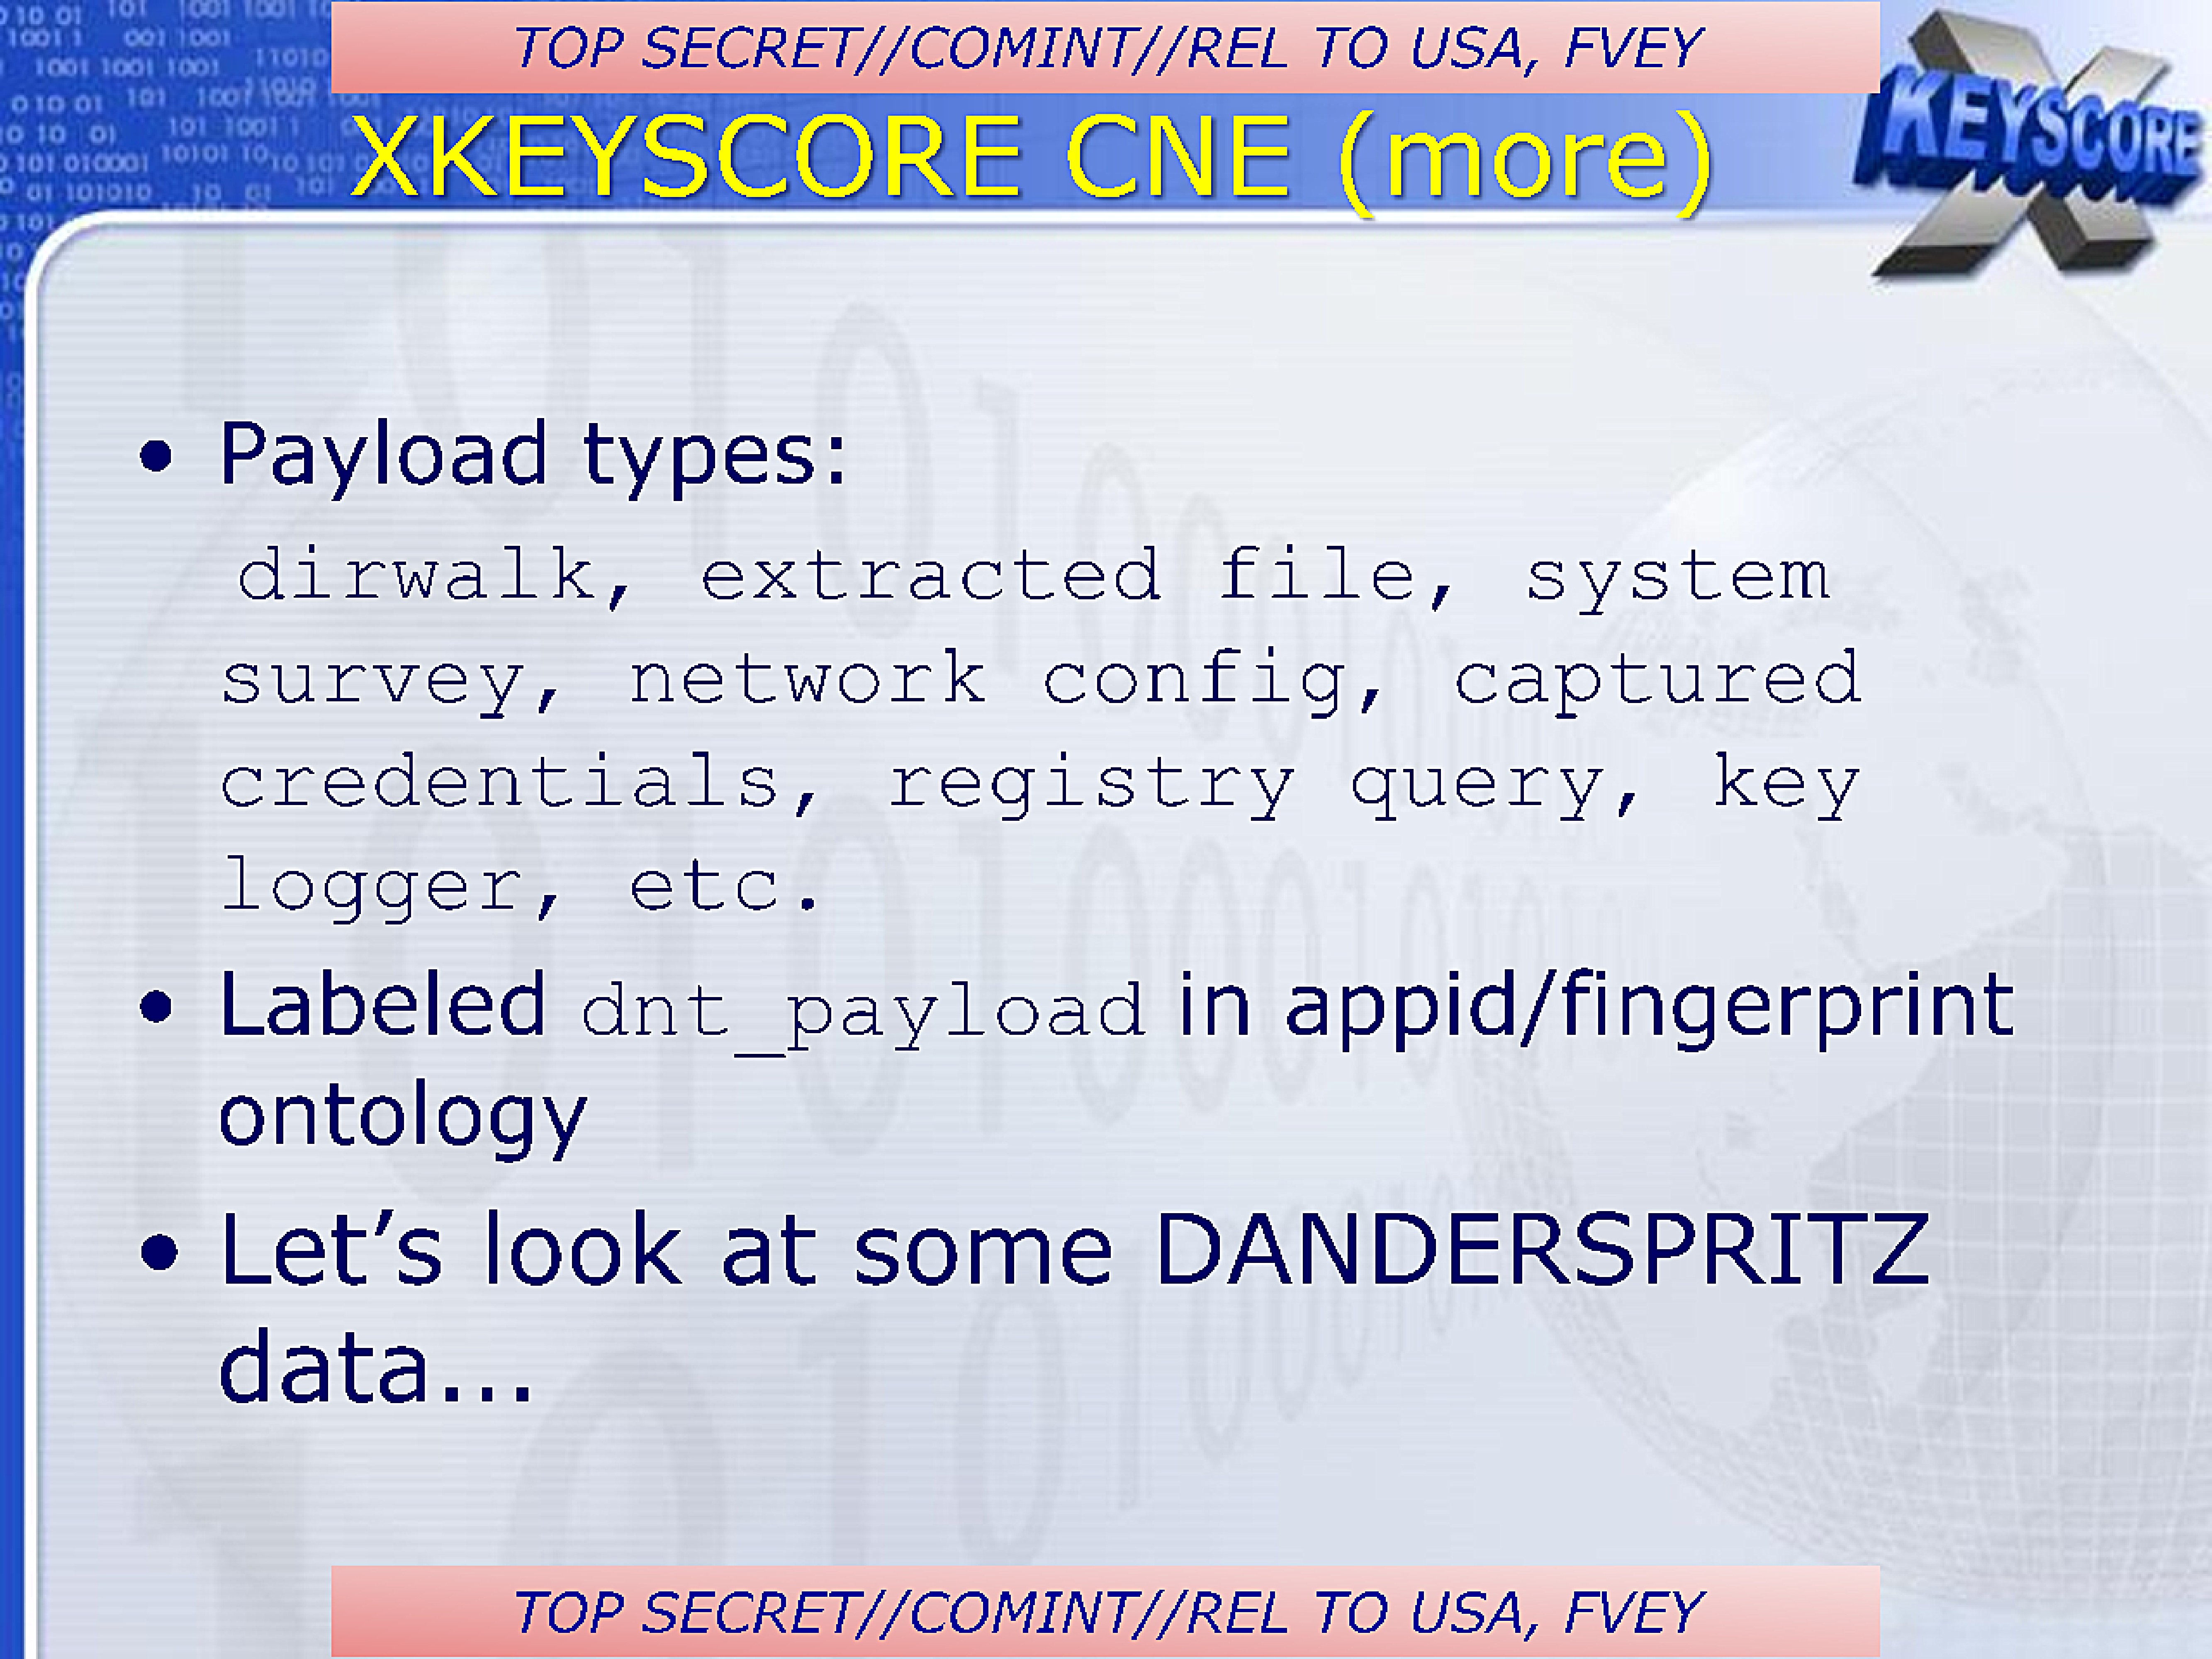
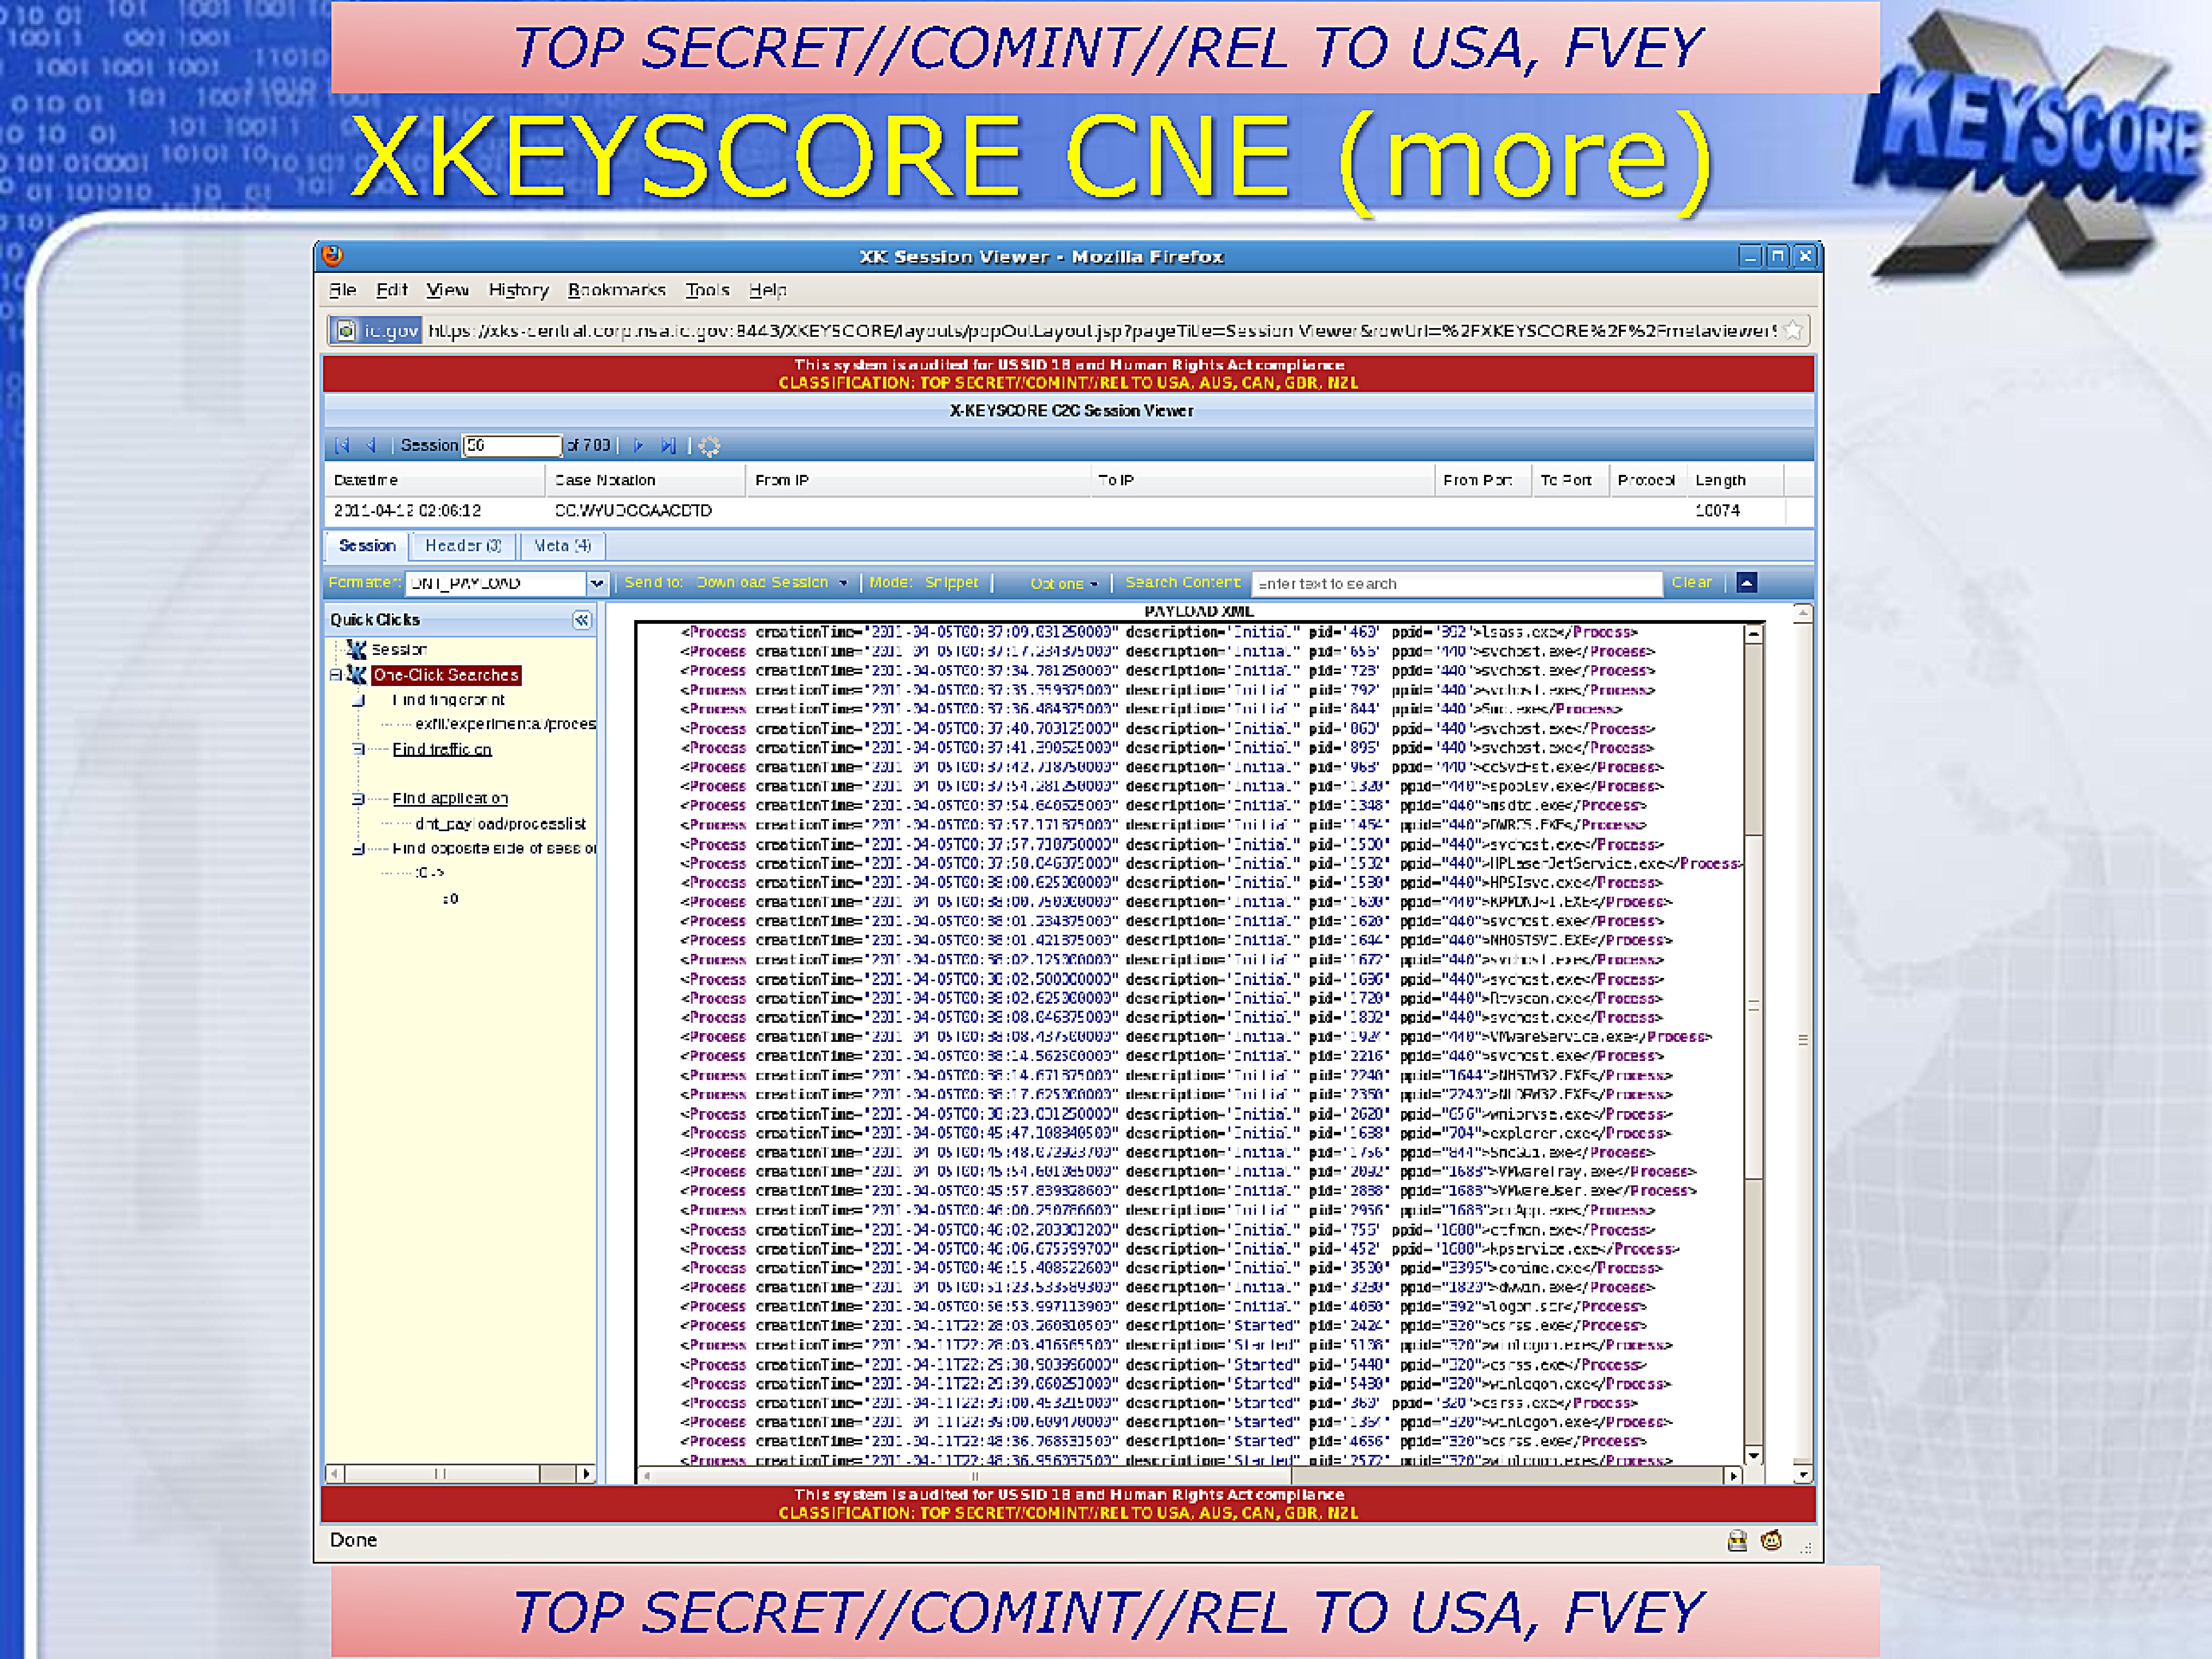
XKEYSCORE CNE (more)
- Payload types:
dirwalk, extracted file, system
survey, network config, captured
credentials, registry query, key
logger, etc.
- Labeled
dnt_payloadin appid/fingerprint ontology - Let's look at some DANDERSPRITZ data...
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
XKEYSCORE CNE (more)
XK Session Viewer - Mozilla Firefox
File Edit View History Bookmarks Tools Help
ic.gov  https://xks-central.corp.nsa.ic.gov:8443/XKEYSCORE/layouts/popOutLayout.jsp?pageTitle=Session+Viewer&rowUrl=%2FXKEYSCORE%2F%2Fmetaviewer$
This system is audited for US SID 18 and Human Rights Act compliance
CLASSIFICATION: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
X-KEYSCORE C2C Session Viewer

Session 56 of 703
Datetime              Case Notation       From IP              To IP            From Port  To Port  Protocol  Length
2011-04-13 02:06:12   CC.WYUDCCAACDTD                                                                         10074

Session  | Header (3) |  Meta (4)

Format:  DNT_PAYLOAD | Send to: Download Session | Mode: Snippet | Options | Search Content | enter text to search Clear

Quick Clicks
Session
One-Click Searches
  Find fingerprint
    exfil/experimental/proces
  Find traffic on
  Find application
    dnt_payload/processlist
  Find opposite side of sess o
    :0 ->
      :0

PAYLOAD XML
<Process creationTime="2011-04-05T00:37:09.031250000" description="Initia." pid="469" ppid="912">lsass.cxe</Process>
<Process creationTime="2011-04-05T00:37:27.281250000" description="Initia." pid="655" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:37:32.343750000" description="Initia." pid="728" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:37:35.359375000" description="Initia." pid="792" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:37:36.484375000" description="Initia." pid="844" ppid="440">svc..exe</Process>
<Process creationTime="2011-04-05T00:37:40.703125000" description="Initia." pid="867" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:37:41.421875000" description="Initia." pid="895" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:37:42.218750000" description="Initia." pid="968" ppid="440">ccSvcHst.exe</Process>
<Process creationTime="2011-04-05T00:37:44.281250000" description="Initia." pid="1320" ppid="440">spoolsv.exe</Process>
<Process creationTime="2011-04-05T00:37:54.640625000" description="Initia." pid="1348" ppid="440">msdtc.exe</Process>
<Process creationTime="2011-04-05T00:37:57.171875000" description="Initia." pid="1454" ppid="440">NWRCS.EXE</Process>
<Process creationTime="2011-04-05T00:37:57.718750000" description="Initia." pid="1500" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:37:50.046875000" description="Initia." pid="1532" ppid="440">HPLaserJetService.exe</Process>
<Process creationTime="2011-04-05T00:38:00.625000000" description="Initia." pid="1539" ppid="440">HPSIsvc.exe</Process>
<Process creationTime="2011-04-05T00:38:00.750000000" description="Initia." pid="1630" ppid="440">KRPRDU-1.EXE</Process>
<Process creationTime="2011-04-05T00:38:01.234375000" description="Initia." pid="1620" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:38:01.421875000" description="Initia." pid="1668" ppid="440">MHOSTSVC.EXE</Process>
<Process creationTime="2011-04-05T00:38:01.125000000" description="Initia." pid="1672" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:38:02.500000000" description="Initia." pid="1696" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:38:02.625000000" description="Initia." pid="1720" ppid="440">fltvscon.exe</Process>
<Process creationTime="2011-04-05T00:38:04.640625000" description="Initia." pid="1832" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:38:08.437500000" description="Initia." pid="964" ppid="440">VMwareService.exe</Process>
<Process creationTime="2011-04-05T00:38:14.562500000" description="Initia." pid="1620" ppid="440">svchost.exe</Process>
<Process creationTime="2011-04-05T00:38:14.671875000" description="Initia." pid="2240" ppid="440">UIHSTMP7.FXP</Process>
<Process creationTime="2011-04-05T00:38:17.625000000" description="Initia." pid="2390" ppid="2243">SIDRMP3.FXP</Process>
<Process creationTime="2011-04-05T00:38:23.031250000" description="Initia." pid="2620" ppid="656">wmiprvse.exe</Process>
<Process creationTime="2011-04-05T00:38:45:47.108340500" description="Initia." pid="1638" ppid="704">explorer.exe</Process>
<Process creationTime="2011-04-05T00:45:48.012923700" description="Started" pid="1756" ppid="844">hncau.exe</Process>
<Process creationTime="2011-04-05T00:45:51.601365000" description="Initia." pid="2092" ppid="1688">VMwareTray.exe</Process>
<Process creationTime="2011-04-05T00:45:57.839938660" description="Initia." pid="2888" ppid="1688">VMwareUser.exe</Process>
<Process creationTime="2011-04-05T00:46:00.250078600" description="Initia." pid="1688">jusched.exe</Process>
<Process creationTime="2011-04-05T00:46:02.203003200" description="Initia." pid="755" ppid="1000">ccfmon.exe</Process>
<Process creationTime="2011-04-05T00:46:06.675999700" description="Initia." pid="452" ppid="1000">kpsservice.exe</Process>
<Process creationTime="2011-04-05T00:46:15.408822600" description="Initia." pid="3530" ppid="3395">conime.exe</Process>
<Process creationTime="2011-04-05T01:23.535889300" description="Initia." pid="3280" ppid="1820">dwwm.exe</Process>
<Process creationTime="2011-04-05T00:56:53.997113900" description="Initia." pid="392" ppid="320">logon.scr</Process>
<Process creationTime="2011-04-11T22:26:03.066816500" description="Started" pid="2424" ppid="320">csrss.exe</Process>
<Process creationTime="2011-04-11T22:26:03.416685500" description="Started" pid="5136" ppid="320">winlogon.exe</Process>
<Process creationTime="2011-04-11T22:29:30.503950000" description="Started" pid="5440" ppid="320">csrss.exe</Process>
<Process creationTime="2011-04-11T22:29:39.066816500" description="Started" pid="5430" ppid="320">winlogon.exe</Process>
<Process creationTime="2011-04-11T22:48:31.000.453235000" description="Started" pid="368" ppid="320">csrss.exe</Process>
<Process creationTime="2011-04-11T22:48:34" description="Started" pid="354" ppid="320">winlogon.exe</Process>
<Process creationTime="2011-04-11T22:48:36.768533500" description="Started" pid="4656" ppid="320">csrss.exe</Process>
<Process creationTime="2011-04-11T22:48:46.766533500" description="Started" pid="2572" ppid="320">winlogon.exe</Process>

This system is audited for USSID 18 and Human Rights Act compliance
CLASSIFICATION: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL

Done
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
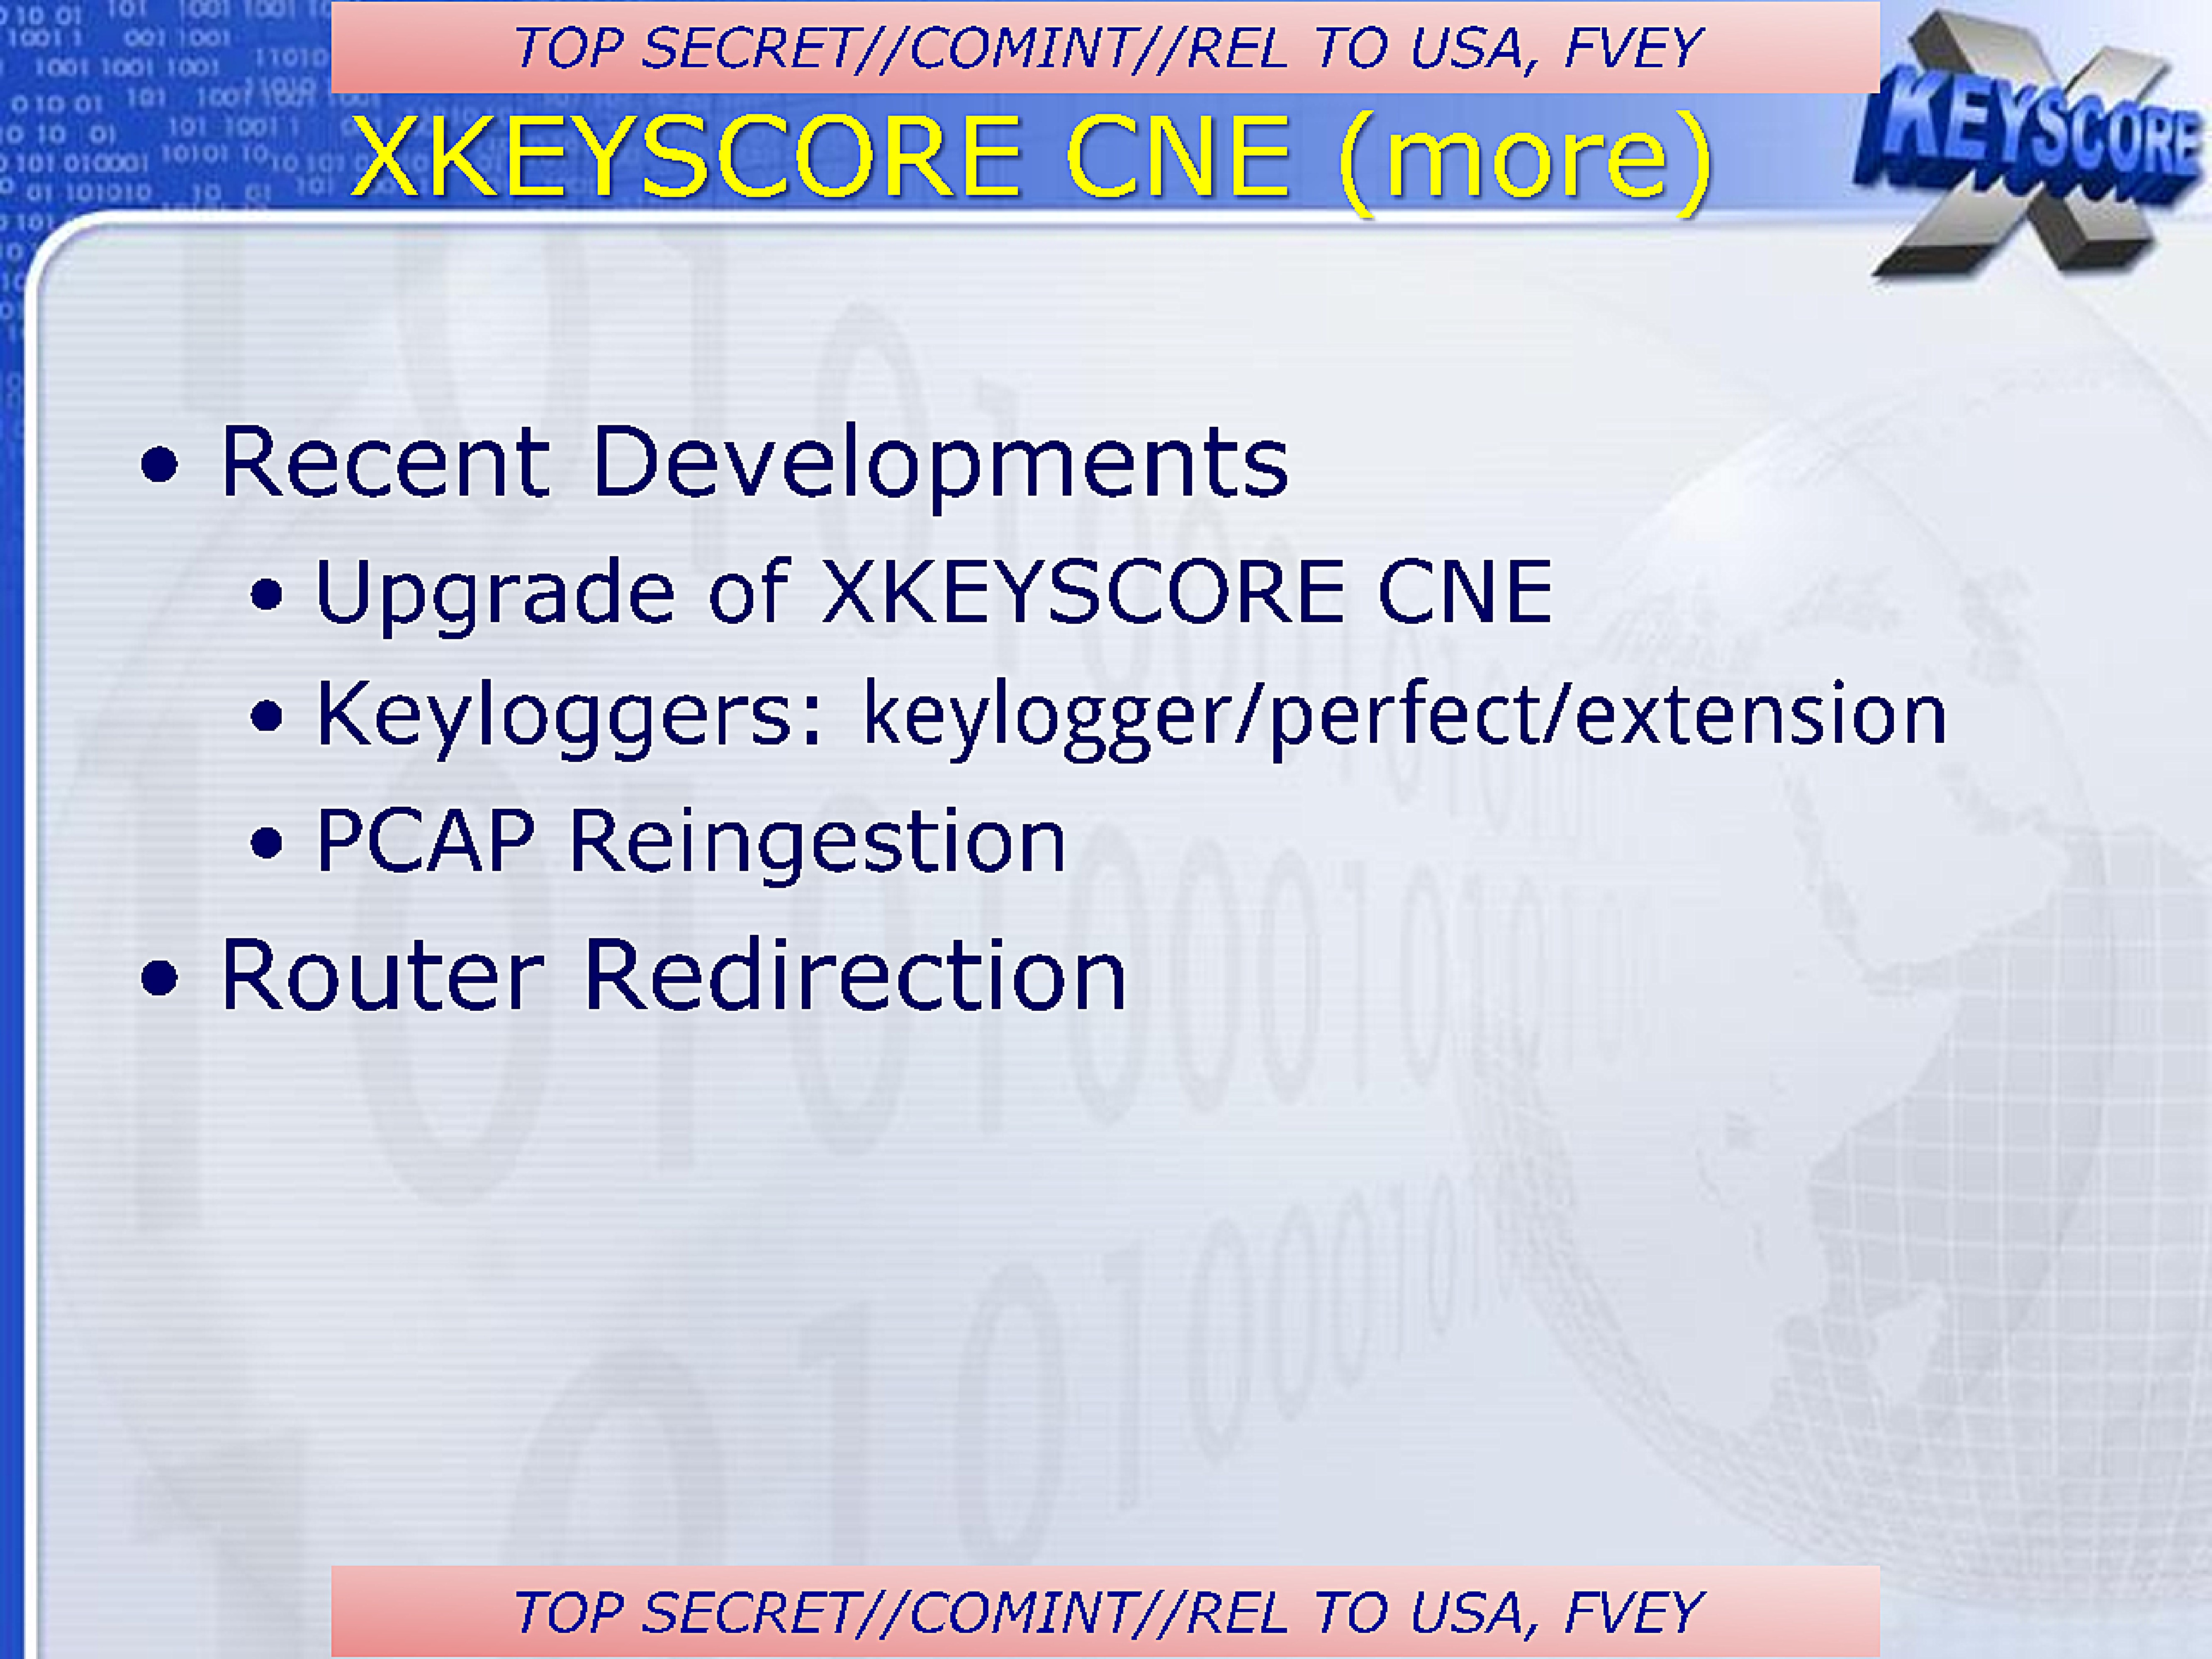
XKEYSCORE CNE (more)
- Recent Developments
- Upgrade of XKEYSCORE CNE
- Keyloggers: keylogger/perfect/extension
- PCAP Reingestion
- Router Redirection
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
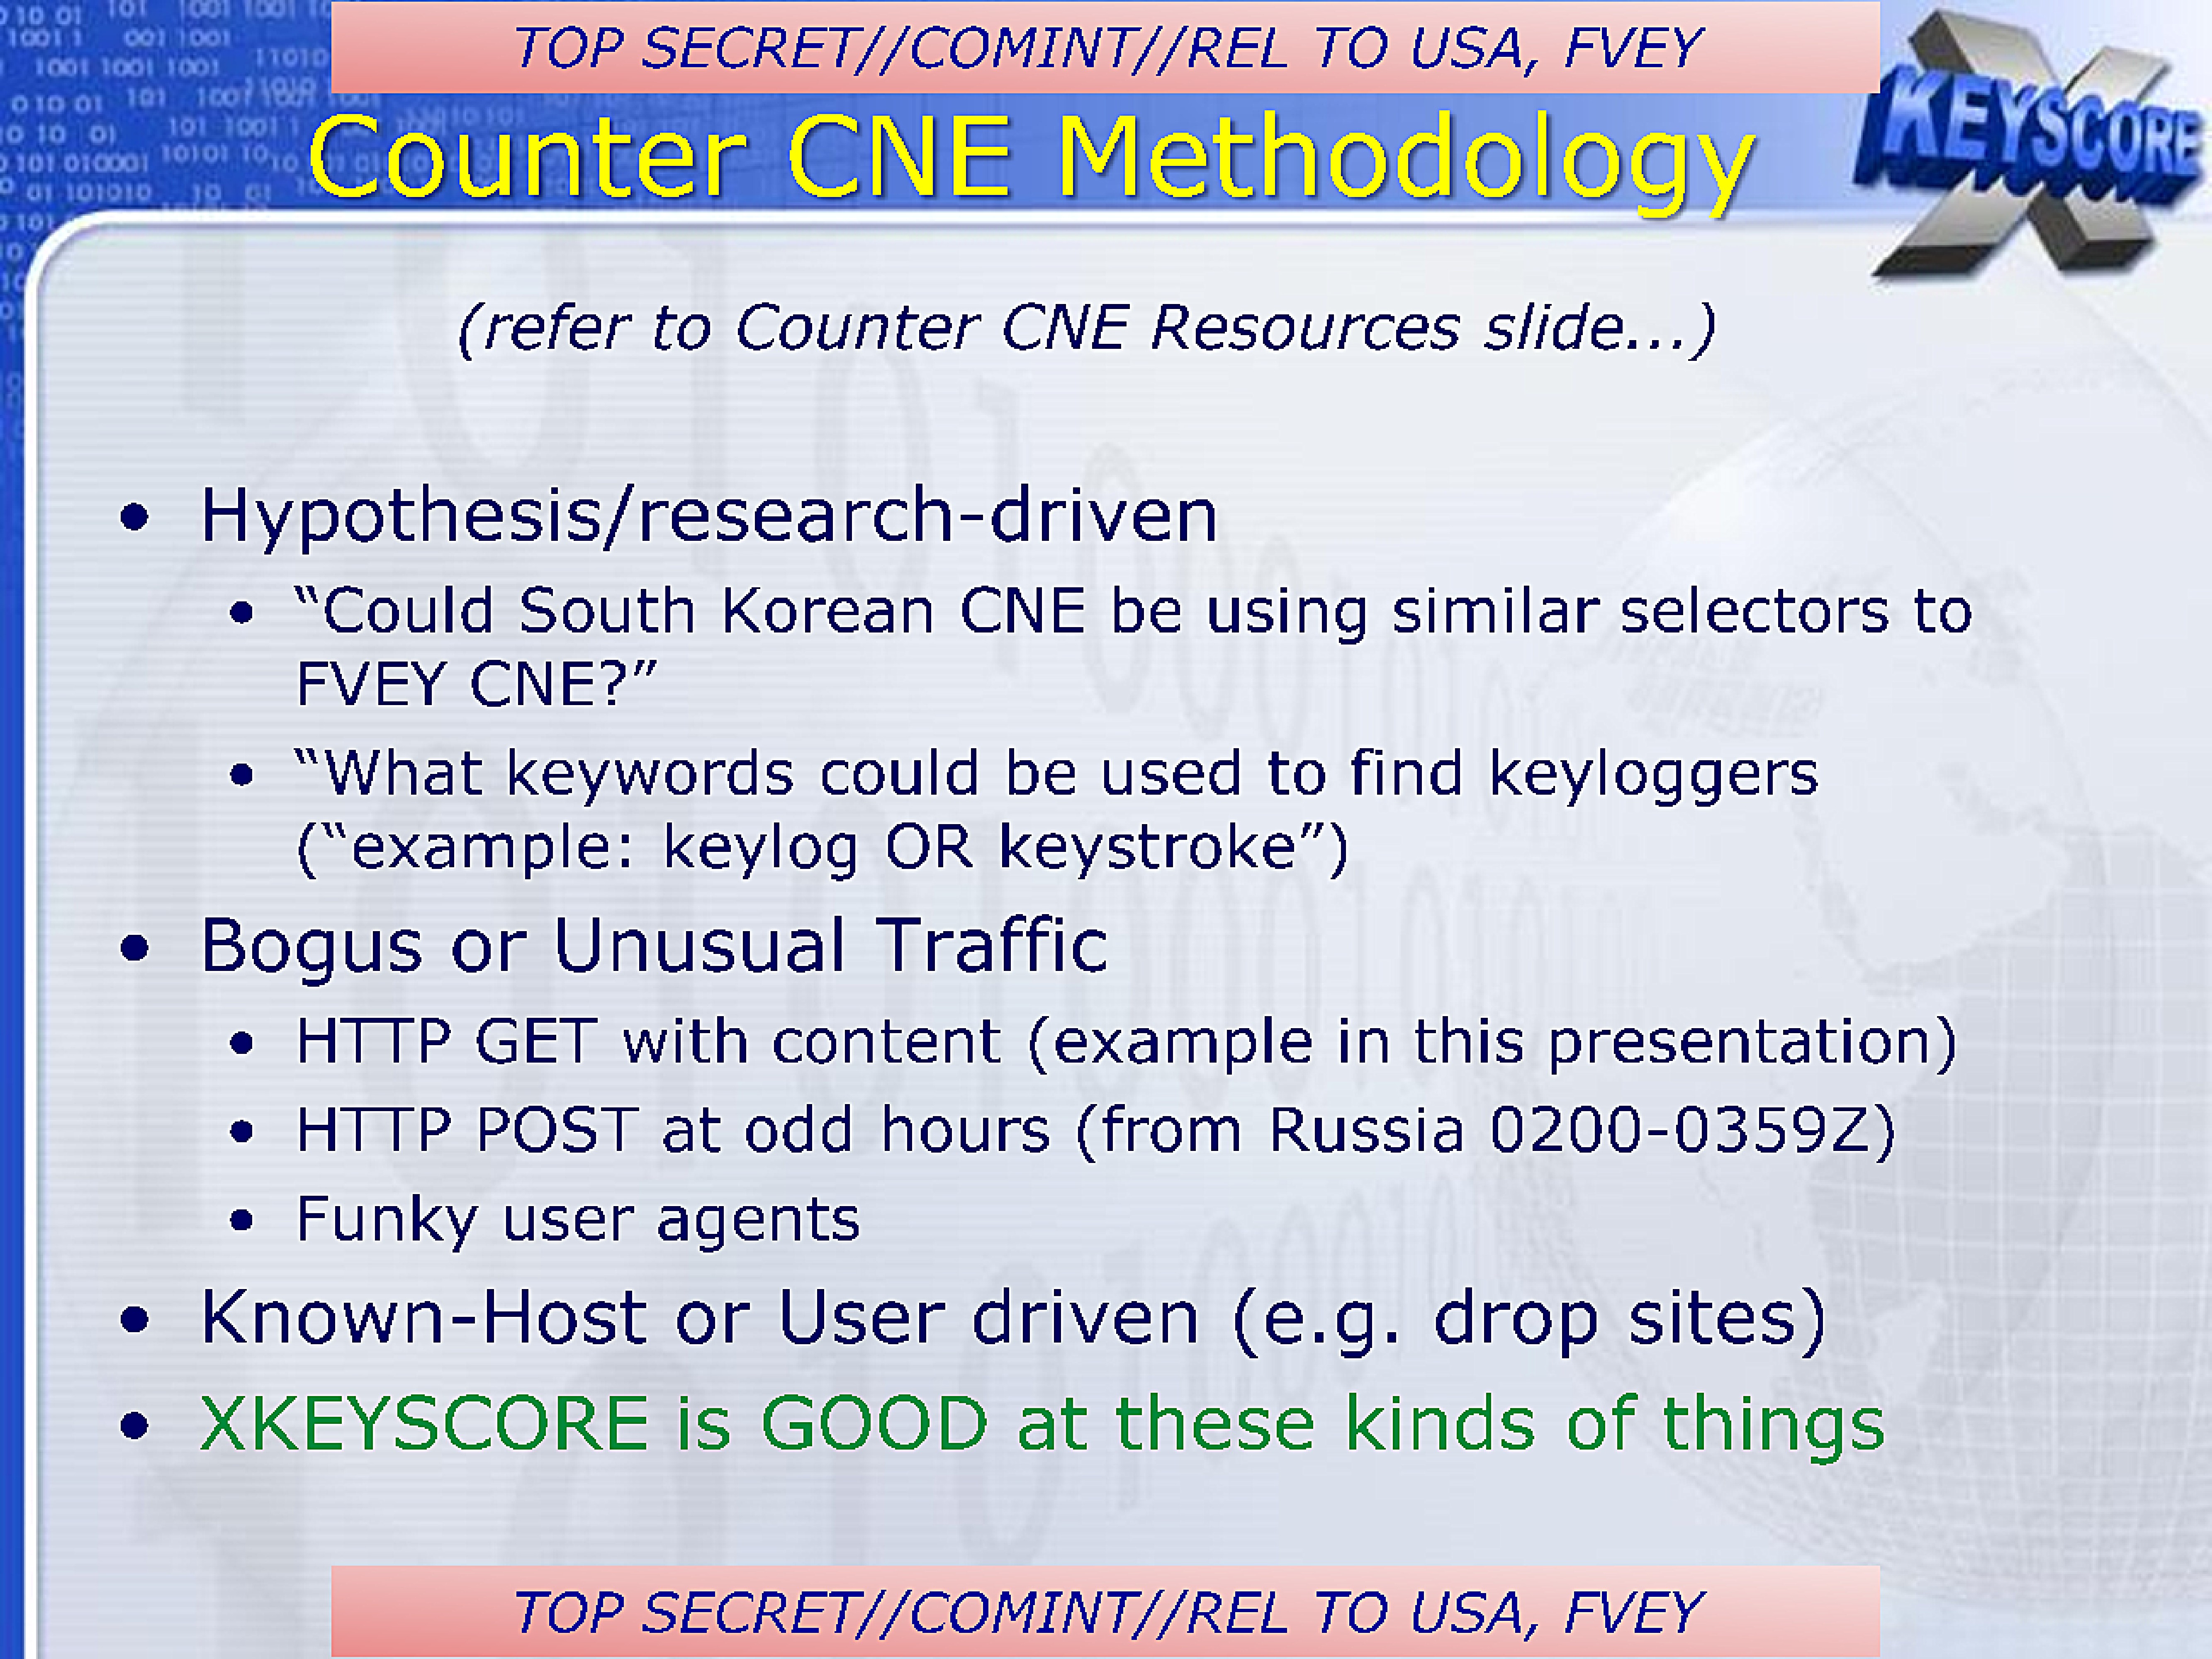
Counter CNE Methodology
(refer to Counter CNE Resources slide...)
- Hypothesis/research-driven
- "Could South Korean CNE be using similar selectors to FVEY CNE?"
- "What keywords could be used to find keyloggers ("example: keylog OR keystroke")
- Bogus or Unusual Traffic
- HTTP GET with content (example in this presentation)
- HTTP POST at odd hours (from Russia 0200-0359Z)
- Funky user agents
- Known-Host or User driven (e.g. drop sites)
- XKEYSCORE is GOOD at these kinds of things
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
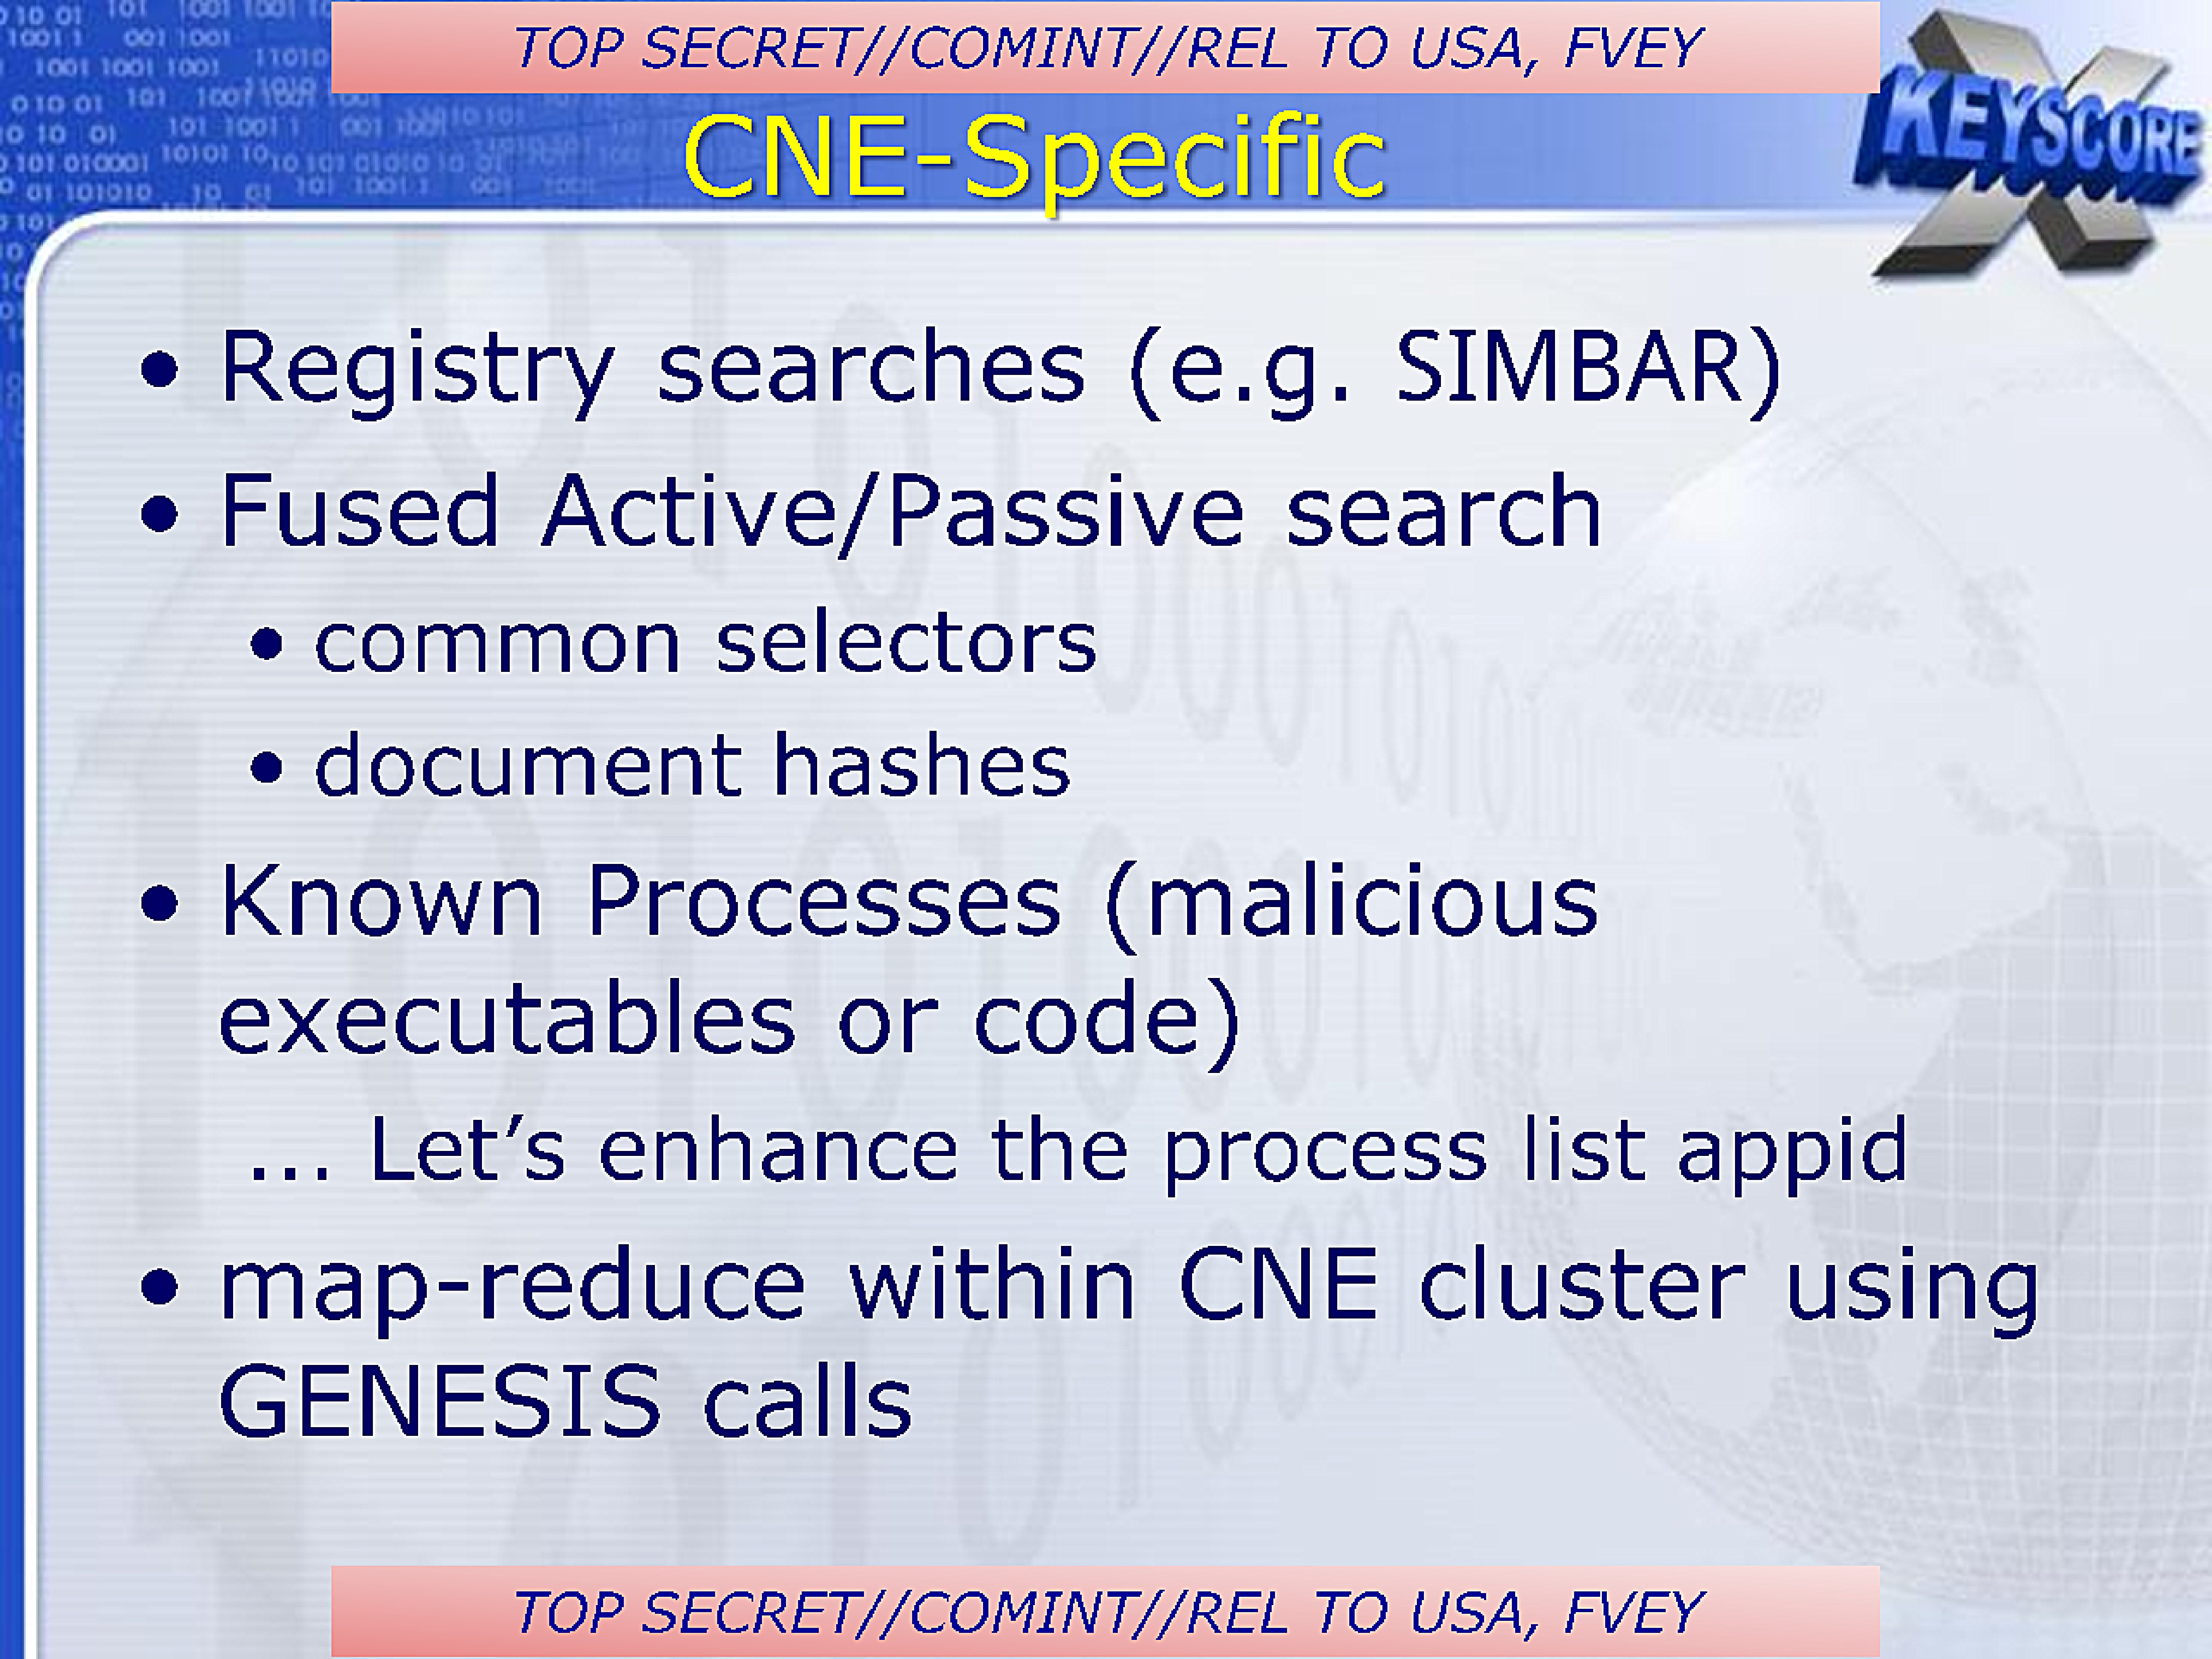
CNE-Specific
- Registry searches (e.g. SIMBAR)
- Fused Active/Passive search
- common selectors
- document hashes
- Known Processes (malicious executables or code)
- ... Let's enhance the process list appid
- map-reduce within CNE cluster using GENESIS calls
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
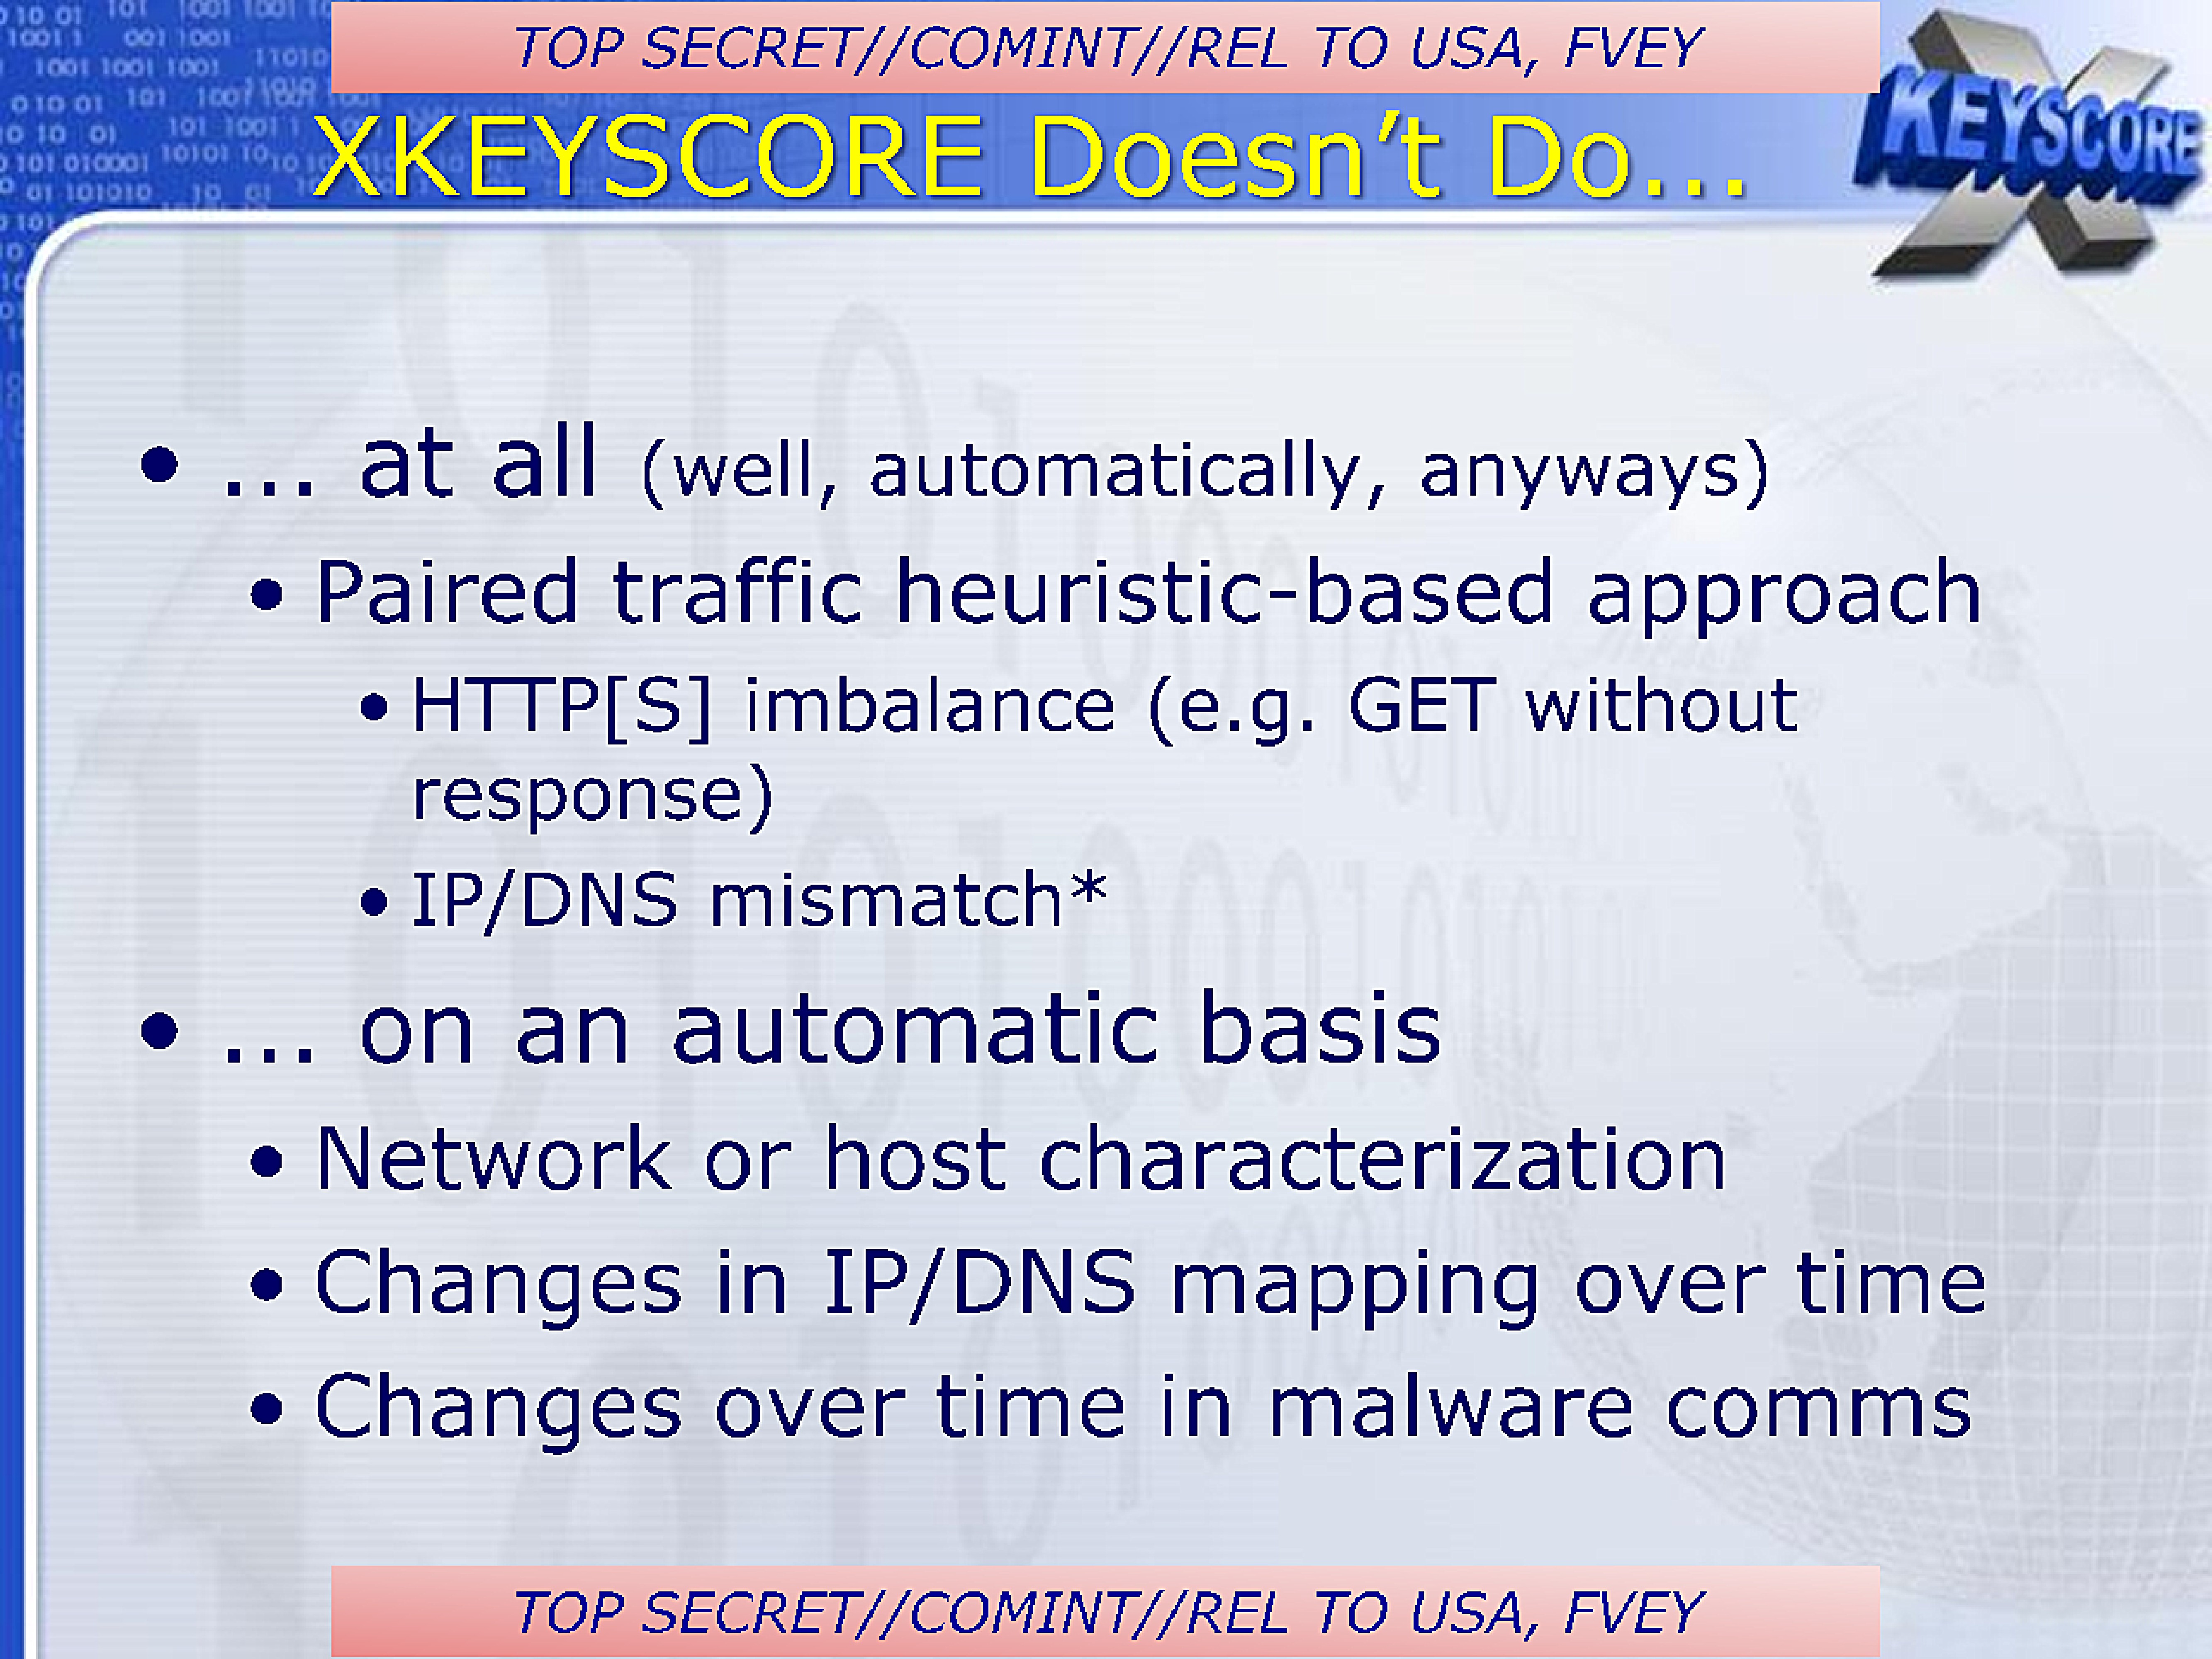
XKEYSCORE Doesn't Do...
- ... at all (well, automatically, anyways)
- Paired traffic heuristic-based approach
- HTTP[S] imbalance (e.g. GET without response)
- IP/DNS mismatch*
- Paired traffic heuristic-based approach
- ... on an automatic basis
- Network or host characterization
- Changes in IP/DNS mapping over time
- Changes over time in malware comms
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
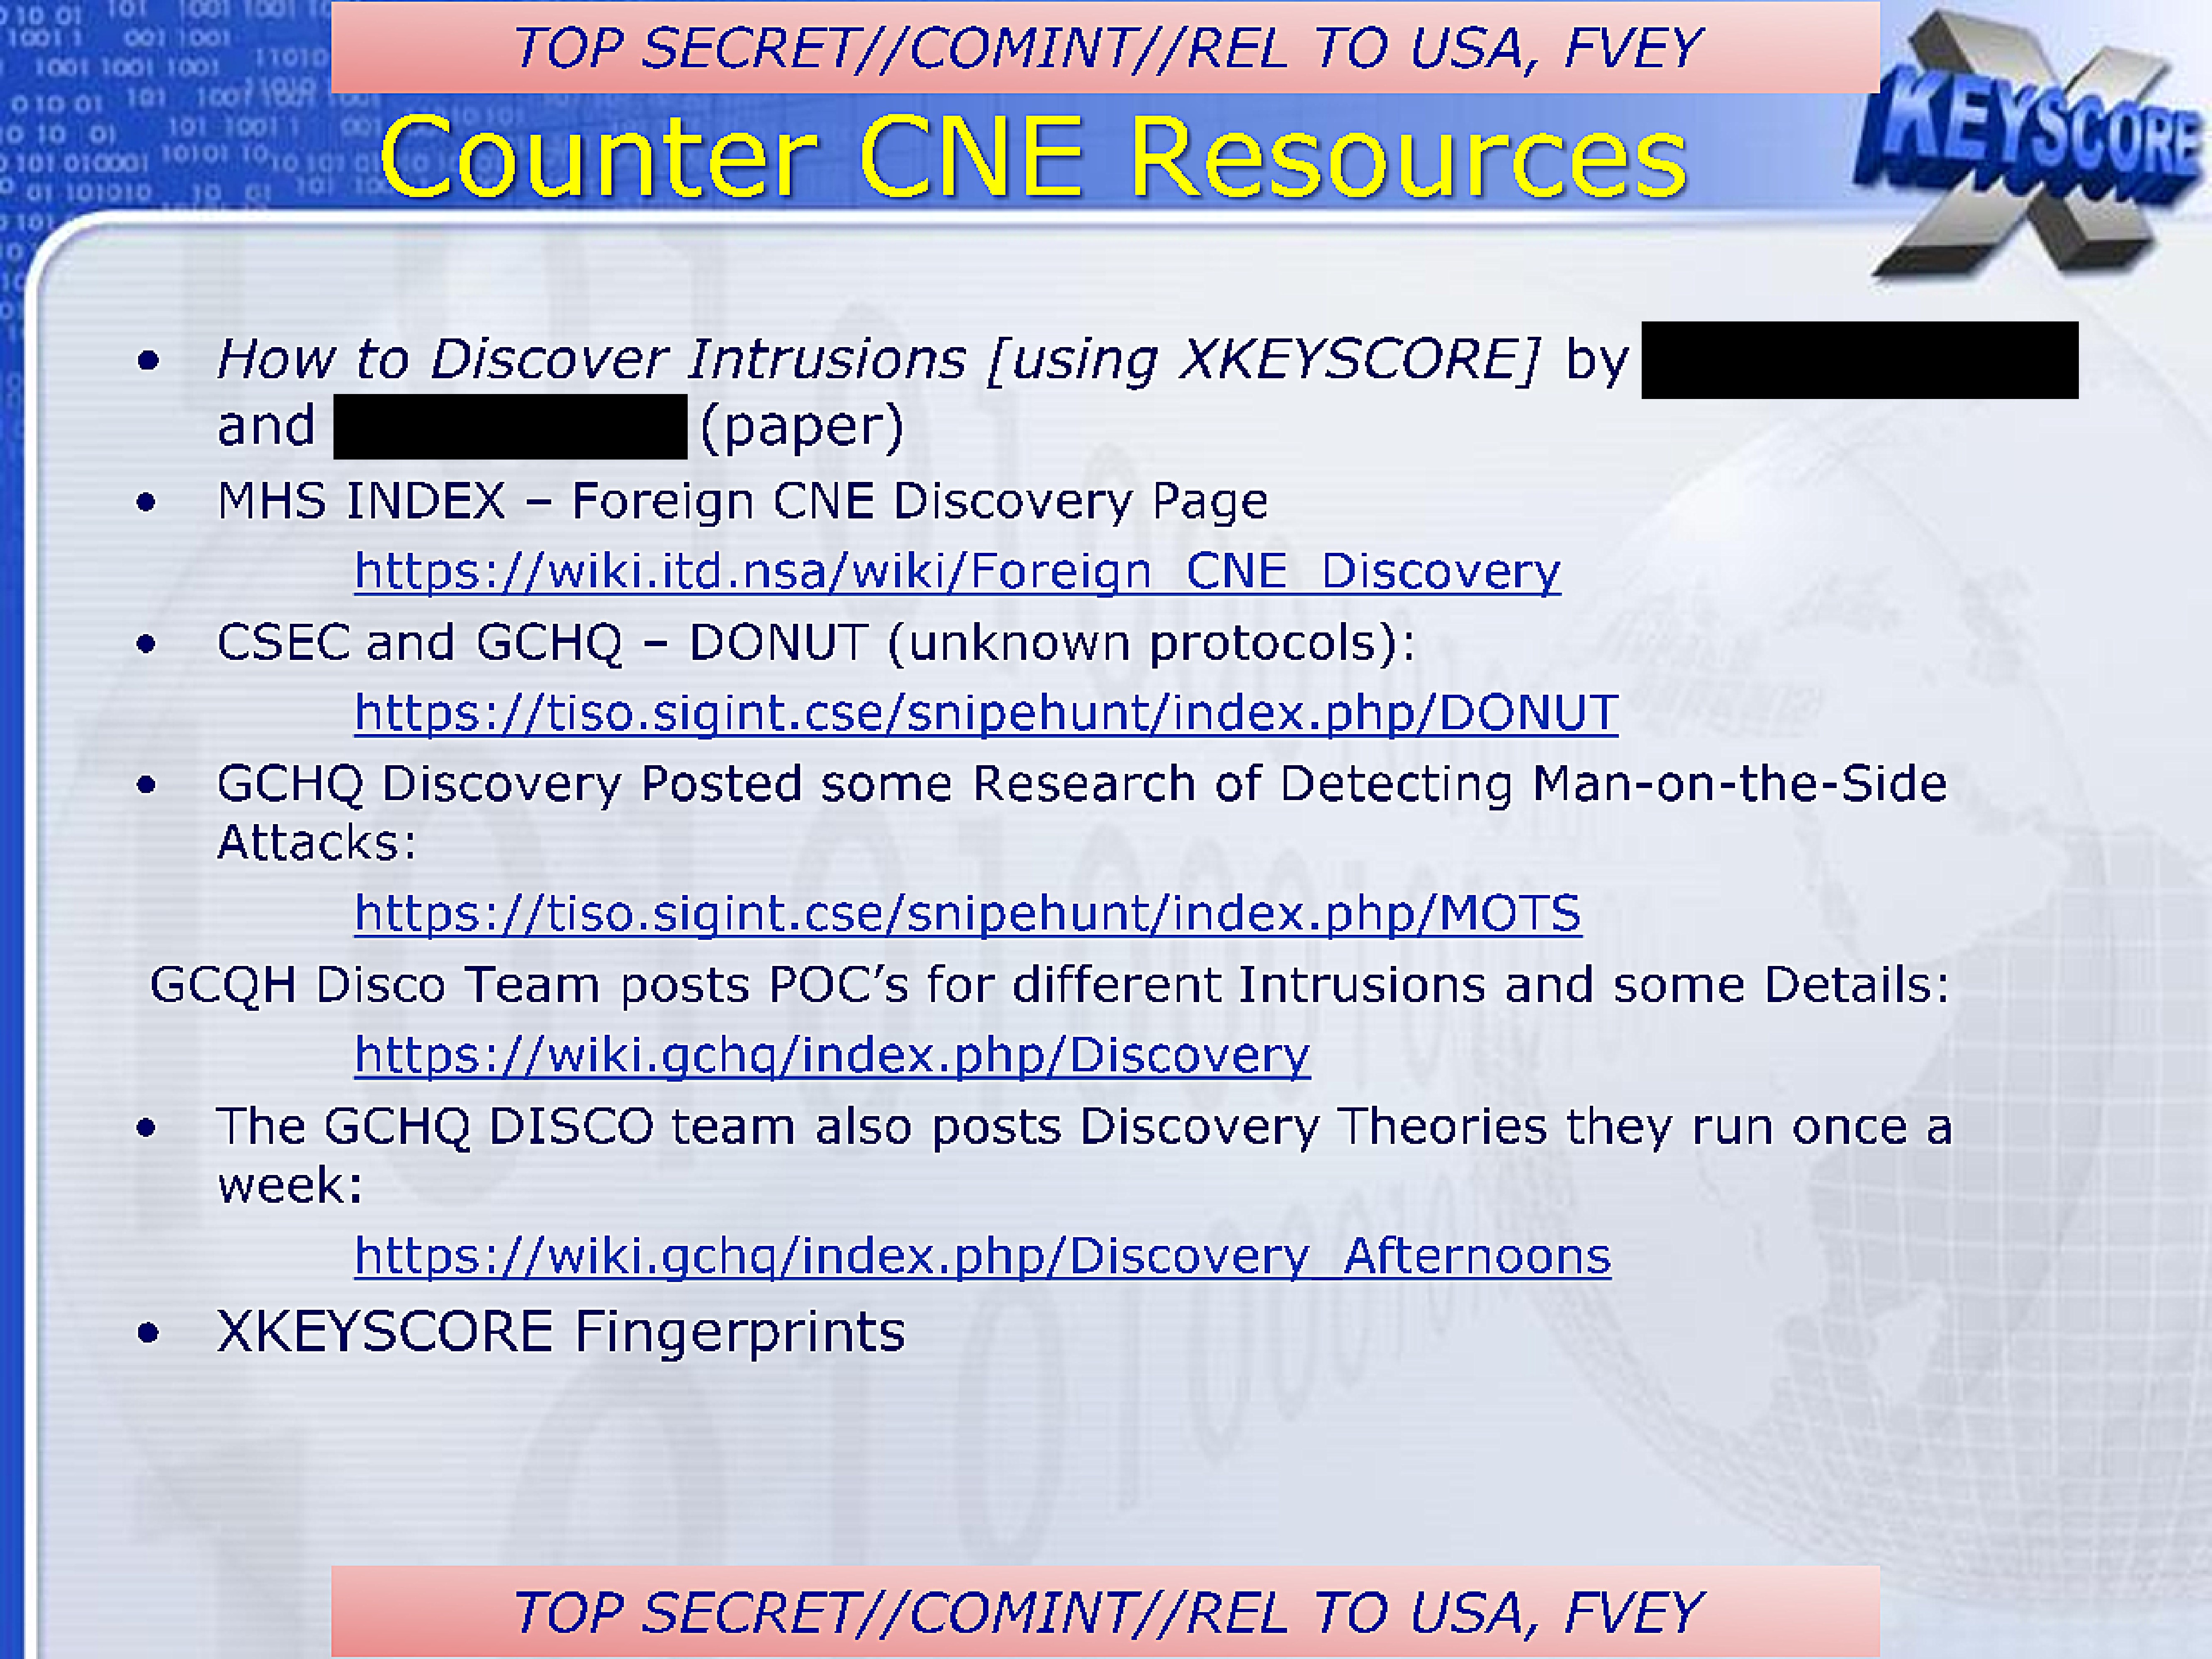
Counter CNE Resources
- How to Discover Intrusions [using XKEYSCORE] by [REDACTED] and [REDACTED] (paper)
- MHS INDEX - Foreign CNE Discovery Page
- https://wiki.itd.nsa/wiki/Foreign_CNE_Discovery
- CSEC and GCHQ - DONUT (unknown protocols):
- https://tiso.sigint.cse/snipehunt/index.php/DONUT
- GCHQ Discovery Posted some Research of Detecting Man-on-the-Side Attacks:
- https://tiso.sigint.cse/snipehunt/index.php/MOTS
- GCQH Disco Team posts POC's for different Intrusions and some Details:
- https://wiki.gchq/index.php/Discovery
- The GCHQ DISCO team also posts Discovery Theories they run once a week:
- https://wiki.gchq/index.php/Discovery_Afternoons
- XKEYSCORE Fingerprints
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
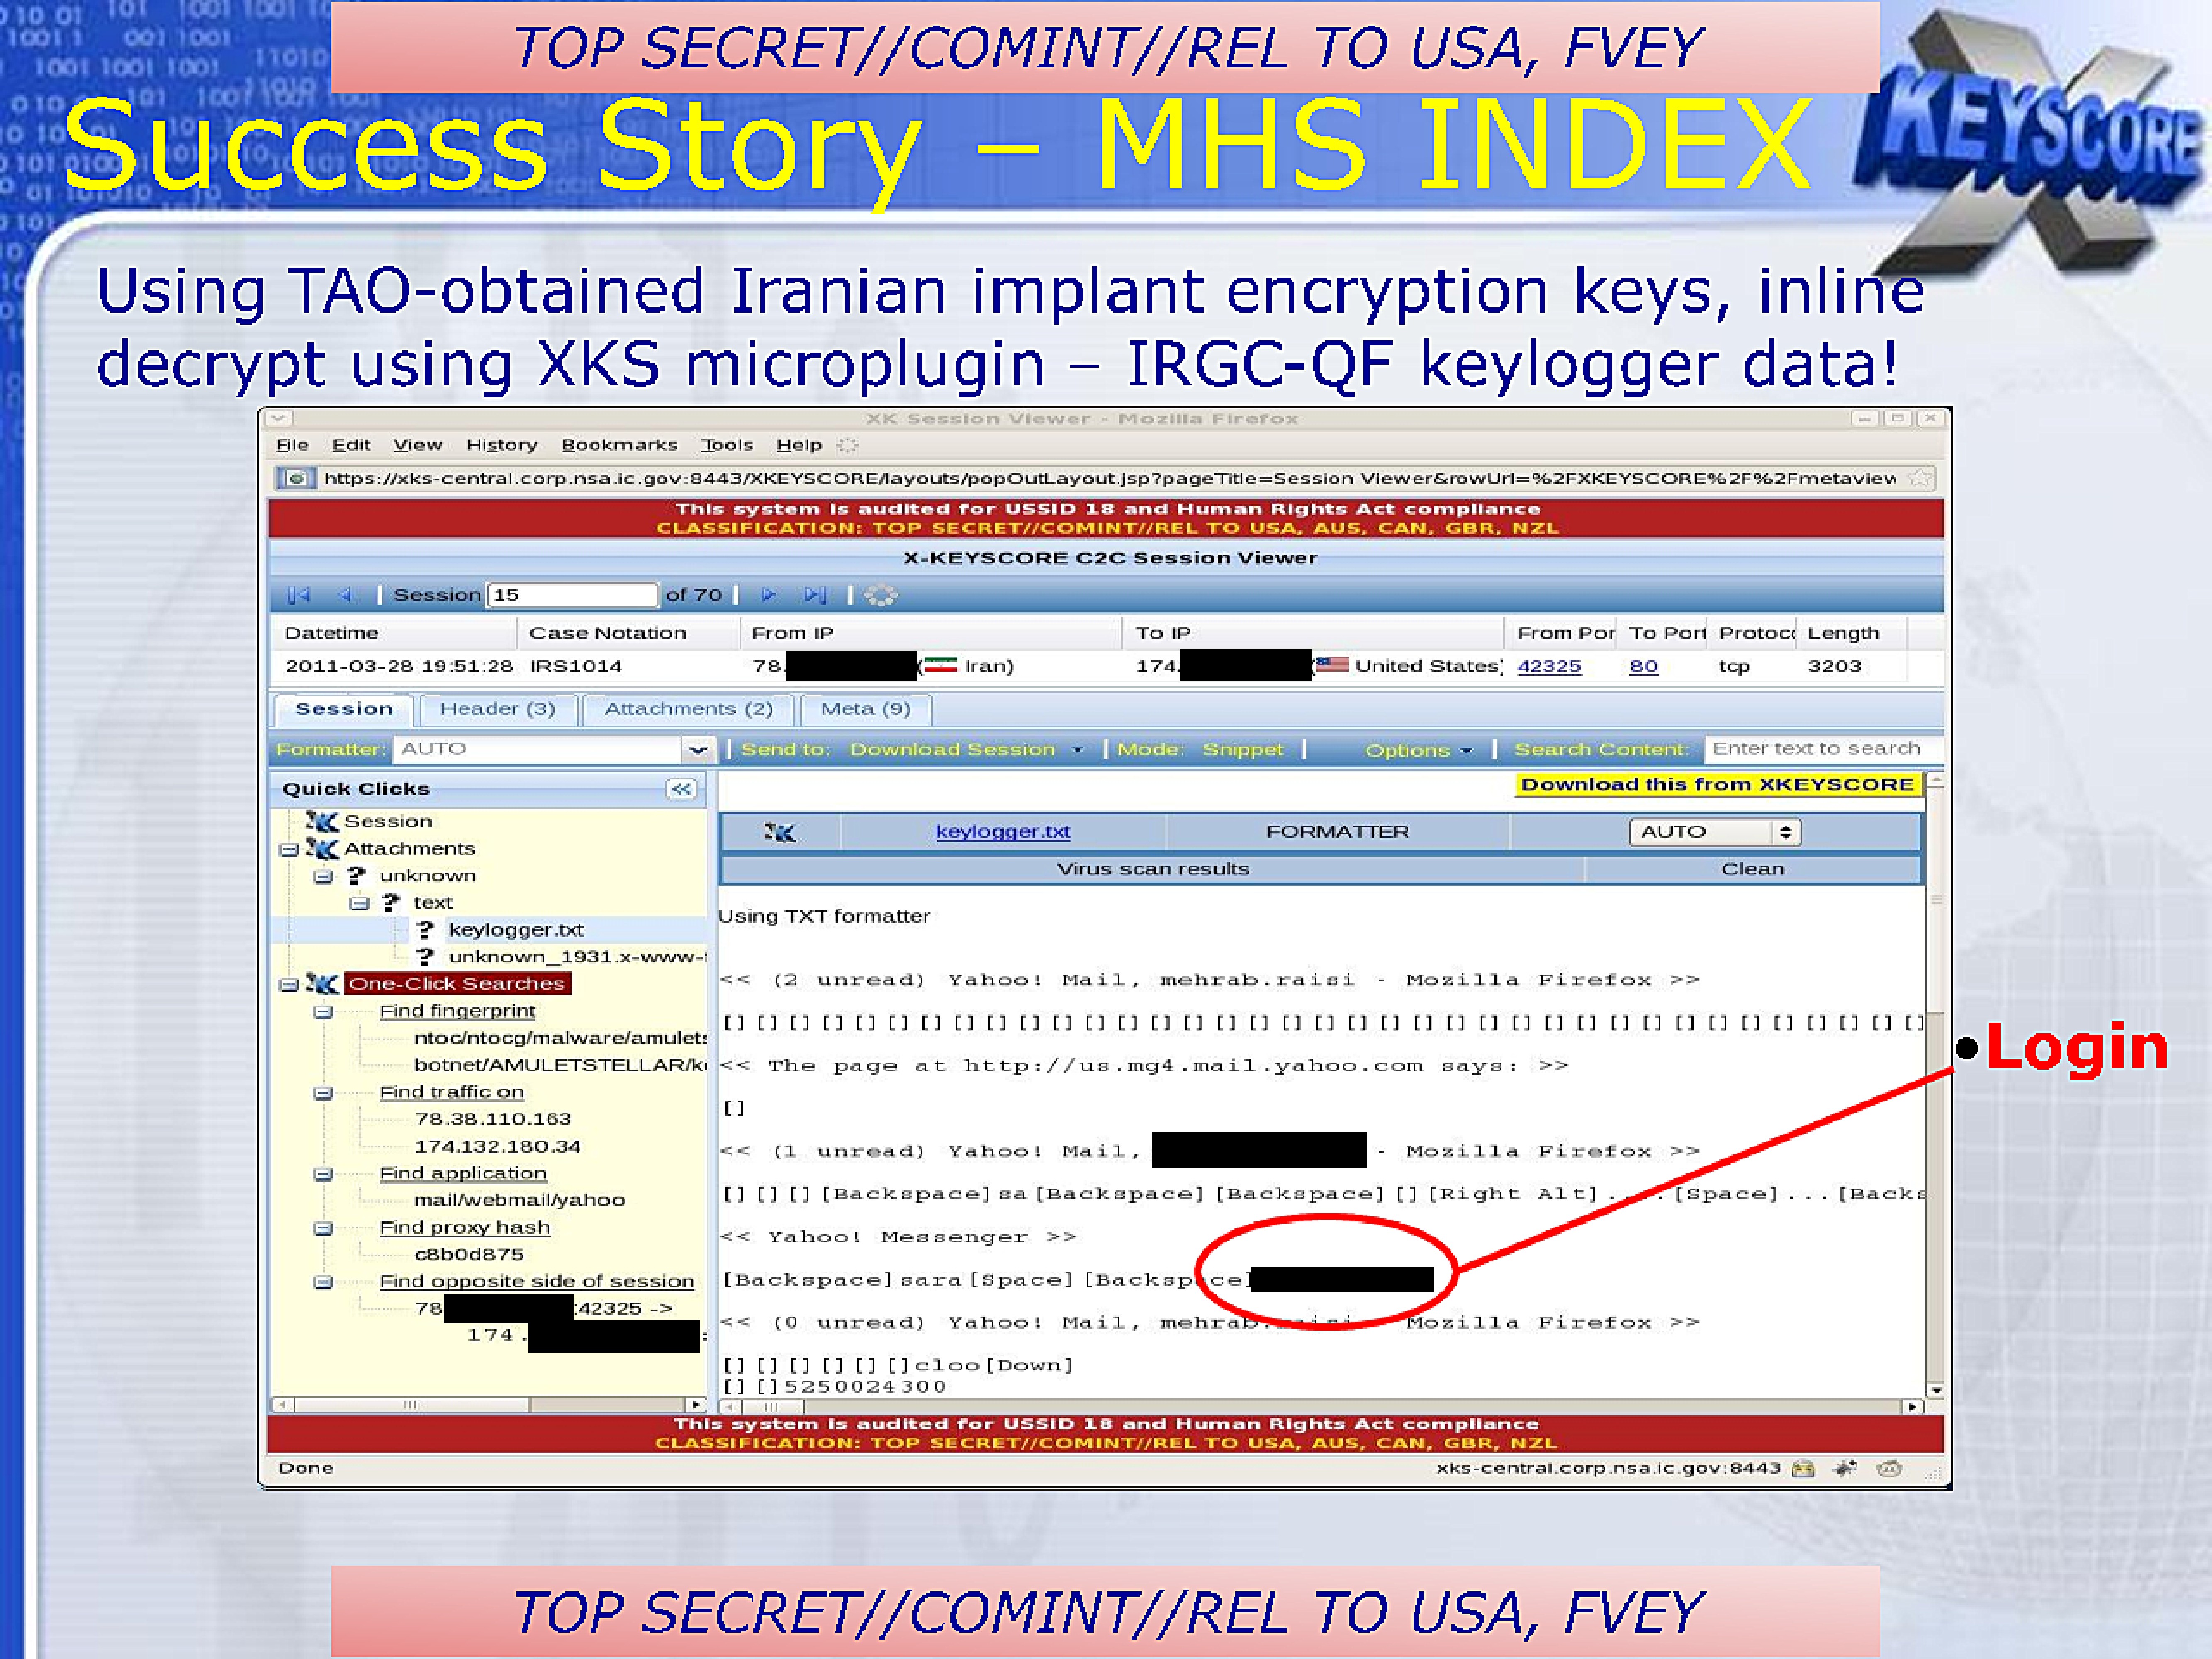
Success Story - MHS INDEX
Using TAO-obtained Iranian implant encryption keys, inline decrypt using XKS microplugin - IRGC-QF keylogger data!
XK Session Viewer - Mozilla Firefox
File Edit View History Bookmarks Tools Help
https://xks-central.corp.nsa.ic.gov:8443/XKEYSCORE/layouts/popOutLayout.jsp?pageTitle=Session Viewer&rowUrl=%2FXKEYSCORE%2F%2Fmetaview

This system is audited for USSID 18 and Human Rights Act compliance
CLASSIFICATION: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL

X-KEYSCORE C2C Session Viewer

Session 15 of 70
| Datetime            | Case Notation | From IP             | To IP                       | From Po | To Port | Protoc | Length
| 2011-03-28 19:51:28 | IRS1014       | 78[REDACTED] (Iran) | 174[REDACTED] United States | 42325   | 80      | tcp    | 320

Session | Header (3) | Attachments (2) | Meta (9)
Formatter: AUTO | Send to: Download Session | Mode: Snippet | Options | Search Content: Exter text to search

Quick Clicks
Session
Attachments
  unknown
    text
      keylogger.txt
      unknown_1931.x-www-
One-Click Searches
  Find fingerprint
    ntoc/ntocg/malware/amulet
    botnet/AMULETSTELLAR/k
  Find traffic on
    78.38.110.163
    174.132.180.34
  Find application
    mail/webmail/yahoo
  Find proxy hash
    c8b0d875
  Find opposite side of session
    78[REDACTED]:42325 ->
      174.[REDACTED]

Download this from XKEYSCORE
keylogger.txt FORMATTER AUTO
Virus scan results Clean
Using TXT formatter

<< (2 unread) Yahoo! Mail, mehrab.raisi - Mozilla Firefox >>
[] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] [] []
<< The page at http://us.mg4.mail.yahoo.com says: >>
[]
<< (1 unread) Yahoo! Mail, [REDACTED] - Mozilla Firefox >>
[][][][Backspace]sa[Backspace][Backspace][][Right Alt]...[Space]...[Backs
<< Yahoo! Messenger >>
[Backspace]sara[Space][Backspace]ce[REDACTED]
<< (0 unread) Yahoo! Mail, mehrab.raisi - Mozilla Firefox >>
[] [] [] [] [] cloo[Down]
[] []5250024300

This system is audited for USSID 18 and Human Rights Act compliance
CLASSIFICATION: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Done xks-central.corp.nsa.ic.gov:8443
- Login
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Points of Contact
- MHS Index Team
- [REDACTED] : [REDACTED]@nsa.ic.gov
- CES/TRANGRESSION
- [REDACTED] : [REDACTED]@nsa.ic.gov
- [REDACTED] : [REDACTED]@nsa.ic.gov
- NSA/Countering Foreign Intelligence
- [REDACTED] : [REDACTED]@nsa.ic.gov
- NTOC ??
- XKEYSCORE
- [REDACTED],[REDACTED] : xks-cne@r1.r.nsa
TOP SECRET//COMINT//REL TO USA, FVEY
Published in the Same Report
(10 of 46 documents)
-
XKEYSCORE intro [pdf]
A TOP SECRET NSA presentation from 2008 introducing XKeyscore — one of the earliest overview documents in the archive — describing the system as a globally distributed Linux cluster across approximately 150 sites and 700+ servers that stores a ~3-day rolling buffer of all unfiltered internet traffic, and demonstrating its core capabilities for finding previously unknown targets by mining metadata, tracking documents by embedded image hashes, detecting encryption and VPN use, and language tracking.
Programs: XKEYSCORE · TURMOIL · TURBULENCE · TRAFFICTHIEF · WEALTHYCLUSTER · MOONSHINE · SEARCHLIGHT · MARINA · PSC · SSO · TIMBERLINEPeople: bin Laden, Osama“'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · “XKeyscore: NSA tool collects 'nearly everything a user does on the internet'” - The Guardian ↗ (2013-07-31) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · Greenwald, Glenn · Bridi, Sônia · Marquis-Boire, Morgan · Lee, Micah -
Advanced HTTP Activity Analysis [pdf]
This NSA training document from 2009 teaches intelligence analysts how to analyze HTTP internet traffic and exploit it using the XKEYSCORE surveillance system to monitor and identify internet users globally.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Analyzing Mobile/Cellular DNI in XKEYSCORE, May 2009 [pdf]
The XKEYSCORE document explains how the agency analyzes mobile/cellular device internet usage by collecting and processing both converged DNI/DNR data within cellular networks and traditional internet traffic, using various tools and indicators to identify mobile users even when their device type isn't immediately evident. The document demonstrates how the system can track mobile internet activity across applications like Yahoo Mail and identifies devices through various technical "hints" including MSISDN codes, browser fingerprints, and user agent strings.
-
Atomic SIGINT Data Format (ASDF) Configuration Read Me [pdf]
This document is a technical configuration guide for setting up XKEYSCORE surveillance systems to generate and forward metadata in the Atomic SIGINT Data Format (ASDF) to various data repositories including MARINA, which tracks users' browser activity and online behavior.
Marking: SECRET -
CADENCE Read Me [pdf]
This NSA engineering manual details how to configure XKEYSCORE—the agency's sprawling surveillance system—to integrate with CADENCE, an automated keyword scanning tool that filters intercepted communications and routes intelligence based on search terms submitted by analysts.
-
How to configure category throttling in XKEYSCORE [pdf]
An NSA technical guide explains how to configure "category throttling" in XKEYSCORE—a feature that automatically stops forwarding intercepted communications once analyst-defined collection targets hit predetermined data volume or session count limits, allowing the surveillance system to continue processing but prevent overflow from high-volume targets.
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
Communications System - How To Guide [pdf]
A TOP SECRET and sensitive compartmented information (SCI) how-to document for the NSA’s XKEYSCORE “Comms” backbone, laying out ports, peer/allow rules, bandwidth pools, and proxy classifications that stitch clusters to central control—a scalable architecture for moving surveillance data with security markings baked in. It also walks through firewall exceptions, HTTPS port-sharing, and a MAILORDER file pipeline, exposing the nuts‑and‑bolts of how collection flows across sites, proxies, and viewers.
-
DEEPDIVE Readme [pdf]
This document is a confidential technical guide that provides step-by-step procedures for configuring an XKEYSCORE server to function as a DEEPDIVE server. DEEPDIVE enhances XKEYSCORE by adding a front-end filter and a rolling buffer of all unfiltered data, creating a federated query system that can scan all collection sites with a single query.
-
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS



Related Documents
-
XKEYSCORE System Administration [pdf]
A December 2012 TOP SECRET XKeyscore System Administration training manual — the detailed technical guide for the engineers who ran XKeyscore field-site clusters — covering the system's Red Hat Linux architecture, master/slave cluster design, database and processing pipeline, the GUI (including built-in Tor, botnet and CNE search menus), the DeepDive full-take packet processor, the xks command-line tool, and monitoring and troubleshooting, with live screenshots from the Timberline site (USF-790) and Menwith Hill Station.
Programs: XKEYSCORE · WEALTHYCLUSTER · MAILORDER · CADENCE · ROGUESTITCH · QUANTUMBOT · COTTONCHAINSAW · MPTRII · SCARFACE · ZAMENSIS · MAPREDUCE · GENESIS · REDUCER · DEEPDIVE · ASDF · CYBER · BULKCRYPT · METTLESOME · PACKETSPLAYYER · PROMOTER · DEFRAG · XFIP · TRAFFICTHIEF · ENDACE · TIMBERLINE · MUSCULAR · FIST · STARPROC -
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
Guide to Using Contexts in XKS Fingerprints [pdf]
This technical guide explains how NSA analysts use "contexts" within XKEYSCORE fingerprints to create highly targeted surveillance queries by restricting searches to specific scopes (e.g., web searches, document bodies, geographic locations), enabling precision targeting such as finding "all people in Kabul performing web searches on Jihad" while avoiding the overwhelming noise of broader keyword searches.
-
Using XKEYSCORE to Enable TAO [pdf]
A TOP SECRET training presentation from 2009, authored by a Booz Allen Hamilton contractor, teaching NSA analysts how to use XKeyscore to harvest the login credentials, router configurations, browser versions and server software details that the Tailored Access Operations hacking unit needs to break into foreign computer networks — with worked examples stealing Cisco router passwords, Iranian government webmail logins and jihadi web forum credentials directly from intercepted internet traffic.