Slides Describe Mission Involving Huawei
Open PDFDocument date: 2010-01-01
Pages: 2
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, AUS, CAN, GBR, NZL
This document details an NSA-led strategic initiative to target Huawei due to its dominance in global telecommunications infrastructure. The operation (codenamed "Shotgiant") aims to exploit Huawei hardware to maintain access to target communications while investigating the company’s potential role in facilitating People’s Republic of China (PRC) signals intelligence and supply chain subversion.
My notes
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
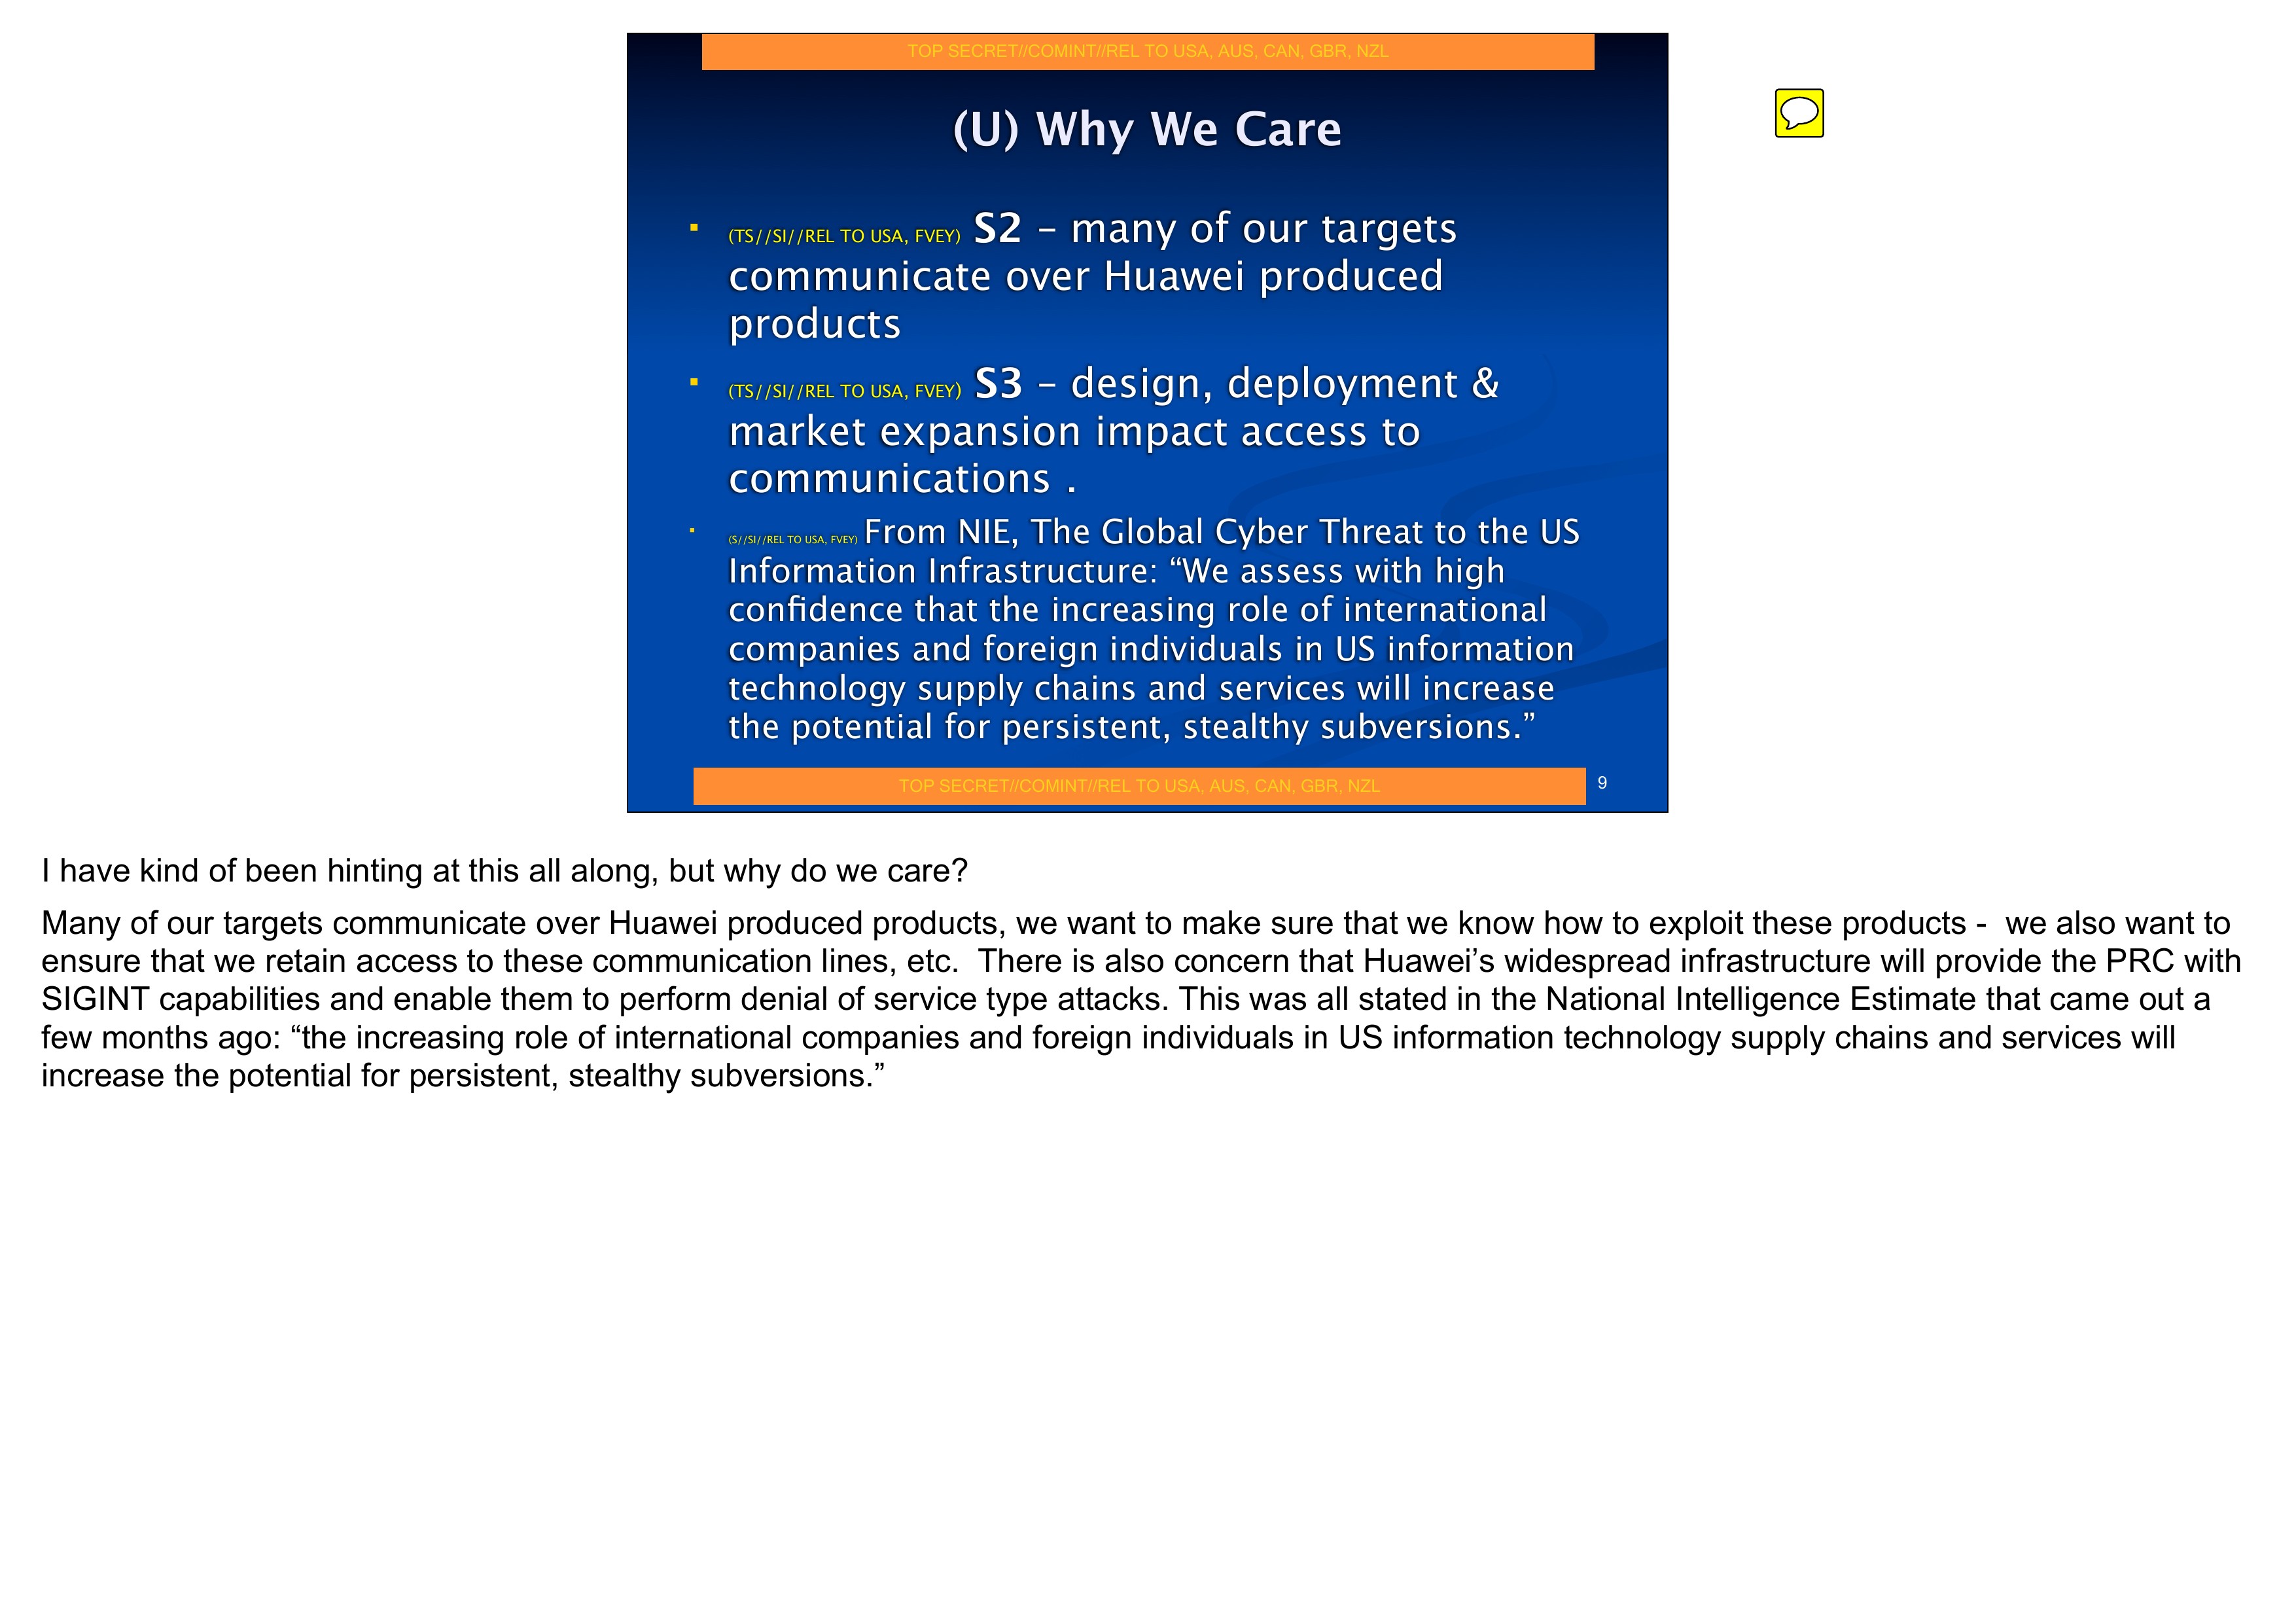
(U) Why We Care
- (TS//SI//REL TO USA, FVEY) S2 – many of our targets communicate over Huawei produced products
- (TS//SI//REL TO USA, FVEY) S3 – design, deployment & market expansion impact access to communications .
- (S//SI//REL TO USA, FVEY) From NIE, The Global Cyber Threat to the US Information Infrastructure: “We assess with high confidence that the increasing role of international companies and foreign individuals in US information technology supply chains and services will increase the potential for persistent, stealthy subversions.”
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
9
I have kind of been hinting at this all along, but why do we care?
Many of our targets communicate over Huawei produced products, we want to make sure that we know how to exploit these products - we also want to ensure that we retain access to these communication lines, etc. There is also concern that Huawei's widespread infrastructure will provide the PRC with SIGINT capabilities and enable them to perform denial of service type attacks. This was all stated in the National Intelligence Estimate that came out a few months ago: “the increasing role of international companies and foreign individuals in US information technology supply chains and services will increase the potential for persistent, stealthy subversions.”
[REDACTED]
So to recap, this is what we are hoping to accomplish:
TS//SI//REL) Determine if Huawei is doing SIGINT for PRC.
(TS//SI//REL) Perform more analysis on Huawei Corp - define relationships, organization, plans, etc.
(TS//SI//REL) Direct efforts against intelligence gaps - IRM decrypts, underwater fiber, R & D facilities, follow the money, supply chain, etc.
(TS//SI//REL) Focus on high priority targets - Iran, Afghanistan, Pakistan, Kenya, Cuba.
(TS//SI//REL) Leverage Huawei presence to gain access to networks of interest.
(TS//SI//REL) Document processes to be used later for targeting other non-partnerable companies.
TS//SI//REL) How is success defined? (timeline 6-9 months)
- Obtaining actionable intelligence of Huawei's (and potentially PRC's) leadership plans and intentions
- Enable SIGINT collection through CNE tools
So what are we going to do about it? The first step was to form a TOPI, so that we can start to report some of our findings and continue tasking the communications. However, targeting Huawei is a big, messy task. In order to help us focus, we broke Huawei into three pillars: The Company, The Technology, The Deployment of the Technology.
When we look at these three different aspects of Huawei we found that two topics showed up across the board - marketing and plans/intentions. So that is our main focus. If we can see how Huawei is marketing itself, and working to expand this will help us to understand the company's plans and intentions. If we can determine the company's plans and intentions, we hope that this will lead us back to plans and intentions of the PRC.
We will consider ourselves a success if we
- Obtaining actionable intelligence of Huawei's (and potentially PRC's) leadership plans and intentions
- Enable SIGINT collection through CNE tools
Related Documents
-
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Assessment of Intelligence Opportunity - Juniper [pdf]
This document reveals that GCHQ, with NSA cooperation, developed capabilities to exploit vulnerabilities in 13 Juniper NetScreen firewall models and was expanding efforts to target Juniper’s broader JUNOS-based products for intelligence collection. It highlights the agencies’ strategic focus on maintaining access to critical network infrastructure globally, leveraging Juniper’s widespread use in high-priority countries.
Programs: HEADRESSNU -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
NSA Supply Chain Attack From PMR 4-24-13 [pdf]
This document is a top-secret NSA report detailing a SIGINT development operation in which a classified Voice-over-IP network shipment was intercepted and subjected to a supply-chain interdiction, allowing NSA and its intelligence community partners to gain access to the hardware and intelligence. It describes the operational process, including tracking the shipment through China, coordinating with Tailored Access Operations (TAO), and using tools like XKEYSCORE to identify targeting selectors, ultimately enabling detailed surveillance and future operational opportunities.