SSO news excerpts
Open PDFDocument date: 2011-01-01
Pages: 1
Genre: newsletter
Classification: TOP SECRET SI
Dissemination: NOFORN
These SSO news exceprts describe the successful deployment of QUANTUMTHEORY and QUANTUMINSERT capabilities by the NSA’s Tailored Access Operations (TAO) team, in collaboration with Special Source Operations (SSO), to exploit high-value targets, including key figures in the Haqqani network. Using a combination of signal case notations and real-time exploitation via QUANTUMHAND, TAO was able to implant malicious software on the target's computer, enabling further intelligence collection and exploitation.
My notes
(TS//SI//NF) DGO Enables Endpoint Implants via QUANTUMTHEORY
By [[REDACTED]] on 2011-09-26 1548
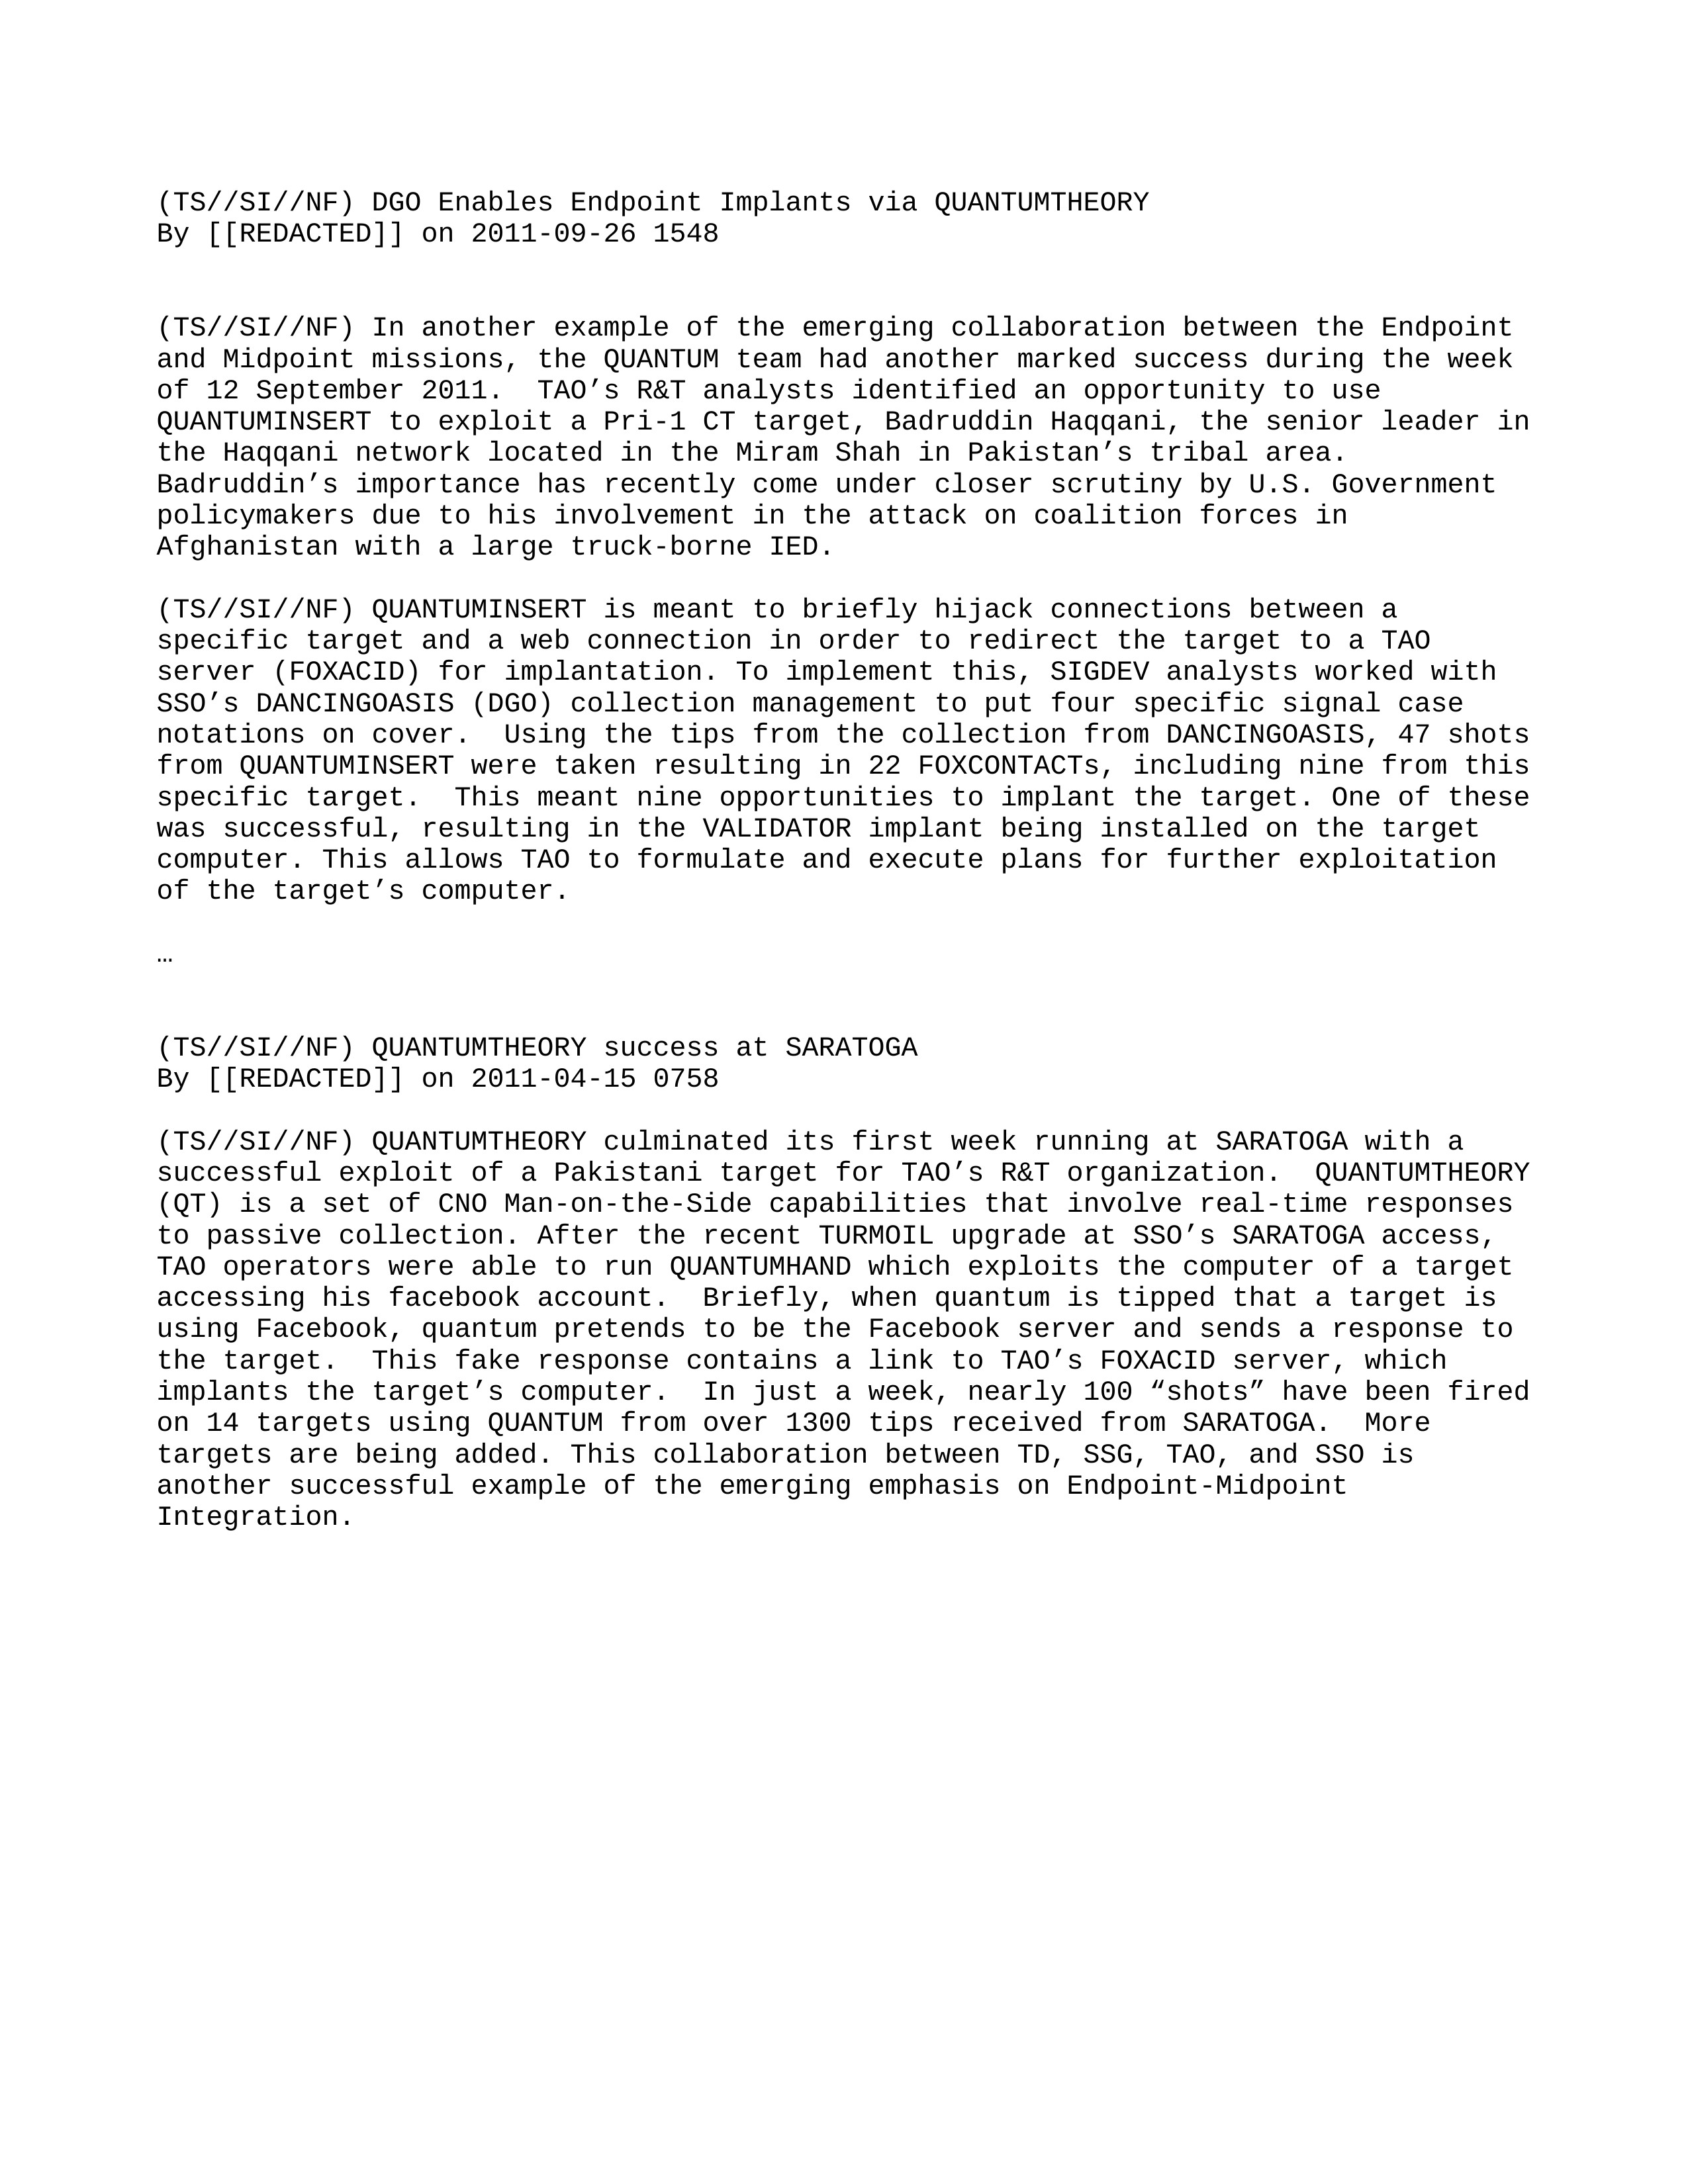
(TS//SI//NF) In another example of the emerging collaboration between the Endpoint and Midpoint missions, the QUANTUM team had another marked success during the week of 12 September 2011. TAO's R&T analysts identified an opportunity to use QUANTUMINSERT to exploit a Pri-1 CT target, Badruddin Haqqani, the senior leader in the Haqqani network located in the Miram Shah in Pakistan's tribal area. Badruddin's importance has recently come under closer scrutiny by U.S. Government policymakers due to his involvement in the attack on coalition forces in Afghanistan with a large truck-borne IED.
(TS//SI//NF) QUANTUMINSERT is meant to briefly hijack connections between a specific target and a web connection in order to redirect the target to a TAO server (FOXACID) for implantation. To implement this, SIGDEV analysts worked with SSO's DANCINGOASIS (DGO) collection management to put four specific signal case notations on cover. Using the tips from the collection from DANCINGOASIS, 47 shots from QUANTUMINSERT were taken resulting in 22 FOXCONTACTS, including nine from this specific target. This meant nine opportunities to implant the target. One of these was successful, resulting in the VALIDATOR implant being installed on the target computer. This allows TAO to formulate and execute plans for further exploitation of the target's computer.
...
(TS//SI//NF) QUANTUMTHEORY success at SARATOGA
By [[REDACTED]] on 2011-04-15 0758
(TS//SI//NF) QUANTUMTHEORY culminated its first week running at SARATOGA with a successful exploit of a Pakistani target for TAO's R&T organization. QUANTUMTHEORY (QT) is a set of CNO Man-on-the-Side capabilities that involve real-time responses to passive collection. After the recent TURMOIL upgrade at SSO's SARATOGA access, TAO operators were able to run QUANTUMHAND which exploits the computer of a target accessing his facebook account. Briefly, when quantum is tipped that a target is using Facebook, quantum pretends to be the Facebook server and sends a response to the target. This fake response contains a link to TAO's FOXACID server, which implants the target's computer. In just a week, nearly 100 “shots” have been fired on 14 targets using QUANTUM from over 1300 tips received from SARATOGA. More targets are being added. This collaboration between TD, SSG, TAO, and SSO is another successful example of the emerging emphasis on Endpoint-Midpoint Integration.
Published in the Same Report
(7 documents)
-
Wireless LAN / CNE Tool Training Course and Evaluation [pdf]
This document is a slide deck introducing a "Close Access" NSA training course to "familiarize, educate, and certify students in the operational usage" of various computer network exploitation tools.
-
Introduction to WLAN / 802.11 Active CNE Operations [pdf]
This NSA powerpoint introduces computer network exploitation (CNE) criteria and assesment as well as active CNE operations. It also introduces the FOXACID program, which is a program to deliver content based exploits to web browsers.
-
Introduction to BADDECISION [pdf]
This presentation details the use of the NSA program BADDECISION, which is a computer network exploitation tool (CNE) that uses a frame injection technique to redirect the target client to a FOXACID server.
-
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO


Related Documents
-
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
Tailored Access Operations, FOXACID, QUANTUM [pdf]
These NSA presentation slides detail "QUANTUM," a sophisticated system that allows the agency to intercept internet traffic and inject malware onto target computers with up to 80% success rates, far exceeding traditional spam-based methods. The system works by monitoring internet traffic for specific identifiers (like Yahoo or Facebook cookies), then racing to inject malicious code before legitimate web servers can respond, thereby compromising targets' computers without their knowledge and establishing persistent backdoor access.
Programs: FOXACID · QUANTUM · QUANTUMTHEORY · QUANTUMBISCUIT · VALIDATOR · OLYMPUS · UNITEDRAKE · OLYMPUSFIRE · SSO · FORESTPLACE -
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO