SNIPs of SIGINT
Open PDFDocument date: 2012-06-27
Pages: 5
Genre: other
Banner: DYNAMIC PAGE TOP SECRET//SI//REL TO USA, FVEY
Classification: TOP SECRET SI
Dissemination: REL TO USA, FVEY
A monthly notes entry from June 2012 by an NSA analyst on exchange at DSD Australia, describing two CNA/CNE tool development projects — PITIEDFOOL, a Windows file system destruction suite that kills the MFT and volume shadow copies and was successfully tested inside FUZZYEBOLA, and PANT SPARTY, an OpenSSH daemon backdoor granting covert root access while suppressing log entries — alongside a briefing to the US Ambassador to Australia on CNA/CNE work and TAO collaboration.
My notes
SNIPs of SIGINT :: (U) Monthly Notes for June 2012
DYNAMIC PAGE
System Max: SECRET//SI/TALENT KEYHOLE//REL TO USA, FVEY
Portion Max: TOP SECRET//SI//REL TO USA, FVEY
SNIPS of SIGINT
(U) Monthly Notes for June 2012
1 of 5
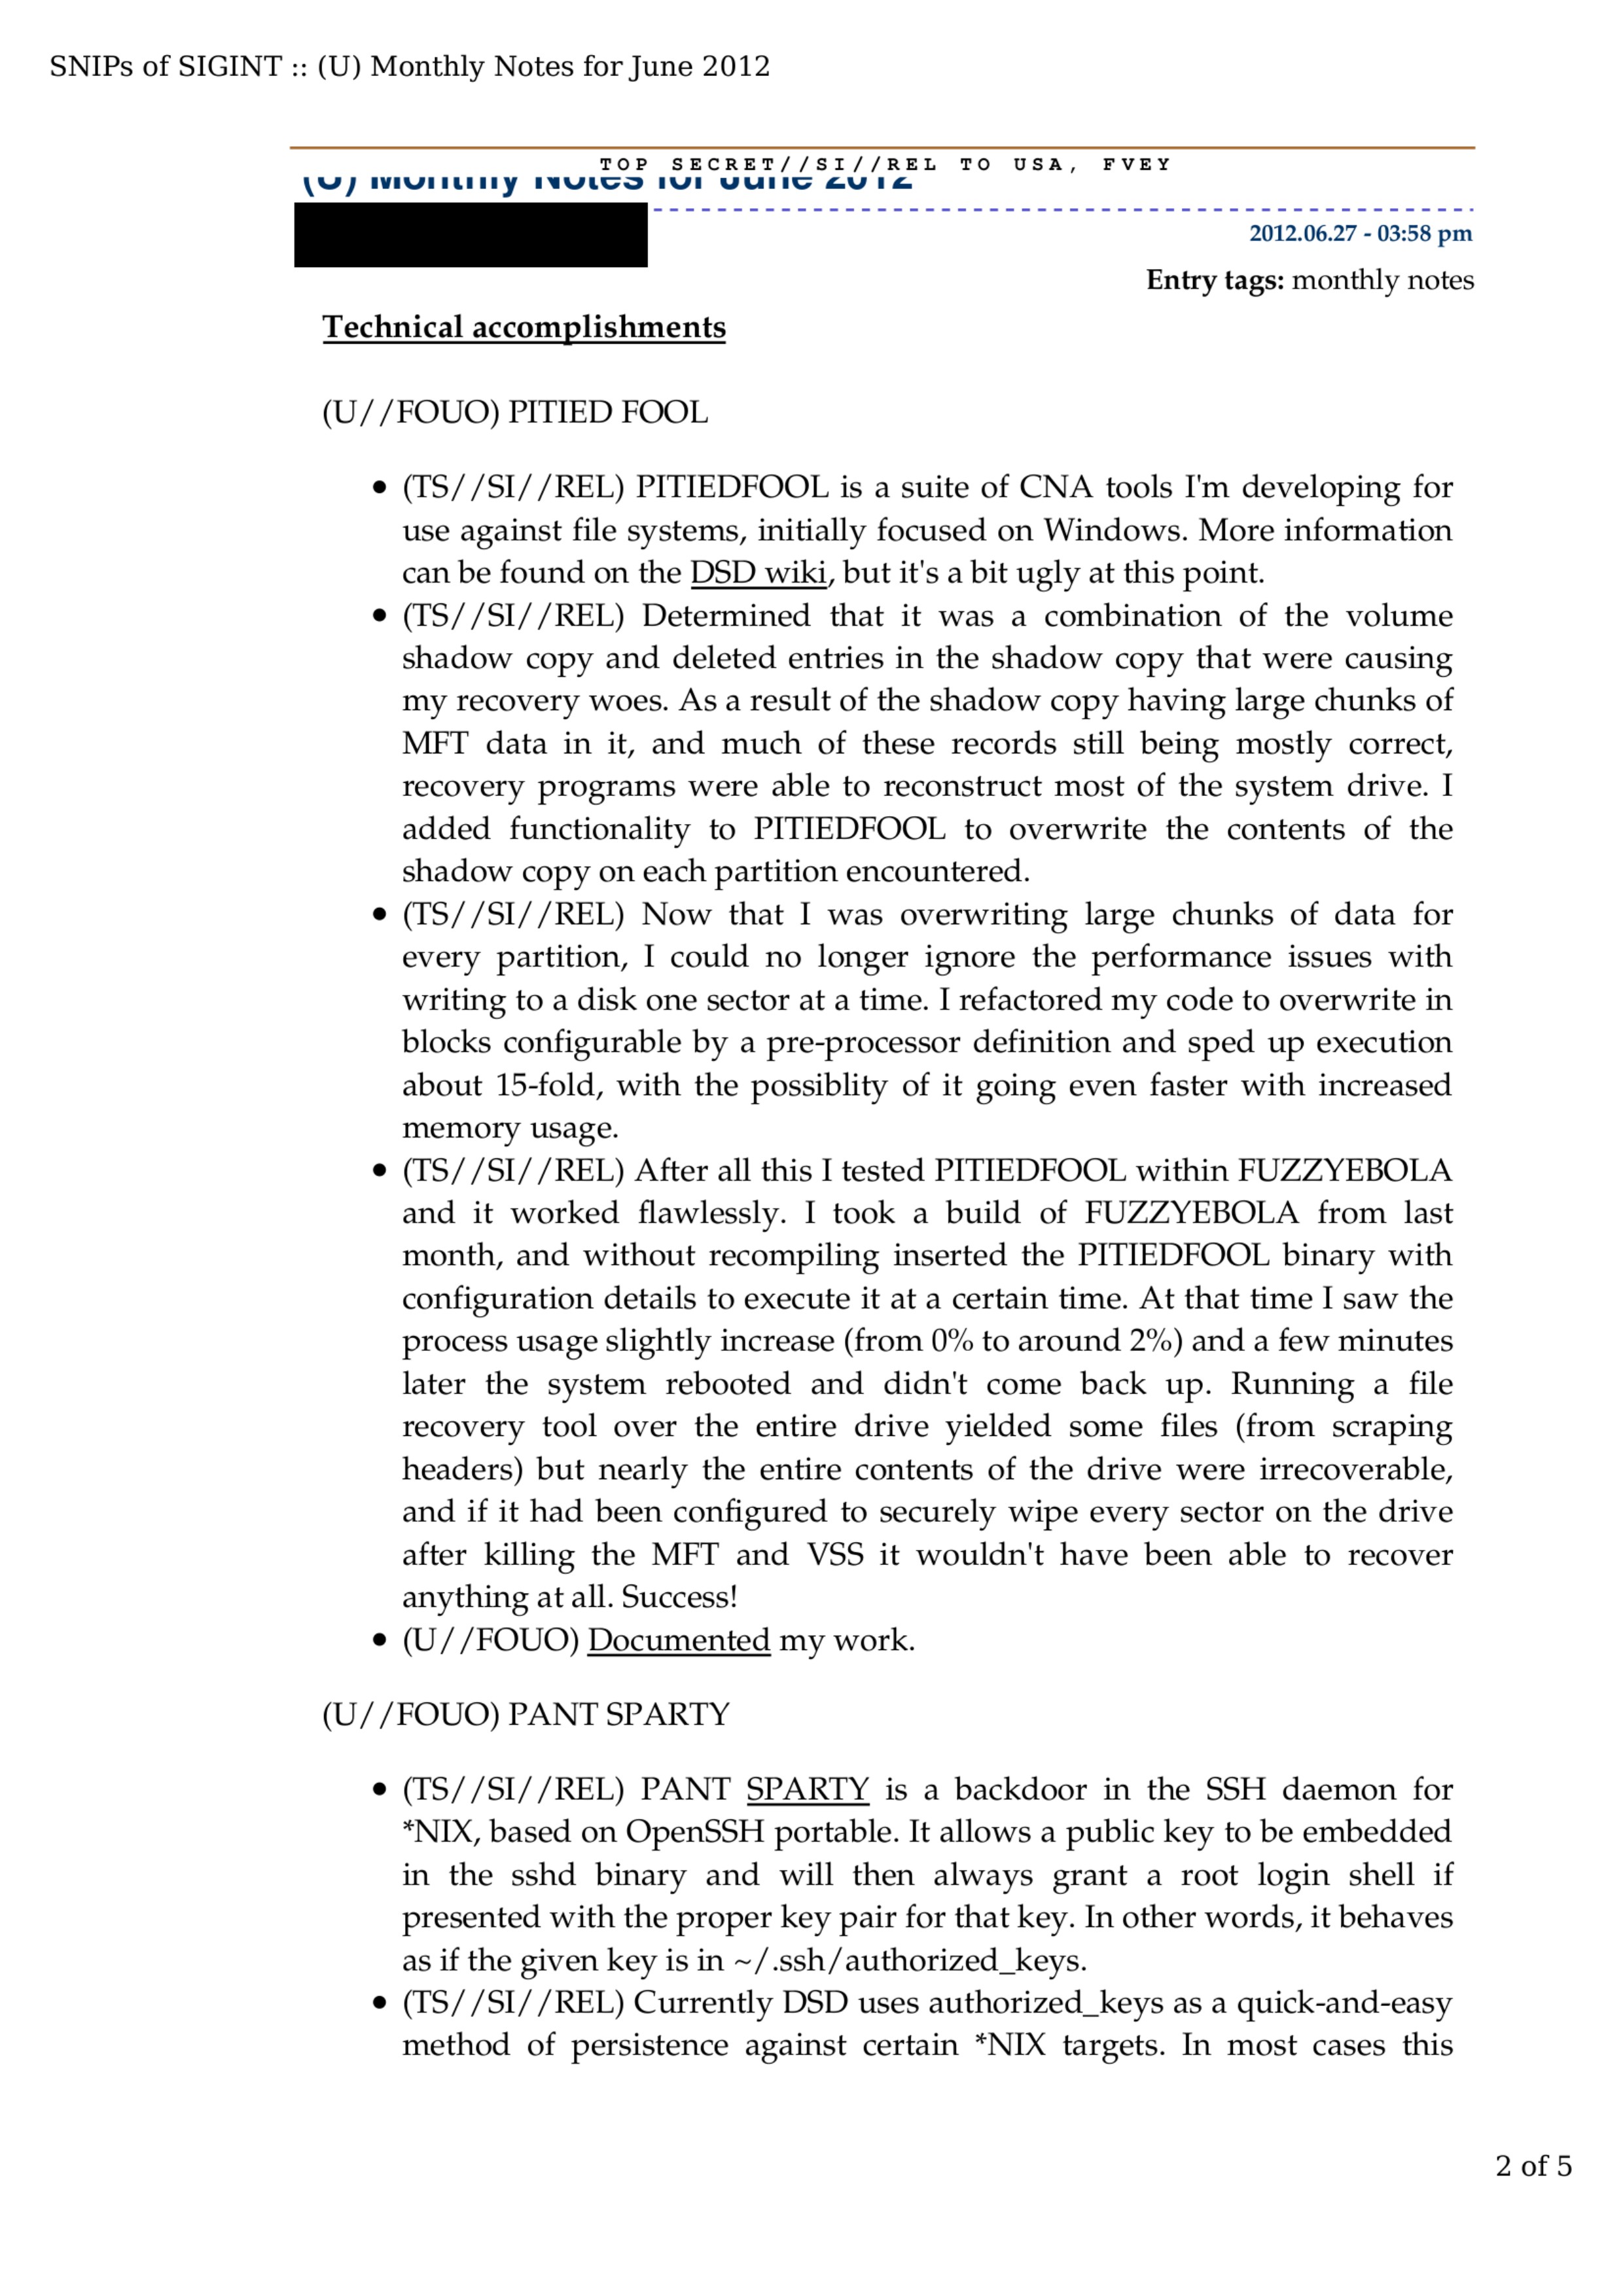
SNIPS of SIGINT :: (U) Monthly Notes for June 2012
TOP SECRET//SI//REL TO USA, FVEY
(U) Monthly Notes for June 2012
2012.06.27 - 03:58 pm
Entry tags: monthly notes
Technical accomplishments
(U//FOUO) PITIED FOOL
- (TS//SI//REL) PITIEDFOOL is a suite of CNA tools I'm developing for
use against file systems, initially focused on Windows. More information
can be found on the DSD wiki, but it's a bit ugly at this point. - (TS//SI//REL) Determined that it was a combination of the volume
shadow copy and deleted entries in the shadow copy that were causing
my recovery woes. As a result of the shadow copy having large chunks of
MFT data in it, and much of these records still being mostly correct,
recovery programs were able to reconstruct most of the system drive. I
added functionality to PITIEDFOOL to overwrite the contents of the
shadow copy on each partition encountered. - (TS//SI//REL) Now that I was overwriting large chunks of data for
every partition, I could no longer ignore the performance issues with
writing to a disk one sector at a time. I refactored my code to overwrite in
blocks configurable by a pre-processor definition and sped up execution
about 15-fold, with the possiblity of it going even faster with increased
memory usage. - (TS//SI//REL) After all this I tested PITIEDFOOL within FUZZYEBOLA
and it worked flawlessly. I took a build of FUZZYEBOLA from last
month, and without recompiling inserted the PITIEDFOOL binary with
configuration details to execute it at a certain time. At that time I saw the
process usage slightly increase (from 0% to around 2%) and a few minutes
later the system rebooted and didn't come back up. Running a file
recovery tool over the entire drive yielded some files (from scraping
headers) but nearly the entire contents of the drive were irrecoverable,
and if it had been configured to securely wipe every sector on the drive
after killing the MFT and VSS it wouldn't have been able to recover
anything at all. Success! - (U//FOUO) Documented my work.
(U//FOUO) PANT SPARTY
- (TS//SI//REL) PANT SPARTY is a backdoor in the SSH daemon for
*NIX, based on OpenSSH portable. It allows a public key to be embedded
in the sshd binary and will then always grant a root login shell if
presented with the proper key pair for that key. In other words, it behaves
as if the given key is in ~/.ssh/authorized_keys. - (TS//SI//REL) Currently DSD uses authorized_keys as a quick-and-easy
method of persistence against certain *NIX targets. In most cases this
2 of 5
SNIPS of SIGINT :: (U) Monthly Notes for June 2012
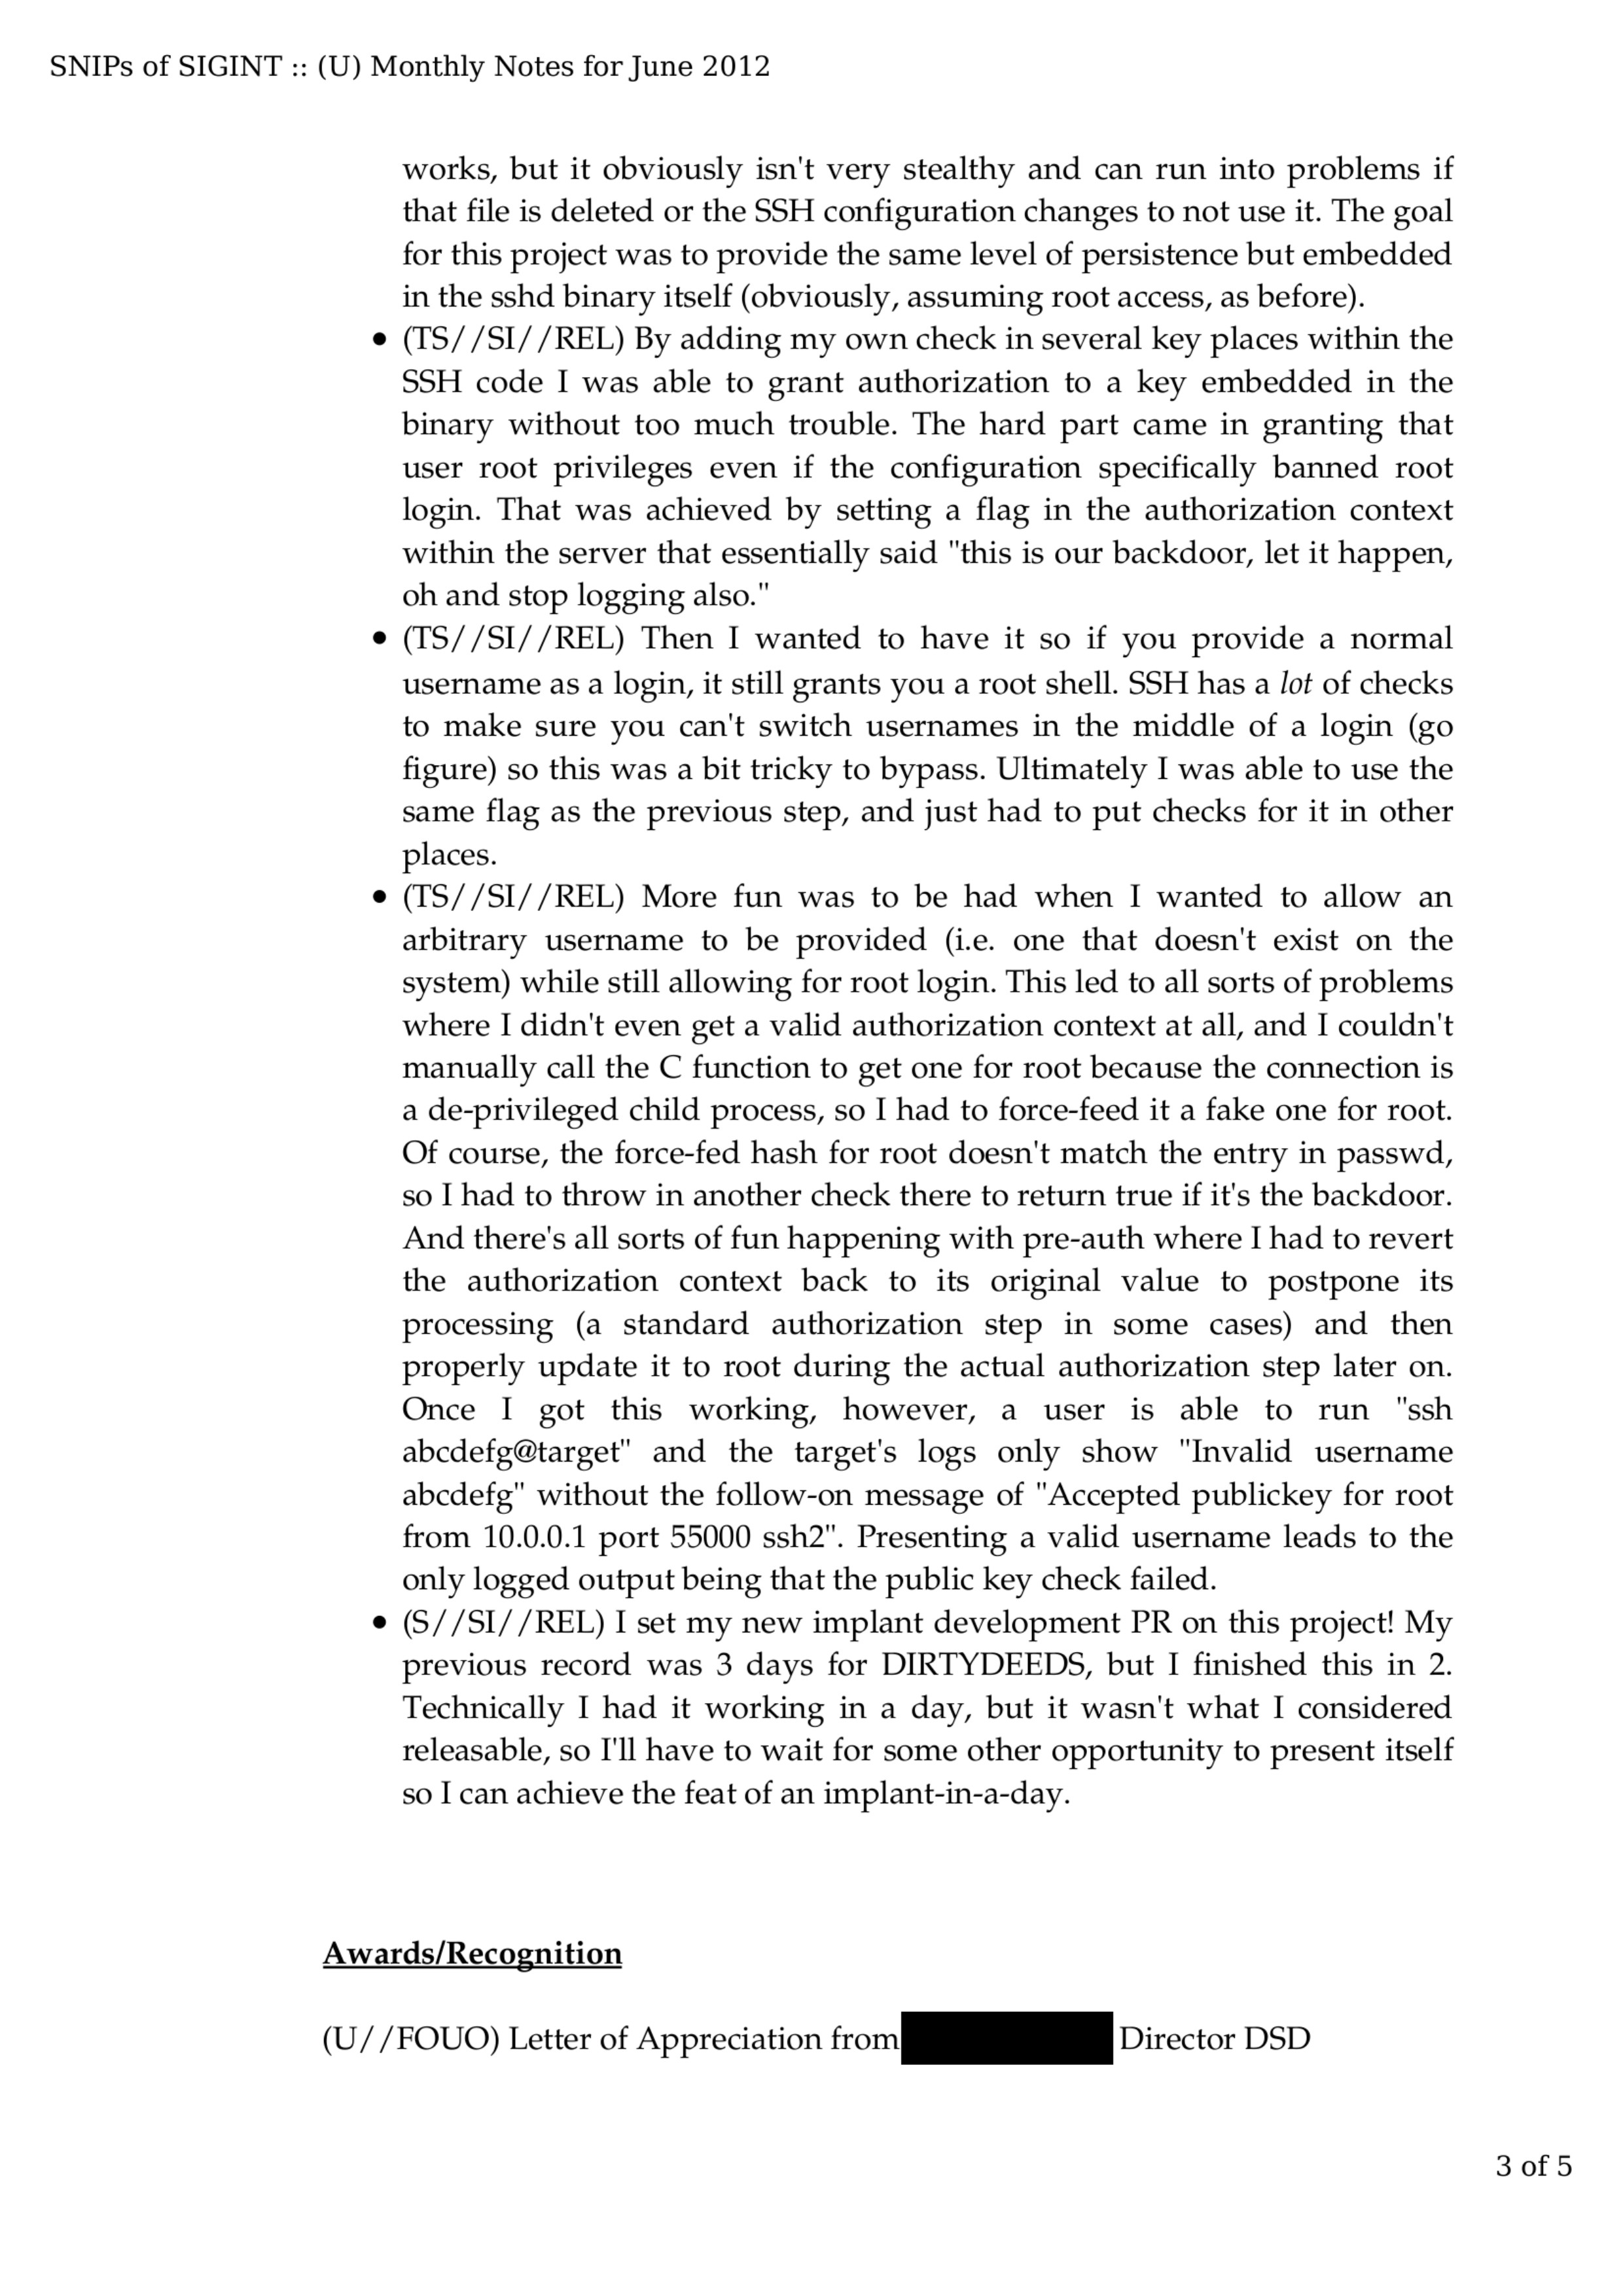
works, but it obviously isn't very stealthy and can run into problems if
that file is deleted or the SSH configuration changes to not use it. The goal
for this project was to provide the same level of persistence but embedded
in the sshd binary itself (obviously, assuming root access, as before).
- (TS//SI//REL) By adding my own check in several key places within the
SSH code I was able to grant authorization to a key embedded in the
binary without too much trouble. The hard part came in granting that
user root privileges even if the configuration specifically banned root
login. That was achieved by setting a flag in the authorization context
within the server that essentially said "this is our backdoor, let it happen,
oh and stop logging also." - (TS//SI//REL) Then I wanted to have it so if you provide a normal
username as a login, it still grants you a root shell. SSH has a lot of checks
to make sure you can't switch usernames in the middle of a login (go
figure) so this was a bit tricky to bypass. Ultimately I was able to use the
same flag as the previous step, and just had to put checks for it in other
places. - (TS//SI//REL) More fun was to be had when I wanted to allow an
arbitrary username to be provided (i.e. one that doesn't exist on the
system) while still allowing for root login. This led to all sorts of problems
where I didn't even get a valid authorization context at all, and I couldn't
manually call the C function to get one for root because the connection is
a de-privileged child process, so I had to force-feed it a fake one for root.
Of course, the force-fed hash for root doesn't match the entry in passwd,
so I had to throw in another check there to return true if it's the backdoor.
And there's all sorts of fun happening with pre-auth where I had to revert
the authorization context back to its original value to postpone its
processing (a standard authorization step in some cases) and then
properly update it to root during the actual authorization step later on.
Once I got this working, however, a user is able to run "ssh
abcdefg@target" and the target's logs only show "Invalid username
abcdefg" without the follow-on message of "Accepted publickey for root
from 10.0.0.1 port 55000 ssh2". Presenting a valid username leads to the
only logged output being that the public key check failed. - (S//SI//REL) I set my new implant development PR on this project! My
previous record was 3 days for DIRTYDEEDS, but I finished this in 2.
Technically I had it working in a day, but it wasn't what I considered
releasable, so I'll have to wait for some other opportunity to present itself
so I can achieve the feat of an implant-in-a-day.
Awards/Recognition
(U//FOUO) Letter of Appreciation from [REDACTED] Director DSD
3 of 5
SNIPS of SIGINT :: (U) Monthly Notes for June 2012
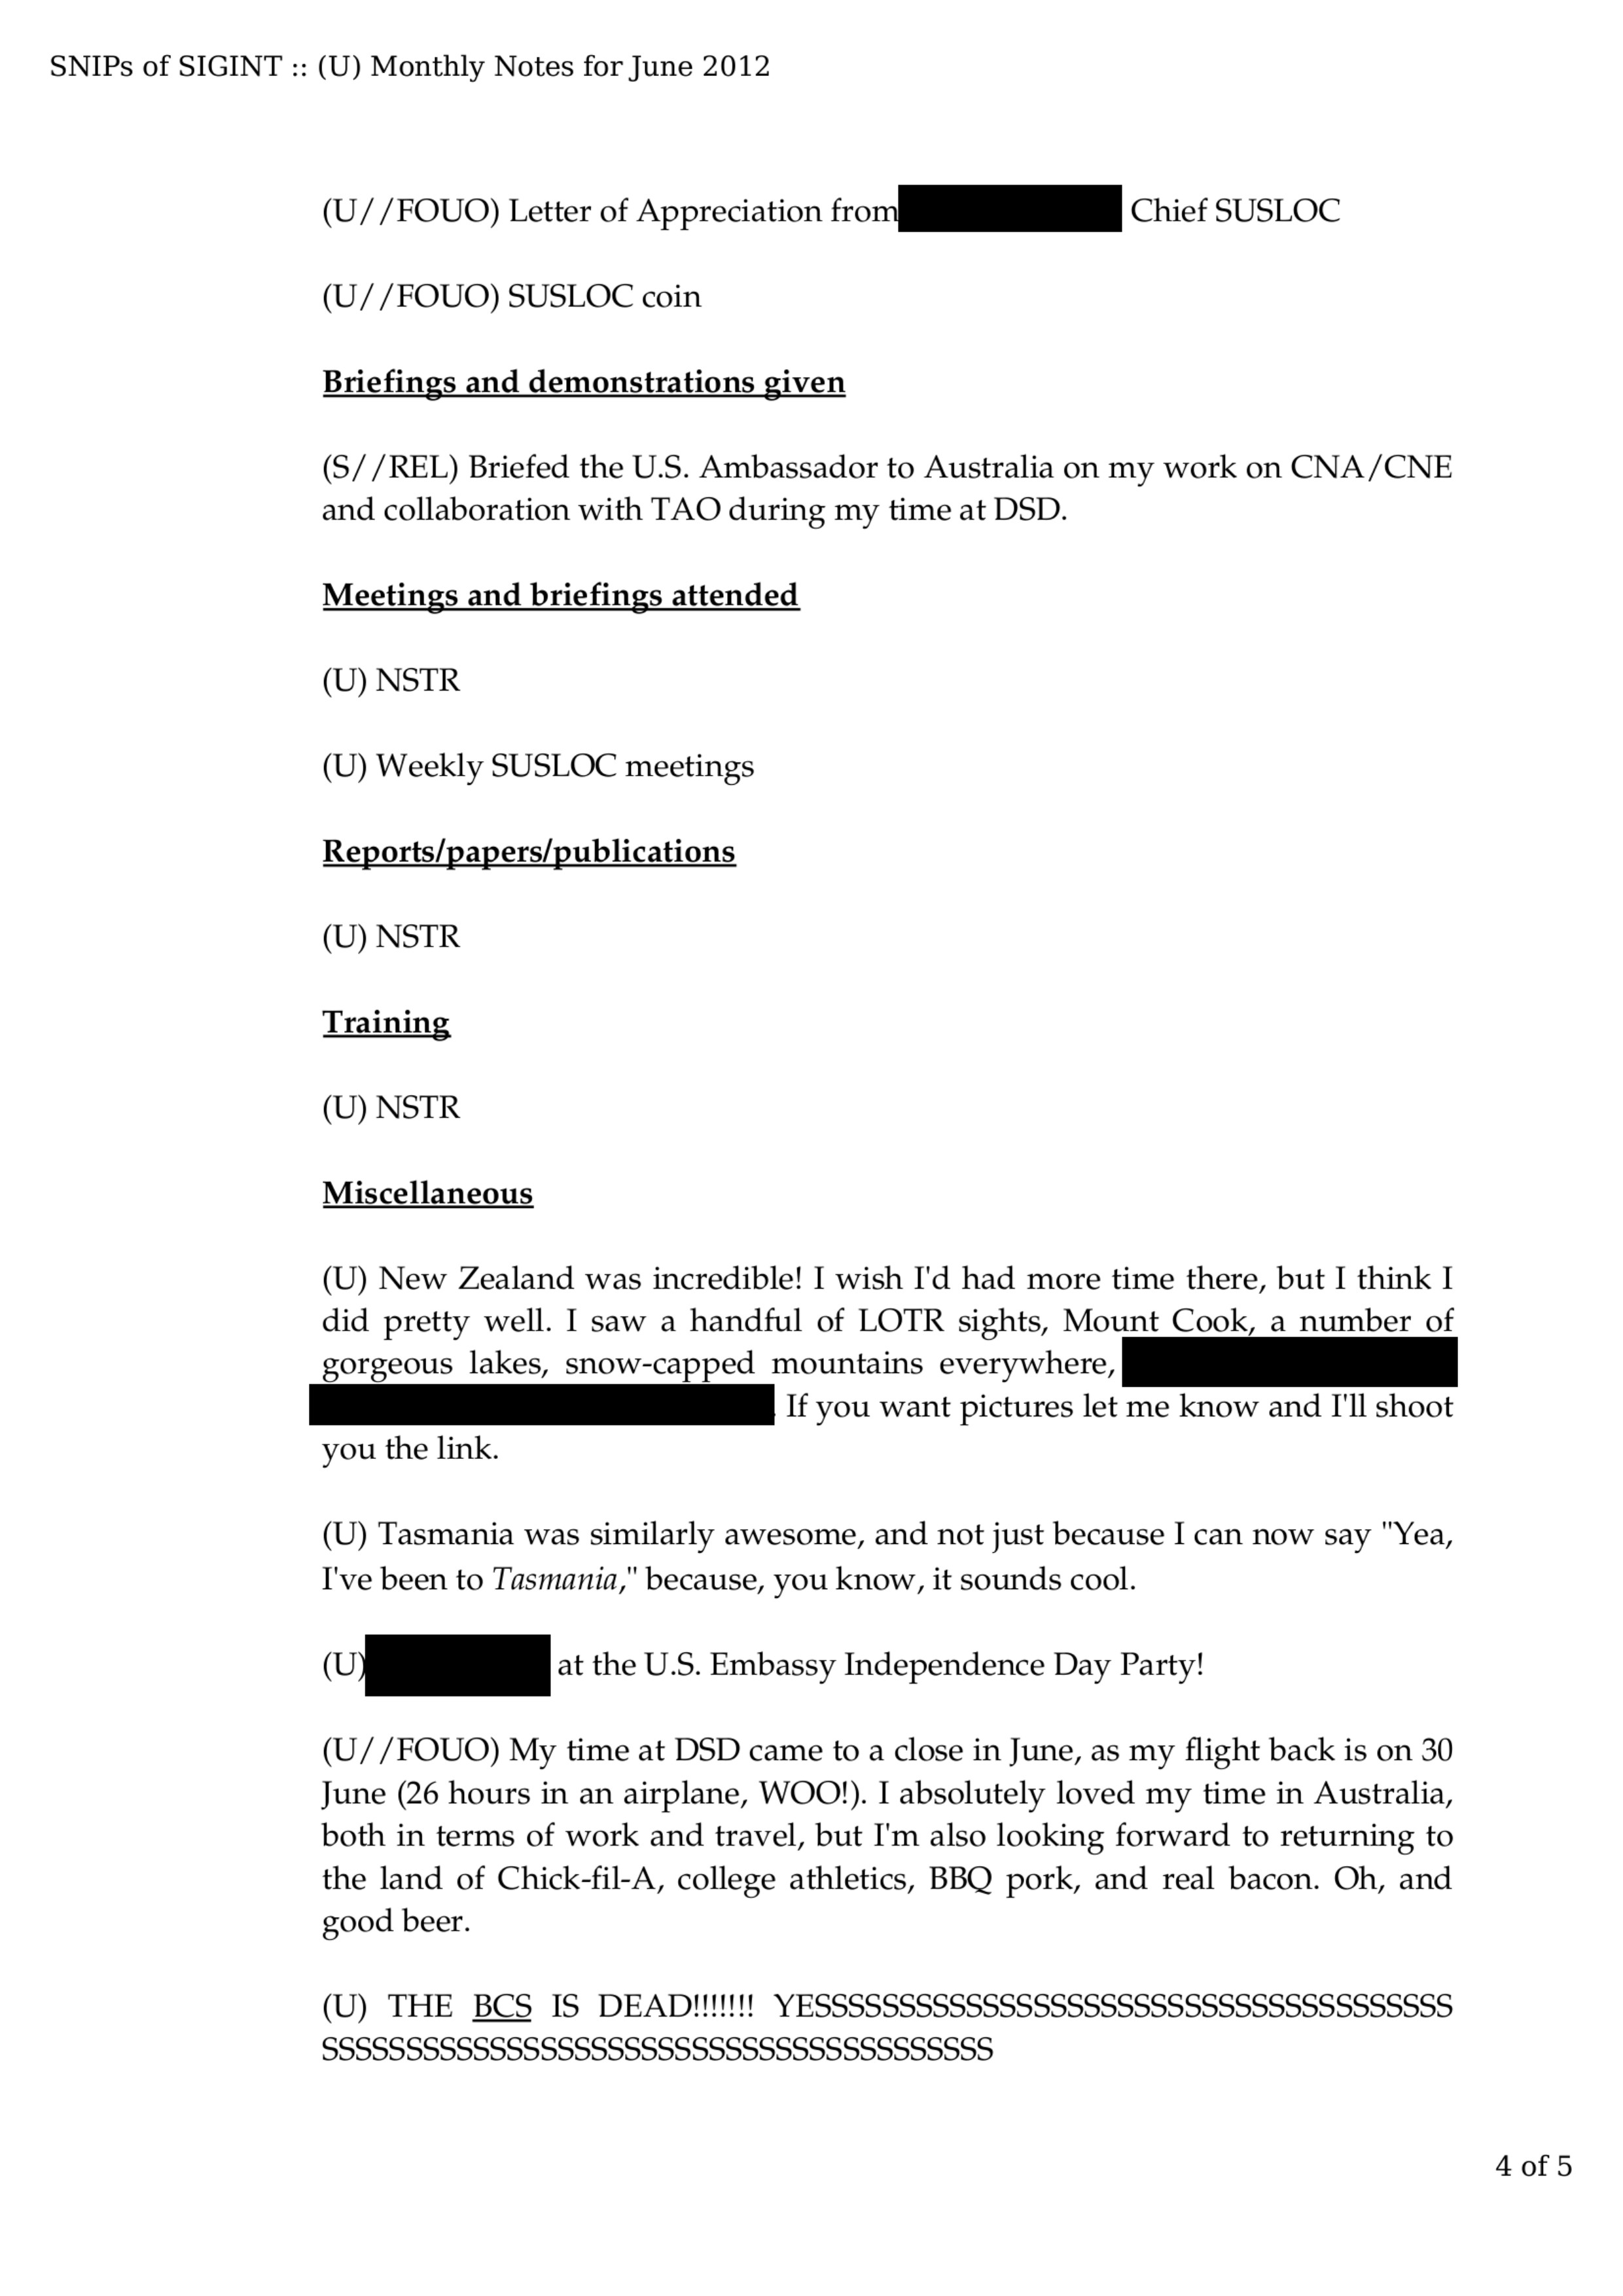
(U//FOUO) Letter of Appreciation from [REDACTED] Chief SUSLOC
(U//FOUO) SUSLOC coin
Briefings and demonstrations given
(S//REL) Briefed the U.S. Ambassador to Australia on my work on CNA/CNE
and collaboration with TAO during my time at DSD.
Meetings and briefings attended
(U) NSTR
(U) Weekly SUSLOC meetings
Reports/papers/publications
(U) NSTR
Training
(U) NSTR
Miscellaneous
(U) New Zealand was incredible! I wish I'd had more time there, but I think I
did pretty well. I saw a handful of LOTR sights, Mount Cook, a number of
gorgeous lakes, snow-capped mountains everywhere, [REDACTED]
[REDACTED] If you want pictures let me know and I'll shoot
you the link.
(U) Tasmania was similarly awesome, and not just because I can now say "Yea,
I've been to Tasmania," because, you know, it sounds cool.
(U) redacted at the U.S. Embassy Independence Day Party!
(U//FOUO) My time at DSD came to a close in June, as my flight back is on 30
June (26 hours in an airplane, WOO!). I absolutely loved my time in Australia,
both in terms of work and travel, but I'm also looking forward to returning to
the land of Chick-fil-A, college athletics, BBQ pork, and real bacon. Oh, and
good beer.
(U) THE BCS IS DEAD!!!!!!! YESSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSS
SSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSS
4 of 5
SNIPS of SIGINT :: (U) Monthly Notes for June 2012
SSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSS
SSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSSS!!!
(Leave a comment)
[REDACTED]
Page Publisher: T314 - End User Solutions
DERIVED FROM: NSA/CSSM 1-52
DATED: 08 JAN 2007
DECLASSIFY ON: 20320108
DYNAMIC PAGE
System Max: SECRET//SI/TALENT KEYHOLE//REL TO USA, FVEY
Portion Max: TOP SECRET//SI//REL TO USA, FVEY
5 of 5
Published in the Same Report
(10 of 34 documents)
-
Expanding Endpoint Operations SIDtoday [pdf]
Tailored Access Operations, NSA's elite hackers, are expanding their endpoint operations -- hacking directly into computers to steal information -- and are establishing the new endpoint operations remote operations center, scheduled to come online in the summer of 2005, that "is capable of managing and conducting endpoint operations on a scale that will dramatically expand collection." The physical office space of this new center will allow TAO to "grow from the current average of 20-25 of these operations per day to over 100 per day," and will allow TAO to increase the number of "active implants," or actively monitored pieces of malware, from 100-150 to thousands.
“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · The Intercept ↗ (2017-04-24) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
The ROC: NSA's Epicenter for Computer Network Operations SIDtoday [pdf]
The Remote Operations Center (ROC) conducts computer network operations against U.S. adversaries and foreign governments. Its motto is: "Your data is our data, your equipment is our equipment, anytime, any place, by any legal means."
The Intercept ↗ (2019-05-29) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
-
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
The FASHIONCLEFT Protocol [pdf]
This October 2008 NSA technical specification details FASHIONCLEFT, the encryption and exfiltration protocol used by TAO implants to securely tunnel captured network packets from compromised devices back to the NSA's Common Data Receptor using layered RSA and RC6 encryption with authentication. The document addresses technical integration challenges of implementing FASHIONCLEFT packet reception within TURMOIL's passive collection infrastructure, particularly cache buffering requirements and metadata handling for exfiltrated traffic.
Programs: FASHIONCLEFT · FOGYNULL · FUNNELAPS · SHELLGREY · TURMOIL · SURPASSPIN · PUZZLECUBE · FLASHHANDLE · HAMMERCHANT · AEG · PPF · ISLANDTRANSPORT -
Moving Data Through Disconnected Networks - Delay-Tolerant Networking and the IC [pdf]
This June 2012 NSA Laboratory for Telecommunications Sciences presentation details Delay-Tolerant Networking (DTN) applications for surveillance operations, including covert communications in denied areas, data exfiltration from isolated networks, unwitting data mules, and integration with TAO's CHIMNEYPOOL implant framework. The document reveals R4 development of FUZZYLINT, an ultra-lightweight DTN implementation designed to enable multi-hop exfiltration from implants without requiring direct physical access.
People: Vahdat, Amin · Becker, David · Juang, Philo · Oki, Hidekazu · Wang, Yong · Martonosi, Margaret · Peh, Li-Shiuan · Rubenstein, Daniel · Grossglauser, Matthias · Tse, David N. C. · Fall, Kevin · Shah, Rahul C. · Roy, Sumit · Jain, Sushant · Brunette, Waylon · Lindgren, Anders · Doria, Avri · Schelen, Olov · Small, Tara · Haas, Zygmunt J. · Zhao, Wenrui · Ammar, Mostafa · Zegura, Ellen · Ginzboorg, Philip · Kärkkäinen, Teemu · Nagata, Akira · Lenders, Vincent · Legendre, Franck · May, Martin · Karlsson, Gunnar · Du, Bowei · Demmer, Michael · Brewer, Eric · Ott, Jörg · Pitkänen, Mikko Juhani · Han, Bo · Hui, Pan





Related Documents
-
COMPUTER NETWORK OPERATIONS - GENIE [pdf]
A TOP SECRET Congressional Budget Justification entry for the NSA/CSS GENIE project — the Tailored Access Operations programme underpinning all endpoint Computer Network Operations — requesting $651.7 million and 1,870 military and civilian positions for FY2013, with plans to maintain 85,000-96,000 implant points-of-presence worldwide and 9,000-10,000 active accesses, including $25.1 million for covert purchase of software vulnerabilities and a $3.4 million supply chain implant operation targeting al-Qaeda.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR -
The ROC: NSA's Epicenter for Computer Network Operations SIDtoday [pdf]
The Remote Operations Center (ROC) conducts computer network operations against U.S. adversaries and foreign governments. Its motto is: "Your data is our data, your equipment is our equipment, anytime, any place, by any legal means."
The Intercept ↗ (2019-05-29) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael