Genre: slides 272 documents
Search documents matching “slides” →What kind of document it is: slides, report, wiki, manual, guide, newsletter.
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Bagram – Area 82 [pdf]
This document is a classified June 2010 progress report on the construction of the NSA’s Real Time Regional Gateway (RT-RG) data center at Area 82, Bagram Airfield, coordination with multiple U.S. and allied agencies, and the eventual deployment of the system after extensive infrastructure work. It emphasizes the transition from temporary container setups to a permanent facility enabling real-time signals intelligence in Afghanistan.
Marking: SECRET“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
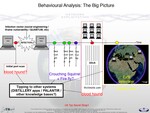
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
BLACK HOLE ANALYTICS, ADD/SD briefing, September 2009 [pdf]
This September 2009 GCHQ briefing describes the BLACK HOLE analytics infrastructure and Next Generation Events (NGE) project, which planned to scale from ~8 10-gigabit connections to ~200 10Gs by March 2011, storing intercepted data in massive flat-file repositories at Benhall and Bude before loading it into "Question Focused Dataset" (QFD) databases that power surveillance tools like MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS, and others. The document outlines how "probes" extract Target Detection Identifiers (TDIs) from intercepted data feeds, store them in BLACK HOLE repositories, then enable analysts to profile targets' online activities, create social networks, investigate websites and forums, track web searches and Google Earth usage, and perform large-scale data mining across internet and telephony data.
Programs: BLACKHOLE · MUTANTBROTH · AUTOASSOC · INFINITEMONKEYS · KARMAPOLICE · SOCIALANIMAL · HRMAP · MEMORYHOLE · MARBLEDGECKO · HARDASSOC · SAMUELPEPYS · BLAZINGSADDLES · TELLURIAN · BUFFER · DISTILLERY · LOOKINGGLASS · NGEPeople: bin Laden, Osama -
BOUNDLESSINFORMANT - Describing Mission Capabilities from Metadata Records [pdf]
This presentation on the Boundless Informant program (BOUNDLESSINFORMANT), which uses big data tools to analyze and visualize global SIGINT metadata collection in near real time. It explains how the system replaced older manual methods, enabling the NSA to track collection volumes, coverage, and trends for specific countries or sites through cloud-based infrastructure.
People: Patel, Vimesh“NSA-files repeatedly show collection of data «against countries» - not «from»” - Dagbladet ↗ (2013-11-22) · “Boundless Informant: the NSA's secret tool to track global surveillance data” - The Guardian ↗ (2013-06-08) · “Claves y giros del espionaje masivo en España” - El Mundo ↗ (2013-11-04) · Greenwald, Glenn · MacAskill, Ewen · Aranda, Germán -
BOUNDLESSINFORMANT Overview [pdf]
World map view from the Boundless Informant program, with "CNE" (Computer Network Exploitation) selected from the dropdown.
Programs: BOUNDLESSINFORMANT -
Bulk collection of webmail address books and emerging protocols [pdf]
TOP SECRET NSA document details the large-scale collection of email address books and contact lists from major webmail and social media providers, emphasizing their metadata value despite low attribution rates to known targets. It also highlights ongoing efforts to identify and analyze emerging communication protocols, such as those used by Hotmail Messenger.
-
BULLRUN [pdf]
A GCHQ TOP SECRET STRAP1 briefing presentation on BULLRUN — summarising the programme's purpose, the network security technologies it targets, the sensitivities surrounding cryptanalytic capabilities, and the access control framework protecting both technical details and the "fact of" capability — notable for explicitly naming three ECIs protecting the technical underpinnings: PICARESQUE, PAWLEYS and AMBULANT.
-
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
Canyondust coverage regions [pdf]
This document describes NSA's capabilities for exploiting commercial satellite communications (VSAT), including systems from Hughes, ViaSat, iDirect, and others. It details programs such as FALLOWHAUNT and CORRALCLOUD for targeting and analyzing satellite communications technologies, including TDMA and PCMA systems.
Programs: CANYONDUST · TIMBERLINE · CARBOY · JACKKNIFE · SHOAL BAY · FALLOWHAUNT · CORRALCLOUD · DOUBLETALK -
CASCADE - Joint Cyber Sensor Architecture [pdf]
This presentation outlines the Communications Security Establishment’s (CSE) plans to unify and expand its cyber sensor networks (ITS and SIGINT) to create a comprehensive, multi-layered national cyber defense system, enabling threat detection, intelligence collection, and defensive operations across Canadian and foreign networks. It emphasizes standardizing sensor deployments, integrating analytic capabilities, and preparing for “Effects” operations to mitigate cyber threats by 2015. The presentation is duplicated from page 33 onwards - three slides of the duplicated slides have internal CSE comments.
Programs: CASCADE · PHOTONICPRISM · EONBLUE · INDUCTION · THIRDEYE · CRUCIBLE · CHOKEPOINT · SUNWHEEL · CASSIOPEIA · SCNET · JAZZFLUTE · GAZEBO · SEEDSPHERE · TEXPRO · SSO -
Case Studies of Integrated Cyber Operation Techniques [pdf]
Programs: AURORAVNC · TUTELAGE · QUANTUM · TURBINE · BOXINGRUMBLE · CLOUDSHIELD · PANDORASMAYHAM · TURMOIL · QUANTUMTHEORY · QUANTUMDNS · TAOSHOOTER · DEFIANTWARRIOR · QUANTUMINSERT · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMHAND · QUANTUMPHANTOM · QUANTUMSKY · QUANTUMCOPPER · QUANTUMSMACKDOWN · QUANTUMSANDMAN · FOXACID“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
Center for Content Extraction - Content Extraction Analytics, SIGDEV End-to-End Demo [pdf]
This document is a technical showcase demonstrating the capabilities of an NSA content‑extraction program, using political leaders and diplomatic figures (such as Angela Merkel) as illustrative examples. It presents how automated language technology can extract, organize, and scale intelligence data from intercepted material.
Programs: MARINA · CYBERTRANS · PAINTBALL · SYNAPSE · NYMROD · THUNDERCLOUD · JOURNEYMAN · GOLDENRETRIEVER · SOCIOPATH · LEXHOUND · HERESYITCH · HLT · TKB · EKS -
Center for Content Extraction - Nymrod Mission [pdf]
This top-secret NSA document outlines the mission and capabilities of NYMROD, a system developed by the Center for Content Extraction (CCE). It explains how NYMROD addresses analytic challenges such as linguistic variation in entity names, especially for person names, and the resolution of entity coreference problems using contextual evidence. The document discusses the multilingual content extraction services provided by NYMROD, which support various NSA enterprise applications and enhance analytic functions like selection, translation, analysis, investigative research, retrieval, and storage.
People: Ban, Ki-moon -
Chinese Exfiltrate Sensitive Military Technology [pdf]
This TOP SECRET NSA SIGINT development briefing describes large-scale Chinese cyber espionage that exfiltrated sensitive U.S. military technologies and inflicted extensive operational, financial, and strategic damage on Department of Defense systems. The document emphasizes both the scale of losses and the role of SIGINT in detecting, understanding, and mitigating adversary malware.
Programs: BYZANTINEHADES -
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
CNO Core Secrets Security Structure [pdf]
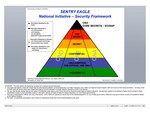
A 3-slide NSA presentation outlining the classification architecture of Sentry Eagle, a national cyber operations initiative, showing how its most sensitive components — covering network hacking, encryption sabotage, and covert industry relationships — are locked behind ECI and SAP designations accessible only to a tiny circle of government officials.
Programs: SENTRYEAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CNO Core Secrets Slide Slices [pdf]
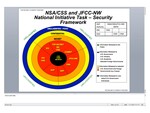
This document outlines the Security Framework for a joint national initiative between the NSA/CSS and JFCC-NW, detailing the highly compartmented structure used to protect cyber and intelligence secrets. It utilizes a concentric security framework diagram to visualize the layers of sensitivity, placing the most critical technical capabilities at the absolute center of the intelligence community's protection.
Programs: SENTRY-EAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CNO Legal Authorities [pdf]
An NSA Office of General Counsel briefing on the legal authorities for computer network operations and the NTOC floor: constitutional and EO 12333 limits, NSCID 6 definitions, Wiretap Act exceptions, NSD 42, service-provider information-assurance rules (DoD 5240.1-R), and oversight and compliance.
-
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
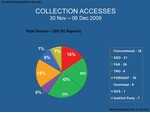
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO -
Contact chaining [pdf]
A secret GCHQ Applied Research presentation describing how the agency's analysts use automated tools to map out a surveillance target's social network — starting with a known email address or phone number, then scoring and ranking every person that target communicates with to identify the most "suspicious" or strongly connected contacts, using twelve different relationship types including direct calls, shared locations, timing patterns, equipment sharing and calling profile similarity.
Programs: CARPAT · PRIME TIME · SNAPDRAGON · MoaG · SORTING FRIENDS · CHART BREAKER · MAMBA · CONTACTLENS · FLEXIMART · PSOUP · IMMINGLE