Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE)
Open PDFDocument date: -
Pages: 1
Genre: slides
Banner: UK Top Secret Strap1
Classification: TOP SECRET STRAP 1
Dissemination: -
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
My notes
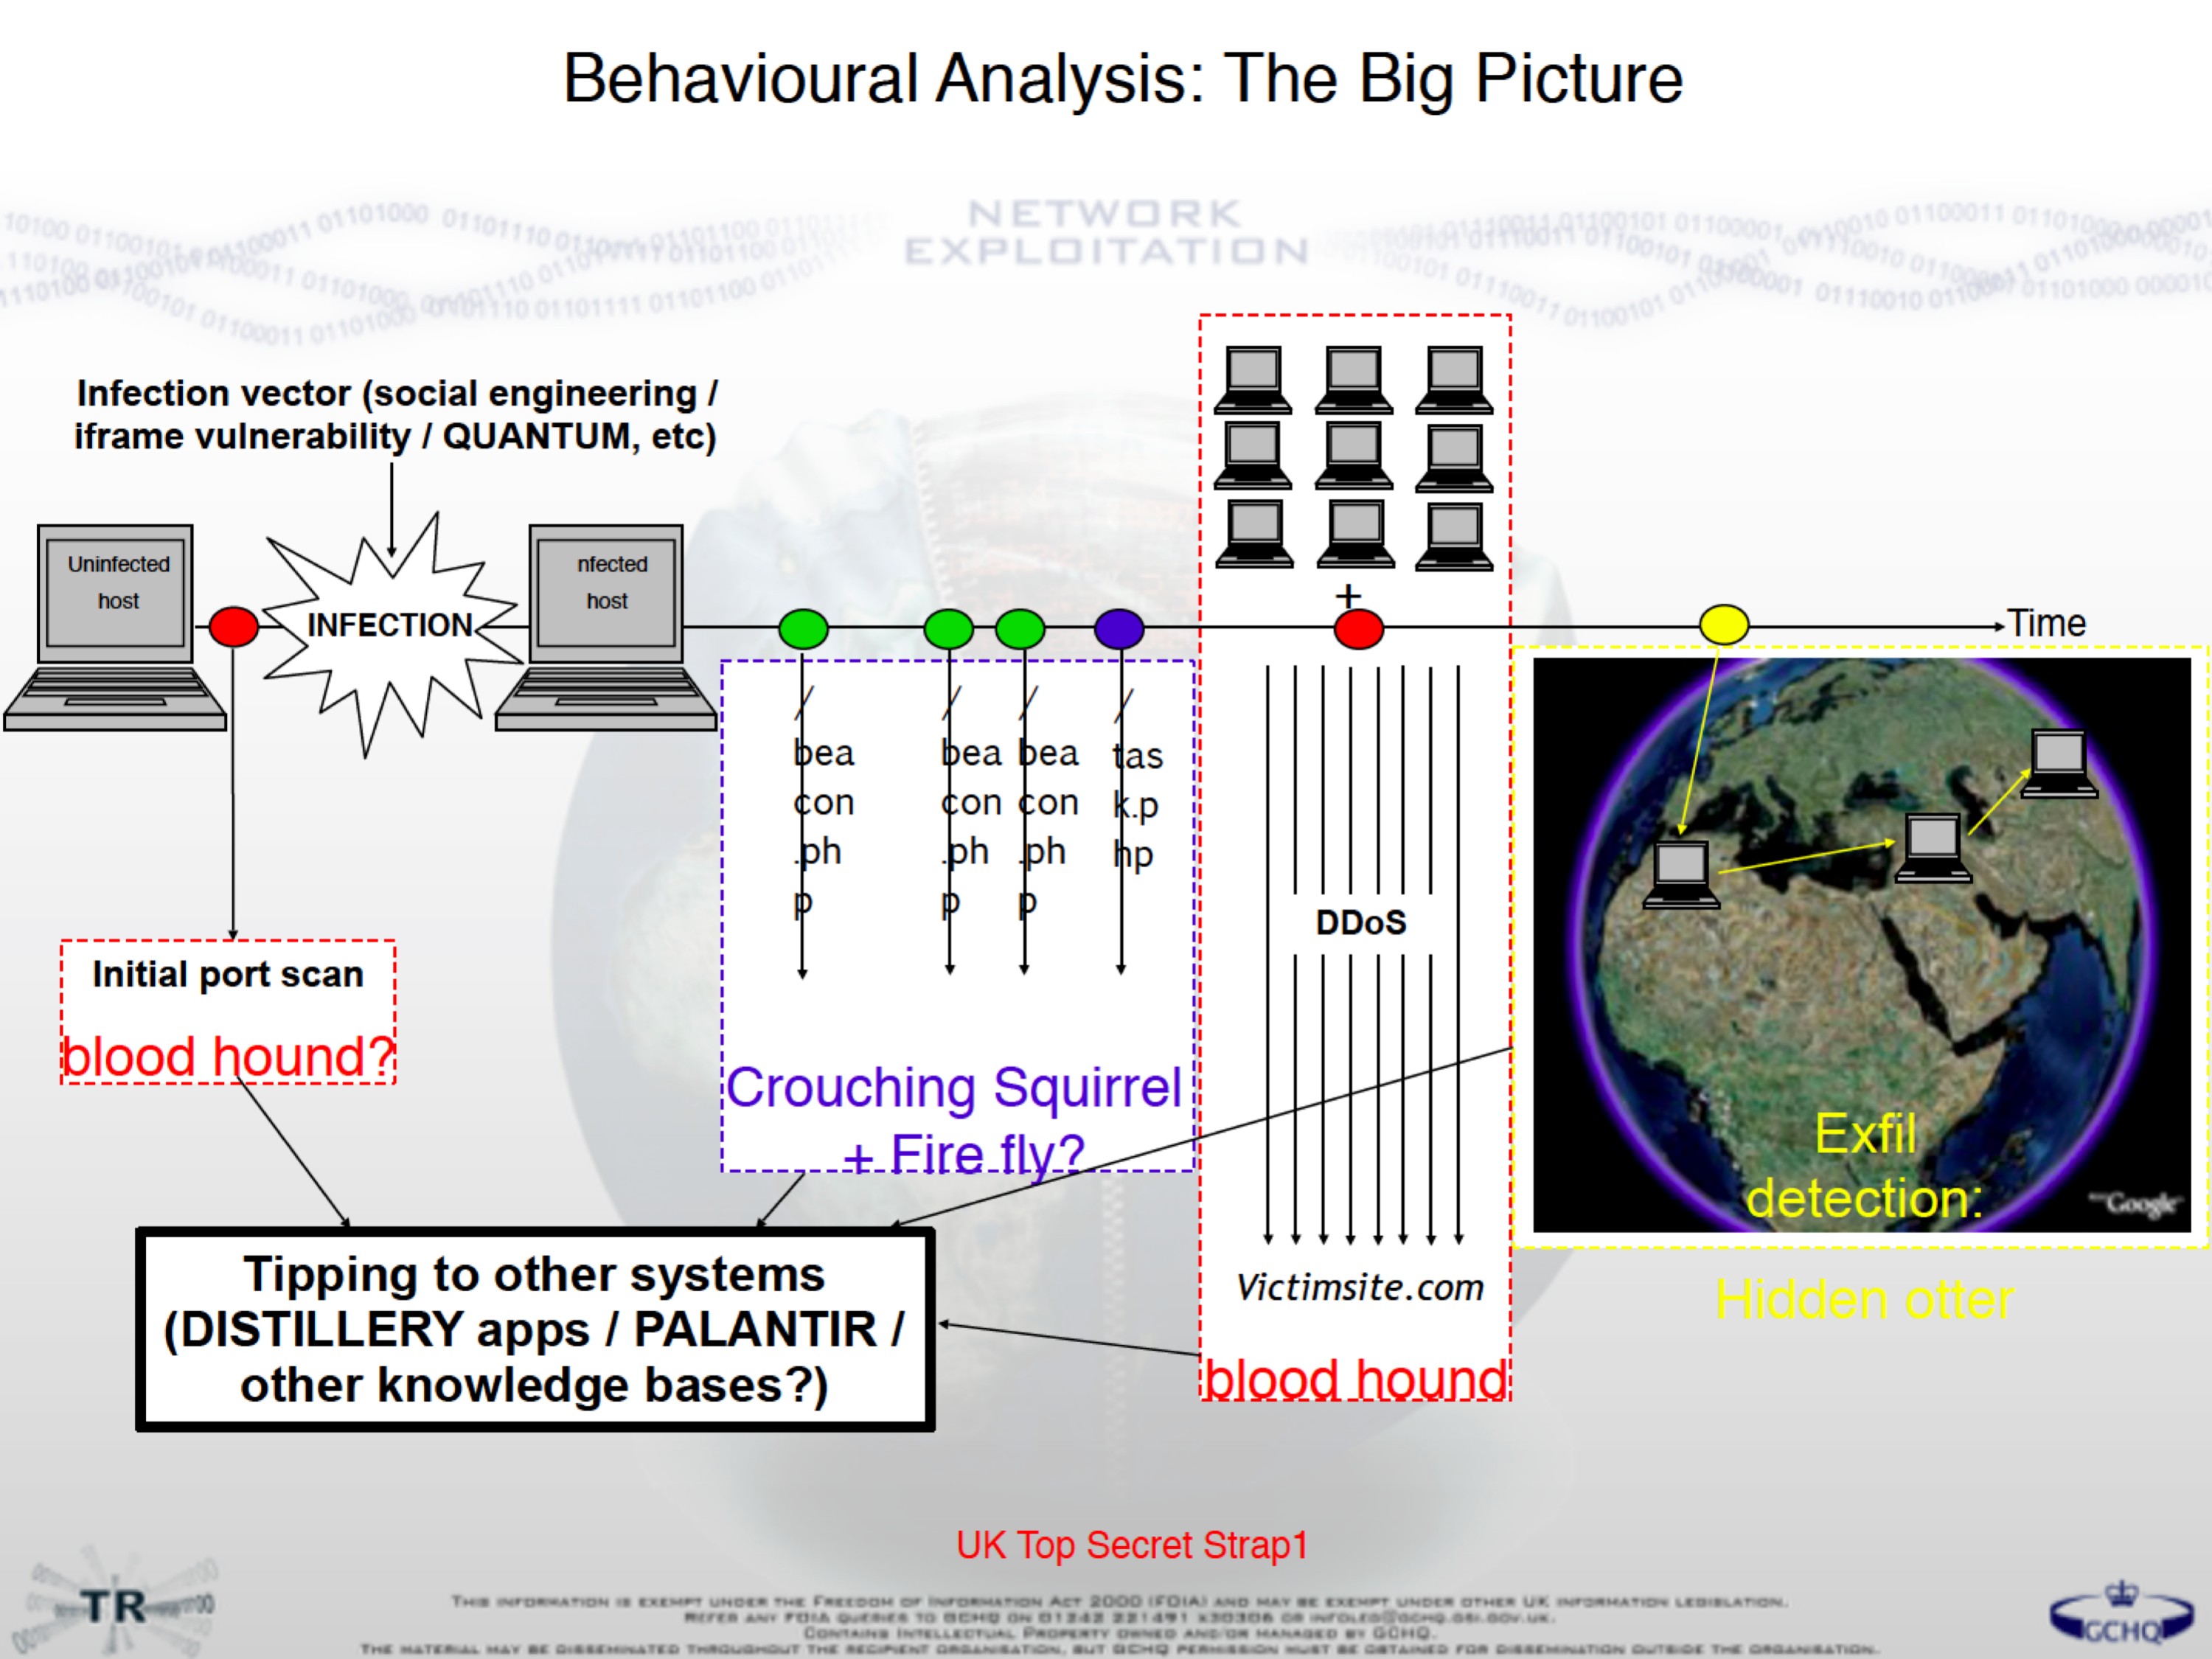
Behavioural Analysis: The Big Picture
NETWORK EXPLOITATION
Infection vector (social engineering / iframe vulnerability / QUANTUM, etc)
Uninfected host INFECTION nfected host
Initial port scan
blood hound?
beacon.php
beacon.php
beacon.php
task.php
Crouching Squirrel + Fire fly?
DDoS
Victimsite.com
blood hound
Tipping to other systems (DISTILLERY apps / PALANTIR / other knowledge bases?)
Time
Exfil detection:
Hidden otter
UK Top Secret Strap1
TR
GCHQ
Published in the Same Report
(6 documents)
-
-
The Tale of Two Sources [pdf]
Programs: SUPERDRAKE · CROUCHINGSQUIRREL · HALTERHITCH · MVR · PPF · GORDIANKNOT · XKEYSCORE · SAMUELPEPYS · ALPINEBUTTERFLY · TRYST · FRACTALJOKER · TM · SPAY · BLACKHOLE · RAPIDTAPIR · HIDDENOTTER · SALTYOTTER · 8BALL · SORCERER · PACMAN · SNORT · WAFTER · CRIMSON · SHORTFALL · GCNET · BROADOAK · RAPTOR · GEOFUSION · MUGSHOT · HACIENDA · FOXTRAIL · FANNER · GLOBALSURGE · PENSIVEGIRAFFE · HRMAP · MUTANTBROTH · SAMPEPYS · INTEGERSPIN · MWX · MARBLEPOLLS · MOONRAKER · RT · DISTILLERY · SQUEAL · DEADSEA · GTE · WDM · TKB · TRAFFIC MASTER · CHOKEPOINT · CONTENT CLOUD · MAPREDUCE · EVENTS · CLOUD · AGILITY · PALANTIR -
SDSG Integrated Analytics Workshop (14 Oct 2011) [pdf]
This document is a summary of a workshop held by the SIGINT Development Steering Group (SDSG) on October 14, 2011, evaluating and comparing the strengths, weaknesses, and potential use of advanced analytics tools, specifically Palantir and Mamba, for intelligence analysis. It discusses the tools' capabilities in data integration, collaboration, and visualization, along with concerns about security, usability, and the risks of relying on commercial software.
Marking: SECRET -
TWO FACE [pdf]
This document describes the GCHQ's TWO FACE project, a part of the Cyber Defence mission, which focuses on enhancing analysis and knowledge sharing tools using Palantir software. It outlines various data sources integrated with Palantir, such as XKEYSCORE and GEOFUSION, and the project's goals to automate and improve data importation, analysis capabilities, and user interface performance. The document also discusses training, user access, and collaboration within the Five Eyes intelligence community, as well as ongoing development to address gaps in existing cyber defense tools. It provides detailed instructions for using Palantir's capabilities to analyze and visualize data from multiple sources, with a focus on cyber defense and network defense operations. Key features include handling large datasets, running complex queries, and automating data integration. The document also highlights ongoing improvements, such as the addition of new data sources and the refinement of analytic tools to better support the cyber defense mission.
Programs: TWOFACE · PALANTIR · FRACTALJOKER · FRACTALWEB · PENSIVEGIRAFFE · XKEYSCORE · LIVE · AUTOASSOC · SOCIALANTHROPOID · INFINITEMONKEYS · KARMAPOLICE · SAMPEPYS · HRMAP · MUTANTBROTH · GEOFUSION · HACIENDA · FOXTRAIL · CROUCHINGSQUIRREL · PITCHFORD · HALTERHITCH · GORDIANKNOT · SAMUELPEPYS · MUGSHOT · RAPIDTAPIR · FIVEALIVE · GOOGLEFUSION · INTEGERSPIN · DEADSEA · MOONRAKER · OBERON · DISCOVER · 8BALL · CASK -
GCHQ VisWeek 2008 Conference Report [pdf]
This GCHQ document summarizes key findings from the VisWeek 2008 visualization conference in Ohio, highlighting techniques and tools relevant to SIGINT analysis including collaborative analysis capabilities, graph visualization methods, and the Palantir Government platform. The report recommends incorporating features like analyst notebooks for tracking investigations, collaborative workspaces for multiple analysts, and various graph layout algorithms into GCHQ's MONTE VISTA visualization system.
Programs: MONTE VISTA · MAMBA · CHARTBREAKER · PIGS EAR · KNIME · RAPTOR · BROAD OAK · HAUSTORIUM · SALAMANCA · IIB · INFOVIS · PALANTIR -
XKEYSCORE Helper Notes [pdf]
This GCHQ document describes new features in the XKEYSCORE Palantir helper tool, including summary/histogram import capabilities that reduce large datasets by aggregating connection data rather than creating individual events for each entry, and data sourcing features that track which XKEYSCORE queries imported specific data into Palantir. The document provides step-by-step screenshots showing how analysts can histogram network traffic by source IP, destination IP, and ports, then import aggregated results showing metadata like total session sizes and connection counts.
Programs: XKEYSCORE
Related Documents
-
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
The Tale of Two Sources [pdf]
Programs: SUPERDRAKE · CROUCHINGSQUIRREL · HALTERHITCH · MVR · PPF · GORDIANKNOT · XKEYSCORE · SAMUELPEPYS · ALPINEBUTTERFLY · TRYST · FRACTALJOKER · TM · SPAY · BLACKHOLE · RAPIDTAPIR · HIDDENOTTER · SALTYOTTER · 8BALL · SORCERER · PACMAN · SNORT · WAFTER · CRIMSON · SHORTFALL · GCNET · BROADOAK · RAPTOR · GEOFUSION · MUGSHOT · HACIENDA · FOXTRAIL · FANNER · GLOBALSURGE · PENSIVEGIRAFFE · HRMAP · MUTANTBROTH · SAMPEPYS · INTEGERSPIN · MWX · MARBLEPOLLS · MOONRAKER · RT · DISTILLERY · SQUEAL · DEADSEA · GTE · WDM · TKB · TRAFFIC MASTER · CHOKEPOINT · CONTENT CLOUD · MAPREDUCE · EVENTS · CLOUD · AGILITY · PALANTIR -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC