Genre: slides 272 documents
Search documents matching “slides” →What kind of document it is: slides, report, wiki, manual, guide, newsletter.
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Content Extraction Enhancements For Target Analytics: SMS Text Messages: A Goldmine to Exploit (9 June 2011) [pdf]
The document describes the NSA’s Dishfire program, which collects hundreds of millions of global SMS messages daily, and the PREFER system, which extracts detailed metadata—including contacts, geolocation, travel, and financial information—from these messages for analytic purposes. It highlights the scale, operational processes, and types of data exploited to support intelligence and target analysis.
-
Converged Analysis of Smartphone Devices [pdf]
This 2010 document outlines NSA methods for identifying, processing, and exploiting data from smartphones by targeting both telephony and digital network intelligence (DNI). It details how analysts use tools like XKEYSCORE and metadata extraction to collect geolocation, app data, call logs, unique identifiers, and user activity from popular mobile apps and services (e.g., Google Maps, Facebook, Flickr), emphasizing the intelligence potential of smartphones as rich surveillance targets.
People: Kuruc, Paula -
CRYPTOLOGIC SERVICES GROUPS (CSGs) [pdf]
Worldwide locations of the Cryptologic Services Groups (CSGs). The visual is a world map annotated with the locations of CSGs embedded in or supporting major U.S. combatant commands and agencies. These groups act as NSA’s cryptologic arms inside military commands. Cryptologic operations are co-located with military command authority and signals intelligence is structurally tied to every major U.S. warfighting domain.
-
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC Cyber Threat Detection [pdf]
This document details the Communications Security Establishment’s (CSEC) cyber threat detection and intelligence infrastructure, including systems like EONBLUE, CROSSBOW, CRUCIBLE, and LODESTONE, which enable passive monitoring, anomaly detection, and botnet identification through metadata and deep packet inspection. It outlines how CSEC integrates SIGINT, cryptanalysis, and network forensics to detect and mitigate cyber intrusions using both SIGINT and domestic sensors, while collaborating with Five Eyes partners to enhance Canada’s cyber defense and situational awareness. The presentation is duplicated from page 7 onwards - one of the duplicated slide has internal CSE comments.
Programs: EONBLUE · SPECIALSOURCE · WARRANTEDACCESS · COVENANT · SEEDSPHERE · DIESELRATTLE · SIENNABLUE · DOWNGRADE · CROSSBOW · CRUCIBLE · LODESTONE -
CSEC ITS/N2E Cyber Threat Discovery [pdf]
A CSEC IT Security presentation to the DISCOCON 2010 conference, given with speakers' notes, on how the agency's cyber threat discovery team hunts for intrusions in the traffic it collects from Government of Canada networks. It describes the PonyExpress email processing system, which the notes record as handling 400,000 emails a day, the 8Ball attachment scanner and the Stripsearch binary analyser, and reports experiments in reducing the volume of metadata analysts see — including a machine learning model that discards 85% of email before deep scanning.
Marking: TOP SECRETPrograms: PONYEXPRESS · 8BALL · STRIPSEARCH · POPQUIZ · SLIPSTREAM · FINDMASK · SAWUNEH · TROPPUSNU · N2E · DISCOCON -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
CSEC Surveillance of Travellers Through Airport Wi-Fi Tracking [pdf]
The leaked 2012 top secret CSEC presentation details a trial program that used airport Wi-Fi metadata to identify and track travellers’ devices across Canada and internationally, developing advanced “IP profiling” techniques to map movements through hotels, airports, and public hotspots. The program, conducted with NSA support, aimed to build powerful analytic tools for surveillance and real-time alerts within the Five Eyes intelligence network.
Marking: TOP SECRET -
Current Efforts - Google [pdf]
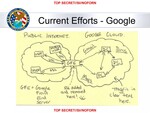
The famous NSA slide from the MUSCULAR program showing where Google's encryption is stripped away — a hand-drawn diagram of Google's cloud architecture annotated with "SSL Added and removed here!" beside a smiley face, marking the exact point where NSA and GCHQ intercepted Google user data flowing unencrypted between Google's data centers.
-
Cyber Integration [pdf]
The leaked 2012 GCHQ JTRIG presentation detail a wide range of offensive cyber and influence operations designed to “deny, disrupt, degrade, and deceive” targets, including hackers, foreign governments, companies, and individuals. Tactics include hacking, DDOS attacks, disinformation, honey traps, credential harvesting, and psychological operations, reflecting a shift from traditional surveillance to active disruption and manipulation campaigns.
“Exclusive: Snowden Docs Show British Spies Used Sex and 'Dirty Tricks'” - NBC News ↗ (2014-02-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Cole, Matthew · Esposito, Richard · Schone, Mark · Greenwald, Glenn -
Cyber Network Defence R&D Activities [pdf]
A September 2010 CSEC briefing to the Five Eyes 5IARC conference on cyber defence R&D, giving the full PONY EXPRESS email attachment scanning architecture and the PHOTONIC PRISM sensor, with speaker notes in which the presenter concedes CSEC does little research of its own.
Marking: SECRETPrograms: PHOTONICPRISM · PONYEXPRESS · SLIPSTREAM · POPQUIZ · 8BALL · SNORT · POPEYESEAR · FLOWPONY · SMTPPONY · MAILPONY · METAPONY · SCANPONY · AGGPONY · SYNCPONY · POOLTABLE · POOLCUE · CORNERPOCKET · TONTO · MULASSES · MULVAL · ASSETRANK · JNDMS · ARMOUR · SWAD · MINISSL · SSLFUZZER · N3C · N3 · CTEC · DCITS · 5IARC -
-
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
Demystifying NGE Rock Ridge [pdf]
This presentation outlines the ROCK RIDGE project, which delivers a suite of "Question Focused Databases" (QFDs) like MUTANT BROTH and KARMA POLICE to analyze massive internet event data. These specialized databases are designed to answer specific intelligence questions and are developed using the BLACK HOLE data repository, a key component of the ROUGH DIAMOND program.
Programs: ROCKRIDGE · ROUGHDIAMONG · BLACKHOLE · HAUSTORIUM · HRMAP · MUTANTBROTH · KARMAPOLICE · GOOBZS · INFINITEMONKEYS · AUTOASSOC · SOCIALANIMAL · MARBLEDGECKO · MEMORYHOLE · SAMUELPEPYS · SALAMANCA · MONOPOLY · RADIUS · HARBOURPILOT · LOOKINGGLASS · FIRESTORM · SUPERDRAKE · BLAZINGSADDLES · BLUESHIFT · SUPPORTINGINO · TERRAINS · GEOFUSION · NGEPeople: Lobban, Iain -
DFS SIGINT-enabled Cyber [pdf]
This February 2013 top-secret DFS presentation outlines how Japan’s Directorate for Signals Intelligence (DFS) developed a SIGINT-enabled cyber program with U.S. NSA support, launching operations in late 2012 using the MALLARD system to collect and analyze satellite-based internet sessions. It details the project’s buildup, early challenges with massive data volumes, reliance on U.S. technical assistance, and plans for expanded antennas, infrastructure, and long-term system upgrades.
Marking: TOP SECRETPrograms: MALLARD“The Untold Story of Japan's Secret Spy Agency” - The Intercept ↗ (2018-05-19) · “日本の諜報 スクープ 最高機密ファイル” - NHK ↗ (2018-05-19) · Gallagher, Ryan -
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
DROPMIRE on the Cryptofax at the EU Embassy D.C. [pdf]
This document reveals that the NSA secretly targeted EU diplomatic communications through a program called DROPMIRE, which involved placing surveillance implants on encrypted fax machines at the EU Embassy in Washington, D.C. This operation was part of a broader effort to spy on 38 foreign embassies and missions—including allies such as France, Italy, and Greece—to gain inside knowledge of policy debates and diplomatic positions.
Programs: DROPMIRE -
Elegant Chaos: collect it all, exploit it all [pdf]
This document outlines a classified project, "Elegant CHAOS," focused on advanced signals intelligence (SIGINT) collection, processing, and analysis using cutting-edge technologies like automated surveys and modems. It highlights goals such as real-time data analysis, collaboration with international partners, and integration with cloud-based platforms to manage massive data. See also the document with notes (by GCHQ): "Elegant-Chaos-collect-it-all-exploit-it-all-plus"
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · AMULETSTELLAR · CLOUD · WEALTHYCLUSTER · MVR · TINT · IPGEOTRAP · MARINA · PLUS -
Elegant Chaos: collect it all, exploit it all (plus notes) [pdf]
GCHQ/NSA presentation describing ELEGANT CHAOS — an automated system at the Menwith Hill Station satellite interception facility that scores and ranks thousands of intercepted satellite signals by intelligence value, automatically deciding which ones deserve collection resources based on criteria like geographic location, target network hits, technology type and Computer Network Operations interest — built to implement the station's directive to "Sniff it All, Know it All, Collect it All, Process it All, Exploit it All, Partner it All" as collection capacity scaled from 100 signals to a planned 3,000 simultaneous intercepts.
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · WHIZBANG · CLOUDBASE · APLUS · MAILORDER · CROSSBONES · AMULET STELLAR · MVR · TINT · WEALTHYCLUSTER · IPGEOTRAP · MARINA · CLOUD · PLUS