Program: BLOODHOUND 2 documents
Search documents matching “BLOODHOUND” →Codenames and programs recorded for each document.
Refine (combine with another filter, via search)
Sort: Title
Documents
-
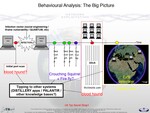
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
ICTR Cloud Efforts [pdf]
A GCHQ presentation details how the agency developed cloud-based big data analytics to achieve "population scale" surveillance—processing trillions of internet events to build geographic and behavioral profiles on every online identifier worldwide, enabling discovery of unknown targets through pattern analysis rather than traditional keyword searches.
Programs: EVERYASSOC · PROBABILITYCLOUD · SILVERLINING · CULTWEAVE · KARMAPOLICE · EVERYPOLICE · AWKWARDTURTLE · GORDIANKNOT · SANDIA · BLOODHOUND · FIVEALIVE · NGE · MAPREDUCE