Article
Hunting for Hackers, N.S.A. Secretly Expands Internet Spying at U.S. Border
Documents published with this article 7
-
CNO Legal Authorities [pdf]
An NSA Office of General Counsel briefing on the legal authorities for computer network operations and the NTOC floor: constitutional and EO 12333 limits, NSCID 6 definitions, Wiretap Act exceptions, NSD 42, service-provider information-assurance rules (DoD 5240.1-R), and oversight and compliance.
-
Final Cyberspace Policy Review: Appendices D and E [pdf]
Appendices D and E of a secret, REL FVEY Cyberspace Policy Review. Appendix D evaluates the Comprehensive National Cybersecurity Initiative initiatives and enablers and the status of each. Appendix E argues for an international cybersecurity policy framework, covering internet governance bodies, free speech, supply chains and deterrence.
Programs: EINSTEIN -
New FAA702 Certification in the Works - Cyber Threat [pdf]
A 23 March 2012 SSO article on a draft FAA 702 certification for cyber threats. It would let analysts task selectors tied to malicious cyber activity without attributing them to a foreign government or terrorist group, and would codify tasking of IP addresses and code strings through PRISM and the upstream accesses.
-
PRISM planning slide (PRISM briefing 1) [pdf]
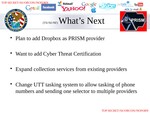
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
PRISM tasking slide (PRISM briefing 2) [pdf]
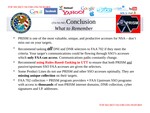
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
SID concur: SSO's Support to the FBI for Implementation of their Cyber FISA Orders (CATS 2012-704) [pdf]
A 2012 NSA staff processing form (CATS 2012-704) with a four-page SSO memo, concurred by the SIGINT Director on 27 March 2012. SSO would give the FBI technical help implementing FISC cyber orders (docket 11-91, which the FBI calls STYGIAN FLOW), using NSA collection and processing infrastructure (LITHIUM, ARTIFICE, TURMOIL), with the FBI responsible for the costs and for legal compliance.
People: Shea, Teresa H. -
NSA Cyber Timeline (Some Key SSO Cyber Milestone Dates Since Fall 2005) [pdf]
A one-page NSA SSO timeline of cyber-related milestones from fall 2005 to late 2012: CNCI implementation, the Protect America Act and FISA Amendments Act certifications, TURMOIL and XKEYSCORE deployments, and the August 2012 Iranian DDoS attack on Saudi Aramco.
Programs: TURMOIL · SSO · BLUESNORT · DANCINGOASIS · MADCAPOCELOT · TURBULENCE · XKEYSCORE · WEALTHYCLUSTER