Document year: 2012 102 documents
Search documents matching “2012” →When each document was written, from its own dateline. Undated documents don't appear here.
Sort: Title
Documents
-
Intellipedia – Supply Chain Cyber Threats [pdf]
This document on Supply Chain Cyber Threats, from an internal wiki for the U.S. intelligence community, outlines vulnerabilities in hardware and firmware components such as power supplies, NICs, RAID controllers, GPUs, and peripheral devices that could be exploited by adversaries through the supply chain. It details assessments from U.S. intelligence agencies (CIA, DIA, FBI, CYBERCOM) highlighting risks from foreign companies, insider threats, and malicious modifications that could compromise critical U.S. government and military systems.
Programs: A-SPACE -
Interview with a SID "Hacker" -- Part 1: How Does TAO Do Its Work? SIDtoday [pdf]
A SIDToday interview from July 2012 with a counterterrorism subject-matter expert in TAO's Requirements and Targeting organisation, explaining how TAO plans and executes computer network exploitation operations.
“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Arbeiten mit geheimen Snowden-Dokumenten” - Der Spiegel ↗ (2015-07-03) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Eckert, Svea · Stark, Holger -
Interview with a SID "Hacker" -- Part 2: Hacker Culture and Worker Retention SIDtoday [pdf]
A SIDtoday internal NSA newsletter interview with a redacted TAO employee discussing hacker culture within the agency's offensive cyber unit, worker retention challenges, and the team's role in operations including the raid that killed Osama bin Laden.
Programs: SCQAWKPeople: bin Laden, Osama -
Is It the End of the SIGINT World as We Have Come to Know It? [pdf]
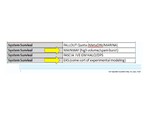
Two excerpts from a 2012 NSA presentation titled "Is It the End of the SIGINT World as We Have Come to Know It?" prepared by a member of the Large-Access Exploitation Group. The table excerpt lists MAINWAY among the systems at highest risk of being overwhelmed by the volume of data the agency was ingesting. The diagram excerpt shows MAINWAY feeding into the Graph-in-Memory (alongside WESTERNSTAR), illustrating how MAINWAY's continuous contact-chaining pushed its precomputed results into the in-memory graph database that analysts actually queried.
Programs: FALLOUT · METADNI · MARINA · MAINWAY · FASCIA · GMHALO · DPS · EKS · WESTERNSTAR · GRAPH-IN-MEMORY -
JTRIG tools and techniques [pdf]
This document is an internal GCHQ wiki page from July 2012 detailing the capabilities of GCHQ’s Joint Threat Research Intelligence Group (JTRIG). It serves as an internal "Chinese menu" or catalog of digital tools and techniques used for engineering, intelligence collection, and "effects" (offensive operations).
Programs: JTRIG · CERBERUS · JTRIG RADIANTSPLENDOUR · ALLIUMARCH · ASTRALPROJECTION · TWILIGHTARROW · SPICEISLAND · POISONARROW · FRUITBOWL · NUTALLERGY · BERRYTWISTER · BERRYTWISTER+ · FORESTWARRIOR · JAZZFUSION · BRANDYSNAP · WINDFARM · BOMBAYROLL · COUNTRYFILE · TECHNOVIKING · JAZZFUSION+ · BUMBLEBEEDANCE · AIRBAG · EXPOW · AXLEGREASE · PODRACE · WATCHTOWER · REAPER · DIALd · DIRTYDEVIL · AIRWOLF · ANCESTRY · BEARTRAP · BIRDSONG · BIRDSTRIKE · BUGSY · DANCINGBEAR · DEVILSHANDSHAKE · DRAGON'SSNOUT · EXCALIBUR · FATYAK · FUSEWIRE · GLASSBACK · GODFATHER · GOODFELLA · HACIENDA · GEOFUSION · GLOBALSURGE · ICE · INSPECTOR · LANDINGPARTY · VIKINGPILLAGE · MINIATUREHERO · MOUTH · MUSTANG · PHOTONTORPEDO · RESERVOIR · SEBACIUM · SILVERSPECTER · SODAWATER · SPRINGBISHOP · DIRTYRAT · SYLVESTER · TANNER · TRACERFIRE · VIEWER · TOPHAT · ANGRYPIRATE · ARSONSAM · BUMPERCAR+ · BOMBBAY · BADGER · BURLESQUE · CANNONBALL · CLEANSWEEP · CLUMSYBEEKEEPER · CHINESEFIRECRACKER · BUMPERCAR · CONCRETEDONKEY · DEERSTALKER · GATEWAY · GAMBIT · GESTATOR · GLITTERBALL · IMPERIALBARGE · PITBULL · POISONEDDAGGER · PREDATORSFACE · ROLLINGTHUNDER · SCARLETEMPEROR · SCRAPHEAPCHALLENGE · SERPENTSTONGUE · SILENTMOVIE · SILVERBLADE · SILVERFOX · SILVERLORD · SKYSCRAPER · SLIPSTREAM · STEALTHMOOSE · SUNBLOCK · SWAMPDONKEY · TORNADOALLEY · UNDERPASS · VIPERSTONGUE · WARPATH · HOMEPORTAL · CYBERCOMMANDCONSOLE · NAMEJACKER · BABYLON · CRYOSTAT · ELATE · PRIMATE · JEDI · JILES · MIDDLEMAN · OUTWARD · TANGLEFOOT · SCREAMINGEAGLE · SLAMMER · EARTHLING · NEWPIN · BYSTANDER · CONDUIT · QUINCY · BEARSCRAPE · SFL · SNOOPY · MOBILEHOOVER · NEVIS · CHANGELING · HAVOK · MIRAGE · SHADOWCAT · SPACEROCKET · RANA · LUMP · GURKHASSWORD · CRINKLECUT · SHORTFALL · DEADPOOL · HUSK · LONGSHOT · MOLTEN-MAGMA · NIGHTCRAWLER · PISTRIX · WURLITZER -
LEVITATION and the FFU Hypothesis [pdf]
This document describes LEVITATION, a top-secret Canadian Communications Security Establishment (CSE) project that monitors millions of daily file uploads and downloads from free file-sharing sites to identify potential extremist activity. It details the program’s data collection methods, analytical workflow, use of partner databases, and examples of successful discoveries related to terrorist materials and hostage videos.
-
LOVELY HORSE – GCHQ Wiki Overview [pdf]
This February 2012 GCWiki page describes LOVELY HORSE, a GCHQ initiative to collect, index, and distribute open-source intelligence from cybersecurity blogs and Twitter accounts to analysts on classified networks, utilizing JTRIG's BIRDSTRIKE architecture to scrape content from approximately 60 sources including security researchers, hacktivist groups like Anonymous and LulzSec, and cybersecurity companies, with legal approval from MP-LEG (Mission Policy-Legal).
Programs: LOVELYHORSE · HAPPYTRIGGER · BIRDSEED · JTRIG · BIRDSTRIKE · MERAPEAK · LEXHOUND · JEDI · DISCOVER -
Metadata-Driven Drone Strikes SIDtoday [pdf]
These documents describe the NSA and CIA’s use of geolocation technology, particularly via UAV-mounted systems like GILGAMESH and VICTORYDANCE, to track mobile devices for targeted drone strikes, including operations that killed U.S. citizen Anwar Nasser Aulaqi. These programs rely heavily on signals intelligence rather than human confirmation, raising concerns about reliability, civilian casualties, and the accuracy of targeting. See also: SIDtoday/documents/2005/2005-01-18_SIDToday_-_New_Tactical_Collection_System_Joins_the_War_on_Terroris
-
Microsoft releases new service, affects FAA 702 collection [pdf]
An SSO item on Microsoft's new outlook.com service encrypting web chat from 31 July 2012 and cutting off FAA 702 collection, and on the surveillance solution Microsoft built with the FBI, which went live on 12 December 2012 and needed no change to UTT tasking.
-
Mobile Apps Checkpoint Meeting Archives [pdf]
This GCHQ document tracks project checkpoints from December 2009 to July 2010, focusing on the rollout and operationalization of mobile apps, TERRAIN system upgrades, GTP/GRX access, and converged event processing. Key themes include coordinating multi-team dependencies, addressing technical gaps in handset and app data characterization, and ensuring timely delivery of milestones like MIP-1.
Programs: TERRAIN · PRESTON · XKEYSCORE · BEGAL · TAMING PASTRIES · MILKWHITE · MVR · SOCIAL ANTHROPOID · INTEGER SPIN · MUTANT BROTH · GEO FUSION · MARBLED GEKO · BLACKHOLE · ACTOR ACTION · TRAFFICMASTER · HARD ASSOC · MIRTF · HEARTBEAT · SILVER LINING · GREENHEART · EREPO · MAGLITE · POKERFACE · BOSTROM · MIDDLESEX GREEN · ENCHANTERSS · HAUSTORIUM · SALAMANCA · BROADOAK · MONKEY PUZZLE · TACHO · EREPO GAMMA · NINJA · PEBBLE BED · GOLDEN EYE · STRAPROC · STARPROC · LOOKING GLASS · SORCERER · SOCIAL ANIMAL · GTE · NGE · PPF · IIB · UDAQ · MES · TERRAINS · CCDF · SINO · GDR · OSDS · LECKWITH -
Moving Data Through Disconnected Networks - Delay-Tolerant Networking and the IC [pdf]
This June 2012 NSA Laboratory for Telecommunications Sciences presentation details Delay-Tolerant Networking (DTN) applications for surveillance operations, including covert communications in denied areas, data exfiltration from isolated networks, unwitting data mules, and integration with TAO's CHIMNEYPOOL implant framework. The document reveals R4 development of FUZZYLINT, an ultra-lightweight DTN implementation designed to enable multi-hop exfiltration from implants without requiring direct physical access.
People: Vahdat, Amin · Becker, David · Juang, Philo · Oki, Hidekazu · Wang, Yong · Martonosi, Margaret · Peh, Li-Shiuan · Rubenstein, Daniel · Grossglauser, Matthias · Tse, David N. C. · Fall, Kevin · Shah, Rahul C. · Roy, Sumit · Jain, Sushant · Brunette, Waylon · Lindgren, Anders · Doria, Avri · Schelen, Olov · Small, Tara · Haas, Zygmunt J. · Zhao, Wenrui · Ammar, Mostafa · Zegura, Ellen · Ginzboorg, Philip · Kärkkäinen, Teemu · Nagata, Akira · Lenders, Vincent · Legendre, Franck · May, Martin · Karlsson, Gunnar · Du, Bowei · Demmer, Michael · Brewer, Eric · Ott, Jörg · Pitkänen, Mikko Juhani · Han, Bo · Hui, Pan -
Net Defense from Encrypted Communications [pdf]
A NSA Technology Directorate briefing from February 2012 describing BLUESNORT — a capability that repurposes GALLANTWAVE's SSL/TLS decryption pipeline for network defence, re-injecting decrypted traffic into TURMOIL Stage 1 Prime where BLUESNORT detects malware and other malicious activity — representing description of NSA using its own bulk decryption infrastructure for cyber defence as well as intelligence collection.
-
New FAA702 Certification in the Works - Cyber Threat [pdf]
A 23 March 2012 SSO article on a draft FAA 702 certification for cyber threats. It would let analysts task selectors tied to malicious cyber activity without attributing them to a foreign government or terrorist group, and would codify tasking of IP addresses and code strings through PRISM and the upstream accesses.
-
NSA June 2012 SSO Weekly Brief Excerpt [pdf]
This NSA Special Source Operations (SSO) briefing from June 2012 describes SPINNERET, a surveillance program that became the second-largest source of phone calling records and "tips" feeding into SHELLTRUMPET, a system that obscures the origin of collected metadata before forwarding it to NSA's Real-Time Regional Gateway (RT-RG) in Texas. The document indicates SHELLTRUMPET "obfuscates the source designators" and filters metadata to only include call events within NSA-Texas's area of responsibility.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
NSA Spied On Porn Habits As Part Of Plan To Discredit 'Radicalizers' [pdf]
Top-secret document reveals how NSA has been gathering records of online sexual activity and evidence of visits to pornographic websites as part of a proposed plan to harm the reputations of those whom the agency believes are radicalizing others through incendiary speeches
-
Number 9... Number 9... SIDtoday [pdf]
SIDtoday is celebrating its ninth anniversary, reflecting on its history and offering a playful "top 9 reasons to read SIDtoday," ranging from staying informed at staff meetings to discovering secret SIGINT handshakes. The publication has played an essential role in keeping the community connected with its regular updates. The document is notable for revealing that in the first nine years of SIDtoday’s life, more than 4,500 stories were posted on the SIDtoday website.
Marking: UNCLASSIFIED -
NWP2 NSA [pdf]
The July 2012 issue of the Yakima Research Station's internal newsletter, covering the station's upcoming 40th anniversary celebrations, its origins under the ECHELON programme for INTELSAT collection during the Cold War, and a Norwegian partner enablement operation, alongside routine staff and community content.
Programs: ECHELON -
One Fish, Two Fish, My Fish, Your Fish! SIDtoday [pdf]
This SIDtoday document discusses the challenges faced by the U.S. and its partners in monitoring foreign fishing fleets, particularly Chinese vessels, in exclusive economic zones (EEZ). It highlights issues with the Automatic Identification System (AIS) used by fishing boats, where Chinese vessels were broadcasting inaccurate positional data, either due to technical errors or intentional misuse of the system, complicating monitoring efforts and posing risks to maritime safety and security.
Programs: SCQAWK -
Op MULLENIZE and beyond - Staining machines 10/10/12 [pdf]
This 2012 report from the NSA's British counterpart, the GCHQ, describes a method of "staining" electronic traffic to distinguish otherwise anonymous users. It is used to unmask Tor users and devices on networks in which many computers share the same Internet address. The method relies on planting code in a web browser to change the "user agent," which is the way the browser identifies itself on the web. In a two month period, the report says, GCHQ managed to implant about 200 computers with uniquely identifying stains.
-
OTR encrypted messages can't be decrypted by the NSA [pdf]
Three intercepted chat sessions from 16 March 2012 collected under PRISM, showing a target switching mid-conversation from unencrypted to OTR-encrypted messaging — with NSA able to collect the session metadata and unencrypted portions but unable to decrypt the OTR messages, each annotated "No decrypt available for this OTR encrypted message."
Programs: PRISM