Dissemination control: REL TO USA, AUS, CAN, GBR, NZL 103 documents
Search documents matching “REL TO USA, AUS, CAN, GBR, NZL” →Handling controls assessed for each document, as component values. If a document contains multiple disseminations, the most restrictive is used here.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
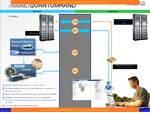
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
Responsibility 3B: Implications of Technology & Geopolitical Trends [pdf]
This document outlines a classified NSA report on geopolitical trends from 2011 to 2016, highlighting key issues like global energy security, military modernization in China and Russia, cyber threats, and the rise of extremism. Notably, climate change is ranked 31st out of 34 priorities, reflecting its relatively low importance compared to issues.
-
Roger Dingledine at NSA NOV 2007 [pdf]
An NSA internal wiki page summarising a talk given at NSA on 1 November 2007 by Roger Dingledine, one of Tor's inventors, covering who Tor's users are, anonymity system design concepts, and Tor's weaknesses.
People: Dingledine, Roger -
RWC Updater Readme [pdf]
A technical NSA manual describing the Royale with Cheese (RwC) Updater — the distribution system used to push XKEYSCORE dictionary updates, fingerprints, VoIP rules, IP geolocation tables and other configuration packages across the global hierarchical network of XKEYSCORE nodes on an hourly basis.
-
SCS - Embassies and Consulates [pdf]
TOP SECRET Special Collection Service (SCS) documents about covert CIA/NSA spying sites operated from diplomatic facilities worldwide.
-
SCS SITES [pdf]
This 2004 NSA document maps the global footprint of the Special Collection Service (SCS), the joint NSA–CIA program that conducts covert signals-intelligence collection from U.S. embassies and consulates abroad under diplomatic cover, prized for intercepting "leadership communications" from within national capitals. Effective January 2002, it lists roughly 65 active, survey, and future SCS sites worldwide.
-
Sensitive Metadata Analytic Collaboration (SMAC) - Concept of Operations, October 2006 [pdf]
This document outlines the Sensitive Metadata Analytic Collaboration (SMAC) initiative, a system developed by the Five Eyes intelligence agencies to facilitate the sharing and analysis of sensitive metadata to support SIGINT (signals intelligence) missions. While the concept aims to improve collaboration and data sharing, its success is hindered by ongoing policy, legal, and technical barriers, as well as concerns about trust and participation among the agencies involved. The document suggests a complex, somewhat opaque process of metadata sharing that risks undermining privacy protections.
Programs: SMAC -
-
SIGINT Strategy 2012-2016 [pdf]
This five-page document, written in 2012, is essentially a National Security Agency mission statement with broad goals, including a desire to push for changes in the law to provide the agency with expanded surveillance powers. It was written before Edward J. Snowden’s leaks, so it provides a glimpse at the thinking of agency officials before Mr. Snowden upset their political calculus.
People: Lynn, William J.“A Strategy for Surveillance Powers” - The New York Times ↗ (2013-11-22) · Risen, James · Poitras, Laura -
SKYNET: Applying Advanced Cloud-based Behavior Analytics [pdf]
A classified NSA SIGINT Development presentation detailing SKYNET, a cloud-based machine learning system that analyzes bulk Pakistani call data records to identify suspected couriers and terrorists through automated travel pattern analysis, behavioral profiling, and social network mapping — with the goal of supporting targeting operations against groups including the Haqqani Network.
Programs: SKYNET · DEMONSPIT · TMAC · FASTSCOPE · TUSKATTIRE · GMHALO · GMPLACE · BULLDOZER · MDR2 · CINEPLEX · JEMA · FASCIA · CLOUD · DPS · SEDB · SMARTTRACKER · SORTINGLEAD · ASSOCIATION · BANYAN · RT-RG · SNOWHAZE · MASTERSHAKE · MAINWAY -
Slides Describe Mission Involving Huawei [pdf]
This document details an NSA-led strategic initiative to target Huawei due to its dominance in global telecommunications infrastructure. The operation (codenamed "Shotgiant") aims to exploit Huawei hardware to maintain access to target communications while investigating the company’s potential role in facilitating People’s Republic of China (PRC) signals intelligence and supply chain subversion.
-
Special Collection Service - Pacific SIGDEV Conference March 2011 [pdf]
This document is a TOP SECRET briefing describing the Special Collection Service (SCS)—its organizational structure, global posture and strategic partnerships—and how SCS leverages advanced SIGINT and cyber capabilities (microwave, cellular, satellite, VPN/Internet exploitation, tools like INTERQUAKE/Einstein/Castanet/Birdwatcher) from embassy/PoP sites to collect, analyze and support intelligence and covert operations. It also outlines SCS modernization goals (unified IT core, cloud/virtualization, expanded cyber presence), operational authorities and mission advantages for enabling both SIGINT and HUMINT activities. See also Spiegel's 2013 reporting based on the same presentation (back then they only published two slides from this presentation): https://www.spiegel.de/international/germany/cover-story-how-nsa-spied-on-merkel-cell-phone-from-berlin-embassy-a-930205.html
-
Special Collection Service – Pacific SIGDEV Conference March 2011 – Supply Chain Excepts [pdf]
This top-secret 2011 NSA presentation outlines how the Special Collection Service—a joint NSA–CIA program operating from U.S. embassies—leverages its global network of “points of presence” to conduct human-enabled SIGINT and cyber operations directly inside “adversary space.” Framed as a “home field advantage,” it portrays U.S. diplomatic sites as launchpads for infiltration, surveillance, and even supply chain attacks, blurring the line between diplomacy and digital espionage.
-
SPIN 15 VPN Story [pdf]
A TOP SECRET planning document describing two parallel workstreams in SPIN 15: the deployment of VPN decryption capabilities to SMOKYSINK (US-3237), a unilateral NSA RAMPART-T cable tap site operating without a third-party partner, and a risk reduction benchmarking activity measuring TURMOIL's VPN and SSL exploitation performance against the Net-Centric Capabilities (NCC) programme's Key Performance Parameters — which targeted 100,000 VPN decrypt requests per hour by the end of fiscal year 2011, and 10 million SSL sessions per day by the end of fiscal year 2012.
Programs: TURMOIL · SMOKYSINK · ISLANDHIDEAWAY · PICARESQUE · KEYCARD · XKEYSCORE · PRESSUREWAVE · ISLANDTRANSPORT · PIQBLADE -
Statistics Configuration Read Me [pdf]
XKEYSCORE administrator readme describing the configuration of statistics collection across the XKEYSCORE distributed infrastructure, including how collection nodes report operational metrics back to a central statistics server via MAILORDER, and defining the hierarchical terminology of the XKEYSCORE deployment architecture.
-
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.