Tag: Palantir 5 documents
Search documents matching “Palantir” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
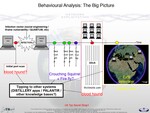
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
GCHQ VisWeek 2008 Conference Report [pdf]
This GCHQ document summarizes key findings from the VisWeek 2008 visualization conference in Ohio, highlighting techniques and tools relevant to SIGINT analysis including collaborative analysis capabilities, graph visualization methods, and the Palantir Government platform. The report recommends incorporating features like analyst notebooks for tracking investigations, collaborative workspaces for multiple analysts, and various graph layout algorithms into GCHQ's MONTE VISTA visualization system.
Programs: MONTE VISTA · MAMBA · CHARTBREAKER · PIGS EAR · KNIME · RAPTOR · BROAD OAK · HAUSTORIUM · SALAMANCA · IIB · INFOVIS · PALANTIR -
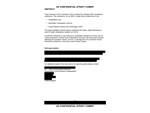
LOVELY HORSE – GCHQ Wiki Overview [pdf]
This February 2012 GCWiki page describes LOVELY HORSE, a GCHQ initiative to collect, index, and distribute open-source intelligence from cybersecurity blogs and Twitter accounts to analysts on classified networks, utilizing JTRIG's BIRDSTRIKE architecture to scrape content from approximately 60 sources including security researchers, hacktivist groups like Anonymous and LulzSec, and cybersecurity companies, with legal approval from MP-LEG (Mission Policy-Legal).
Programs: LOVELYHORSE · HAPPYTRIGGER · BIRDSEED · JTRIG · BIRDSTRIKE · MERAPEAK · LEXHOUND · JEDI · DISCOVER -
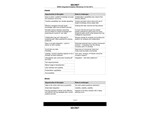
SDSG Integrated Analytics Workshop (14 Oct 2011) [pdf]
This document is a summary of a workshop held by the SIGINT Development Steering Group (SDSG) on October 14, 2011, evaluating and comparing the strengths, weaknesses, and potential use of advanced analytics tools, specifically Palantir and Mamba, for intelligence analysis. It discusses the tools' capabilities in data integration, collaboration, and visualization, along with concerns about security, usability, and the risks of relying on commercial software.
Marking: SECRET -
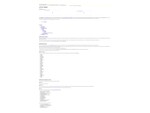
XKEYSCORE Helper Notes [pdf]
This GCHQ document describes new features in the XKEYSCORE Palantir helper tool, including summary/histogram import capabilities that reduce large datasets by aggregating connection data rather than creating individual events for each entry, and data sourcing features that track which XKEYSCORE queries imported specific data into Palantir. The document provides step-by-step screenshots showing how analysts can histogram network traffic by source IP, destination IP, and ports, then import aggregated results showing metadata like total session sizes and connection counts.
Programs: XKEYSCORE