Genre: slides 272 documents
Search documents matching “slides” →What kind of document it is: slides, report, wiki, manual, guide, newsletter.
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Content Acquisition Optimization PowerPoint Slides [pdf]
An NSA presentation on content acquisition optimisation — describing how incidental bulk collection from Yahoo Webmessenger, email address books, buddy lists and webmail inboxes was generating massive unintended collection volumes.
-
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO -
Slides Describe Mission Involving Huawei [pdf]
This document details an NSA-led strategic initiative to target Huawei due to its dominance in global telecommunications infrastructure. The operation (codenamed "Shotgiant") aims to exploit Huawei hardware to maintain access to target communications while investigating the company’s potential role in facilitating People’s Republic of China (PRC) signals intelligence and supply chain subversion.
-
3G: impact and update - SDF Nov 09 [pdf]
This 2009 top-secret presentation from Australia’s Defence Signals Directorate (DSD) detailing 3G mobile network rollouts in Southeast Asia and identifying Indonesian President Susilo Bambang Yudhoyono, his wife, and senior officials as surveillance targets. It includes handset information, call data records, intercepted call attempts, and outlines plans for continued interception of Indonesian leadership communications.
-
A potential technique to deanonymise users of the TOR network [pdf]
A TOP SECRET GCHQ research presentation describing a traffic correlation attack against Tor — using cumulative packet counts observed simultaneously at a controlled exit node and at SIGINT collection points near a target's guard node to deanonymise Tor users without breaking the encryption — with GTE and JTRIG having adapted owned exit nodes to collect the required data for live deployment.
-
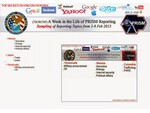
A Week in the Life of PRISM Reporting [pdf]
A slide from the "PRISM/US-984XN Overview" deck, showing different reporting topics from one week in the early February 2013.
“EUA espionaram milhões de e-mails e ligações de brasileiros” - O Globo ↗ (2013-07-12) · “NSA targets Indian politics, space & n-programmes” - The Hindu ↗ (2013-09-24) · Greenwald, Glenn · Kaz, Roberto · Casado, José · Saxena, Shobhan -
Access to the future [pdf]
The conclusion slide excerpt of a GCHQ presentation on TEMPORA, telling analysts they are in a "privileged" and "enviable" position with ready access to a great deal of sensitive data, and to "have fun and make the most of it".
Programs: TEMPORA -
Access: Vision 2013 [pdf]
This July 2010 GCHQ strategic document outlines the agency's vision for 2013 to create "the world's biggest SIGINT engine" with access to 800 10-gigabit connections (up from existing capacity), expanding overseas operations to 60% while reducing UK-based to 40%, and developing new capabilities including computer network exploitation (CNE), exfiltration, beaconry, geolocation, and collection of "Internet Pocket Litter" like cookies and browsing data. The strategy emphasizes "scale and pace," "balance," and "agility" while claiming to operate within legal frameworks of "necessity, proportionality and authorisation," and highlights partnerships with second and third parties to access "intractable and hard targets."
Marking: SECRET -
Advanced HTTP Activity Analysis [pdf]
This NSA training document from 2009 teaches intelligence analysts how to analyze HTTP internet traffic and exploit it using the XKEYSCORE surveillance system to monitor and identify internet users globally.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Afghanistan Coalition Dissemination Brief to Senior Leadership Forum [pdf]
This document ooutlines the structure, goals, and challenges of multinational signals intelligence (SIGINT) collaboration in Afghanistan as of 2009. It reveals how the U.S. and its intelligence-sharing allies (notably the 5 Eyes, 9 Eyes, and 14 Eyes) coordinated SIGINT collection, decryption, analysis, and dissemination across NATO and coalition forces.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT -
Analyzing Mobile/Cellular DNI in XKEYSCORE, May 2009 [pdf]
The XKEYSCORE document explains how the agency analyzes mobile/cellular device internet usage by collecting and processing both converged DNI/DNR data within cellular networks and traditional internet traffic, using various tools and indicators to identify mobile users even when their device type isn't immediately evident. The document demonstrates how the system can track mobile internet activity across applications like Yahoo Mail and identifies devices through various technical "hints" including MSISDN codes, browser fingerprints, and user agent strings.
-
AND THEY SAID TO THE TITANS: « WATCH OUT OLYMPIANS IN THE HOUSE! » [pdf]
This Top Secret CSEC “Olympia” document details a Canadian intelligence program that analyzed and tracked the Brazilian Ministry of Mines and Energy’s telecommunications, mapping IPs, servers, proxies, and mobile devices while automating data collection and network analysis to develop actionable intelligence. It outlines tools, workflows, and contacts used for surveillance, though the presentation does not explain the specific purpose of the operation.
Programs: OLYMPIA · QUOVA · PROMETHEUS · PEITHO · SLINGSHOT · LEVITATE · STRATOS · EVILOLIVE · GCHQ Geofusion · ATLAS · HYPERION · ATHENA · DANAUS · TIDALSURGE · BLACKPEARL · MARINA · STARSEARCH · PEPPERBOX · TRITON · PACKAGEDGOODS · ARK · TOYGRIPPE · FRIARTUCK · MASTERSHAKE · COEUS · STALKER · MAINWAY · FASCIA · SEDB · OCTSKYWARD · FASTBAT · TWINSERPENT · EONBLUE · DISHFIRE · GNDB“Read a CSEC document that was first acquired by Edward Snowden” - The Globe and Mail ↗ (2013-11-30) · “Ministério de Minas e Energia está na mira de espiões americanos e canadenses” - O Globo ↗ (2013-10-06) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Freeze, Colin · Bridi, Sônia · Greenwald, Glenn -
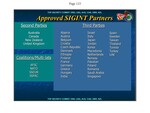
Approved SIGINT Partners [pdf]
A Foreign Affairs Directorate slide listing NSA's approved SIGINT partners: the four Second Parties, 33 Third Parties from Algeria to the United Arab Emirates, and the coalitions AFSC, NATO, SSEUR and SSPAC. This is document is from Fiscal Year 2013 "Foreign Partner Review."
-
AURORAGOLD Working Group [pdf]
The "AURORAGOLD Working Group" briefing is a highly classified SIGINT development presentation from June 2012 that outlines the NSA's progress in mapping the global mobile landscape (GSM/UMTS/LTE). It focuses on the project's "value proposition": providing an exhaustive database of network identifiers and technical configurations—often obtained by intercepting internal company documents—to support tactical military operations and long-term surveillance forecasting.
Programs: AURORAGOLD · UTT · XKEYSCORE · CADENCE · JUBILEECORONA · RONIN · NKB · GLOBALTIPPER · PINWALE -
AURORAGOLD – Project Overview [pdf]
A technical briefing document outlining an NSA SIGINT initiative designed to map, monitor, and forecast the evolution of global mobile networks. It details the project's infrastructure, which aggregates both unclassified commercial data and classified intelligence intercepted from international roaming agreements to identify technical trends and exploitation opportunities.
-
AURORAGOLD – Target Technology Trends Center support to WPMO [pdf]
This briefing details the technical architecture and data pipeline used to process global cellular network information. It specifically highlights the synergy between data gathering on GSM/UMTS networks and the implementation of "Auto-Minimization" to ensure the resulting SIGINT reporting complies with NSA legal and policy requirements.
-
Automated NOC detection [pdf]
This slide deck lays out how GCHQ and Canada’s CSEC systematically identified and penetrated Network Operations Centers—most notably Belgacom—by automating NOC discovery and weaponizing that mapping for QUANTUM INSERT attacks. It reads like a blueprint for turning router configs, metadata, and bulk scans into cookie-based targeting against telecom engineers inside core networks.
Programs: SURGE · NOCTURNALSURGE · RT · NACSHACK · CHAINGUARD · TIDALSURGE · GLOBALSURGE · PENTAHO · OLYMPIA · HYPERION · TERMINALSURGE · HACIENDA · QUANTUMINSERT · MUTANTBROTH · OPSOCIALIST · SAMUEL PEPYS · GEOFUSION · FIVEALIVE · NRTA · RADIUS“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS