Tag: man-on-the-side 11 documents
Search documents matching “man-on-the-side” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
Industrial-Scale Exploitation [pdf]
This top-secret NSA document details the operational philosophy behind the TURBINE system's transition to "industrial-scale exploitation." By integrating with both active and passive sensors, TURBINE automates the delivery of malware and the maintenance of network implants, specifically targeting routers and server-side code execution.
-
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
QUANTUMHAND [pdf]
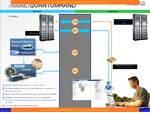
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
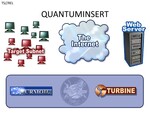
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
SSO news excerpts [pdf]
These SSO news exceprts describe the successful deployment of QUANTUMTHEORY and QUANTUMINSERT capabilities by the NSA’s Tailored Access Operations (TAO) team, in collaboration with Special Source Operations (SSO), to exploit high-value targets, including key figures in the Haqqani network. Using a combination of signal case notations and real-time exploitation via QUANTUMHAND, TAO was able to implant malicious software on the target's computer, enabling further intelligence collection and exploitation.
Programs: QUANTUMTHEORY · QUANTUM · QUANTUMINSERT · FOXACID · DANCINGOASIS · FOXCONTACT · VALIDATOR · SARATOGA · TURMOIL · QUANTUMHAND · SSOPeople: Haqqani, Badruddin -
XKEYSCORE for Counter-CNE [pdf]
A TOP SECRET presentation from March 2011 describing how NSA uses XKeyscore for counter-CNE — detecting and exploiting foreign hacking operations — including ingesting NSA's own TAO implant data, hunting for foreign intrusion sets like DISGRUNTLEDDUCK, and a success story in which Menwith Hill used TAO-stolen Iranian implant encryption keys to decrypt and read keylogger data the Iranian Revolutionary Guard's hackers were stealing from their own victims.
Programs: XKEYSCORE · DISGRUNTLEDDUCK · GENESIS · DANDERSPRITZ · SIMBAR · DONUT · AMULETSTELLAR · TRANGRESSION · TRANSGRESSION