Tag: behavioral analysis 13 documents
Search documents matching “behavioral analysis” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
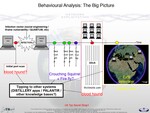
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
Broadcast/Internet Radio Exploitation and Analysis, 6th November 2009, GCHQ [pdf]
This GCHQ report analyzes 6.68 million internet radio listening events collected over three months in 2009, detailing global broadcasting patterns, user behaviors, and specifically examining Islamic radio stations and Pakistan-UK connections for potential radicalization intelligence, while recommending integration with bulk surveillance databases like KARMA POLICE for enhanced user profiling.
-
GCHQ Analytic Cloud Challenges [pdf]
The 2012 GCHQ Analytic Cloud document outlines a sophisticated data processing infrastructure handling approximately 50 billion daily events across multiple sites, utilizing QFD databases and HADOOP clusters for various analytic capabilities targeting intelligence gathering and analysis. It describes architectural components, challenges in scaling and enabling analysts to cope with data complexity, and proposes future technology options including consolidation approaches and new cloud architectures to enhance capabilities.
Programs: EVOLVEDMUTANTBROTH · MUTANTBROTH · HARDASSOC · HRMAP · KARMAPOLICE · SOCIALANTHROPOID · AUTOASSOC · GEOFUSION · MVR · TERRAIN · SALAMANCA · BLACKHOLE · SAMUELPEPYS · BROKER · VAIL · GUIDINGLIGHT · FIRSTCONTACT · CLOUDYCOBRA · RUMOURMILL · EVERYASSOC · EVERYPOLICE · EVERYCREATURE · EVERYEAD · EVERYCIPHER · GREYFOX · SILVERFOX · GOLDENAXE · TRIBALCARNEM · PUBLICANEMONE · EPICFAIL · STERLINGMOTH · FOGHORN · LOOKINGGLASS · FIREENGINE · NGGEO · ALPHACENTAURI · CLOUDBASE · ACCUMULO · ASEM · SEM · HAKIM · STREAMING · HBASE · LAUREL · SKINNYCLOUD · HARDY · GCHQCORE -
GHOSTMACHINE: Identifier Lead Triage with ECHOBASE [pdf]
This June 2012 presentation introduces ECHOBASE, an NSA analytic architecture designed to automate the triage of massive identifier lead lists (ranging from 50 to 10,000+ entries). By applying behavior-based analytics and "yes/no" behavioral queries against raw SIGINT, the system allows analysts to prioritize high-interest targets and discard irrelevant leads at scale.
Programs: GHOSTMACHINE · ECHOBASE · IDENTIFIERSCOREBOARD · FOREMAN · CONTRAOCTAVE · OCTAVE · UTT · WAVELEGAL · CASPORT · PSC -
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
ICTR Cloud Efforts [pdf]
A GCHQ presentation details how the agency developed cloud-based big data analytics to achieve "population scale" surveillance—processing trillions of internet events to build geographic and behavioral profiles on every online identifier worldwide, enabling discovery of unknown targets through pattern analysis rather than traditional keyword searches.
Programs: EVERYASSOC · PROBABILITYCLOUD · SILVERLINING · CULTWEAVE · KARMAPOLICE · EVERYPOLICE · AWKWARDTURTLE · GORDIANKNOT · SANDIA · BLOODHOUND · FIVEALIVE · NGE · MAPREDUCE -
Identity Intelligence: Image Is Everything [pdf]
This document is a highly classified NSA/CSS briefing detailing Identity Intelligence (i2), a comprehensive methodology for exploiting unique fragments of information to track, identify, and exploit targets of interest. It outlines an expansive architecture for data collection that spans Biometric/Biologic, Biographic, and Contextual/Behavioral domains, essentially mapping every conceivable data point of an individual's physical existence and digital/social footprint.
-
Introduction to Context Sensitive Scanning with X-KEYSCORE Fingerprints [pdf]
This May 2010 NSA training document introduces XKEYSCORE's context-sensitive scanning capabilities using "fingerprints"—customizable detection rules that allow analysts to surgically target specific types of Internet traffic without needing prior knowledge of email addresses or other strong selectors, using over 70 unique contexts to identify patterns in communications and behaviors.
-
Introduction to XKS Application IDs and Fingerprints [pdf]
This August 2009 NSA training document introduces XKEYSCORE's Application IDs (AppIDs) and Fingerprints system, explaining how metadata tags are automatically applied to intercepted sessions to identify and categorize different types of Internet traffic, applications, and behaviors, evolving through four generations from simple keyword matching to sophisticated code-based metadata extraction.
-
LEVITATION and the FFU Hypothesis [pdf]
This document describes LEVITATION, a top-secret Canadian Communications Security Establishment (CSE) project that monitors millions of daily file uploads and downloads from free file-sharing sites to identify potential extremist activity. It details the program’s data collection methods, analytical workflow, use of partner databases, and examples of successful discoveries related to terrorist materials and hostage videos.
-
Menwith initiatives maximizing our access [pdf]
11 p.This document details Menwith Hill Station’s initiatives to maximize and optimize SIGINT collection, processing, and exploitation, including large-scale monitoring of internet and communications traffic, metadata analysis, and cross-platform target tracking. It describes programs and techniques for surveying, processing, and exploiting signals, enabling analysts to identify, geolocate, and track targets across multiple networks and devices.
Programs: ASPHALT · BLACKTOP · TARMAC · GTE · INDEX · ROADBED · DARKQUEST · EVIL EYE · Spider · SHAREDVISION · QUEST · NOSEYPARKER · XKEYSCORE · GRANDPIANO · FOGHORN · BASSQUEST · APPARITION · MUTANT BROTH · KARMAPOLICE · SOCIALANIMAL · MEMORY HOLE · TURBULENCE · TELLURIAN · MAILORDER · AUTO ASSOC · SLR · BLACKHOLE · JTRIG · PPF · LECKWITH · SCEPTRE · CLOUDPeople: Alexander, Keith B.“GCHQ taps fibre-optic cables for secret access to world's communications” - The Guardian ↗ (2013-06-21) · “Inside Menwith Hill: The NSA’s British Base at the Heart of U.S. Targeted Killing” - The Intercept ↗ (2016-09-06) · MacAskill, Ewen · Borger, Julian · Hopkins, Nick · Davies, Nick · Ball, James · Gallagher, Ryan -
NSA's Counterterrorism (CT) Relationship with the German Federal Intelligence Service (BND) and the German Federal Office for the Protection of the Constitution (BfV) [pdf]
This April 2013 NSA talking points document prepares leadership for discussions with German intelligence services BND and BfV about counterterrorism cooperation, highlighting NSA's formal relationship with BfV approved March 20, 2013, planned provision of XKEYSCORE technology to enable German domestic surveillance, and warning that German requests for Skype interception capabilities and use of SIGINT in open court represent potential complications.
-
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark