NSA Supply Chain Attack From PMR 4-24-13
Open PDFDocument date: 2013-04-24
Pages: 2
Genre: slides
Banner: TOP SECRET//SI//NOFORN
Classification: TOP SECRET SI
Dissemination: NOFORN
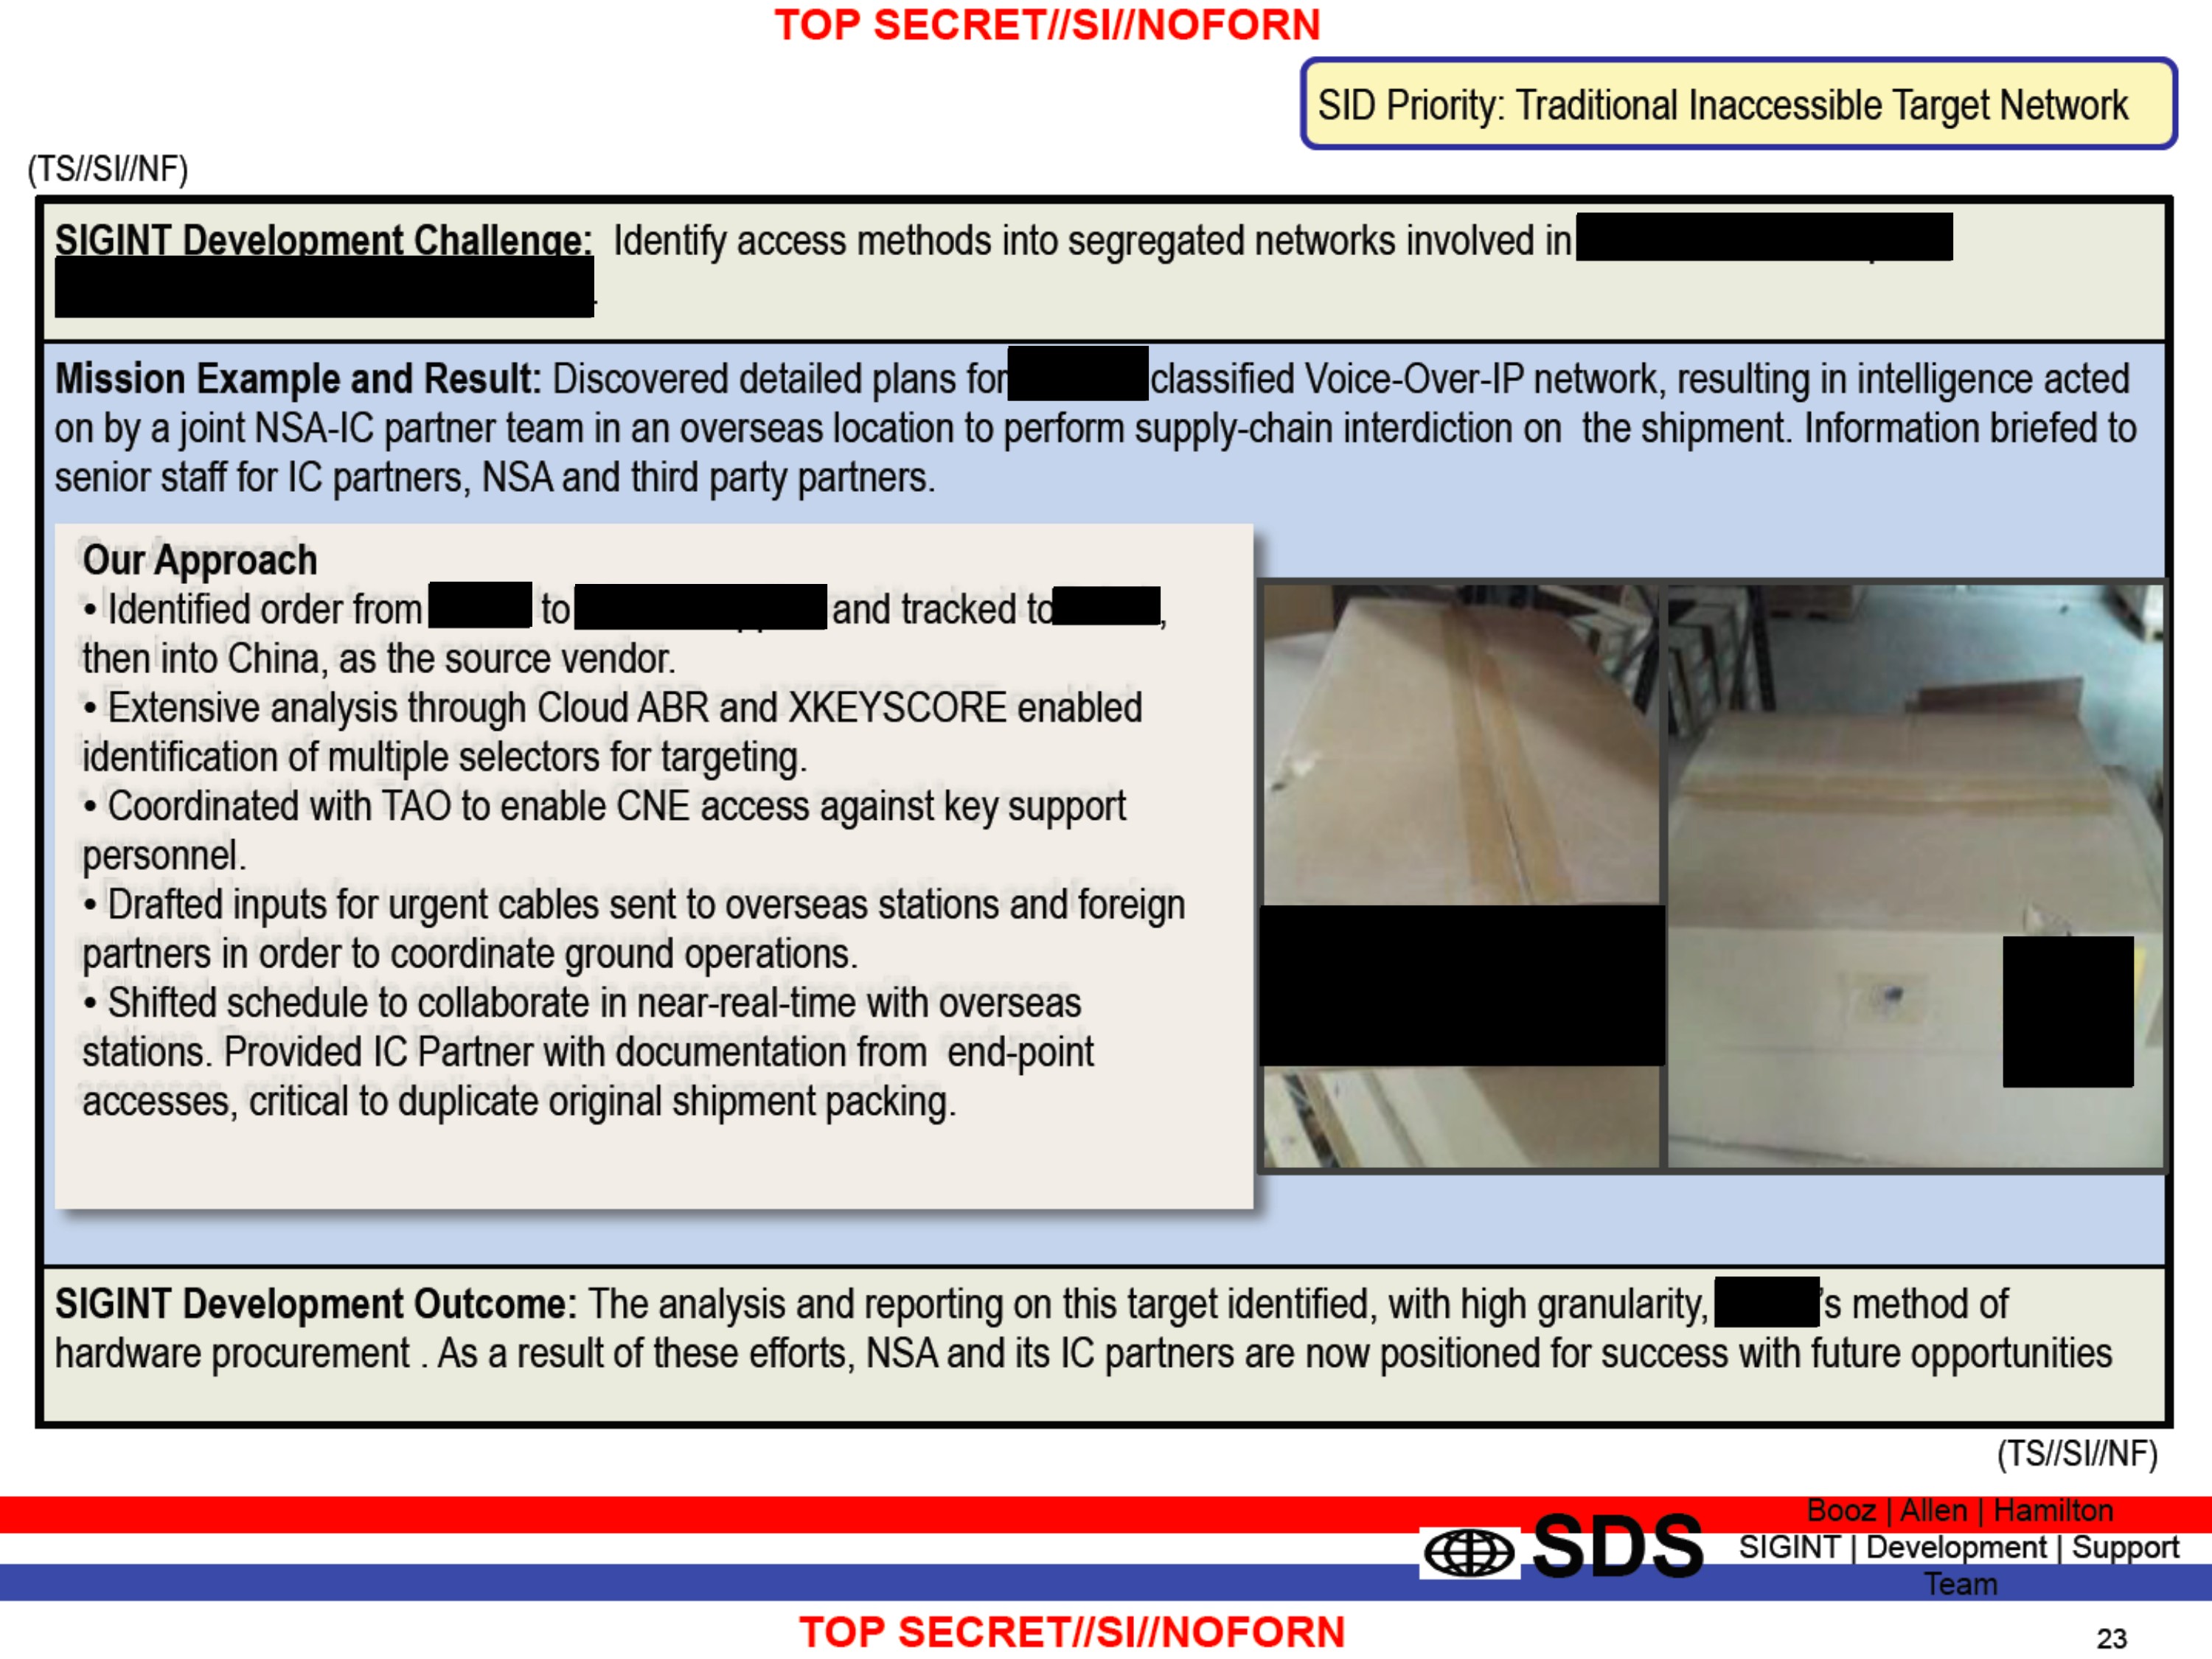
This document is a top-secret NSA report detailing a SIGINT development operation in which a classified Voice-over-IP network shipment was intercepted and subjected to a supply-chain interdiction, allowing NSA and its intelligence community partners to gain access to the hardware and intelligence. It describes the operational process, including tracking the shipment through China, coordinating with Tailored Access Operations (TAO), and using tools like XKEYSCORE to identify targeting selectors, ultimately enabling detailed surveillance and future operational opportunities.
My notes
TOP SECRET//SI//NOFORN
(U) SIGINT Development Support II Program Management Review
24 April 2013
NATIONAL SECURITY AGENCY
SIGDEV
SIGINT DEVELOPMENT
The overall classification of this brief is
TOP SECRET//COMINT//NOFORN
Derived From: NSA/CSSM 1-52
Dated: 20070108
Declassify On: 20291123
SDS
Booz | Allen | Hamilton
SIGINT | Development | Support
Team
1
TOP SECRET//SI//NOFORN
TOP SECRET//SI//NOFORN
SID Priority: Traditional Inaccessible Target Network
(TS//SI//NF)
SIGINT Development Challenge: Identify access methods into segregated networks involved in [REDACTED].
Mission Example and Result: Discovered detailed plans for [REDACTED] classified Voice-Over-IP network, resulting in intelligence acted on by a joint NSA-IC partner team in an overseas location to perform supply-chain interdiction on the shipment. Information briefed to senior staff for IC partners, NSA and third party partners.
Our Approach
- Identified order from [REDACTED] to [REDACTED] and tracked to [REDACTED], then into China, as the source vendor.
- Extensive analysis through Cloud ABR and XKEYSCORE enabled identification of multiple selectors for targeting.
- Coordinated with TAO to enable CNE access against key support personnel.
- Drafted inputs for urgent cables sent to overseas stations and foreign partners in order to coordinate ground operations.
- Shifted schedule to collaborate in near-real-time with overseas stations. Provided IC Partner with documentation from end-point accesses, critical to duplicate original shipment packing.
SIGINT Development Outcome: The analysis and reporting on this target identified, with high granularity, [REDACTED]'s method of hardware procurement. As a result of these efforts, NSA and its IC partners are now positioned for success with future opportunities
(TS//SI//NF)
SDS
Booz | Allen | Hamilton
SIGINT | Development | Support
Team
23
TOP SECRET//SI//NOFORN
Published in the Same Report
(8 documents)
-
DoD 2011 Strategy for Operating in Cyberspace – Supply Chain Excerpts [pdf]
The classified 2011 Department of Defense strategy warns that U.S. reliance on foreign manufacturing—especially from countries like China—creates major cybersecurity risks, including the potential insertion of malicious hardware or software into critical systems. It outlines a government-wide plan to mitigate these supply chain vulnerabilities through coordinated policies, risk management strategies, and collaboration with industry.
-
Intellipedia – Air Gapped Network Threats [pdf]
This document from an internal wiki for the U.S. intelligence community, surveys threats to so-called air-gapped systems, arguing that supply-chain compromises, physical implants (BIOS, KVMs, peripherals), infected removable media, and enabled wireless/emanations present realistic paths for adversaries to bridge isolated networks. It assesses likelihoods and attack vectors (including insider help and CDS/guard exploitation), highlights specific historic incidents (Agent.BTZ/MAKERSMARK), and recommends strict removable-media policies, TEMPEST countermeasures, and rigorous cross-domain guard protections to mitigate the risk.
People: Witte, Griff · Warren, Peter · Streeter, Michael · Watson, Paul · Louchard, Bjørn · Crawford, George · Rudge, David · Terrazas, Michael -
Intellipedia – BIOS Threats [pdf]
This from an internal wiki for the U.S. intelligence community, titled “BIOS Threats” details the use of malicious BIOS implants as a means of achieving persistent system compromise for cyber espionage and attack purposes. It discusses the history, technical challenges, detection limitations, and global development of BIOS-based malware by both state and non-state actors, including U.S. and Chinese cyber units.
-
Intellipedia – Supply Chain Cyber Threats [pdf]
This document on Supply Chain Cyber Threats, from an internal wiki for the U.S. intelligence community, outlines vulnerabilities in hardware and firmware components such as power supplies, NICs, RAID controllers, GPUs, and peripheral devices that could be exploited by adversaries through the supply chain. It details assessments from U.S. intelligence agencies (CIA, DIA, FBI, CYBERCOM) highlighting risks from foreign companies, insider threats, and malicious modifications that could compromise critical U.S. government and military systems.
Programs: A-SPACE -
National Intelligence Estimate 2009 Global Cyber Threat – Supply Chain Excerpts [pdf]
These Supply Chain Excerpts from the 2009 National Intelligence Estimate, assesses that the U.S. faces a growing cyber threat from state actors, particularly Russia and China, who have the capability and strategic intent to exploit or disrupt U.S. and allied information systems. It emphasizes vulnerabilities from supply chains, insider threats, and technology trends that favor offensive operations, while noting the difficulty of detecting and fully defending against these sophisticated cyber threats.
-
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Special Collection Service – Pacific SIGDEV Conference March 2011 – Supply Chain Excepts [pdf]
This top-secret 2011 NSA presentation outlines how the Special Collection Service—a joint NSA–CIA program operating from U.S. embassies—leverages its global network of “points of presence” to conduct human-enabled SIGINT and cyber operations directly inside “adversary space.” Framed as a “home field advantage,” it portrays U.S. diplomatic sites as launchpads for infiltration, surveillance, and even supply chain attacks, blurring the line between diplomacy and digital espionage.
-
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.




Related Documents
-
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
Using XKEYSCORE to Enable TAO [pdf]
A TOP SECRET training presentation from 2009, authored by a Booz Allen Hamilton contractor, teaching NSA analysts how to use XKeyscore to harvest the login credentials, router configurations, browser versions and server software details that the Tailored Access Operations hacking unit needs to break into foreign computer networks — with worked examples stealing Cisco router passwords, Iranian government webmail logins and jihadi web forum credentials directly from intercepted internet traffic.
-
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR