Notes for Dutch SIGINT/Cyber Analytic Exchange
Open PDFDocument date: 2013-02-14
Pages: 3
Genre: report
Banner: TOP SECRET//SI//REL TO USA, NLD
Classification: TOP SECRET SI
Dissemination: REL TO USA, NLD
This document provides top-secret notes between the NSA and the Dutch intelligence services (AIVD and MIVD). This document outlines a significant restructuring of the Dutch intelligence community, including the creation of a unified SIGINT and Cyber Division and a Single Point of Contact (SPOC) at AIVD headquarters in Zoetermeer. The briefing details the operational challenges of the newly formed National Cyber Security Center (NCSC), the development of the National Detection Network (NDN) for cyber sensors, and the shared technical interests between the two nations regarding malware detection, Tor (The Onion Router) exploitation, and the analysis of web forums via Computer Network Exploitation (CNE).
My notes
TOP SECRET//SI//REL TO USA, NLD
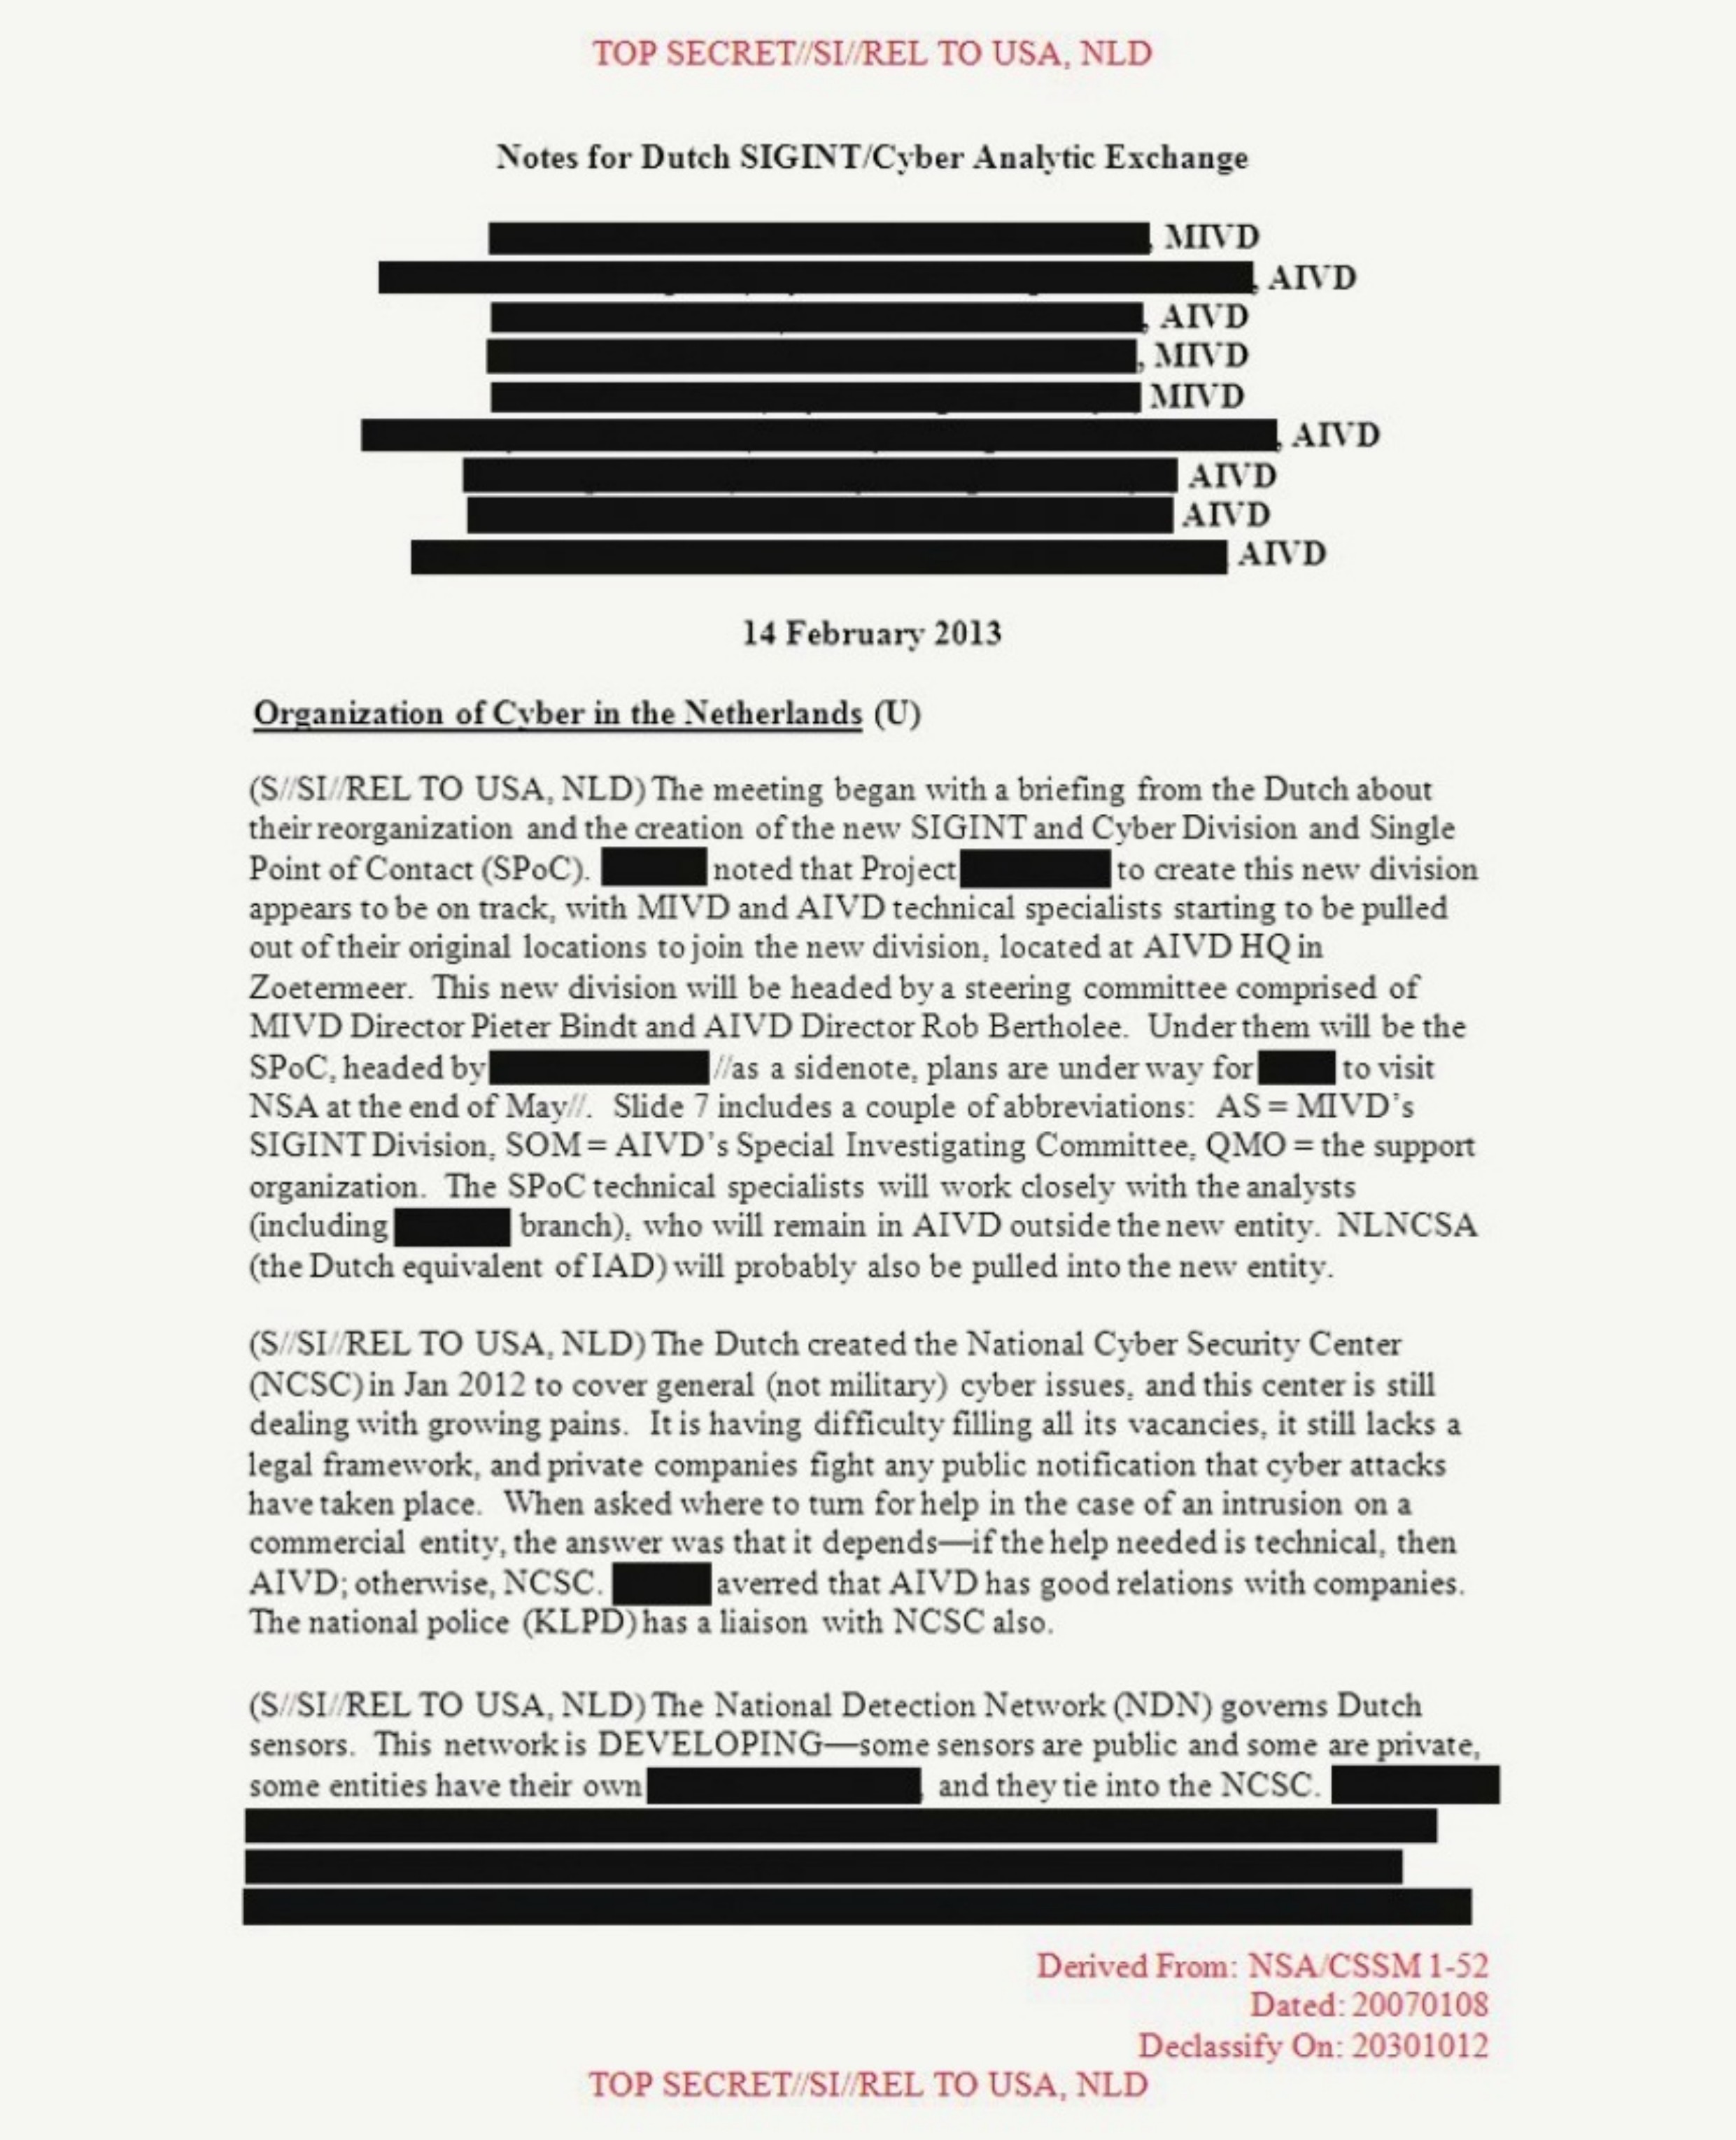
Notes for Dutch SIGINT/Cyber Analytic Exchange
[REDACTED] MIVD
[REDACTED] AIVD
[REDACTED] AIVD
[REDACTED] MIVD
[REDACTED] MIVD
[REDACTED] AIVD
[REDACTED] AIVD
[REDACTED] AIVD
[REDACTED] AIVD
14 February 2013
Organization of Cyber in the Netherlands (U)
(S//SI//REL TO USA, NLD) The meeting began with a briefing from the Dutch about their reorganization and the creation of the new SIGINT and Cyber Division and Single Point of Contact (SPOC). [REDACTED] noted that Project [REDACTED] to create this new division appears to be on track, with MIVD and AIVD technical specialists starting to be pulled out of their original locations to join the new division, located at AIVD HQ in Zoetermeer. This new division will be headed by a steering committee comprised of MIVD Director Pieter Bindt and AIVD Director Rob Bertholee. Under them will be the SPOC, headed by [REDACTED]. Was a sidenote, plans are under way for [REDACTED] to visit NSA at the end of May//. Slide 7 includes a couple of abbreviations: AS = MIVD's SIGINT Division, SOM = AIVD's Special Investigating Committee, QMO = the support
organization. The SPoC technical specialists will work closely with the analysts (including [REDACTED] branch), who will remain in AIVD outside the new entity. NLNCSA (the Dutch equivalent of IAD) will probably also be pulled into the new entity.
(S//SI//REL TO USA, NLD) The Dutch created the National Cyber Security Center (NCSC) in Jan 2012 to cover general (not military) cyber issues, and this center is still dealing with growing pains. It is having difficulty filling all its vacancies, it still lacks a legal framework, and private companies fight any public notification that cyber attacks have taken place. When asked where to turn for help in the case of an intrusion on a commercial entity, the answer was that it depends if the help needed is technical, then AIVD; otherwise, NCSC. [REDACTED] averred that AIVD has good relations with companies. The national police (KLPD) has a liaison with NCSC also.
(S//SI//REL TO USA, NLD) The National Detection Network (NDN) governs Dutch sensors. This network is DEVELOPING—some sensors are public and some are private, some entities have their own [REDACTED] and they tie into the NCSC. [REDACTED]
[REDACTED]
Derived From: NSA/CSSM1-52
Dated: 20070108
Declassify On: 20301012
TOP SECRET//SI//REL TO USA, NLD
TOP SECRET//SI//REL TO USA, NLD
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
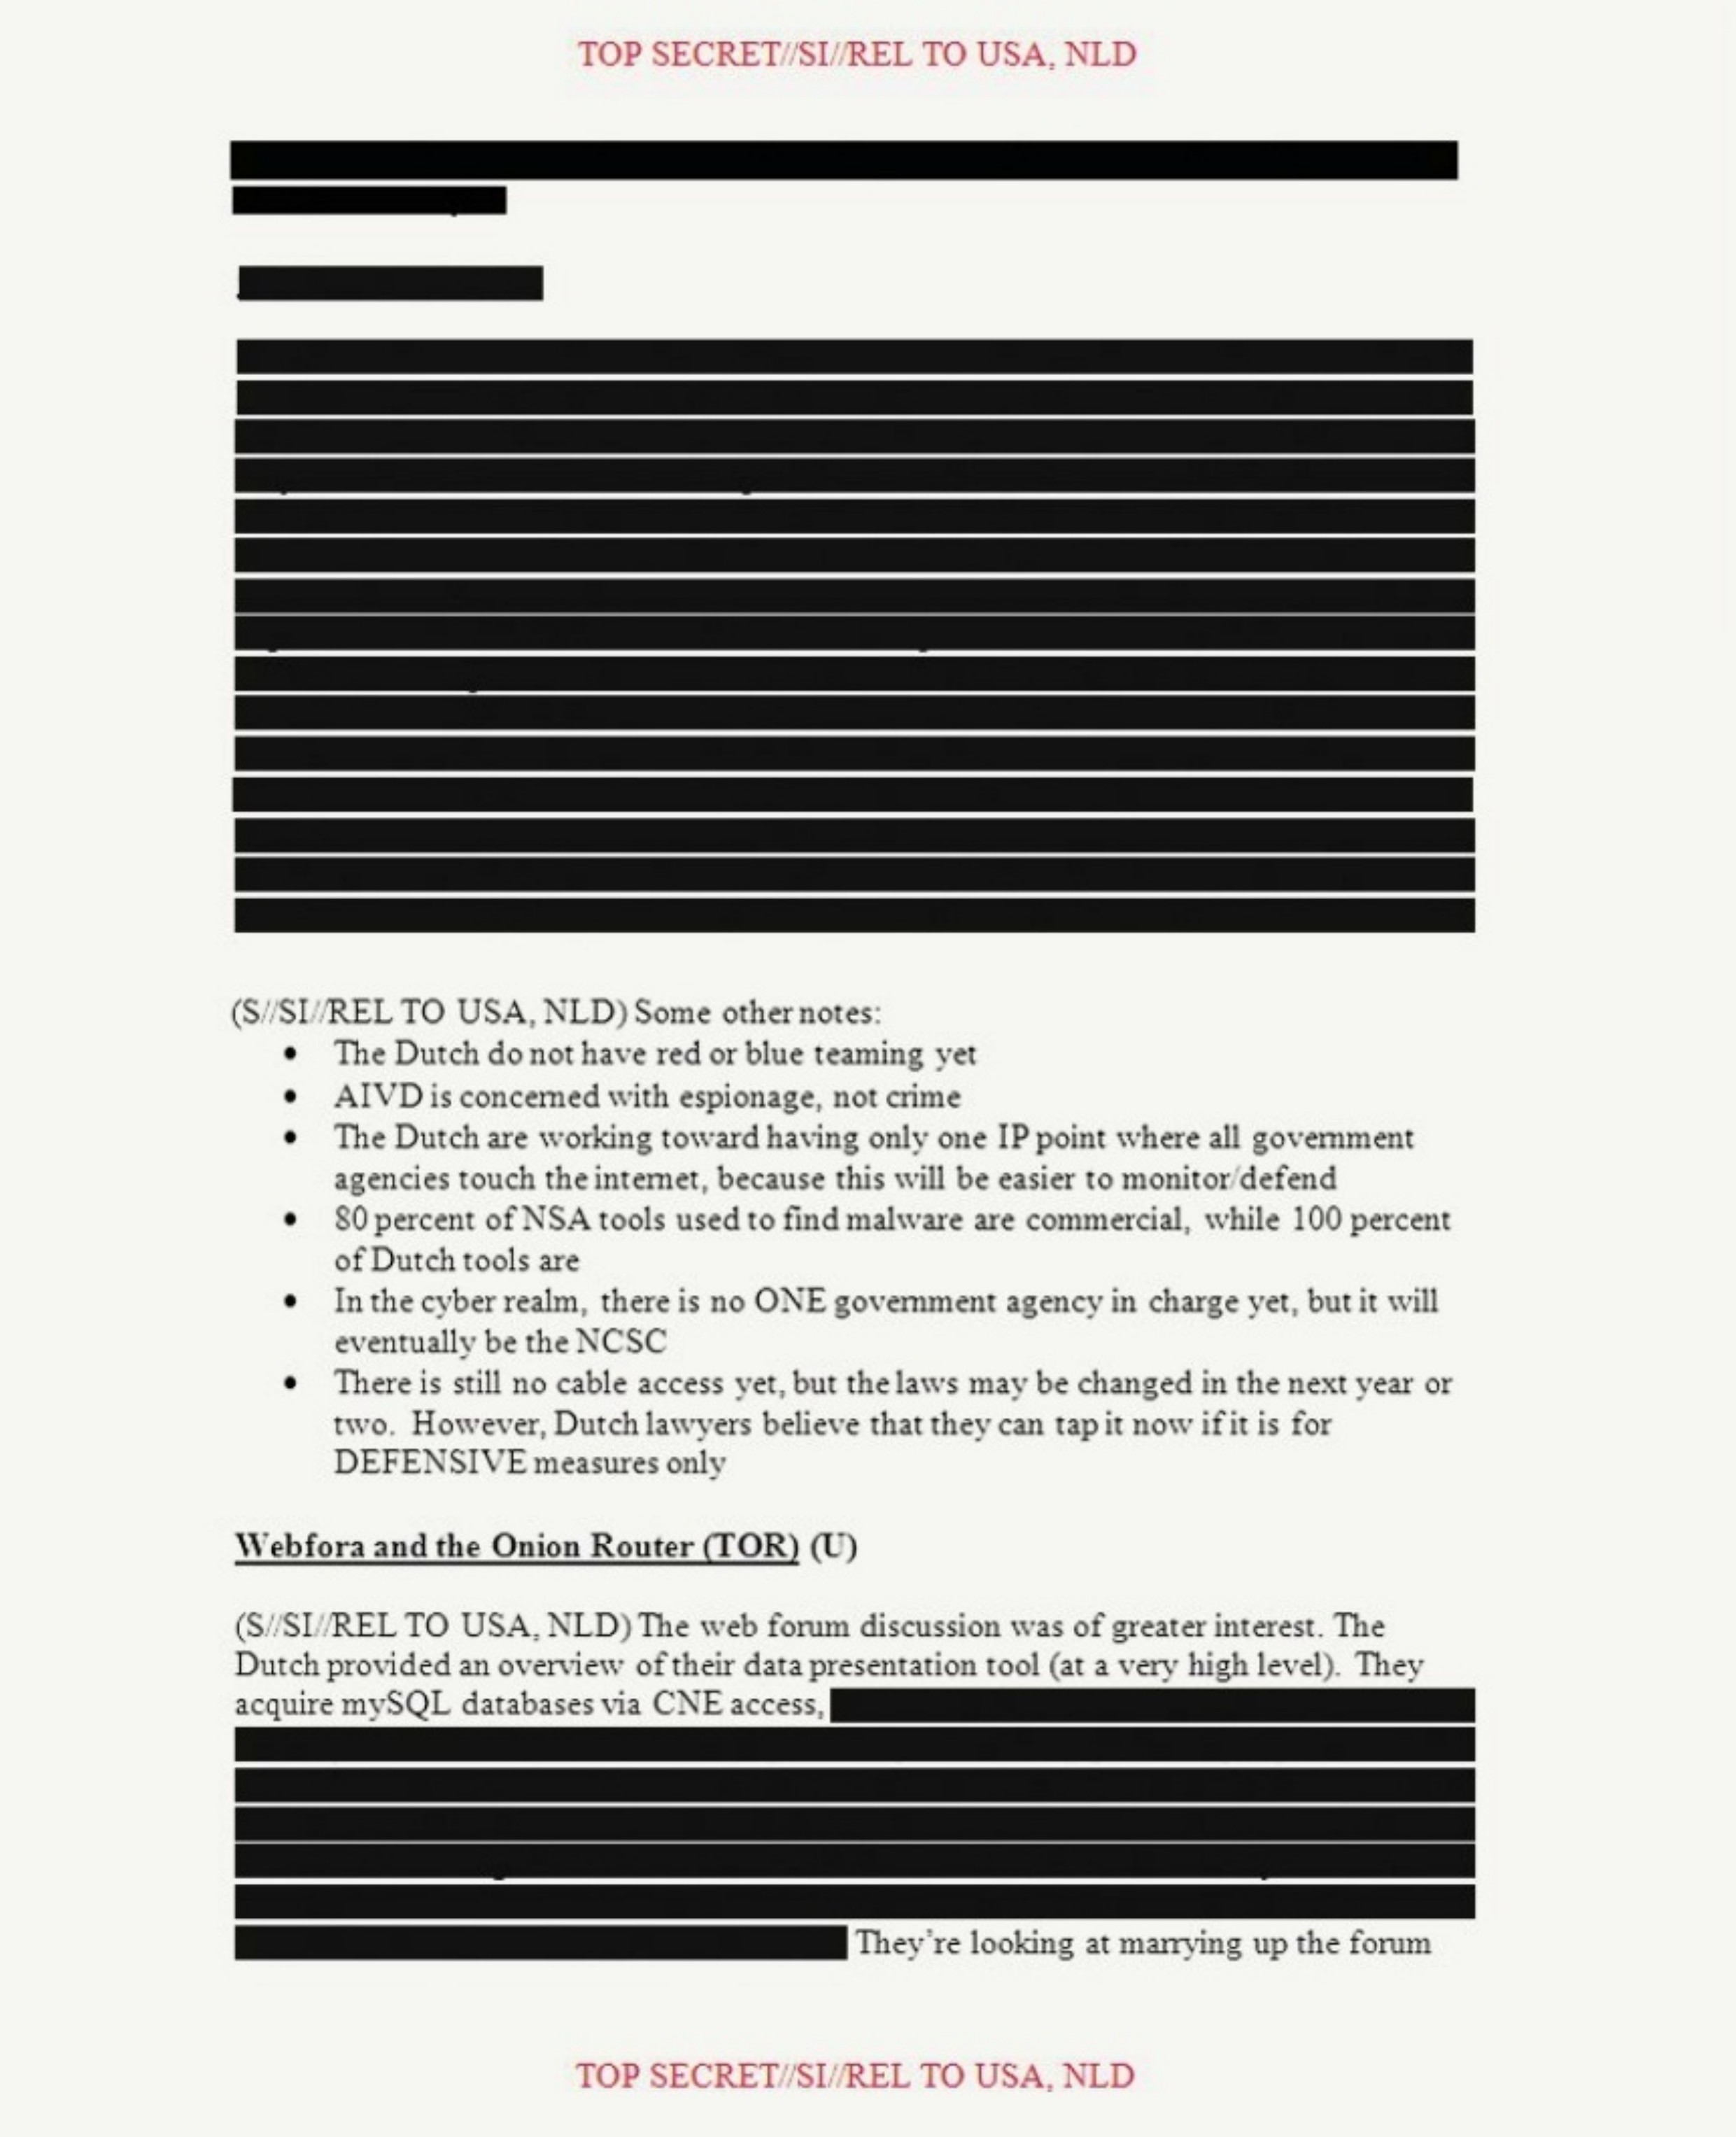
(S//SI//REL TO USA, NLD) Some other notes:
- The Dutch do not have red or blue teaming yet
- AIVD is concerned with espionage, not crime
- The Dutch are working toward having only one IP point where all government agencies touch the internet, because this will be easier to monitor/defend
- 80 percent of NSA tools used to find malware are commercial, while 100 percent of Dutch tools are
- In the cyber realm, there is no ONE government agency in charge yet, but it will eventually be the NCSC
- There is still no cable access yet, but the laws may be changed in the next year or two. However, Dutch lawyers believe that they can tap it now if it is for DEFENSIVE measures only
Webfora and the Onion Router (TOR) (U)
(S//SI//REL TO USA, NLD) The web forum discussion was of greater interest. The Dutch provided an overview of their data presentation tool (at a very high level). They acquire mySQL databases via CNE access, [REDACTED]
[REDACTED]
[REDACTED]
[REDACTED]
[REDACTED] They're looking at marrying up the forum
TOP SECRET//SI//REL TO USA, NLD
TOP SECRET//SI//REL TO USA, NLD
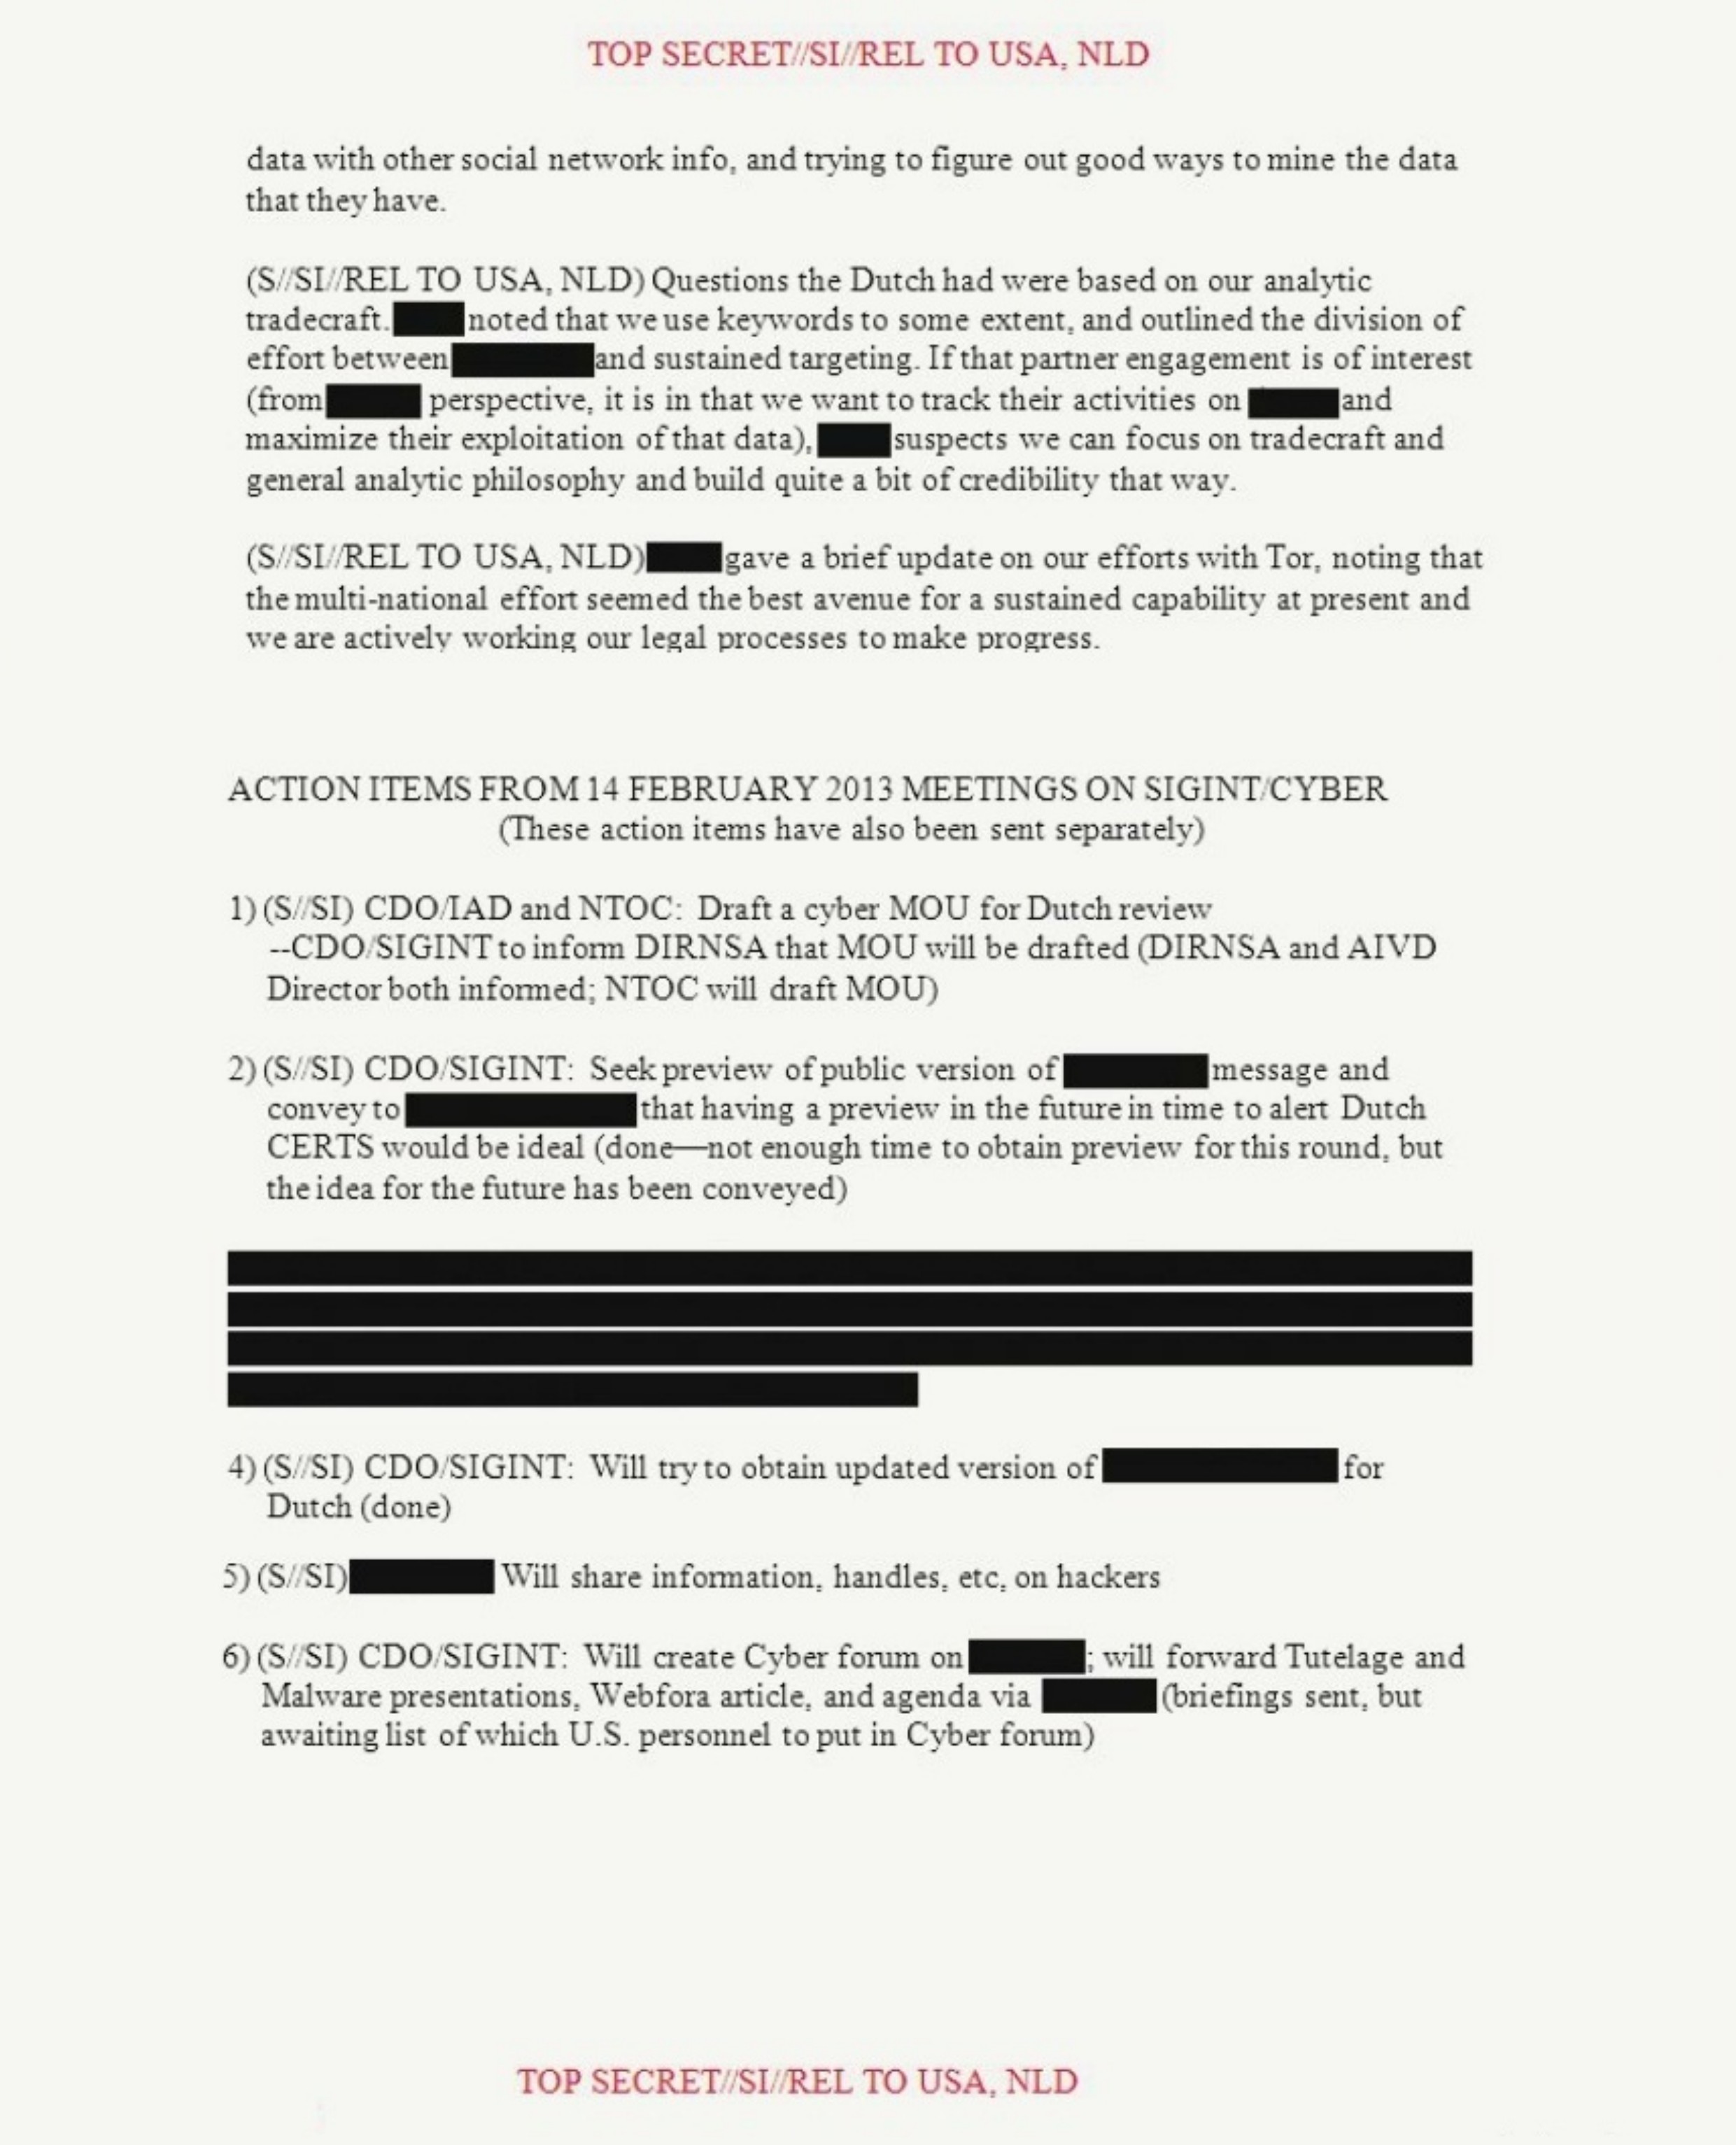
data with other social network info, and trying to figure out good ways to mine the data that they have.
(S//SI//REL TO USA, NLD) Questions the Dutch had were based on our analytic tradecraft. [REDACTED] noted that we use keywords to some extent, and outlined the division of effort between [REDACTED] and sustained targeting. If that partner engagement is of interest (from [REDACTED] perspective, it is in that we want to track their activities on [REDACTED] and maximize their exploitation of that data). [REDACTED] suspects we can focus on tradecraft and general analytic philosophy and build quite a bit of credibility that way.
(S//SI//REL TO USA, NLD) [REDACTED] gave a brief update on our efforts with Tor, noting that the multi-national effort seemed the best avenue for a sustained capability at present and we are actively working our legal processes to make progress.
ACTION ITEMS FROM 14 FEBRUARY 2013 MEETINGS ON SIGINT/CYBER
(These action items have also been sent separately)
1) (S//SI) CDO/IAD and NTOC: Draft a cyber MOU for Dutch review--CDO/SIGINT to inform DIRNSA that MOU will be drafted (DIRNSA and AIVD Director both informed; NTOC will draft MOU)
2) (S//SI) CDO/SIGINT: Seek preview of public version of [REDACTED] message and convey to [REDACTED] that having a preview in the future in time to alert Dutch CERTS would be ideal (done—not enough time to obtain preview for this round, but the idea for the future has been conveyed)
[REDACTED]
[REDACTED]
[REDACTED]
4) (S//SI) CDO/SIGINT: Will try to obtain updated version of [REDACTED] for Dutch (done)
5) (S//SI) [REDACTED] Will share information, handles, etc, on hackers
6) (S//SI) CDO/SIGINT: Will create Cyber forum on [REDACTED] will forward Tutelage and Malware presentations, Webfora article, and agenda via [REDACTED] (briefings sent, but awaiting list of which U.S. personnel to put in Cyber forum)
TOP SECRET//SI//REL TO USA, NLD
Related Documents
-
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe -
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael