Tag: Computer Network Exploitation 143 documents
Search documents matching “Computer Network Exploitation” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Farewell, but Forever in the Fight! SIDtoday [pdf]
NSA chief of the National Tactical Integration Office retires after almost 40 years in SIGINT.
People: Flynn, ThomasThe Intercept ↗ (2016-08-10) -
FASHIONCLEFT - Interface Control Document (15 June 2009) [pdf]
This 2009 NSA Interface Control Document provides comprehensive technical specifications for FASHIONCLEFT, the protocol that acts as a covert shipping system enabling TAO malware implants to send stolen network data back to NSA collection servers with minimal computer processing requirements—using multiple encryption layers (RSA-1024 and RC6-128) to disguise the traffic as it travels across the internet while allowing NSA's Common Data Receptor to reassemble and authenticate the original intercepted packets. The document details how implants make modified copies of captured network traffic (changing destination addresses to point toward NSA instead of legitimate recipients), apply various levels of encryption or scrambling ("munging") depending on how powerful the infected computer is, attach metadata instructions explaining how to reconstruct the original packets, and use pattern-matching algorithms to ensure NSA systems can identify which stolen packets belong to which collection operation.
Programs: FASHIONCLEFT · FLAXENPRECEPT · SHELLGREY · SURPASSPIN · SEAGULLFARO · ROOTKNOT · FIGBUILD · OPTICPINCH · VINYLSEAT · OLYMPUS · UNITEDRAKE · HOGTECH · SWEEPFORWARD · CONVEY · PINWALE · TREBLECLEF · FOGYNULL · FUNNELAPS · FLASHHANDLE -
FINAL Agenda SWEDUSA [pdf]
Detailed list of points and participants in the summit meeting between the top brass of the FRA and the NSA in April 2013.
Programs: TURTLEPOWER · TURMOIL · XKEYSCORE · WINTERLIGHT · QUANTUM · PARTNERMALL · VIVIAN · NAPA-3 · GCE · SSO -
Finding and Querying Document Metadata [pdf]
This 2009 NSA training guide, created by Booz Allen Hamilton, explains how analysts can use the XKEYSCORE system to track targets by searching for "non-traditional selectors" embedded within documents, such as author names, company information, or even the hash values of company logos.
Programs: XKEYSCORE · TUNINGFORK · PINWALE · FOXACID · FOXBASE · CARBOY · CARDAMON · UNITEDRAKE · CADENCE -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
GCHQ Application for Renewal of Warrant GPW/1160 [pdf]
GCHQ’s 2008 application to renew warrant GPW/1160 seeks blanket cover under ISA section 5 to reverse engineer and modify commercial software—explicitly breaching copyright and licensing—to enable CNE, vulnerability research, and even police forensics. It catalogues concrete ops against web forums, routers, and antivirus, and asserts a novel legal theory blessed by the Intelligence Services Commissioner to immunize intellectual‑property interference.
-
GCHQ Intelligence Production Head Outlines Present and Future Priorities SIDtoday [pdf]
According to a talk recently given at NSA's UK base in Menwith Hill, counterterrorism absorbs most (30%) of GCHQ's resources. Afghanistan and China are given increasing attention, while Russia gets less. Long term, GCHQ foresees challenges in keeping up with the internet and "huge amounts of data", while peace is expected in Iraq.
People: Ashton, JonThe Intercept ↗ (2019-05-29) -
GCHQ NAC review – April to June (2011) [pdf]
The GCHQ NAC review (Apr–Jun 2011) details the continuation of Operation Socialist, describing how NAC supported mapping Belgacom’s internal network and guided CNE operators to infiltrate key GRX routers. The aim was to establish positions within the network to enable man-in-the-middle (MitM) operations against roaming mobile handsets.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – January to March (2011) [pdf]
The GCHQ NAC review (Jan–Mar 2011) highlights a successful MyNOC surge against GRX operators that significantly expanded intelligence on operator networks and traffic during Operation Socialist. This effort facilitated a major CNE operation against Belgacom (MERION ZETA), securing both deep and edge network access, with continued work to build on this infiltration.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – January to March (2012) [pdf]
The GCHQ NAC review (Jan–Mar 2012) reports ongoing progress in maintaining CNE access to the Belgacom GRX operator, with the CNE EREPO team issuing new operational requirements to the NAC to further guide and support the hacking operation "OP Socialist".
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – July to September (2011) [pdf]
The GCHQ NAC review (Jul–Sep 2011) outlines the continued support by NAC following the successful OP SOCIALIST operation, focusing on mapping Belgacom’s internal network and identifying key internal GRX routers to establish man-in-the-middle (MitM) platforms targeting roaming mobile handsets.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ NAC review – October to December (2011) [pdf]
The GCHQ NAC review (Oct–Dec 2011) reports that the Belgacom GRX exploitation was highly successful, enabling both CNE and Crypt Ops by uncovering extensive VPN exploitation opportunities through OP SOCIALIST II. The surge operation focused on mapping mobile operators connecting via VPN, analyzing GTP traffic for target selector extraction, and identifying optimal access points—ultimately strengthening sustained network exploitation under the VERACIOUS Project.
“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCHQ Report on the Technical Capabilities of the Powerful Espionage Program TEMPORA, which Allows for Full Take. [pdf]
In May 2012, GCHQ introduced the TEMPORA internet buffer capability, enabling full take collection of internet communications. This innovation provides NSA and GCHQ analysts access to extensive amounts of data, enhancing their analytical capabilities significantly.
-
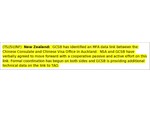
GCSB has identified an MFA data link [pdf]
A short extract from an April 2013 NSA document recording that GCSB had identified a Chinese Ministry of Foreign Affairs data link between the Chinese Consulate and the Chinese Visa Office in Auckland, and that NSA and GCSB had verbally agreed to mount a joint passive and active operation against it.
“Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · Fisher, David · Gallagher, Ryan · Hager, Nicky -
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO -
Getting the 'Ungettable' Intelligence: An Interview with TAO's Teresa Shea SIDtoday [pdf]
An interview with Teresa Shea, then chief of Tailored Access Operations, NSA's offensive hacking unit. In 2006 TAO had "access to over 258 target sets in 89 countries."
The Intercept ↗ (2019-05-29) -
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.