Genre: slides 272 documents
Search documents matching “slides” →What kind of document it is: slides, report, wiki, manual, guide, newsletter.
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
NSA target package [pdf]
This 2011 target package focuses on Muhammad Tahir Shahzad (alias Abu Hamza), a Pakistan-based bomb builder and Al-Qaeda facilitator. The document was produced by the Counter IED Analysis Integration Cell (CAIC) at the NSA. Notably, the document credits the tracking of Shahzad’s 60+ digital selectors with the eventual capture of high-value targets, including himself and Bali bombing suspect Umar Patek. The accompanying Washington Post investigation uses this specific case to highlight the massive scale of "incidental collection." While Shahzad was a valid foreign target under Section 702 of the FISA Amendments Act (FAA), the investigation revealed that for every legitimate target like him, the NSA intercepted nine "non-targeted" users—many of whom were Americans—capturing deeply personal photos, medical records, and private correspondence.
-
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
NSA/CSS Mission: PROVIDE AND PROTECT VITAL INFORMATION FOR THE NATION [pdf]
These slides, from an internal presentation in the first week of October 2001, show how critical the NSA sees electronic eavesdropping.
-
NSA/GCHQ/CSEC Network Tradecraft Advancement Team [pdf]
The "NSA/GCHQ/CSEC Network Tradecraft Advancement Team (NTAT) 2010" document describes a collaborative mission between the US, UK, and Canada to synchronize and advance SIGINT techniques. The NTAT focused on "Network Analysis Tradecraft," specifically integrating analysis tools such as IRASCIABLE RABBIT and TOYGRIPPE into CSEC's OLYMPIA and developing standardized "use cases" for tracking mobile networks and virtual private networks (VPNs).
-
NSA: How Network Mapping is Helping to Target the Credit Card Authorization Networks [pdf]
This document outlines NSA efforts to map and exploit credit card authorization networks by collecting, parsing, and ingesting transactional data from key geographic regions. It focuses on locating large stores of cardholder data, overcoming technical barriers to collection, and turning this financial information into actionable intelligence — part of a broader, highly secretive global financial surveillance program.
Programs: FOLLOWTHEMONEY -
NTAC Overview [pdf]
This document outlines the structure, mission, and operations of the U.K.’s National Technical Assistance Centre (NTAC), a GCHQ-controlled unit responsible for enabling and managing lawful interception of communications and decryption of data across national networks. It details NTAC’s integration into GCHQ, its key role in programs like MILKWHITE, its extensive interception capacity, and the technical and resource challenges it faces in adapting to evolving telecommunications technologies.
Marking: SECRET -
Offsensive Session: the Boundaries and Against Hacktivism [pdf]
GCHQ slides on “effects” operations against hacktivists: disruption in place of traditional law enforcement, denial-of-service attacks on key communications outlets during Op WEALTH in summer 2011, and a disruption playbook of infiltration, ruse, set-piece, false-flag, false-rescue, disruption and sting operations.
-
Operational Engineering November 2010 [pdf]
This internal GCHQ briefing from late 2010 documents the Events Product Centre's suite of bulk internet and communications surveillance tools — including IMMINGLE, SALAMANCA, SOCIAL ANTHROPOID, MUTANT BROTH, KARMA POLICE, SAMUEL PEPYS and GUIDING LIGHT — covering scaling targets, new data sources, and operational capabilities across telephony, webmail, instant messaging, social media, GPRS and VoIP collection.
Programs: EVENTS · IMMINGLE · SALAMANCA · GUIDINGLIGHT · B3M · HARDASSOC · MAINWAY · THUGGEE · FASCIA · HAUSTORIUM · FIRESTORM · TERRAIN · SHAREOWN · ESCHAR · BRIO · INFINITEMONKEY · KARMAPOLICE · MARBLEDGECKO · MEMORYHOLE · MUTANTBROTH · SAMUELPEPYS · SOCIALANIMAL · SOCIALANTHROPOID · HEARTBEAT · SANTHROPOID · LEAKYGATEWAYS · GTPTUNNEL · LUSTRE · GLASSBACK · COLLATERAL · HRMAP · SWORDPLAY · BROADOAK · REFORMER · ARTEMIS · MERLOT · CONTRAOCTAVE · CRYINGFOWL · CULTWEAVE · SAMDYCE · GCQUERY · BLAZZINGSADDLES · EREPO · JTRIG · SOUNDER -
Operational Legalities – GCHQ Powerpoint Presentation [pdf]
GCHQ’s “Operational Legalities” deck is an internal compliance playbook that translates the UK’s surveillance laws into day‑to‑day SIGINT procedure—drilling staff on authorisation, necessity, and proportionality, and walking through warrants, targeting justifications, database queries, dissemination, and oversight. Half slides and half speaker notes, it shows how analysts are trained to document, audit, and defend operations under ISA, RIPA, HRA, and WTA while navigating edge cases like location, nationality, second‑party constraints, and “indirect targeting.”
-
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
Peeling Back the Layers of TOR with EGOTISTICALGIRAFFE [pdf]
An NSA Tailored Access Operations presentation describing EGOTISTICALGIRAFFE and EGOTISTICALGOAT — Firefox browser exploits targeting Tor Browser Bundle users — covering fingerprinting Tor users via the TorButton BuildID, the EGOTISTICALGOAT type confusion vulnerability in Firefox's E4X implementation enabling remote code execution, and the FINKDIFFERENT/FUNNELOUT callback infrastructure used to exfiltrate data from exploited targets.
Programs: EGOTISTICALGIRAFFE · EGOTISTICALGOAT · ERRONEOUSINGENUITY · ERIN · EGGO · FINKDIFFERENT · FIDI · EGGI · FUNNELOUT -
Phone Number Extractor [pdf]
A top secret XKEYSCORE training document from October 2009 describing the Phone Number Extractor capability, which automatically identifies and extracts telephone numbers from intercepted internet traffic including website content, email signature blocks, HTTP GET requests from mobile devices, HTTP POST submissions, and converged DNR/DNI collection — with operational examples targeting Iran, Lebanon, and Pakistan.
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Presentation on the spying program PRISM and ECC's participation [pdf]
This presentation provides statistics on the PRISM surveillance program, detailing intelligence reporting and target tasking across various NSA units and partners from 2011 to 2013. The data reveals that while not the top producer by volume, the European Cryptologic Center (ECC) was the most proportionally reliant on PRISM, which constituted over half of its intelligence output.
-
PRESTON Study [pdf]
This GCHQ document details the PRESTON surveillance program, revealing that over a six-month period, 97% of intercepted communications—including calls, texts, and internet data—were not viewed by analysts despite being fully warranted, highlighting systemic challenges in processing and exploiting the vast volume of collected intelligence. It underscores the reliance on traditional PRESTON sources for events like the London G20, while noting gaps in data feeds from other repositories, reflecting both operational scale and limitations in effective oversight.
-
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
PRISM Olympic Option [pdf]
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
PRISM planning slide (PRISM briefing 1) [pdf]
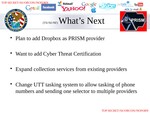
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.