Genre: slides 272 documents
Search documents matching “slides” →What kind of document it is: slides, report, wiki, manual, guide, newsletter.
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Mobile apps doubleheader: BADASS Angry Birds [pdf]
A joint GCHQ/GTE/CSEC presentation describing BADASS — the BEGAL Automated Deployment and Survey System for rapidly developing and deploying mobile app exploitation rules — illustrated through detailed analysis of Angry Birds' Dataflurry analytics traffic leaking IMEI, IMSI, cell network metadata and device identifiers, alongside AdMob, Mobclix and Mydas ad network traffic leaking UDIDs and IMEIs across iOS, Android, BlackBerry and Windows Phone 7 platforms.
Programs: BADASS · BEGAL · SEM · UNIQUELYCHALLENGED · BLACKHOLE · MOUNTAINVIEW · VOB · BABELFISH · BISHOP · MVR · PPF · AEG · DATAFLURRY -
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Mobile Theme Briefing (May 28, 2010) [pdf]
This 2010 GCHQ briefing document outlines the “Mobile Applications Project,” which aims to expand intelligence capabilities to exploit the growing shift from fixed to mobile internet usage. It details objectives for targeting mobile apps and roaming network traffic (GRX), enabling converged analysis of voice, text, command-and-control, and geolocation data across multiple mobile platforms such as iPhone, Symbian, Android, and Windows Mobile. See also: EFF_-_20140128-guard-leaky_phone_apps_0 (includes other slides from the same slideset)
Programs: Mobile Applications Project -
MORECOWBELL [pdf]
This document describes how NSA is covertly monitoring DNS resolutions and target websites in near real-time using covertly rented servers in Malaysia, Germany and Denmark.
-
Moving Data Through Disconnected Networks - Delay-Tolerant Networking and the IC [pdf]
This June 2012 NSA Laboratory for Telecommunications Sciences presentation details Delay-Tolerant Networking (DTN) applications for surveillance operations, including covert communications in denied areas, data exfiltration from isolated networks, unwitting data mules, and integration with TAO's CHIMNEYPOOL implant framework. The document reveals R4 development of FUZZYLINT, an ultra-lightweight DTN implementation designed to enable multi-hop exfiltration from implants without requiring direct physical access.
People: Vahdat, Amin · Becker, David · Juang, Philo · Oki, Hidekazu · Wang, Yong · Martonosi, Margaret · Peh, Li-Shiuan · Rubenstein, Daniel · Grossglauser, Matthias · Tse, David N. C. · Fall, Kevin · Shah, Rahul C. · Roy, Sumit · Jain, Sushant · Brunette, Waylon · Lindgren, Anders · Doria, Avri · Schelen, Olov · Small, Tara · Haas, Zygmunt J. · Zhao, Wenrui · Ammar, Mostafa · Zegura, Ellen · Ginzboorg, Philip · Kärkkäinen, Teemu · Nagata, Akira · Lenders, Vincent · Legendre, Franck · May, Martin · Karlsson, Gunnar · Du, Bowei · Demmer, Michael · Brewer, Eric · Ott, Jörg · Pitkänen, Mikko Juhani · Han, Bo · Hui, Pan -
National Security Agency: Overview Briefing [pdf]
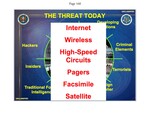
A slide from an unclassified NSA overview briefing, “The threat today”, which lists hackers, criminal elements, insiders and terrorists alongside technologies — the Internet, wireless, high-speed circuits, pagers, facsimile and satellite — as the threats the agency faces.
Marking: UNCLASSIFIED -
-
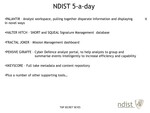
NDIST — GCHQ’s Developing Cyber Defence Mission [pdf]
GCHQ’s NDIST sets out a developing cyber defence mission to reduce vulnerability and harm while enabling prosperity, centered on building a global-level picture of strategic threats and sharing intelligence with allies. The team anchors this work in massive telemetry, claiming roughly 100 million malware events collected per day to drive situational awareness.
-
Net Defense from Encrypted Communications [pdf]
A NSA Technology Directorate briefing from February 2012 describing BLUESNORT — a capability that repurposes GALLANTWAVE's SSL/TLS decryption pipeline for network defence, re-injecting decrypted traffic into TURMOIL Stage 1 Prime where BLUESNORT detects malware and other malicious activity — representing description of NSA using its own bulk decryption infrastructure for cyber defence as well as intelligence collection.
-
Network Shaping 101 [pdf]
An NSA top-secret training presentation that uses Yemen as a case study to explain how to "shape" a nation's Internet traffic by exploiting Autonomous Systems, upstream providers, BGP routing, and physical link topology to redirect or collect communications. The slide deck walks through practical router/IP/link details, passive SIGINT collection points and limitations, and warns that many assumptions are fabricated for the lesson and that real-world capabilities and link behavior can vary.
-
Next Generation Events [pdf]
A 2009 TOP SECRET briefing outlines the “Next Generation Events” program to scale internet metadata and content analysis across Five Eyes, addressing explosive growth in data volume and the limits of legacy ingest systems. It presents a phased roadmap combining cloud infrastructure, large‑scale event processing, and enhanced profiling to enable bulk analytics and contact chaining.
Programs: NGE · HAUSTORIUM · BLAZINGSADDLES · HARBOURPILOT · MUTANTBROTH · AUTOASSOC · KARMAPOLICE · SOCIALANIMAL · INFINITEMONKEYS · HRMAP · MEMORYHOLE · MARBLEDGECKO · SIMMER · ROCKRIDGE · SAMUELPEPYS · CAFFEINEHIT · LAUGHINGHYENA · SALAMANCA · CLOUD · MONTEVISTA · LOOKINGGLASS · XKEYSCORE · FUMECUPBOARD · IIB · MoaG -
NIOC MARYLAND ADVANCED COMPUTER NETWORK OPERATIONS COURSE [pdf]
Programs: GENIE · HAWKEYE · EINSTEIN · TUTELAGE · NEPTUNETHUNDER · BLINDDATE · HAPPYHOUR · NITESTAND · WAITAUTO · MATCHCRIMP -
NSA Area 82 Update April 2009 [pdf]
Programs: RT-RG“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
NSA Cyber Timeline (Some Key SSO Cyber Milestone Dates Since Fall 2005) [pdf]
A one-page NSA SSO timeline of cyber-related milestones from fall 2005 to late 2012: CNCI implementation, the Protect America Act and FISA Amendments Act certifications, TURMOIL and XKEYSCORE deployments, and the August 2012 Iranian DDoS attack on Saudi Aramco.
Programs: TURMOIL · SSO · BLUESNORT · DANCINGOASIS · MADCAPOCELOT · TURBULENCE · XKEYSCORE · WEALTHYCLUSTER -
NSA June 2012 SSO Weekly Brief Excerpt [pdf]
This NSA Special Source Operations (SSO) briefing from June 2012 describes SPINNERET, a surveillance program that became the second-largest source of phone calling records and "tips" feeding into SHELLTRUMPET, a system that obscures the origin of collected metadata before forwarding it to NSA's Real-Time Regional Gateway (RT-RG) in Texas. The document indicates SHELLTRUMPET "obfuscates the source designators" and filters metadata to only include call events within NSA-Texas's area of responsibility.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
NSA Relationship With the Israeli SIGINT National Unit [pdf]
This top secret April 2007 NSA presentation provides an overview of the relationship between NSA and Israel's SIGINT National Unit (ISNU), detailing the organizational structure of Israeli signals intelligence, the history and terms of cooperation since the 1950s, and specific intelligence challenges that arose during the 2006 Israel-Hezbollah war when Israeli requests raised USG policy issues over geolocational data and NSA resources.
Programs: CHIPPEWAPeople: Shalit, Gilad -
NSA slide on Saudi ordered attack by Syrian opposition [pdf]
This NSA report revealed that Saudi Prince Salman bin Sultan directly ordered Syrian opposition forces to attack Damascus on the second anniversary of the revolution, providing 120 tons of explosives and weapons, with U.S. surveillance giving advance warning of the assault on the airport, presidential palace, and other targets. The Saudis were reportedly very satisfied with the results, and PRISM collected nearly all intelligence on the opposition’s plans and operations.
Programs: PRISMPeople: Sultan, Salman bin -
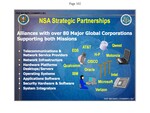
NSA Strategic Partnerships [pdf]
A slide on NSA's “alliances with over 80 major global corporations”, naming AT&T, Verizon, Qwest, Cisco, Microsoft, Oracle, Intel, IBM, HP, Motorola, Qualcomm and EDS across telecommunications, network infrastructure, hardware, operating systems, applications and security.
-
NSA Supply Chain Attack From PMR 4-24-13 [pdf]
This document is a top-secret NSA report detailing a SIGINT development operation in which a classified Voice-over-IP network shipment was intercepted and subjected to a supply-chain interdiction, allowing NSA and its intelligence community partners to gain access to the hardware and intelligence. It describes the operational process, including tracking the shipment through China, coordinating with Tailored Access Operations (TAO), and using tools like XKEYSCORE to identify targeting selectors, ultimately enabling detailed surveillance and future operational opportunities.