NSA/GCHQ/CSEC Network Tradecraft Advancement Team
Open PDFDocument date: 2010-01-01
Pages: 1
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, FVEY//20320108
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, FVEY
The "NSA/GCHQ/CSEC Network Tradecraft Advancement Team (NTAT) 2010" document describes a collaborative mission between the US, UK, and Canada to synchronize and advance SIGINT techniques. The NTAT focused on "Network Analysis Tradecraft," specifically integrating analysis tools such as IRASCIABLE RABBIT and TOYGRIPPE into CSEC's OLYMPIA and developing standardized "use cases" for tracking mobile networks and virtual private networks (VPNs).
My notes
NTAT
Network Tradecraft Advancement Team
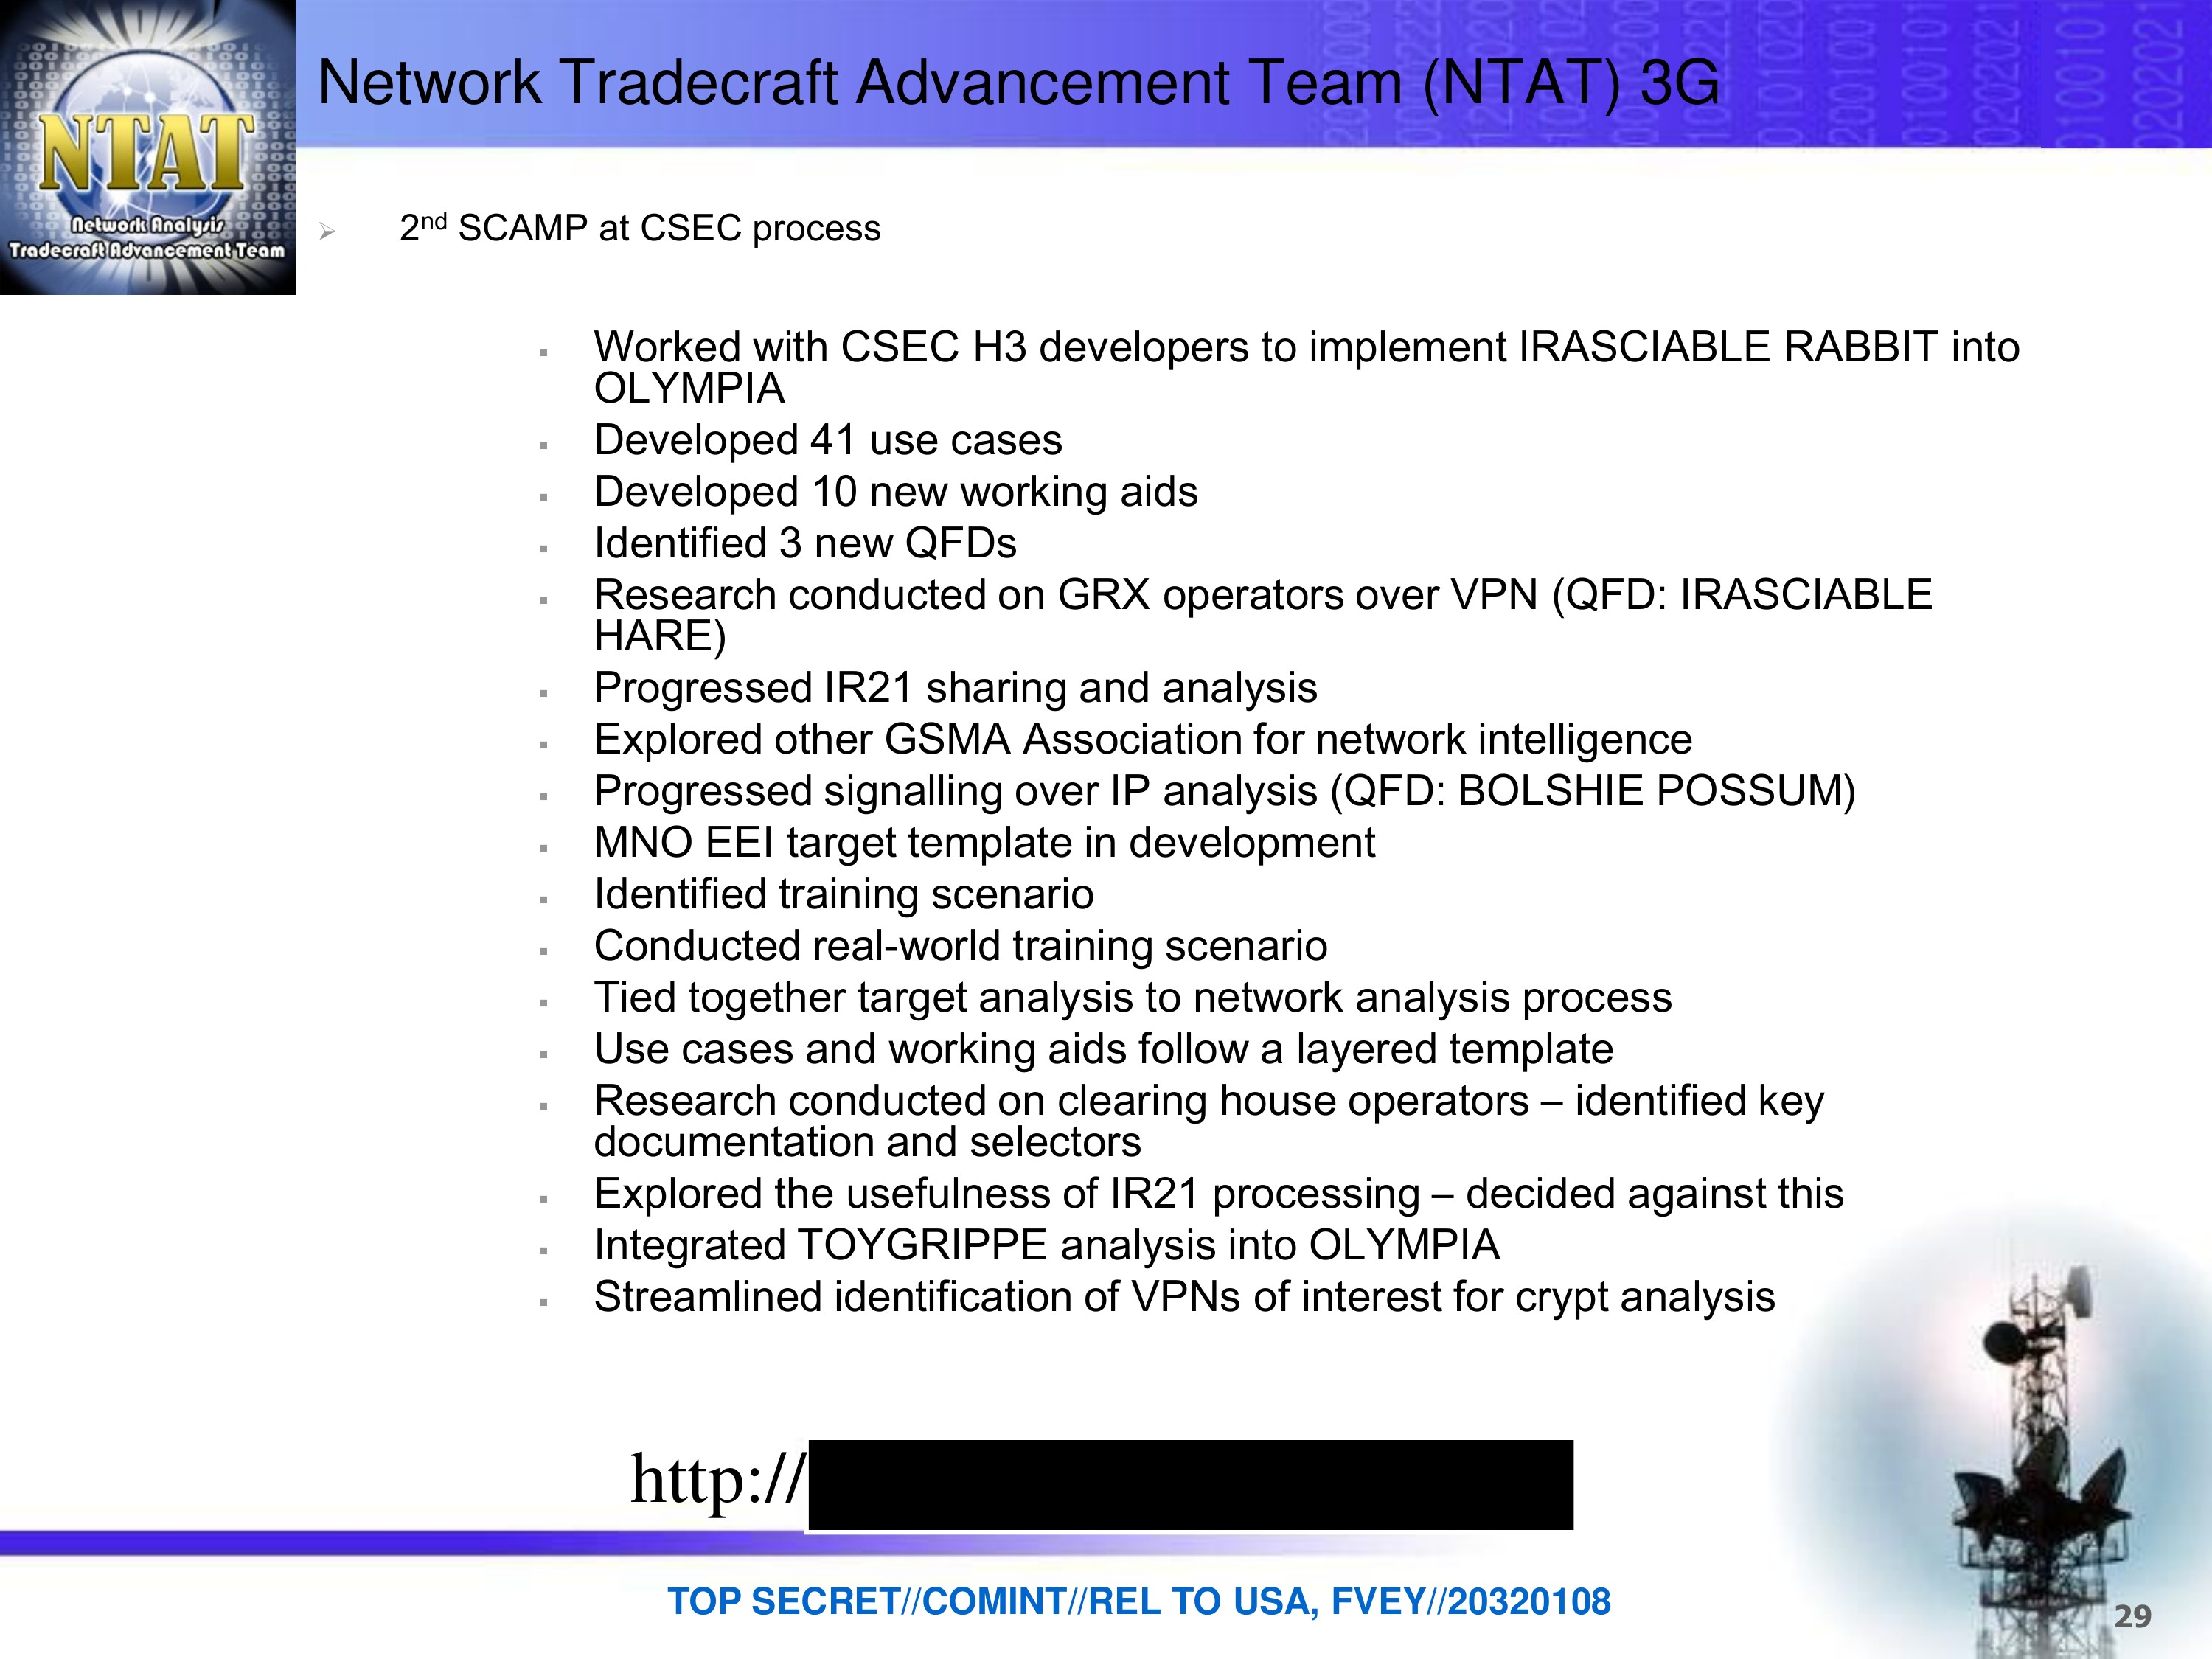
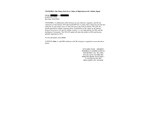
Network Tradecraft Advancement Team (NTAT) 3G
2nd SCAMP at CSEC process
- Worked with CSEC H3 developers to implement IRASCIABLE RABBIT into OLYMPIA
- Developed 41 use cases
- Developed 10 new working aids
- Identified 3 new QFDs
- Research conducted on GRX operators over VPN (QFD: IRASCIABLE HARE)
- Progressed IR21 sharing and analysis
- Explored other GSMA Association for network intelligence
- Progressed signalling over IP analysis (QFD: BOLSHIE POSSUM)
- MNO EEI target template in development
- Identified training scenario
- Conducted real-world training scenario
- Tied together target analysis to network analysis process
- Use cases and working aids follow a layered template
- Research conducted on clearing house operators – identified key documentation and selectors
- Explored the usefulness of IR21 processing – decided against this
- Integrated TOYGRIPPE analysis into OLYMPIA
- Streamlined identification of VPNs of interest for crypt analysis
http://[REDACTED]
29
TOP SECRET//COMINT//REL TO USA, FVEY//20320108
Published in the Same Report
(8 documents)
-
AURORAGOLD – Project Overview [pdf]
A technical briefing document outlining an NSA SIGINT initiative designed to map, monitor, and forecast the evolution of global mobile networks. It details the project's infrastructure, which aggregates both unclassified commercial data and classified intelligence intercepted from international roaming agreements to identify technical trends and exploitation opportunities.
-
AURORAGOLD – Target Technology Trends Center support to WPMO [pdf]
This briefing details the technical architecture and data pipeline used to process global cellular network information. It specifically highlights the synergy between data gathering on GSM/UMTS networks and the implementation of "Auto-Minimization" to ensure the resulting SIGINT reporting complies with NSA legal and policy requirements.
-
AURORAGOLD Working Aid [pdf]
This document is a technical reference guide for analysts that categorizes the specific data fields extracted from mobile network documents (IR.21s) and commercial databases. It serves as a manual for translating telecommunications infrastructure data—such as encryption types, network layer protocols, and hardware versions—into actionable intelligence for target development and cyber exploitation.
Programs: AURORAGOLD -
AURORAGOLD Working Group [pdf]
The "AURORAGOLD Working Group" briefing is a highly classified SIGINT development presentation from June 2012 that outlines the NSA's progress in mapping the global mobile landscape (GSM/UMTS/LTE). It focuses on the project's "value proposition": providing an exhaustive database of network identifiers and technical configurations—often obtained by intercepting internal company documents—to support tactical military operations and long-term surveillance forecasting.
Programs: AURORAGOLD · UTT · XKEYSCORE · CADENCE · JUBILEECORONA · RONIN · NKB · GLOBALTIPPER · PINWALE -
IR.21 – A Technology Warning Mechanism [pdf]
This 2010 TOP SECRET NSA briefing defines the IR.21 roaming document as a critical tool for "horizon scanning" and "forecasting" global telecommunications shifts. The document outlines how the NSA uses these technical files to proactively identify emerging 3G and 4G technologies, pinpointing vulnerabilities for exploitation before new systems are even fully deployed.
-
OPULENT PUP Encryption Attack [pdf]
"OPULENT PUP encryption attack (GCHQ)" is a 2009 technical planning document from the British intelligence agency GCHQ. It outlines a "proof-of-concept demonstrator" for a new capability to intercept and decrypt GSM communications protected by the A5/3 algorithm, requiring a complete overhaul of the existing processing chain used for the older A5/1 standard.
Programs: OPULENTPUP -
NSA First-Ever Collect of High-Interest 4G Cellular Signal [pdf]
The memorandum documents a technical milestone achieved in January 2010: the first successful interception of Time Division-Long Term Evolution (TD-LTE) 4G communications. This collection was conducted at the RAINFALL site (the unclassified cover term for the Joint Defence Facility Pine Gap in Australia) and marked the transition of intelligence priority from 2G/3G systems to all-Internet Protocol (IP) 4G networks.
Programs: RAINFALL -
WOLFRAMITE Encryption Attack [pdf]
The "WOLFRAMITE Encryption Attack" is a GCHQ strategic annex from March 2011 detailing a joint effort with the NSA to compromise the A5/3 encryption standard. The document outlines a specialized research and development program aimed at scaling up handset exploitation and securing funding—estimated at approximately £4 million—to prototype a functional decryption attack against modern mobile broadband security.
Related Documents
-
AND THEY SAID TO THE TITANS: « WATCH OUT OLYMPIANS IN THE HOUSE! » [pdf]
This Top Secret CSEC “Olympia” document details a Canadian intelligence program that analyzed and tracked the Brazilian Ministry of Mines and Energy’s telecommunications, mapping IPs, servers, proxies, and mobile devices while automating data collection and network analysis to develop actionable intelligence. It outlines tools, workflows, and contacts used for surveillance, though the presentation does not explain the specific purpose of the operation.
Programs: OLYMPIA · QUOVA · PROMETHEUS · PEITHO · SLINGSHOT · LEVITATE · STRATOS · EVILOLIVE · GCHQ Geofusion · ATLAS · HYPERION · ATHENA · DANAUS · TIDALSURGE · BLACKPEARL · MARINA · STARSEARCH · PEPPERBOX · TRITON · PACKAGEDGOODS · ARK · TOYGRIPPE · FRIARTUCK · MASTERSHAKE · COEUS · STALKER · MAINWAY · FASCIA · SEDB · OCTSKYWARD · FASTBAT · TWINSERPENT · EONBLUE · DISHFIRE · GNDB“Read a CSEC document that was first acquired by Edward Snowden” - The Globe and Mail ↗ (2013-11-30) · “Ministério de Minas e Energia está na mira de espiões americanos e canadenses” - O Globo ↗ (2013-10-06) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Freeze, Colin · Bridi, Sônia · Greenwald, Glenn -
Belgacom connections [pdf]
A "Belgacom connections" map lays out the carrier’s sprawling roaming and backbone interconnects, precisely the arteries GCHQ wanted to get access into. Under Operation Socialist GCHQ successfully gained access to Belgacom’s infrastructure, including internal employee computers and encrypted and unencrypted streams of private communications handled by the company.
Programs: CARBONROD“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
AURORAGOLD Working Group [pdf]
The "AURORAGOLD Working Group" briefing is a highly classified SIGINT development presentation from June 2012 that outlines the NSA's progress in mapping the global mobile landscape (GSM/UMTS/LTE). It focuses on the project's "value proposition": providing an exhaustive database of network identifiers and technical configurations—often obtained by intercepting internal company documents—to support tactical military operations and long-term surveillance forecasting.
Programs: AURORAGOLD · UTT · XKEYSCORE · CADENCE · JUBILEECORONA · RONIN · NKB · GLOBALTIPPER · PINWALE -
AURORAGOLD – Target Technology Trends Center support to WPMO [pdf]
This briefing details the technical architecture and data pipeline used to process global cellular network information. It specifically highlights the synergy between data gathering on GSM/UMTS networks and the implementation of "Auto-Minimization" to ensure the resulting SIGINT reporting complies with NSA legal and policy requirements.
-
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark