Document year: 2011 84 documents
Search documents matching “2011” →When each document was written, from its own dateline. Undated documents don't appear here.
Sort: Title
Documents
-
FAA Certification Renewals with Caveats [pdf]
This NSA document shows that after the FISA Court found NSA’s upstream internet collection unconstitutional and illegal, the agency’s response was less about reform and more about finding technical and procedural workarounds to keep surveillance running as usual. While the court ordered changes within 30 days, NSA officials planned to sequester and filter “higher-risk” data to appease the judge—not halt collection—revealing a mindset focused on preserving operations rather than addressing legal violations.
-
Finding Nuggets -- Quickly -- in a Heap of Voice Collection, From Mexico to Afghanistan SIDtoday [pdf]
A 2011 article by an NSA Texas analyst describing the deployment of Human Language Technology analytics — including speech-to-text, speaker identification, gender recognition and language identification — to Special Collection Service sites in the Americas and to the Afghanistan Remote Operations Cryptologic Center, with operational examples ranging from tunnel detection in Tijuana to intelligence support in Kandahar.
Programs: HLT -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
GCHQ – Making network sense of the encryption problem (2011) [pdf]
GCHQ’s Network Analysis Centre convened a 2011 roundtable on “making network sense” of encryption, pushing a metadata-first strategy to triage SSL/TLS, IKE, OpenVPN, and SSH flows, pivot from “seed” indicators, and zero in on targets and subnets worth decrypting. The playbook leans on enrichment, AS-level scoping (explicitly citing Belgacom AS6774 GRX VPNs), and “access optimisation” to collect data pre‑encryption—passively or actively.
Programs: SQUEAL · BEARDEDPIGGY · CLOUD · IRASCIBLEHARE · IRASCIBLERABBIT · IRASCIBLEMOOSE · IRASCIBLEEMITT“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO -
Graph theory in the operational environment – GCHQ [pdf]
This document details GCHQ’s research on identifying “closed loops” of communication, where targets use a small set of phones to communicate exclusively among themselves, often with cheap, disposable handsets like the Nokia 1100. It explains the methodology for analyzing anonymized metadata, constructing contact graphs, and extracting non-giant, non-tree components to discover operationally relevant closed loops for intelligence and counterterrorism purposes.
Programs: VOICESAILPeople: Rumsfeld, Donald -
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
-
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
How Is Human Language Technology (HLT) Progressing? SIDtoday [pdf]
This document provides an operational update on the deployment of "HLT Labs"—a specialized suite of voice analytics designed to automate the discovery of intelligence "nuggets" within massive volumes of audio collection. The document highlights successful field applications in Afghanistan, Georgia, Texas, and Latin America, noting that these tools are becoming "force multipliers" that allow linguists to bypass manual listening in favor of automated keyword searching and speaker recognition.
-
ICTR Cloud Efforts [pdf]
A GCHQ presentation details how the agency developed cloud-based big data analytics to achieve "population scale" surveillance—processing trillions of internet events to build geographic and behavioral profiles on every online identifier worldwide, enabling discovery of unknown targets through pattern analysis rather than traditional keyword searches.
Programs: EVERYASSOC · PROBABILITYCLOUD · SILVERLINING · CULTWEAVE · KARMAPOLICE · EVERYPOLICE · AWKWARDTURTLE · GORDIANKNOT · SANDIA · BLOODHOUND · FIVEALIVE · NGE · MAPREDUCE -
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Is There a Sustainable Ops Tempo in S2? How Can Analysts Deal with the Flood of Collection? SIDtoday [pdf]
The NSA's Deputy Director for Analysis and Production discusses the unsustainable operational tempo caused by overwhelming data collection volumes, advocating for "Analytic Modernization" that would shift from treating SIGINT as "radioactive" NSA-only material to sharing raw intelligence with other agencies for collaborative exploitation.
Programs: A-SPACE -
It's OK to Have a Personality... Most of the Time! SIDtoday [pdf]
In this column, SIDtoday's editor explains the importance of injecting some personality into your writing.
The Intercept ↗ (2019-05-29) -
Japan: Eternal Land of the Rising Sun SIDtoday [pdf]
This document contains the NSA's SIGINT Deputy Director's reflections on his experiences in Japan, both during and after the devastating 2011 earthquake and tsunami. It highlights the resilience of the Japanese people, the swift recovery of U.S. personnel stationed in Japan, and their contributions to humanitarian efforts. The author also emphasizes the importance of SIGINT operations in the region and encourages others to consider field assignments in Japan, praising the country’s cultural richness and the strong sense of community among U.S. personnel stationed there.
Programs: SCQAWK -
JTAC Attack Methodology Team [pdf]
This September 2011 GCWiki page describes GCHQ's Joint Terrorism Analysis Centre (JTAC) Attack Methodology Team, a thematic assessment unit staffed by secondees from various government and military departments with access to Five Eyes intelligence, specializing in analyzing Islamist weaponry, tactics, training, IED construction, and terrorist attack methodologies.
Programs: RUSSETT -
June 2011 Nato Afghanistan Intelligence Report [pdf]
A June 2011 SHAPE weekly report to NATO HQ assessing the state of ISAF operations in Afghanistan, covering Taliban command and control deterioration, insurgent supply shortages, the post-bin Laden strain on NATO's Pakistani logistics routes, and notable attacks across regional commands.
Marking: NATO SECRET -
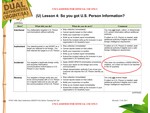
Lesson 4: So you got U.S. Person Information? [pdf]
This slide is used in a training course for NSA intelligence collectors and analysts. It tells the trainees what to do if they collect communications "to, from or about" a U.S. citizen, green card holder or company. The slide's revision date is nearly one month after the Foreign Intelligence Surveillance Court ruled on Oct. 3, 2011 that the NSA's handling of some "U.S. Persons" data was unlawful. The highlighted portion of the slide is notable because it shows that "incidentally" acquired U.S. communications, which may account for the highest volume of American content collected, are not purged from NSA databases. Analysts do not need to report "incidental" collection to the NSA Inspector General because it is not deemed a violation of rules. They may use the data routinely in "minimized" form, with identities masked, and with supervisory permission they may unmask the identities of U.S. persons in reports if the "customer set" requires them.
-
Manhunting Timeline 2008 - Intellipedia [pdf]
This document is an archived Intellipedia entry titled "Manhunting Timeline 2008," a collaborative wiki used by the U.S. Intelligence Community to track high-value targeting operations. It catalogs a global series of assassinations, captures, and military strikes against state officials and militant leaders, ranging from the arrest of the "Merchant of Death" to clandestine naval commando operations.
Programs: LORAINAPeople: Sulayman, Muhammad · al-Masri, Abu Khabab · Mursi, Midhat · Karadžić, Radovan · Ayrow, Aden Hashi · Ayro, Aden Hashi Farah · Nuristani, Mohammad Tamim · Hekmatyar, Gulbuddin · Khan, Kashmir · Bout, Viktor · Bush, George W. · Obama, Barack · Jones, James L. · Nabhan, Saleh Ali Saleh · Musharraf, Pervez · Kayani, Ashfaq Parvez · Kulick, Amir · bin Laden, Osama · Sarkozy, Nicolas -
May 2011 Nato Afghanistan Intelligence Report [pdf]
A May 2011 SHAPE weekly report to NATO HQ assessing ISAF operations in Afghanistan — including a major failed Taliban spring offensive in Kandahar, insurgent cache dispersal tactics, and the limited impact of bin Laden's death on Taliban operational capacity — alongside an update on Operation Unified Protector in Libya covering the Misrata siege and Gaddafi regime military activity.
Marking: NATO SECRET -
MILKWHITE Enrichment Service (MES) Programme [pdf]
This March 2011 GCHQ document details the MILKWHITE program, which is enhancing domestic interception and data analysis capabilities. It outlines expanded funding for advanced analytics, bulk data storage, and service scaling to meet growing demand from multiple law enforcement and intelligence agencies, including SOCA, HMRC, MI5, and SIS, thereby broadening access to large volumes of internet-derived metadata for operational use.