JTAC Attack Methodology Team
Open PDFDocument date: 2011-09-08
Pages: 3
Genre: wiki
Banner: TOP SECRET STRAP1 COMINT
Classification: TOP SECRET STRAP 1 COMINT
Dissemination: -
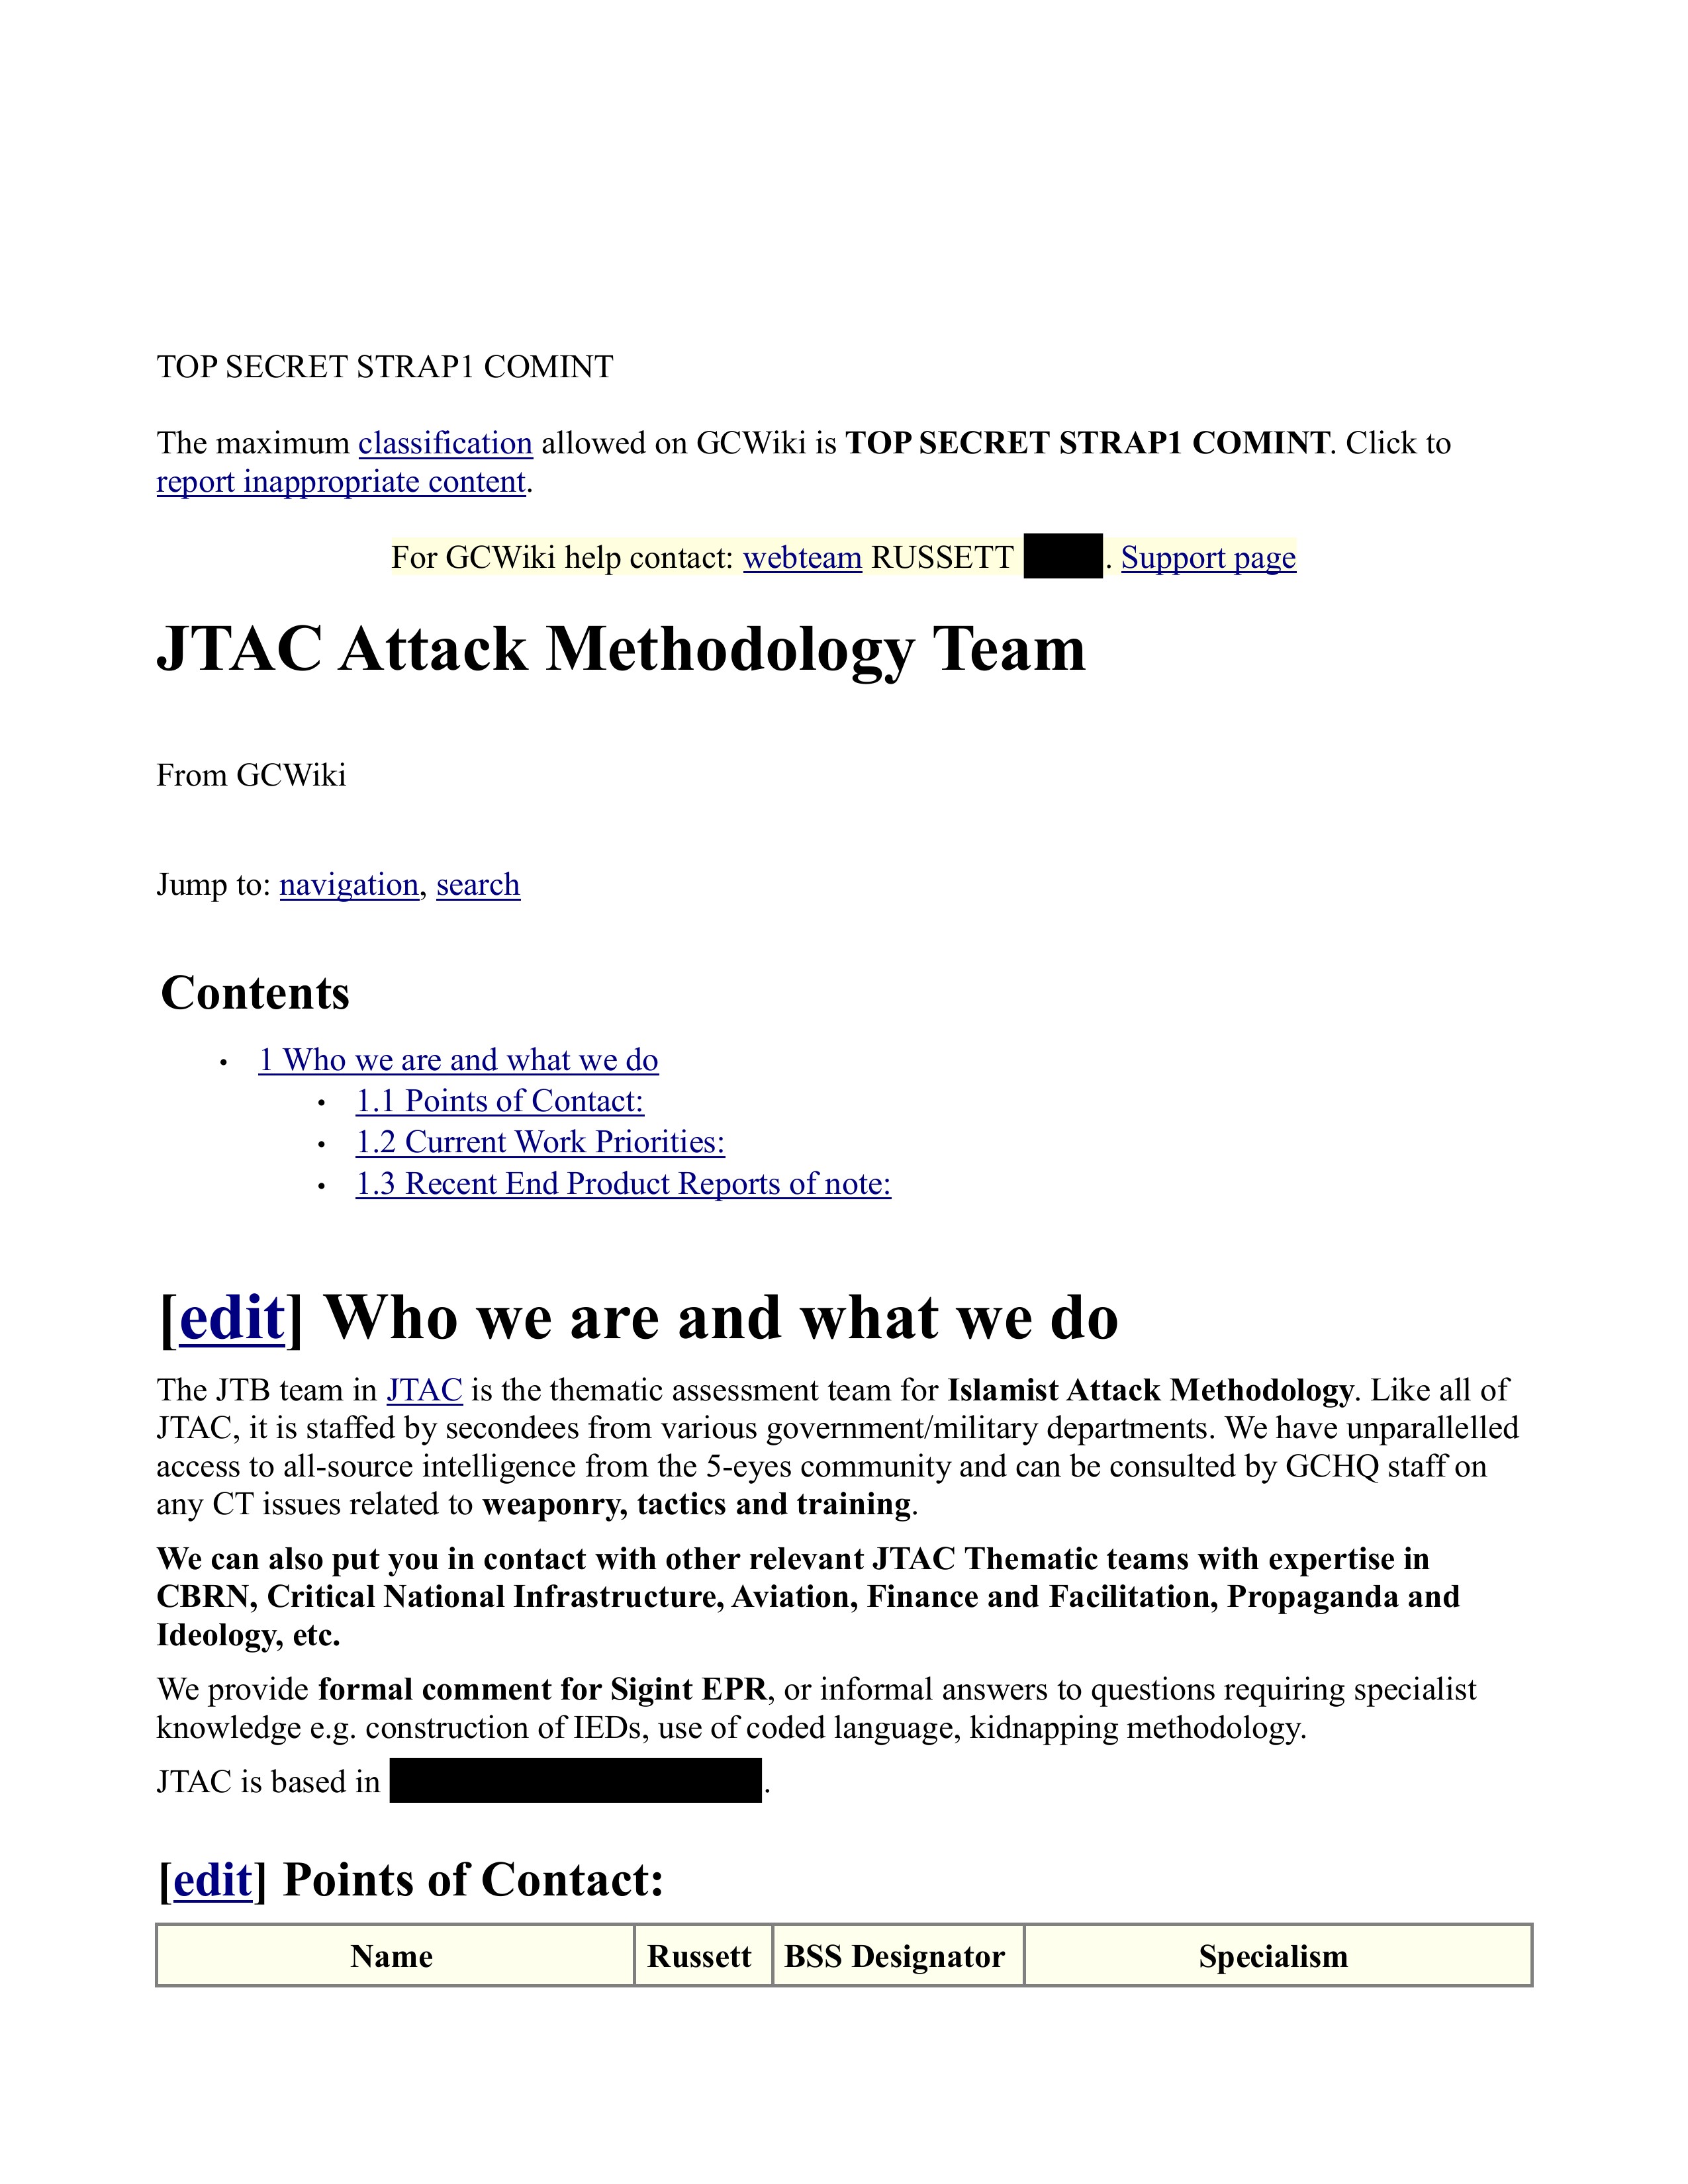
This September 2011 GCWiki page describes GCHQ's Joint Terrorism Analysis Centre (JTAC) Attack Methodology Team, a thematic assessment unit staffed by secondees from various government and military departments with access to Five Eyes intelligence, specializing in analyzing Islamist weaponry, tactics, training, IED construction, and terrorist attack methodologies.
My notes
TOP SECRET STRAP1 COMINT
The maximum classification allowed on GCWiki is TOP SECRET STRAP1 COMINT. Click to
report inappropriate content.
For GCWiki help contact: webteam RUSSETT [REDACTED]. Support page
JTAC Attack Methodology Team
From GCWiki
Jump to: navigation, search
Contents
1 Who we are and what we do
- 1.1 Points of Contact:
- 1.2 Current Work Priorities:
- 1.3 Recent End Product Reports of note:
[edit] Who we are and what we do
The JTB team in JTAC is the thematic assessment team for Islamist Attack Methodology. Like all of
JTAC, it is staffed by secondees from various government/military departments. We have unparallelled
access to all-source intelligence from the 5-eyes community and can be consulted by GCHQ staff on
any CT issues related to weaponry, tactics and training.
We can also put you in contact with other relevant JTAC Thematic teams with expertise in
CBRN, Critical National Infrastructure, Aviation, Finance and Facilitation, Propaganda and
Ideology, etc.
We provide formal comment for Sigint EPR, or informal answers to questions requiring specialist
knowledge e.g. construction of IEDs, use of coded language, kidnapping methodology.
JTAC is based in [REDACTED].
[edit] Points of Contact:
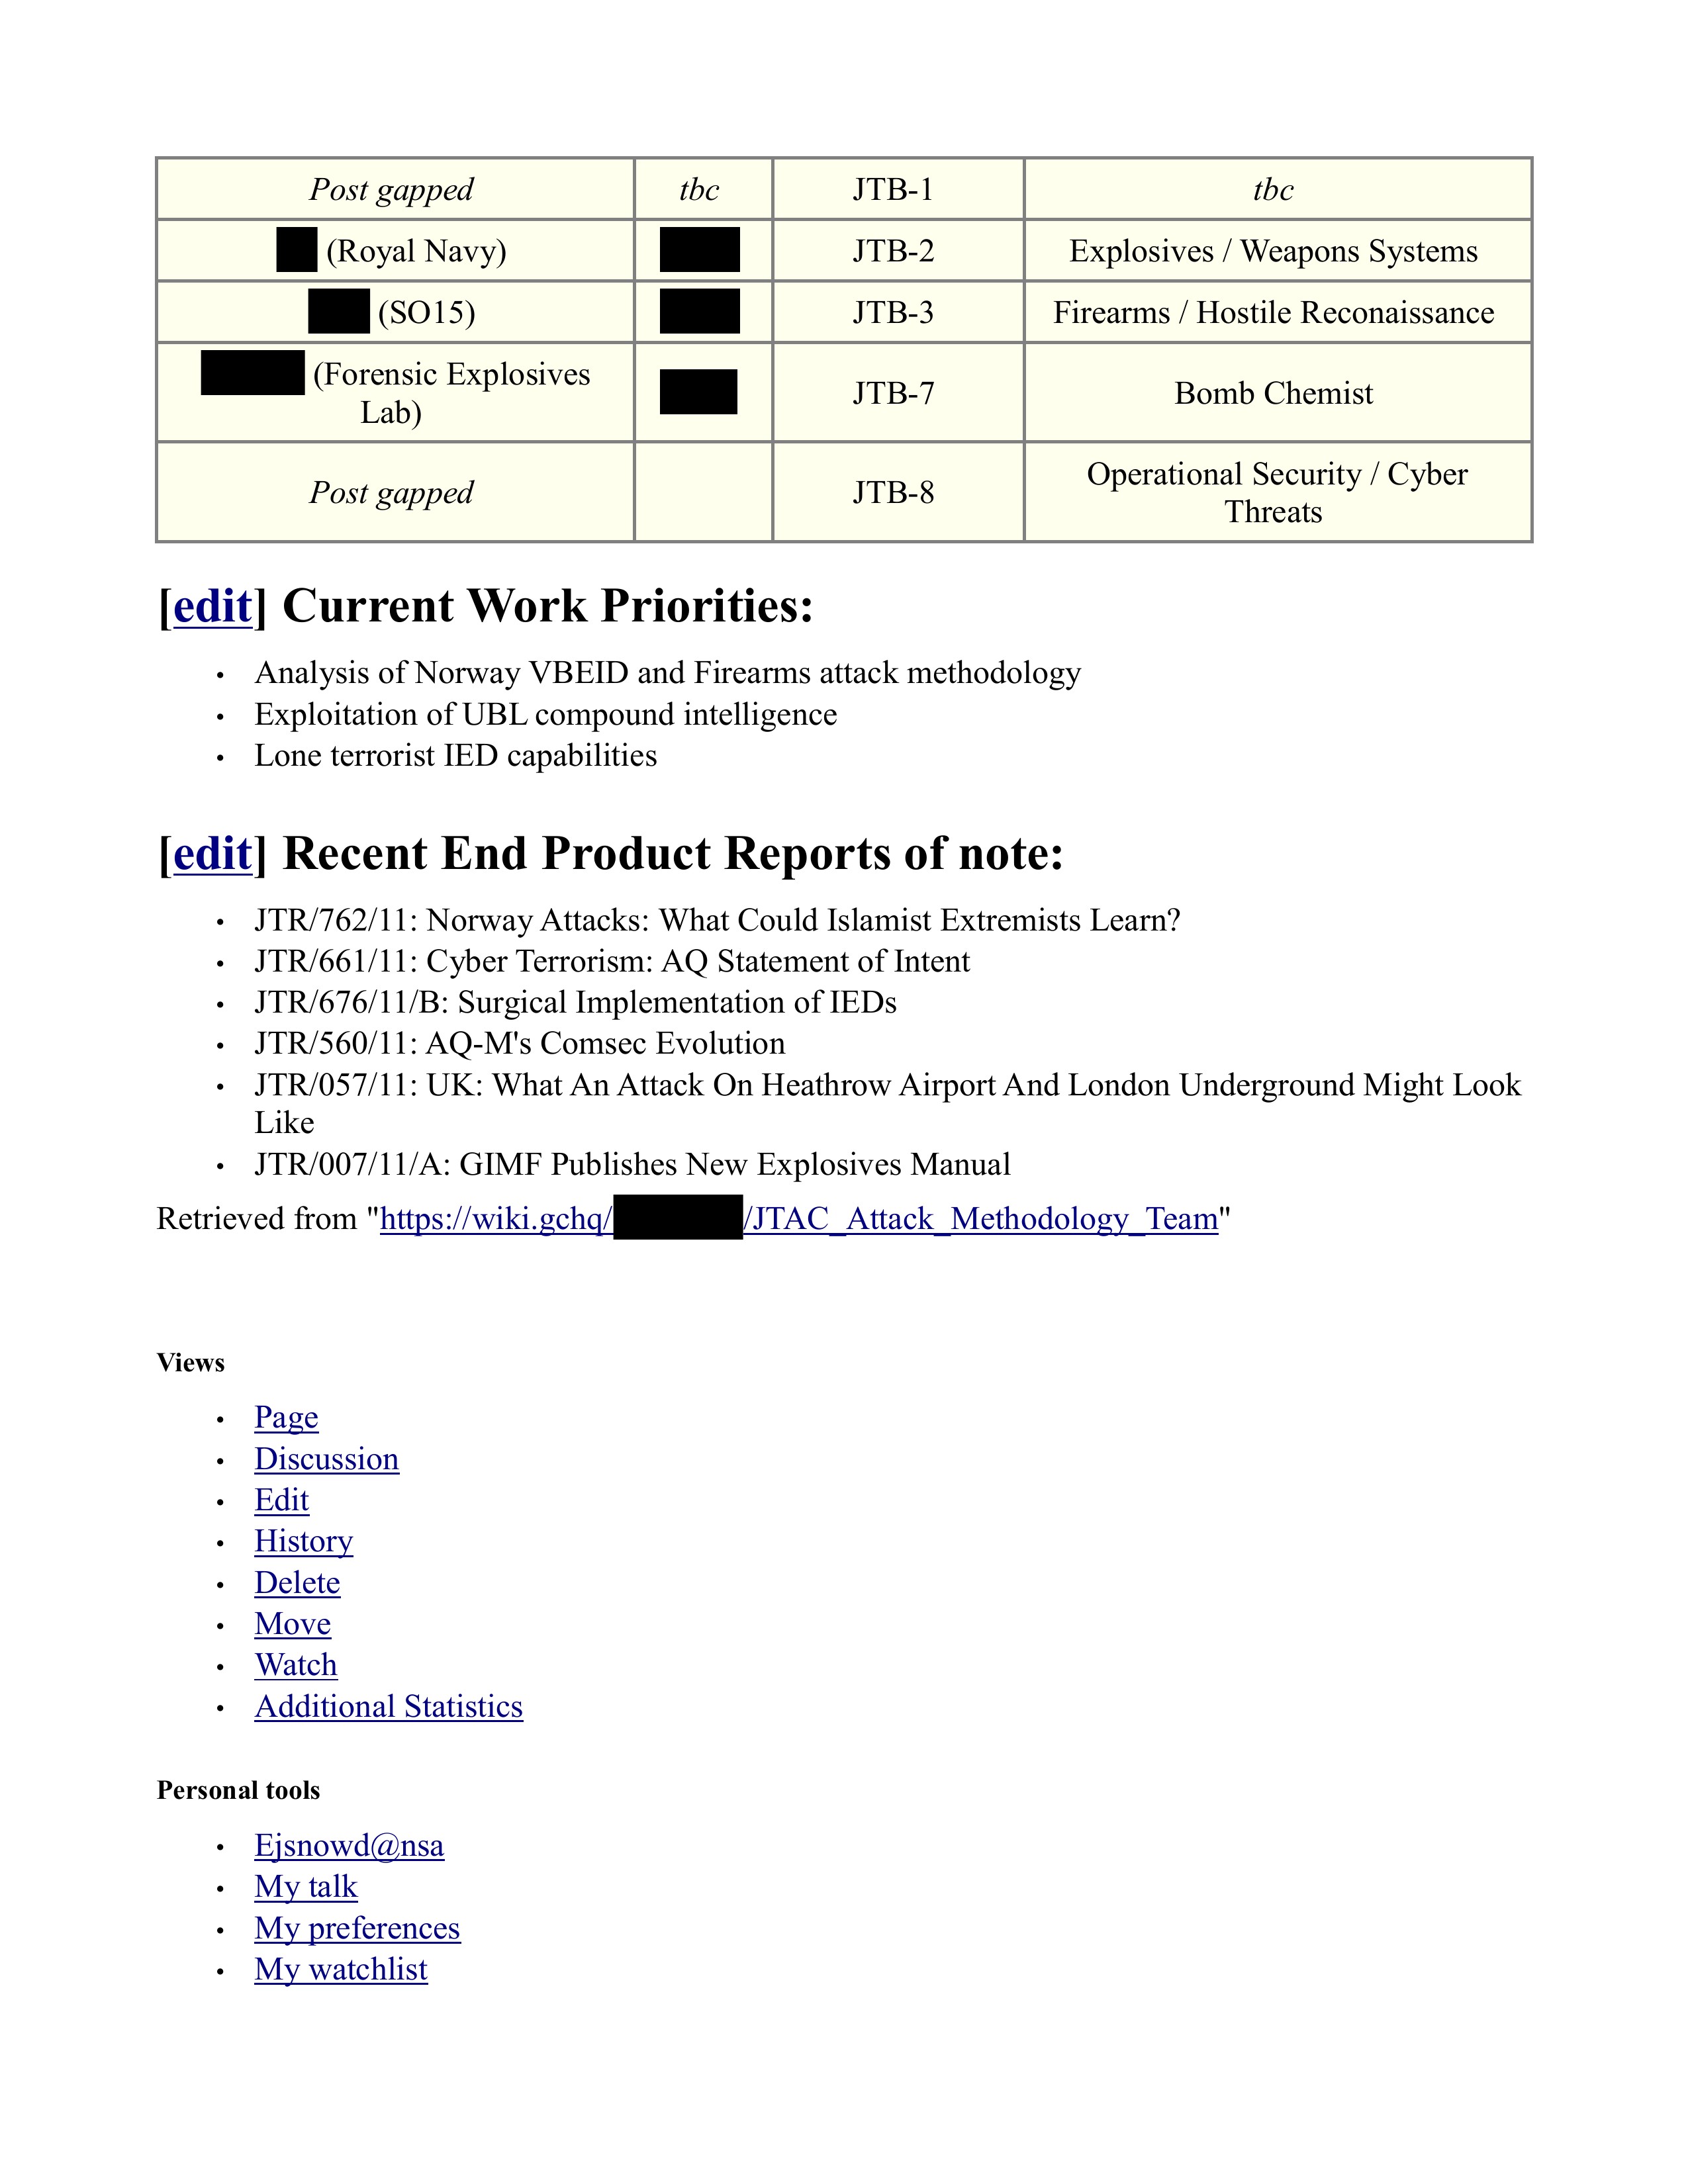
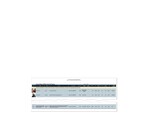
| Name | Russett BSS Designator | Specialism | |
|---|---|---|---|
| Post gapped | tbc | JTB-1 | tbc |
| [REDACTED] (Royal Navy) | [REDACTED] | JTB-2 | Explosives / Weapons Systems |
| [REDACTED] (SO15) | [REDACTED] | JTB-3 | Firearms / Hostile Reconaissance |
| [REDACTED] (Forensic Explosives Lab) | [REDACTED] | JTB-7 | Bomb Chemist |
| Post gapped | JTB-8 | Operational Security / Cyber Threats |
[edit] Current Work Priorities:
- Analysis of Norway VBEID and Firearms attack methodology
- Exploitation of UBL compound intelligence
- Lone terrorist IED capabilities
[edit] Recent End Product Reports of note:
- JTR/762/11: Norway Attacks: What Could Islamist Extremists Learn?
- JTR/661/11: Cyber Terrorism: AQ Statement of Intent
- JTR/676/11/B: Surgical Implementation of IEDs
- JTR/560/11: AQ-M's Comsec Evolution
- JTR/057/11: UK: What An Attack On Heathrow Airport And London Underground Might Look Like
- JTR/007/11/A: GIMF Publishes New Explosives Manual
Retrieved from "https://wiki.gchq/[REDACTED]/JTAC_Attack_Methodology_Team"
Views
- Page
- Discussion
- Edit
- History
- Delete
- Move
- Watch
- Additional Statistics
Personal tools
- Ejsnowd@nsa
- My talk
- My preferences
- My watchlist
- My contributions
Navigation
- Main Page
- Help Pages
- Wikipedia Mirror
- Ask Me About...
- Random page
- Recent changes
- Report a Problem
- Contacts
- GCWeb
Search
Go Search
Toolbox
- What links here
- Related changes
- Upload file
- Special pages
- Printable version
- Permanent link
- This page was last modified on 8 September 2011, at 15:30.
- This page has been accessed 2,211 times.
- All material is UK [http://[REDACTED] Crown Copyright] © 2008 or is held under licence from third parties. This information is
exempt under the Freedom of Information Act 2000 (FOIA) and may be exempt under other UK
information legislation. Refer any FOIA queries to GCHQ on 01242 [REDACTED] x [REDACTED] or
[REDACTED]@gchq.gsi.gov.uk - Privacy policy
- About GCWiki
- Disclaimers
TOP SECRET STRAP1 COMINT
The maximum classification allowed on GCWiki is TOP SECRET STRAP1 COMINT. Click to
report inappropriate content.
Published in the Same Report
(10 documents)
-
SIGINT Obtains Details of Usama bin Laden Message to Top al-Qa'ida Leader in Iraq SIDtoday [pdf]
A 2007 NSA SIDtoday article describing how SIGINT analysts intercepted and decoded a message from Osama bin Laden to al-Qaeda's leader in Iraq, revealing bin Laden's strategic thinking on the Iraq war, his anger toward the UAE, and the communications pathway used by senior al-Qaeda figures between Pakistan, Iran, and Iraq.
Programs: SCQAWK -
What Does the Death of Usama bin Laden Mean? SIDtoday [pdf]
A 2011 NSA SIDtoday interview with SID's Associate Deputy Director for Counterterrorism assessing the significance of Osama bin Laden's death, revealing that NSA played a central role in identifying his compound and providing force-protection support during the SEAL raid, while also disclosing that bin Laden had been invisible to SIGINT since 1998.
Programs: SCQAWK -
SIGINT Year in Review, November 2011 SIDtoday [pdf]
A 2011 year-in-review message from NSA SIGINT Director Teresa Shea summarizing the directorate's major operational and capability accomplishments over the past year, including SIGINT contributions to the killing of Osama bin Laden, operations against Anwar al-Awlaki and other al-Qaeda figures, and support for military campaigns and crises across the Middle East.
Programs: SCQAWK -
FY2013 Congressional Budget Justification Bin Laden Excerpts [pdf]
This document includes excerpts from the 2013 National Intelligence Program budget justification describing the integrated intelligence community efforts that led to locating and raiding Osama bin Laden's compound, detailing contributions from NSA's signal intelligence, CIA's geolocation analysis, NGA's imagery modeling, and post-raid forensic DNA confirmation.
People: bin Laden, Osama -
NCTC Current Status of Major Terrorism Figures [pdf]
A TOP SECRET joint HUMINT–COMINT status report from June 2008 summarizes the whereabouts and threat posture of senior al‑Qaida leaders, highlighting Usama bin Ladin, Ayman al‑Zawahiri, and a key courier assessed as critical to locating them. The document reflects U.S. intelligence tracking priorities just three years before bin Ladin’s death.
-
Interview with a SID "Hacker" -- Part 2: Hacker Culture and Worker Retention SIDtoday [pdf]
A SIDtoday internal NSA newsletter interview with a redacted TAO employee discussing hacker culture within the agency's offensive cyber unit, worker retention challenges, and the team's role in operations including the raid that killed Osama bin Laden.
Programs: SCQAWKPeople: bin Laden, Osama -
Regional Command Southwest Intelligence Report June 19 2011 [pdf]
A June 2011 intelligence summary from Regional Command Southwest in Afghanistan assessing the destabilizing aftermath of the Osama bin Laden raid on U.S.-Pakistan relations, Pakistani internal security, Taliban activity along the RC(SW) border, and local governance developments in Helmand Province.
-
Regional Command Southwest Intelligence Report June 23 2011 [pdf]
A June 2011 RC Southwest intelligence summary documenting a covert ALP-Taliban collusion arrangement in Nad'Ali district, and a separate intelligence report detailing Taliban internal supply shortages, infighting, and morale deterioration across northern Helmand Province in the aftermath of Osama bin Laden's death.
-
June 2011 Nato Afghanistan Intelligence Report [pdf]
A June 2011 SHAPE weekly report to NATO HQ assessing the state of ISAF operations in Afghanistan, covering Taliban command and control deterioration, insurgent supply shortages, the post-bin Laden strain on NATO's Pakistani logistics routes, and notable attacks across regional commands.
Marking: NATO SECRET -
May 2011 Nato Afghanistan Intelligence Report [pdf]
A May 2011 SHAPE weekly report to NATO HQ assessing ISAF operations in Afghanistan — including a major failed Taliban spring offensive in Kandahar, insurgent cache dispersal tactics, and the limited impact of bin Laden's death on Taliban operational capacity — alongside an update on Operation Unified Protector in Libya covering the Misrata siege and Gaddafi regime military activity.
Marking: NATO SECRET
Related Documents
-
Reverse Engineering – GCHQ Wiki [pdf]
GCHQ’s internal GCWiki page sketches the TEA Reverse Engineering unit inside the TECA Product Centre: a lab team built to dissect hardware and embedded crypto devices, defeat smartcard‑class microprocessors, and turn black boxes into SIGINT‑ready emulators. It doubles as a training hub and liaison node, with kit lists, tours, and SRE exchanges—most real work pushed behind higher‑compartment CAWiki pages.
Marking: UK SECRETPrograms: RUSSETT -
FININT Tasking [pdf]
This document outlines GCHQ's financial intelligence (FININT) operations, detailing the use of tools like LUCKY STRIKE and LUCKY ESCAPE to search and fuse datasets from financial and travel sources. It also describes procedures for requesting financial checks on individuals and mentions the collection of bulk banking and credit card data from specific regions.
Programs: TRACFIN · LUCKY STRIKE · LUCKY ESCAPE · TAPERLAY · TMM · MOON RAKER · BROADOAK · FININTTRACKER · FINTOOLS · FOLLOWTHEMONEY · PLATINUMPLUS · RUSSETT -
PHANTOM PARROT [pdf]
This document discusses PHANTOM PARROT, a GTAC tool used for querying mobile phone data collected from individuals stopped at UK ports as part of the ITT Op WILDWAY initiative. The tool allows intelligence analysts to access phonebook, SMS, and call log data from these stops, which can be used for counter-terrorism efforts. Data is obtained under the Terrorism Act 2000, and the tool is part of a broader intelligence-gathering effort, eventually to be integrated into the LUCKY STRIKE project.
Programs: PHANTOM PARROT · WILDWAY · RANNOCH MOOR · LUCKY STRIKE · LOOKING GLASS · DISHFIRE · CORINTH · MOONRAKER · RUSSETT -
Operational Legalities – GCHQ Powerpoint Presentation [pdf]
GCHQ’s “Operational Legalities” deck is an internal compliance playbook that translates the UK’s surveillance laws into day‑to‑day SIGINT procedure—drilling staff on authorisation, necessity, and proportionality, and walking through warrants, targeting justifications, database queries, dissemination, and oversight. Half slides and half speaker notes, it shows how analysts are trained to document, audit, and defend operations under ISA, RIPA, HRA, and WTA while navigating edge cases like location, nationality, second‑party constraints, and “indirect targeting.”
-
TECA Product Centre — Wiki [pdf]
The TECA Product Centre is a GCHQ unit, within the Technical Enabling Covert Access group (TEA), whose mission is to develop and exploit specialist technologies and physical access methods to gain intelligence or SIGINT access where conventional methods fail. It works closely with SIS (MI6) on technical operations and deployment, offering bespoke managed services rather than direct products.