Country: Canada 55 documents
Search documents matching “Canada” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Event RARE weekly summaries [pdf]
This document outlines GCHQ's ongoing surveillance efforts in Libya, focusing on intercepting and analyzing communications from the Libyan regime, including military command and control via mobile satellite phones and other communication channels. It details the use of advanced SIGINT tools and close cooperation with the NSA, US, and Canadian intelligence agencies to monitor key military targets and opposition forces, supporting both tactical military operations and strategic intelligence objectives.
People: Gaddafi, Muammar -
FAD FY 12 CCP Funding of Partners [pdf]
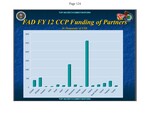
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
First-Ever Formal SIGINT Development (SIGDEV) Training Is Provided to SIGINT Seniors Europe (SSEUR) Partners [pdf]
This internal NSA report details the first formal training course on "SIGINT Development" (SIGDEV) offered to the "SIGINT Seniors Europe" (SSEUR) coalition, a group comprising the Five Eyes nations and nine European third-party partners. The document highlights the strategic goal of standardizing analytic tradecraft among these allies to improve collaboration on priority missions like counter-terrorism and the war in Afghanistan.
“New NSA Revelations: Inside Snowden's Germany File” - Der Spiegel ↗ (2014-06-18) · “Read the Snowden Documents From the NSA” - SVT Nyheter ↗ (2013-12-11) · Becker, Sven · Gude, Hubert · Horchert, Judith · Müller-Maguhn, Andy · Poitras, Laura · Reißmann, Ole · Rosenbach, Marcel · Schindler, Jörg · Schmid, Fidelius · Sontheimer, Michael · Stark, Holger · Björklund, Axel -
FISA Amendments Act of 2008 Section 702 summary document [pdf]
This document summarizes the way the law works and describes the three types of certifications used to permit the surveillance, as well as targeting and minimization procedures. The three certification are for foreign governments, counterterrorism and WMD/proliferation.
-
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
INTOLERANT – Who Else Is Targeting Your Target? Collecting Data Stolen by Hackers – SIDtoday SIDtoday [pdf]
A TOP SECRET SIDToday article from Menwith Hill Station describing how NSA and CSEC discovered and began exploiting INTOLERANT — a sophisticated email-stealing hacking operation targeting Indian diplomats, Central Asian diplomats, Chinese human rights defenders, Tibetan pro-democracy activists, Uighur activists and European officials — by intercepting the stolen emails as they transited satellite links, a technique internally called "fourth party collection" or "outsourcing SIGINT."
Programs: INTOLERANT -
LEVITATION and the FFU Hypothesis [pdf]
This document describes LEVITATION, a top-secret Canadian Communications Security Establishment (CSE) project that monitors millions of daily file uploads and downloads from free file-sharing sites to identify potential extremist activity. It details the program’s data collection methods, analytical workflow, use of partner databases, and examples of successful discoveries related to terrorist materials and hostage videos.
-
Linguistic Resource Sharing in Asia-Pacific Region Takes Step Forward SIDtoday [pdf]
This document highlights a significant development in linguistic resource sharing within the Asia-Pacific region, where NSA Hawaii initiated the first successful voice cut exchange among SIGINT Seniors Pacific (SSPAC) members in June 2007. The use of the CRUSHED ICE data-sharing network to facilitate this exchange marks a key step in enhancing collaborative counterterrorism efforts by expanding the linguistic resources available for terrorist communications analysis.
Programs: CRUSHEDICE -
Memorandum Of Understanding between the NSA/CSS and the Israeli Sigint National Unit (ISNU) [pdf]
This document is a highly classified Memorandum of Understanding (MOU) between the NSA and the Israeli SIGINT National Unit (ISNU) regarding the sharing of raw, unminimized Signals Intelligence (SIGINT). The agreement establishes formal procedures to protect the privacy rights of U.S. persons contained within the data provided by the U.S. to Israel. While it mandates the "masking" of U.S. identities in Israeli reports, it notably allows Israel to receive and process massive streams of unevaluated data—including metadata and content—before the NSA has reviewed or filtered it.
Programs: CHIPPEWA -
Mobile apps doubleheader: BADASS Angry Birds [pdf]
A joint GCHQ/GTE/CSEC presentation describing BADASS — the BEGAL Automated Deployment and Survey System for rapidly developing and deploying mobile app exploitation rules — illustrated through detailed analysis of Angry Birds' Dataflurry analytics traffic leaking IMEI, IMSI, cell network metadata and device identifiers, alongside AdMob, Mobclix and Mydas ad network traffic leaking UDIDs and IMEIs across iOS, Android, BlackBerry and Windows Phone 7 platforms.
Programs: BADASS · BEGAL · SEM · UNIQUELYCHALLENGED · BLACKHOLE · MOUNTAINVIEW · VOB · BABELFISH · BISHOP · MVR · PPF · AEG · DATAFLURRY -
NSA CSEC Partnership [pdf]
This NSA paper outlines the long-standing intelligence partnership between the U.S. and Canada’s Communications Security Establishment Canada (CSEC), dating back to WWII. It highlights mutual SIGINT cooperation, shared technological resources, and the role of CSEC in cryptography, cyber defense, and intelligence sharing, particularly in high-priority global and transnational targets.
-
NSA document on targeting Five Eyes countries and territories [pdf]
This document states that the National Security Agency is prohibited from conducting foreign surveillance on the "Five Eyes" countries, which include U.S. allies Australia, Canada, New Zealand and the United Kingdom, or their territories.
-
NSA Intelligence Relationship with New Zealand [pdf]
An April 2013 NSA information paper on the SIGINT relationship with New Zealand's GCSB, listing what each side provides: GCSB collection on China, Japanese, North Korean, Vietnamese and South American diplomatic communications, South Pacific Island nations, Pakistan, India, Iran, Antarctica and French police and nuclear testing activities in New Caledonia, and its role since 2004 as the Intelligence Community's lead on the Bangladesh counterterrorism target. It also covers GCSB's operational lead on cyber, the compliance review that followed its assistance to New Zealand law enforcement under Director Ian Fletcher, and its term as chair of SIGINT Seniors Pacific (SSPAC).
People: Fletcher, Ian“Snowden revelations: Nicky Hager and Ryan Gallagher: New Zealand's spy reach stretches across globe” - The New Zealand Herald ↗ (2015-03-11) · “New Zealand Targets Trade Partners, Hacks Computers in Spy Operations” - The Intercept ↗ (2015-03-10) · “Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · “New Zealand Spy Data Shared With Bangladeshi Human Rights Abusers” - The Intercept ↗ (2015-04-15) · “Secret documents shine light on GCSB spying in Bangladesh” - The New Zealand Herald ↗ (2015-04-16) · Hager, Nicky · Gallagher, Ryan · Fisher, David -
NSA’s intelligence relationship with Australia [pdf]
This document summarizes the close intelligence partnership between the U.S. NSA and Australia’s Defence Signals Directorate (DSD), highlighting collaboration on cyber operations, SIGINT collection, and military support. It emphasizes Australia’s contributions through satellite access, geolocation, and terrorism-related communications, particularly in the Pacific region, while noting shared focus on China and joint participation in multinational intelligence coalitions.
-
Operational Legalities – GCHQ Powerpoint Presentation [pdf]
GCHQ’s “Operational Legalities” deck is an internal compliance playbook that translates the UK’s surveillance laws into day‑to‑day SIGINT procedure—drilling staff on authorisation, necessity, and proportionality, and walking through warrants, targeting justifications, database queries, dissemination, and oversight. Half slides and half speaker notes, it shows how analysts are trained to document, audit, and defend operations under ISA, RIPA, HRA, and WTA while navigating edge cases like location, nationality, second‑party constraints, and “indirect targeting.”
-
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel