Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Frankly Speaking: Capturing Zarqawi's Laptop SIDtoday [pdf]
Announcement of a presentation on the NSA's part in collaborating with the intelligence community on the capture of jihadi Abu Musab al-Zarqawi's laptop.
People: al-Zarqawi, Abu MusabThe Intercept ↗ (2017-09-13) -
Free File Uploaders [pdf]
This 2009 NSA training presentation for the XKEYSCORE system details how analysts can monitor Free File Uploader (FFU) websites like Zshare and RapidShare, which are difficult to track due to a lack of strong selectors. The guide introduces the "Web File Transfer" plug-in, a specialized tool designed to extract key metadata like original filenames and download/delete links from FFU web traffic.
-
From the SID Mailbag: When To Mark Things 'COMINT' SIDtoday [pdf]
The COMINT (Communications Intelligence) classification marking, along with Special Intelligence, often refers to information derived from foreign communications. However, the marking can also be used for “SIGINT equities that support the production of Communications Intelligence.” For example, secret information-sharing arrangements with foreign governments are classified SI, because these relationships lead to the acquisition of foreign communications.
Programs: ITISThe Intercept ↗ (2018-03-01) -
Full Log vs HTTP [pdf]
This 2009 NSA training presentation explains the difference between using the "Full Log" and "HTTP Activity" queries in the XKEYSCORE surveillance system, showing analysts how to use both in tandem to gain a complete picture of a target's online activities, including identifying the use of anonymizing proxies.
-
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
FY 2013 Congressional Budget Justification, Volume I, National Intelligence Program Summary, February 2012 [pdf]
This document outlines the $52.6 billion “black budget,” detailing the structure, priorities, successes, and shortcomings of the 16 U.S. intelligence agencies. It reveals unprecedented insight into funding allocations, operations, and intelligence gaps—including the CIA’s dominant role, expanding cyber operations, and persistent challenges in areas such as North Korea and counterterrorism—while emphasizing the tension between secrecy and public accountability.
-
-
-
FY2013 Congressional Budget Justification Bin Laden Excerpts [pdf]
This document includes excerpts from the 2013 National Intelligence Program budget justification describing the integrated intelligence community efforts that led to locating and raiding Osama bin Laden's compound, detailing contributions from NSA's signal intelligence, CIA's geolocation analysis, NGA's imagery modeling, and post-raid forensic DNA confirmation.
People: bin Laden, Osama -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
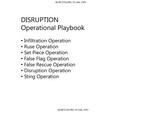
GCHQ - DISRUPTION Operational Playbook [pdf]
A JTRIG “Disruption Operational Playbook” outlines GCHQ’s online covert action toolkit to discredit people and companies, manipulate narratives, and execute false flag, sting, and infiltration operations across targets. It’s a blunt handbook for the four D’s—deny, disrupt, degrade, deceive—translating psychological warfare into clickable tactics on social platforms and forums.
Programs: JTRIG -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
GCHQ access to international internet communications [pdf]
This document describes the scale of the agency's access to international internet communications, stating that GCHQ receives upwards of 50 billion events per day and that this volume is growing.
Programs: GUIDINGLIGHT“The US/UK Campaign to Demonize Social Media Companies as Terrorist Allies” - The Intercept ↗ (2014-11-26) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
GCHQ Analytic Cloud Challenges [pdf]
The 2012 GCHQ Analytic Cloud document outlines a sophisticated data processing infrastructure handling approximately 50 billion daily events across multiple sites, utilizing QFD databases and HADOOP clusters for various analytic capabilities targeting intelligence gathering and analysis. It describes architectural components, challenges in scaling and enabling analysts to cope with data complexity, and proposes future technology options including consolidation approaches and new cloud architectures to enhance capabilities.
Programs: EVOLVEDMUTANTBROTH · MUTANTBROTH · HARDASSOC · HRMAP · KARMAPOLICE · SOCIALANTHROPOID · AUTOASSOC · GEOFUSION · MVR · TERRAIN · SALAMANCA · BLACKHOLE · SAMUELPEPYS · BROKER · VAIL · GUIDINGLIGHT · FIRSTCONTACT · CLOUDYCOBRA · RUMOURMILL · EVERYASSOC · EVERYPOLICE · EVERYCREATURE · EVERYEAD · EVERYCIPHER · GREYFOX · SILVERFOX · GOLDENAXE · TRIBALCARNEM · PUBLICANEMONE · EPICFAIL · STERLINGMOTH · FOGHORN · LOOKINGGLASS · FIREENGINE · NGGEO · ALPHACENTAURI · CLOUDBASE · ACCUMULO · ASEM · SEM · HAKIM · STREAMING · HBASE · LAUREL · SKINNYCLOUD · HARDY · GCHQCORE -
GCHQ Application for Renewal of Warrant GPW/1160 [pdf]
GCHQ’s 2008 application to renew warrant GPW/1160 seeks blanket cover under ISA section 5 to reverse engineer and modify commercial software—explicitly breaching copyright and licensing—to enable CNE, vulnerability research, and even police forensics. It catalogues concrete ops against web forums, routers, and antivirus, and asserts a novel legal theory blessed by the Intelligence Services Commissioner to immunize intellectual‑property interference.
-
GCHQ Cyber Operations Against Anonymous and Hacktivist Groups [pdf]
The leaked 2012 GCHQ presentation reveals that the agency’s JTRIG unit conducted offensive cyber operations against Anonymous and other hacktivist groups, including DDOS attacks (codenamed “Rolling Thunder”), online infiltration, and covert intelligence collection to disrupt their communications and identify key members.
-
GCHQ – Computer Network Exploitation [pdf]
This document outlines GCHQ’s Computer Network Exploitation (CNE) capabilities, detailing how teams remotely access computers and networks without owners’ consent to gather intelligence, support operations, and conduct effects. It also covers operational tools, techniques, infrastructure, joint working with partners, deconfliction, and challenges such as avoiding detection and meeting increasing intelligence demands.
-
GCHQ – Making network sense of the encryption problem (2011) [pdf]
GCHQ’s Network Analysis Centre convened a 2011 roundtable on “making network sense” of encryption, pushing a metadata-first strategy to triage SSL/TLS, IKE, OpenVPN, and SSH flows, pivot from “seed” indicators, and zero in on targets and subnets worth decrypting. The playbook leans on enrichment, AS-level scoping (explicitly citing Belgacom AS6774 GRX VPNs), and “access optimisation” to collect data pre‑encryption—passively or actively.
Programs: SQUEAL · BEARDEDPIGGY · CLOUD · IRASCIBLEHARE · IRASCIBLERABBIT · IRASCIBLEMOOSE · IRASCIBLEEMITT“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
GCSB access, XKEYSCORE [pdf]
4 p.These documents confirm that GCSB's Waihopai base (IRONSAND) provides Five Eyes partners, including the UK, with both "strong selected data" and a "full-take feed" of communications from the South Pacific via the NSA's XKEYSCORE system, confirming New Zealand's deep integration into the U.S.-led surveillance network despite facing internal issues with GCSB analysts accessing their own national data within NSA databases.
-
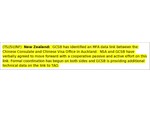
GCSB has identified an MFA data link [pdf]
A short extract from an April 2013 NSA document recording that GCSB had identified a Chinese Ministry of Foreign Affairs data link between the Chinese Consulate and the Chinese Visa Office in Auckland, and that NSA and GCSB had verbally agreed to mount a joint passive and active operation against it.
“Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · Fisher, David · Gallagher, Ryan · Hager, Nicky