GCHQ Cyber Operations Against Anonymous and Hacktivist Groups
Open PDFDocument date: 2012-01-01
Pages: 15
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, AUS, CAN, GBR, NZL
The leaked 2012 GCHQ presentation reveals that the agency’s JTRIG unit conducted offensive cyber operations against Anonymous and other hacktivist groups, including DDOS attacks (codenamed “Rolling Thunder”), online infiltration, and covert intelligence collection to disrupt their communications and identify key members.
My notes
NBCNEWS INVESTIGATIONS investigations.nbcnews.com
The Snowden files: British intelligence agency describes attack on Anonymous
GCHQ, the British signals intelligence agency, prepared the following slides for a top-secret conference in 2012, revealing that it had mounted an online attack on the hacktivist collective known as Anonymous in September 2011.
The slides were leaked by former NSA contractor Edward Snowden and obtained exclusively by NBC News.
NBC News is publishing the documents with minimal redactions to protect individuals. All annotations appear in the original documents prepared by GCHQ.
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
Hacktivism: Online Covert Action
- Hacktivist groups
- Online Humint
- Effects Operations
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
Hacktivist groups
- They are diverse and often have multiple, varied aims
- Anonymous
- LulzSec
- A-Team
- Syrian Cyber Army
- Targets include: Corporations, banks, governments, copyright associations, political parties
- Techniques: DDoS, data theft – SQLi, social engineering
- Aims:
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
Online HUMINT -CHIS
- 2 Examples from Anonymous IRC Channels:
- Gzero
- P0ke
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
Gzero & [REDACTED]
- Asking for traffic
- Engaged with target
- Discovered Botnet with malware analysis & SIGINT
- Outcome: Charges, arrest, conviction
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
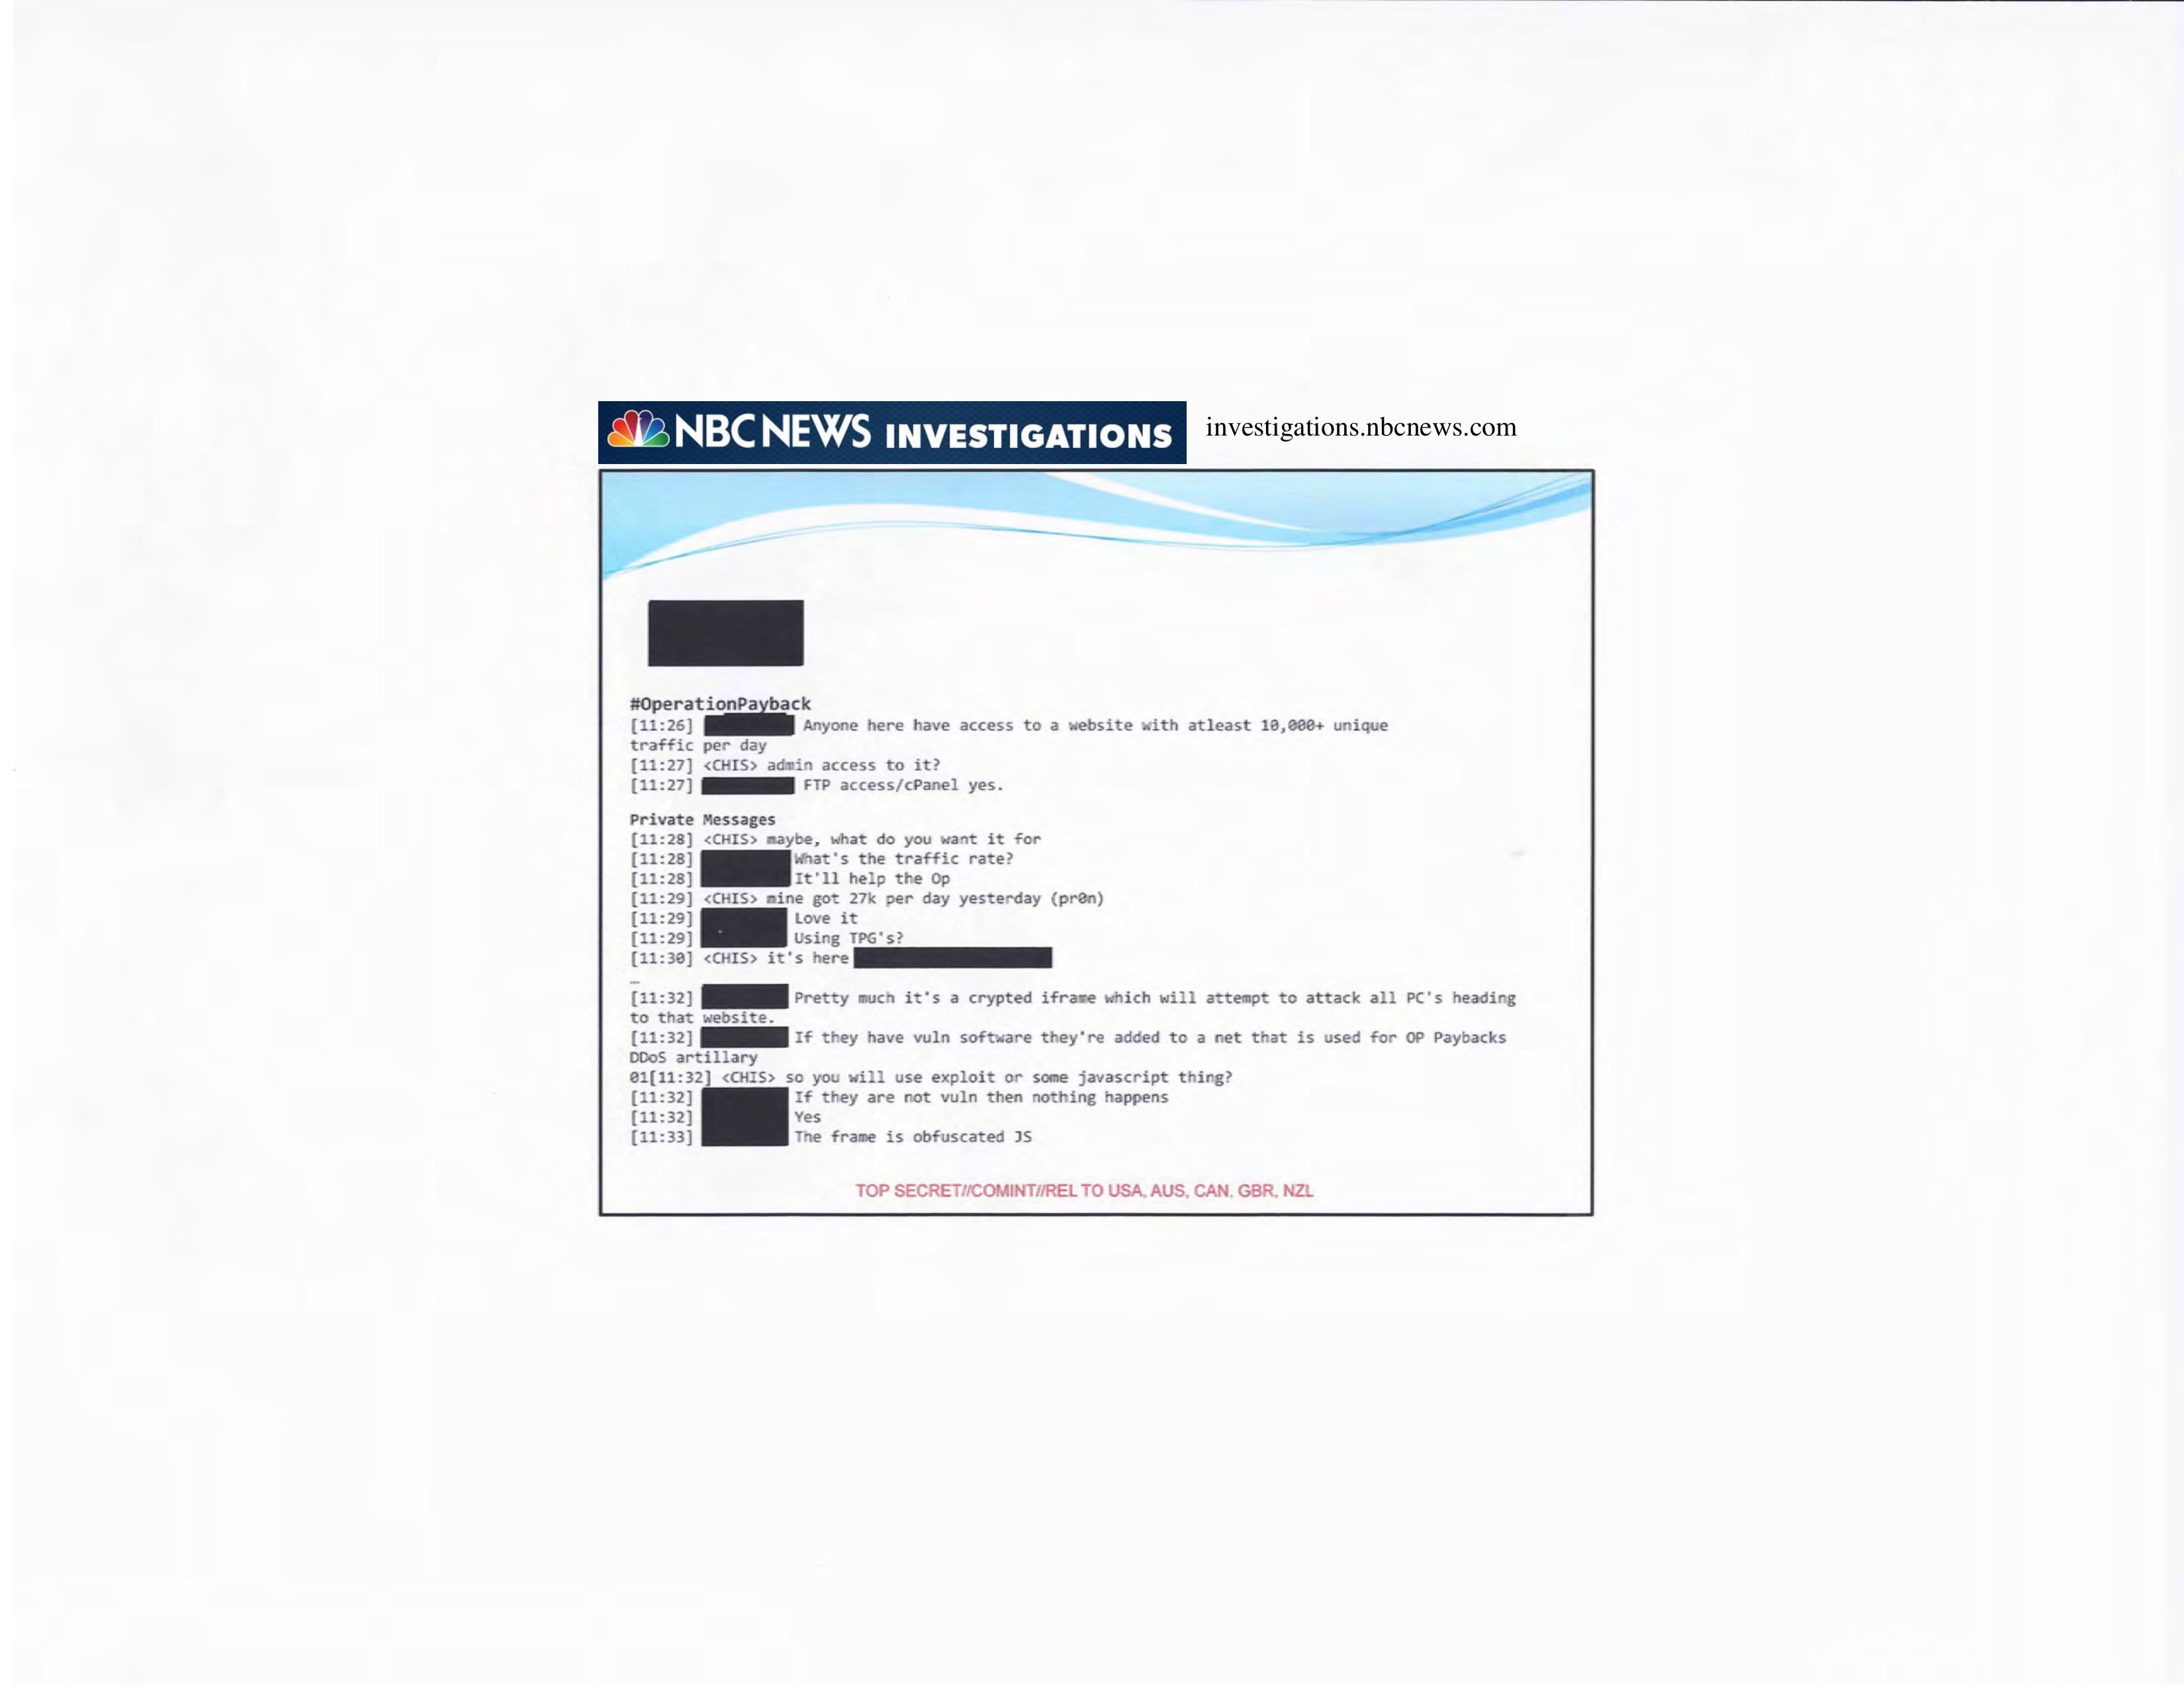
[REDACTED]
# OperationPayback
[11:26] [REDACTED] Anyone here have access to a website with atleast 10,000+ unique traffic per day
[11:27] <CHIS> admin access to it?
[11:27] [REDACTED] FTP access/cPanel yes.

Private Messages
[11:28] <CHIS> maybe, what do you want it for
[11:28] [REDACTED] What's the traffic rate?
[11:28] [REDACTED] It'll help the Op
[11:29] <CHIS> mine got 27k per day yesterday (pr0n)
[11:29] [REDACTED] Love it
[11:29] [REDACTED] Using TPG's?
[11:30] <CHIS> it's here [REDACTED]
[11:32] [REDACTED] Pretty much it's a crypted iframe which will attempt to attack all PC's heading to that website.
[11:32] [REDACTED] If they have vuln software they're added to a net that is used for OP Paybacks DDoS artillary
01[11:32] <CHIS> so you will use exploit or some javascript thing?
[11:32] [REDACTED] If they are not vuln then nothing happens
[11:32] [REDACTED] Yes
[11:33] [REDACTED] The frame is obfuscated JS
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
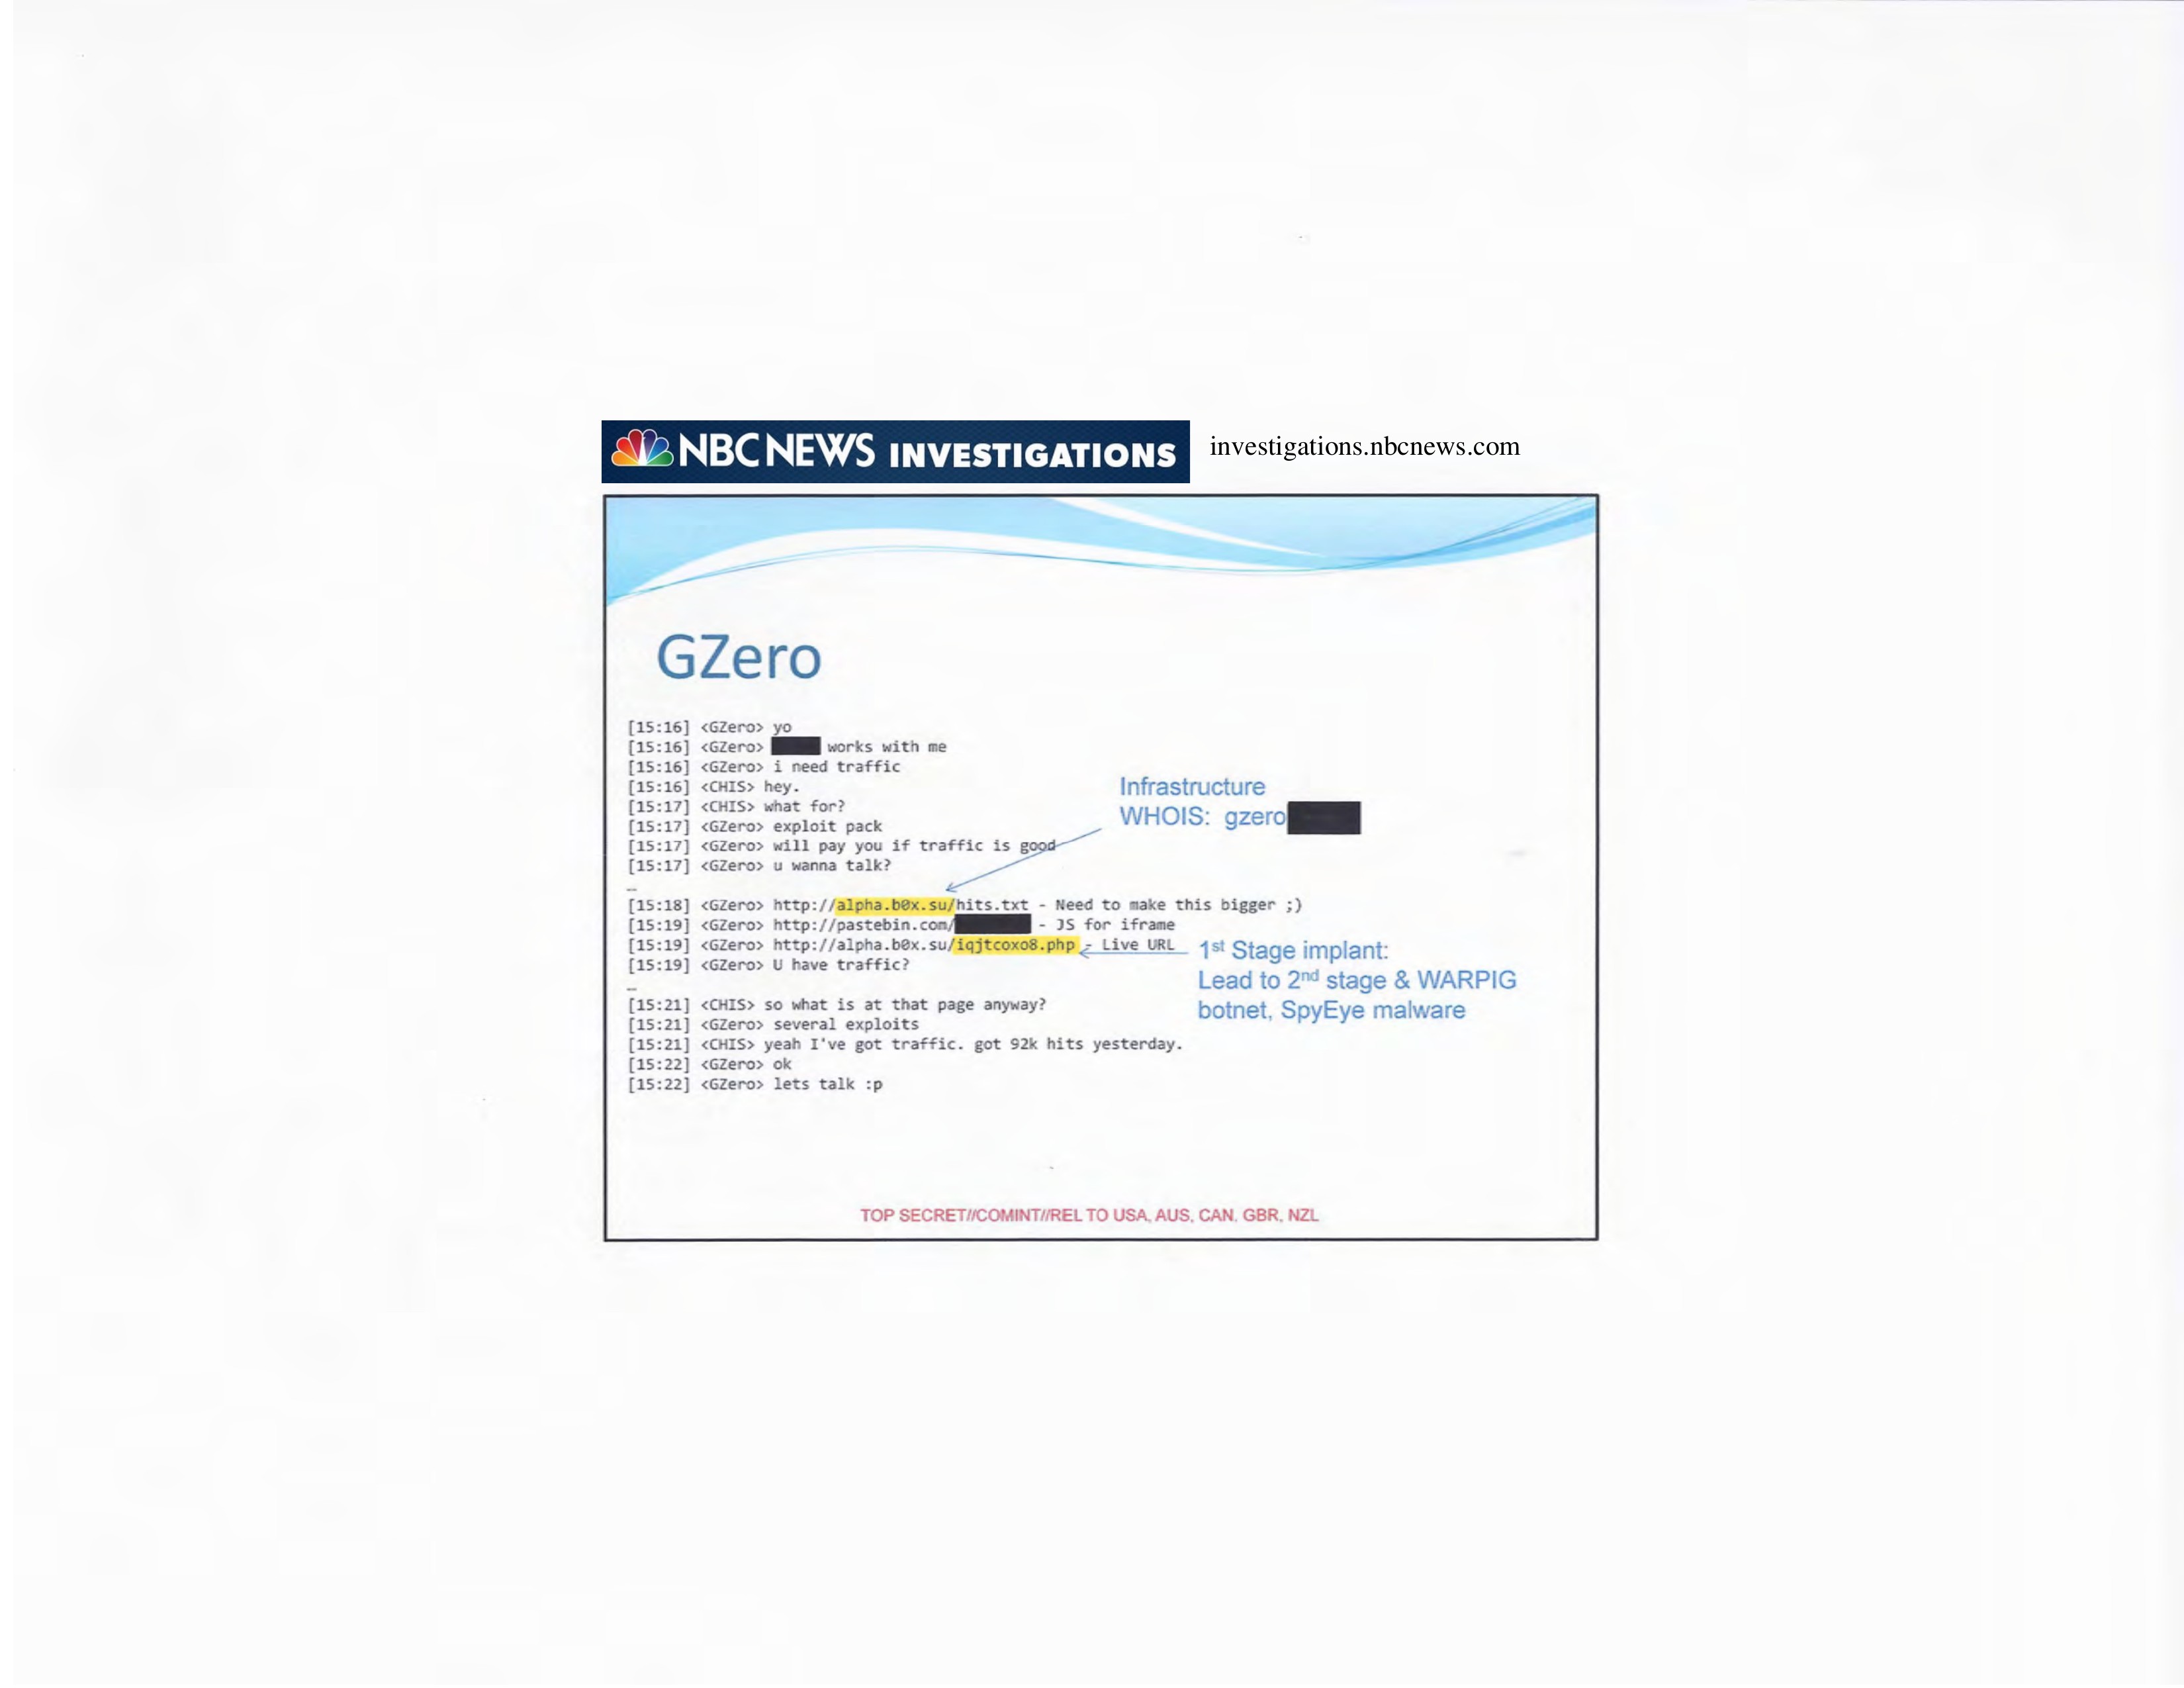
GZero
[15:16] <GZero> yo
[15:16] <GZero> [REDACTED] works with me
[15:16] <GZero> i need traffic
[15:16] <CHIS> hey.
[15:17] <CHIS> what for?
[15:17] <GZero> exploit pack
[15:17] <GZero> will pay you if traffic is good
[15:17] <GZero> u wanna talk?

Infrastructure
WHOIS: gzero [REDACTED]

[15:18] <GZero> http://alpha.b0x.su/hits.txt - Need to make this bigger ;)
[15:19] <GZero> http://pastebin.com/[REDACTED] JS for iframe
[15:19] <GZero> http://alpha.b0x.su/iqjtcoxo8.php Live URL
[15:19] <GZero> U have traffic?

1st Stage implant:
Lead to 2nd stage & WARPIG botnet, SpyEye malware

[15:21] <CHIS> so what is at that page anyway?
[15:21] <GZero> several exploits
[15:21] <CHIS> yeah I've got traffic. got 92k hits yesterday.
[15:22] <GZero> ok
[15:22] <GZero> lets talk :p
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
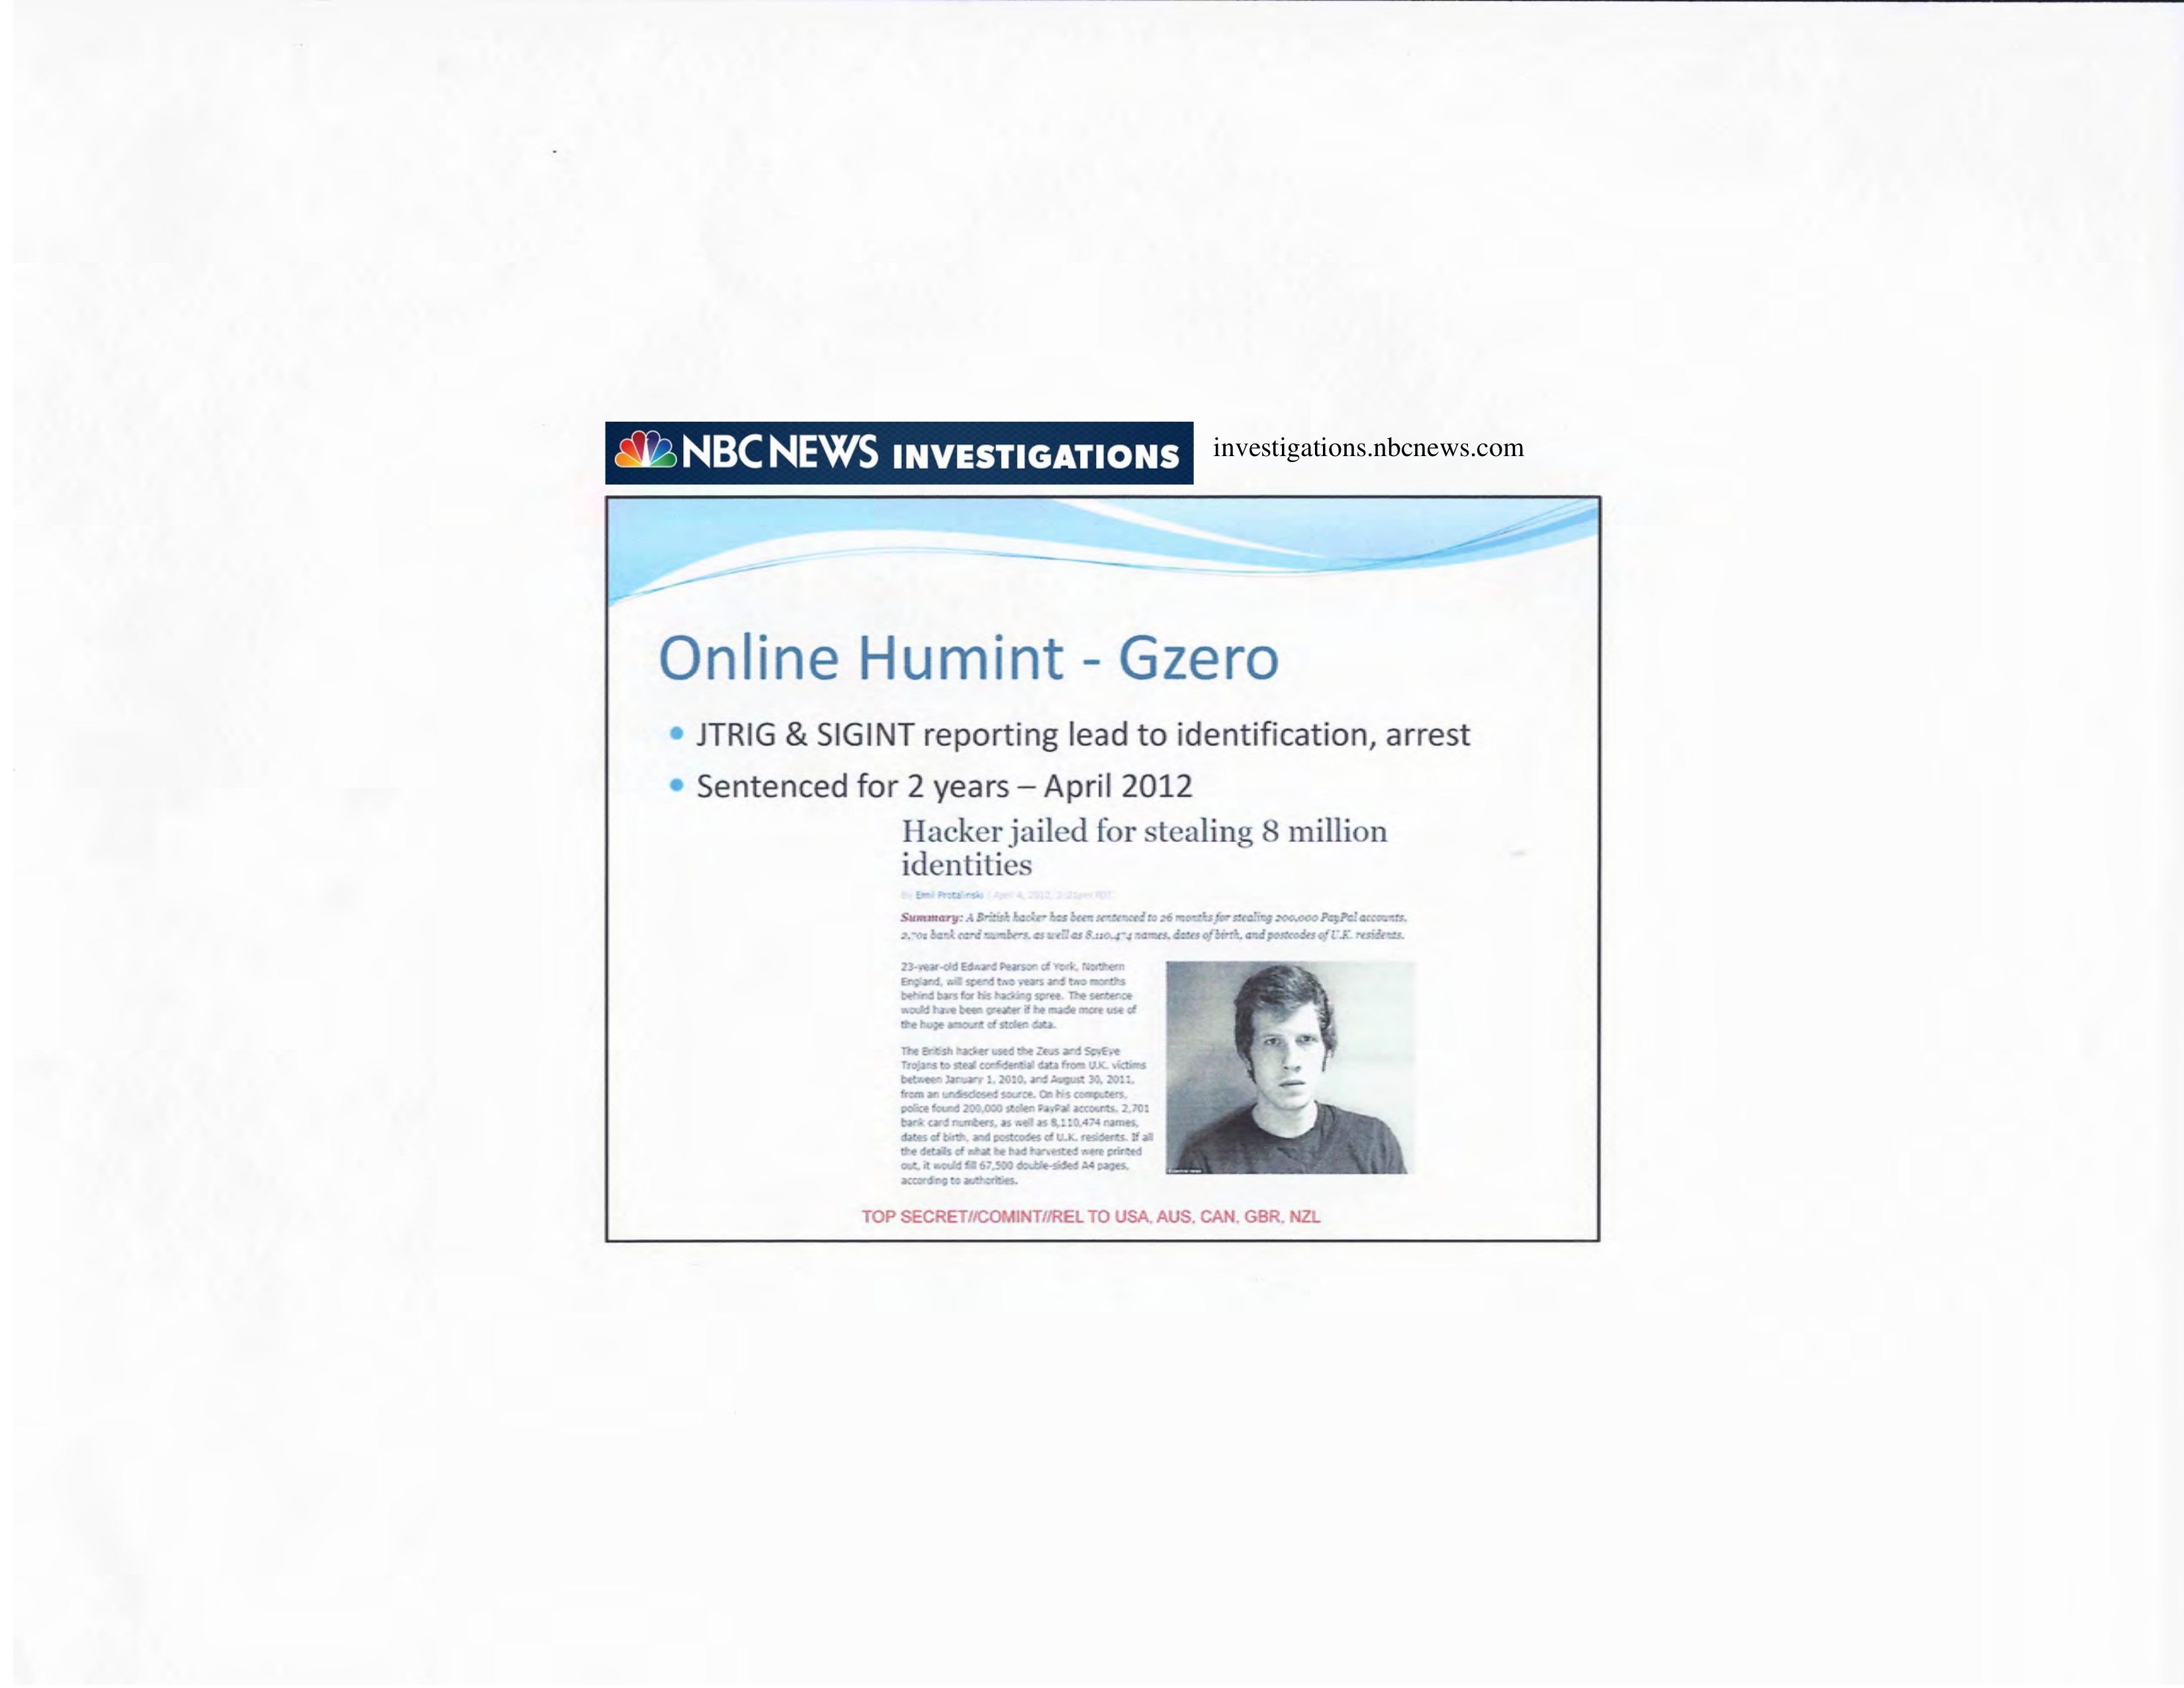
Online Humint - Gzero
- JTRIG & SIGINT reporting lead to identification, arrest
- Sentenced for 2 years - April 2012
Hacker jailed for stealing 8 million identities

By Emil Protalinski | April 4, 2012 | 3:07 PM PDT

Summary: A British hacker has been sentenced to 26 months for stealing 200,000 PayPal accounts, 2,701 bank card numbers, as well as 8,110,474 names, dates of birth, and postcodes of U.K. residents.

23-year-old Edward Pearson of York, Northern England, will spend two years and two months behind bars for his hacking spree. The sentence would have been greater if he made more use of the huge amount of stolen data.

The British hacker used the Zeus and SpyEye Trojans to steal confidential data from U.K. victims between January 1, 2010, and August 30, 2011, from an undisclosed source. On his computers, police found 200,000 stolen PayPal accounts, 2,701 bank card numbers, as well as 8,110,474 names, dates of birth, and postcodes of U.K. residents. If all the details of what he had harvested were printed out, it would fill 67,500 double-sided A4 pages, according to authorities.
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
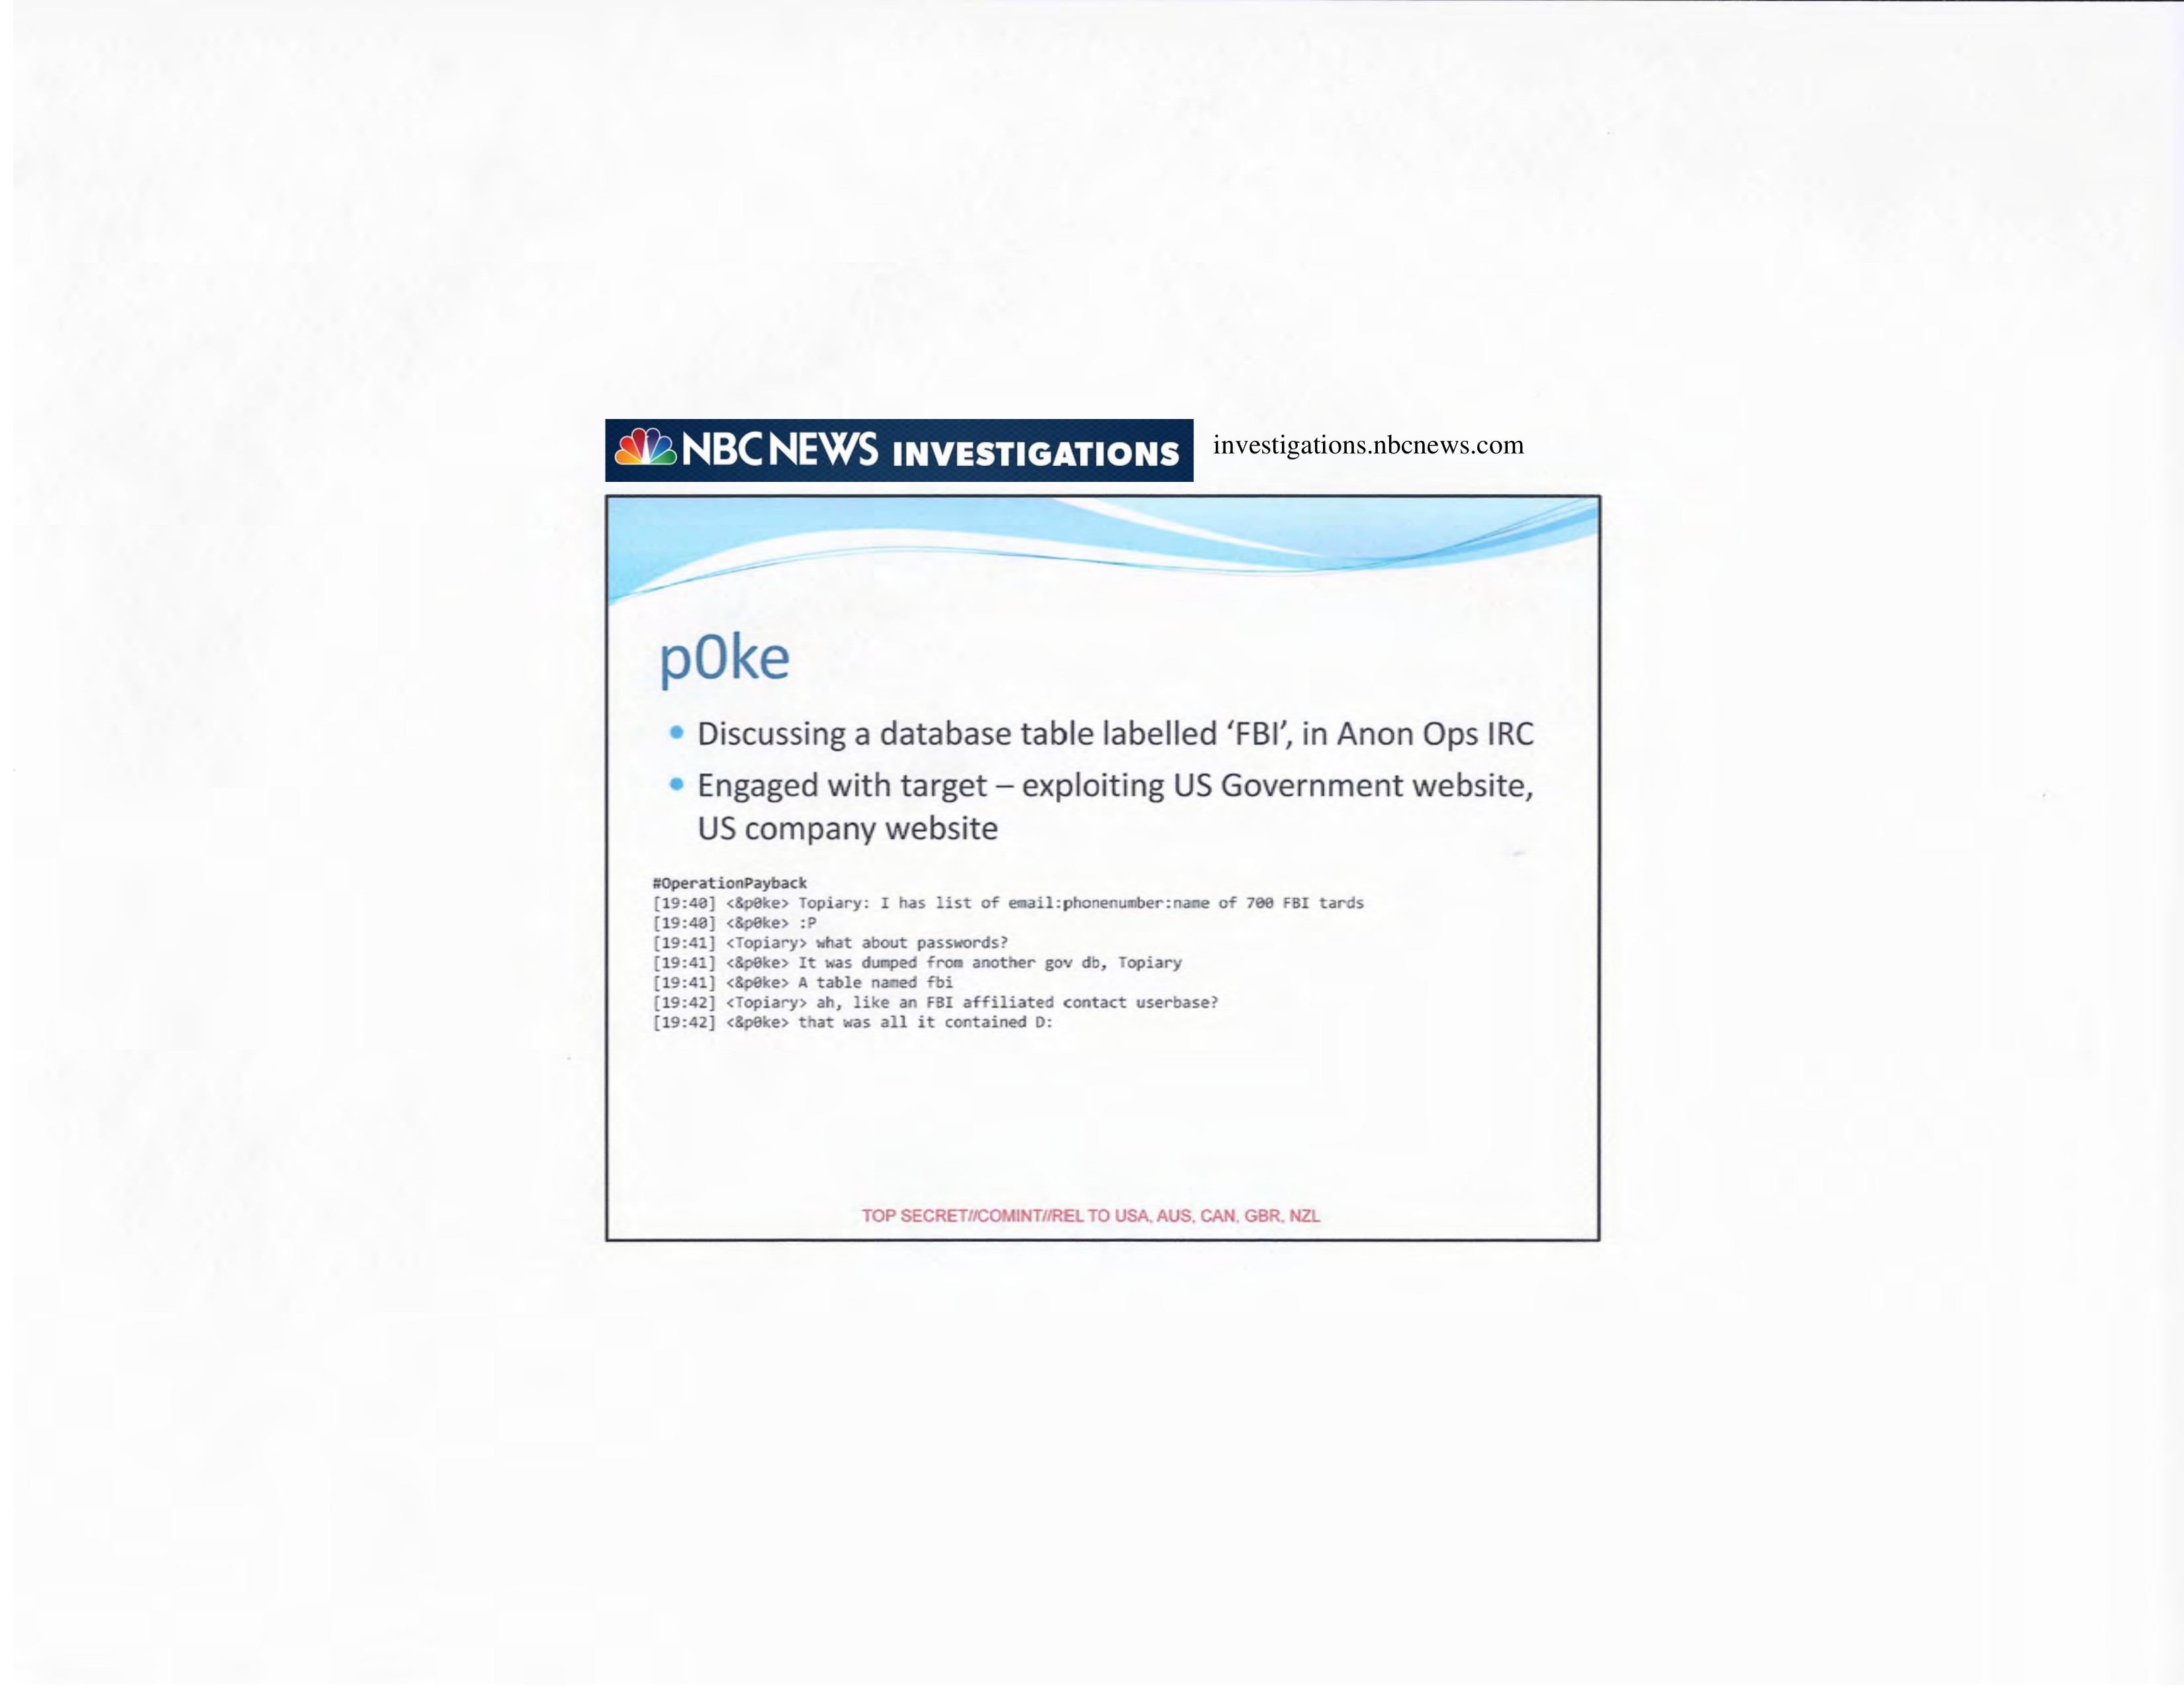
p0ke
- Discussing a database table labelled 'FBI', in Anon Ops IRC
- Engaged with target – exploiting US Government website, US company website
# OperationPayback
[19:40] <&p0ke> Topiary: I has list of email:phonenumber: name of 700 FBI tards
[19:40] <&p0ke> :P
[19:41] <Topiary> what about passwords?
[19:41] <&p0ke> It was dumped from another gov db, Topiary
[19:41] <&p0ke> A table named fbi
[19:42] <Topiary> ah, like an FBI affiliated contact userbase?
[19:42] <&p0ke> that was all it contained D:
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
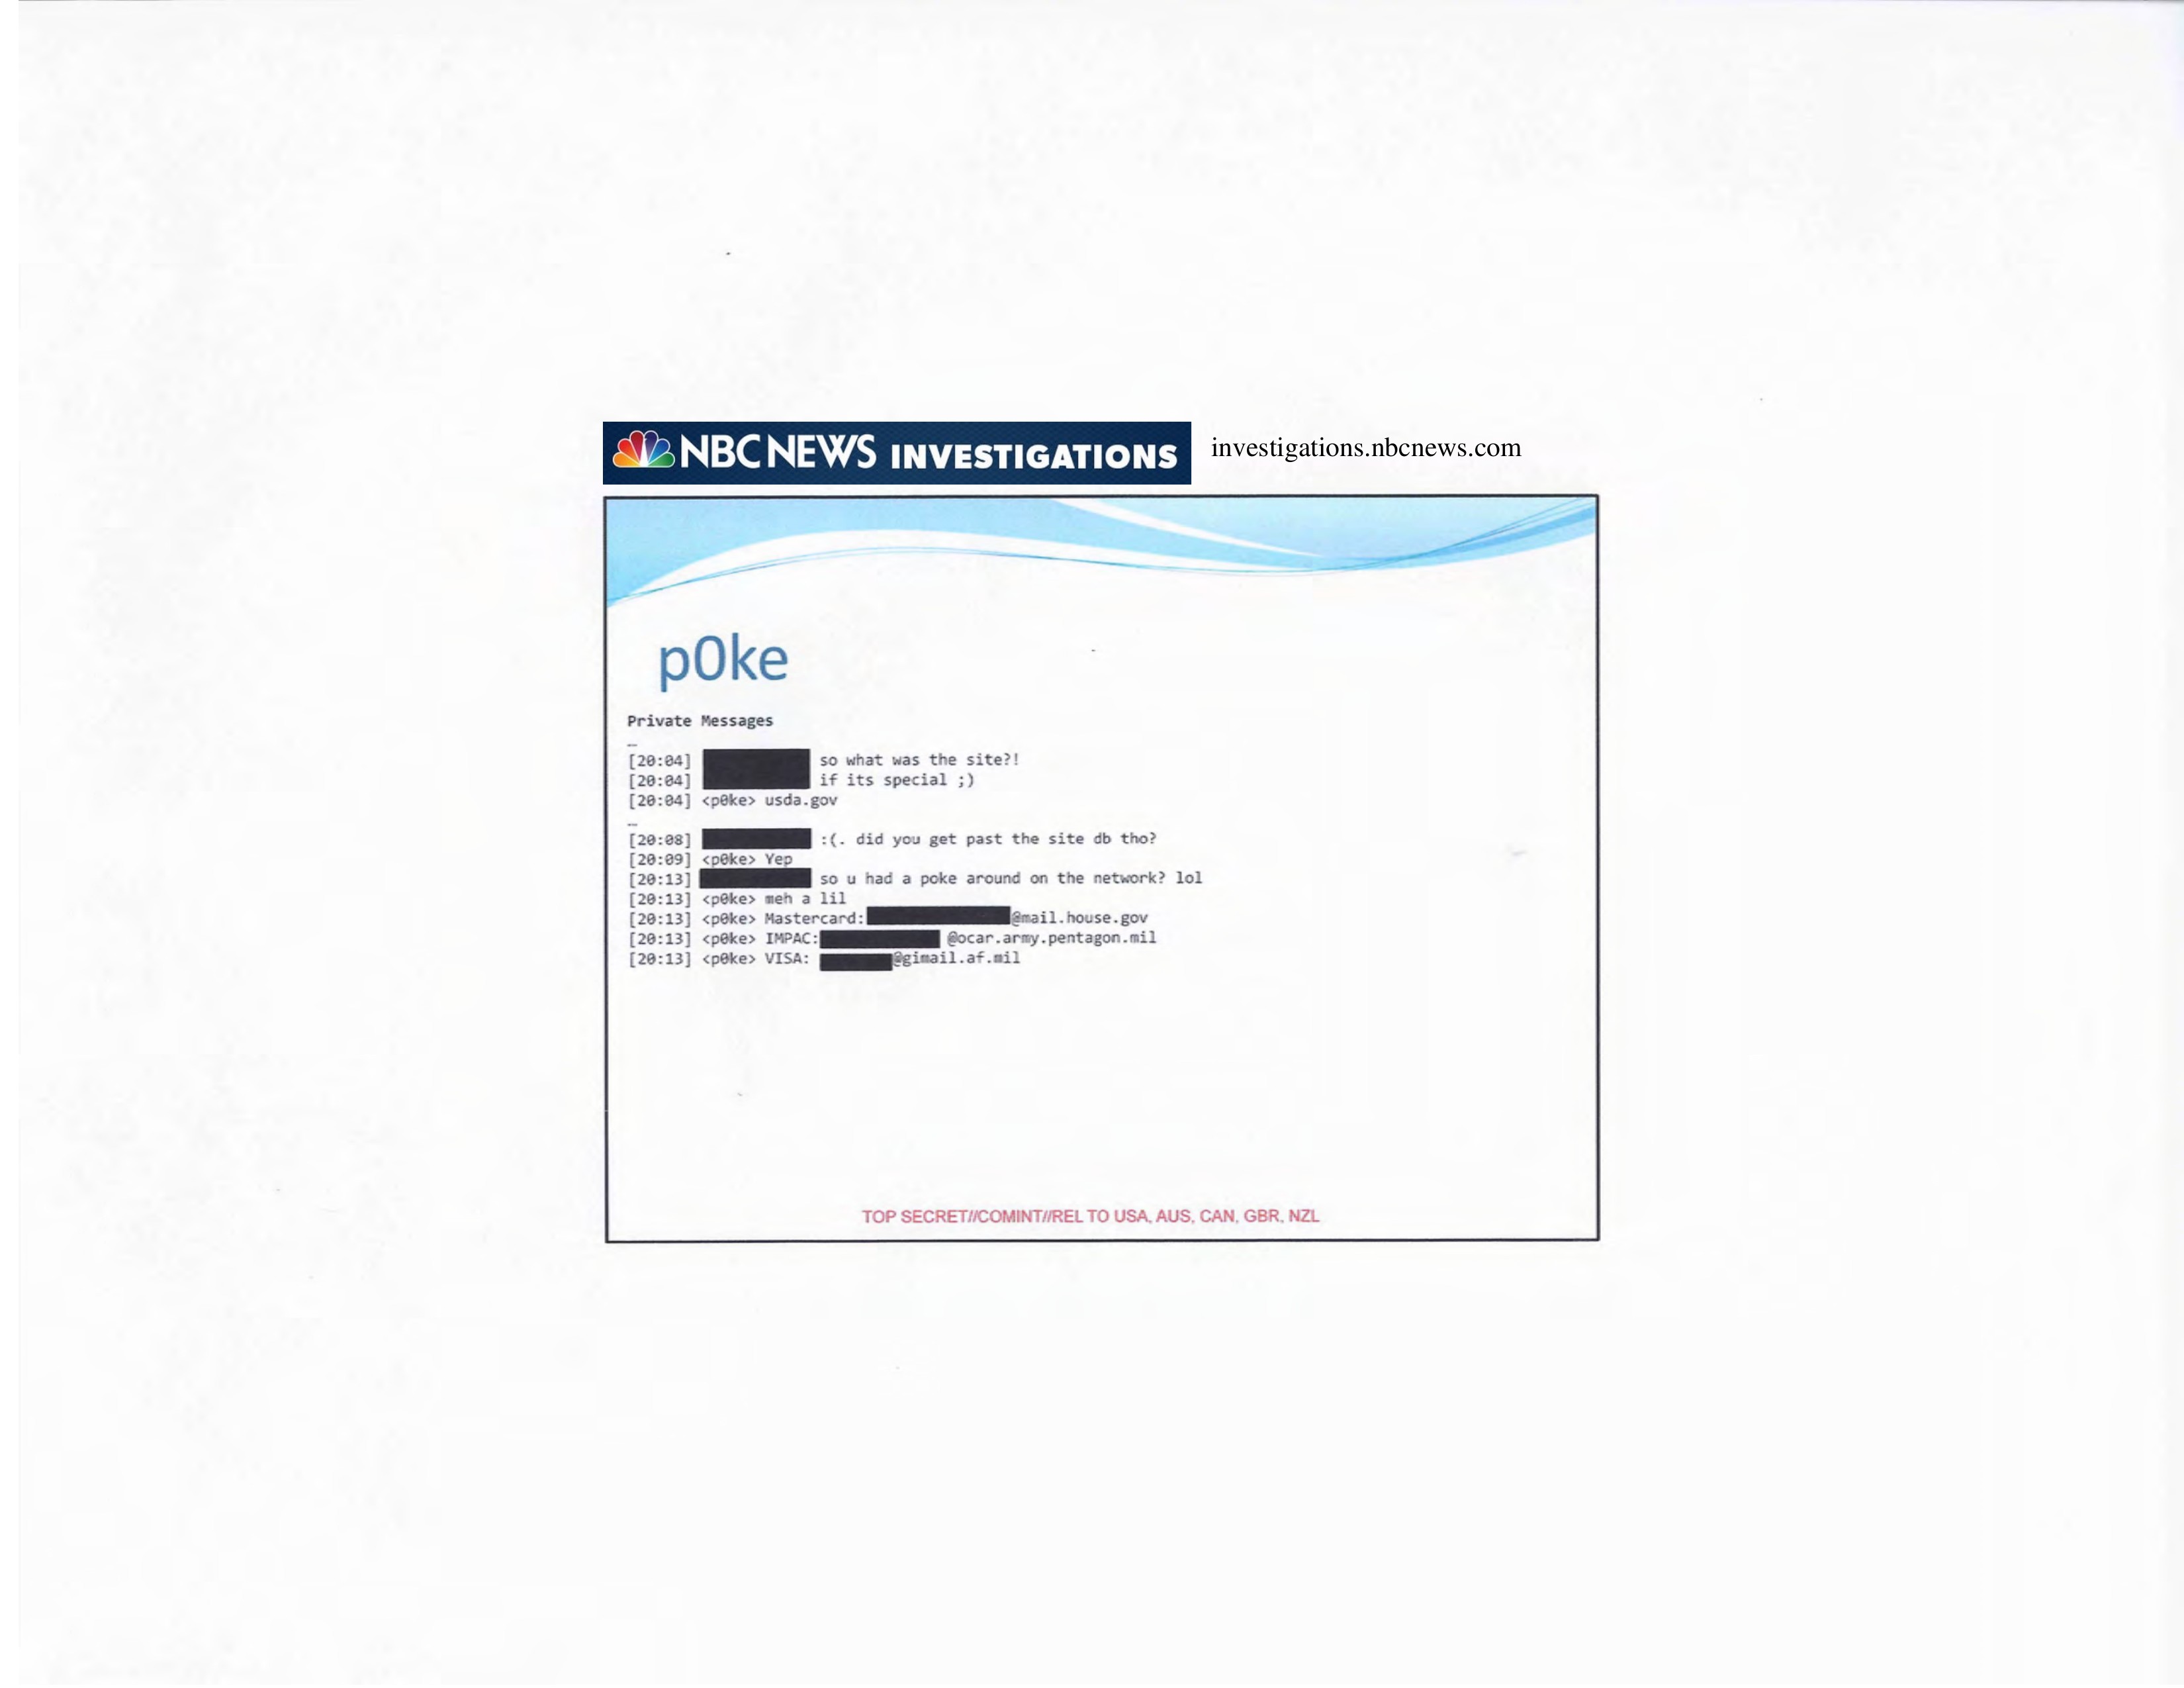
p0ke
Private Messages
[20:04] [REDACTED] so what was the site?!
[20:04] [REDACTED] if its special ;)
[20:04] <p0ke> usda.gov
[20:08] [REDACTED] :(. did you get past the site db tho?
[20:09] <p0ke> Yep
[20:13] [REDACTED] so u had a poke around on the network? lol
[20:13] <p0ke> meh a lil
[20:13] <p0ke> Mastercard: [REDACTED]@mail.house.gov
[20:13] <p0ke> IMPAC: [REDACTED]@ocar.army.pentagon.mil
[20:13] <p0ke> VISA: [REDACTED]@gimail.af.mil
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
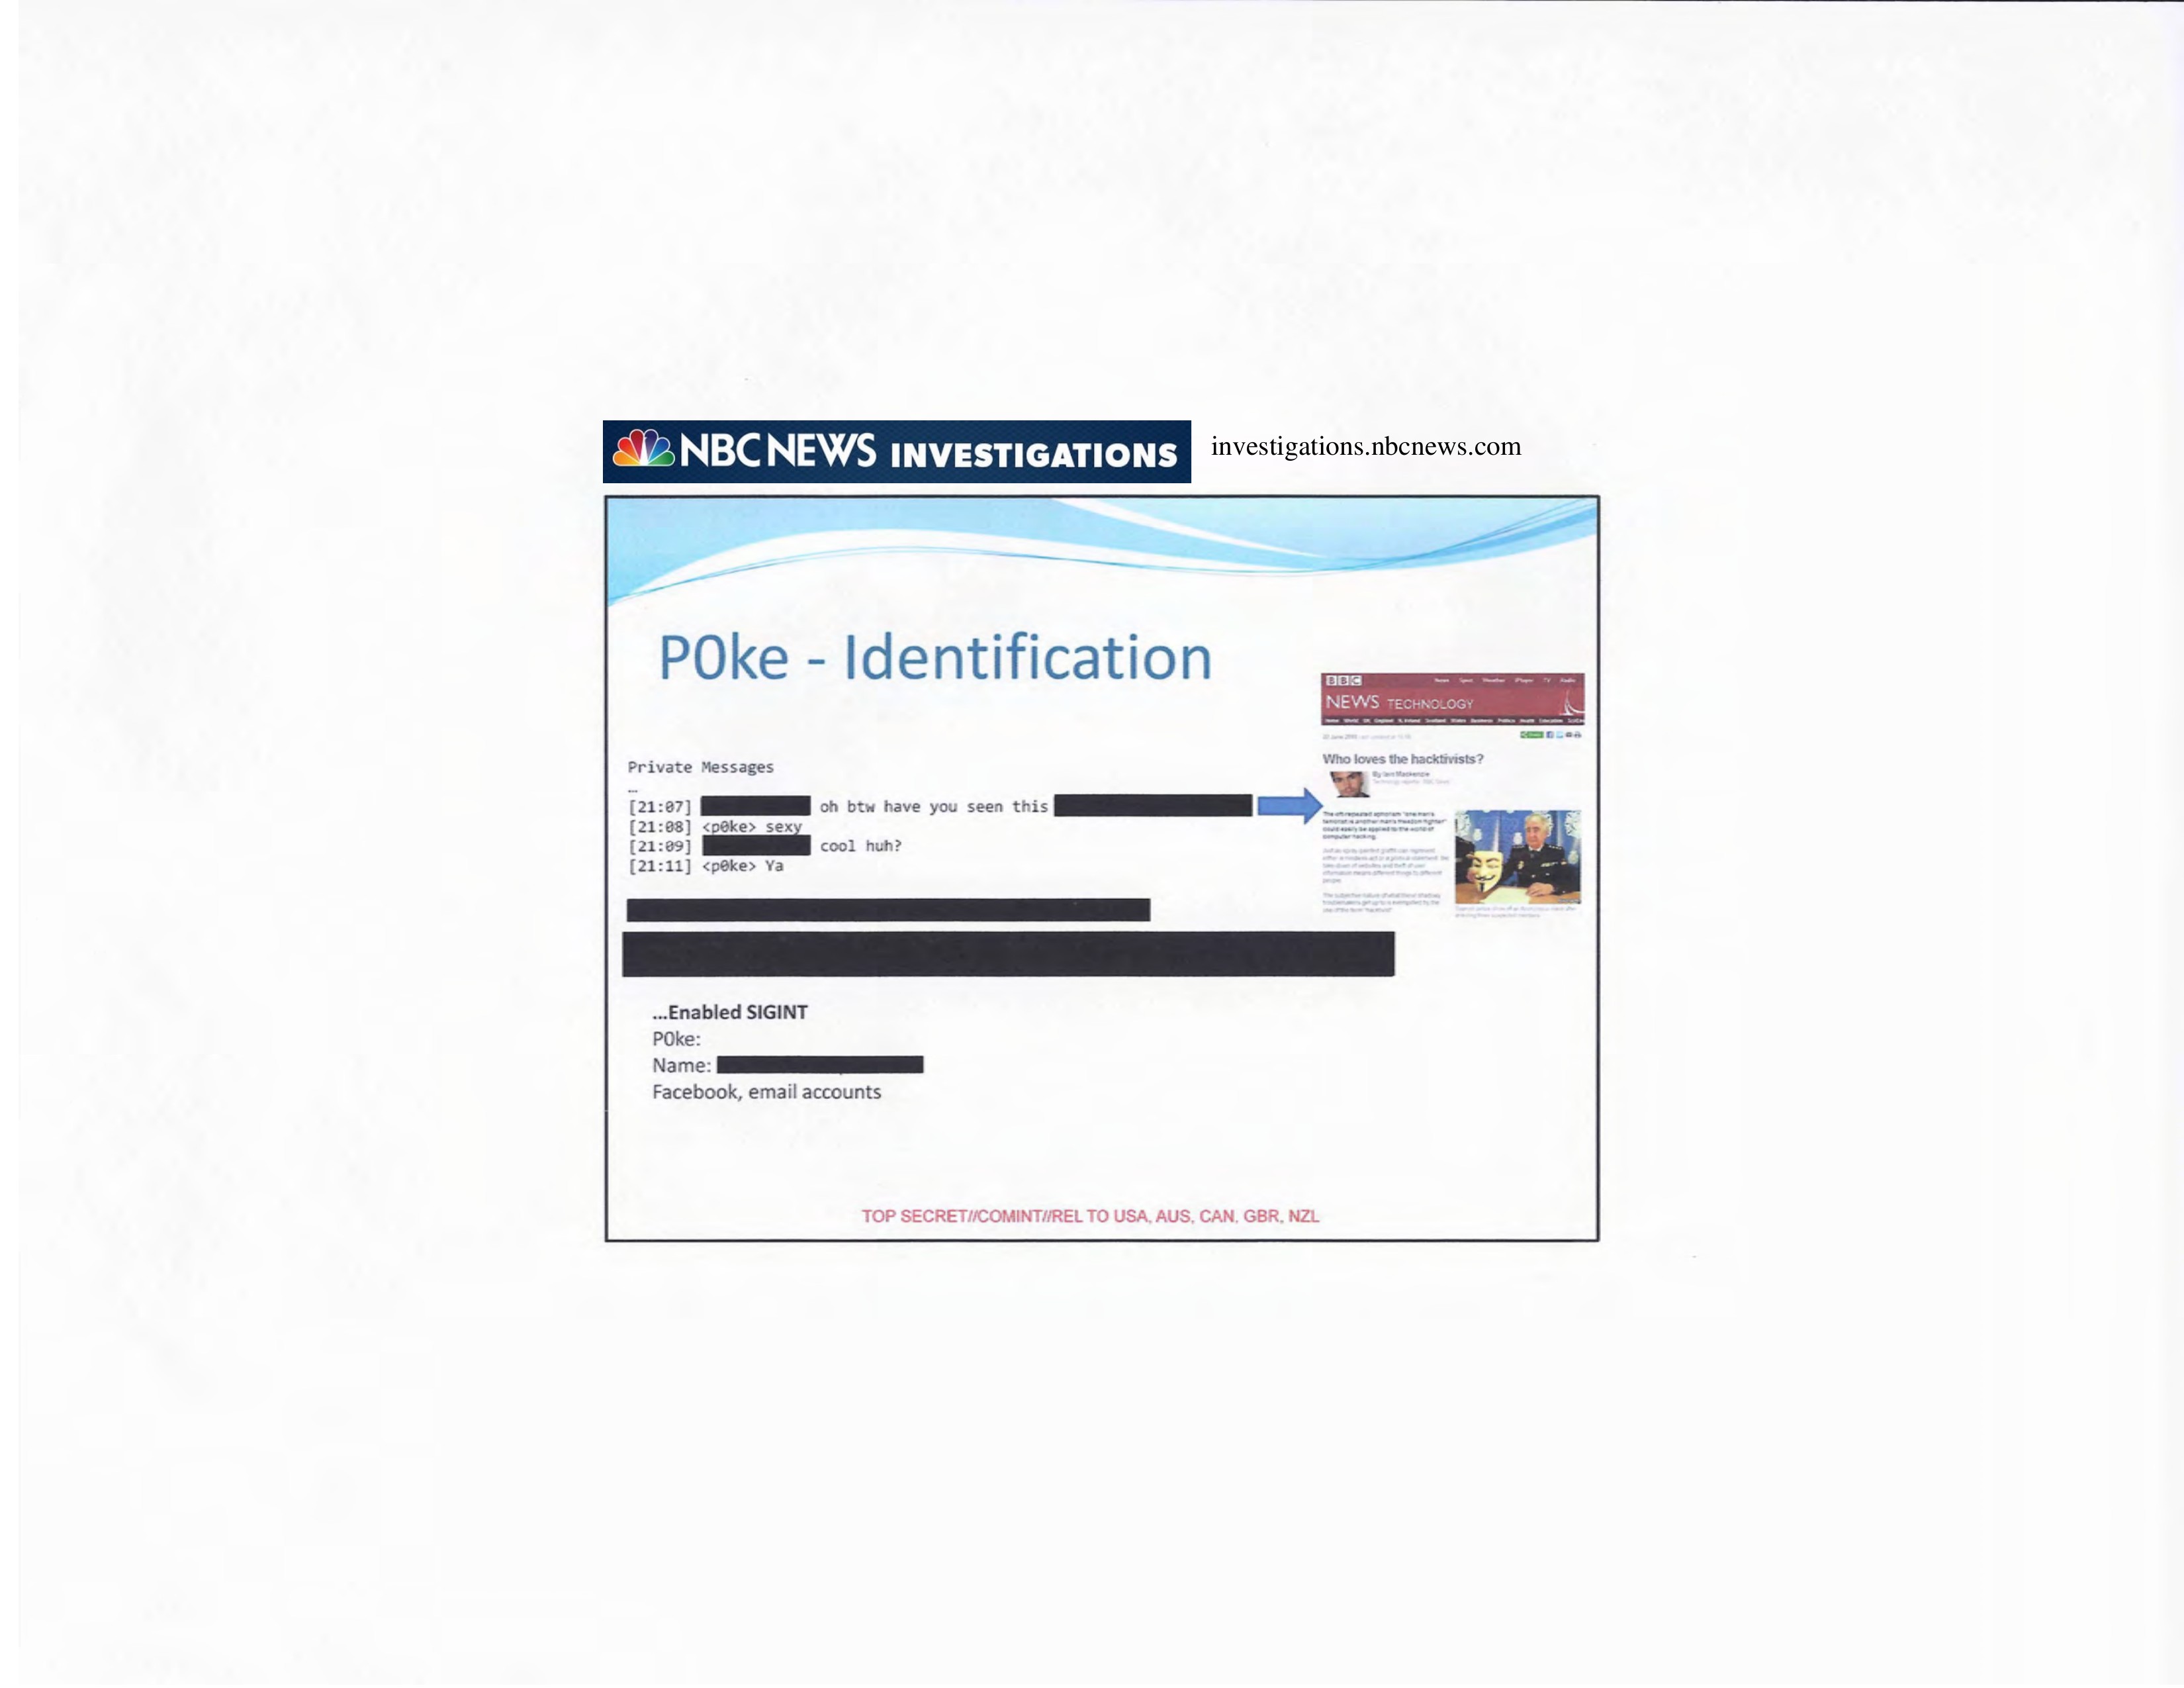
P0ke - Identification
BBC
NEWS TECHNOLOGY
Who loves the hacktivists?
By Iain Mackenzie
Private Messages
[21:07] [REDACTED] oh btw have you seen this [REDACTED]
[21:08] <p0ke> sexy
[21:09] [REDACTED] cool huh?
[21:11] <p0ke> Ya
[REDACTED]
[REDACTED]
...Enabled SIGINT
P0ke:
Name: [REDACTED]
Facebook, email accounts
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
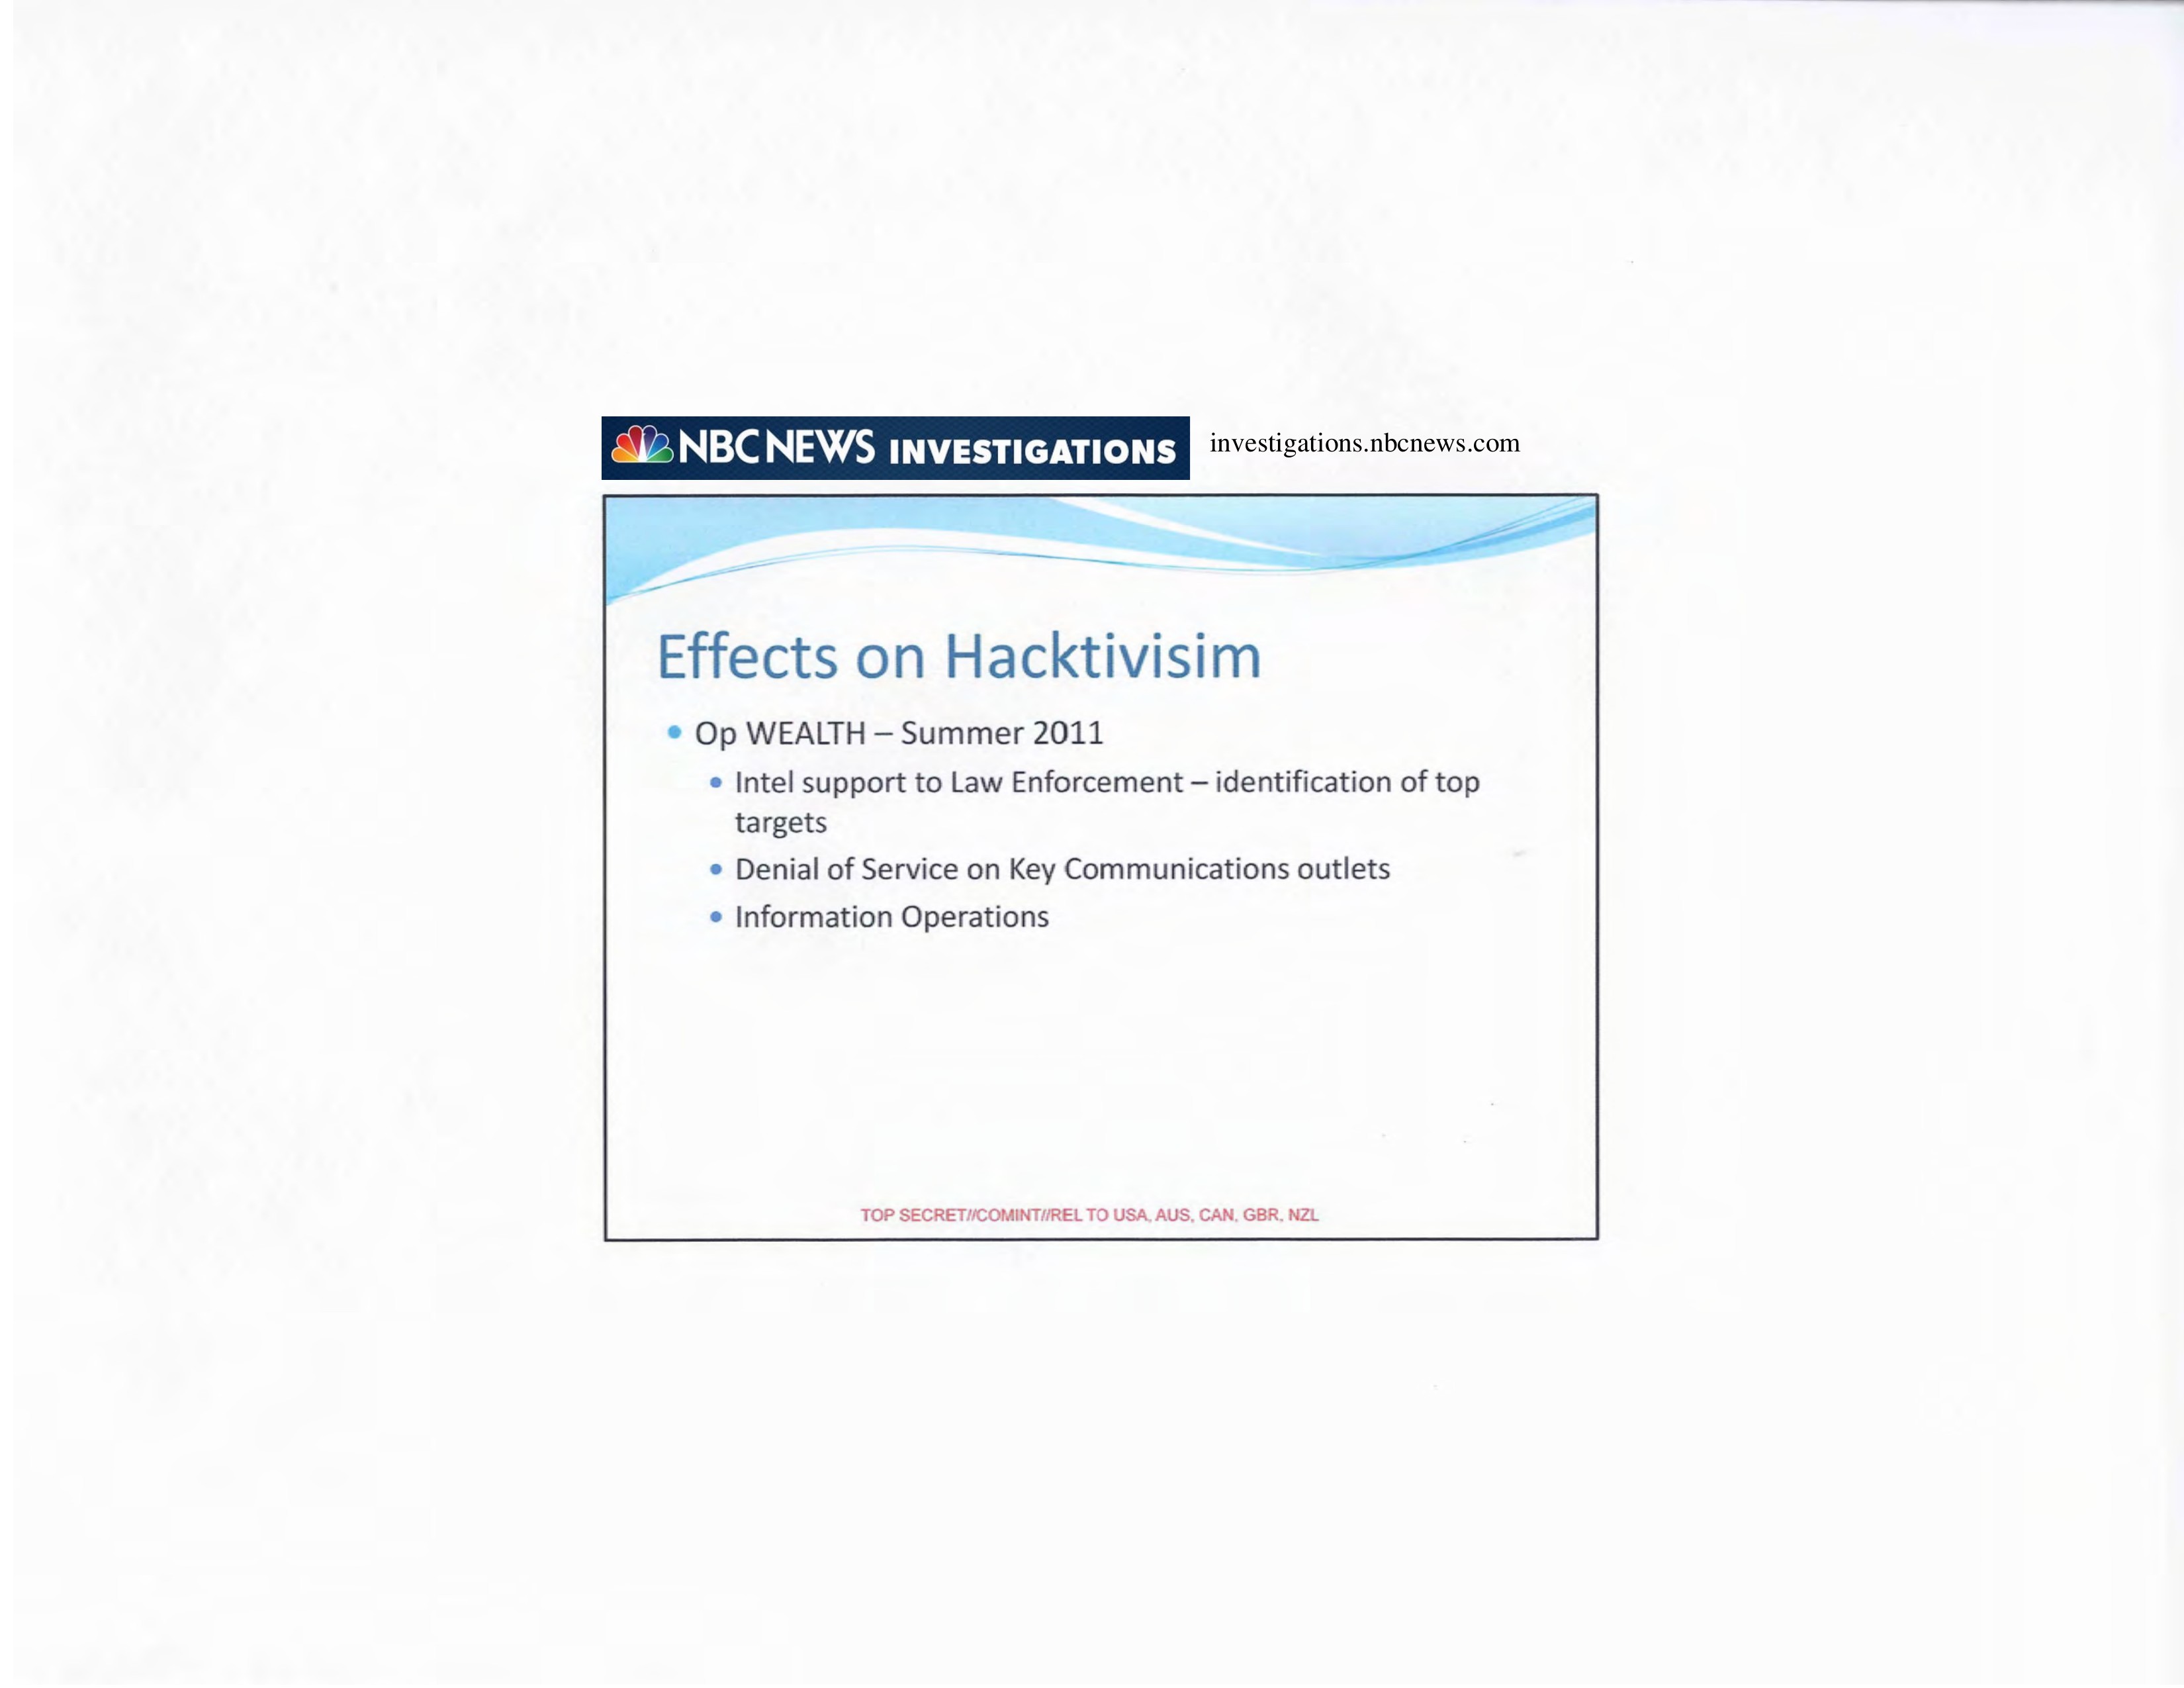
Effects on Hacktivism
- Op WEALTH - Summer 2011
- Intel support to Law Enforcement - identification of top targets
- Denial of Service on Key Communications outlets
- Information Operations
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
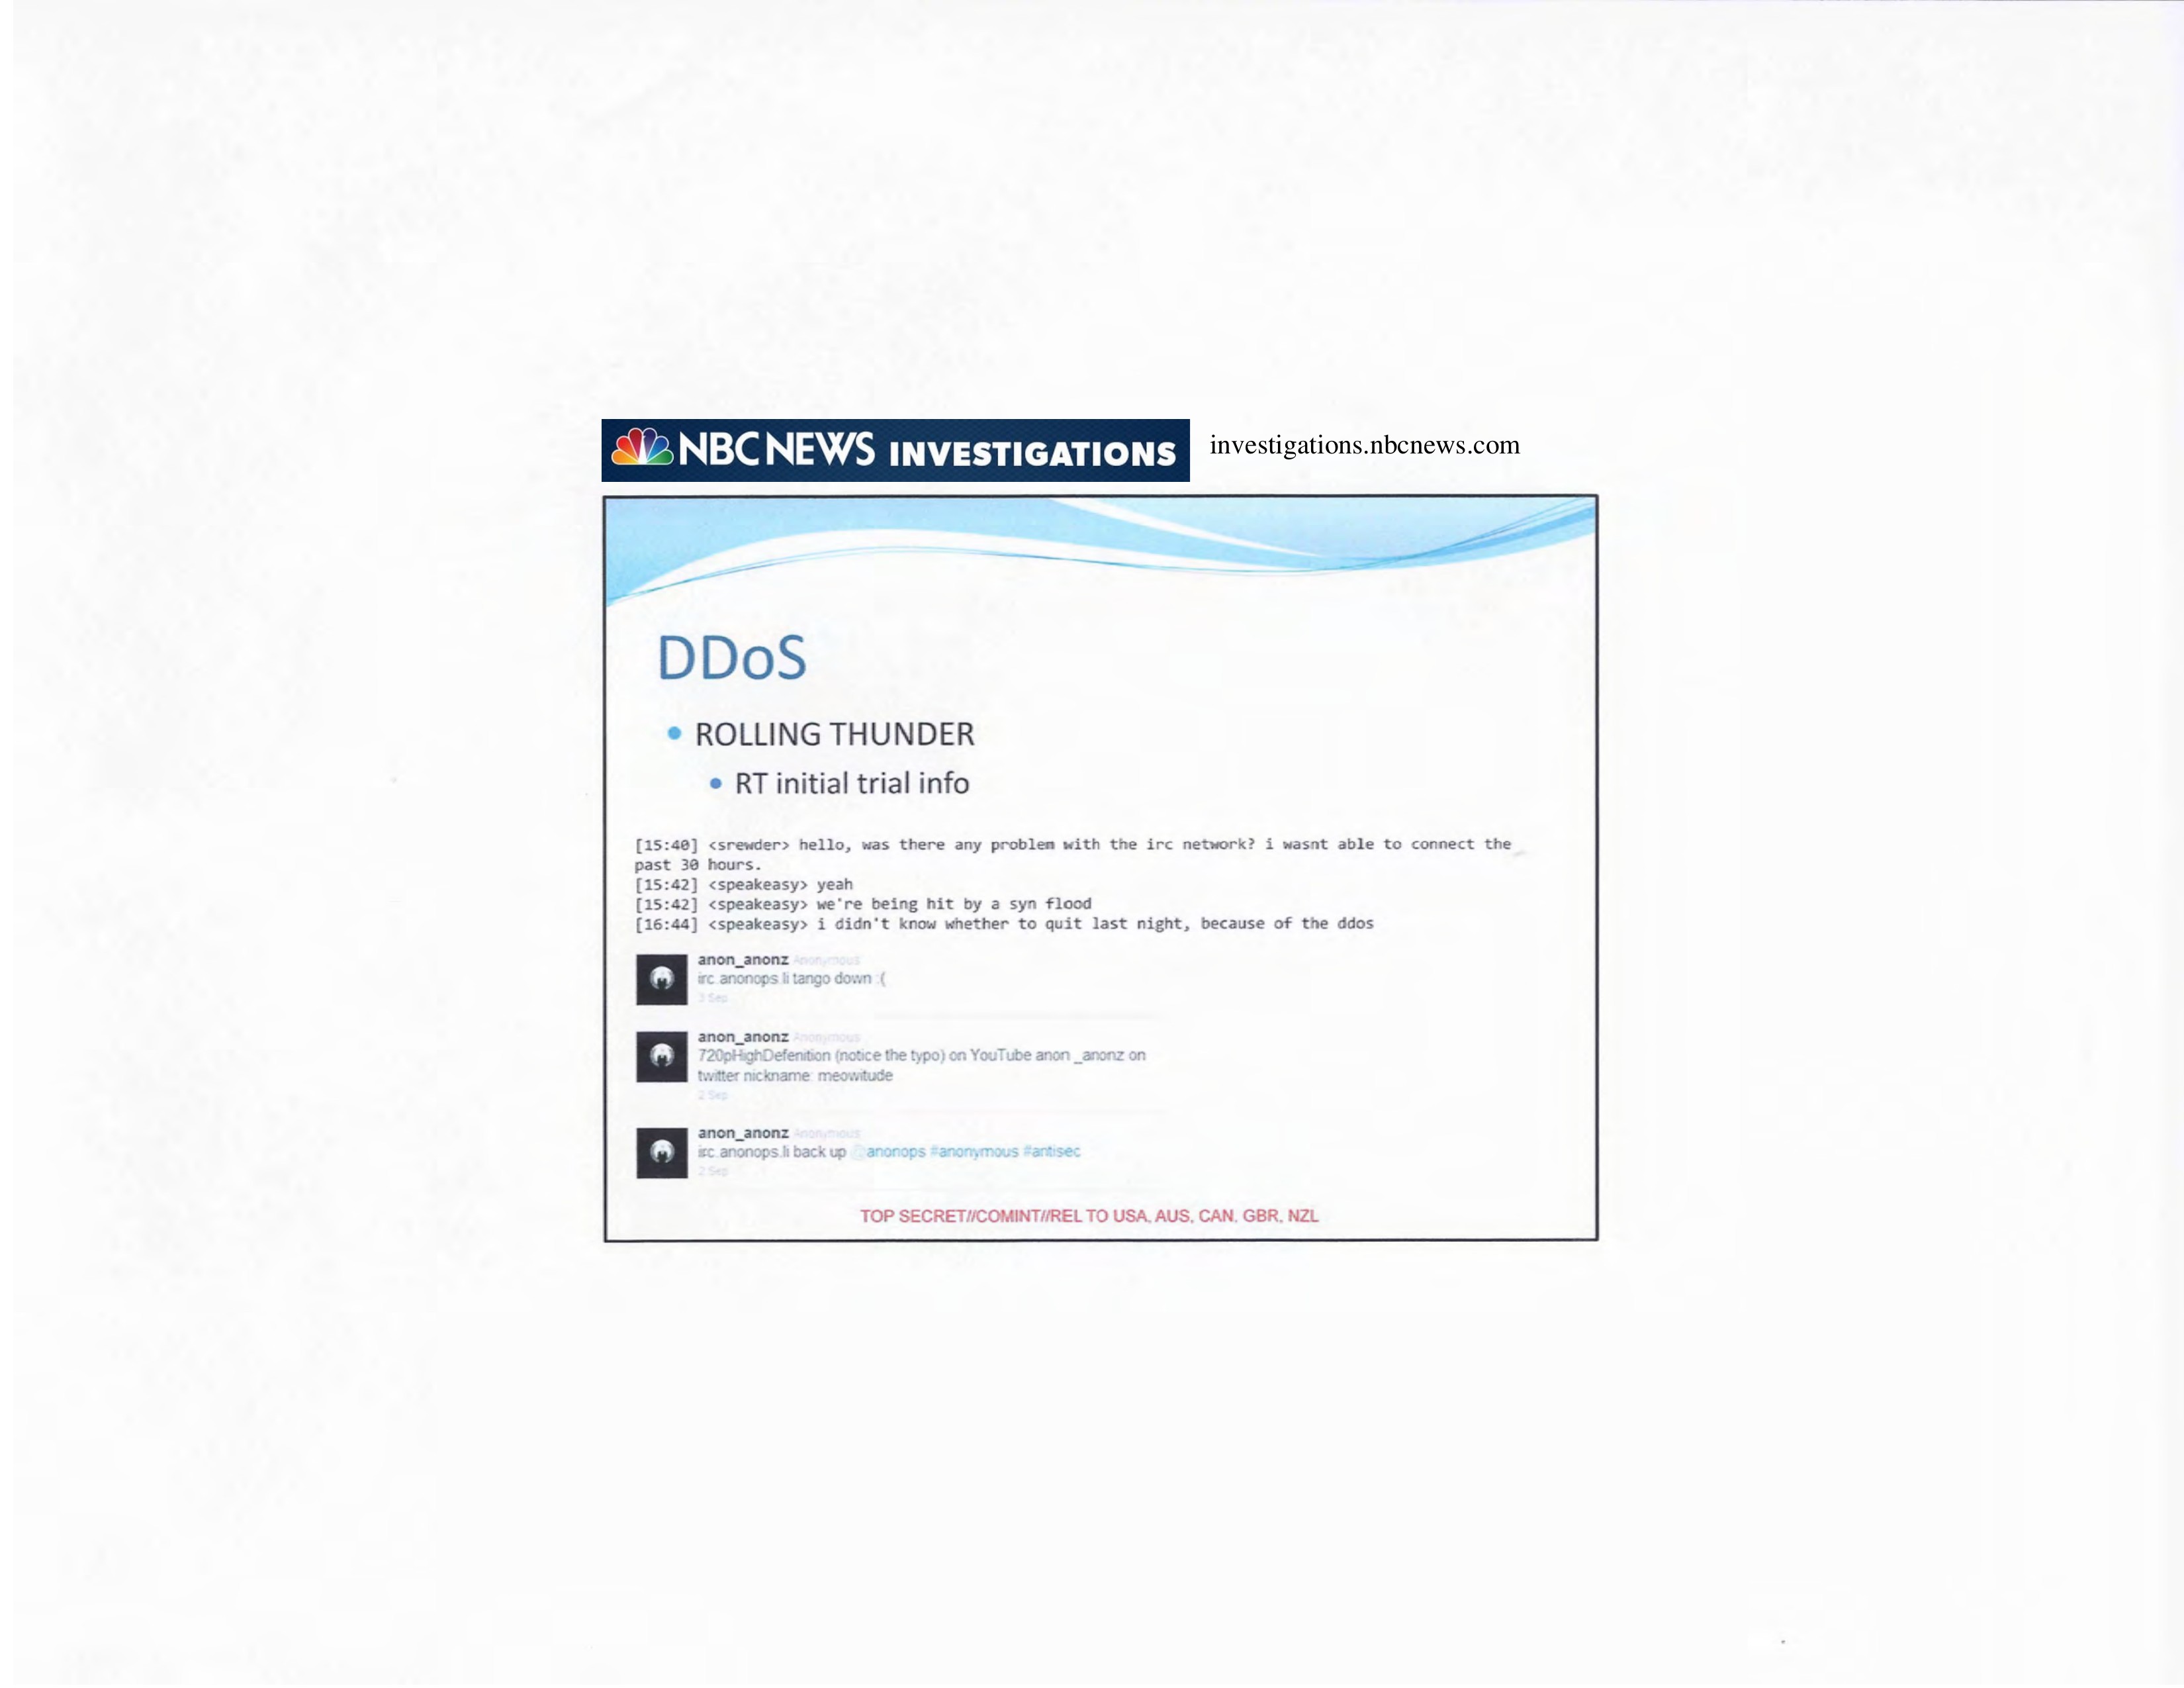
DDoS
- ROLLING THUNDER
- RT initial trial info
[15:40] <srewder> hello, was there any problem with the irc network? i wasnt able to connect the past 30 hours.
[15:42] <speakeasy> yeah
[15:42] <speakeasy> we're being hit by a syn flood
[16:44] <speakeasy> i didn't know whether to quit last night, because of the ddos
anon_anonz Anonymous
irc.anonops li tango down :(
3 Sep

anon_anonz Anonymous
720pHigh Defenition (notice the typo) on YouTube anon_anonz on
twitter nickname: meowitude
2 Sep

anon_anonz Anonymous
irc.anonops.li back up @anonops #anonymous #antisec
2 Sep
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
IO Outcome
- CHIS with [REDACTED]
- 80% of those messaged where not in the IRC channels 1 month later
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
NBC NEWS INVESTIGATIONS investigations.nbcnews.com
Conclusion
- Team working – SIGINT, JTRIG, CDO, INOC – was key to success
- Online Covert Action techniques can aid cyber threat awareness
- Effects can influence the target space
TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL
Related Documents
-
Cyber Integration [pdf]
The leaked 2012 GCHQ JTRIG presentation detail a wide range of offensive cyber and influence operations designed to “deny, disrupt, degrade, and deceive” targets, including hackers, foreign governments, companies, and individuals. Tactics include hacking, DDOS attacks, disinformation, honey traps, credential harvesting, and psychological operations, reflecting a shift from traditional surveillance to active disruption and manipulation campaigns.
“Exclusive: Snowden Docs Show British Spies Used Sex and 'Dirty Tricks'” - NBC News ↗ (2014-02-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Cole, Matthew · Esposito, Richard · Schone, Mark · Greenwald, Glenn -
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
JTRIG tools and techniques [pdf]
This document is an internal GCHQ wiki page from July 2012 detailing the capabilities of GCHQ’s Joint Threat Research Intelligence Group (JTRIG). It serves as an internal "Chinese menu" or catalog of digital tools and techniques used for engineering, intelligence collection, and "effects" (offensive operations).
Programs: JTRIG · CERBERUS · JTRIG RADIANTSPLENDOUR · ALLIUMARCH · ASTRALPROJECTION · TWILIGHTARROW · SPICEISLAND · POISONARROW · FRUITBOWL · NUTALLERGY · BERRYTWISTER · BERRYTWISTER+ · FORESTWARRIOR · JAZZFUSION · BRANDYSNAP · WINDFARM · BOMBAYROLL · COUNTRYFILE · TECHNOVIKING · JAZZFUSION+ · BUMBLEBEEDANCE · AIRBAG · EXPOW · AXLEGREASE · PODRACE · WATCHTOWER · REAPER · DIALd · DIRTYDEVIL · AIRWOLF · ANCESTRY · BEARTRAP · BIRDSONG · BIRDSTRIKE · BUGSY · DANCINGBEAR · DEVILSHANDSHAKE · DRAGON'SSNOUT · EXCALIBUR · FATYAK · FUSEWIRE · GLASSBACK · GODFATHER · GOODFELLA · HACIENDA · GEOFUSION · GLOBALSURGE · ICE · INSPECTOR · LANDINGPARTY · VIKINGPILLAGE · MINIATUREHERO · MOUTH · MUSTANG · PHOTONTORPEDO · RESERVOIR · SEBACIUM · SILVERSPECTER · SODAWATER · SPRINGBISHOP · DIRTYRAT · SYLVESTER · TANNER · TRACERFIRE · VIEWER · TOPHAT · ANGRYPIRATE · ARSONSAM · BUMPERCAR+ · BOMBBAY · BADGER · BURLESQUE · CANNONBALL · CLEANSWEEP · CLUMSYBEEKEEPER · CHINESEFIRECRACKER · BUMPERCAR · CONCRETEDONKEY · DEERSTALKER · GATEWAY · GAMBIT · GESTATOR · GLITTERBALL · IMPERIALBARGE · PITBULL · POISONEDDAGGER · PREDATORSFACE · ROLLINGTHUNDER · SCARLETEMPEROR · SCRAPHEAPCHALLENGE · SERPENTSTONGUE · SILENTMOVIE · SILVERBLADE · SILVERFOX · SILVERLORD · SKYSCRAPER · SLIPSTREAM · STEALTHMOOSE · SUNBLOCK · SWAMPDONKEY · TORNADOALLEY · UNDERPASS · VIPERSTONGUE · WARPATH · HOMEPORTAL · CYBERCOMMANDCONSOLE · NAMEJACKER · BABYLON · CRYOSTAT · ELATE · PRIMATE · JEDI · JILES · MIDDLEMAN · OUTWARD · TANGLEFOOT · SCREAMINGEAGLE · SLAMMER · EARTHLING · NEWPIN · BYSTANDER · CONDUIT · QUINCY · BEARSCRAPE · SFL · SNOOPY · MOBILEHOOVER · NEVIS · CHANGELING · HAVOK · MIRAGE · SHADOWCAT · SPACEROCKET · RANA · LUMP · GURKHASSWORD · CRINKLECUT · SHORTFALL · DEADPOOL · HUSK · LONGSHOT · MOLTEN-MAGMA · NIGHTCRAWLER · PISTRIX · WURLITZER -
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe