Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe -
Having the (SIGINT) Time of My Life! SIDtoday [pdf]
An NSA representative with a military task force in Afghanistan discusses how central signals intelligence is to war decisions. He writes that when the task force "'actions' a target, they head straight to the CSG [Cryptologic Support Group] and ask for information that almost always is the deciding factor on whether or not a 'target' is actioned. ... Isn't it awesome to be relevant?"
The Intercept ↗ (2017-09-13) -
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
Hollywood Special Effects? No, It's Modern-Day SIGINT SIDtoday [pdf]
An NSA staffer flies to Baghdad to demonstrate the Real Time Regional Gateway system to awestruck representatives from FBI and other government agencies.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · The Intercept ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
HOMING PIGEON [pdf]
Slides on a query-focused dataset that would correlate GSM handsets seen on two or more aircraft flights with their subscribers.
“US and Britain refine their ability to tap into airline passenger’s mobile phones while they are in the air” - Le Monde ↗ (2016-12-07) · “American and British Spy Agencies Targeted In-Flight Mobile Phone Use” - The Intercept ↗ (2016-12-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Follorou, Jacques · Greenwald, Glenn -
How do we do SIGDEV or private networks? [pdf]
Top Secret SIGINT Development (SIGDEV) briefing explains how analysts conduct reconnaissance on private networks, noting that many targets rely on them and that 30–40% of traffic surveyed in BLACKPEARL has at least one private endpoint. It demonstrates the ROYALNET tool and its analytics for identifying network features, NetStrings, and links likely to carry a target’s traffic, with named targets and feature sets including Google’s infrastructure, the SWIFT banking network, the French Ministry of Foreign Affairs, Brazil’s Petrobras, and Huawei.
People: Higgins, Jean -
How NSA Is Prepared for the Winter Olympics (Which Kick Off Tomorrow) SIDtoday [pdf]
NSA is ready for yet another Olympics in the geographically challenging Italian alps. A SCIF has been set up and analyst deployed to Turin and the National Counterterrorism Center in Virginia. Though the Italians are deemed better at providing security than the Greeks were in Athens, NSA will be "monitoring host government communications to verify security planning, performance and sharing of threat information."
Programs: VOICESAILPeople: Bush, LauraThe Intercept ↗ (2018-08-15) -
How NSA Teams Support Tactical Forces in Iraq SIDtoday [pdf]
Members of early Cryptologic Support Teams deployed to Iraq remember difficulties and successes of the combat support missions in Balad and Mosul in 2004.
Programs: GEOCELLThe Intercept ↗ (2018-03-01) -
How SIGINT Helped Liberate an American Hostage in Iraq SIDtoday [pdf]
A cryptologic support team identified mobile phone handsets involved in kidnappings in Iraq, which allowed special forces to capture and interrogate individuals with information regarding the hostage Roy Hallums, leading to his rescue.
The Intercept ↗ (2018-03-01) -
How the NSA Accesses Smartphone Data [pdf]
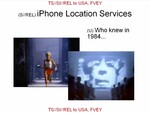
This document reveals how the NSA and its Five Eyes partners developed sophisticated methods to exploit iPhone location services and BlackBerry communications, framing smartphone users as “zombies” willingly sharing data. It includes examples of intercepted geolocation data and decrypted BlackBerry emails, illustrating targeted surveillance capabilities against both consumer and government communications.
-
How the NSA Pinpoints a Mobile Device [pdf]
This document is an internal National Security Agency classification guide outlining the agency's abilities to intercept cellular communications.
Programs: ARCVIEW -
How the NSA verifies a target's location [pdf]
This is an excerpt from a transcript of National Security Agency training videos that describe how to verify the location of a targeted device. It explains how the NSA monitors different types of mobile signaling information known as HLR and VLR registrations in order to locate individuals. It also makes clear that the agency is able to use location tracking to ascertain whether a target is in the United States.
-
HTTP Activity in XKEYSCORE [pdf]
This training presentation from March 2009 provides NSA and Five Eyes analysts with detailed instructions on exploiting HTTP web browsing activity collected by XKEYSCORE, explaining how to differentiate client-to-server requests (GET/POST) from server-to-client responses, extract metadata like search terms, URLs, cookies, language, and browser types, and use this data to discover new surveillance targets, track individuals' online behavior, and conduct "pattern of life" analysis.
-
HTTP Activity vs User Activity [pdf]
This NSA training document from June 2009 explains the distinction between HTTP Activity (general web browsing data) and User Activity (communications metadata from specific protocols like webmail and chat) within the XKEYSCORE surveillance system, demonstrating through Iranian examples how analysts combine both search types to develop comprehensive intelligence on targets.
Programs: XKEYSCORE · MARINA · FOXTRAIL · DECODEORDAIN · YACHTSHOP · BRUTUS · WINDCHASER · NKB · UIS · STARPROC -
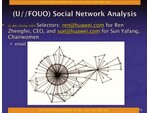
Huawei - Social Network Analysis [pdf]
This document describes Social Network Analysis targeting top leadership at Huawei. By tracking the email selectors of CEO Ren Zhengfei and Chairwoman Sun Yafang, the agency mapped their professional and personal connections.
“NSA: Imperiale Visionen” - Der Spiegel ↗ (2014-03-23) · Rosenbach, Marcel · Stark, Holger · Zand, Bernhard -
I hunt sys admins [pdf]
These internal documents outline the NSA’s strategy for identifying and targeting foreign system administrators to gain "keys to the kingdom" access to global network infrastructure. By correlating disparate datasets—such as passive telnet/SSH metadata and personal social media/webmail logins—the agency identifies personal accounts to facilitate QUANTUM-based hacking operations and network "pwnage."
-
ICREACH Wholesale Sharing (2007) [pdf]
This document serves as an official submission by the SID Technical Director detailing the leadership and collaborative efforts required to transition ICREACH from a conceptual framework into the Intelligence Community's first wholesale metadata-sharing platform. This document emphasizes the role of the SID team in securing critical legal and policy approvals through the NSA's Office of the General Counsel and coordinating with Five Eyes partners to ensure international participation in the system.
Programs: ICREACH -
ICTR Cloud Efforts [pdf]
A GCHQ presentation details how the agency developed cloud-based big data analytics to achieve "population scale" surveillance—processing trillions of internet events to build geographic and behavioral profiles on every online identifier worldwide, enabling discovery of unknown targets through pattern analysis rather than traditional keyword searches.
Programs: EVERYASSOC · PROBABILITYCLOUD · SILVERLINING · CULTWEAVE · KARMAPOLICE · EVERYPOLICE · AWKWARDTURTLE · GORDIANKNOT · SANDIA · BLOODHOUND · FIVEALIVE · NGE · MAPREDUCE -
Identity Intelligence: Image Is Everything [pdf]
This document is a highly classified NSA/CSS briefing detailing Identity Intelligence (i2), a comprehensive methodology for exploiting unique fragments of information to track, identify, and exploit targets of interest. It outlines an expansive architecture for data collection that spans Biometric/Biologic, Biographic, and Contextual/Behavioral domains, essentially mapping every conceivable data point of an individual's physical existence and digital/social footprint.