Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Entry From SSO News [pdf]
This document discusses the initial operational capability of MONKEYROCKET, a non-Western Internet anonymization service developed as part of the OAKSTAR program, aimed at supporting counter-terrorism efforts. As of July 2012, the system was forwarding metadata to backend repositories, with a significant user base of around 16,000, primarily from countries like Iran and China. The service is expected to grow in usage, generating about 2,000 events per day.
-
Entry From SSODictionary v1.0 [pdf]
This document outlines a pending access point for MONKEYROCKET under the OAKSTAR program, focusing on full-take data collection from selected counter-terrorism (CT) targets using a non-Western anonymous browsing service. The collection will include user data, such as billing information and IP addresses, and support NSA's long-term strategy targeting terrorism and other criminal activities, with data gathered under Executive Order 12333. The system used for collection will be vPCS or XKS, and the operation is codenamed "THUNDERISLAND."
-
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
Event RARE weekly summaries [pdf]
This document outlines GCHQ's ongoing surveillance efforts in Libya, focusing on intercepting and analyzing communications from the Libyan regime, including military command and control via mobile satellite phones and other communication channels. It details the use of advanced SIGINT tools and close cooperation with the NSA, US, and Canadian intelligence agencies to monitor key military targets and opposition forces, supporting both tactical military operations and strategic intelligence objectives.
People: Gaddafi, Muammar -
Excerpt of May 2008 NSA Afghanistan Dataflow Analysis [pdf]
The document outlines how the NSA’s Real Time Regional Gateway (RT-RG) in Afghanistan progressively expanded from late 2007 through 2008 to ingest massive amounts of GSM, VHF, HF, and telephony metadata from dozens of locations across Afghanistan, supplemented by third-party “dirtbox” collection from allied nations such as the Netherlands, Denmark, Norway, Germany, and Spain. It details the specific collection sites, data types, and timelines (SPIN 9, 10, 11, etc.), illustrating how partner contributions and multiple signals sources fed into the RT-RG system to enable real-time intelligence.
Programs: FOURCORNERS · FORTRESS · WARRIOR · ECHIDNA · CASSIEOPIA · KARUS · SOUNDER · SNICK · TEMPOWOLFE · CALYPSO · TATTERAN · AIRBORNE · LEAVEBEHIND · UDEAUS · NELEUS · CROSSHAIR · SSO · DRT · RIVET JOINT · VOICESAIL“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Expanding PRISM Sharing With FBI and CIA [pdf]
An SSO item describing two projects that widened PRISM sharing with the FBI and CIA: PRINTAURA software that compiles the tasked-selector list every two weeks for both agencies, and weekly operational PRISM news and guidance from the mission programme manager.
-
Expanding TAO's Operational Capabilities Out to the CCs SIDtoday [pdf]
NSA Cryptologic Centers in Hawaii, Texas, and Georgia can now conduct Computer Network Exploitation.
The Intercept ↗ (2019-05-29) -
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
Experiences of a SIGINT'er in Baghdad SIDtoday [pdf]
A Data Acquisition lead reflects on his tour of duty in Iraq, which he describes as "an all-out effort to penetrate Iraqi networks using everything in the tool box of the most sophisticated SIGINT agency in the world." The workdays were long and entailed collaborations with all levels of U.S. military personnel, Iraqi government officials, and CEOs of Iraqi telecom companies. He appreciated the NSA's "daring" role in pursing Iraqi SIGINT targets.
Programs: SSOPeople: Rober, DonnaThe Intercept ↗ (2017-09-13) -
Exploiting Facebook traffic in the passive environment to obtain specific information [pdf]
A GCHQ Global Telecommunications Exploitation presentation on extracting information about Facebook users from passively collected traffic: why online social networks are a rich source, how Facebook's use of the Akamai content delivery network exposes a user's ID inside image URLs, and how profile and album images are then obtained through SPRING BISHOP, GODFATHER and JTRIG.
-
Exploiting Foreign Lawful Intercept (LI) Roundtable [pdf]
Top-secret PowerPoint presentation, "Exploiting Foreign Lawful Intercept Roundtable," highlights the agency’s strategy to exploit vulnerabilities in lawful intercept systems from telecom companies, such as Ericsson, Motorola, and Nokia, in countries like Mexico, Indonesia, and Egypt. The presentation also discusses NSA's use of various "Fingerprints" for identifying data and its collaboration with industry players and foreign lawful intercept systems.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · Bamford, James · Petropoulos, Aggelos -
Exploiting Terrorists' Passwords SIDtoday [pdf]
The SIGINT Forensics Lab discovered that computer disks seized by the government not only contain intelligence, but are also a "rich source of passwords and related information." Researchers created special tools and harvested "hundreds of thousands of occurrences of passwords," which they used to attack encrypted files.
Programs: JUMBLEDPETPeople: O'Hara, MikeThe Intercept ↗ (2016-12-07) -
Exploiting US/UK/CAN Phone Numbers -- In Compliance with USSID-18 Policy SIDtoday [pdf]
The NSA can now classify certain U.S. phone numbers as foreign, allowing them to be targeted. Such targeting may occur on a U.S. number if the phone number is “identified on foreign links” and if it is associated with a “Pick Your Own Number” internet service such as Vonage.
The Intercept ↗ (2018-08-15) -
Eye-Opening Experience in Haiti (part 1) SIDtoday [pdf]
An intelligence analysis intern was deployed to Haiti on a National Intelligence Support Team, which includes personnel from NSA, CIA, NGA, and DIA. There were operational challenges because the Marines on the ground had not requested the NIST deployment.
The Intercept ↗ (2017-04-24) -
Eye-Opening Experience in Haiti (part 2) SIDtoday [pdf]
The intelligence analysis intern deployed to Haiti describes how the SIGINT used by tactical forces on the ground is different from the product for most SID customers.
The Intercept ↗ (2017-04-24) -
F6, NSA Texas, and Yakima Research Station Collaborate on Venezuela Survey SIDtoday [pdf]
In the first in a series about SIGINT Development (SIGDEV) collaboration, the authors describe how three different departments worked together to develop new sources of signals intelligence on Venezuela. The Special Collection Service (F6), NSA Texas, and the Yakima Research Center worked on a remote survey that "uncovered dozens of links carrying traffic for Venezuelan targets of interest."
Programs: ESECSThe Intercept ↗ (2019-05-29) -
FAA Certification Renewals with Caveats [pdf]
This NSA document shows that after the FISA Court found NSA’s upstream internet collection unconstitutional and illegal, the agency’s response was less about reform and more about finding technical and procedural workarounds to keep surveillance running as usual. While the court ordered changes within 30 days, NSA officials planned to sequester and filter “higher-risk” data to appease the judge—not halt collection—revealing a mindset focused on preserving operations rather than addressing legal violations.
-
FAA702 comms memo [pdf]
This document details NSA's response to concerns raised by the FISA Court over the collection of non-targeted data in FAA-702 upstream collection. To mitigate the risk of continued acquisition, NSA is implementing temporary measures, including cautionary banners and updated processes, to prevent misuse of data that may not be directly related to tasked selectors.
People: Shea, Teresa H. -
FAA702 Glossary - Section 702 of the Fisa Amendments Act (FAA) [pdf]
This document outlines NSA rules under Section 702 of the FISA Amendments Act, which prohibit directly targeting U.S. persons or individuals inside the U.S., but quietly note a 2011 rule change allowing analysts to use U.S. person identifiers to query data already collected under 702—pending internal oversight. This effectively establishes a “backdoor search” capability enabling warrantless searches of Americans’ communications stored in NSA databases. Section 702 also gives the NSA authority to target without warrant the communications of foreign targets.
-
FAD FY 12 CCP Funding of Partners [pdf]
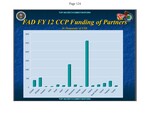
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.