Tag: Tailored Access Operations 105 documents
Search documents matching “Tailored Access Operations” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Tailored Access Operations [pdf]
A classified NSA Texas Cryptologic Center presentation introducing the TAO unit's staffing, operations, facilities, and growth plans — including detailed statistics on hacking operations, a breakdown of Operation WHITETAMALE targeting Mexico's Public Security Secretariat, and a personnel expansion plan projecting growth from 57 to 270 employees by FY2015.
Programs: WHITETAMALE · FREEZEPOST · DOCKETDICTATE · BACONRIDGE · OLYMPUS · SHARPFOCUS · PARCHDUSK · FOXACID -
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.
-
Tailored Access Operations, FOXACID, QUANTUM [pdf]
These NSA presentation slides detail "QUANTUM," a sophisticated system that allows the agency to intercept internet traffic and inject malware onto target computers with up to 80% success rates, far exceeding traditional spam-based methods. The system works by monitoring internet traffic for specific identifiers (like Yahoo or Facebook cookies), then racing to inject malicious code before legitimate web servers can respond, thereby compromising targets' computers without their knowledge and establishing persistent backdoor access.
Programs: FOXACID · QUANTUM · QUANTUMTHEORY · QUANTUMBISCUIT · VALIDATOR · OLYMPUS · UNITEDRAKE · OLYMPUSFIRE · SSO · FORESTPLACE -
Advanced CNE at the Kunia RSOC SIDtoday [pdf]
The Kunia Regional Security Operations Center in Hawaii is officially sanctioned by TAO as the "first organization of the Extended Enterprise to conduct advanced Computer Network Exploitation."
The Intercept ↗ (2016-12-07) -
Agencies Get Collective 'Boost' in Tackling Russian Missile Problem Together SIDtoday [pdf]
The NSA is collaborating with the Defense Intelligence Agency and GCHQ to solve the issue of intelligence on Russia's S-400/S-500 missile systems.
The Intercept ↗ (2017-09-13) -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT -
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
Changes in SID Leadership SIDtoday [pdf]
Changes in SID leadership are announced. Jim Allen has resigned. There is a new SID chief of staff as well.
The Intercept ↗ (2017-04-24) -
CLASSIFICATION GUIDE FOR ECI PAWLEYS (PAW) [pdf]
This 2006 NSA classification guide outlines the protocols for ECI PAWLEYS (PAW). PAWLEYS is an Exceptionally Compartmented Information (ECI) category designed to protect clandestine operations—both physical (HUMINT) and digital (CNE)—specifically aimed at acquiring foreign cryptographic information and material. The document confirms that the NSA actively seeks to circumvent encryption through clandestine HUMINT and computer network access aimed at cryptographic information and material, rather than relying solely on traditional codebreaking.
Programs: PAWLEYS -
Close Access SIGADS [pdf]
A 10 September 2010 NSA reference list of Close Access SIGADs revealing the codenames, locations and collection methods used to bug the embassies and UN missions of 38 targets — including US allies France, Italy, Greece, Japan, India, Mexico, South Korea and the EU — through implants, computer-screen capture, hard-drive imaging and electromagnetic emanation collection, most conducted against diplomatic facilities in Washington DC and New York.
Programs: KATEEL · POCOMOKE · MERCED · BANISTER · PERDIDO · MAGOTHY · BLACKFOOT · WABASH · NAVARRO · POWELL · KLONDIKE · NASHUA · OSAGE · OSWAYO · BRUNEAU · HEMLOCK · MULBERRY · ALAMITO · FLEMING · DOBIE · SULPHUR · REQUETTE · YUKON · WESTPORT · NAVAJO · PANTHER · LIFESAVER · HIGHLANDS · VAGRANT · MINERALIZ · DROPMIRE · PBX · MAGNETIC · OCEAN · GENIE · BLACKHEART · CRYPTOENABLED · CUSTOMS · DEWSWEEPER · RADON · MINERALIZE · COOP · STARRUBY · TRASHINT“No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Espionnage de la NSA : la diplomatie française était sur écoute aux Etats-Unis” - Le Monde ↗ (2013-10-22) · “Da qui ci spiano gli americani” - L'Espresso ↗ (2013-12-05) · Greenwald, Glenn · Follorou, Jacques · Maurizi, Stefania -
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
CNE Presence in CT10 Status Report [pdf]
A TOP SECRET NSA status report from April 2008 describing how a counterterrorism analysis team began importing data from the agency's hacking operations into their tracking system — specifically logs from FOXACID, an NSA tool that infects targets' computers mainly through their web browsers — enabling real-time alerts when new targets were successfully hacked, with plans to expand into tracking four named surveillance implants (VALIDATOR, UNITEDRAKE, OLYMPUS and STRAITBIZARRE) as they phone home to NSA servers for instructions and stolen data.
-
Collaboration in Overdrive: A CNE Success SIDtoday [pdf]
A collaboration between several NSA departments achieved, for the first time, Computer Network Exploitation against "Turkish leadership."
Programs: CMAP“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · The Intercept ↗ (2019-05-29) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
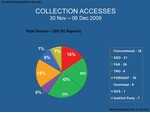
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO -
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Computer Network Exploitation Comes to NSA/CSS Georgia SIDtoday [pdf]
The Georgia Tailored Access Operations’s Remote Operations Center is officially opened — with a fiber-optic cable-cutting ceremony. The plan is to go from three operators doing computer network exploitation to a total of between 80 and 100 staffers, and to add computer network defense and attack capabilities.
The Intercept ↗ (2018-08-15) -
COMPUTER NETWORK OPERATIONS - GENIE [pdf]
A TOP SECRET Congressional Budget Justification entry for the NSA/CSS GENIE project — the Tailored Access Operations programme underpinning all endpoint Computer Network Operations — requesting $651.7 million and 1,870 military and civilian positions for FY2013, with plans to maintain 85,000-96,000 implant points-of-presence worldwide and 9,000-10,000 active accesses, including $25.1 million for covert purchase of software vulnerabilities and a $3.4 million supply chain implant operation targeting al-Qaeda.