Tag: exfiltration 9 documents
Search documents matching “exfiltration” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Access: Vision 2013 [pdf]
This July 2010 GCHQ strategic document outlines the agency's vision for 2013 to create "the world's biggest SIGINT engine" with access to 800 10-gigabit connections (up from existing capacity), expanding overseas operations to 60% while reducing UK-based to 40%, and developing new capabilities including computer network exploitation (CNE), exfiltration, beaconry, geolocation, and collection of "Internet Pocket Litter" like cookies and browsing data. The strategy emphasizes "scale and pace," "balance," and "agility" while claiming to operate within legal frameworks of "necessity, proportionality and authorisation," and highlights partnerships with second and third parties to access "intractable and hard targets."
Marking: SECRET -
CNE Presence in CT10 Status Report [pdf]
A TOP SECRET NSA status report from April 2008 describing how a counterterrorism analysis team began importing data from the agency's hacking operations into their tracking system — specifically logs from FOXACID, an NSA tool that infects targets' computers mainly through their web browsers — enabling real-time alerts when new targets were successfully hacked, with plans to expand into tracking four named surveillance implants (VALIDATOR, UNITEDRAKE, OLYMPUS and STRAITBIZARRE) as they phone home to NSA servers for instructions and stolen data.
-
FASHIONCLEFT - Interface Control Document (15 June 2009) [pdf]
This 2009 NSA Interface Control Document provides comprehensive technical specifications for FASHIONCLEFT, the protocol that acts as a covert shipping system enabling TAO malware implants to send stolen network data back to NSA collection servers with minimal computer processing requirements—using multiple encryption layers (RSA-1024 and RC6-128) to disguise the traffic as it travels across the internet while allowing NSA's Common Data Receptor to reassemble and authenticate the original intercepted packets. The document details how implants make modified copies of captured network traffic (changing destination addresses to point toward NSA instead of legitimate recipients), apply various levels of encryption or scrambling ("munging") depending on how powerful the infected computer is, attach metadata instructions explaining how to reconstruct the original packets, and use pattern-matching algorithms to ensure NSA systems can identify which stolen packets belong to which collection operation.
Programs: FASHIONCLEFT · FLAXENPRECEPT · SHELLGREY · SURPASSPIN · SEAGULLFARO · ROOTKNOT · FIGBUILD · OPTICPINCH · VINYLSEAT · OLYMPUS · UNITEDRAKE · HOGTECH · SWEEPFORWARD · CONVEY · PINWALE · TREBLECLEF · FOGYNULL · FUNNELAPS · FLASHHANDLE -
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
Strawhorse: Attacking the MacOS and iOS Software Development Kit [pdf]
Abstract from the 2012 CIA Trusted Computing Base Jamboree, presented by Sandia National Laboratories, describing successful modification of Apple's Xcode 4.1 SDK to create a covert injection vector capable of embedding backdoors, exfiltrating developer private keys, forcing data transmission to intelligence listening posts, disabling ASLR in kernel extensions, and installing a keylogger via a modified OS X updater.
People: Thompson, Ken“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
The Wizards of OZ II: Looking Over the Shoulder of a Chinese C2C Operation SIDtoday [pdf]
A survey team discovers that Chinese hackers have compromised computers at the Indian Embassy in Beijing, exfiltrating "sensitive Indian diplomatic files" to public drop boxes on the internet. Seizing on this unique opportunity to look their colleagues over the shoulders, the team sets up "sustained collection" before returning home.
Programs: MUSKETEERThe Intercept ↗ (2019-05-29) -
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR -
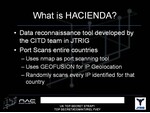
What is HACIENDA? [pdf]
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).