Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
CNE EndPoint Project Load [pdf]
The CNE EndPoint Project Load document lists multiple GCHQ exploitation projects, with “PFENNING ALPHA” targeting Flag Telecom’s network. It notes automated pulls of router monitoring webpages, collection of performance statistics, and ongoing efforts to gain further access points within Reliance’s infrastructure, while other projects and targets remain redacted.
Programs: PFENNING ALPHA · BURRITO ALPHA · GLADDY IOTA · HEADRESS IOTA · HEADRESS KAPPA · HEADRESS NU · HEADRESS OMICRON · GLADDY CHI · EREPO · RELIANCE · GTE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
CNE Presence in CT10 Status Report [pdf]
A TOP SECRET NSA status report from April 2008 describing how a counterterrorism analysis team began importing data from the agency's hacking operations into their tracking system — specifically logs from FOXACID, an NSA tool that infects targets' computers mainly through their web browsers — enabling real-time alerts when new targets were successfully hacked, with plans to expand into tracking four named surveillance implants (VALIDATOR, UNITEDRAKE, OLYMPUS and STRAITBIZARRE) as they phone home to NSA servers for instructions and stolen data.
-
CNO Core Secrets Security Structure [pdf]
A 3-slide NSA presentation outlining the classification architecture of Sentry Eagle, a national cyber operations initiative, showing how its most sensitive components — covering network hacking, encryption sabotage, and covert industry relationships — are locked behind ECI and SAP designations accessible only to a tiny circle of government officials.
Programs: SENTRYEAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CNO Core Secrets Slide Slices [pdf]
This document outlines the Security Framework for a joint national initiative between the NSA/CSS and JFCC-NW, detailing the highly compartmented structure used to protect cyber and intelligence secrets. It utilizes a concentric security framework diagram to visualize the layers of sensitivity, placing the most critical technical capabilities at the absolute center of the intelligence community's protection.
Programs: SENTRY-EAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CNO Legal Authorities [pdf]
An NSA Office of General Counsel briefing on the legal authorities for computer network operations and the NTOC floor: constitutional and EO 12333 limits, NSCID 6 definitions, Wiretap Act exceptions, NSD 42, service-provider information-assurance rules (DoD 5240.1-R), and oversight and compliance.
-
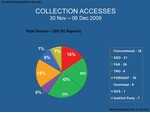
Collection Accesses 30 Nov - 06 Dec 2009 [pdf]
This National Security Agency chart shows the varied sources of 103 “accesses” to communications or computers collected in a single week in 2009 at the N.S.A.’s big station in San Antonio, Texas.
Programs: SSO -
Come to SID's Identity Intelligence (I2) Day Conference and See Your Target in a Whole New Light! SIDtoday [pdf]
This SIDtoday article promotes NSA's Identity Intelligence (I2) Day Conference, highlighting the importance of using SIGINT tools and techniques to track individuals across time and space. It emphasizes the growing role of biometrics, biographic data, and digital footprints in identifying and targeting foreign persons of interest, with insights from key speakers and case studies.
-
COMET NEWS (March 2010) [pdf]
This document is a March 2010 edition of the COMET NEWS newsletter, a high-level GCHQ publication designed to inform targeting teams about the latest capabilities and successful operations within the "Overhead" satellite constellation. It specifically highlights a coordinated GCHQ and US overhead (OH) effort to intercept high-priority military and leadership communications from Argentina, utilizing specialized US satellite assets and geolocation techniques to map digital microwave emitters.
Programs: COMET“Britain Used Spy Team to Shape Latin American Public Opinion on Falklands” - The Intercept ↗ (2015-04-02) · “#EspiadosPorLosIngleses: los nuevos documentos de Snowden revelan un plan de espionaje de Gran Bretaña en Argentina por Malvinas” - Todo Noticias ↗ (2015-04-02) · Fishman, Andrew · Greenwald, Glenn -
Coming Soon! A Tool that Enables Non-Linguists to Analyze Foreign-TV News Programs SIDtoday [pdf]
This document introduces eViTAP (Enhanced Video Text and Audio Processing), a fully automated system designed to monitor and translate international television broadcasts. Primarily aimed at analysts who do not possess specific foreign language skills, the tool leverages automated processing to transform open-source media into actionable intelligence.
-
Communications Capability Development Programme [pdf]
The Communications Capability Development (CCD) Programme (formerly the Intercept Modernisation Programme, IMP) was a Home Office–led effort to maintain the U.K.’s lawful interception and communications data capabilities amid changing technologies, emphasizing that law enforcement faced a “significant decline” without new measures. GCHQ supported CCD with technical expertise and interim services like MILKWHITE Enrichment, while stressing that CCD was politically contentious, technically complex, and required legislation to mandate data retention by U.K. network operators.
-
Communications System - How To Guide [pdf]
A TOP SECRET and sensitive compartmented information (SCI) how-to document for the NSA’s XKEYSCORE “Comms” backbone, laying out ports, peer/allow rules, bandwidth pools, and proxy classifications that stitch clusters to central control—a scalable architecture for moving surveillance data with security markings baked in. It also walks through firewall exceptions, HTTPS port-sharing, and a MAILORDER file pipeline, exposing the nuts‑and‑bolts of how collection flows across sites, proxies, and viewers.
-
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
COMPUTER NETWORK OPERATIONS - GENIE [pdf]
A TOP SECRET Congressional Budget Justification entry for the NSA/CSS GENIE project — the Tailored Access Operations programme underpinning all endpoint Computer Network Operations — requesting $651.7 million and 1,870 military and civilian positions for FY2013, with plans to maintain 85,000-96,000 implant points-of-presence worldwide and 9,000-10,000 active accesses, including $25.1 million for covert purchase of software vulnerabilities and a $3.4 million supply chain implant operation targeting al-Qaeda.
-
Computer-Network Exploitation Successes South of the Border [pdf]
Pena Nieto's predecessor as president, Felipe Calderon, was also targeted. This image shows an excerpt from an NSA document classified as "top secret," from November 2010. The National Security Agency (NSA) has a division for particularly difficult cases. Called "Tailored Access Operations," or TAO for short, this department devises special methods for special targets. In May 2010, the division reported mission accomplished. A report classified as "top secret" said: "TAO successfully exploited a key mail server in the Mexican Presidencia domain within the Mexican Presidential network to gain first-ever access to President Felipe Calderon's public email account." According to the NSA, this email domain was also used by cabinet members, and contained "diplomatic, economic and leadership communications which continue to provide insight into Mexico's political system and internal stability."
Programs: FLATLIQUID -
Comsat GCHQ [pdf]
GCHQ outlines its COMSAT antenna strategy, driven by ballooning maintenance costs from decades of accumulated satellite dishes at CARBOY, SOUNDER, and SNICK—aiming to cut total cost of ownership while expanding collection under the Five Eyes SHAREDQUEST program and NSA's "Access It All" push.
Marking: SECRET -
Contact chaining [pdf]
A secret GCHQ Applied Research presentation describing how the agency's analysts use automated tools to map out a surveillance target's social network — starting with a known email address or phone number, then scoring and ranking every person that target communicates with to identify the most "suspicious" or strongly connected contacts, using twelve different relationship types including direct calls, shared locations, timing patterns, equipment sharing and calling profile similarity.
Programs: CARPAT · PRIME TIME · SNAPDRAGON · MoaG · SORTING FRIENDS · CHART BREAKER · MAMBA · CONTACTLENS · FLEXIMART · PSOUP · IMMINGLE -
Content Acquisition Optimization PowerPoint Slides [pdf]
An NSA presentation on content acquisition optimisation — describing how incidental bulk collection from Yahoo Webmessenger, email address books, buddy lists and webmail inboxes was generating massive unintended collection volumes.
-
Content Extraction Enhancements For Target Analytics: SMS Text Messages: A Goldmine to Exploit (9 June 2011) [pdf]
The document describes the NSA’s Dishfire program, which collects hundreds of millions of global SMS messages daily, and the PREFER system, which extracts detailed metadata—including contacts, geolocation, travel, and financial information—from these messages for analytic purposes. It highlights the scale, operational processes, and types of data exploited to support intelligence and target analysis.