Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
PRISM planning slide (PRISM briefing 1) [pdf]
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
PRISM tasking slide (PRISM briefing 2) [pdf]
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
PRISM/US-984XN Overview [pdf]
Blurry screengrabs from the "PRISM/US-984XN Overview" slide deck shown on the Fantástico O Globo broadcast. This document contains slides that are not incldued in the slides published by The Washington Post, The Guardian, Le Monde, and others.
-
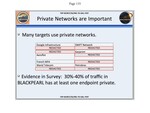
Private Networks are Important [pdf]
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
Procedures Used By The National Security Agency For Targeting Non-United States Persons Reasonably Believed To Be Located Outside The United States To Acquire Foreign Intelligence Court Information Pursuant To Section 702 Of The Foreign Intelligence Surveillance Act Of 1978 [pdf]
The NSA’s 2009 Section 702 targeting procedures lay out how analysts decide who can be surveilled without a warrant, supposedly limiting spying to foreigners abroad. In reality, the rules give the agency wide latitude to presume people are foreign, rely on vague “totality of the circumstances” tests, and allow broad technical methods like IP filters and metadata checks. Oversight is mostly internal and after-the-fact, creating significant potential for U.S. communications to be swept up with little accountability.
People: Holder, Eric H. Jr. -
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
PROJECT BULLRUN Classification Guide [pdf]
This BULLRUN classification guide outlines the NSA’s highly secretive methods for undermining and exploiting encryption technologies through a combination of cryptanalysis, industry collaboration, covert implants, and network exploitation. It specifies strict classification protocols for capabilities against protocols like TLS/SSL, VPNs, VoIP, and webmail, emphasizing secrecy around sources, methods, and industry partnerships that make commercial encryption systems deliberately vulnerable.
Programs: BULLRUN · APERIODIC · AMBULANT · AUNTIE · PAINTEDEAGLE · PAWLEYS · PITCHFORD · PENDLETON · PICARESQUE · PIEDMONT“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · Ball, James · Borger, Julian · Greenwald, Glenn · Perlroth, Nicole · Larson, Jeff · Shane, Scott -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
Project SANDSTORM [pdf]
This document shortly describes Project SANDSTORM, part of the Active Sigint Enabling Passive Geolocation (ASEPG) program at Menwith Hill, which uses Wi-Fi signal characterization and satellite-based Overhead capabilities to geolocate high-value targets, with geolocations of under 100 meters expected even for low-power signals in denied areas. It focuses on actively enabling SIGINT to track targets via 802.11 wireless networks.
-
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
PTC Glossary [pdf]
This GCWiki PTC Glossary excerpt defines SIGINT-related telecom terms—IMEI, IMSI, INMARSAT—and documents internal collection systems (e.g., INCENSER at Bude) and targeting notes (which identifiers are useful for targeting and which are not). It’s a technical reference for signals analysts describing selectors, collection sources, and operational caveats.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Pull Steering Group Minutes [pdf]
A top secret STRAP1 GCHQ PullThrough Steering Group meeting record from February 2008 documenting the approval process for five surveillance and intelligence prototypes including KARMA POLICE — the mass internet browsing profiling system — alongside ORB FINDER for CNE operational relay box identification, SALTY OTTER for cross-media timing analysis, MOOSE MILK for telephone kiosk surveillance, and LIGHTWOOD for email address extraction used by JTRIG.
Programs: MYOFIBRIL · SALTYOTTER · PRIMETIME · KARMAPOLICE · ORBFINDER · MOOSEMILK · LIGHTWOOD · JTRIG · MERAPEAK · MONTEVISTA · KED -
QFD BLACKHOLE Technology Behind INOC [pdf]
A UK SECRET STRAP2 COMINT ORCON GCHQ Applied Research presentation from March 2009 documenting the BLACK HOLE bulk data repository's scale and structure, and the suite of analytical tools — MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS and MARBLED GECKO — built on top of it to answer specific intelligence questions about online presence, browsing activity, forum usage and geolocation searches.
Programs: BLACKHOLE · MESME · NETEZZA · CLOUDS · MUTANTBROTH · KARMAPOLICE · INFINITEMONKEYS · MARBLEDGECKO · GOOB · AUTOASSOC · PSOUP · SOCIALANIMAL · SAMUELPEPYS · MEMORYHOLE · HRMAP · PSOUPALERT · LAUGHINGHYENA -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R. -
QUANTUM Shooter SBZ Notes [pdf]
An NSA WikiInfo technical reference page describing the QUANTUM shooter infrastructure — covering how compromised internet hosts are configured with STRAITBIZARRE implants using FELONYCROWBAR and Deployed Node Documents, the CHIMNEYPOOL/FRIEZERAMP communications architecture linking shooters to TURBINE via SURPLUSHANGAR and HANGARSURPLUS diodes, and GCHQ's distinct MHS shooter configuration that suppresses callbacks entirely.
Programs: QUANTUM · QUANTUMSHOOTER · FREEFLOW · CHIMNEYPOOL · FELONYCROWBAR · STRAITBIZARRE · SURPLUSHANGAR · HANGARSURPLUS · PASSAGEHILL · FORESTPLACE · FUSSYKEEL · FINGERGNOME · FROZENEARTH · FRIEZERAMP · ISLANDTRANSPORT · GENIE · MIDDLEMAN · WEBSNIPERGATEWAY · WAITAUTO · ZOMBIEARMY · FIPTRIX · TURBINE -
Quantum – from GCHQ documents dates October 2012 [pdf]
Portion of a document from the NSA’s British equivalent, the GCHQ, in which Sweden is not mentioned, but it describes an example of how Quantum has been used to attack computers in an African country where the users have visited extremist websites.
-
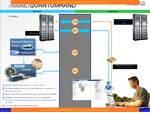
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
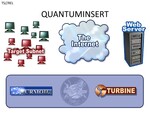
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael